
routeros-scanner
 microsoft/routeros-scanner
Tool to scan for RouterOS (Mikrotik) forensic artifacts and vulnerabilities.
configuration-auditingdigital-forensicsembedded-systems-security+8
microsoft/routeros-scannerTool to scan for RouterOS (Mikrotik) forensic artifacts and vulnerabilities.
 star-sg/random-scripts
Collection of DFIR and OSINT Python scripts for parsing malicious LNK samples, extracting OLE objects from MHTML, and hashing favicons to hunt…
 seekbytes/ipa
GUI analyzer for deep-diving into PDF files. Detect malicious payloads, understand object relationships, and extract key information for threat…
 msuhanov/easy_triage
Scripts to triage compromised systems (Linux, ESXi, FreeBSD/NetScaler)
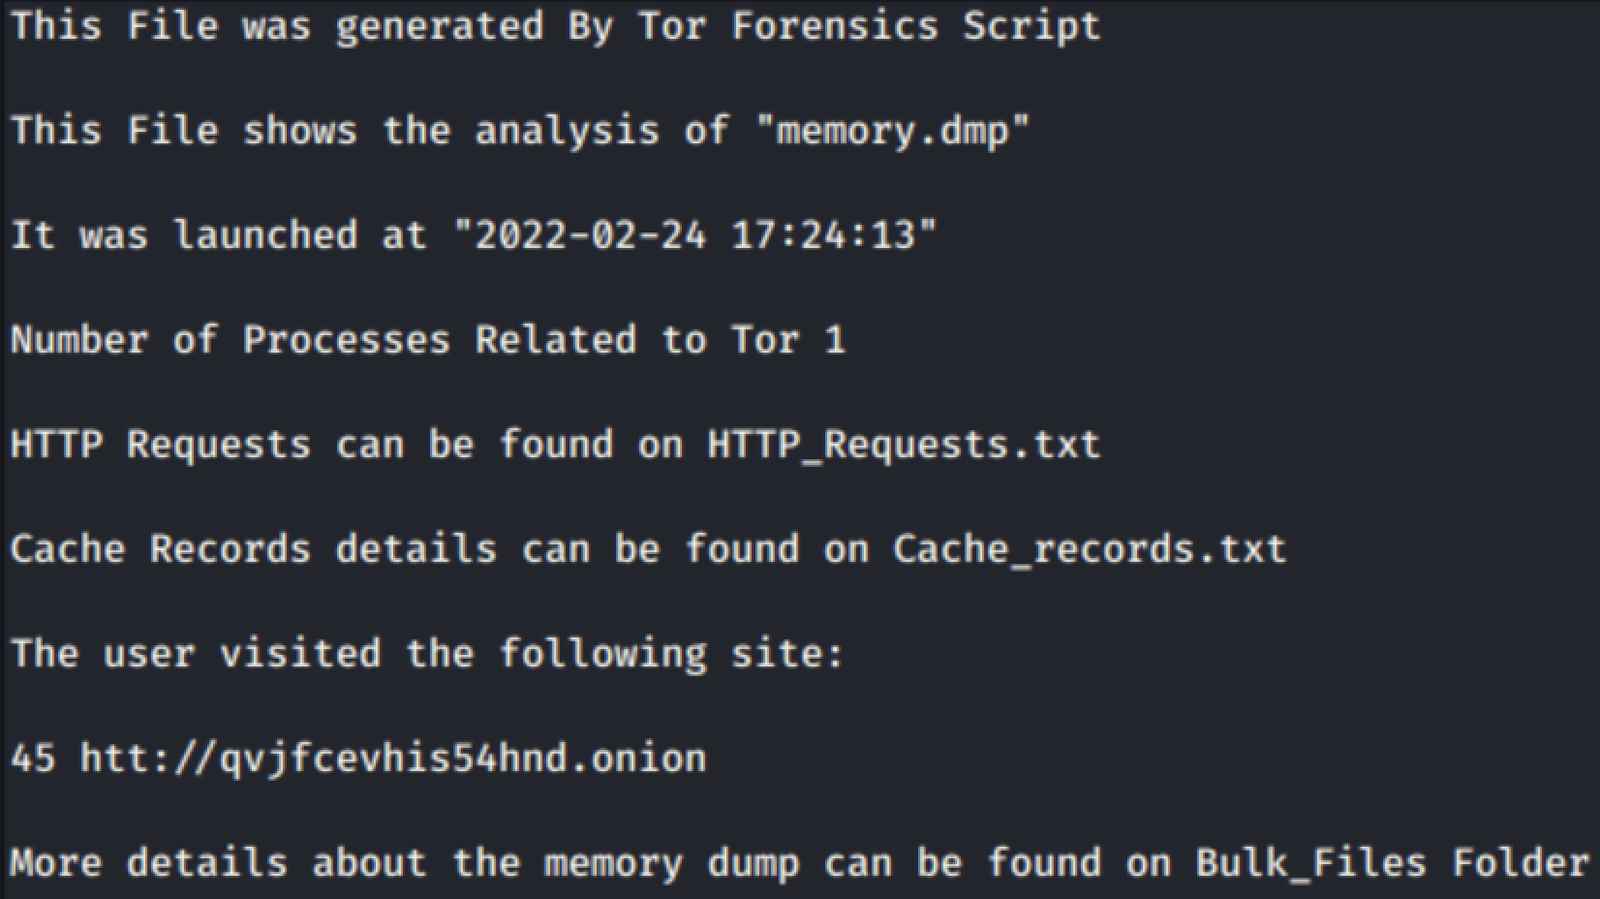 exmak-s/cve-2021-46702
Proof-of-concept script that analyzes Windows memory dumps to recover visited Tor onion services, bypassing Tor Browser's anonymity by exploiting…
 toxy4ny/rinhit
Collects macOS and iOS artifacts to build timelines of network activity, cross-device identity, and physical location correlation for reconnaissance…
 itsmoorgrove/tgscope
Telegram OSINT, scraping and archival as a local web app. Multi-account collection, profile lookup with historic photos and change diffs, ten export…
 cenobyte-vincit/memdumper
Abuses macOS debugger entitlements and DYLD_INSERT_LIBRARIES to dump or search a running process's memory while shifting EDR attribution to a signed…
 talha-nazeef-ahmed/alpc-enumerator
A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.
 xephora/threat-remediation-scripts
This repository contains a list of new remediation scripts.
 dfir-orc/dfir-orc
Forensics artefact collection tool for systems running Microsoft Windows
 c3n7ral051nt4g3ncy/osint_inception-links
Current links from the OSINT Inception start-me project
 cisagov/untitledgoosetool
Untitled Goose Tool is a robust and flexible hunt and incident response tool that adds novel authentication and data gathering methods in order to…
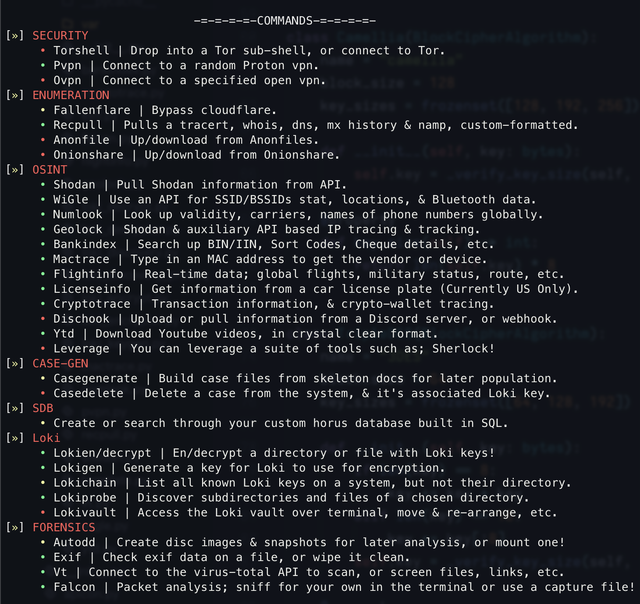 6abd/horus
An OSINT / digital forensics tool built in Python

 nccgroup/metadataplus
A tool to use novel locations to extract metadata from Office documents.
 synacktiv/ntdissector
Active Directory NTDS database parser that dumps records to JSON, supports object filtering, and decrypts encrypted columns using SYSTEM hive or…
 thehive-project/cortex
Cortex: a Powerful Observable Analysis and Active Response Engine