

Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
20 results
wireshark preview

wireshark

GitHubwireshark/wireshark

Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
bluetooth-securitydata-exfiltrationdigital-forensics+11
9.9k
2 days ago
Cyber-Defenders-lab- preview

Cyber-Defenders-lab-

GitHubabiral-timalsina/cyber-defenders-lab-

My write-ups from CyberDefenders' Blue Team labs, solved using Wireshark. Covers TeamCity RCE (CVE-2024-27198), XSS session hijacking, and…
digital-forensicseducationincident-response+3
1 month ago
Wireshark preview

Wireshark

GitHubkirkdjohnson/wireshark

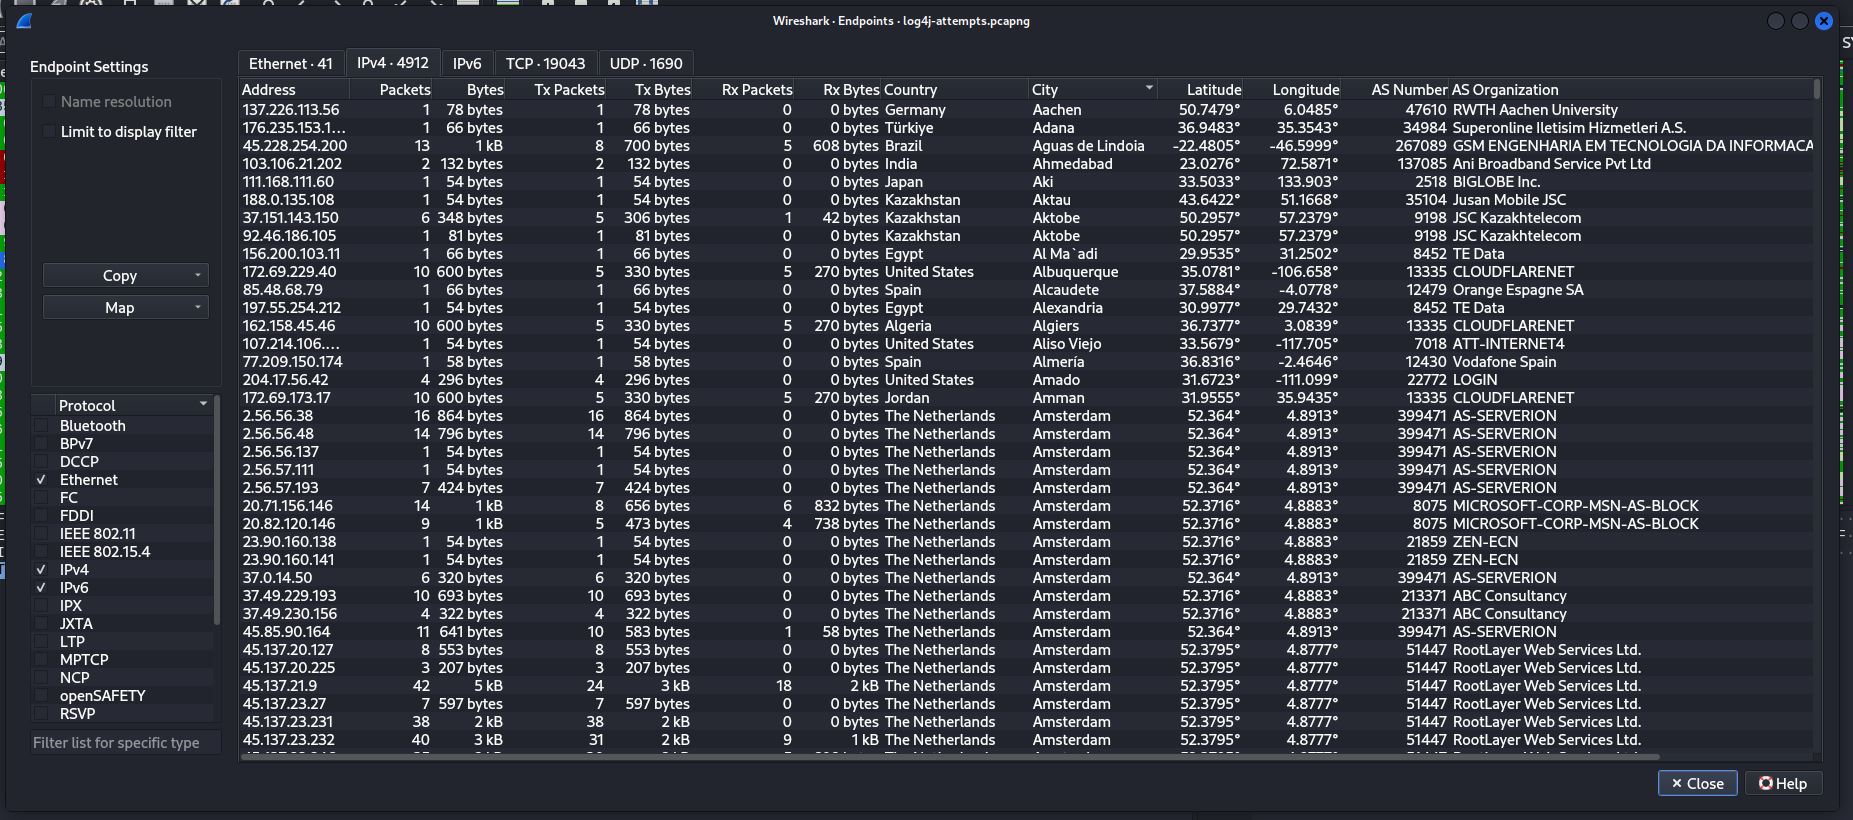
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…

command-and-controldigital-forensicseducation+9
32 years ago
ptcpdump preview

ptcpdump

GitHubmozillazg/ptcpdump

eBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…
cloud-securitycontainer-securitydigital-forensics+5
1.3k4 months ago
fim-ebpf preview

fim-ebpf

GitHubharshavmb/fim-ebpf

A lightweight eBPF program to monitor file creation and modification events on Linux. This tool leverages eBPF (Extended Berkeley Packet Filter) to…

defensive-toolsdigital-forensicsforensics+1
78 months ago
Network-Filesystem-Forensics preview

Network-Filesystem-Forensics

GitHubgilberto47831/network-filesystem-forensics

Reports on post-exploitation on honeypot exploiting vulnerable wu-ftpd (CVE-2001-0550)

digital-forensicsforensicsnetwork-forensics+2
4 years ago
An-Integrated-Wireless-Network-Forensic-Analysis-Framework preview

An-Integrated-Wireless-Network-Forensic-Analysis-Framework

GitHubbenadia/an-integrated-wireless-network-forensic-analysis-framework

This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…
digital-forensicsforensicsnetwork-forensics+2
68 years ago
Dshell preview

Dshell

GitHubusarmyresearchlab/dshell

Dshell is a network forensic analysis framework.
digital-forensicsdns-analysisforensics+3
5.5k2 years ago
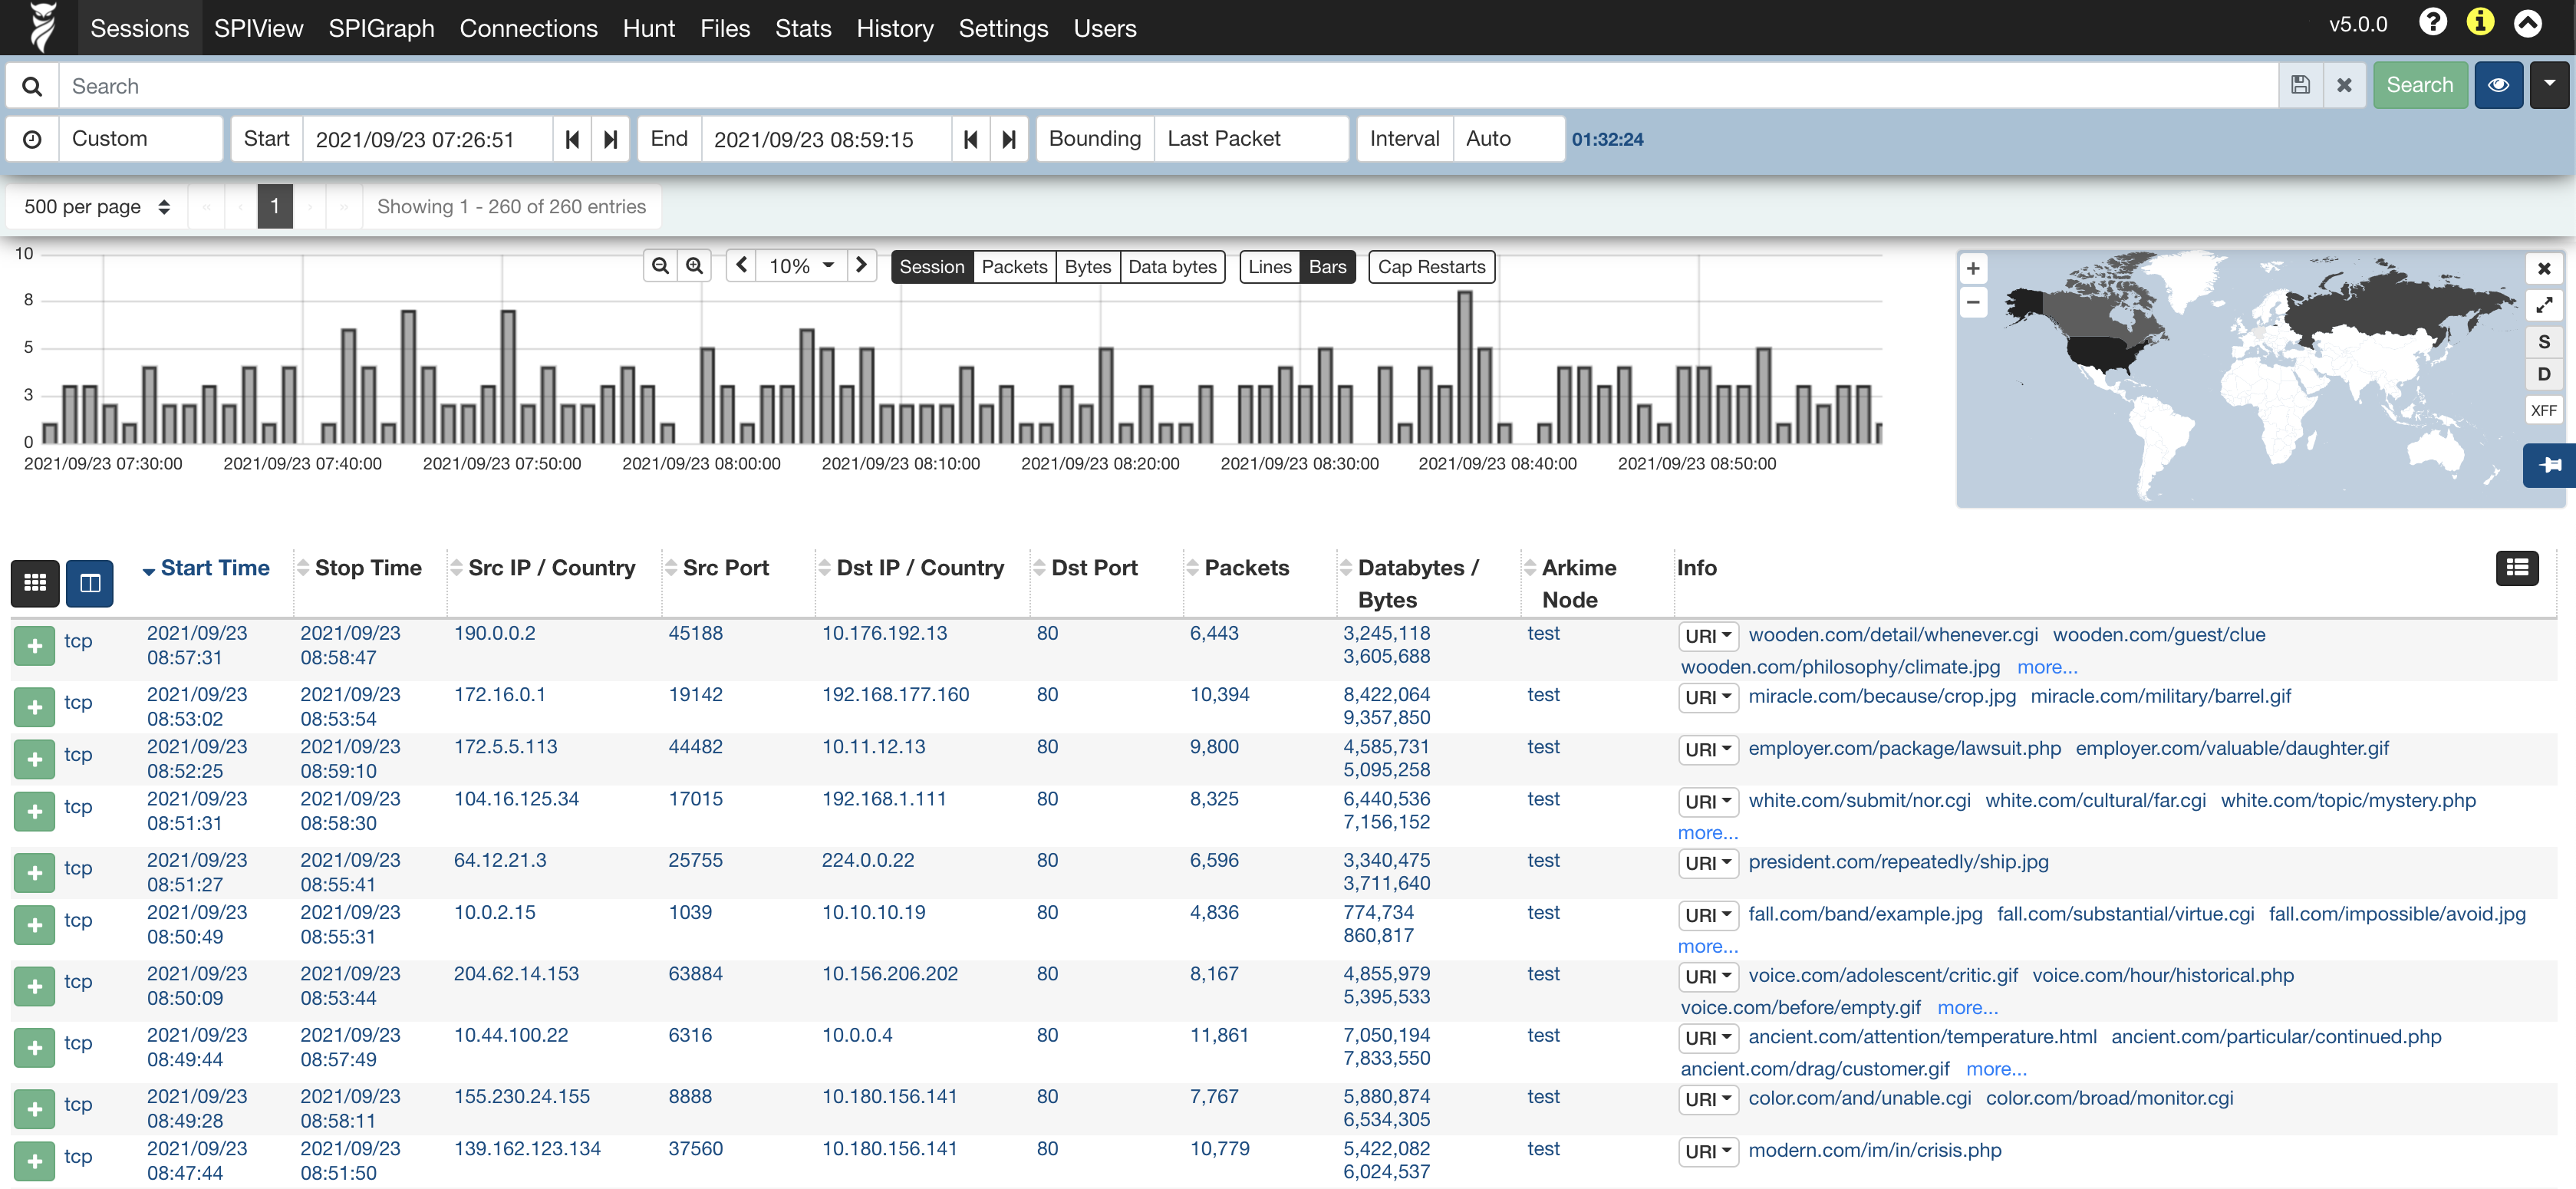
arkime preview

arkime

GitHubarkime/arkime

Arkime is an open source, large scale, full packet capturing, indexing, and database system.
defensive-toolsdigital-forensicsforensics+7
7.5k2 days ago
TCPViewer preview

TCPViewer

GitHubproxymanapp/tcpviewer

The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark

digital-forensicsforensicsinformation-gathering+3
42720h 58m ago
tcpflow preview

tcpflow

GitHubsimsong/tcpflow

TCP/IP packet demultiplexer. Download from:

digital-forensicsforensicsnetwork-forensics+1
1.8k7 months ago
joy preview

joy

GitHubcisco/joy

A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.
anomaly-detectiondigital-forensicsdns-analysis+7
1.4k6 years ago
pcapfex preview

pcapfex

GitHubvikwin/pcapfex

'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files
data-recoverydigital-forensicsforensics+2
2306 years ago
Malcolm preview

Malcolm

GitHubidaholab/malcolm

Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
defensive-toolsdigital-forensicsforensics+8
48119 days ago
pyshark preview

pyshark

GitHubkiminewt/pyshark

Python wrapper for tshark, allowing python packet parsing using wireshark dissectors

digital-forensicsencryption-decryption-toolsforensics+5
2.5k5 months ago
etl2pcapng preview

etl2pcapng

GitHubmicrosoft/etl2pcapng

Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.
digital-forensicsforensicsnetwork-forensics+2
7381 year ago
phantomprint preview

phantomprint

GitHubharuu77g/phantomprint

Passive hybrid fingerprinting engine — identify hosts without sending a single packet
digital-forensicsinformation-gatheringnetwork-mapping+7
428 days ago
packetsifterTool preview

packetsifterTool

GitHubpacketsifter/packetsiftertool

PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…

defensive-toolsdigital-forensicsforensics+5
935 years ago
Previous12Next