

DeadMatter
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
data-recoverydigital-forensicsforensics+7
qsecure-labs/deadmatterOffset Independent Credential Extraction Tool
 crypt0p3g/dpapi-toolkit
Drop any Windows DPAPI artifact and it identifies the format and the exact master key it needs, then decrypts once you supply the key. Offline, CLI +…
 amperclock/cve-2023-32784-kdbxpassdmp
Retrieves the master password from Keepass memory dump, using a hint of bruteforce.
 pugazhendii22/keepass-exfil-forensics
Network forensics writeup + tooling for a TryHackMe DFIR challenge: reverses a hex→Base64→XOR exfiltration chain from PCAP traffic, then recovers a…
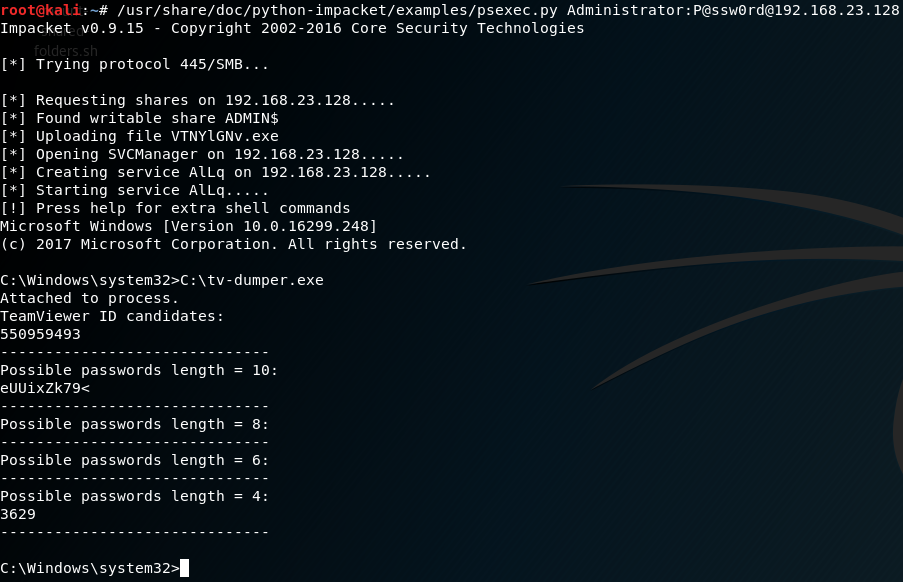 attackercan/teamviewer-dumper
Dump TeamViewer ID and password from memory. Works much better than other tools.
 mister-turtle/cve-2023-32784
Extracts KeePass master passwords from memory dumps of unlocked databases, outputting potential characters by position, a passphrase, and a…
 dev0558/cve-2023-32784-exploit-report
Educational demonstration of CVE-2023-32784 KeePass master password recovery via memory dump analysis, with step-by-step exploit setup and mitigation…
 b1tbreaker/cve-2025-48708
Lack of argument sanitization leading to password leakage in Ghostscript PDF versions up to 10.05.0.
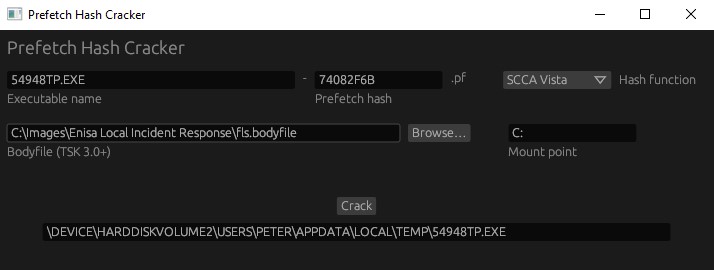 harelsegev/prefetch-hash-cracker
Brute-force tool that recovers full executable paths from Windows prefetch hashes using bodyfiles, supporting XP, Vista, and 2008 hash functions for…
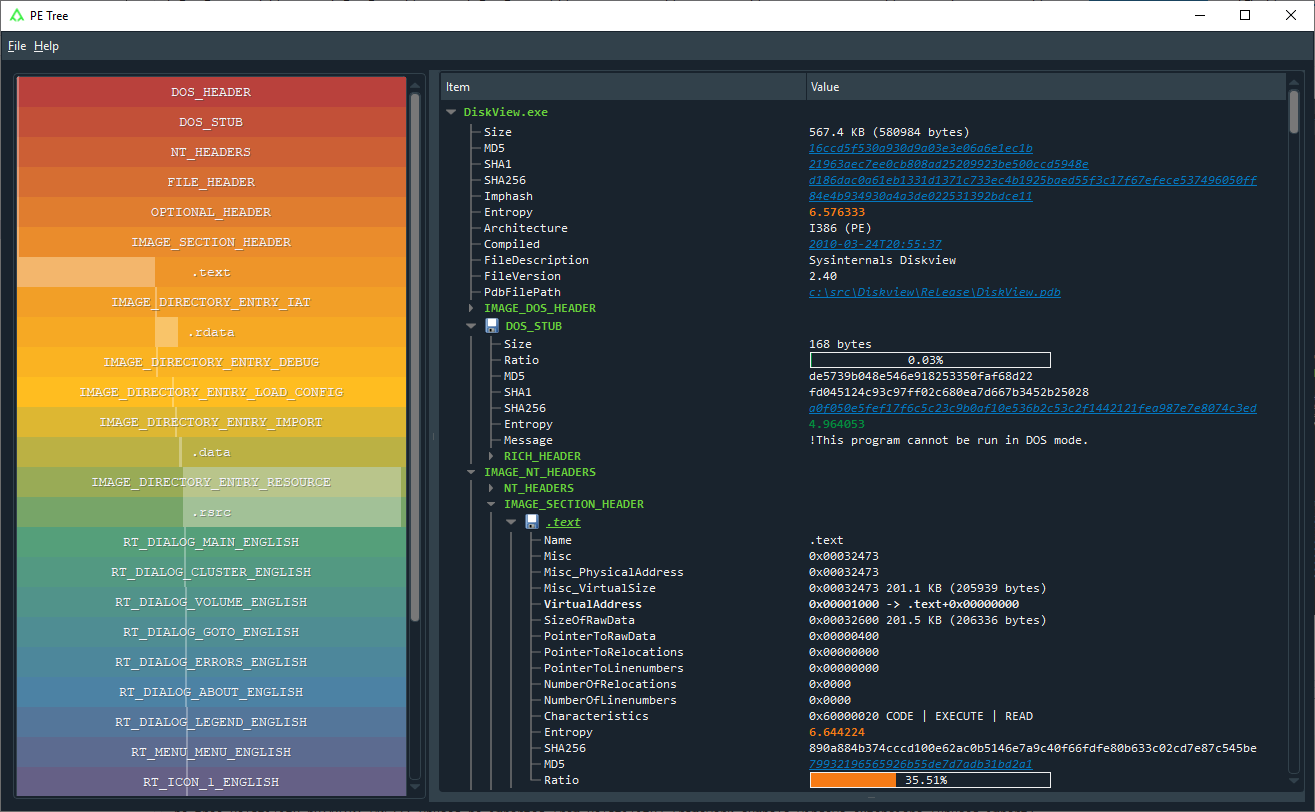 blackberry/pe_tree
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…