
webhacklist
 irsdl/webhacklist
Archive of the Top 10 Web Hacking Techniques - every nominee since 2006, preserved
curated-resourcesdigital-forensicseducation+4
91222h 41m ago
irsdl/webhacklistArchive of the Top 10 Web Hacking Techniques - every nominee since 2006, preserved
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 rawfilejson/awesome-osint-arsenal
OSINT & recon toolkit // 100+ tools, one-command installer, SOCMINT, GEOINT, network recon, dark web, forensics & more.
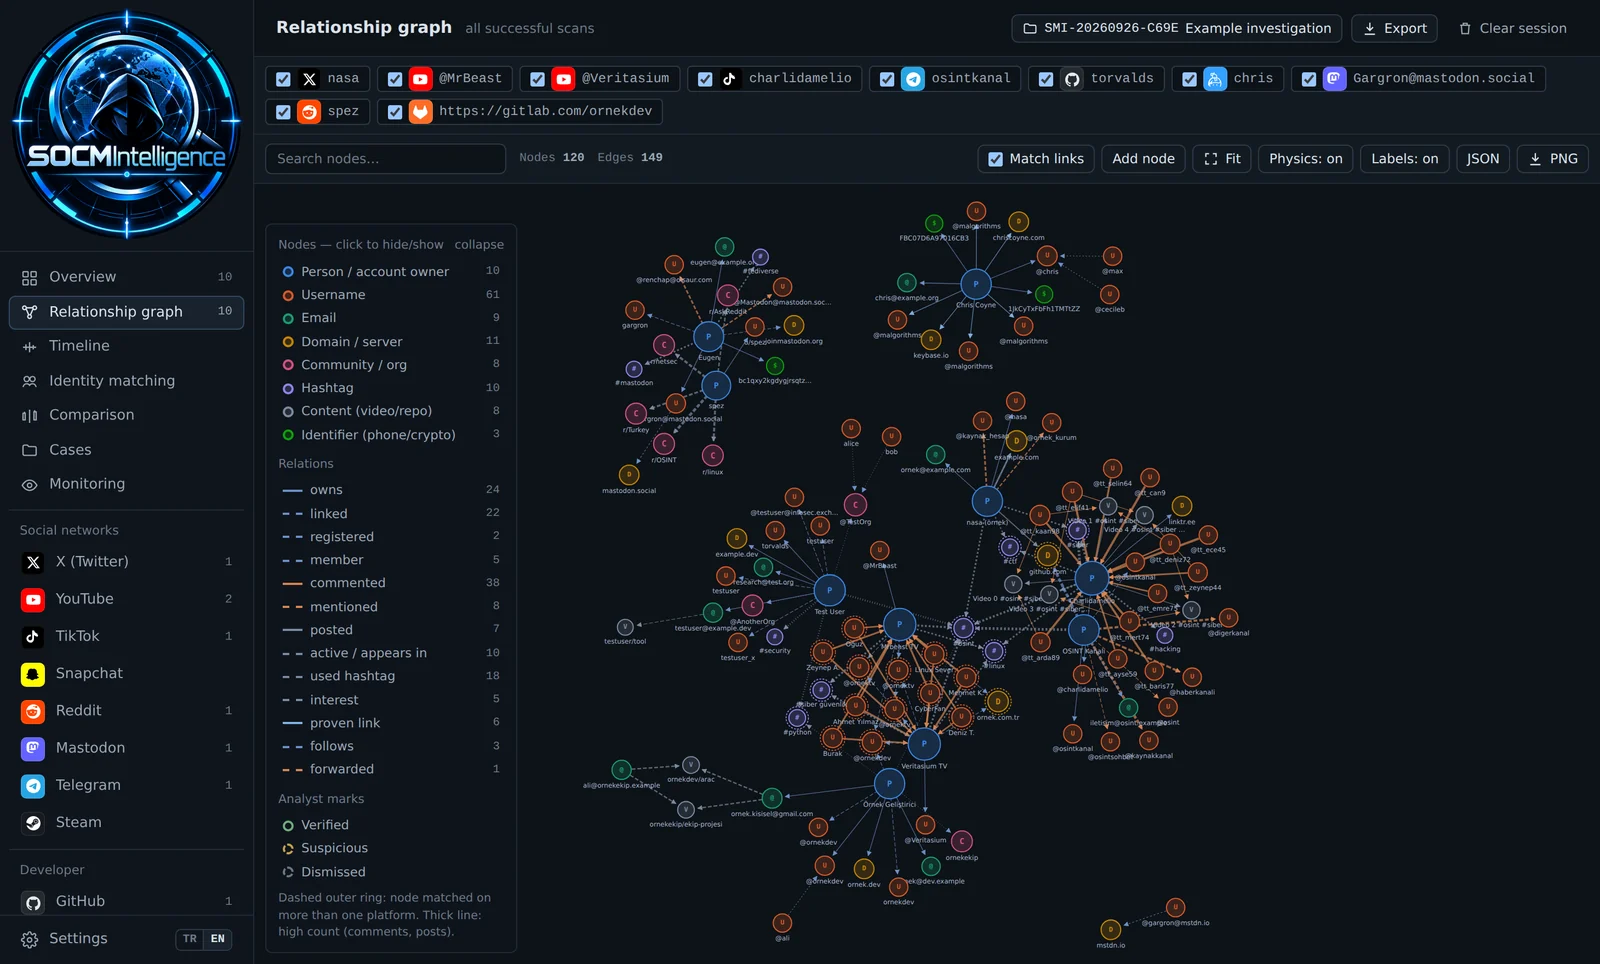 emrekybs/socmintelligence
A modular OSINT & SOCMINT framework for social media intelligence, investigation, and public data analysis.
 ilias1988/hacking-cheatsheets
A comprehensive collection of penetration testing cheatsheets, guides, and tools.
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…

 fox-it/citrix-netscaler-triage
Forensic triage toolkit for Citrix NetScaler devices, featuring a Dissect-based IOC scanner for webshells, timestomping, and suspicious binaries,…
 hasamba/dfir-companion
DFIR forensics companion server + capture extension
 microsoft/etl2pcapng
Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.
 maximilianfeix/hexvero
Know what changed inside your Electron release: diff two builds for IPC, preload, windows, fuses and hosts, with file:line. CLI, CI gate, MCP server.
 eset/malware-research
Code written as part of our various malware investigations
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
 c3n7ral051nt4g3ncy/osint_inception-links
Current links from the OSINT Inception start-me project
 lascc/dfirhub
Search Windows forensic artifacts, see where each one lives on disk, and copy the KAPE command to collect it. Also builds collection scripts and…
 cr0nx/awesome-linux-attack-forensics-purplelabs
This page is a result of the ongoing hands-on research around advanced Linux attacks, detection and forensics techniques and tools.
 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
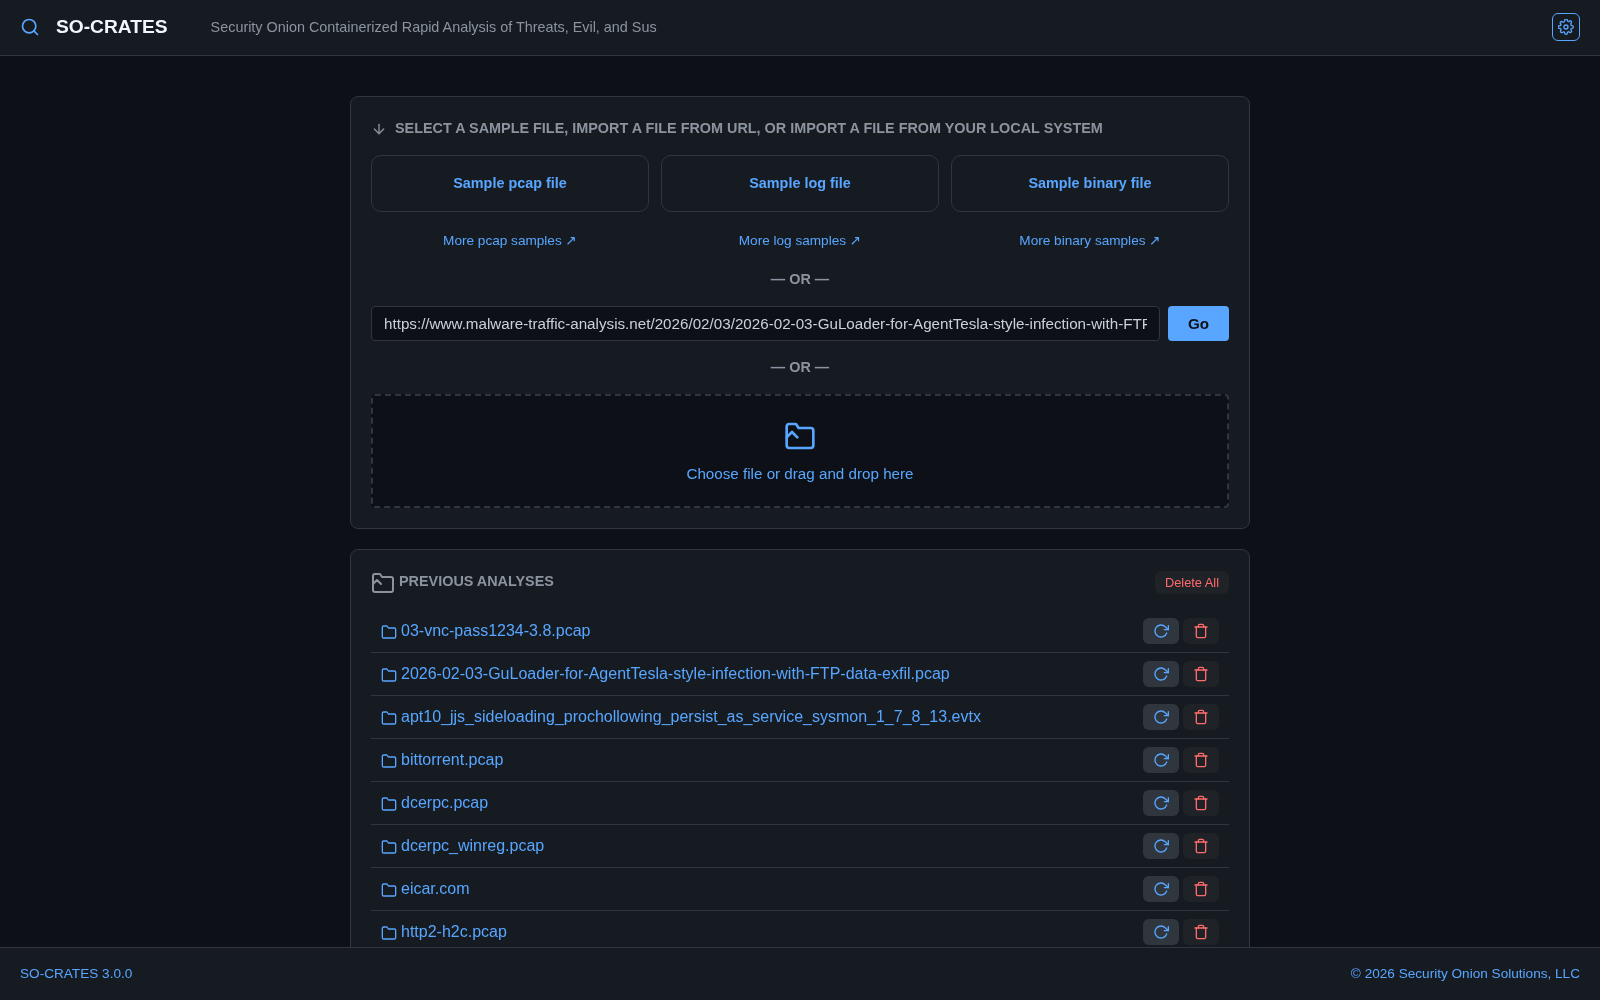 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!