


 seekbytes/ipa
GUI analyzer for deep-diving into PDF files. Detect malicious payloads, understand object relationships, and extract key information for threat…
 intelowlproject/intelowl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
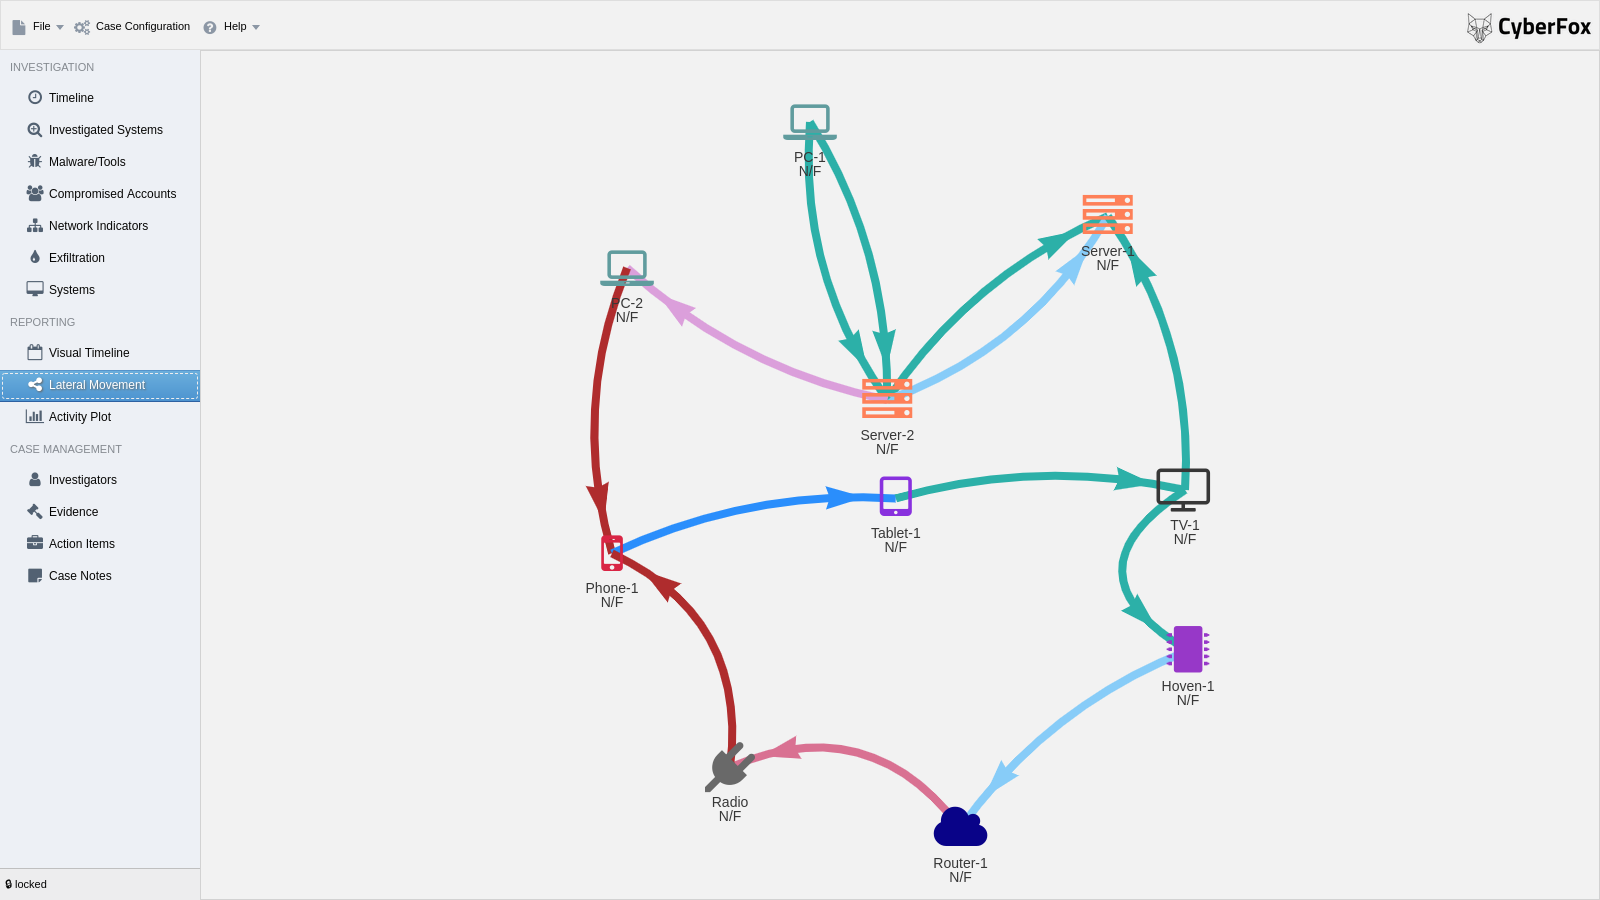 cyb3rfox/aurora-incident-response
Incident Response Documentation made easy. Developed by Incident Responders for Incident Responders
 c3n7ral051nt4g3ncy/osint_inception-links
Current links from the OSINT Inception start-me project
 simsong/bulk_extractor
This is the development tree. Production downloads are at:

 circl/factual-rules-generator
Generates YARA rules from installed software on a running OS to baseline known software and find similar installations across digital forensic…
 busindre/dumpzilla
Extract all forensic interesting information of Firefox, Iceweasel and Seamonkey browsers
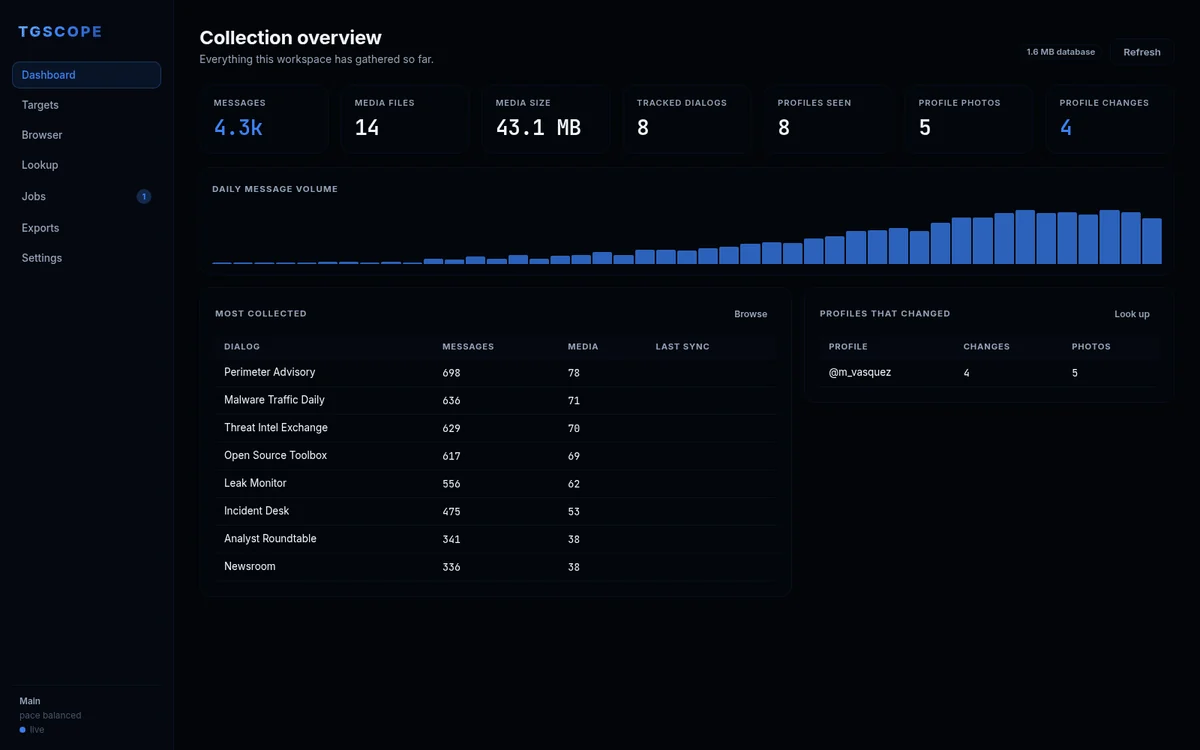 itsmoorgrove/tgscope
Telegram OSINT, scraping and archival as a local web app. Multi-account collection, profile lookup with historic photos and change diffs, ten export…
 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
 cenobyte-vincit/memdumper
Abuses macOS debugger entitlements and DYLD_INSERT_LIBRARIES to dump or search a running process's memory while shifting EDR attribution to a signed…
 lgggreg/skype-log-viewer
Download and View Skype History Without Skype
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
 xephora/threat-remediation-scripts
This repository contains a list of new remediation scripts.
 circl/ail-framework
AIL framework - Analysis Information Leak framework. Project moved to https://github.com/ail-project