
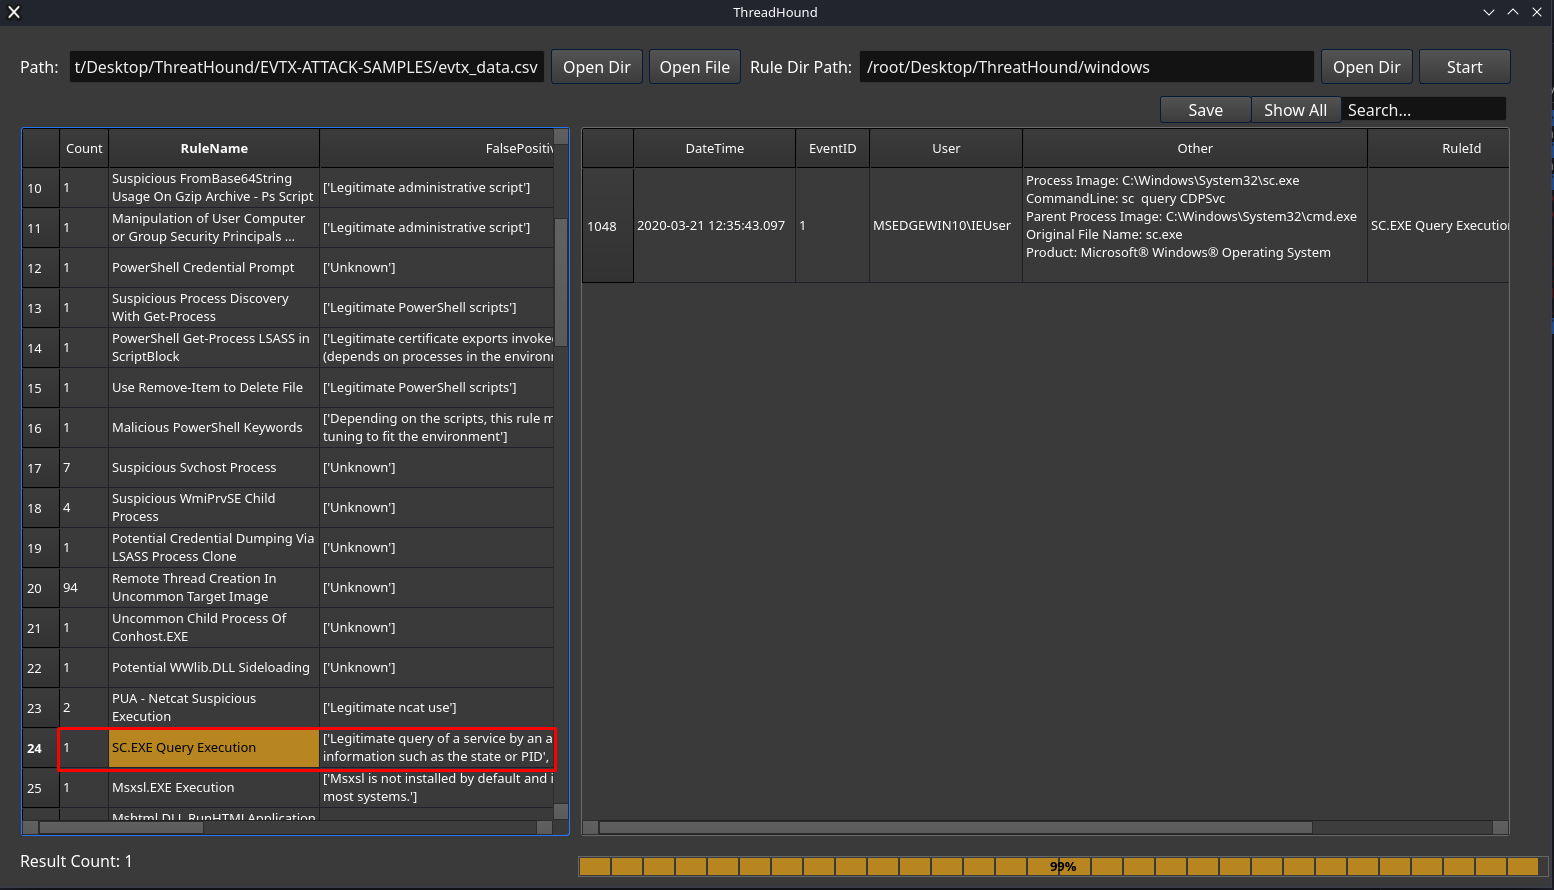
ThreatHound
 mazx0p/threathound
Automated threat hunting and incident response tool for Windows Event Logs with Sigma rule integration, real-time detection, and forensic artifact…
digital-forensicsincident-responselog-analysis+1
159
mazx0p/threathoundAutomated threat hunting and incident response tool for Windows Event Logs with Sigma rule integration, real-time detection, and forensic artifact…
 yamato-security/wela
Audits Windows event log settings against best-practice guidelines and Sigma-rule detectability, with automated configuration for DFIR readiness.
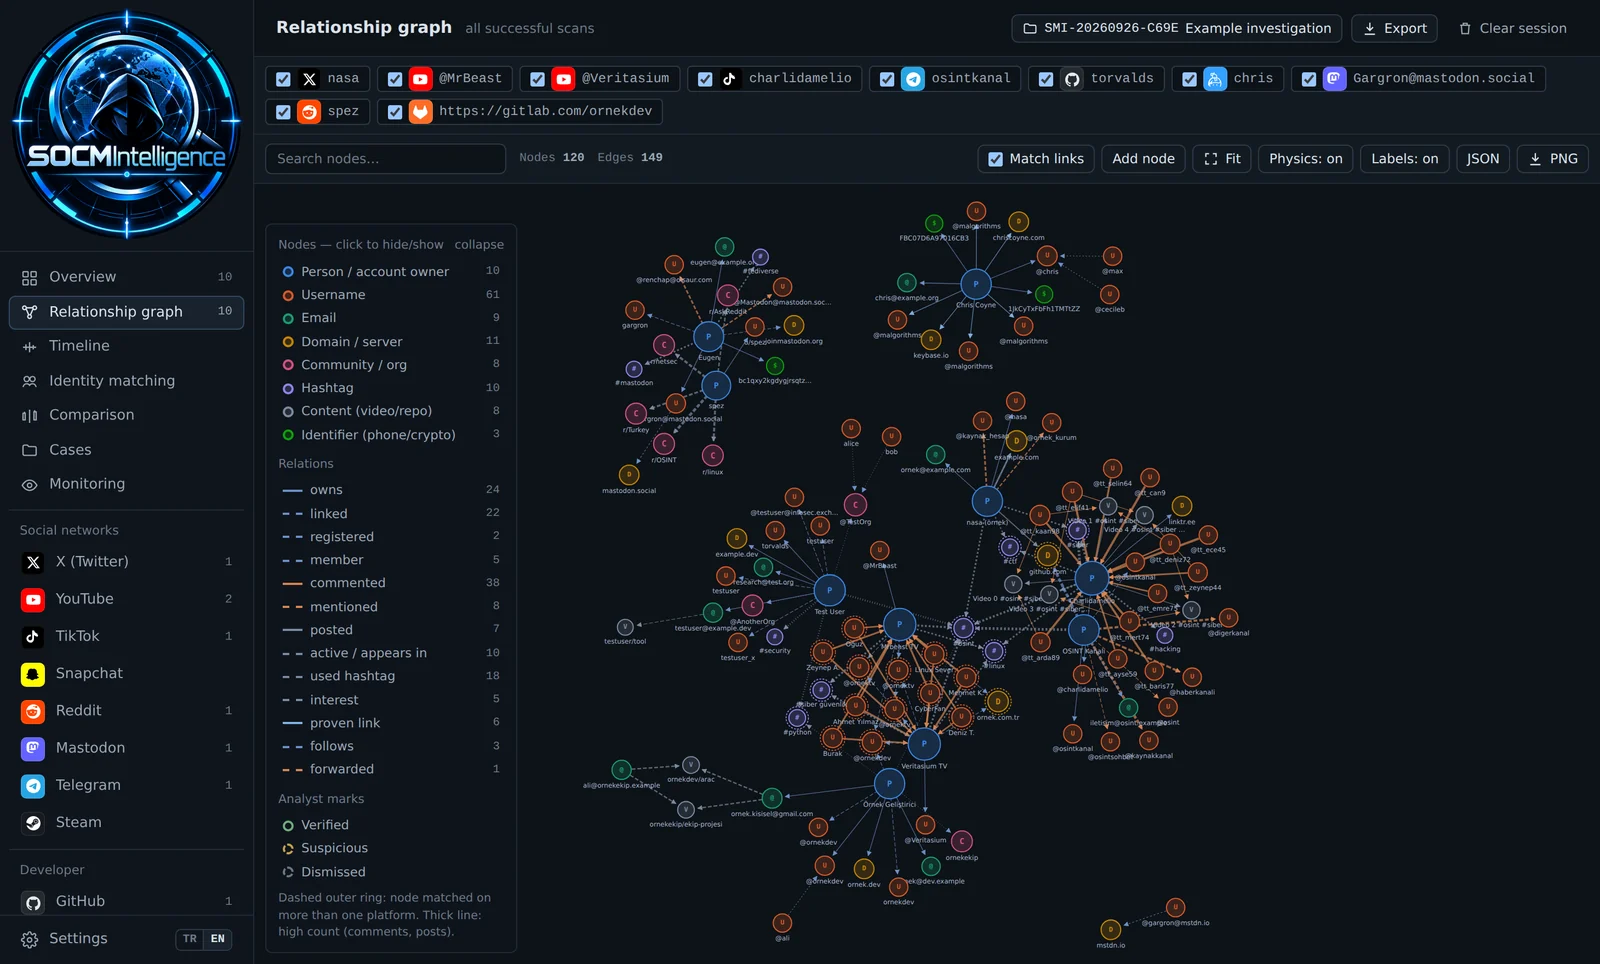 emrekybs/socmintelligence
A modular OSINT & SOCMINT framework for social media intelligence, investigation, and public data analysis.
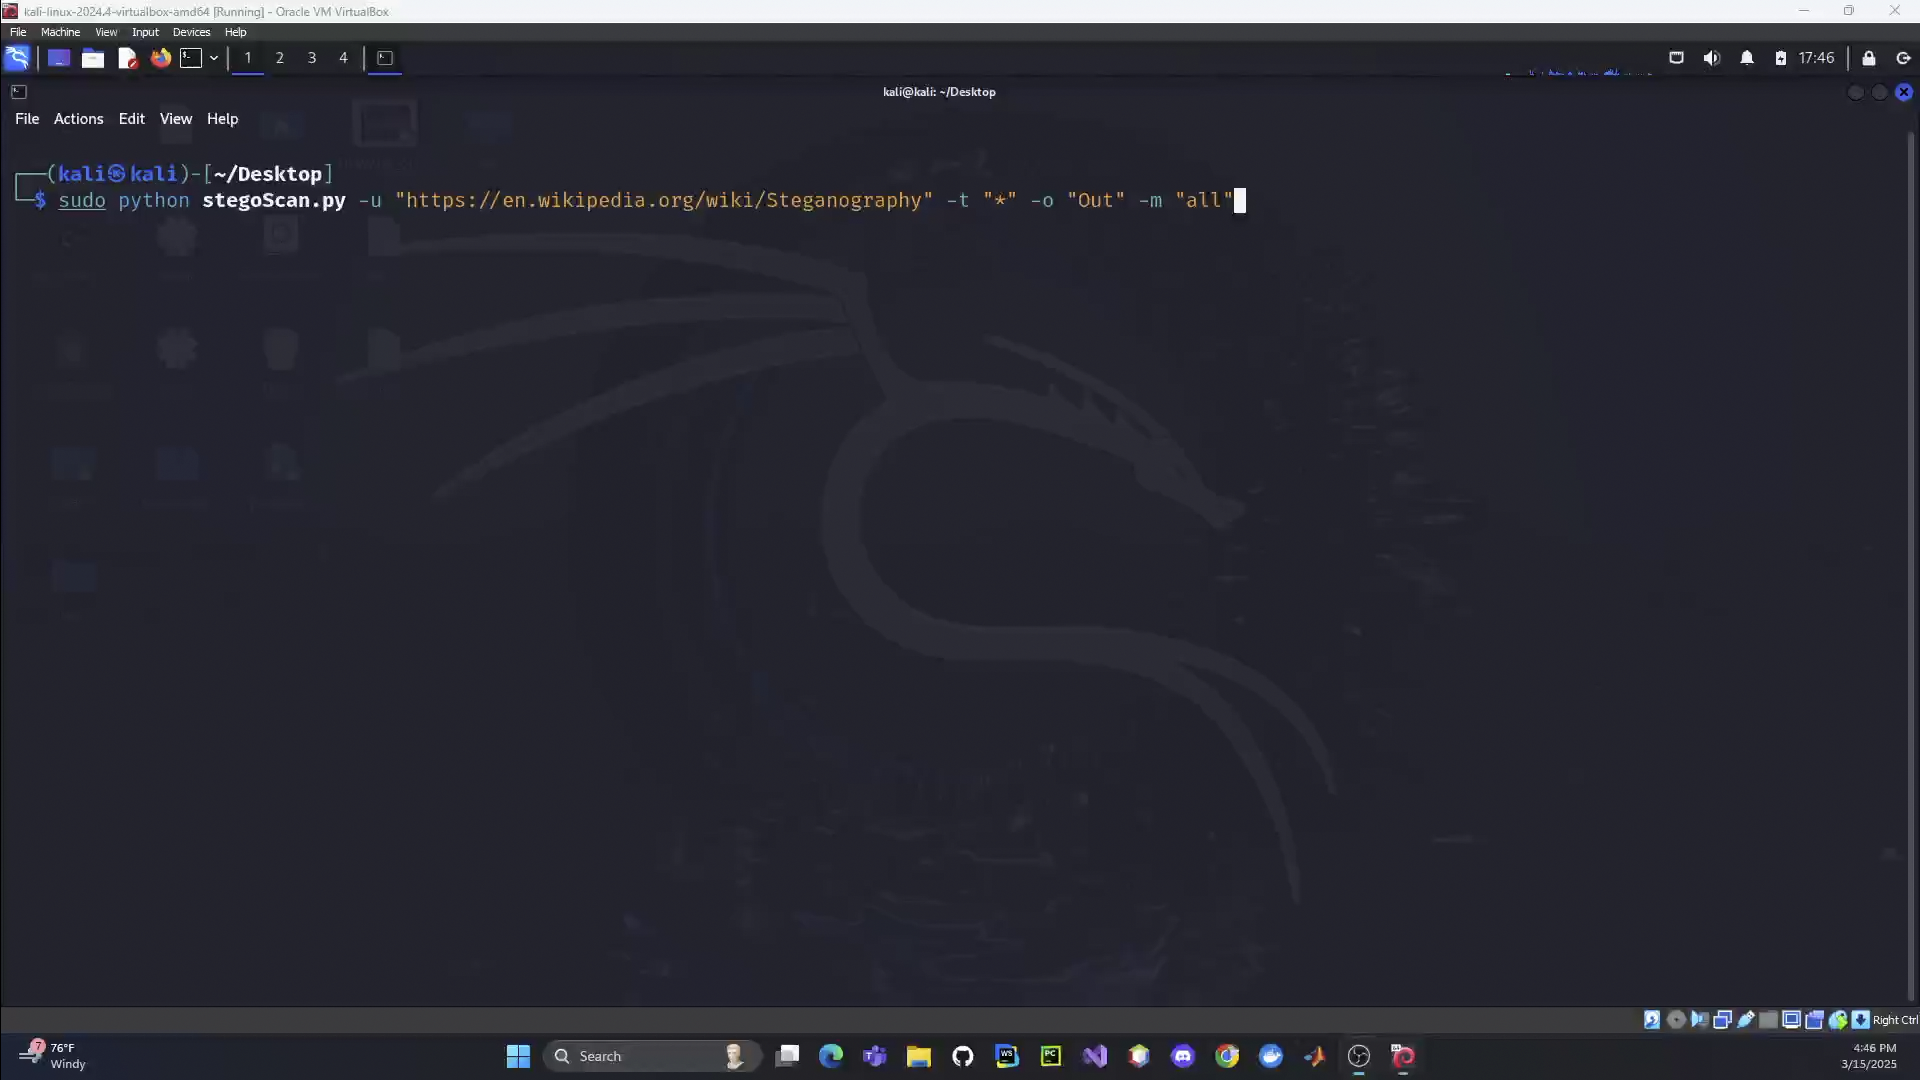 lcbower33/stegoscan
Automated steganography detection tool that scans websites, web servers, and local directories using AI-driven object/text recognition and deep file…
 fboldewin/atmmalscan
Command-line DFIR tool for scanning Windows ATM systems to detect malware traces in process memory and disk, with automated memory dump creation for…
 emalderson/thephish
ThePhish: an automated phishing email analysis tool
 caveeroo/gv_decryptor
Gallery Vault dump recovery tool with automated discovery, key derivation and automatic media restoration.
 guibacellar/tex
Telegram intelligence collection tool for researchers and investigators. Scrapes groups, messages, media, and user data with OCR, Elasticsearch…
 invictus-ir/alfa
Automated forensic analysis tool for Google Workspace audit logs. Acquires all log types, maps events to MITRE ATT&CK Cloud Framework, and identifies…