
walletool
 qg5casz/walletool
Extracts cryptocurrency private keys and addresses from wallet.dat files for Bitcoin and Litecoin, enabling wallet recovery and forensic analysis.
cryptographydata-recoverydigital-forensics+2
524
qg5casz/walletoolExtracts cryptocurrency private keys and addresses from wallet.dat files for Bitcoin and Litecoin, enabling wallet recovery and forensic analysis.
 crypt0p3g/dpapi-toolkit
Drop any Windows DPAPI artifact and it identifies the format and the exact master key it needs, then decrypts once you supply the key. Offline, CLI +…
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 neccie/yellowkey-bitlocker-cve-2026-45585
Manage BitLocker recovery keys, unlock encrypted drives, and monitor encryption status with this lightweight Windows utility.
 amperclock/cve-2023-32784-kdbxpassdmp
Retrieves the master password from Keepass memory dump, using a hint of bruteforce.
 s4larie/walletool
A utility for extracting cryptocurrency wallet data from wallet.dat files.
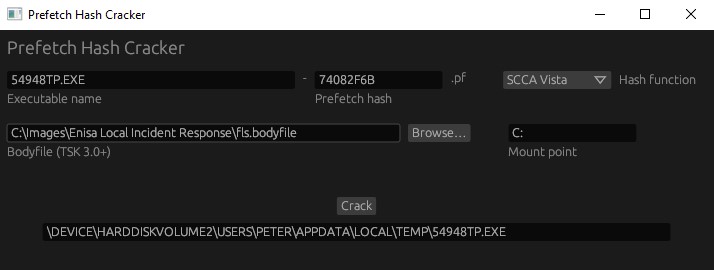 harelsegev/prefetch-hash-cracker
Brute-force tool that recovers full executable paths from Windows prefetch hashes using bodyfiles, supporting XP, Vista, and 2008 hash functions for…
 pugazhendii22/keepass-exfil-forensics
Network forensics writeup + tooling for a TryHackMe DFIR challenge: reverses a hex→Base64→XOR exfiltration chain from PCAP traffic, then recovers a…
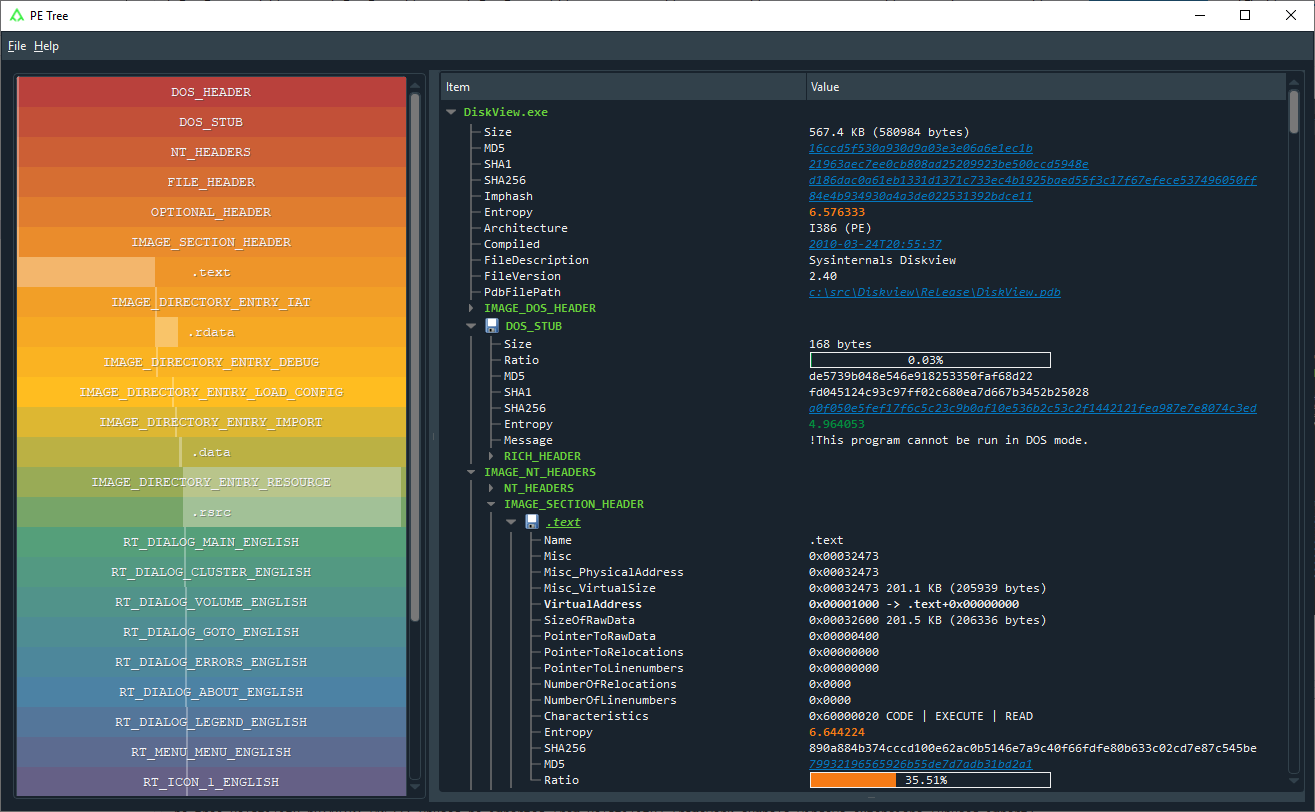 blackberry/pe_tree
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
 patrickdw123/paranoidf
ParanoiDF - PDF Analysis Suite based on PeePDF by Jose Miguel Esparza (http://peepdf.eternal-todo.com/). Tools added: Password cracking, redaction…
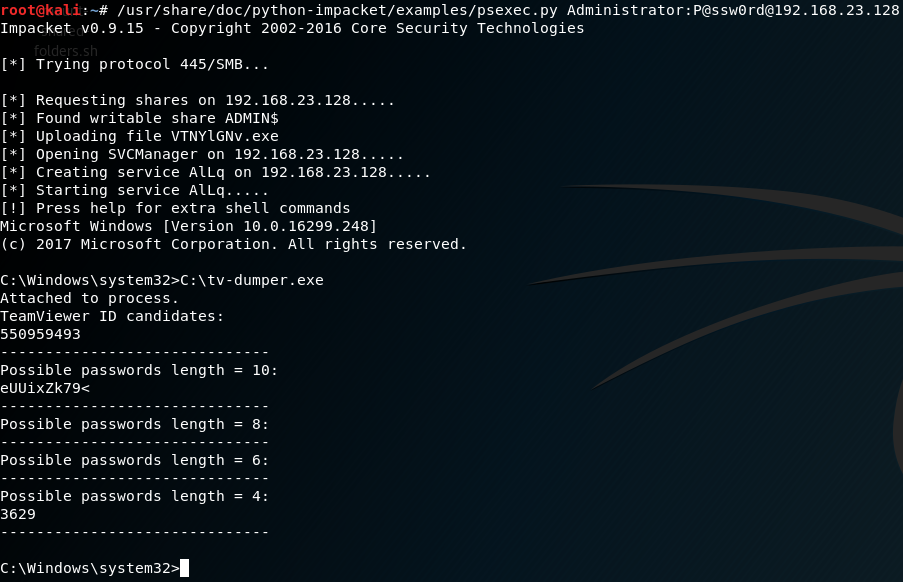 attackercan/teamviewer-dumper
Dump TeamViewer ID and password from memory. Works much better than other tools.
 b1tbreaker/cve-2025-48708
Lack of argument sanitization leading to password leakage in Ghostscript PDF versions up to 10.05.0.
 dev0558/cve-2023-32784-exploit-report
Educational demonstration of CVE-2023-32784 KeePass master password recovery via memory dump analysis, with step-by-step exploit setup and mitigation…
 s3cur3th1ssh1t/creds
Some usefull Scripts and Executables for Pentest & Forensics
 skelsec/adiskreader-secretsdump
Extract registry and NTDS secrets from local or remote disk images
 mister-turtle/cve-2023-32784
Extracts KeePass master passwords from memory dumps of unlocked databases, outputting potential characters by position, a passphrase, and a…