

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
137 results
zeek preview

zeek

GitHubzeek/zeek

Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.

anomaly-detectionanti-botdefensive-tools+14
8.2k1 day ago
systeminformer preview

systeminformer

GitHubwinsiderss/systeminformer

Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
debuggersdigital-forensicsforensics+6
16.4k2 days ago
citrix-netscaler-triage preview

citrix-netscaler-triage

GitHubfox-it/citrix-netscaler-triage

Forensic triage toolkit for Citrix NetScaler devices, featuring a Dissect-based IOC scanner for webshells, timestomping, and suspicious binaries,…
digital-forensicsincident-responseioc-management+3
7429 days ago
etl2pcapng preview

etl2pcapng

GitHubmicrosoft/etl2pcapng

Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.
digital-forensicsforensicsnetwork-forensics+2
7421 year ago
watermarks-remover preview

watermarks-remover

GitHubguillaumemeyer/watermarks-remover

A privacy-first app that strips AI watermarks from content you own.

adversarial-attackai-securitydigital-forensics+5
25.8k10 days ago
Incident-Response-Powershell preview

Incident-Response-Powershell

GitHubbert-janp/incident-response-powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…


digital-forensicsdisk-forensicsforensics+6
8265 months ago
ndaal_public_auditd preview

ndaal_public_auditd

GitLabndaal_open_source/ndaal_public_auditd

Best-practice Linux Auditd rule set with 14,956 MITRE ATT&CK-mapped rules, Ansible deployment role, and lint/test tooling for security monitoring and…
configuration-auditingdefensive-toolsdevsecops+5
45 days ago
openstego preview

openstego

GitHubsyvaidya/openstego

OpenStego is a steganography application that provides two functionalities: a) Data Hiding: It can hide any data within an image file. b)…

digital-forensicsencryption-decryption-toolssteganography
1.4k3 years ago
hexvero preview

hexvero

GitHubmaximilianfeix/hexvero

Know what changed inside your Electron release: diff two builds for IPC, preload, windows, fuses and hosts, with file:line. CLI, CI gate, MCP server.

ai-securityandroid-securitybinary-analysis+9
97 days ago
IntelOwl preview

IntelOwl

GitHubintelowlproject/intelowl

Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…

curated-resourcesdigital-forensicsdynamic-analysis-sandboxing+14
4.8k2 months ago
Kage-DFIR-toolkit preview

Kage-DFIR-toolkit

GitHubkarim852/kage-dfir-toolkit

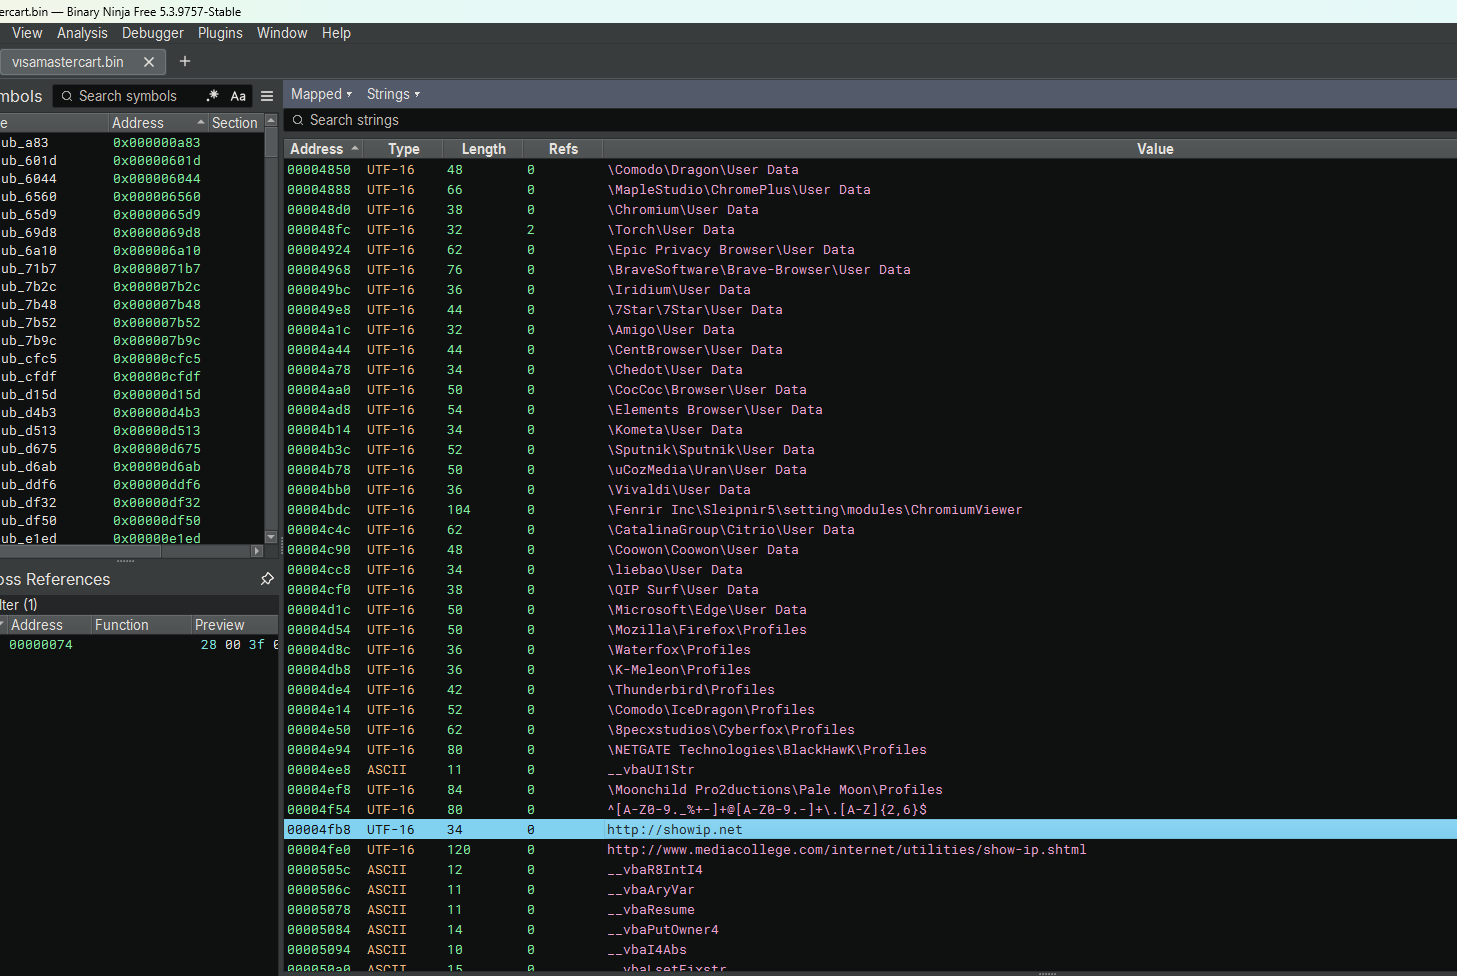
Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…
defensive-toolsdigital-forensicsforensics+8
4222 days ago
DarkTortilla-RAT-Telegram-Exfiltration-Payload-Extraction-Analysis preview

DarkTortilla-RAT-Telegram-Exfiltration-Payload-Extraction-Analysis

GitHubkaandemir993/darktortilla-rat-telegram-exfiltration-payload-extraction-analysis

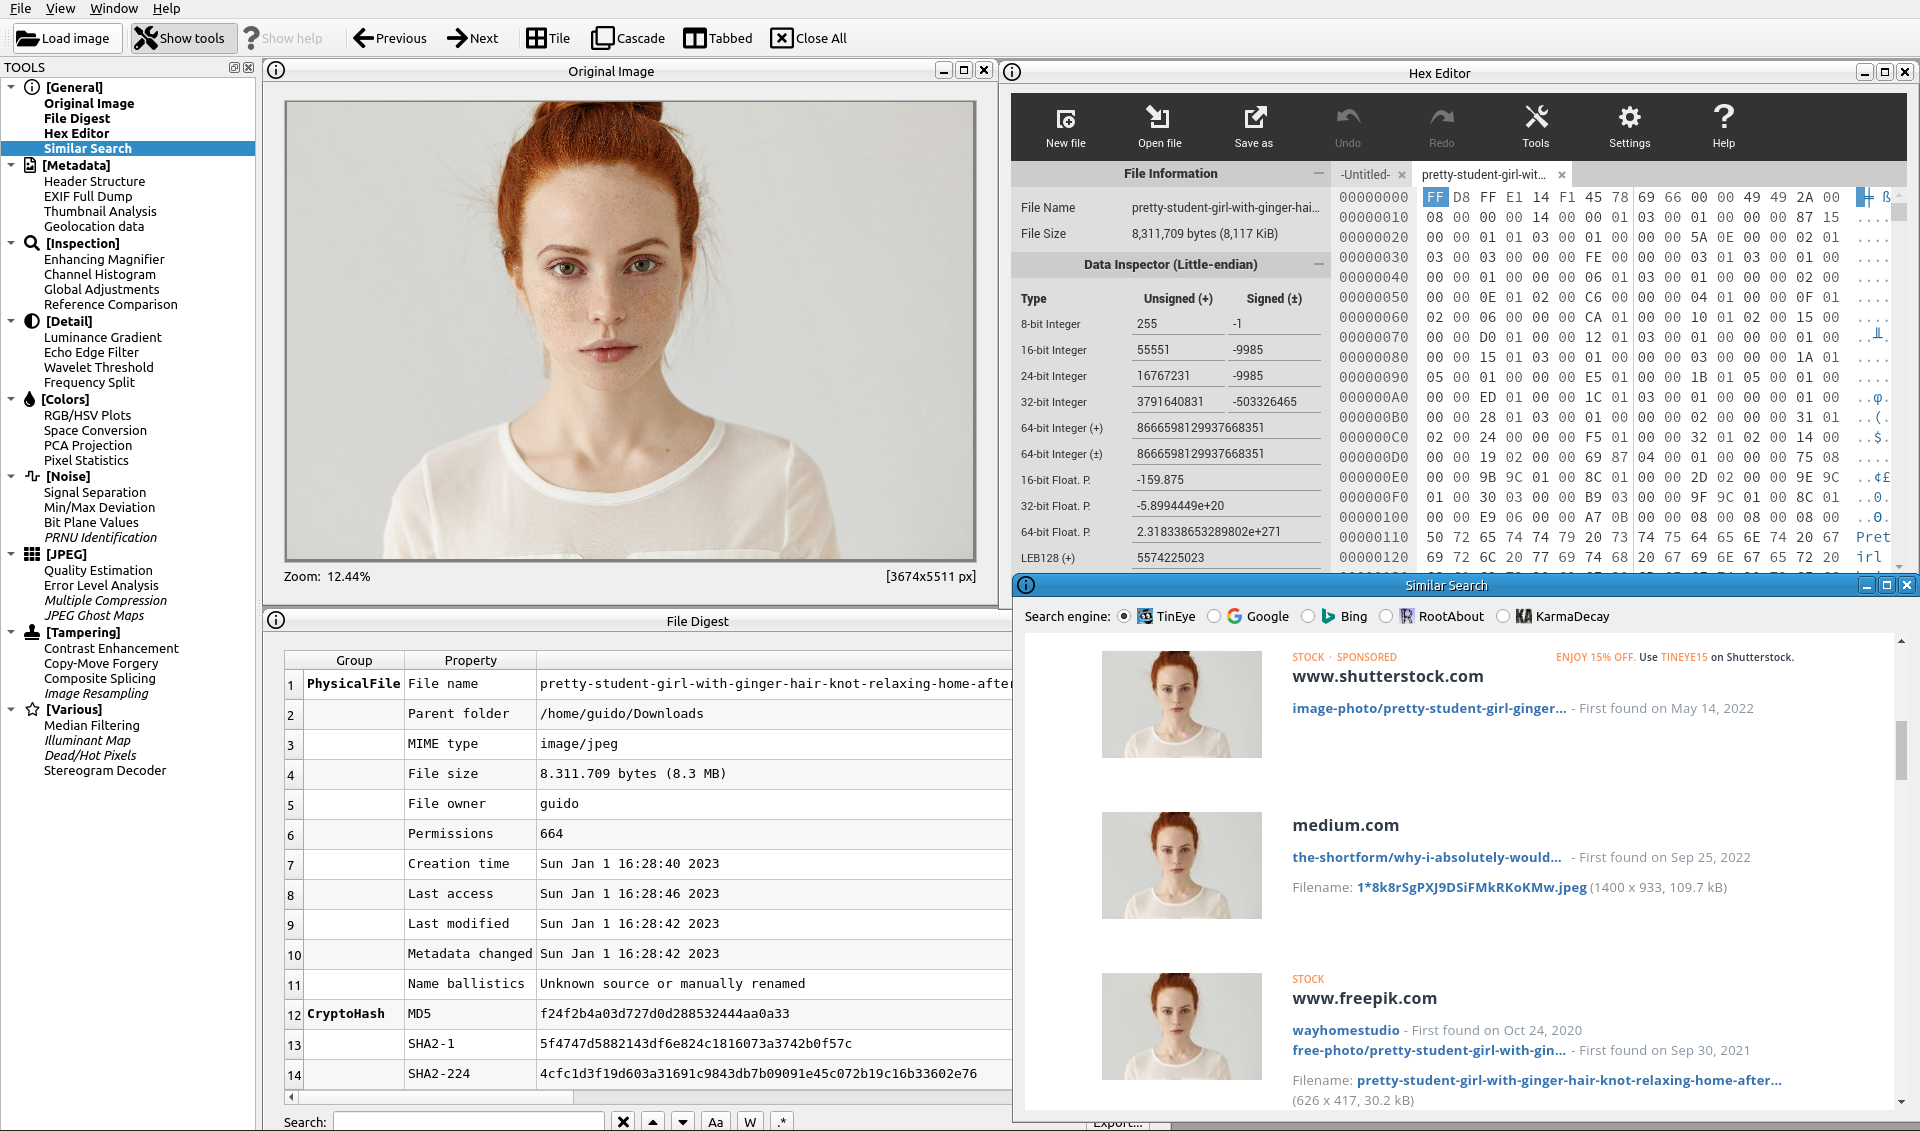
Reverse engineering analysis of DarkTortilla RAT, a sophisticated malware that steals credit card data, decrypts browser passwords, and exfiltrates…
command-and-controldata-exfiltrationdigital-forensics+4
491 month ago
sherloq preview

sherloq

GitHubguidobartoli/sherloq

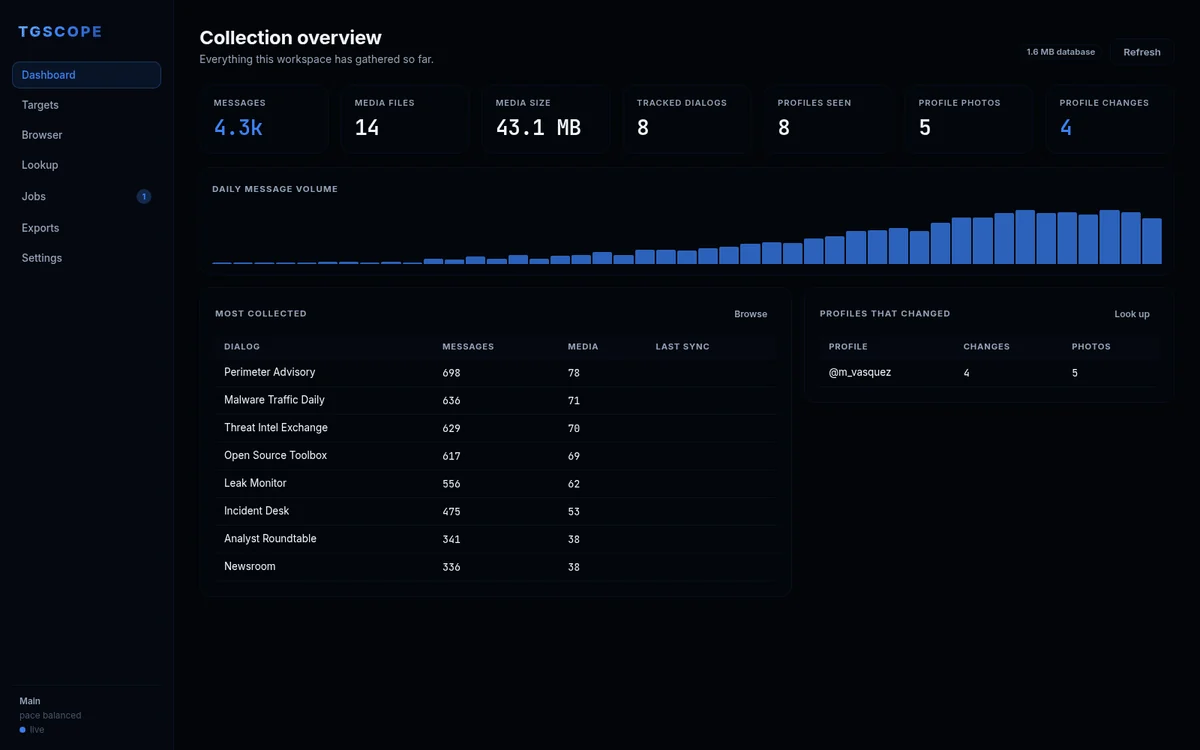
An open-source digital image forensic toolset
cryptographydigital-forensicseducation+4
3.2k3 months ago
tgscope preview

tgscope

GitHubitsmoorgrove/tgscope

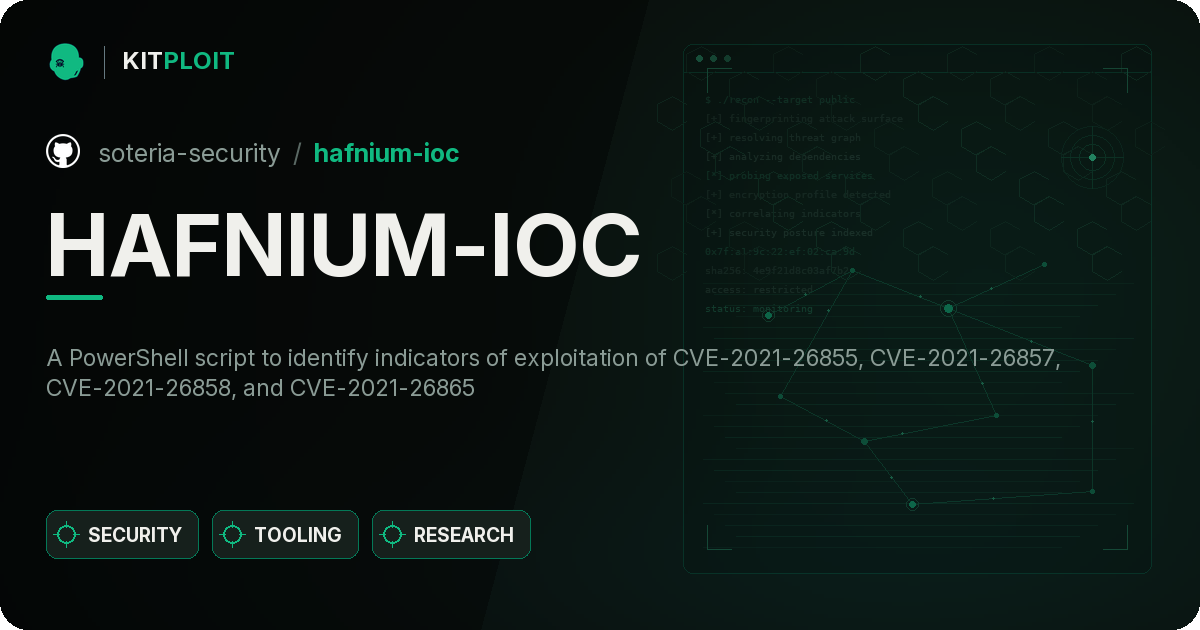
Telegram OSINT, scraping and archival as a local web app. Multi-account collection, profile lookup with historic photos and change diffs, ten export…
crawlerdigital-forensicsinformation-gathering+1
2 months ago
HAFNIUM-IOC preview
Archived

HAFNIUM-IOC

GitHubsoteria-security/hafnium-ioc

A PowerShell script to identify indicators of exploitation of CVE-2021-26855, CVE-2021-26857, CVE-2021-26858, and CVE-2021-26865
digital-forensicsforensicsincident-response+3
225 years ago
ics-forensics-tools preview

ics-forensics-tools

GitHubmicrosoft/ics-forensics-tools

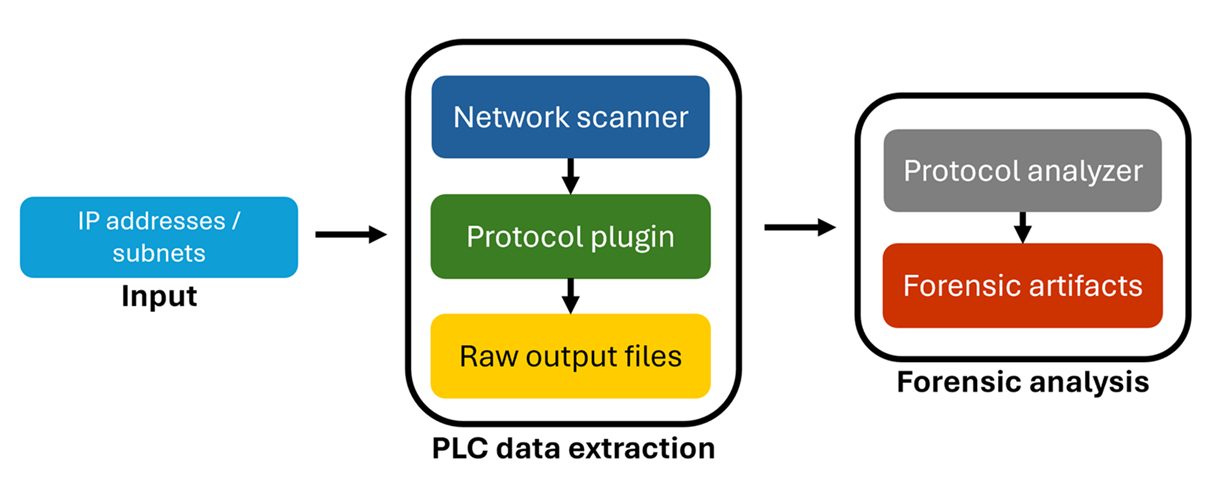
Open-source forensics framework for analyzing Industrial PLC metadata and project files. Scans for suspicious artifacts in ICS environments to…

digital-forensicsforensicsincident-response+2
3751 year ago
volatility3 preview

volatility3

GitHubvolatilityfoundation/volatility3

Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…

digital-forensicsforensicsincident-response+2
4.6k19 days ago
DFIR-LABS preview

DFIR-LABS

GitHubazr43lkn1ght/dfir-labs

Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…

ctfdigital-forensicsdisk-forensics+6
6661 month ago
Previous12…8Next