
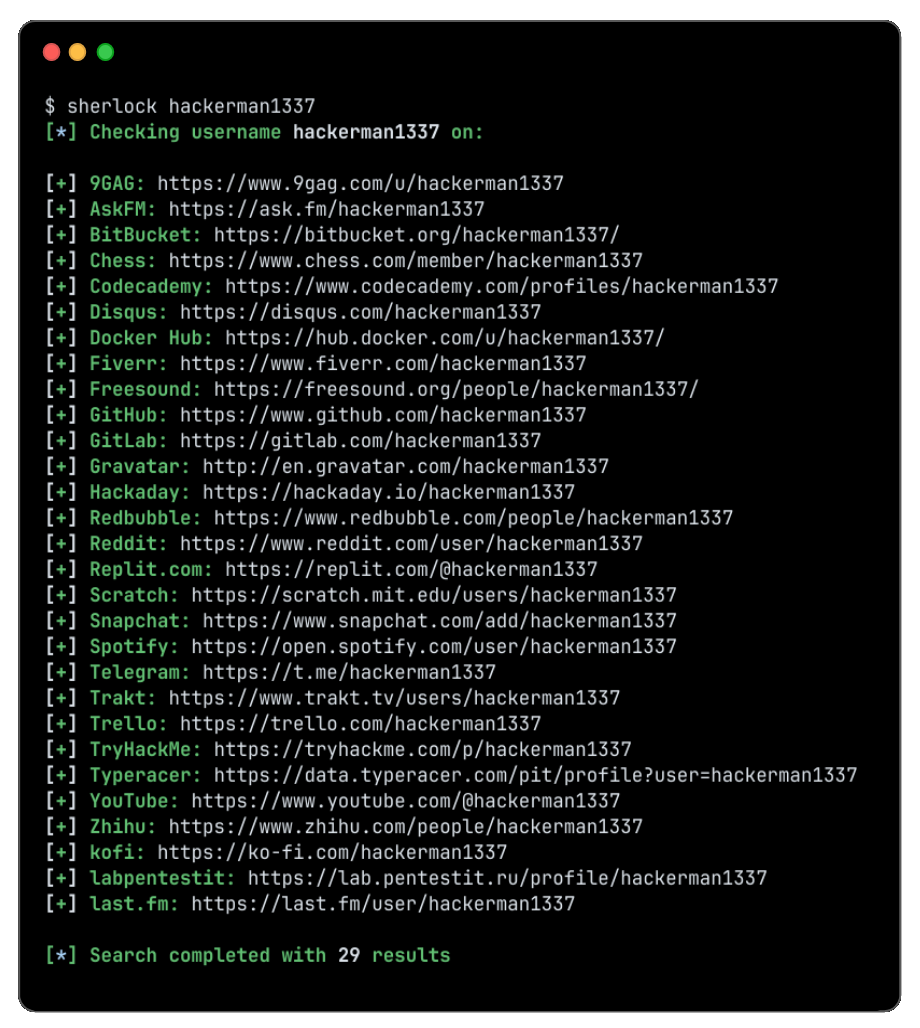
sherlock
 sherlock-project/sherlock
Hunt down social media accounts by username across social networks
digital-forensicsemail-harvestingforensics+11
93.3k10 days ago
sherlock-project/sherlockHunt down social media accounts by username across social networks
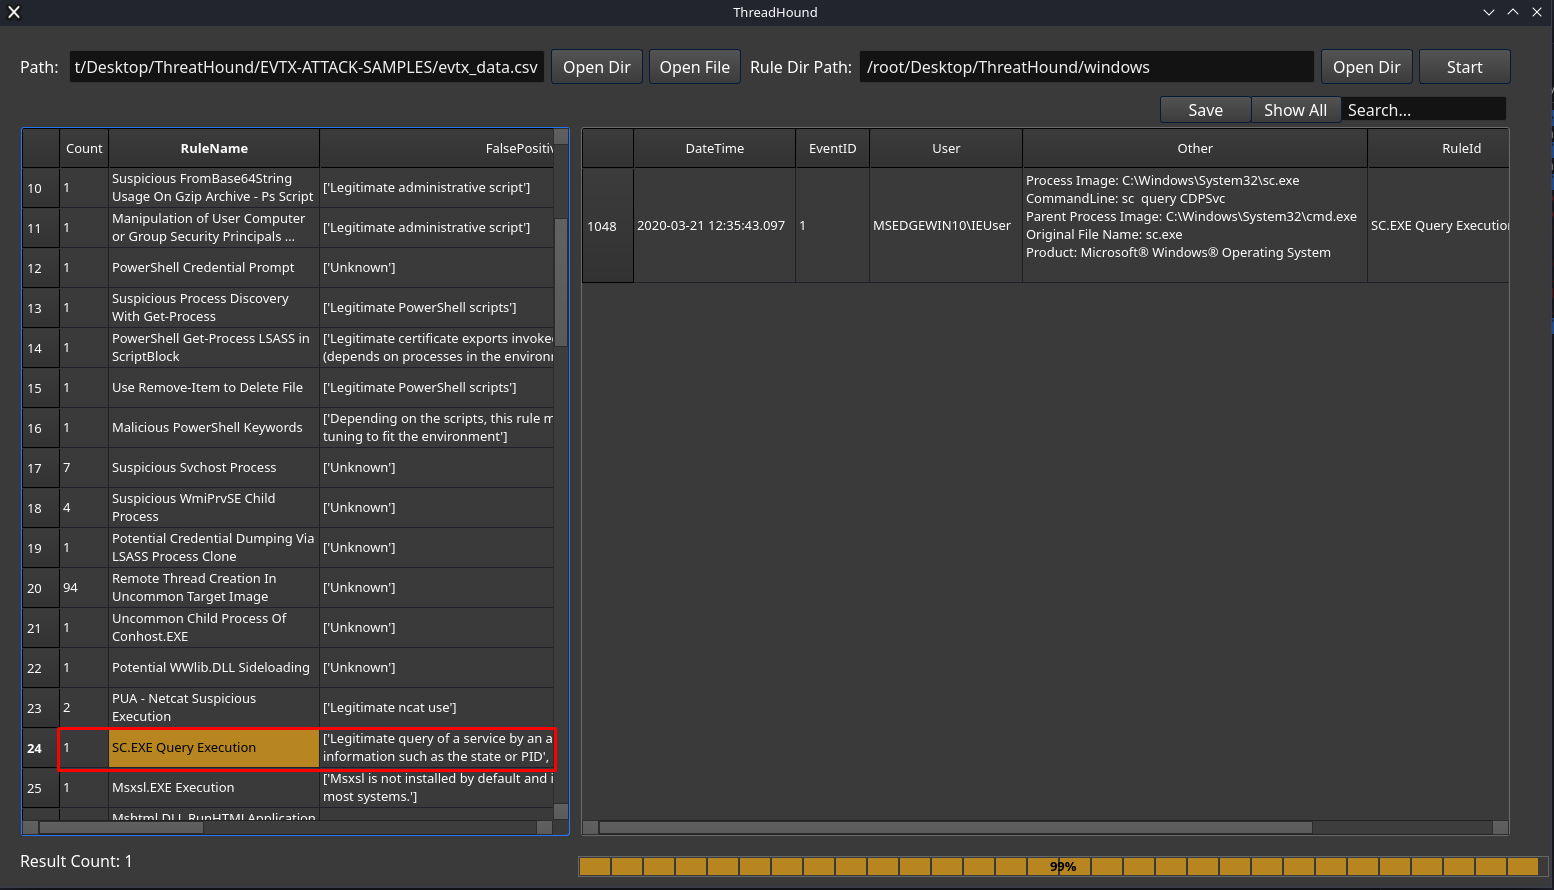 mazx0p/threathound
Automated threat hunting and incident response tool for Windows Event Logs with Sigma rule integration, real-time detection, and forensic artifact…
 wiltodelta/remove-ai-watermarks
Remove visible and invisible AI watermarks and provenance metadata from images and video. Python library and CLI for SynthID, C2PA, EXIF, IPTC, XMP,…
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…

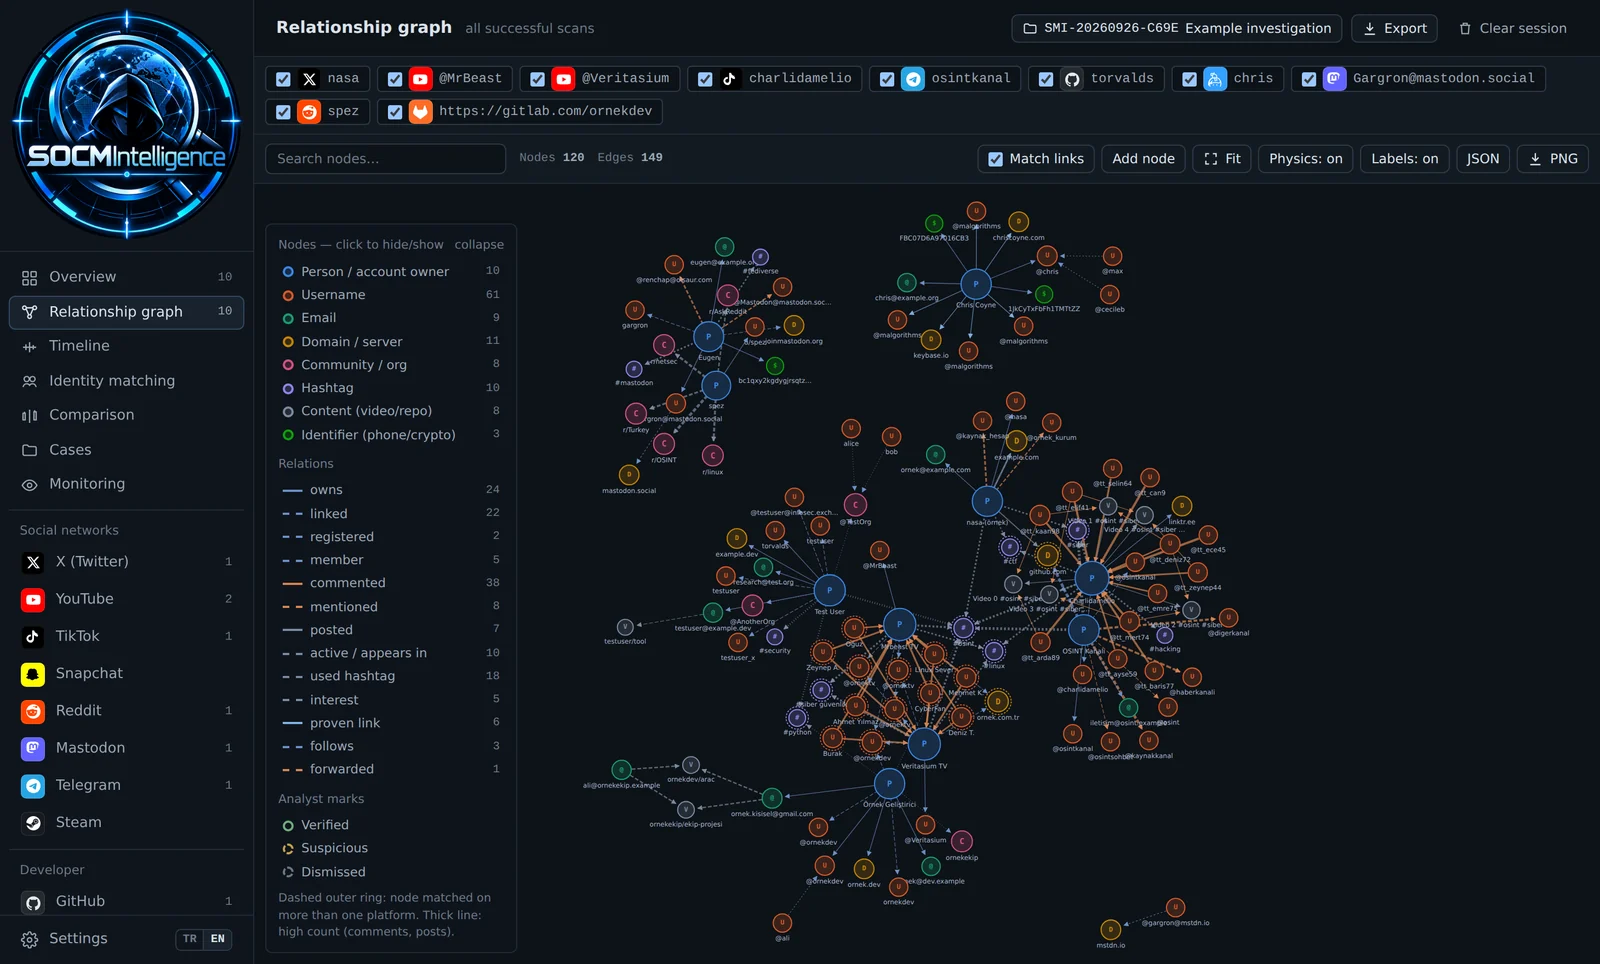 emrekybs/socmintelligence
A modular OSINT & SOCMINT framework for social media intelligence, investigation, and public data analysis.
 idiom/pftriage
Python tool and library to help analyze files during malware triage and analysis.
 usarmyresearchlab/dshell
Dshell is a network forensic analysis framework.
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
 jpcertcc/logontracer
Investigate malicious Windows logon by visualizing and analyzing Windows event log
 microsoft/etl2pcapng
Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.
 guillaumemeyer/watermarks-remover
A privacy-first app that strips AI watermarks from content you own.
 nmatt0/moria
IoT firmware identification and extraction
 hasamba/dfir-companion
DFIR forensics companion server + capture extension
 withsecureopensource/chainsaw
Rapidly Search and Hunt through Windows Forensic Artefacts