
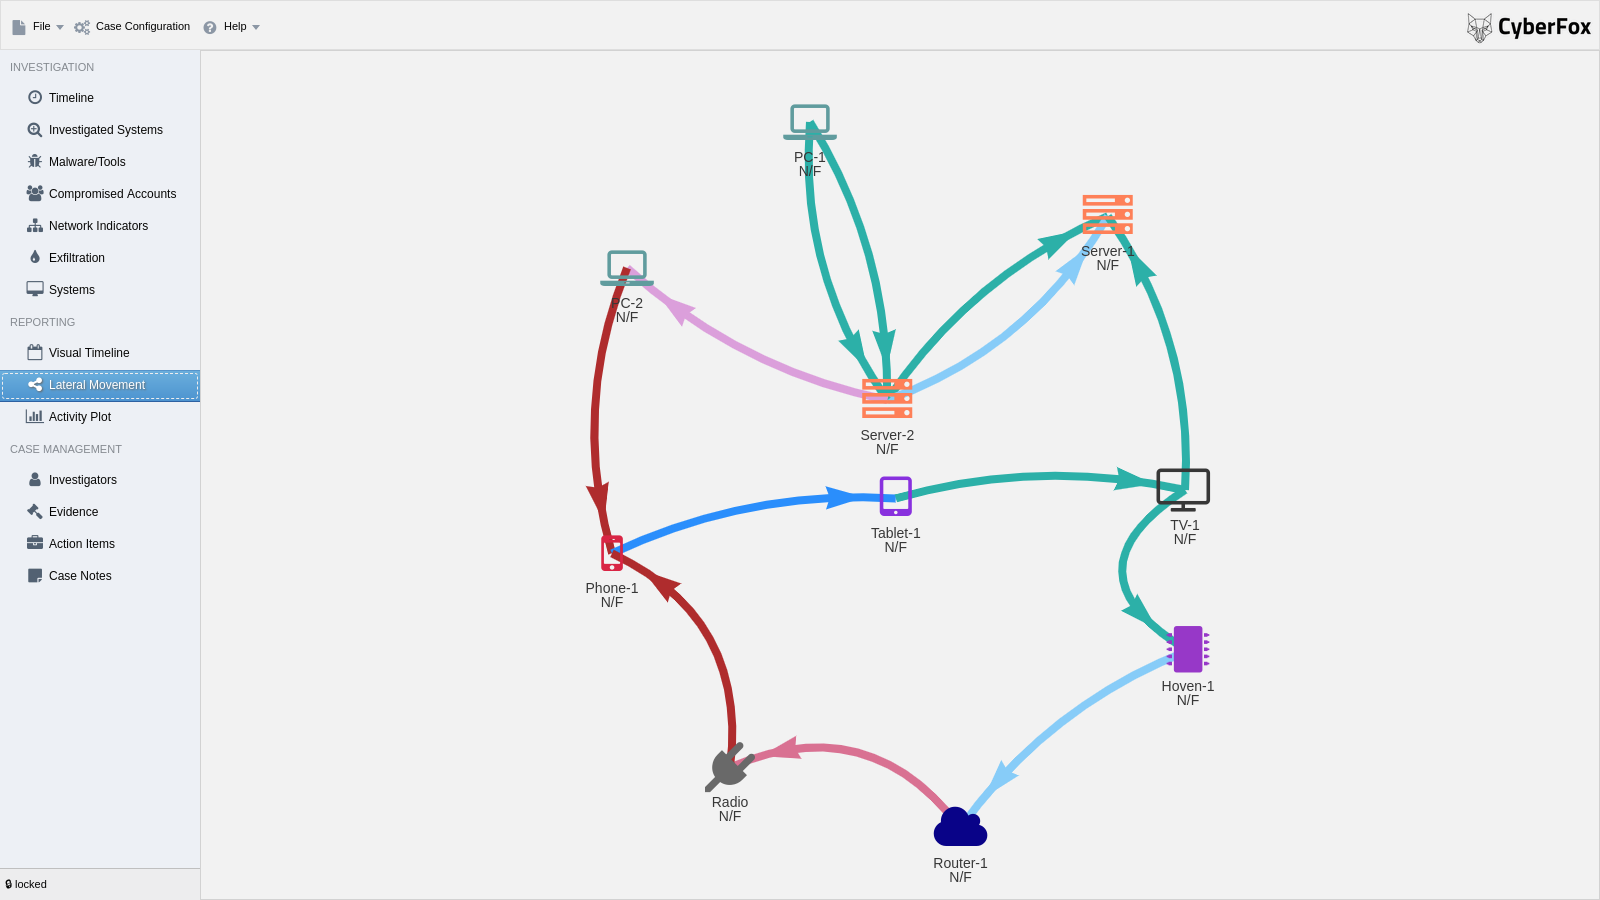
Aurora-Incident-Response
 cyb3rfox/aurora-incident-response
Incident Response Documentation made easy. Developed by Incident Responders for Incident Responders
digital-forensicsforensicsincident-response+3
1.1k
cyb3rfox/aurora-incident-responseIncident Response Documentation made easy. Developed by Incident Responders for Incident Responders
 circl/factual-rules-generator
Generates YARA rules from installed software on a running OS to baseline known software and find similar installations across digital forensic…
 ab2pentest/macosthreattrack
Bash tool used for proactive detection of malicious activity on macOS systems.
 busindre/dumpzilla
Extract all forensic interesting information of Firefox, Iceweasel and Seamonkey browsers
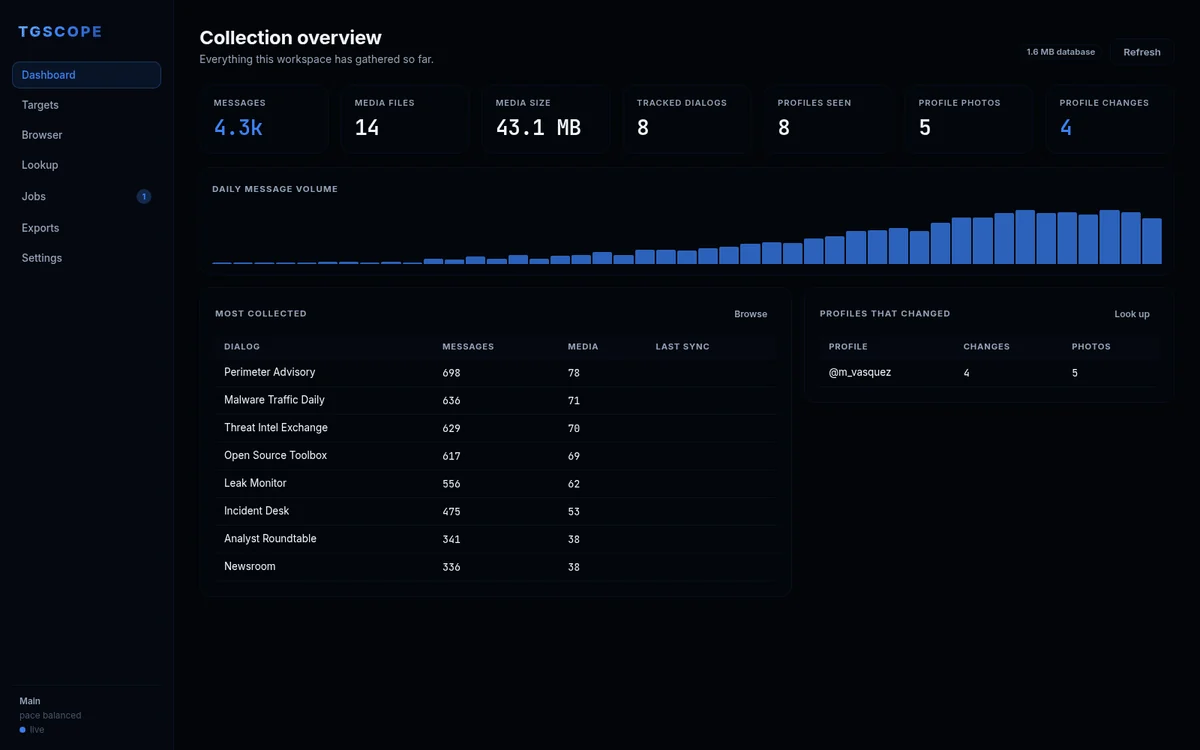 itsmoorgrove/tgscope
Telegram OSINT, scraping and archival as a local web app. Multi-account collection, profile lookup with historic photos and change diffs, ten export…
 adrecon/adrecon
PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
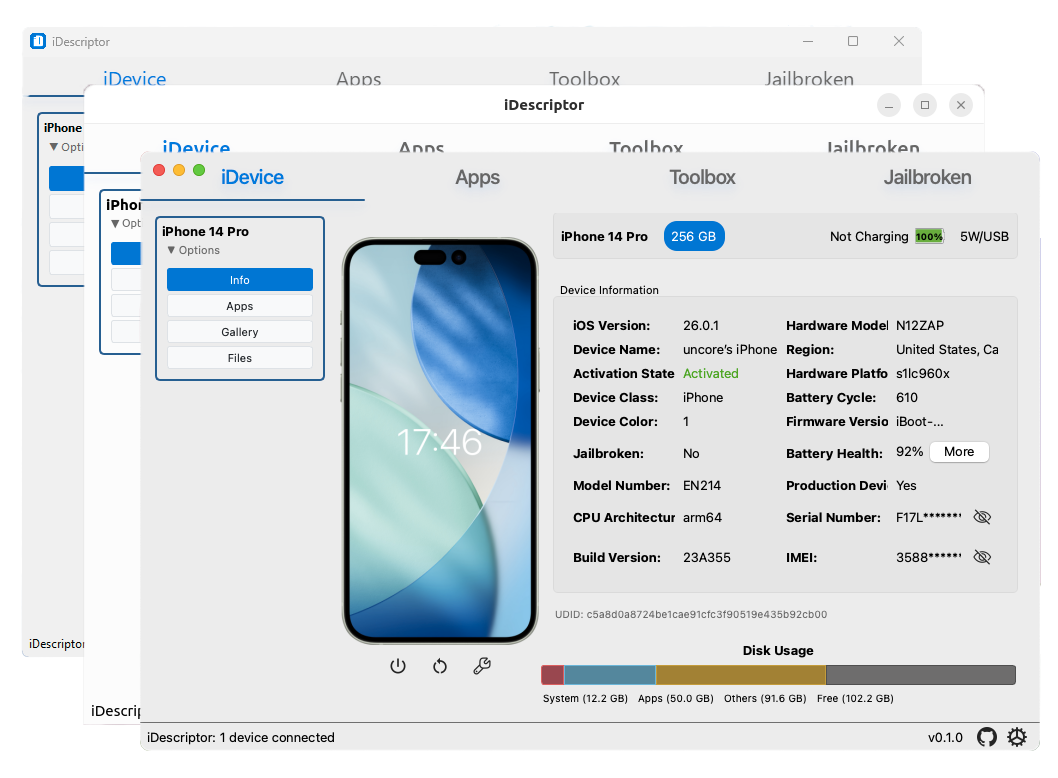 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
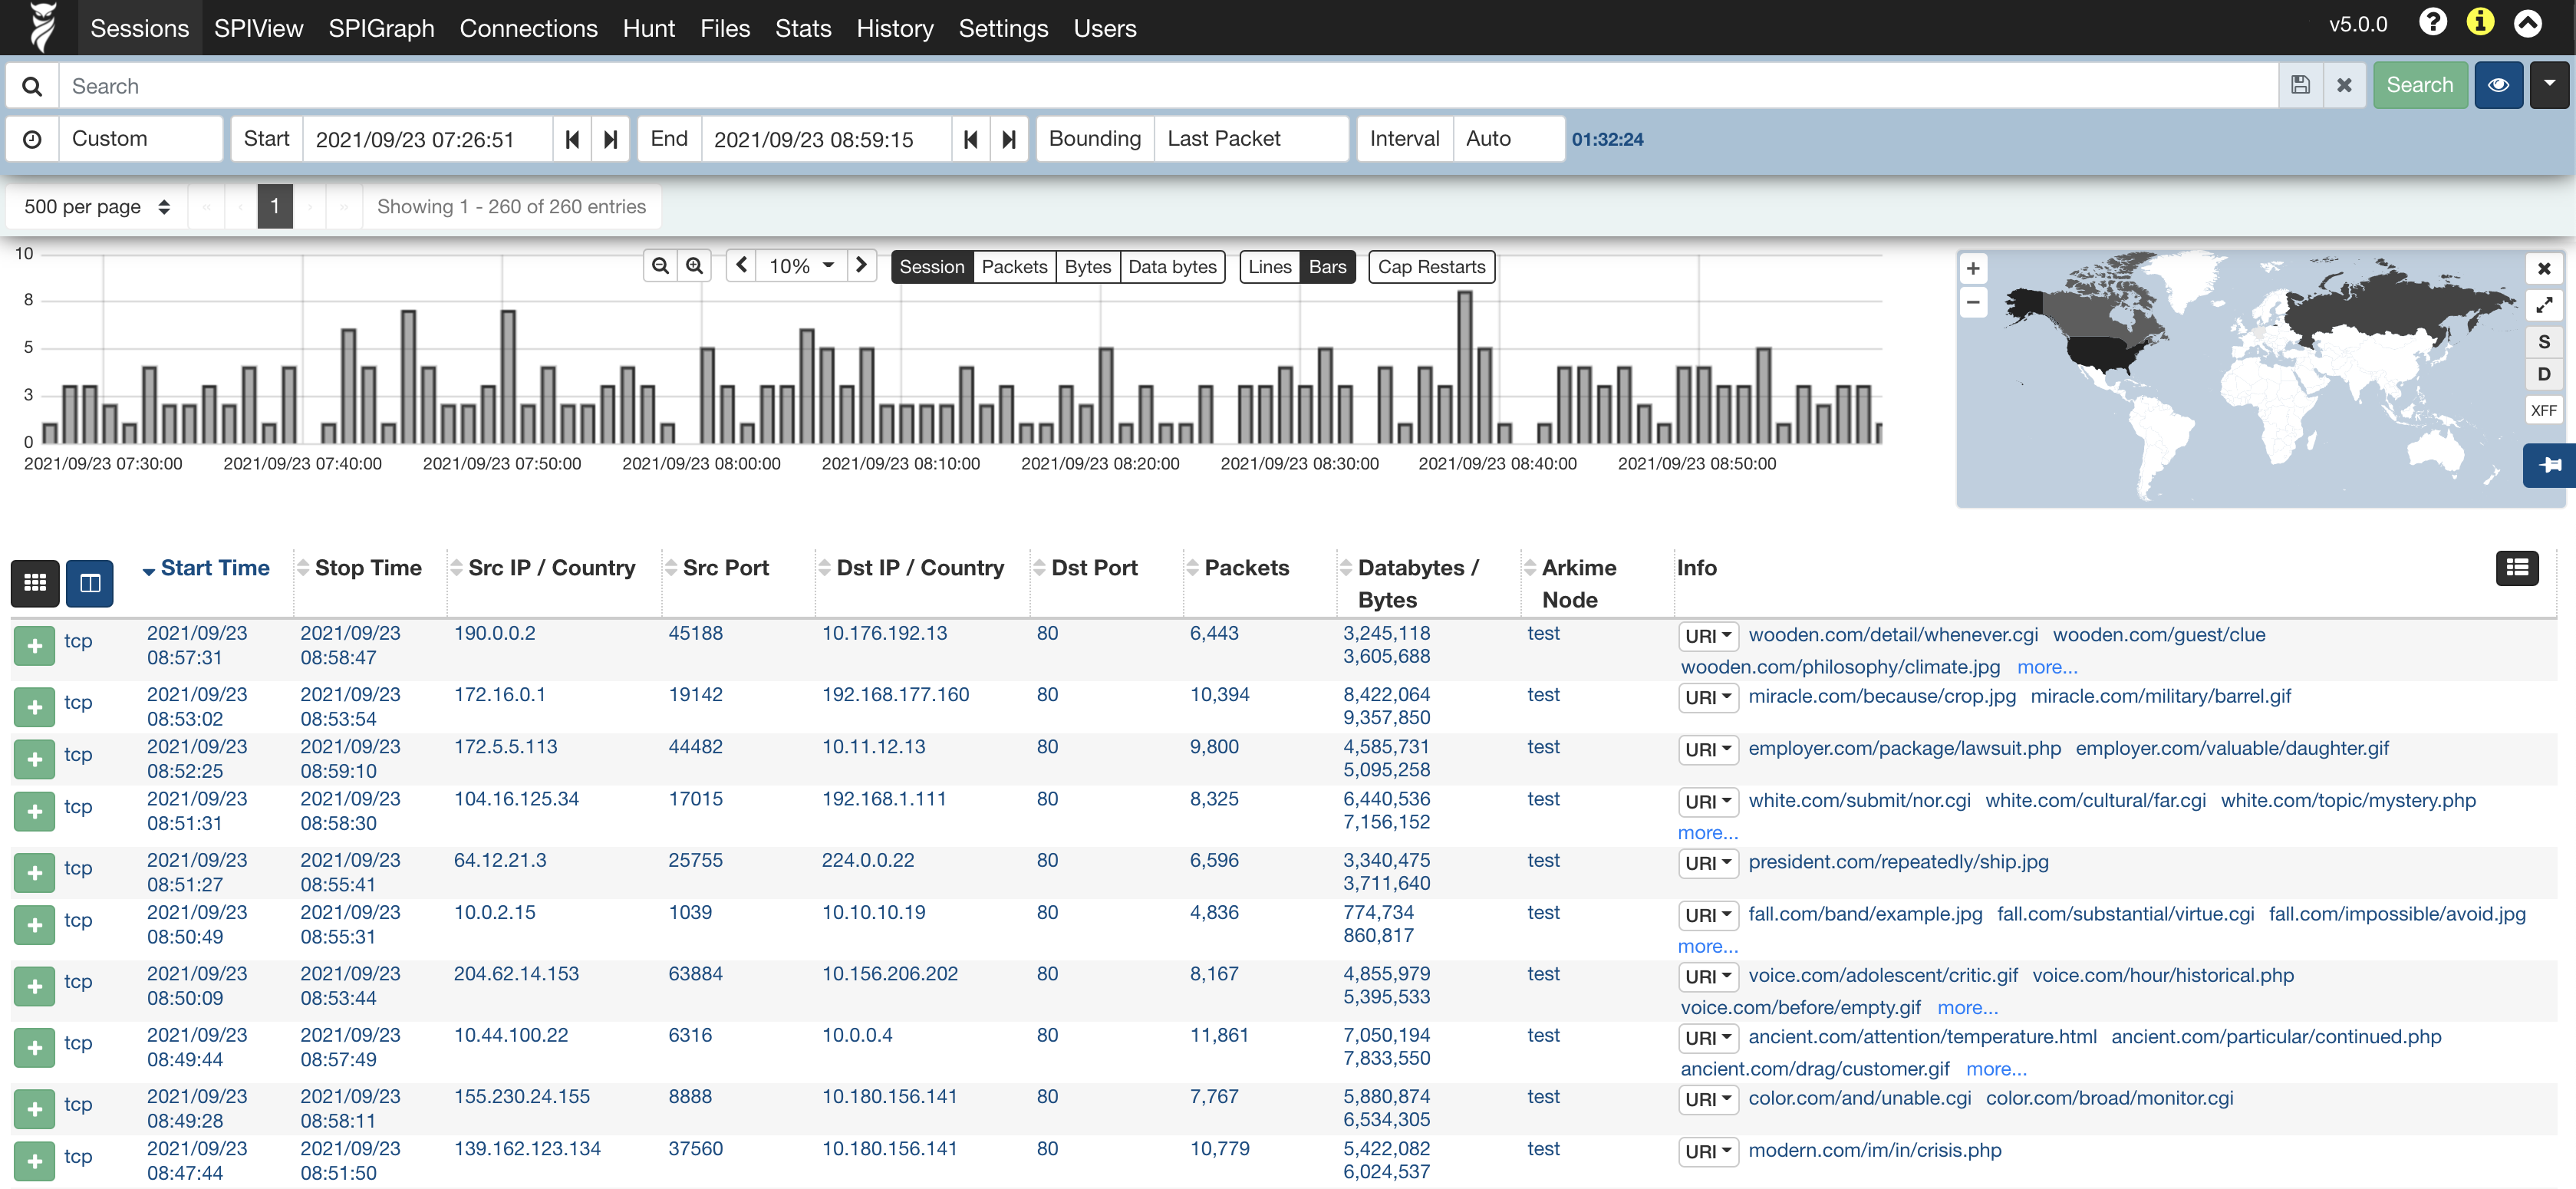 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
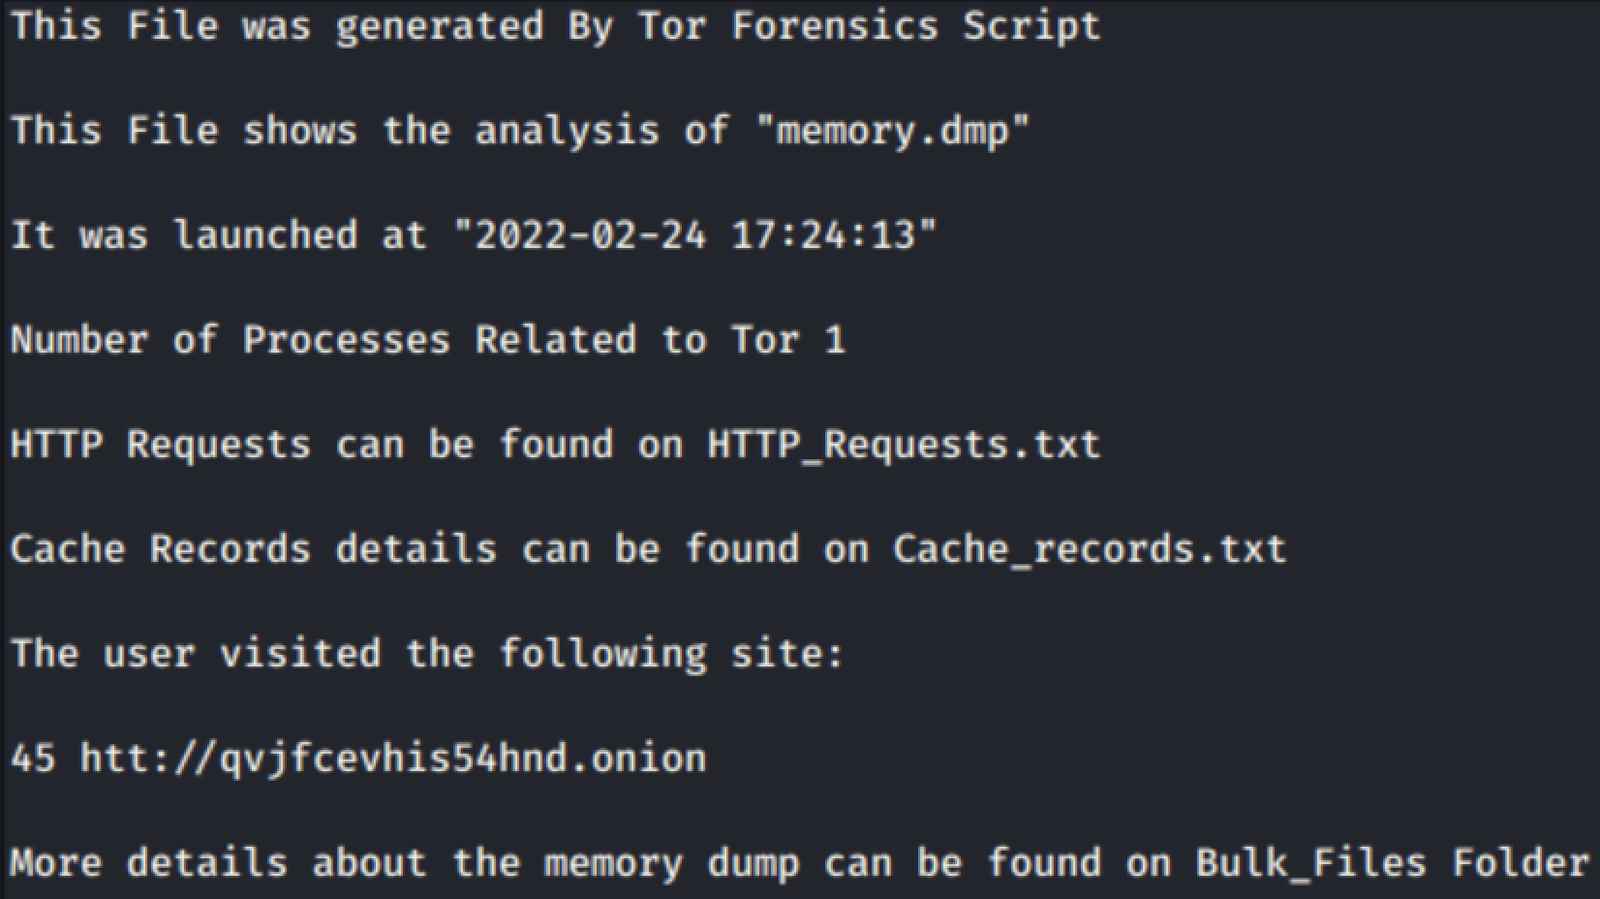 exmak-s/cve-2021-46702
Proof-of-concept script that analyzes Windows memory dumps to recover visited Tor onion services, bypassing Tor Browser's anonymity by exploiting…
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
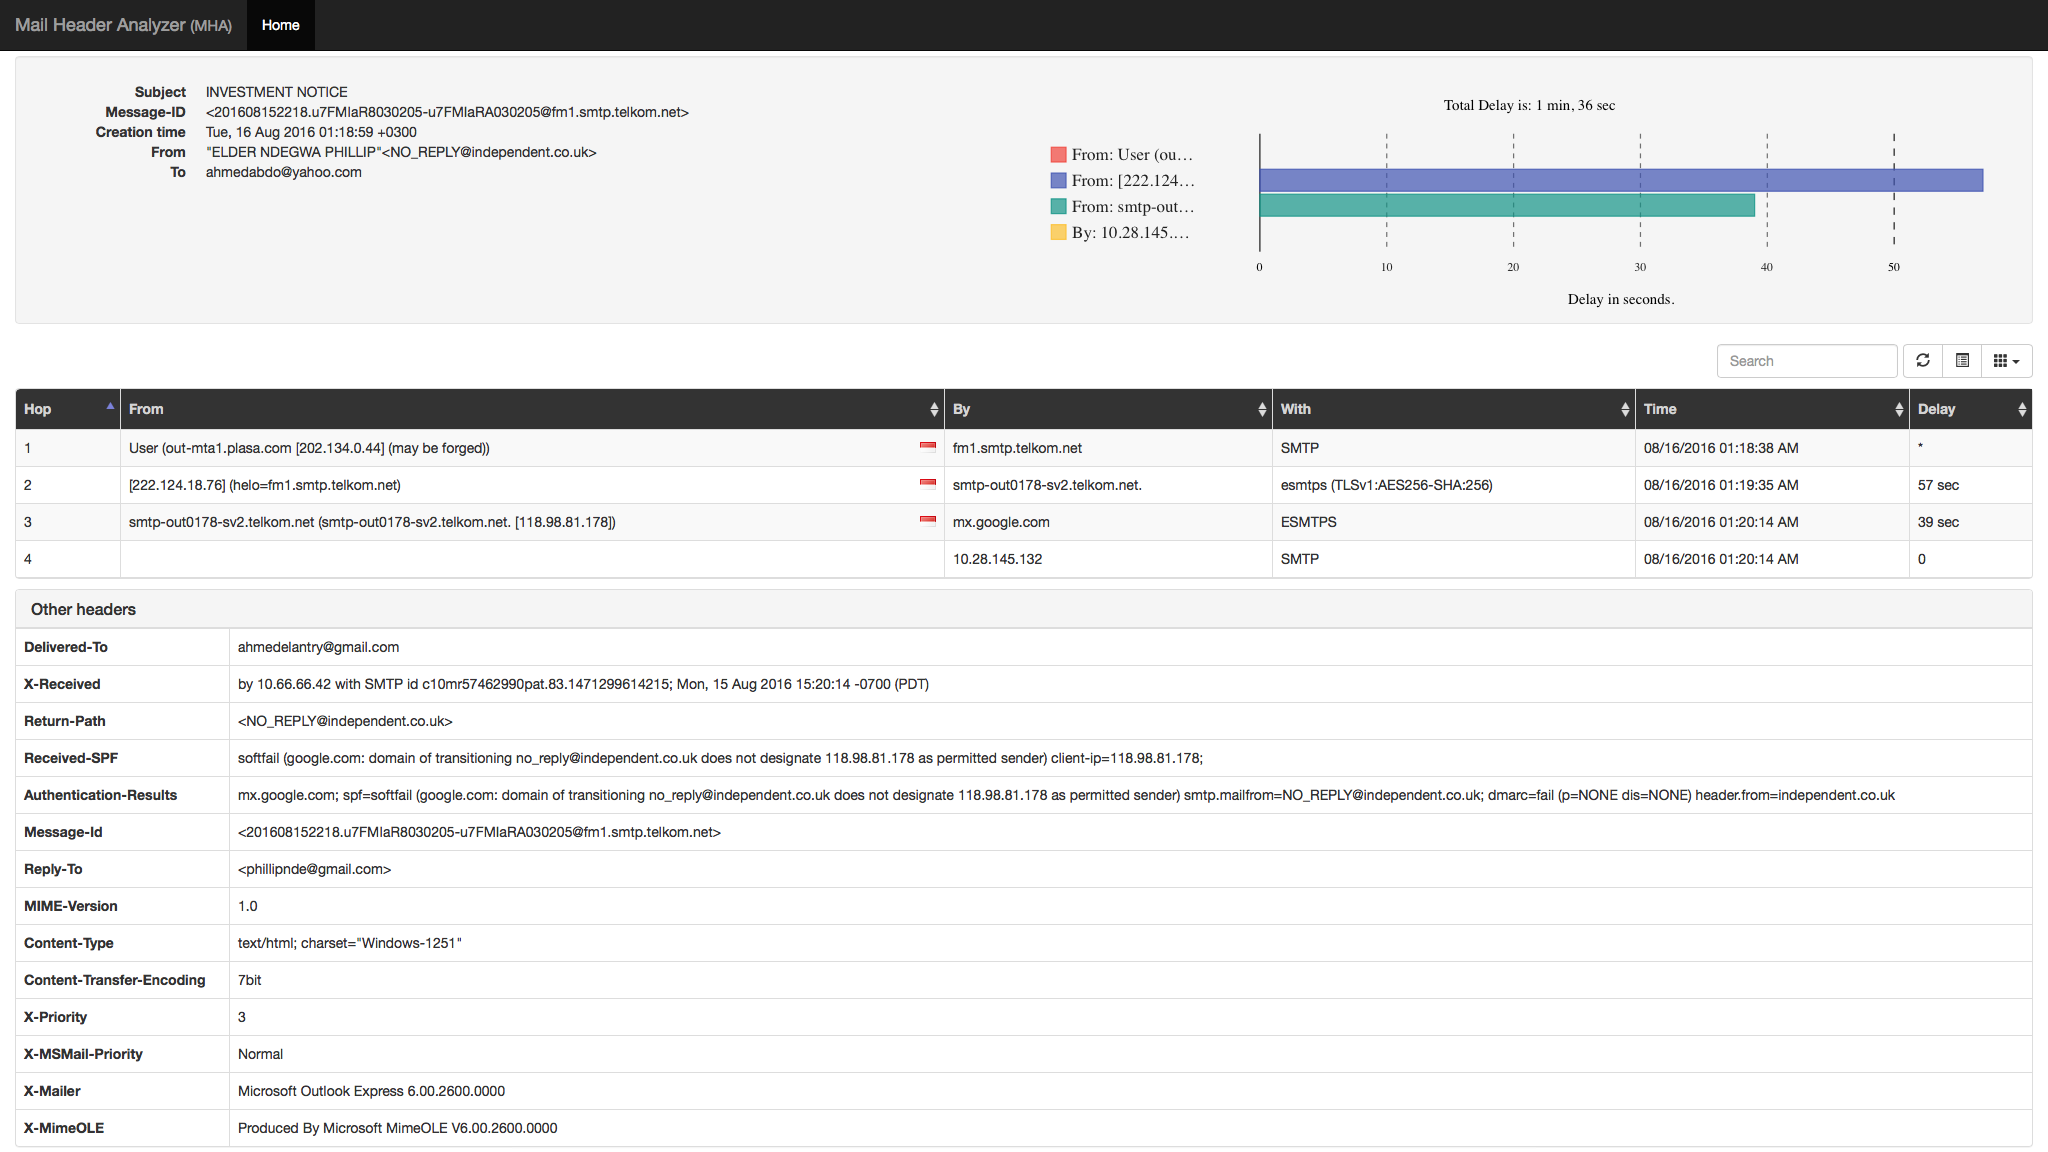 cyberdefenders/email-header-analyzer
E-Mail Header Analyzer
 redaelli/imago-forensics
Imago is a python tool that extract digital evidences from images.
 mr-r3b00t/crime-mapper
A tool for mapping cyber crime
 ssrajadh/sentrysearch
Semantic search over videos using Gemini Embedding 2 or Qwen3-VL.
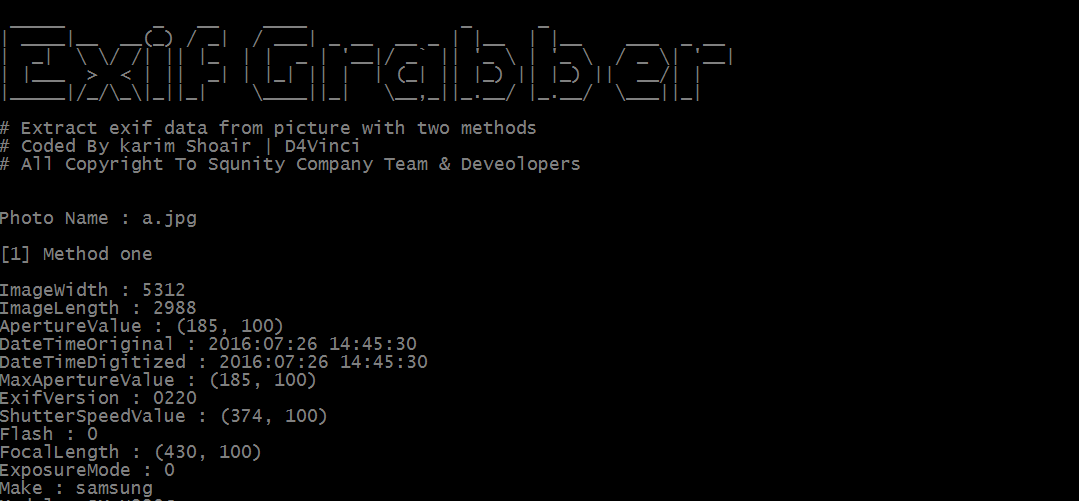 d4vinci/exif-grabber
A python tool that will extract exif data from picture with two methods
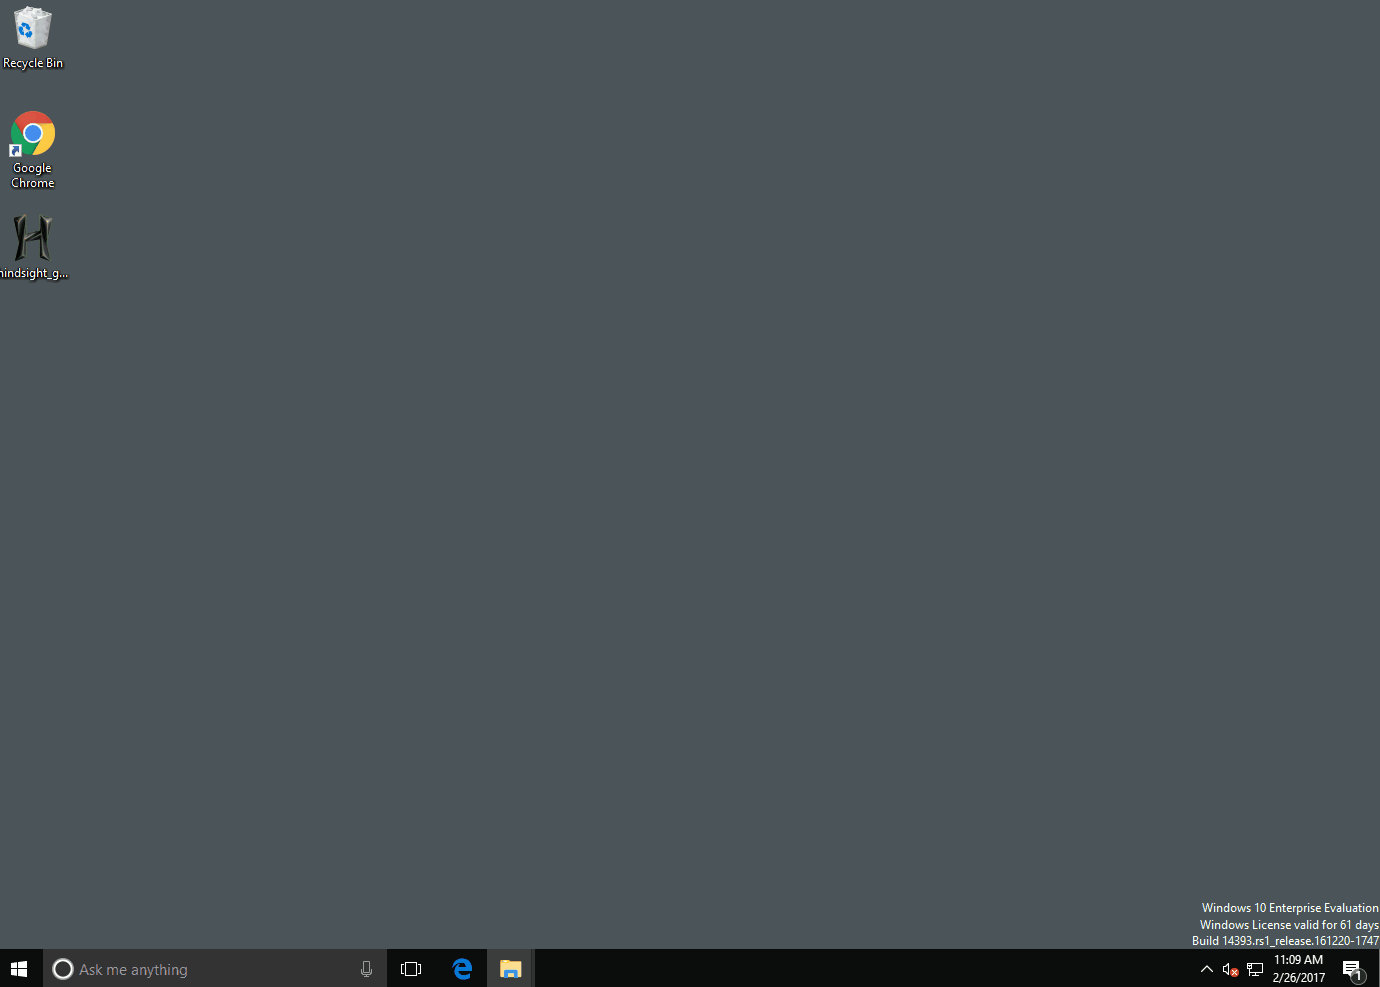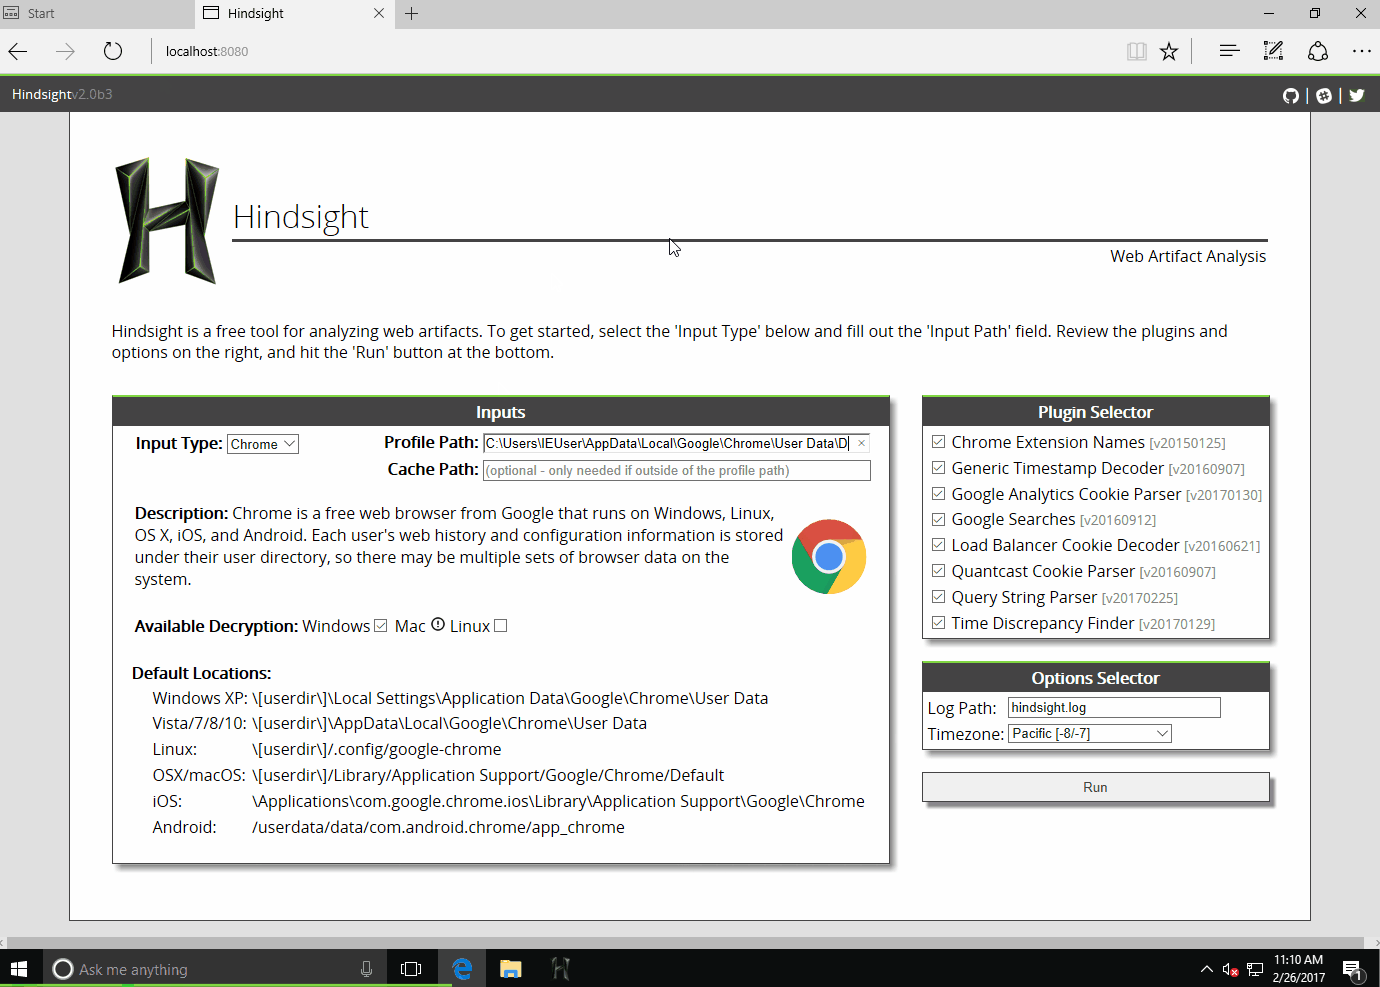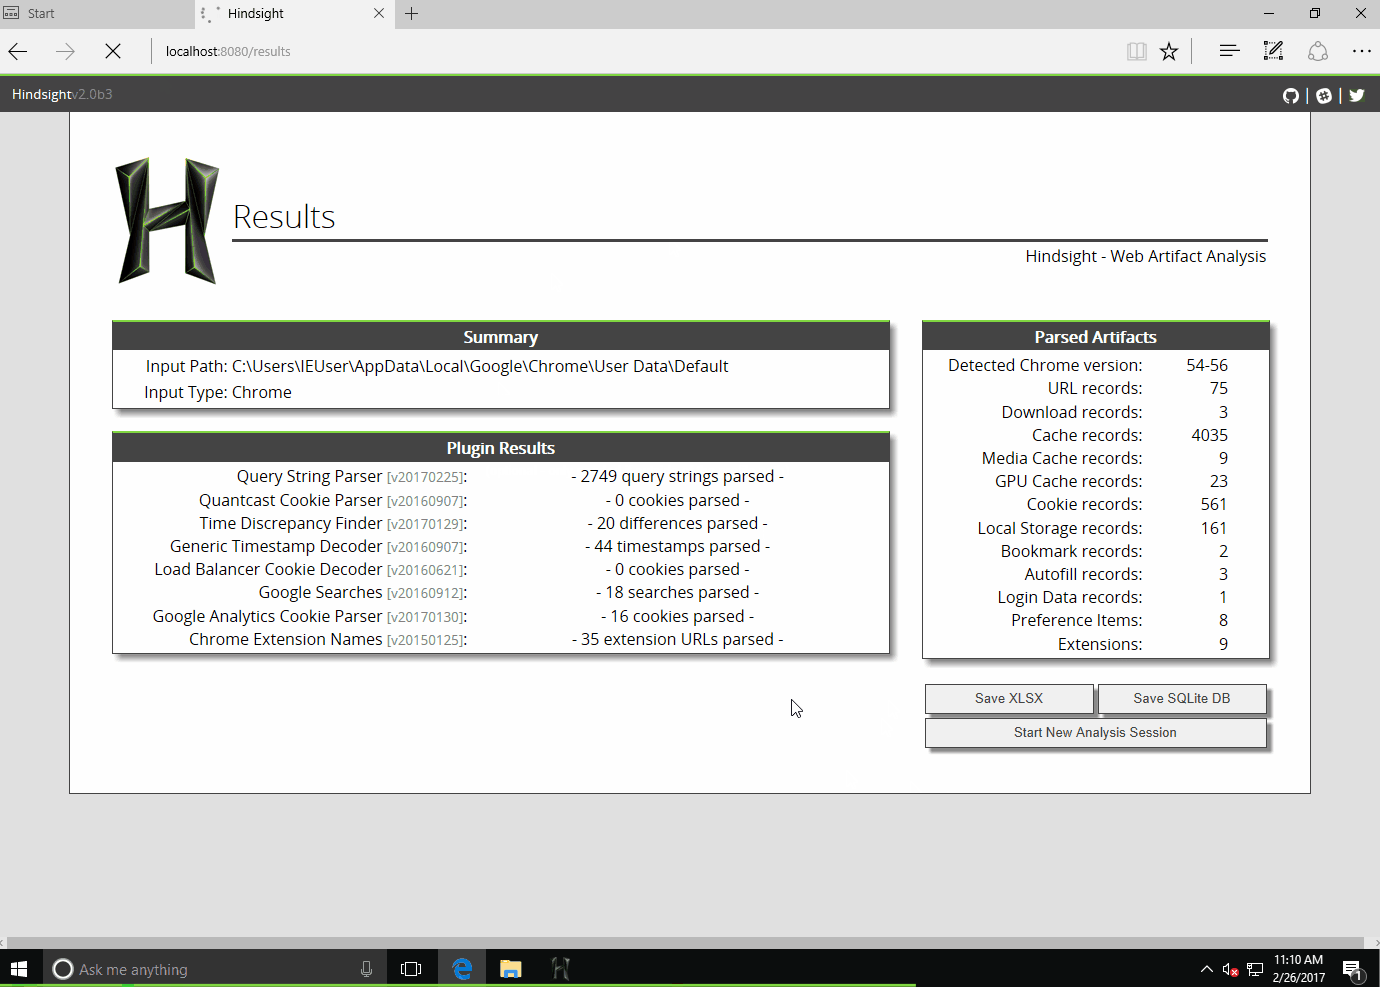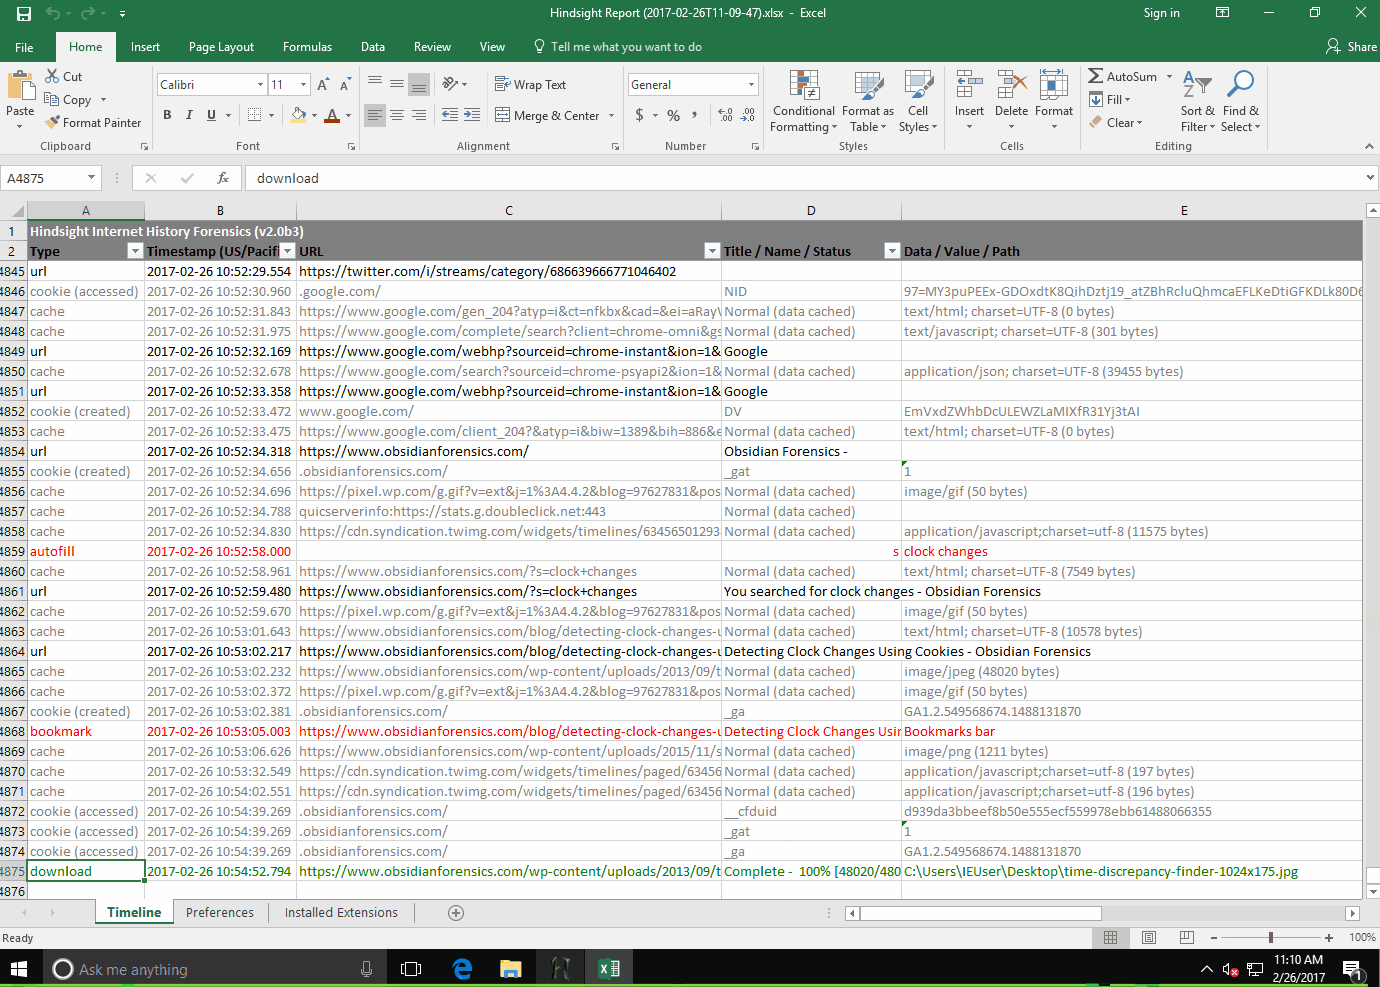 ryandfir/hindsight
Browser forensics tool for Google Chrome, other Chromium-based browsers, and Mozilla Firefox