
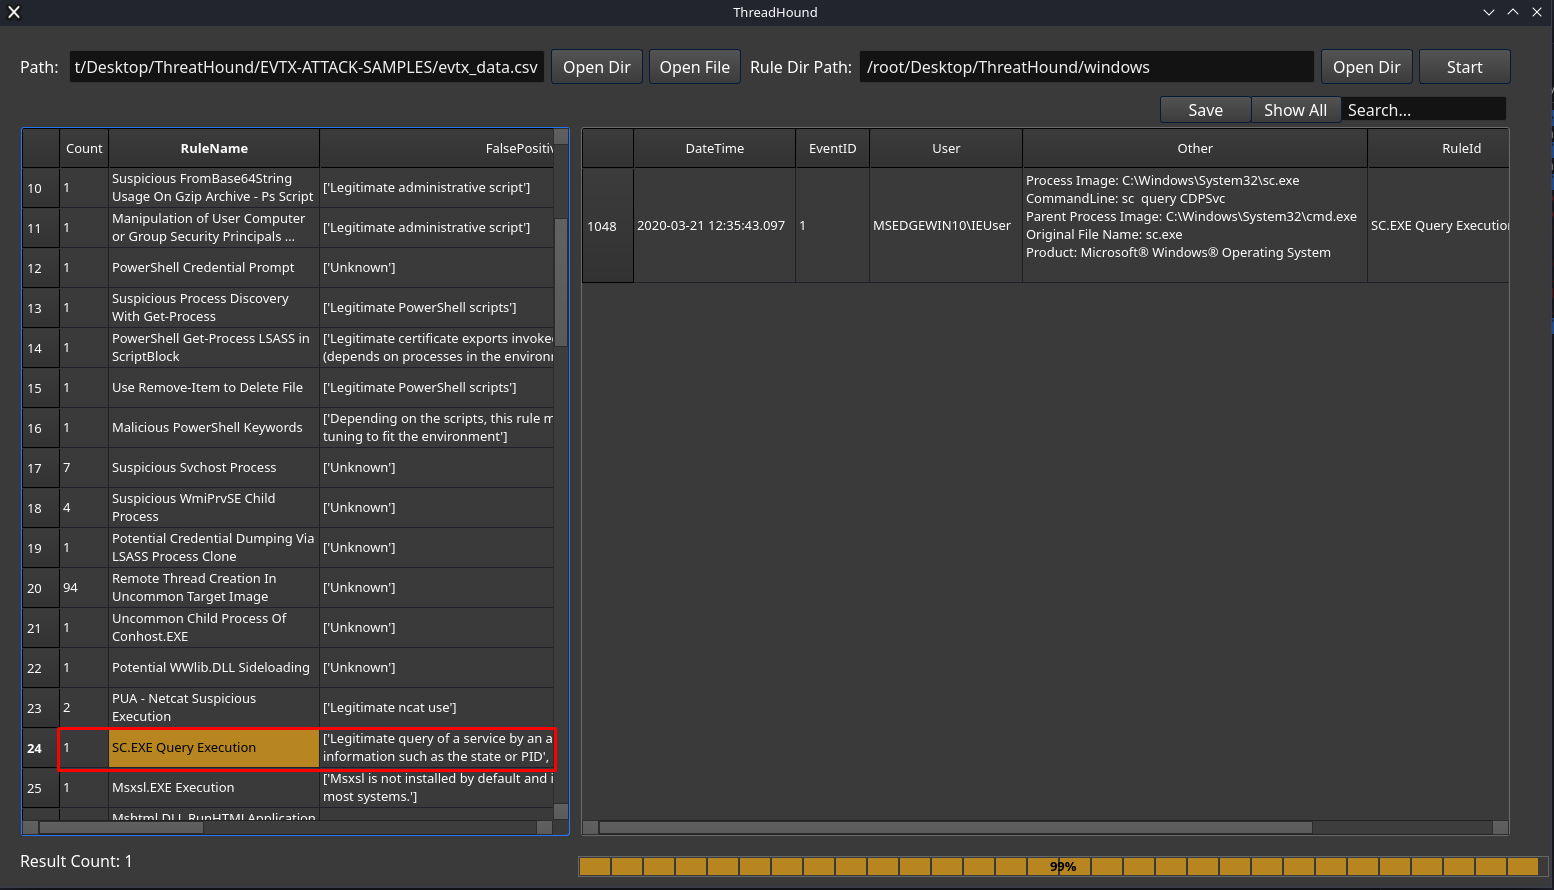
ThreatHound
 mazx0p/threathound
Automated threat hunting and incident response tool for Windows Event Logs with Sigma rule integration, real-time detection, and forensic artifact…
digital-forensicsincident-responselog-analysis+1
158
mazx0p/threathoundAutomated threat hunting and incident response tool for Windows Event Logs with Sigma rule integration, real-time detection, and forensic artifact…
 themittenmac/truetree
A command line tool for pstree-like output on macOS with additional pid capturing capabilities
 yamato-security/hayabusa
Multi-threaded Windows event log forensics timeline generator and threat hunting tool with full Sigma rule support, producing CSV/JSON timelines for…
 guillaumemeyer/watermarks-remover
A privacy-first app that strips AI watermarks from content you own.
 withsecureopensource/chainsaw
Rapidly Search and Hunt through Windows Forensic Artefacts

 cado-security/dfir_resources_revil_kaseya
Resources for DFIR Professionals Responding to the REvil Ransomware Kaseya Supply Chain Attack
 blakebratcher/wcw-cyberring-pav-decryptor
Cryptanalysis of a proprietary 1999 video DRM system. Recovers 61 encrypted wrestling videos from the WCW Internet Powerdisk CD-ROM through static…
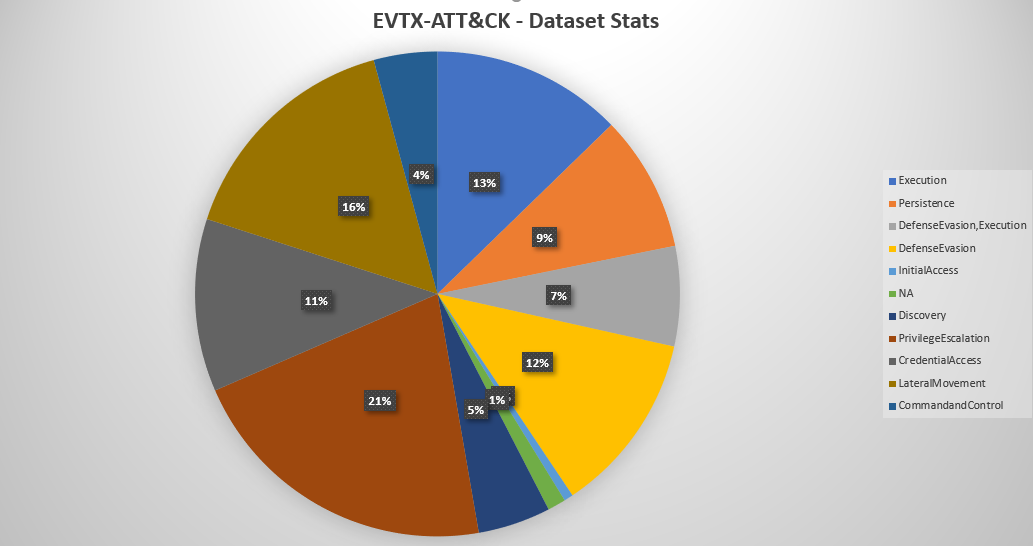 sbousseaden/evtx-attack-samples
Curated collection of Windows EVTX attack samples mapped to MITRE ATT&CK techniques, designed for testing detection scripts, DFIR training, and…
 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
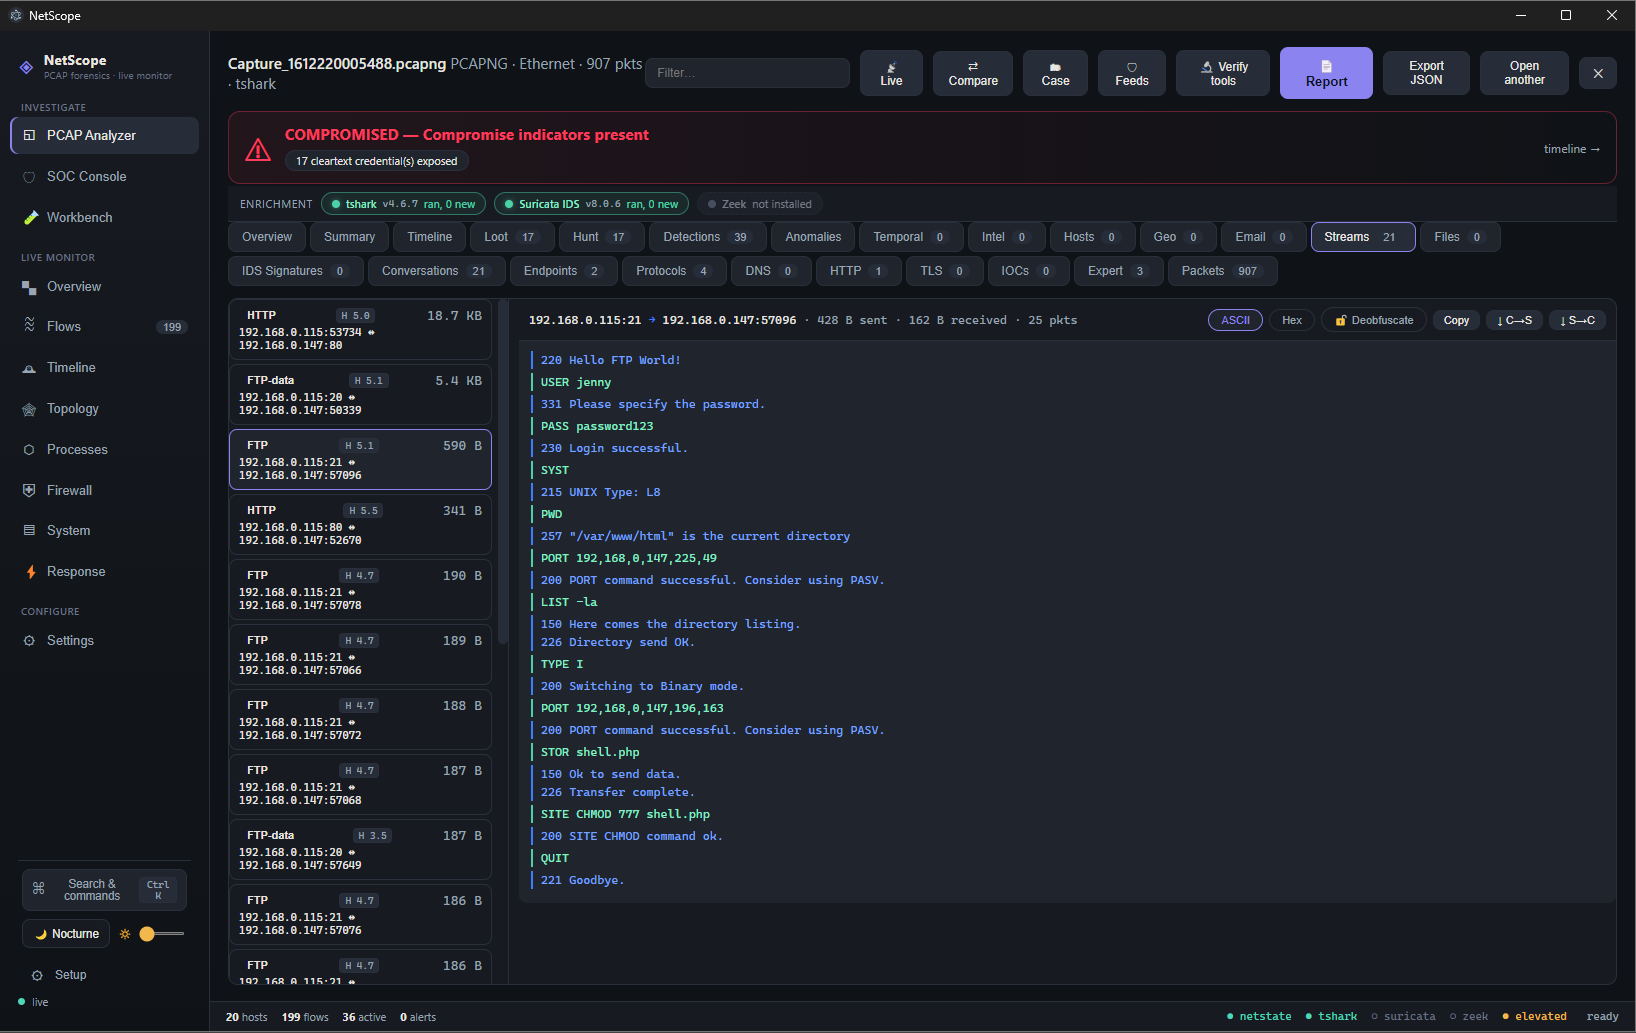 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
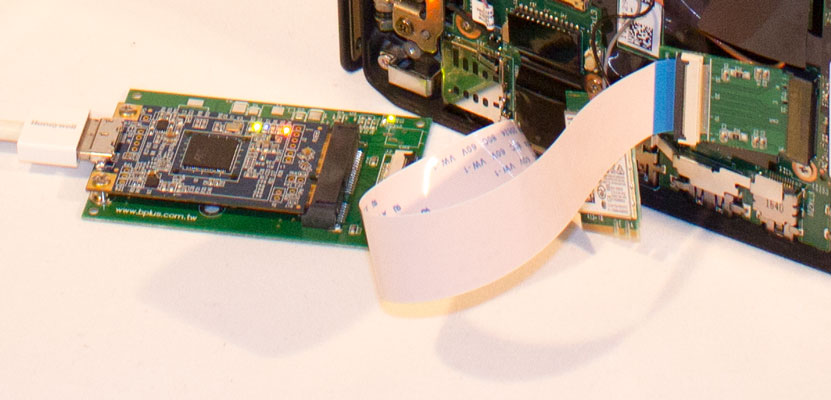 ufrisk/pcileech
Direct Memory Access (DMA) Attack Software
 mitre/brawl-public-game-001
Data from a BRAWL Automated Adversary Emulation Exercise
 aloshdenny/reverse-synthid
reverse engineering Gemini's SynthID detection
 disqualifier/psa-2026-00043-recovery
Recovery notes for proxmox advisory ID: PSA-2026-00043-1 (CVE-2023-54391)
 vignesh-hp/lockbit-ransomware-analysis
Threat intelligence and incident response case study on LockBit ransomware exploiting CVE-2023-4966 (Citrix Bleed).
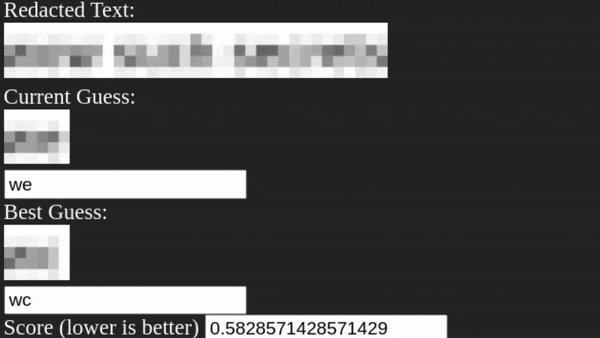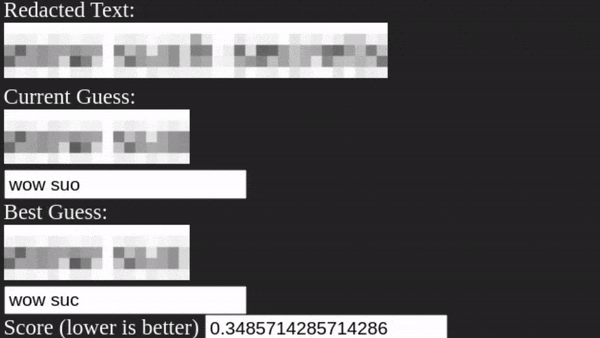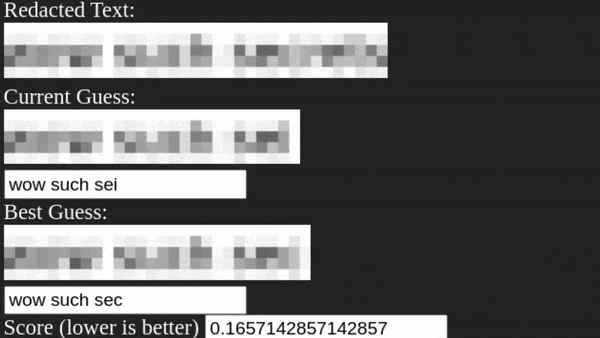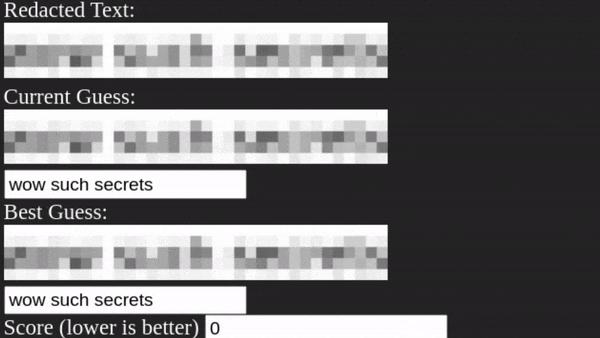 bishopfox/unredacter
Never ever ever use pixelation as a redaction technique
 emalderson/thephish
ThePhish: an automated phishing email analysis tool