

Archived

 iocx-dev/iocx
An extensible, deterministic static‑analysis engine that extracts high‑signal IOCs from PE binaries and text, built for SOC automation and modern…
 gitleaks/gitleaks
Fast, open-source static analysis tool for detecting hardcoded secrets like passwords, API keys, and tokens in git repositories, files, and stdin…
 yelp/detect-secrets
An enterprise friendly way of detecting and preventing secrets in code.
 gitguardian/ggshield
Detect and validate 500+ types of hardcoded secrets with advanced checks. Use it as a pre-commit hook, GitHub Action, or CLI for proactive secret…
 thoughtworks/talisman
Git hook-based secret scanner that detects tokens, passwords, and private keys in outgoing changesets, preventing sensitive data from being committed…
 avito-tech/deepsecrets
Static analysis tool that scans source code for hardcoded secrets, API keys, and credentials using semantic understanding of code context.
 nccgroup/ccs
Regex-based scanner for detecting hard-coded credentials in codebases, designed for CI/CD integration with suppression comment support and low…
 dbzoo/log4j_scanner
Filesystem scanner for Log4Shell (CVE-2021-44228) and related CVEs. Detects vulnerable JAR files via hash matching and class presence. Runs…
 vihaaninnovations/autonoma
Detects and auto-fixes hardcoded secrets in Python repos — refuses when the fix could break your code

 niclas-zone/ci/gitleaks
CI component for Gitleaks SAST tool that scans git repositories for hardcoded secrets, API keys, and tokens with custom and remote configuration…
 aboutcode-org/scancode-toolkit
🔍 ScanCode detects licenses, copyrights, dependencies by "scanning code" ... to discover and inventory open source and third-party packages used in…
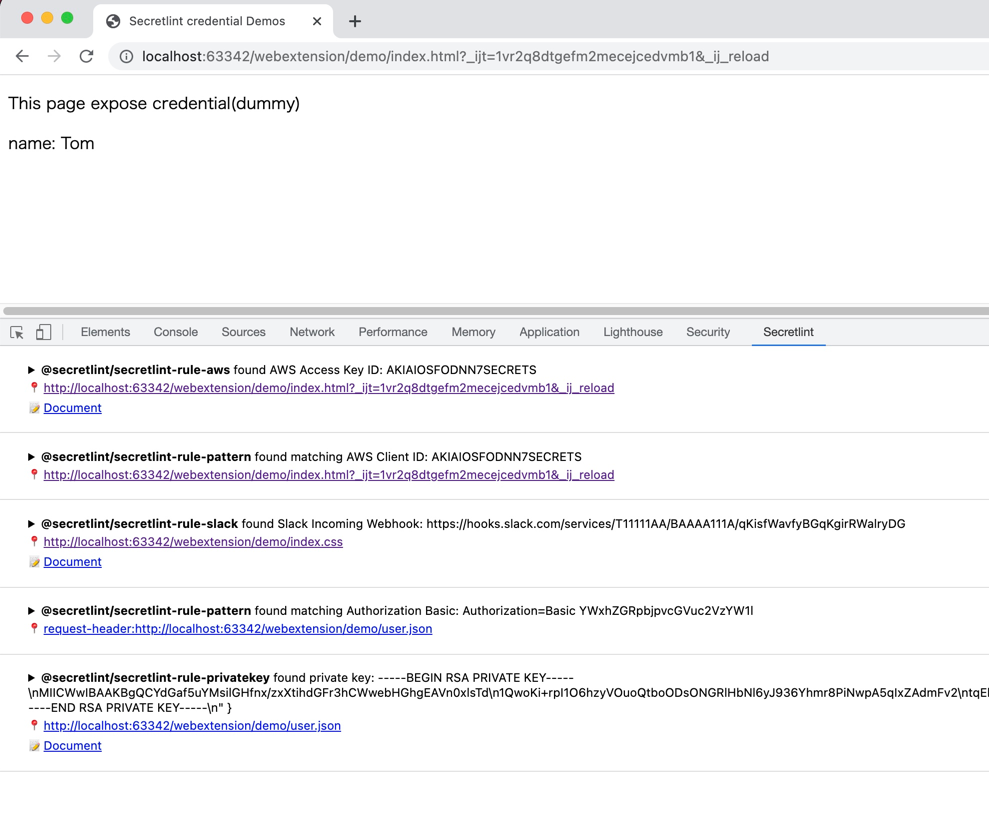 secretlint/secretlint
Pluggable linting tool to prevent committing credential.
 lirantal/npq
safely install npm packages by auditing them pre-install stage

 globocom/huskyci
Performing security tests inside your CI
 coinbase/salus
We would like to request that all contributors please clone a *fresh copy* of this repository since the September 21st maintenance.