
ftw
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
devsecopspenetration-testingvulnerability-scanners+2
142
coreruleset/ftwYAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 weaveworks/weave-gitops
Weave GitOps is transitioning to a community driven project! It provides insights into your application deployments, and makes continuous delivery…
 owasp/docksec
AI-powered Docker security scanner that explains vulnerabilities in plain English. An OWASP Lab Project.
 hubblestack/hubble
Hubble is a modular, open-source security compliance framework. The project provides on-demand profile-based auditing, real-time security event…
 greatscott/enject
enject: Hide .env secrets from prAIng eyes: secrets live in local encrypted stores (per project) and are injected directly into apps at runtime,…
 noveogroup/android-check
Static code analysis plugin for Android project. (Checkstyle, PMD)
 owasp/sedated
SEDATED® Project (Sensitive Enterprise Data Analyzer To Eliminate Disclosure)
 owasp/owasp-aibom
OWASP project defining an AI Bill of Materials (AIBOM) standard to document AI/ML components, dependencies, and supply chain risks for AI security…

 components/dependency-scanning
Generates CycloneDX SBOMs and dependency scanning reports to identify project dependencies, licenses, and vulnerabilities within GitLab CI/CD…
 pvharmo2/gha-lab-3f1ff30e9c
Authorized security-research lab reproducing CVE-2026-31852 (jellyfin/jellyfin-ios pull_request_target pwn in code-quality.yml) — isolated snapshot,…
 swiftdevcollective/xcodeprojectsecurity
A macOS app to scan Xcode project files for possible security issues.
 felipecruz91/node-ip-vex
Sample project that uses VEX to supress CVE-2024-29415.
 shoucheng3/jeremylong__dependencycheck_cve-2018-12036_3-1-2
Software composition analysis tool that detects publicly disclosed vulnerabilities in project dependencies using CPE matching, generating detailed…
 meterianhq/log4j-vuln-coverage-check
A simple project to check coverage of Log4J vuln CVE-2021-44228 (and related)
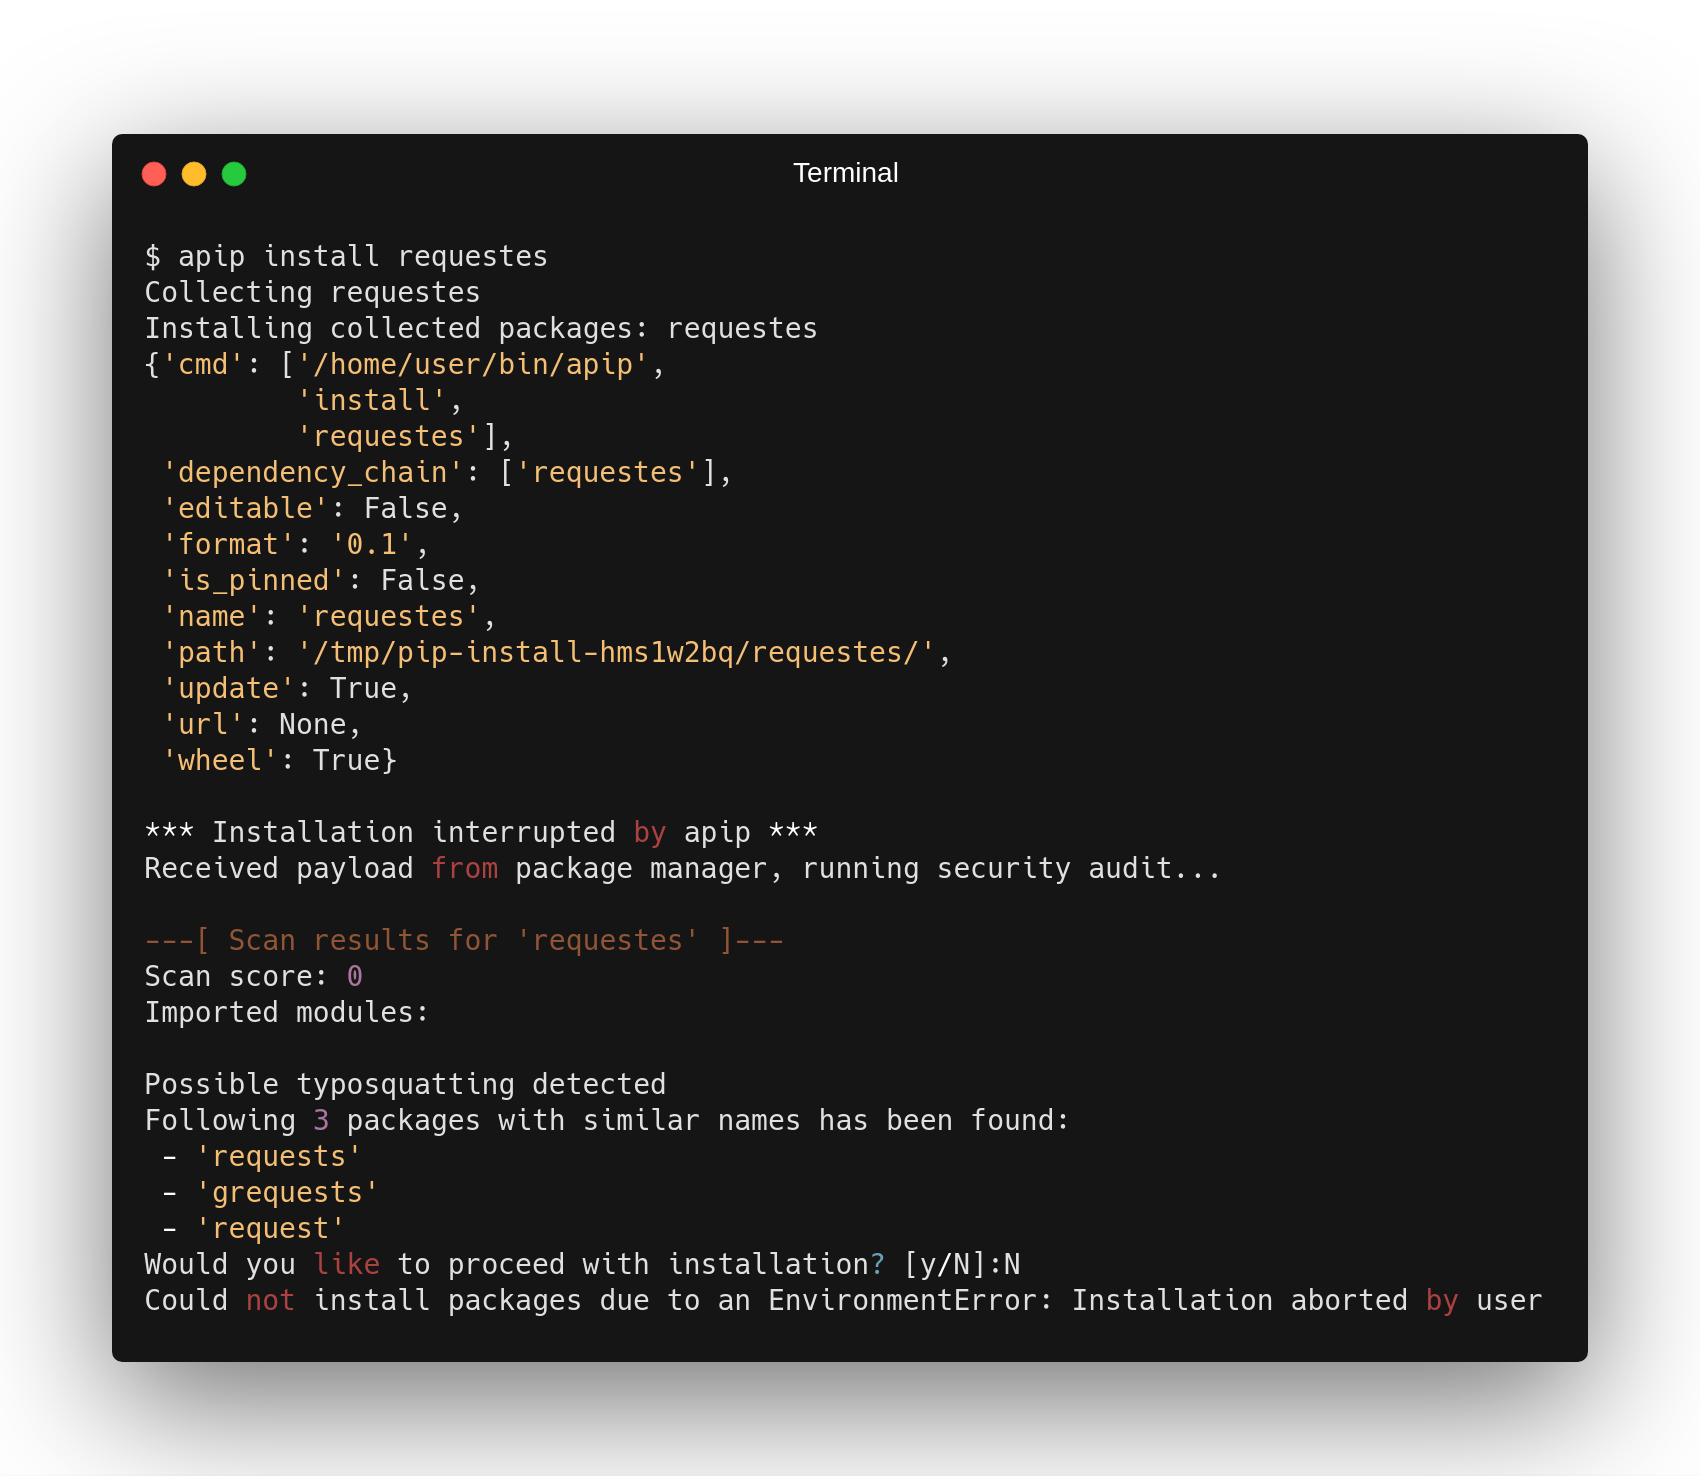 rootlug/aura
Project Aura: Security auditing and code introspection
 hawkeyesec/scanner-cli
A project security/vulnerability/risk scanning tool
 gitlab-da/tutorials/security-and-governance/custom-scanner-integration/fern-pattern-scanner
Scans selected files for patterns stated in rules. This is used in order to find secrets you may have accidentally written to a file. This scanner is…