
kratos
 ory/kratos
API-first identity and user management system for cloud-native applications. Handles login, registration, MFA, recovery, and profile management with…
api-securityauthenticationauthentication-authorization+5
13.9k
ory/kratosAPI-first identity and user management system for cloud-native applications. Handles login, registration, MFA, recovery, and profile management with…
 andreicscs/honeywire
Open-source deception platform that turns any Linux machine into a high-signal canary. Deploy tripwire sensors on files, ports, and network services…
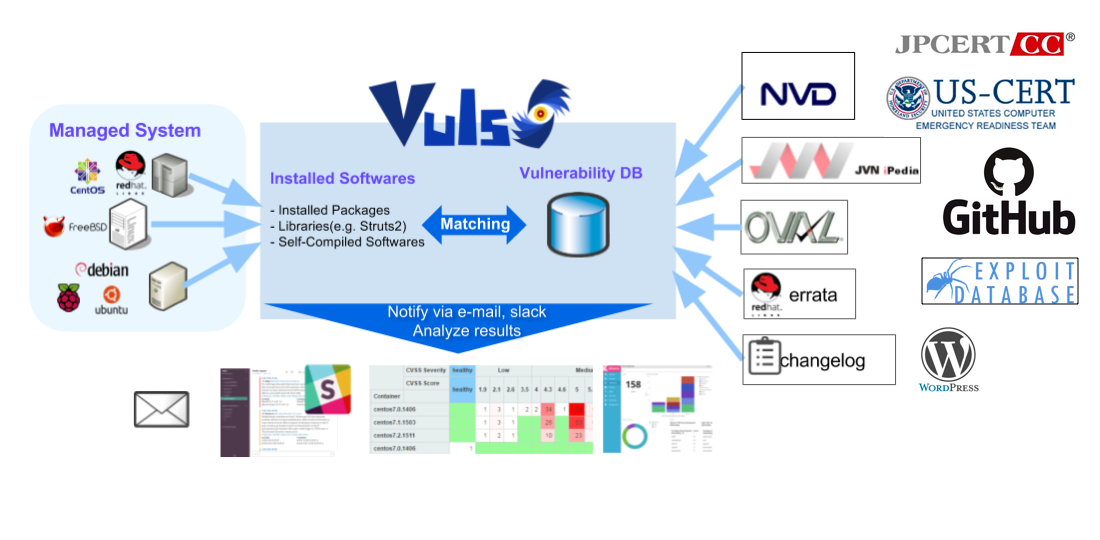 future-architect/vuls
Agent-less vulnerability scanner for Linux, FreeBSD, Container, WordPress, Programming language libraries, Network devices
 netalertx/netalertx
Centralized network visibility and continuous asset discovery. Monitor devices, detect change, and stay aware across distributed networks.
 alexei-led/pumba
Chaos testing, network emulation, and stress testing tool for containers
 cloud-gouv/securix
SécurixOS is a NixOS-based secure operating system tailored for small to medium-sized teams. It provides a minimal, hardened environment with strong…
 bomfather/agent
eBPF-based Linux agent that enforces executable-level access policies in kernel space, sandboxing processes and restricting file, network, and GPU…
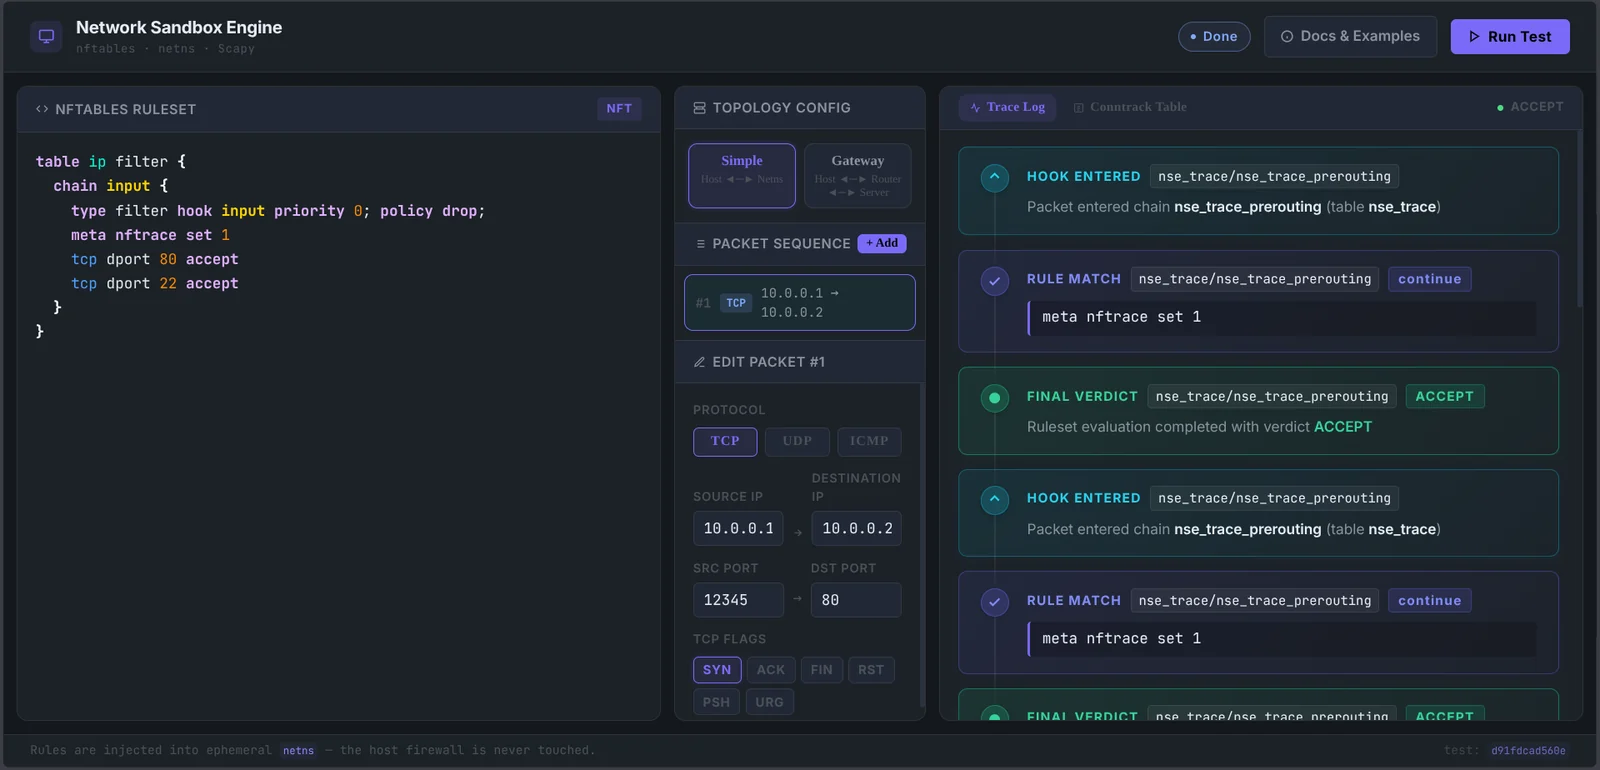 onyks-os/networksandboxengine
A deterministic network sandbox for testing nftables rules. It uses ephemeral Linux network namespaces (netns) and Scapy to validate firewall logic…
 soemoescode/guardskill
Read-only scanner for what lets a repository run code in a coding agent (Claude Code, Codex, Cursor, Copilot): git settings, hooks, and committed MCP…
 hargabyte/cve-scanner
Local CVE scanner for OpenClaw that checks versions against 522+ known vulnerabilities, displays recent HIGH-severity CVEs, and recommends upgrades.…
 hackervlogofficial/cve-2026-23918
This is a proactive tool for security auditing. For your GitHub repository, you’ll want a description that highlights its safety (non-intrusive) and…
 dgourillon/mitigate-cve-2024-6387
Shell script to detect and mitigate CVE-2024-6387 vulnerability by auditing system configurations and applying recommended fixes.
 opnsense/core
OPNsense GUI, API and systems backend
 liamromanis101/dead.letter-cve-2026-45185
Shell-based vulnerability scanner for CVE-2026-45185 (Dead.Letter) in Exim MTA. Detects use-after-free in GnuTLS builds, checks version, TLS library,…

 ndaal_open_source/ndaal_public_auditd
Best-practice Linux Auditd rule set with 14,956 MITRE ATT&CK-mapped rules, Ansible deployment role, and lint/test tooling for security monitoring and…
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
 greenbone/openvas-scanner
This repository contains the scanner component for Greenbone Community Edition.
 docker/docker-bench-security
The Docker Bench for Security is a script that checks for dozens of common best-practices around deploying Docker containers in production.