almalinux-fix-cve-2026-31431

Automates kernel patching for CVE-2026-31431 and Dirty Frag, sets secure kernel as default in GRUB, and disables testing repo for production safety.
cloud-infrastructure-securityconfiguration-auditingdevsecops+1

Automates kernel patching for CVE-2026-31431 and Dirty Frag, sets secure kernel as default in GRUB, and disables testing repo for production safety.

Safe detection tooling for CVE-2026-31431 "Copy Fail" and CVE-2026-43284 "Dirty Frag" — a local privilege escalation in the Linux kernel's algif_aead…

Processes SARIF output from static analysis tools to detect and redact hard-coded secrets in source code, creating a clean copy without the original…

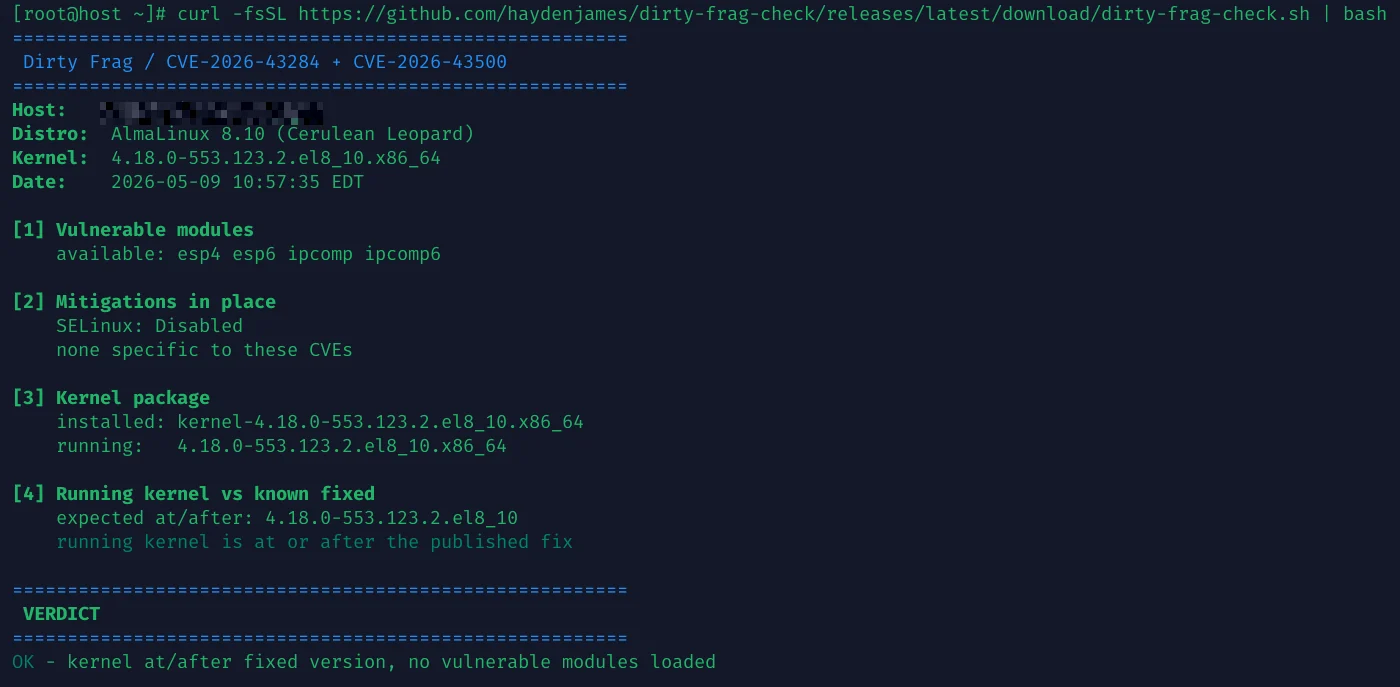
Read-only checker for CVE-2026-43284 / CVE-2026-43500 (Dirty Frag) Linux kernel local-root vulns

Ansible playbook automating CVE-2016-5195 (Dirty COW) mitigation on CentOS/Scientific Linux using SystemTap kernel module generation.