
git-all-secrets
 anshumanbh/git-all-secrets
A tool to capture all the git secrets by leveraging multiple open source git searching tools
code-analysisdevsecopsinformation-gathering+1
1.1k
anshumanbh/git-all-secretsA tool to capture all the git secrets by leveraging multiple open source git searching tools
 aquasecurity/vexhub
Aggregates Vulnerability Exploitability eXchange (VEX) documents from open-source projects. Organizes by PURL for automated security tool integration.
 adimahluf/rapidwebrecon
A high-performance automation tool designed to bridge the gap between technical web reconnaissance and executive reporting. Developed by **Adi…
 tillson/git-hound
Fast GitHub recon tool. Scans for leaked secrets across all of GitHub, not just known repos and orgs. Support for GitHub dorks.
 dionach/reposcanner
Python script to scan Git repos for interesting strings
 praetorian-inc/gato
GitHub Actions Pipeline Enumeration and Attack Tool
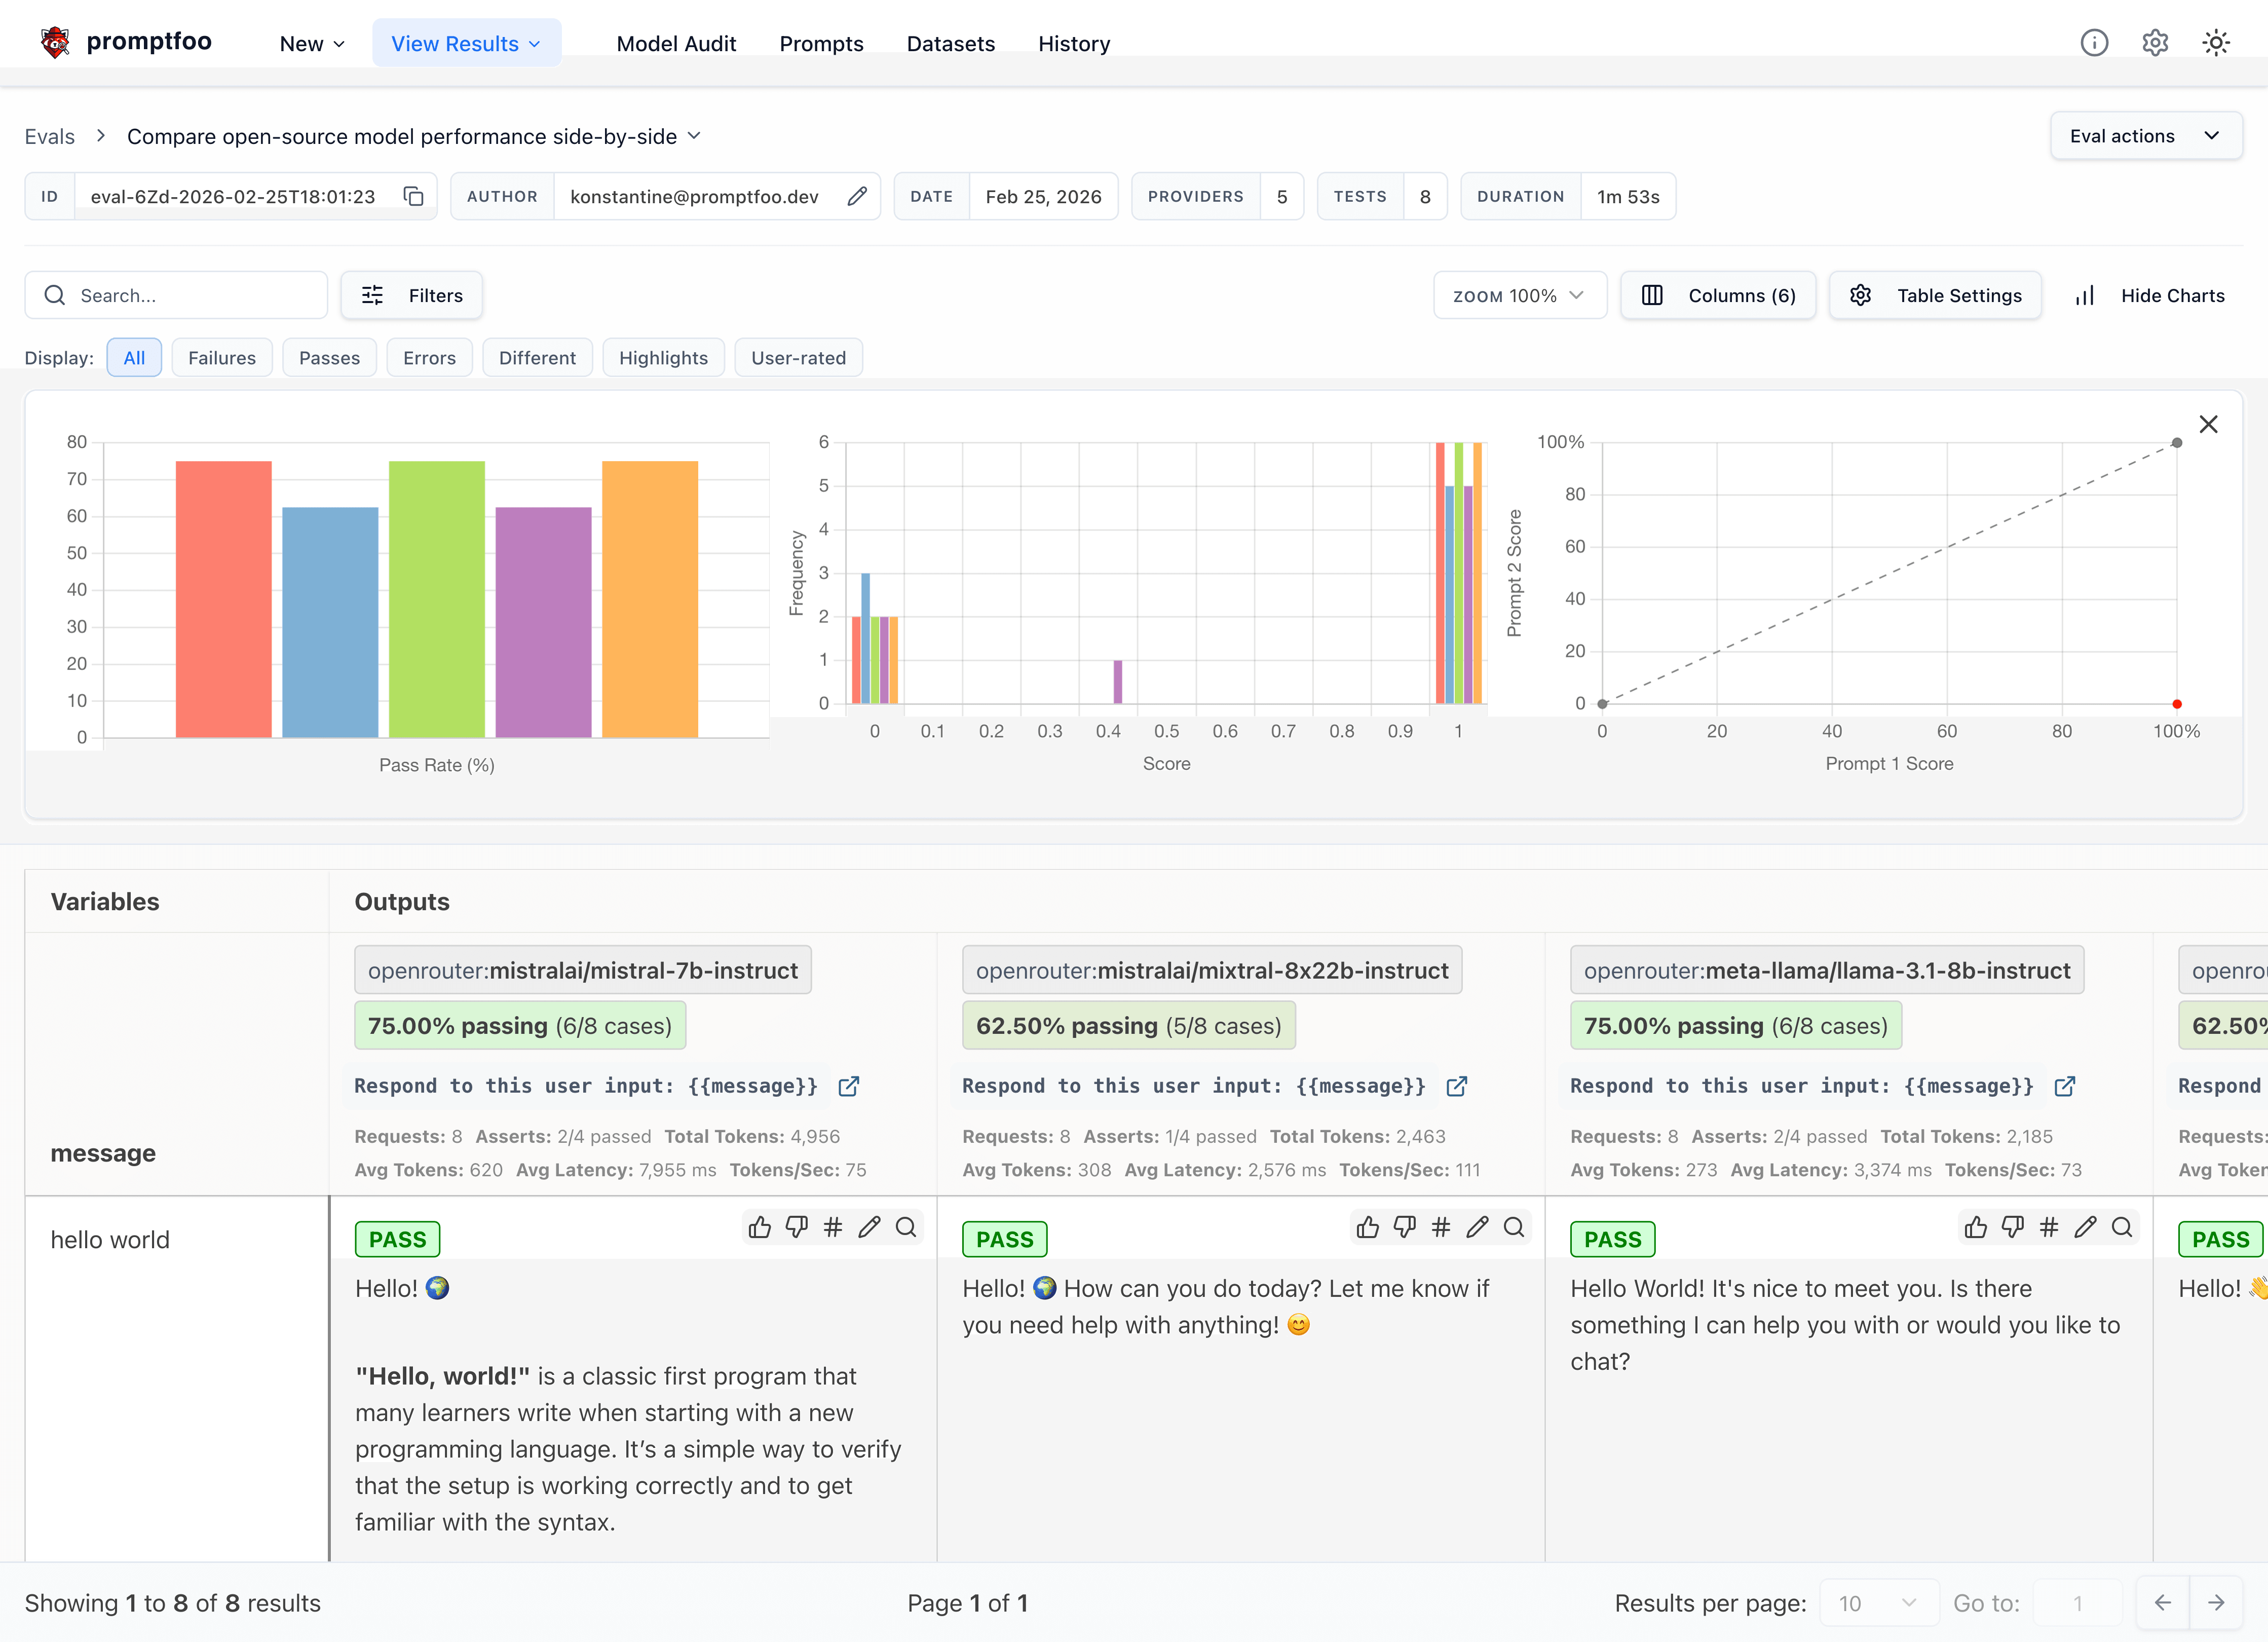 promptfoo/promptfoo
Test your prompts, agents, and RAGs. Red teaming/pentesting/vulnerability scanning for AI. Compare performance of GPT, Claude, Gemini, DeepSeek, and…
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
 infobyte/faraday
Open-source and AI-powered cybersecurity tools for offensive security, vulnerability management, and autonomous pentesting. Built by hackers in Latin…
 stackrox/stackrox
The StackRox Kubernetes Security Platform performs a risk analysis of the container environment, delivers visibility and runtime alerts, and provides…
 securecodebox/securecodebox
Kubernetes-native security scanning orchestrator that automates continuous vulnerability detection by integrating multiple open-source scanners into…
 in-toto/in-toto
Protects software supply chain integrity by verifying each step is performed by authorized functionaries, using signed layout and link metadata.
 cyberark/conjur
CyberArk Conjur automatically secures secrets used by privileged users and machine identities
 google/capslock
CLI tool for analyzing Go package capabilities by tracing transitive calls to privileged standard library operations, enabling supply chain risk…
 aquasecurity/starboard
Superseded by https://github.com/aquasecurity/trivy-operator
 lirantal/npq
safely install npm packages by auditing them pre-install stage
 0sec-labs/0
Full-stack AI security OS for your browser, terminal, and agents. Find, verify, and fix vulnerabilities. Prioritized by business impact instead of…