
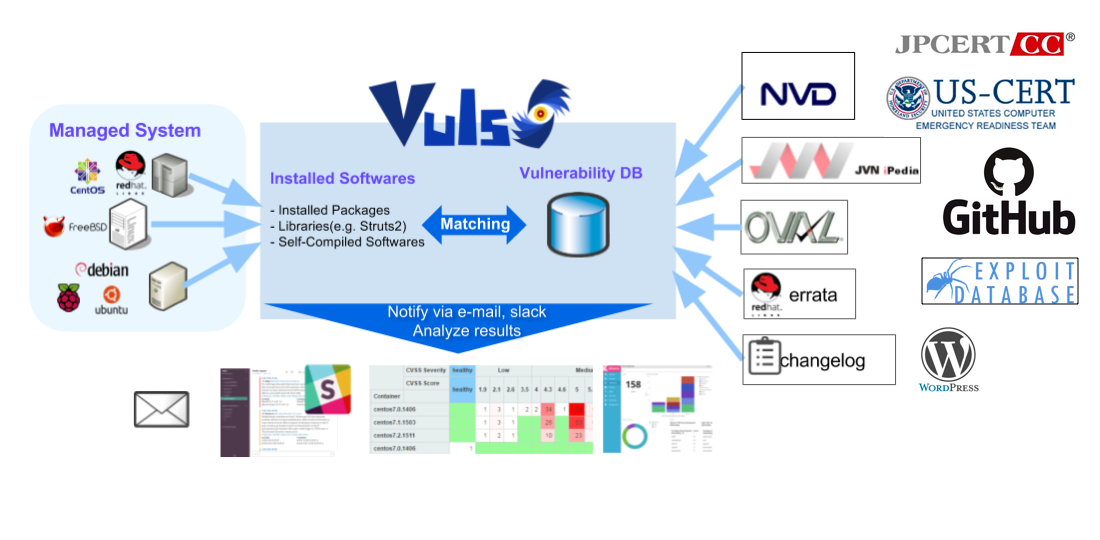
vuls
 future-architect/vuls
Agent-less vulnerability scanner for Linux, FreeBSD, Container, WordPress, Programming language libraries, Network devices
cloud-securityconfiguration-auditingcontainer-security+5
12.3k
future-architect/vulsAgent-less vulnerability scanner for Linux, FreeBSD, Container, WordPress, Programming language libraries, Network devices
 semgrep/semgrep-rules
Static analysis rule pack for detecting security vulnerabilities, dangerous code patterns, and configuration issues across many languages; integrates…
 squid-protocol1/gitgalaxy
AST-free heuristic knowledge graph engine for deep repository intelligence and zero-trust security scanning. Integrates as a GitLab CI/CD component,…
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 infobyte/faraday_agent_dispatcher
Faraday Agent Dispatcher launches any security tools and send results to Faradaysec Platform.
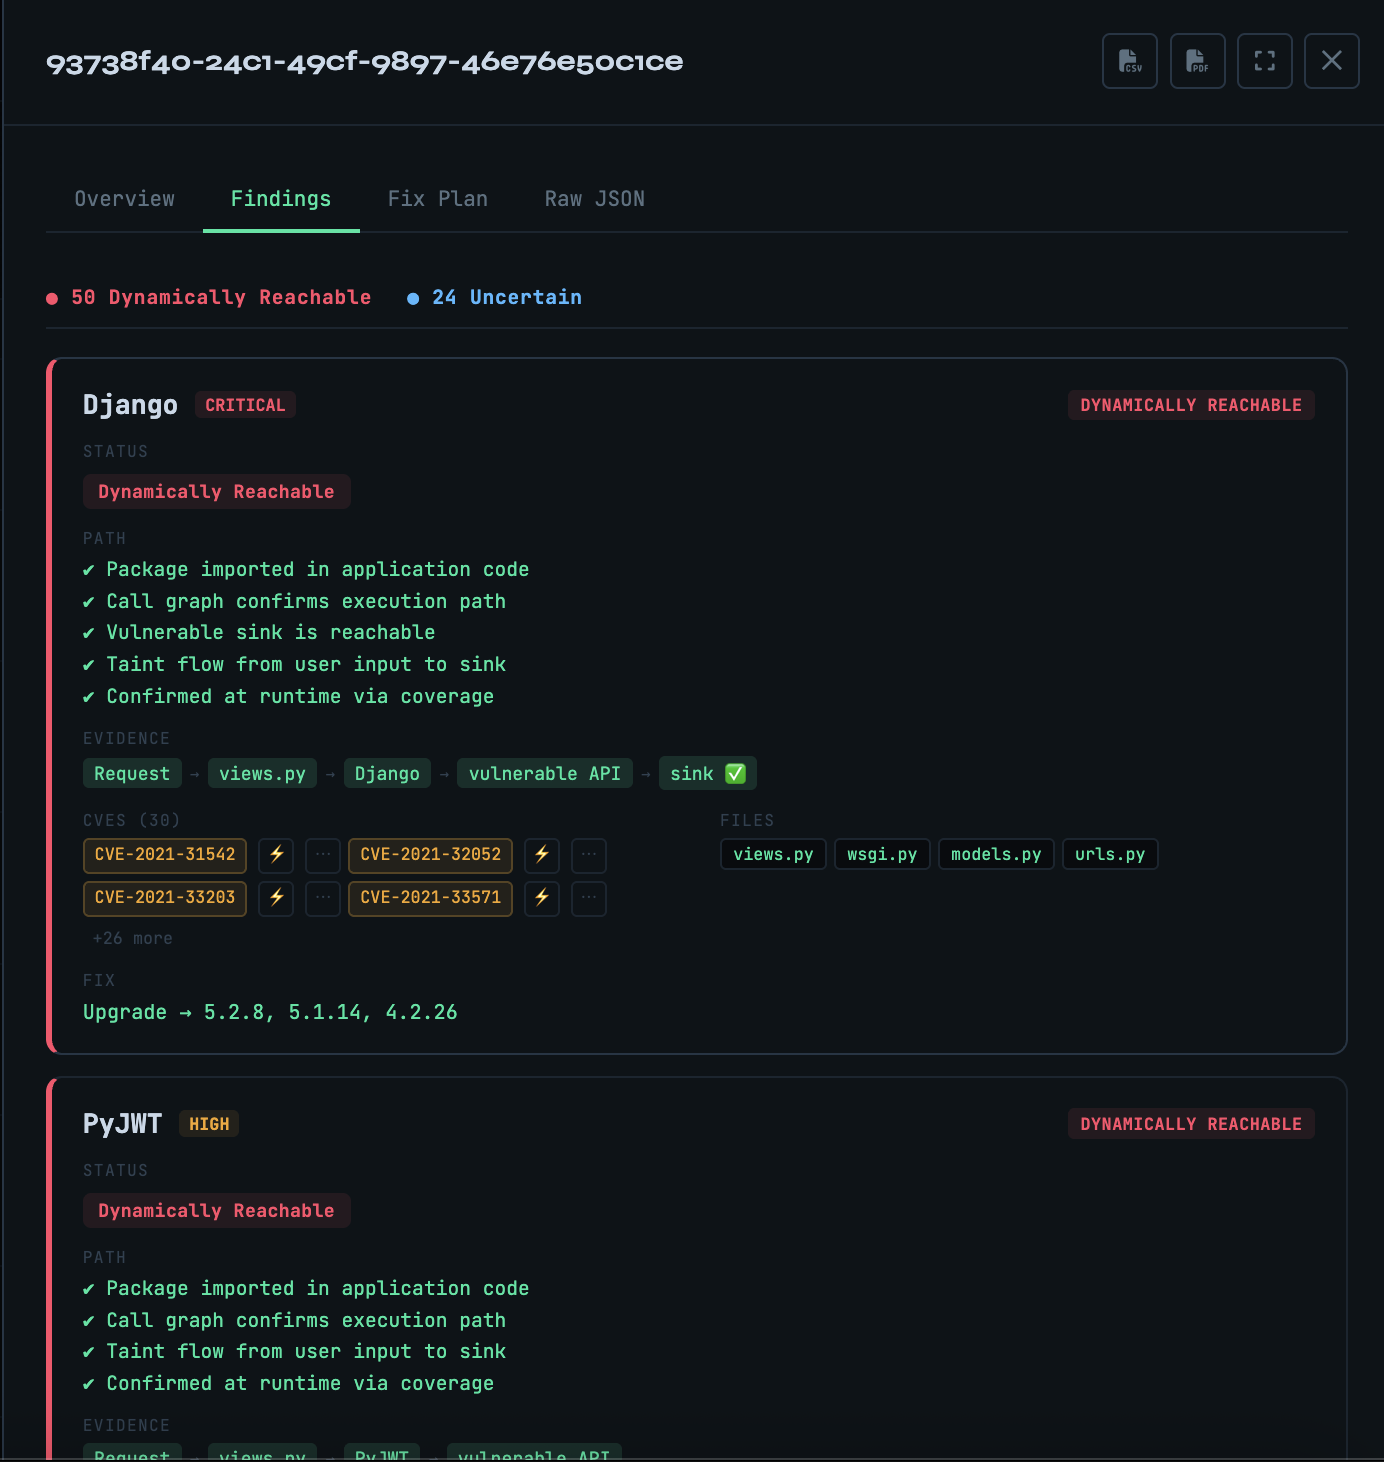 owasp/vulnreach
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.
 sshwarts/skillscript
Skillscript — a small declarative language for authoring agent workflows. Runtime, compiler, and CLI.
 harbor-framework/terminal-bench-2
Benchmark for evaluating AI agents on real-world tasks including vulnerability resolution, code debugging, and protein assembly in containerized…
 dnscontrol/dnscontrol
Infrastructure as code for DNS!
 google/oss-fuzz-gen
LLM powered fuzzing via OSS-Fuzz.
 aerleon/aerleon
Generate firewall ACLs for Cisco, Juniper, Palo Alto, and more from a single YAML policy language via CLI or Python API.
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 hacktricks-wiki/hacktricks-cloud
Community-driven knowledge base for pentesting cloud environments and CI/CD pipelines: attack techniques, enumeration, privilege escalation, and…
 open-policy-agent/conftest
Write tests against structured configuration data using the Open Policy Agent Rego query language
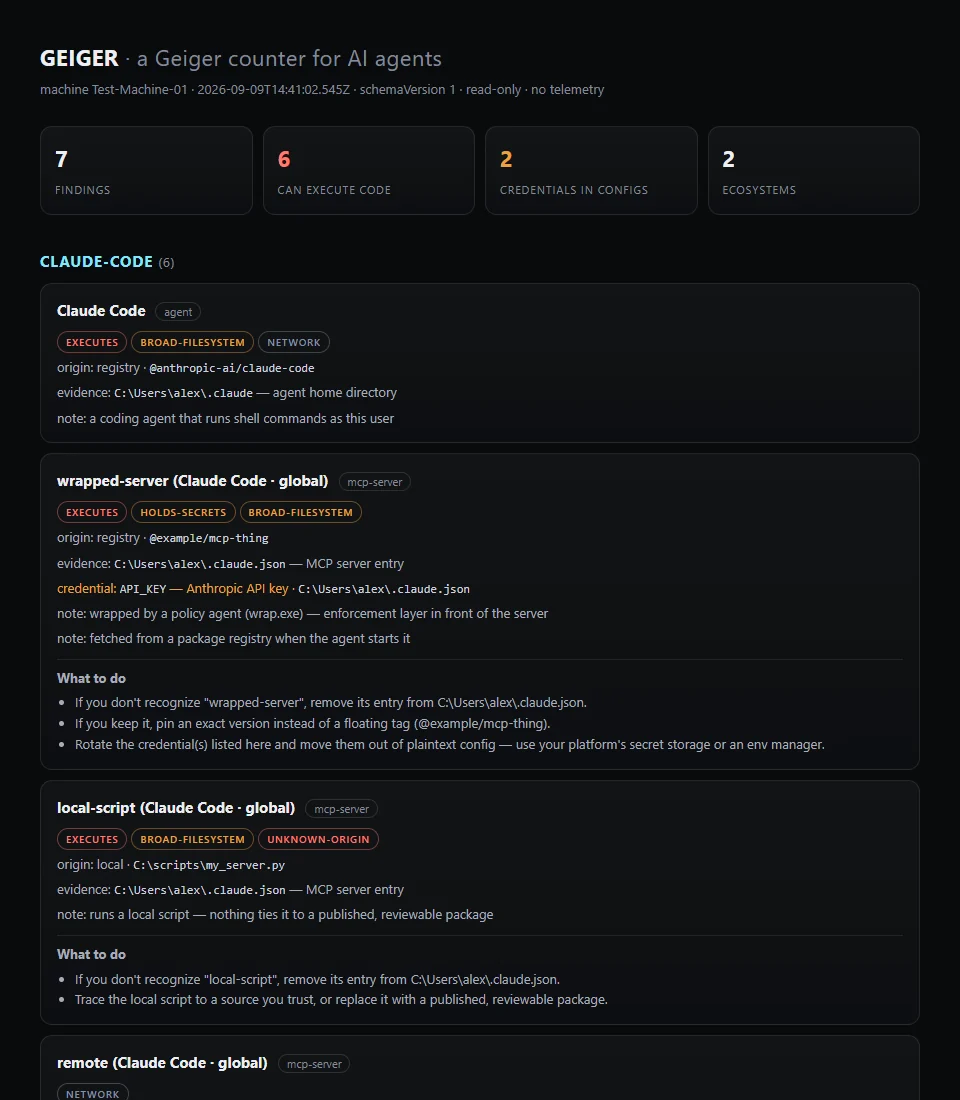 atomburstofficial/geiger
Read-only CLI that inventories AI agents, MCP servers, plugins, and extensions on a machine, reporting their capabilities and exposure with…
 threatcl/threatcl
Documenting your Threat Models with HCL
 cyberark/vulnhalla
Automated security analysis pipeline that runs CodeQL queries on GitHub repositories and uses LLMs to classify and filter true vulnerabilities from…