jeremylong__DependencyCheck_CVE-2018-12036_3-1-2

Software composition analysis tool that detects publicly disclosed vulnerabilities in project dependencies using CPE matching, generating detailed…

Software composition analysis tool that detects publicly disclosed vulnerabilities in project dependencies using CPE matching, generating detailed…

Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.

Monorepo of OWASP Bug Logging Tool projects: crowd-sourced vulnerability reporting, bug bounty workflows, CVE namespace, autopatching, and security…

A Rust CLI tool that recursively discovers Git repositories, captures state changes, generates diffs, extracts code elements with full snippets, and…

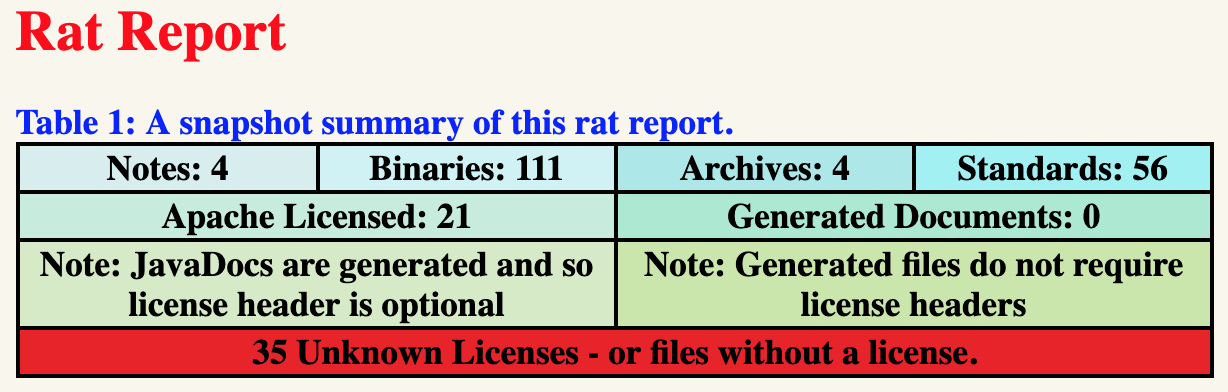
Apache RAT (Release Audit Tool) Gradle Plugin

🔐 Learn authentication by building it right. An extensible, standards-compliant reference implementation for Cloudflare Workers with Hono, Turso,…

Powershell-based bot framework

Sample project that uses VEX to supress CVE-2024-29415.

AI-powered Docker security scanner that explains vulnerabilities in plain English. An OWASP Lab Project.

threatspec - continuous threat modeling, through code

OWASP Security Culture repository

A project security/vulnerability/risk scanning tool

🐺 Vulfy – Fast Rust based package version scanner

Automated secret and leak detection scanner for GitHub and paste sites, with heuristic filtering, IOL enrichment via Shhgit/TruffleHog, and ELK-based…

A macOS app to scan Xcode project files for possible security issues.

Pluggable linting tool to prevent committing credential.

Next-generation dependency vulnerability scanner with reachability analysis, SBOM generation, license audit, and container image scanning for CI/CD…

Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.