
policy_sentry
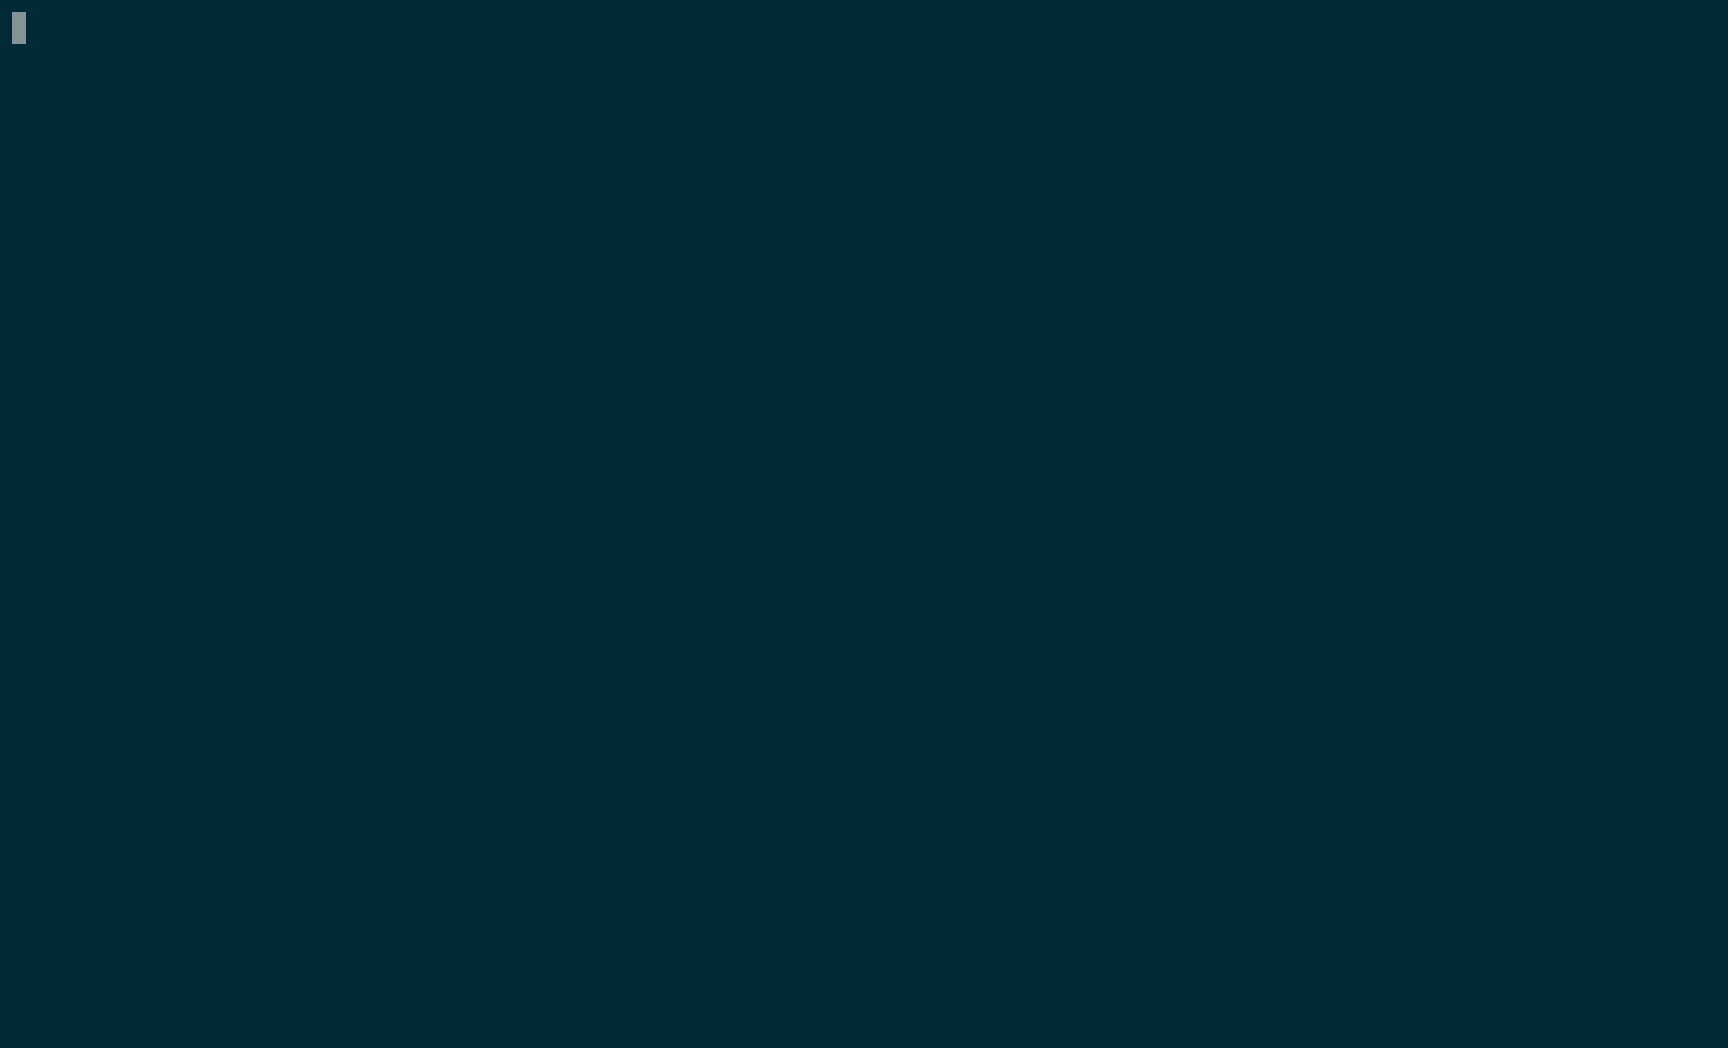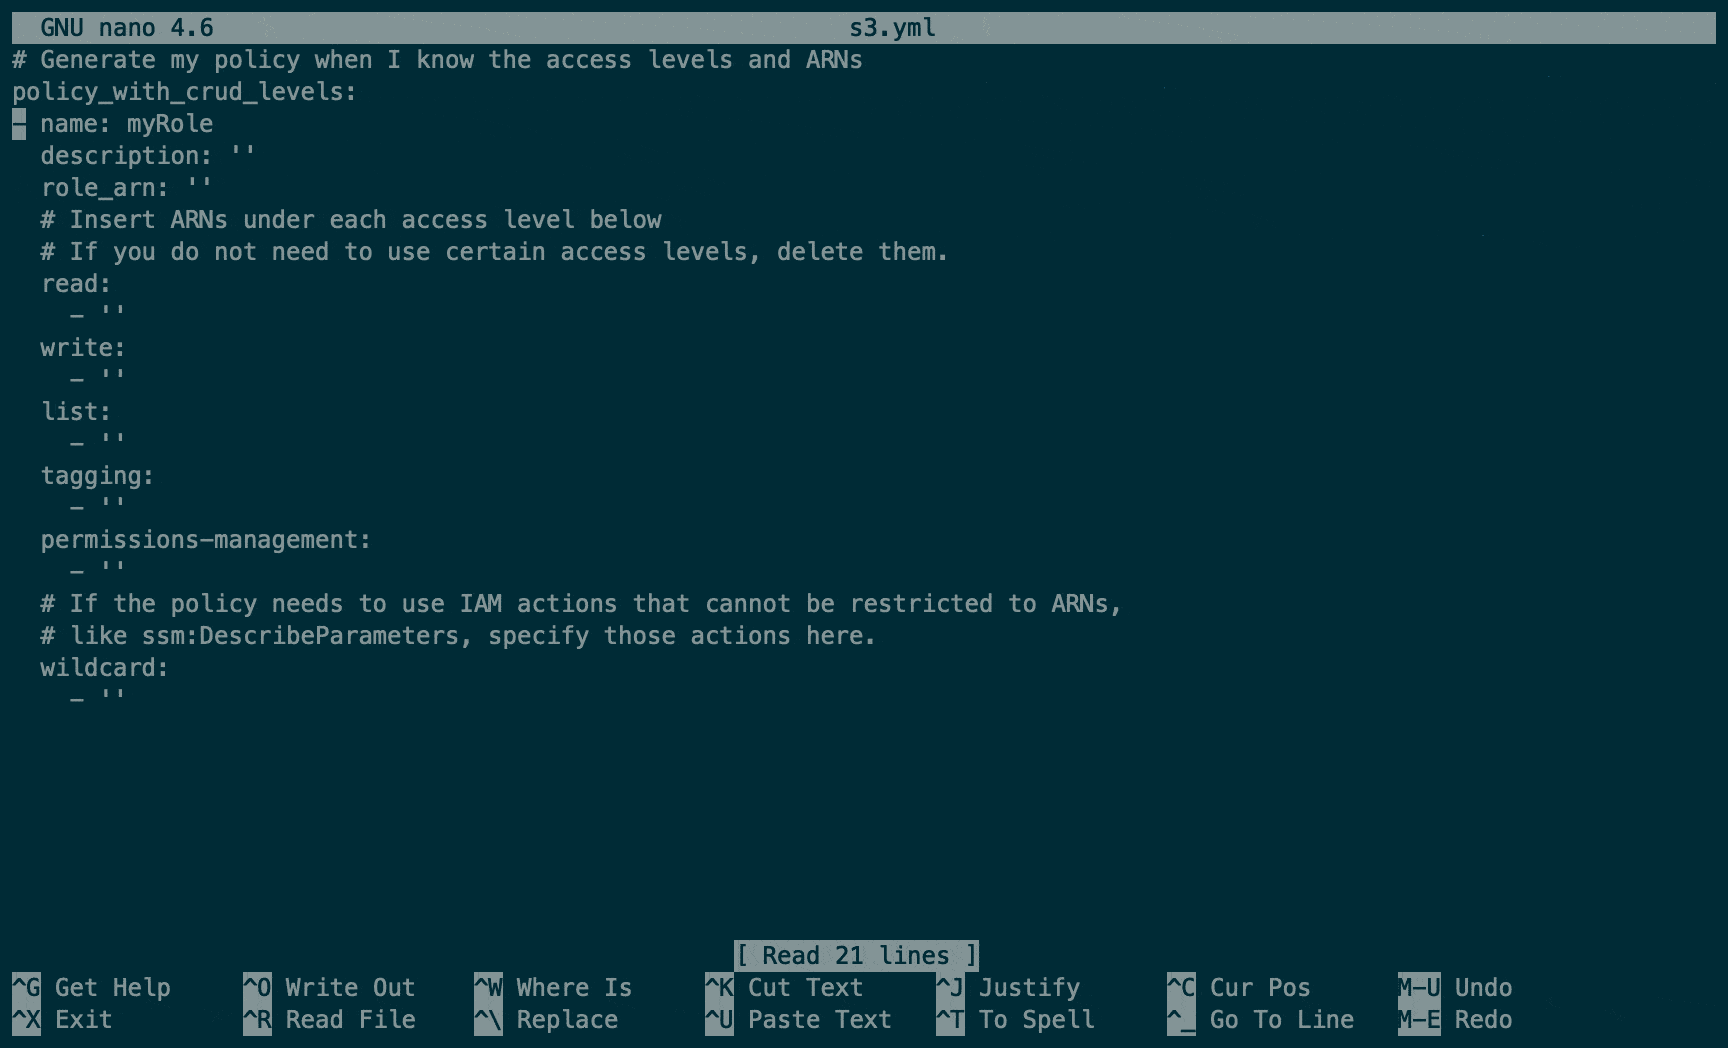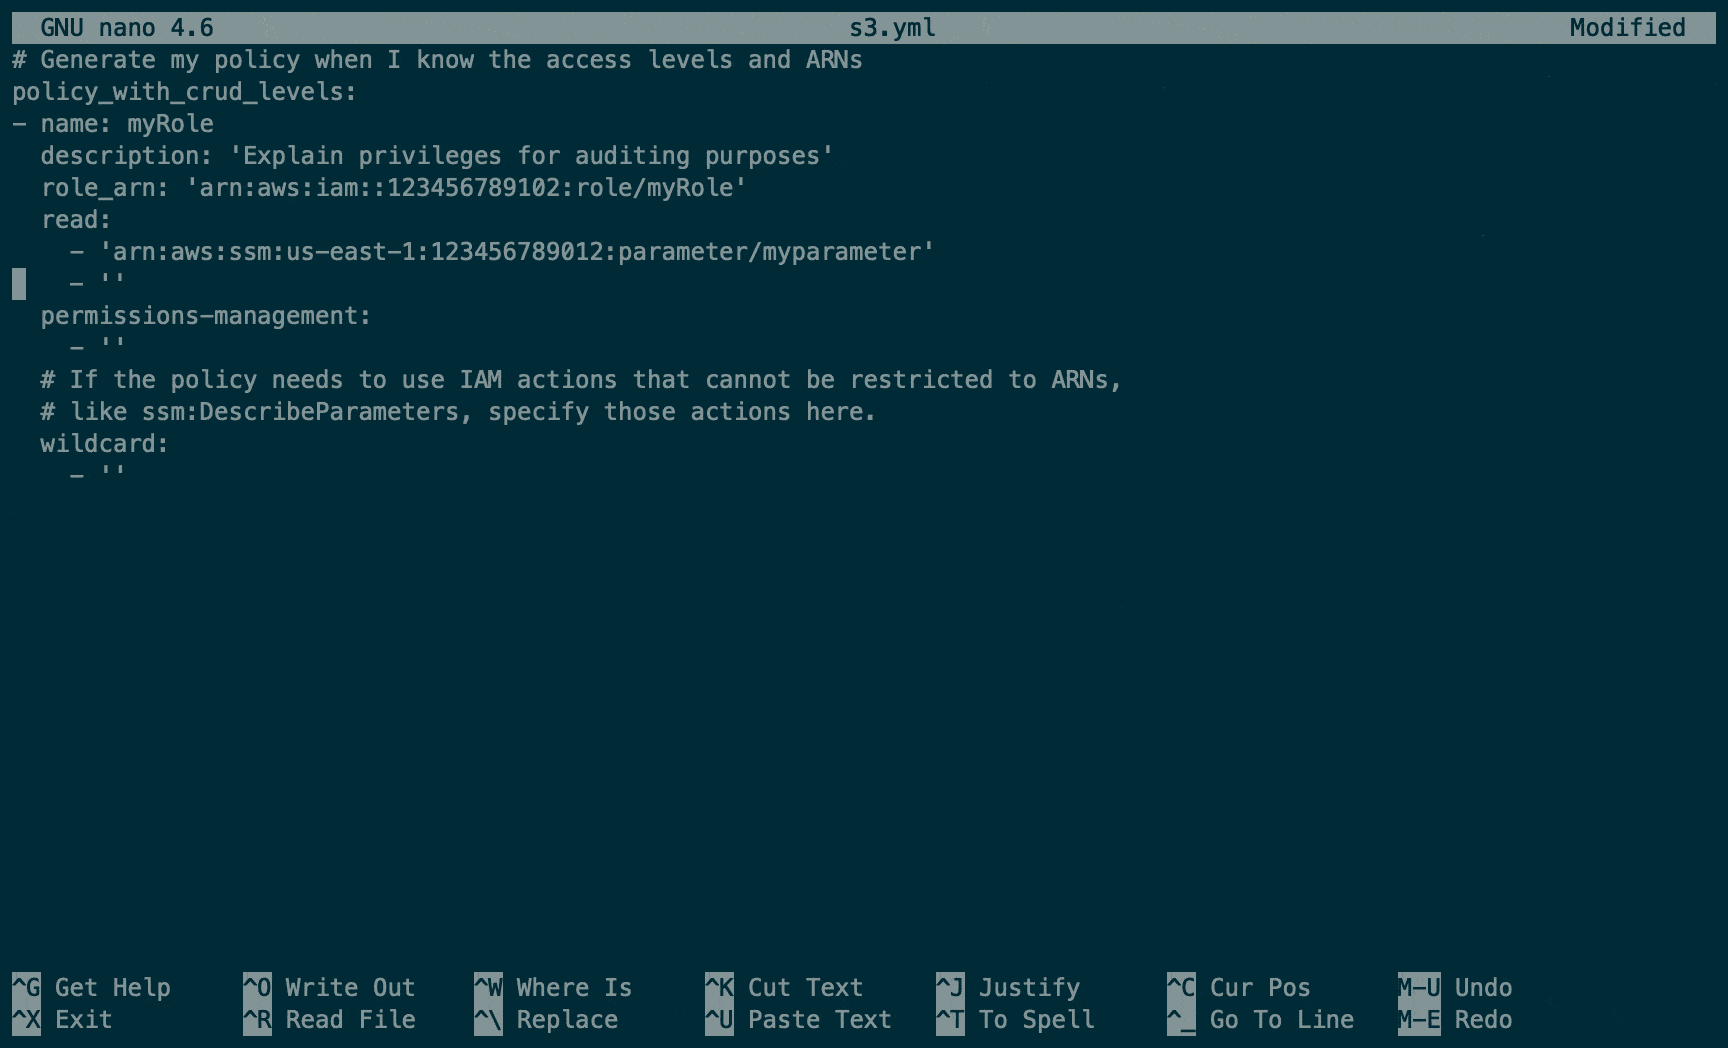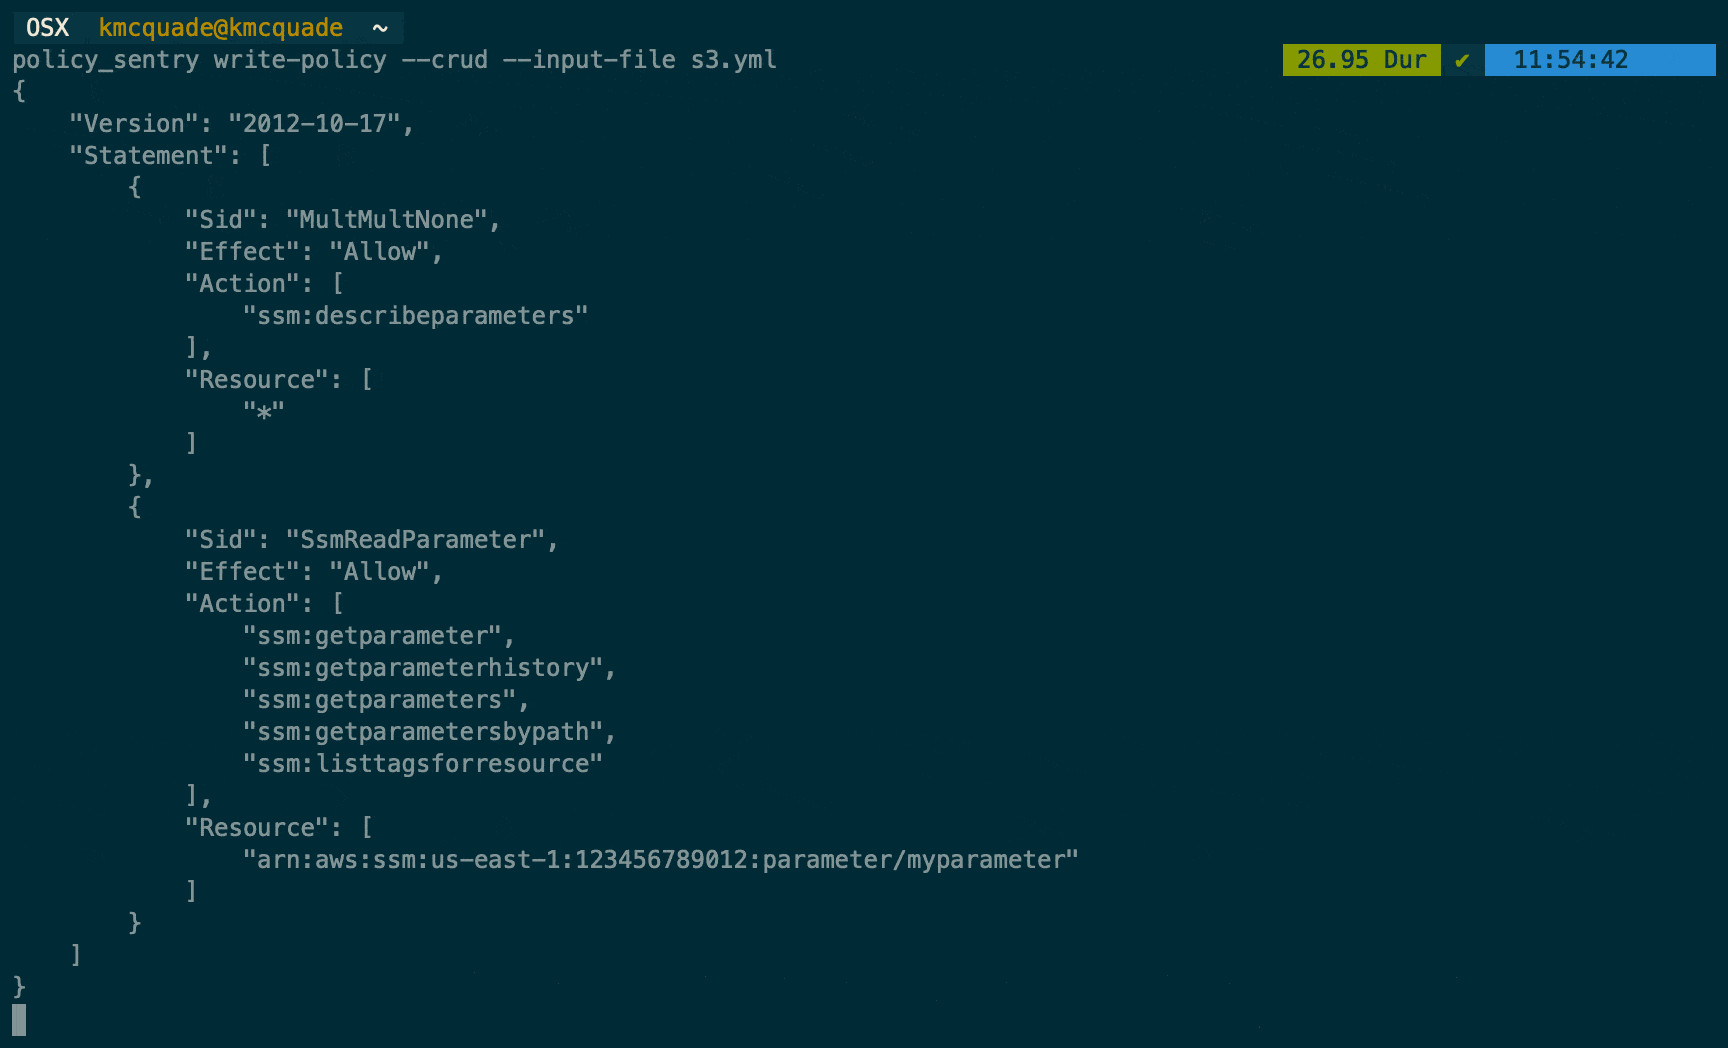
Generates least-privilege AWS IAM policies based on resource ARNs and access levels, automating secure policy creation for cloud infrastructure.

Generates least-privilege AWS IAM policies based on resource ARNs and access levels, automating secure policy creation for cloud infrastructure.

Zero-trust SSH bastion proxy with Vault-backed key management, RBAC policy enforcement, full session recording, and admin TUI for auditable access to…

A Rust CLI tool that recursively discovers Git repositories, captures state changes, generates diffs, extracts code elements with full snippets, and…

Executable security regression testing for agentic applications and MCP-integrated systems.

Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.

A lightweight, file-based CLI API client with age-encrypted secrets, first-class GraphQL support, and a built-in MCP server for AI agent workflows.

Next-generation dependency vulnerability scanner with reachability analysis, SBOM generation, license audit, and container image scanning for CI/CD…

A macOS app to scan Xcode project files for possible security issues.

Static code analysis plugin for Android project. (Checkstyle, PMD)

🐺 Vulfy – Fast Rust based package version scanner

A project security/vulnerability/risk scanning tool

Agent skill + script to scan projects for CVE-2026-111497 (Brotli), rate criticality and suggest fixes

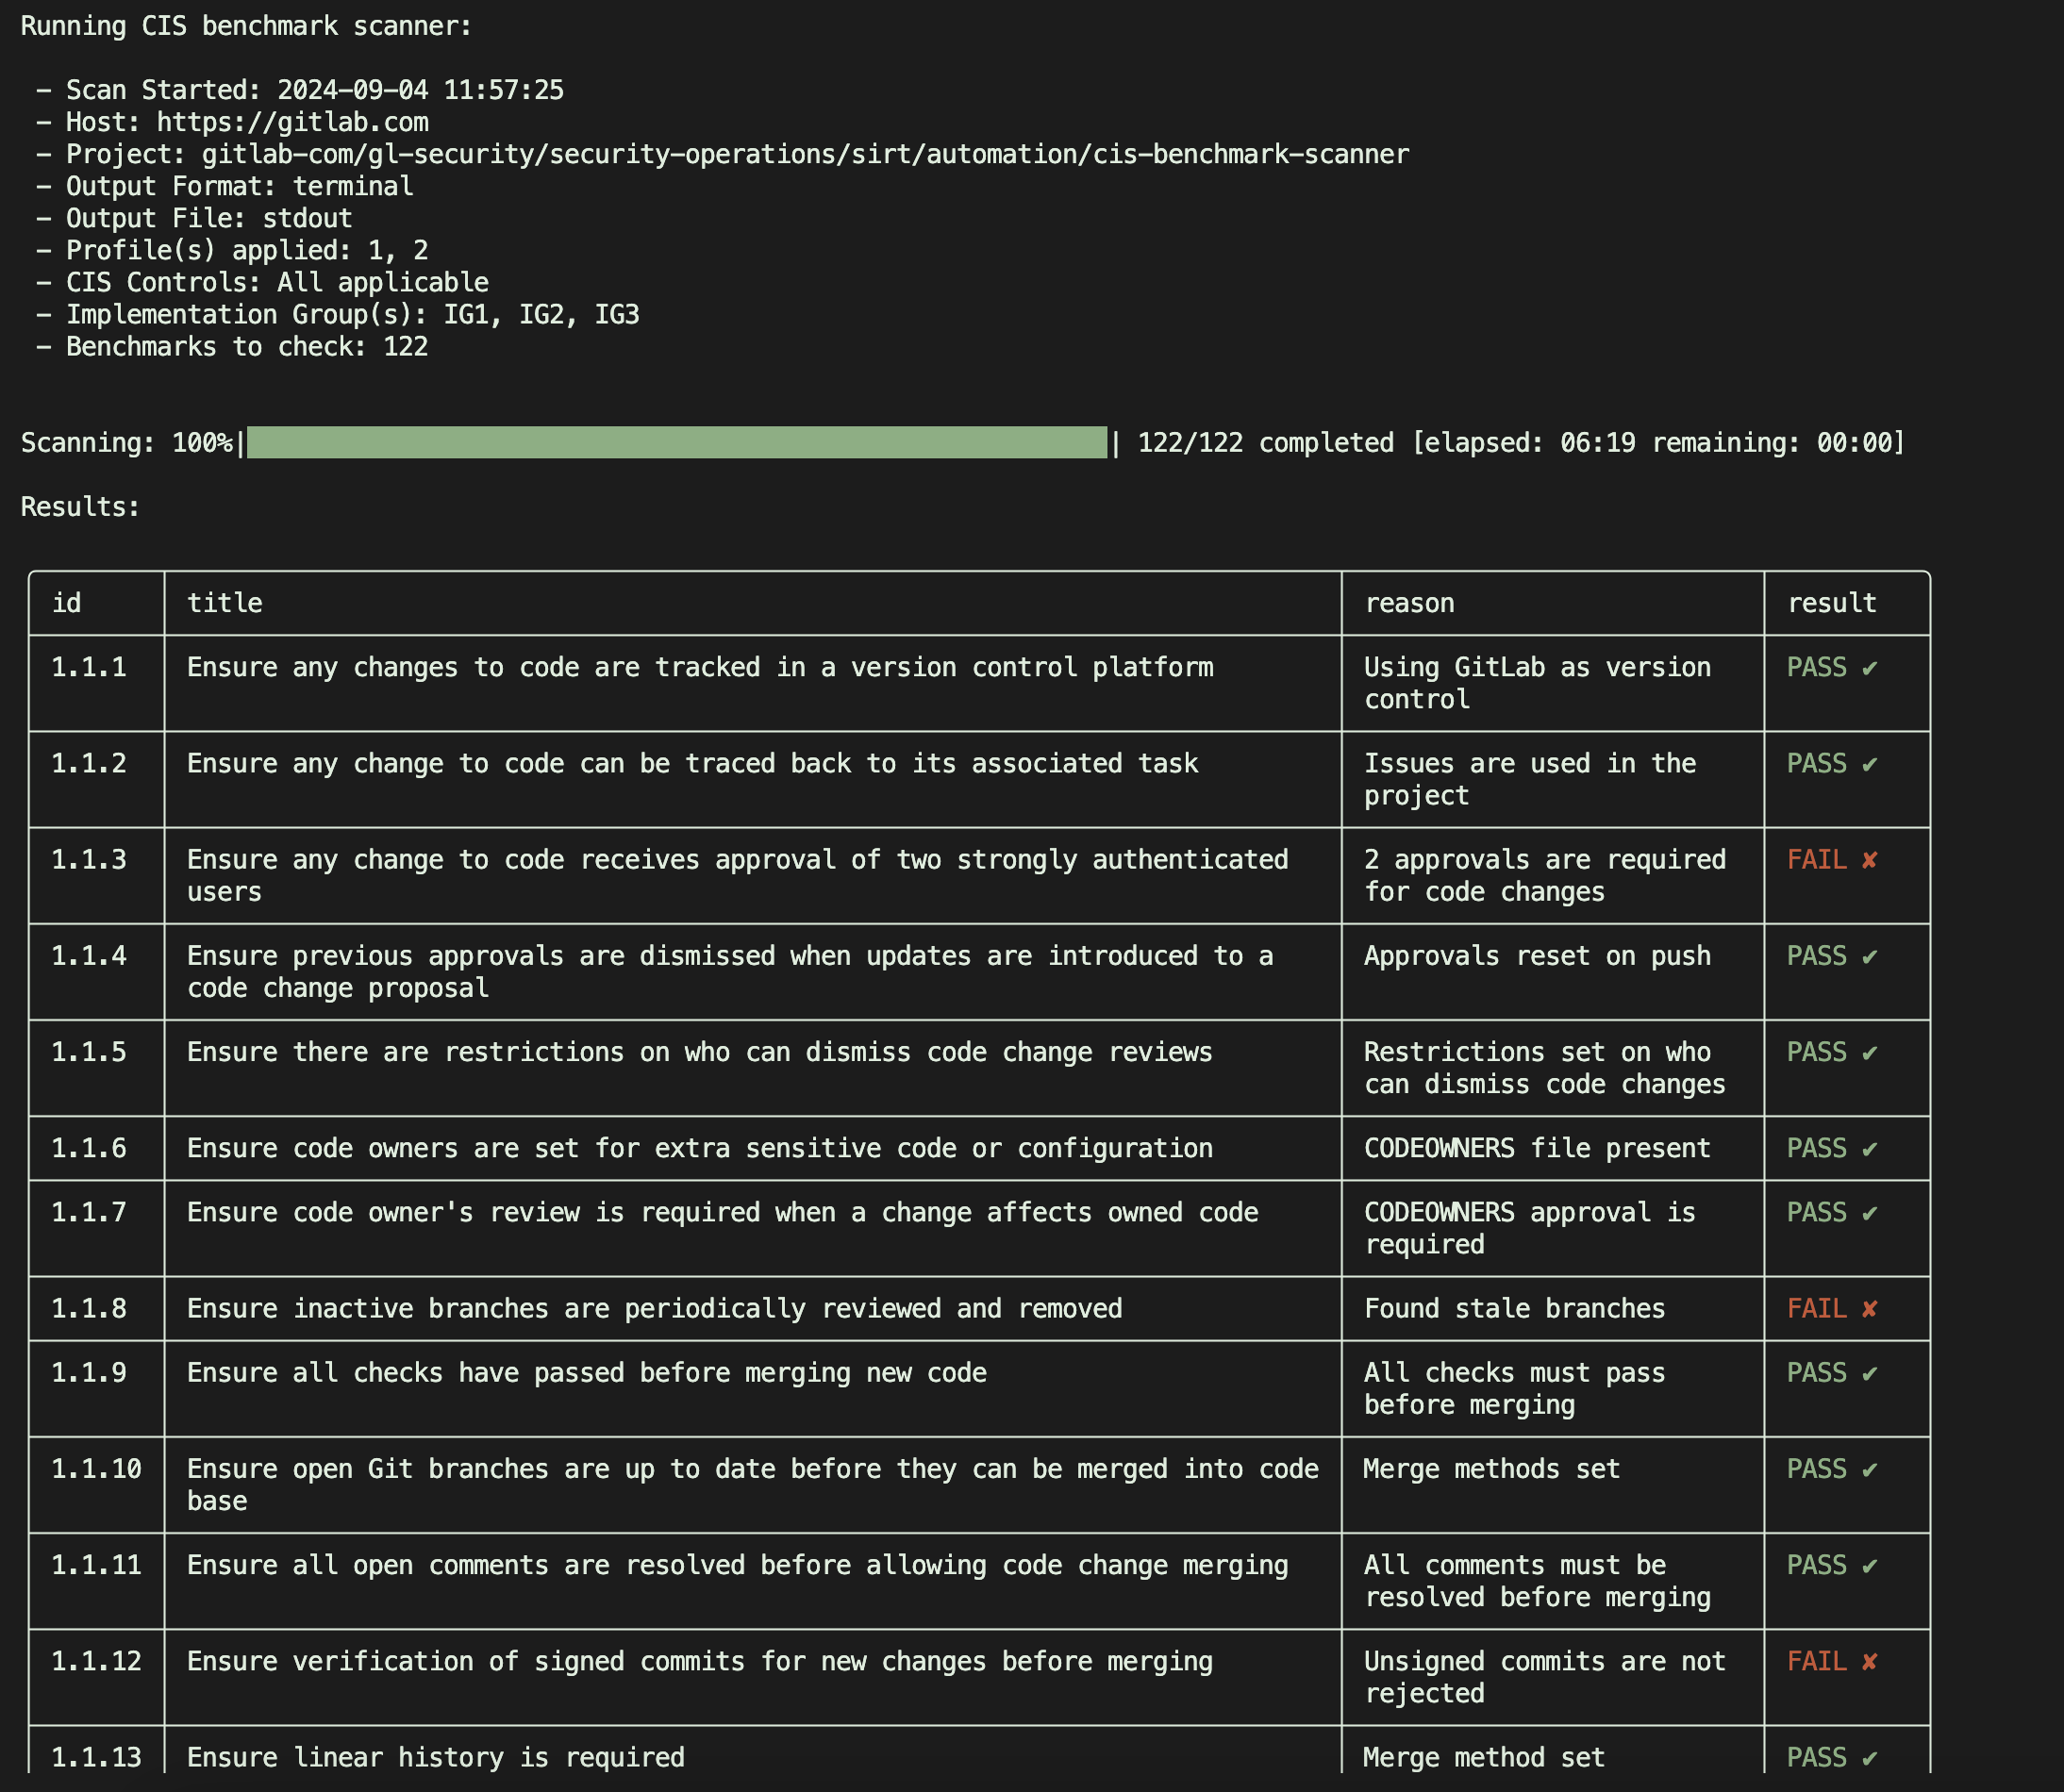
Audits GitLab projects against the CIS GitLab Benchmark via read-only API checks, generating JSON reports on compliance and hardening recommendations.

Runtime patches for algertc/alpr-dashboard: async logger fix and CVE-2025-29927 nginx mitigation


Fleet-scale CVE-2026-31431 audit and remediation orchestrator for Linux hosts via SSH, with strict host-key verification and multi-format reporting.

Buildpack providing a workaround for CVE-2021-44228 (Log4j RCE exploit)

红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool