

OpenShell
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
ai-securityauthentication-authorizationcloud-security+7
12.4k
nvidia/openshellSandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
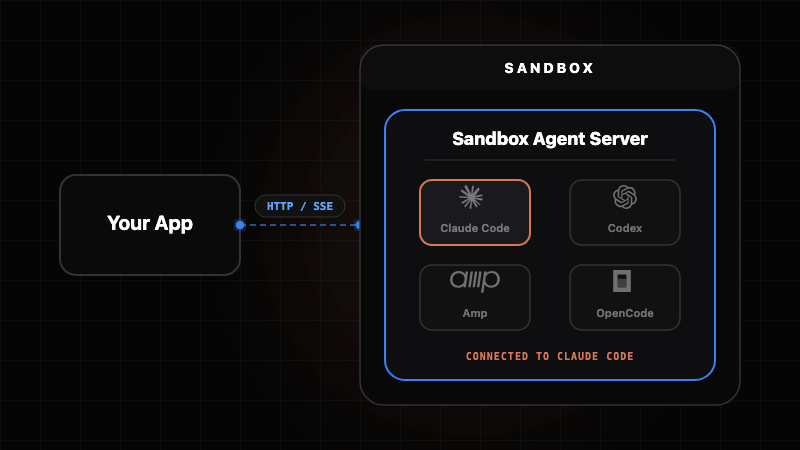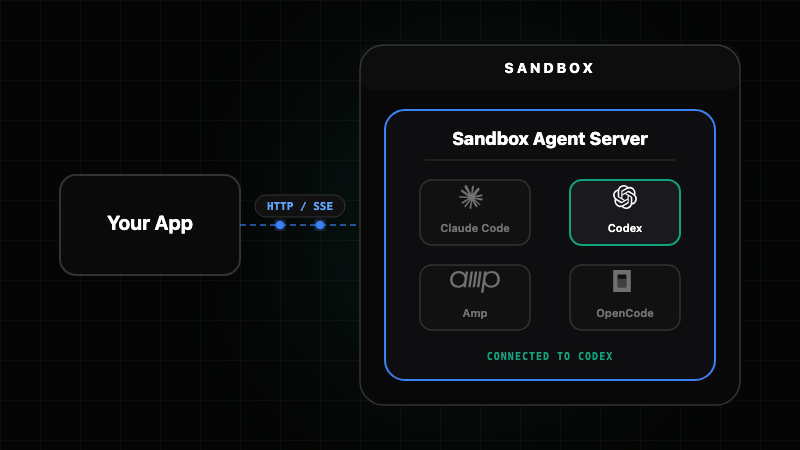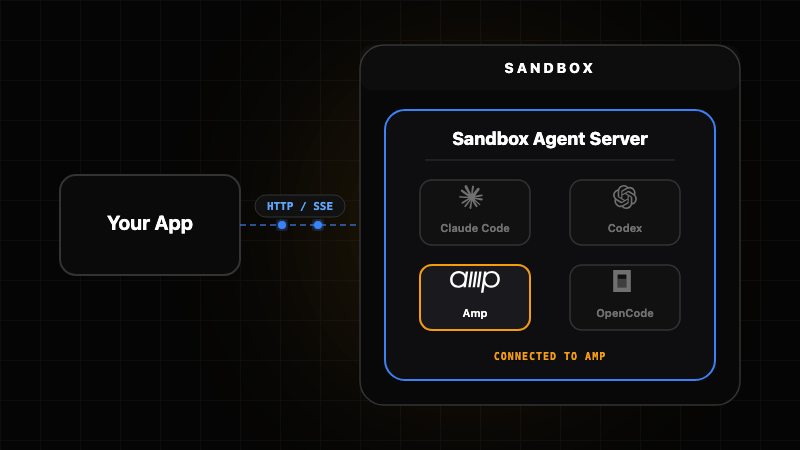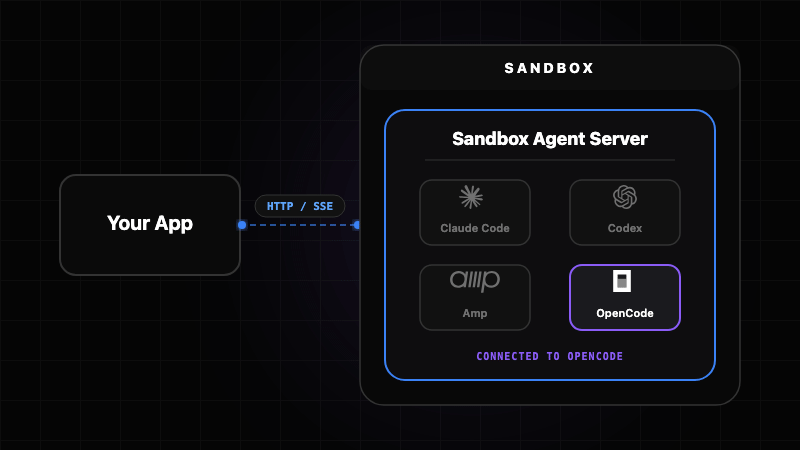 rivet-dev/sandbox-agent
A durable process per agent, with memory that survives restarts
 backbay-labs/clawdstrike
Policy engine and EDR for AI agent fleets and developer workstations. Monitors tool calls, file access, network flows, and process execution with…
 afshinm/zerobox
Lightweight, cross-platform process sandboxing powered by OpenAI Codex's runtime. Sandbox any command with file, network, and credential controls.
 tejasprasad2008-afk/tracetree
Runtime behavioral analysis tool that sandboxes suspicious packages in Docker, traces syscalls with strace, maps process cascades into directed…
 owasp/threat-modeling-playbook
Structured playbook for integrating threat modeling into product security, covering stakeholder buy-in, organizational embedding, training, process…
 cicd-sensor/cicd-sensor
eBPF-powered runtime security sensor for CI/CD pipelines. Detects supply-chain attacks, logs process ancestry and file access, and provides forensic…
 vinnimarcon/log4j-updater
Log4J Updater Bash Script to automate the framework update process on numerous machines and prevent the CVE-2021-44228
 aikidosec/safe-chain
Protect against malicious code installed via npm, yarn, pnpm, npx, pnpx, pip, uv and poetry with Aikido Safe Chain. Free to use, no tokens required.
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 threatspec/threatspec
threatspec - continuous threat modeling, through code
 santhreal/keyhog
Open-source secret scanner in Rust
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
 vikasudasi/exfil-scan
Scan LLM outputs and AI-generated content for data exfiltration signals (EchoLeak, CVE-2025-32711) before they reach users or downstream systems
 felipecosta09/cve-2024-3094
Step-by-step tutorial for detecting CVE-2024-3094 (XZ Backdoor) in container images using Trend Micro Vision One TMAS CLI, with automated scanning…