

PSCF
 owasp/pscf
OWASP framework providing structured security capabilities for software products, derived from regulatory and industry standards analysis to guide…
curated-resourcesdevsecopseducation+2
28
owasp/pscfOWASP framework providing structured security capabilities for software products, derived from regulatory and industry standards analysis to guide…
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 owasp/riskassessmentframework
The Secure Coding Framework
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 wi3memake/react2shell-scanner
Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…
 dipjyotimetia/hybridtestframework
End to End testing of Web, API, Cloud, Events and Security

 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
 purpleteam-labs/purpleteam-orchestrator
Orchestration component of purpleteam

 owasp/security-culture
OWASP Security Culture repository
 securityrat/securityrat
OWASP SecurityRAT (version 1.x) - Tool for handling security requirements in development
 owasp/kubelight
OWASP Kubernetes security and compliance tool [WIP]
 owasp/blt
Monorepo of OWASP Bug Logging Tool projects: crowd-sourced vulnerability reporting, bug bounty workflows, CVE namespace, autopatching, and security…
 owasp/teach-appsec
OWASP teaching modules covering application security fundamentals including risk management, secure software development, and operations security for…
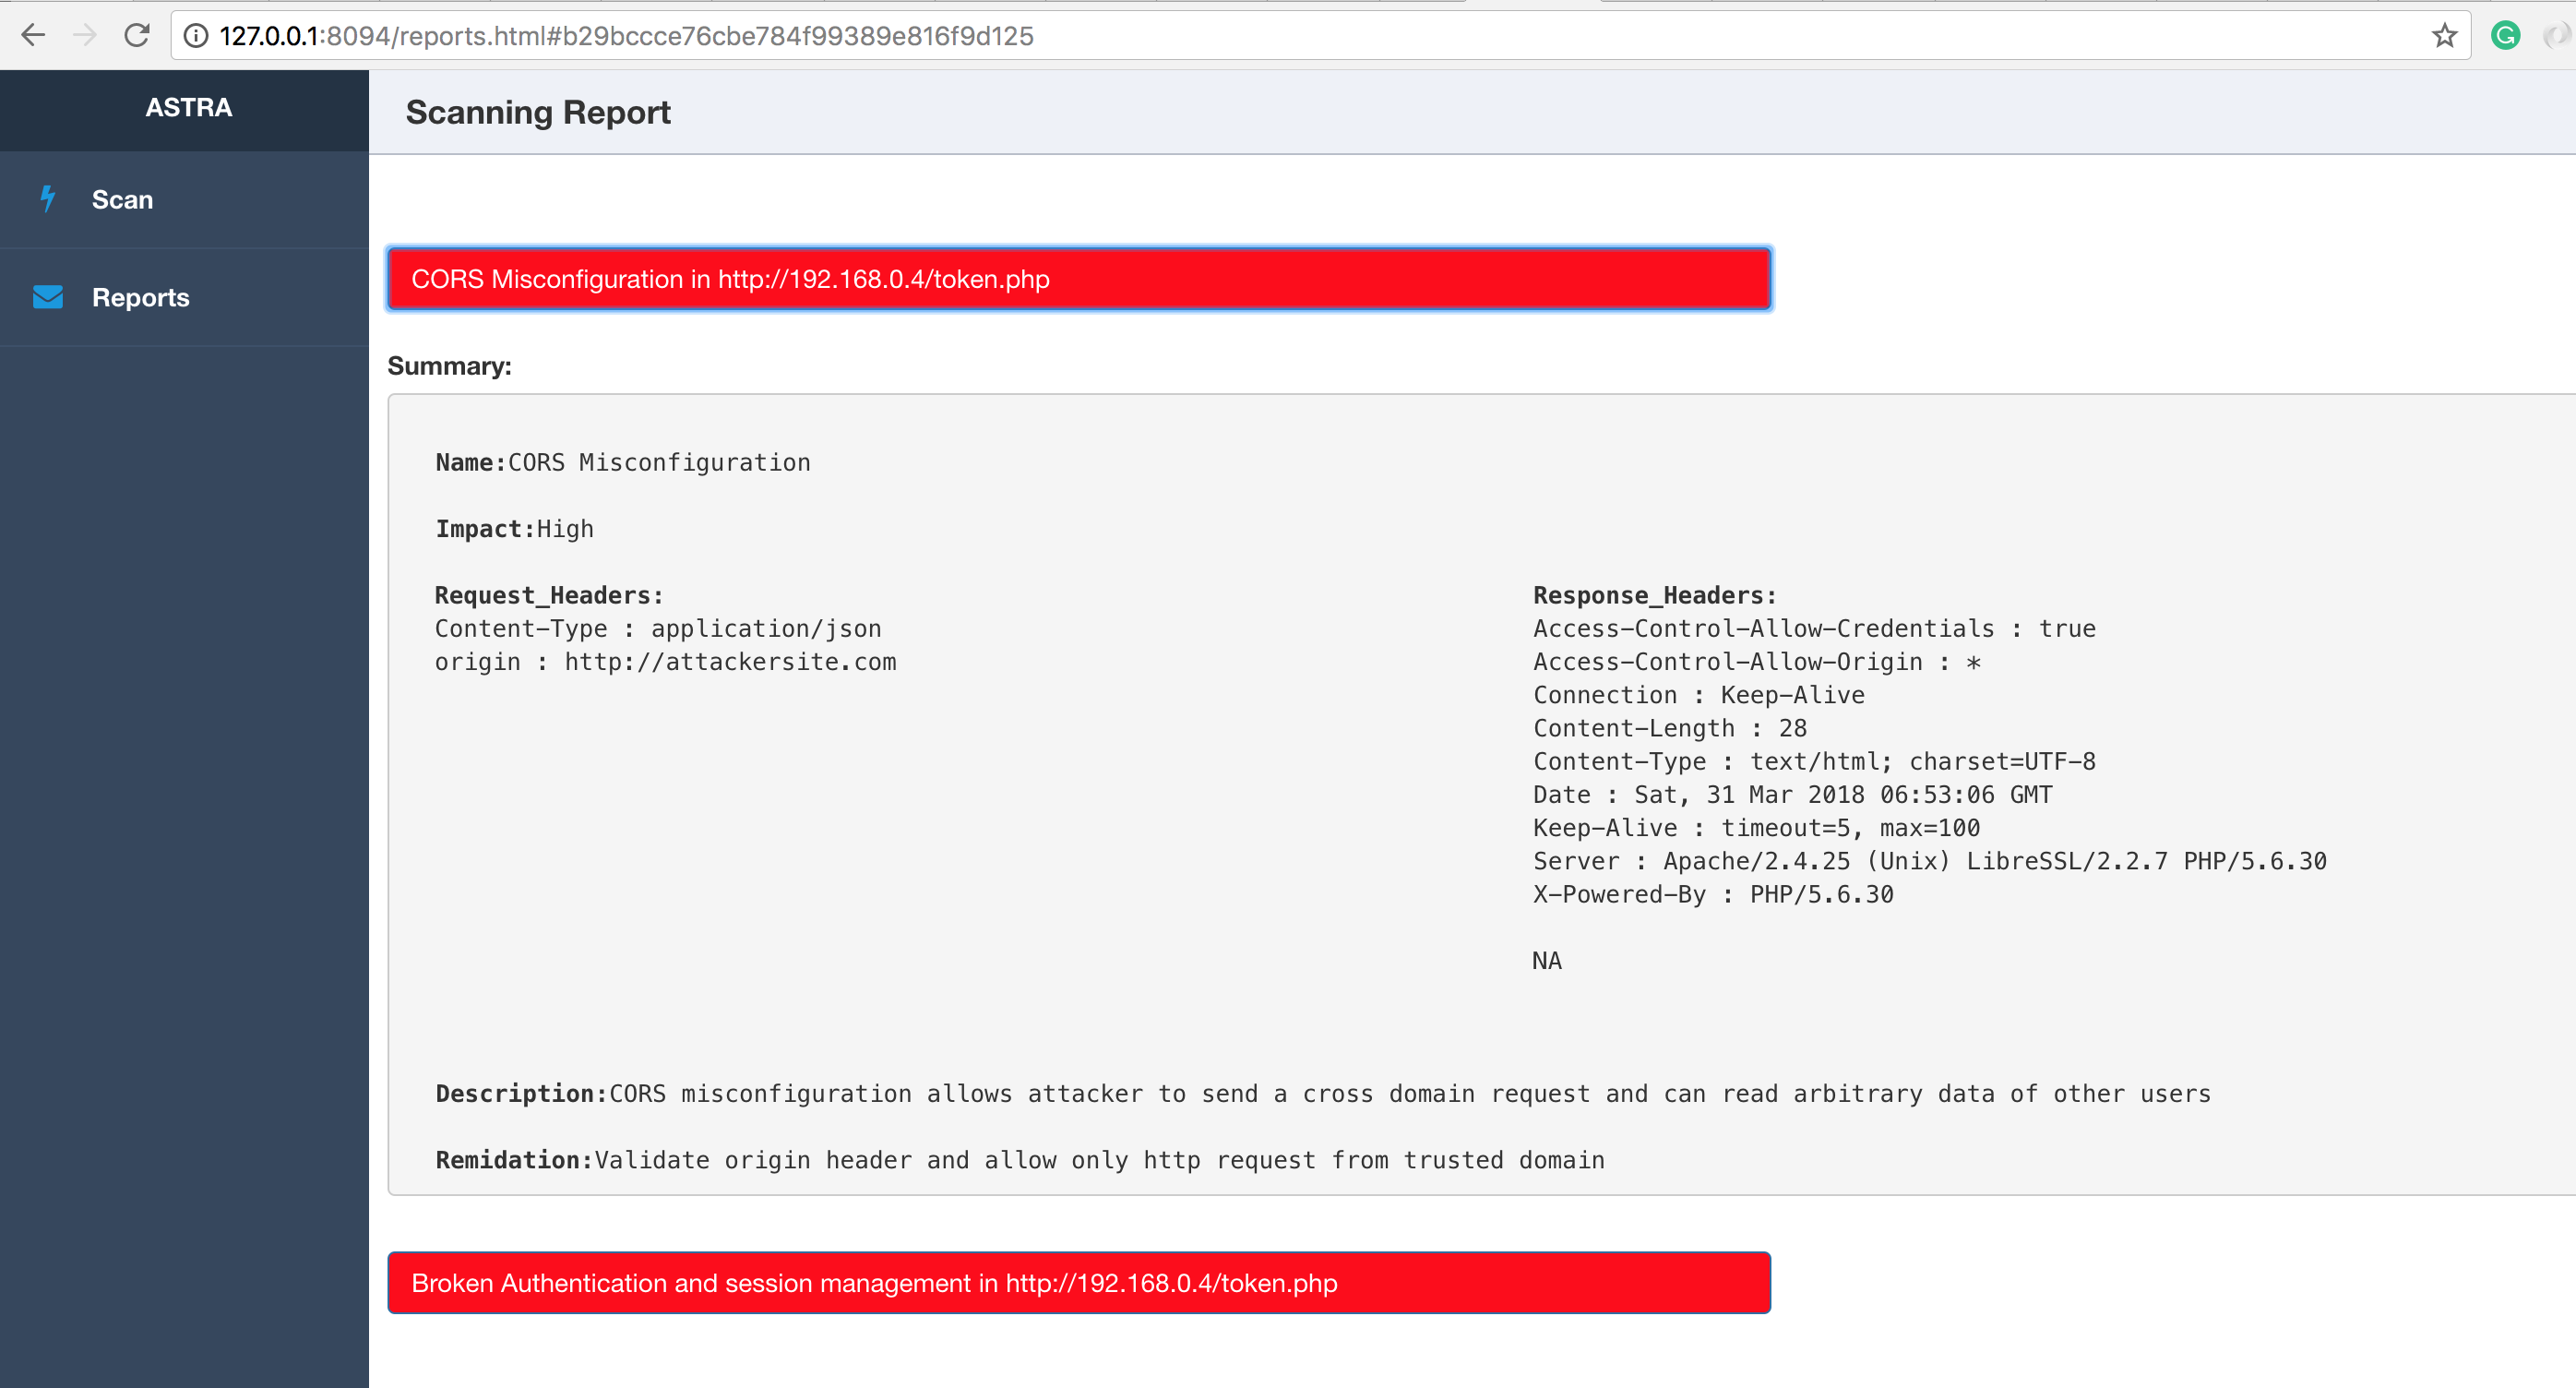 flipkart-incubator/astra
Automated Security Testing For REST API's
 0x4d31/burpa
Burp-Automator: A Burp Suite Automation Tool with Slack Integration. It can be used with Jenkins and Selenium to automate Dynamic Application…