

Elkeid
 bytedance/elkeid
Elkeid is an open source solution that can meet the security requirements of various workloads such as hosts, containers and K8s, and serverless. It…
cloud-securityconfiguration-auditingcontainer-security+6
2.7k
bytedance/elkeidElkeid is an open source solution that can meet the security requirements of various workloads such as hosts, containers and K8s, and serverless. It…
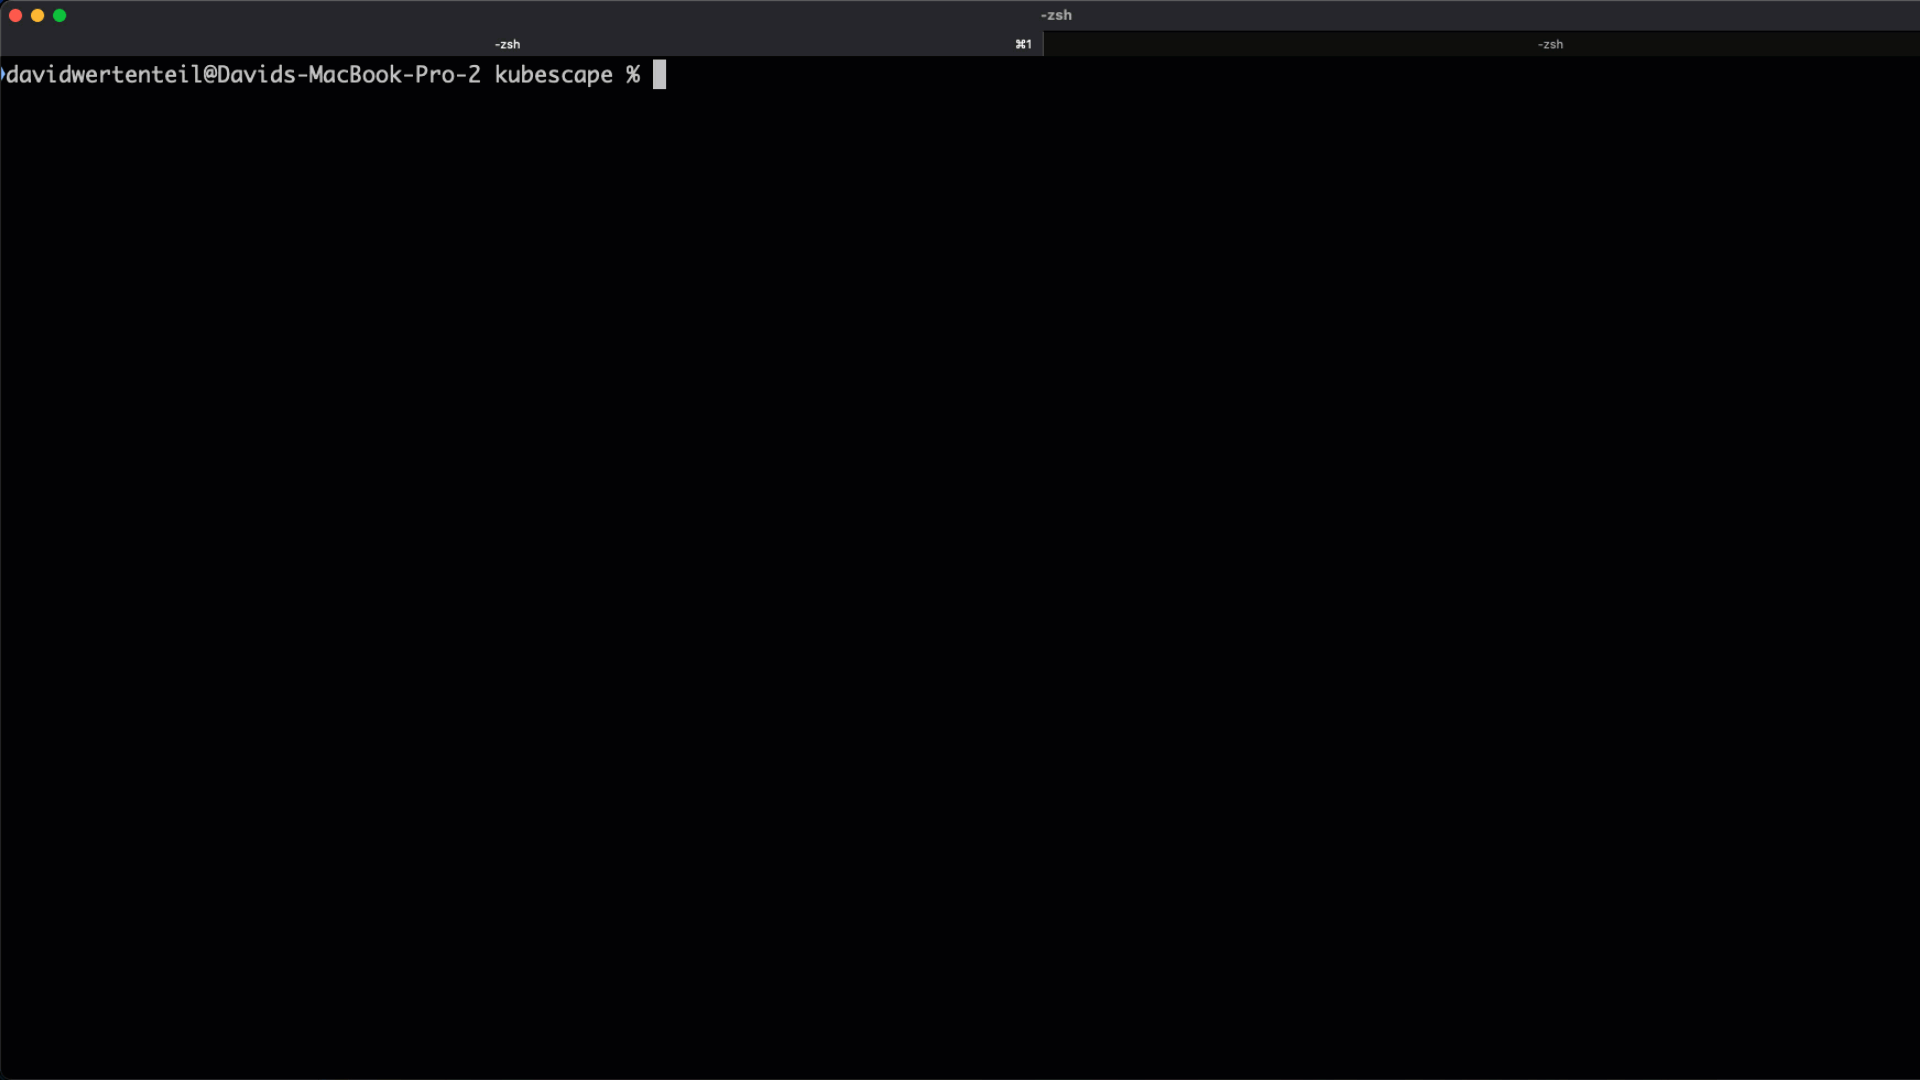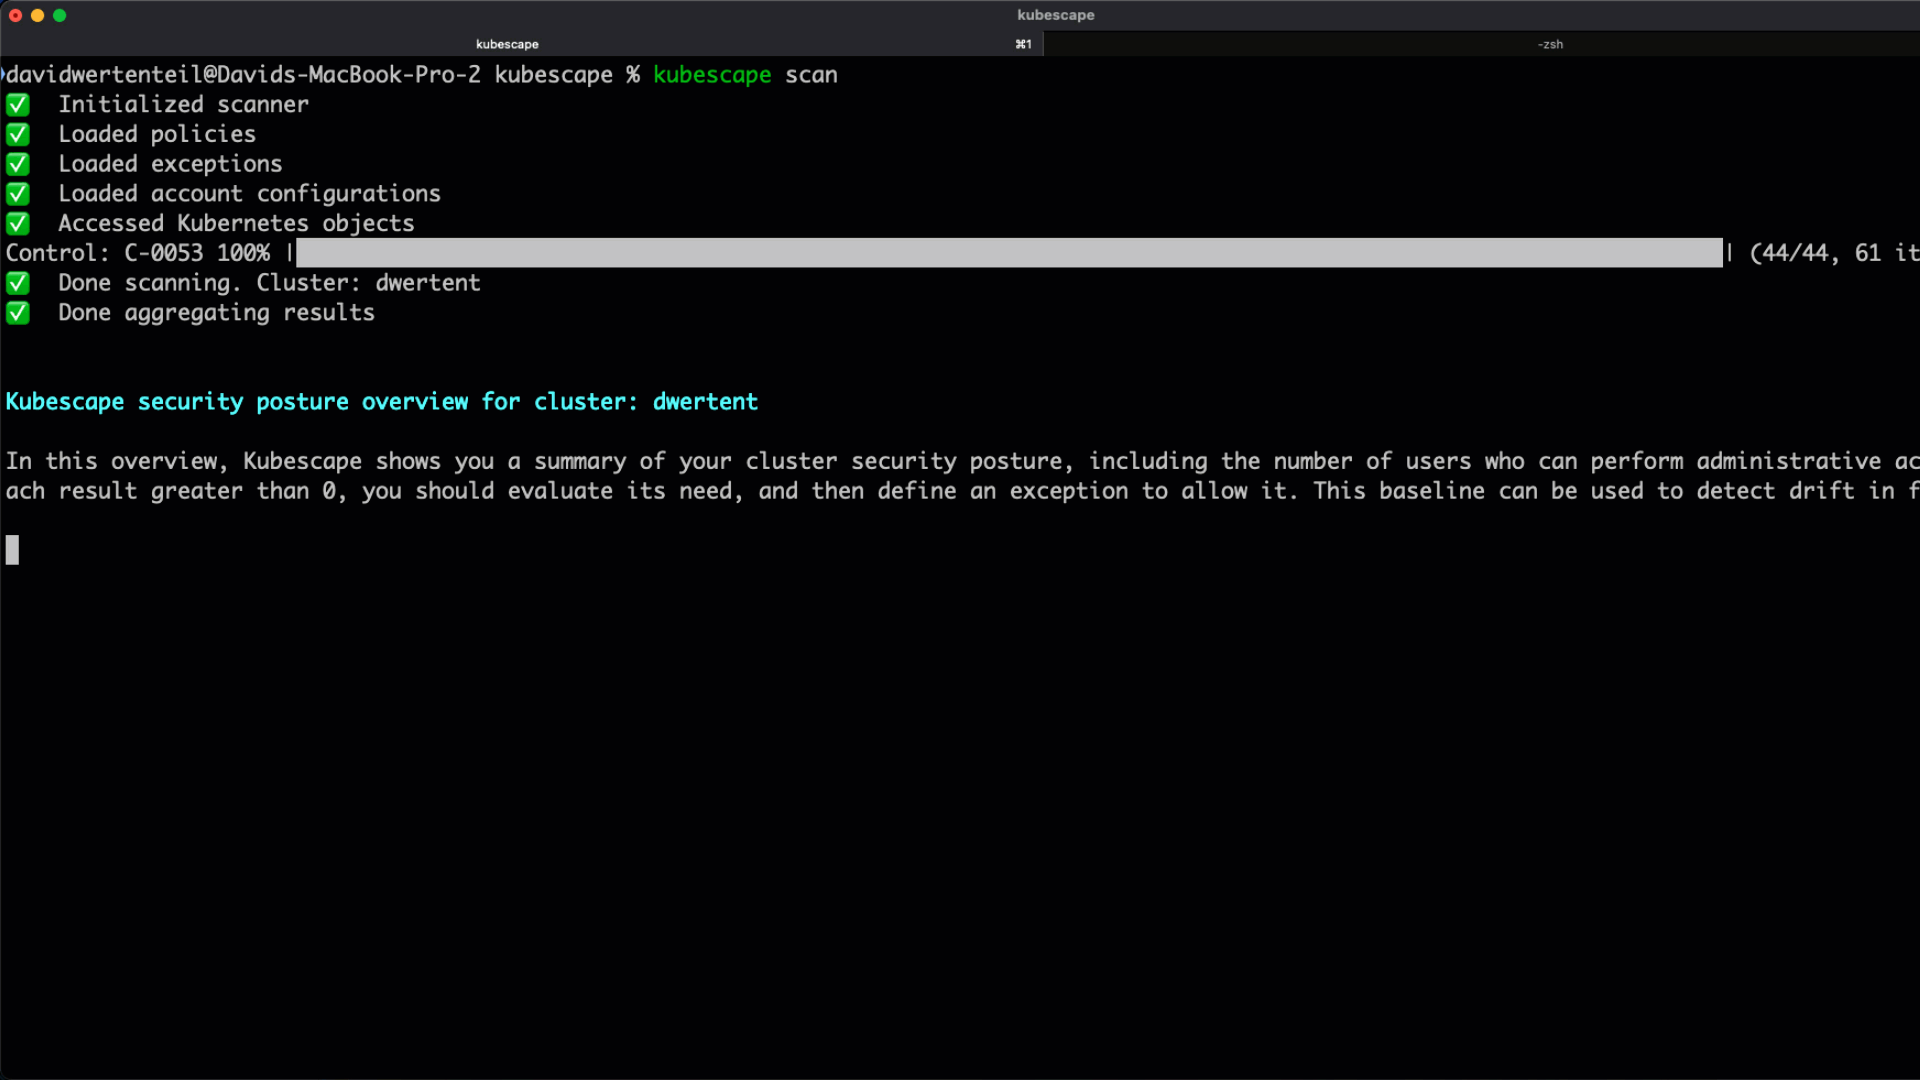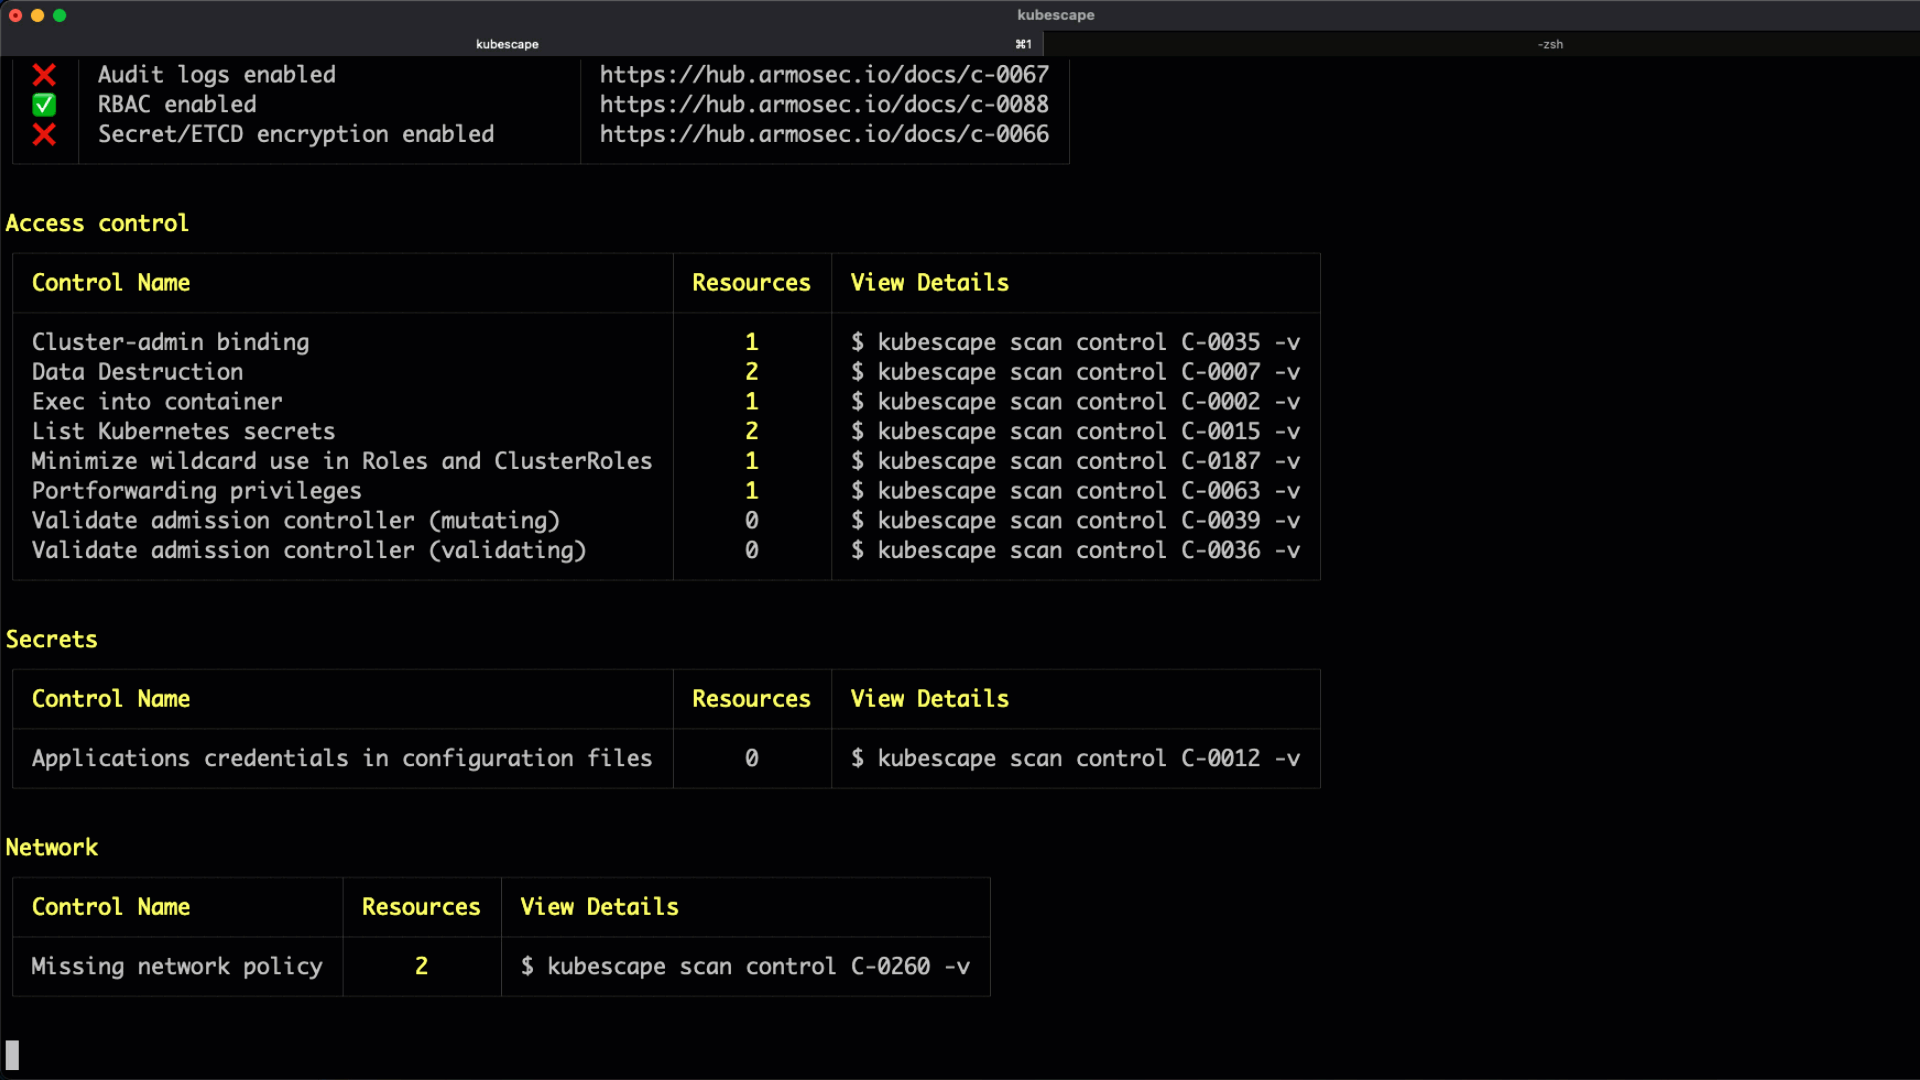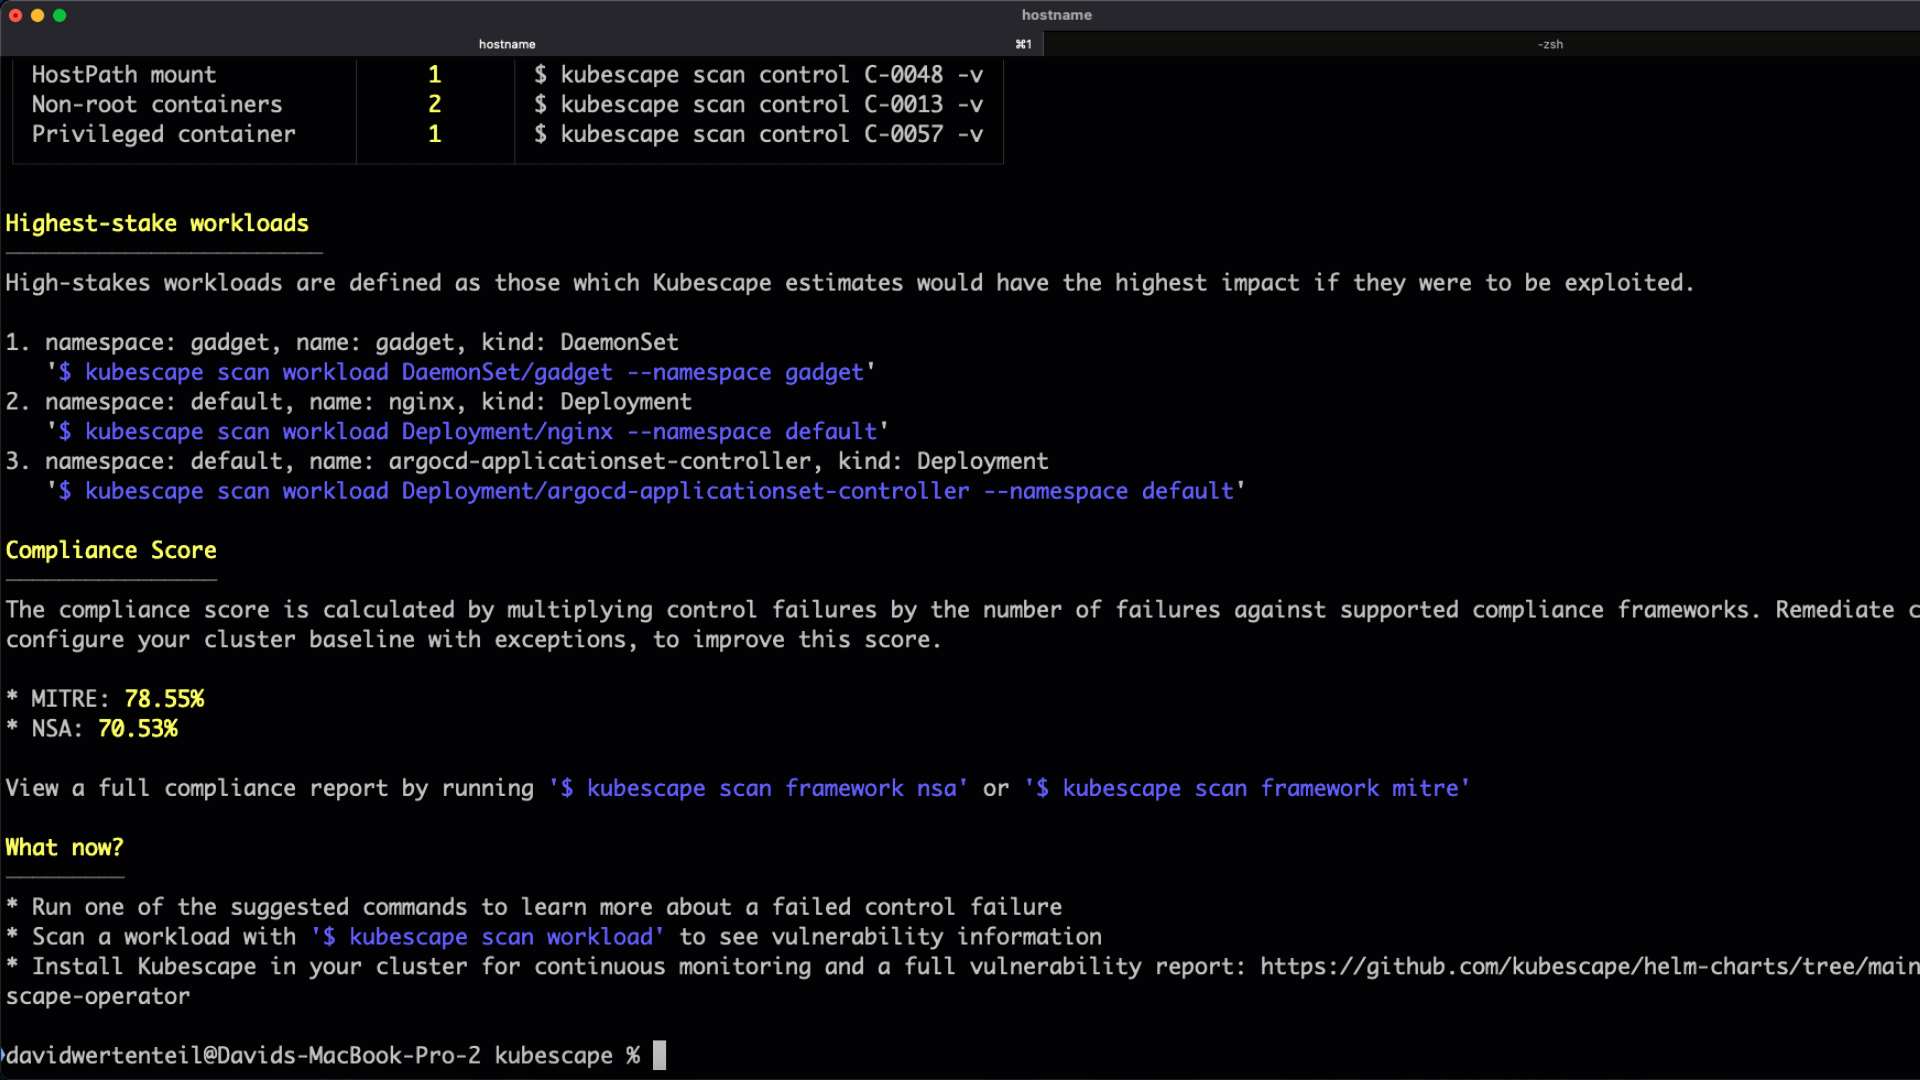 kubescape/kubescape
Open-source Kubernetes security platform scanning clusters, manifests, and images for misconfigurations, vulnerabilities, and compliance against NSA,…
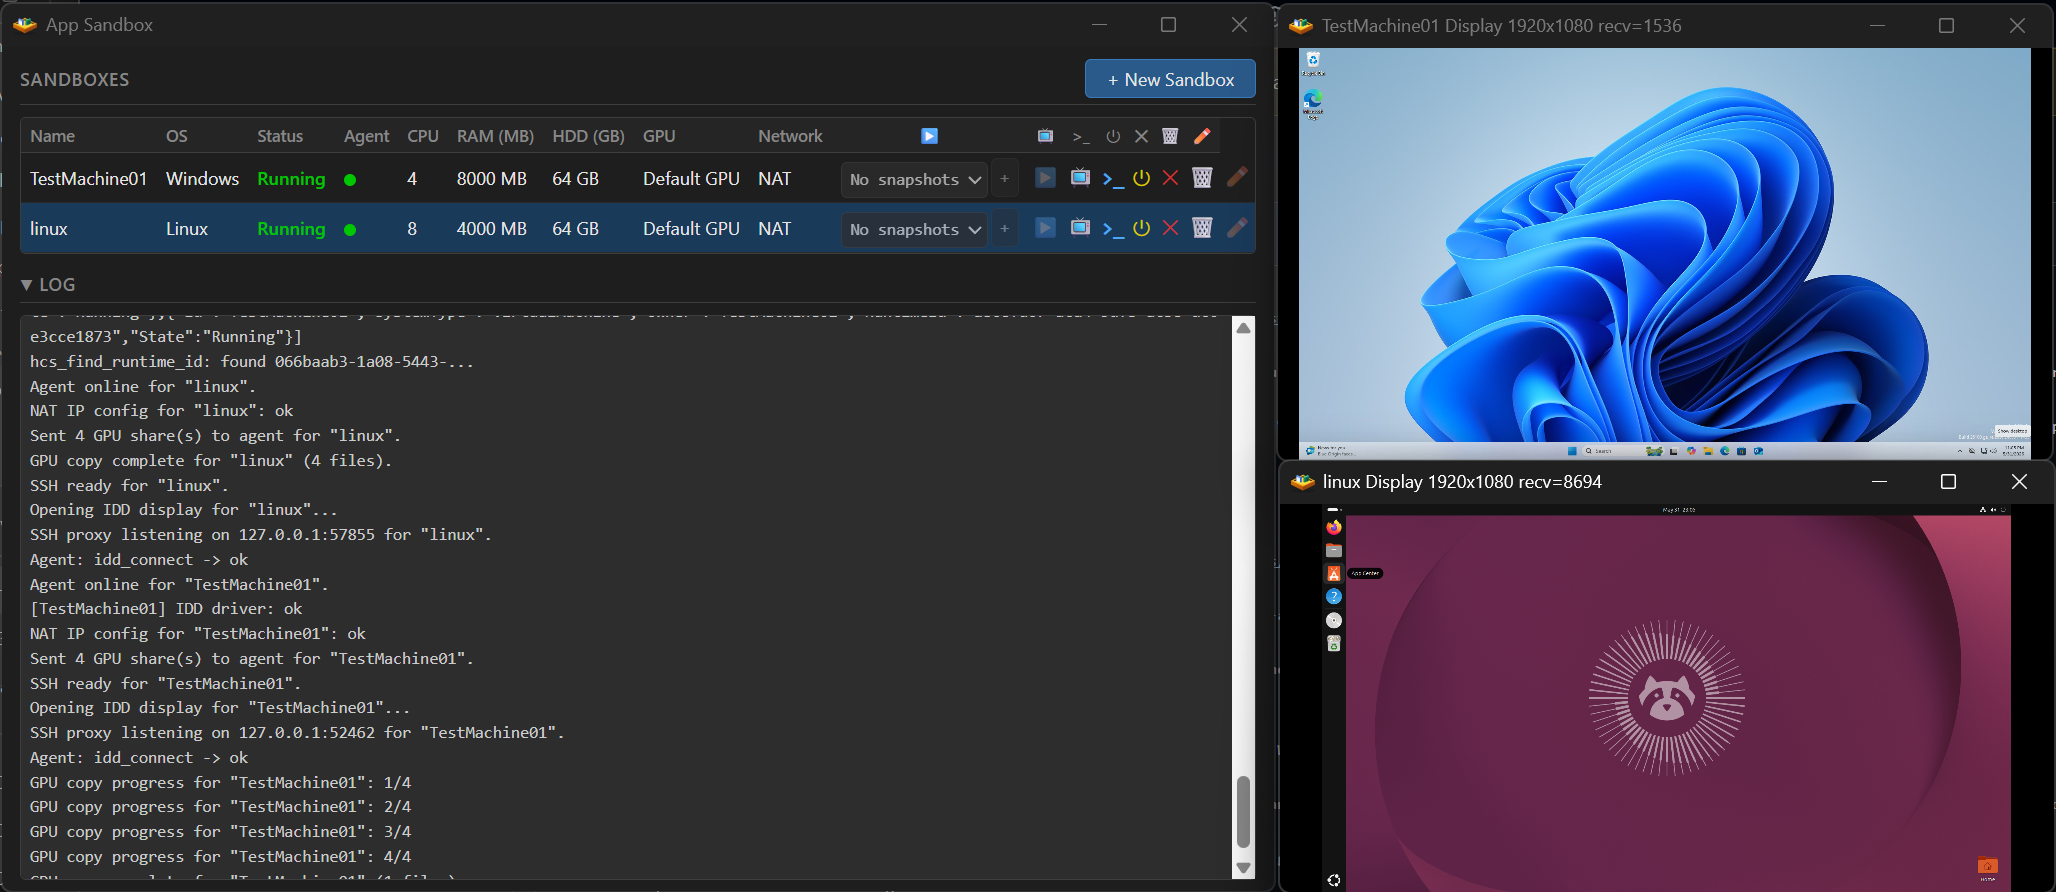 jamesstringer90/appsandbox
Easily create full virtual machines that are sandboxed for development or computer use models.
 finbarr/yolobox
Let your AI go full send. Your home directory stays home.
 cspf-founder/api-scanner-docker
Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …
 dheeraj-jayaswal/cicd-goat-vapt-writeup
Full VAPT writeup of OWASP CICD-Goat — 9 CTFd flags captured, 4 critical + 5 high findings (incl. CVE-2024-23897) mapped to the OWASP Top 10 CI/CD…
 nihal799/zttp
Zero-trust SSH bastion proxy with Vault-backed key management, RBAC policy enforcement, full session recording, and admin TUI for auditable access to…
 teycir/diffcatcher
A Rust CLI tool that recursively discovers Git repositories, captures state changes, generates diffs, extracts code elements with full snippets, and…
 barappteam/nginx-cve-fix
Source-built nginx 1.25.5 container with backported CVE-2026-42945 fix, OpenSSL bump, full provenance chain, and VEX attestation.
 dnscontrol/dnscontrol
Infrastructure as code for DNS!
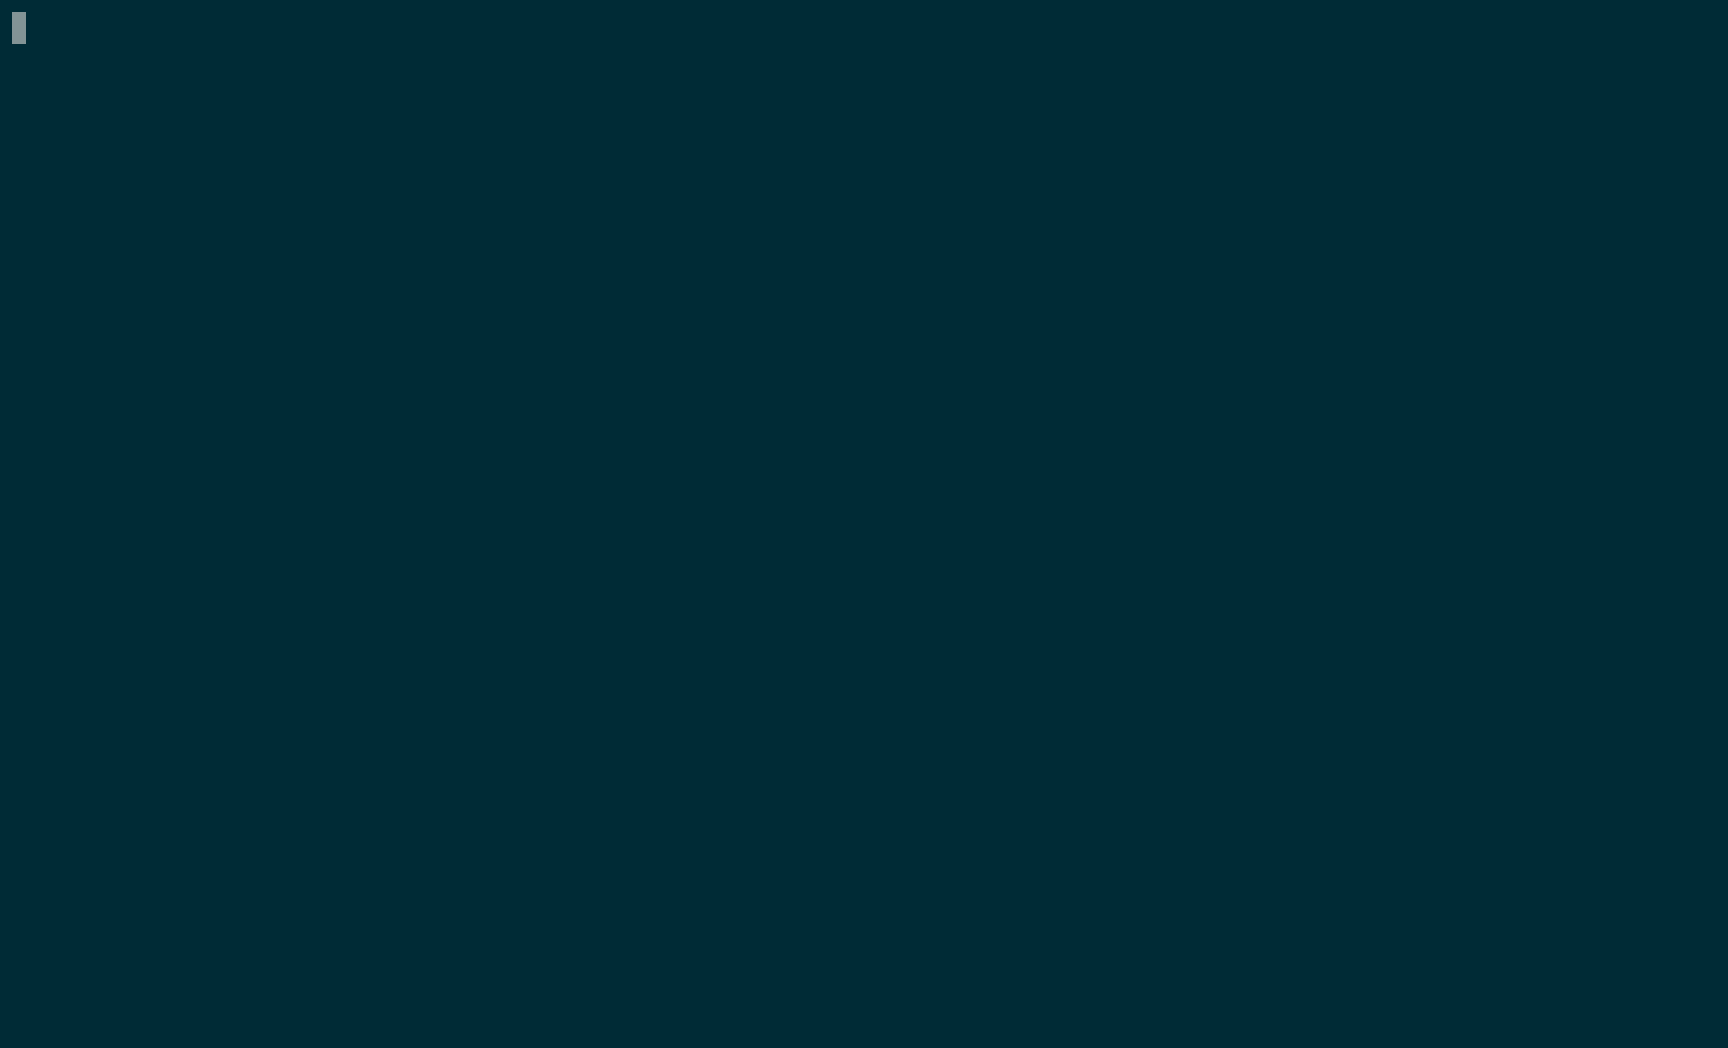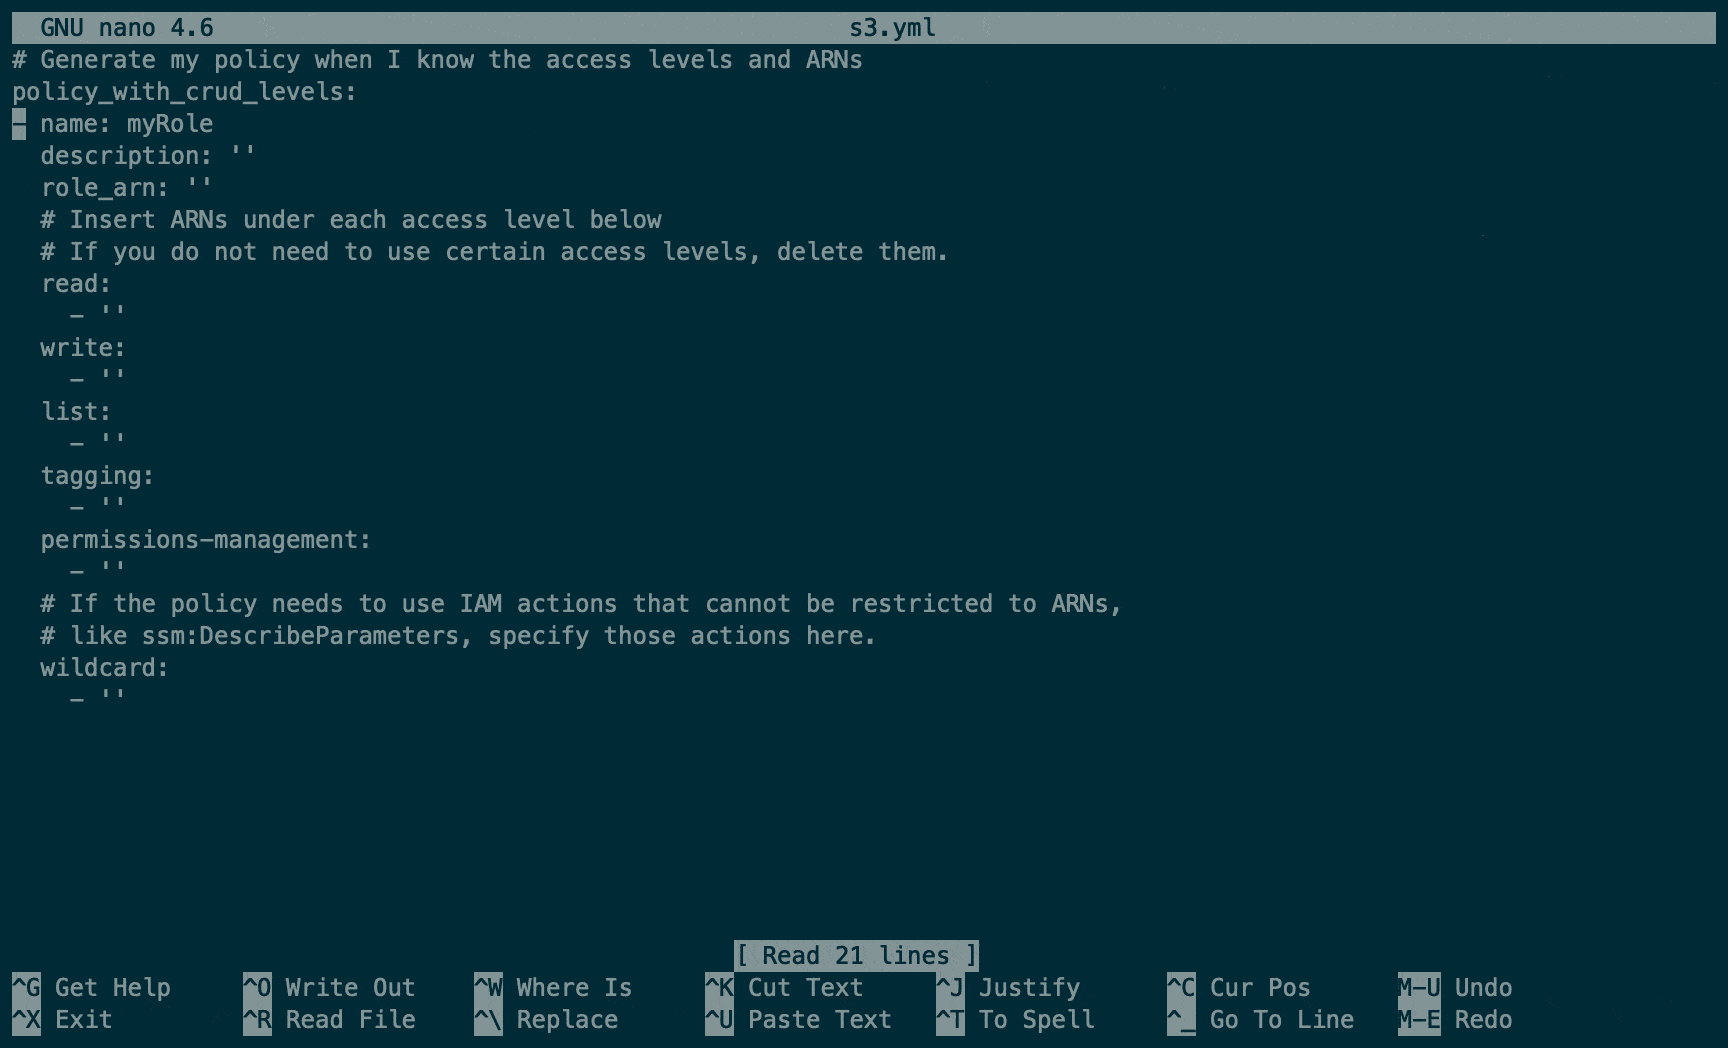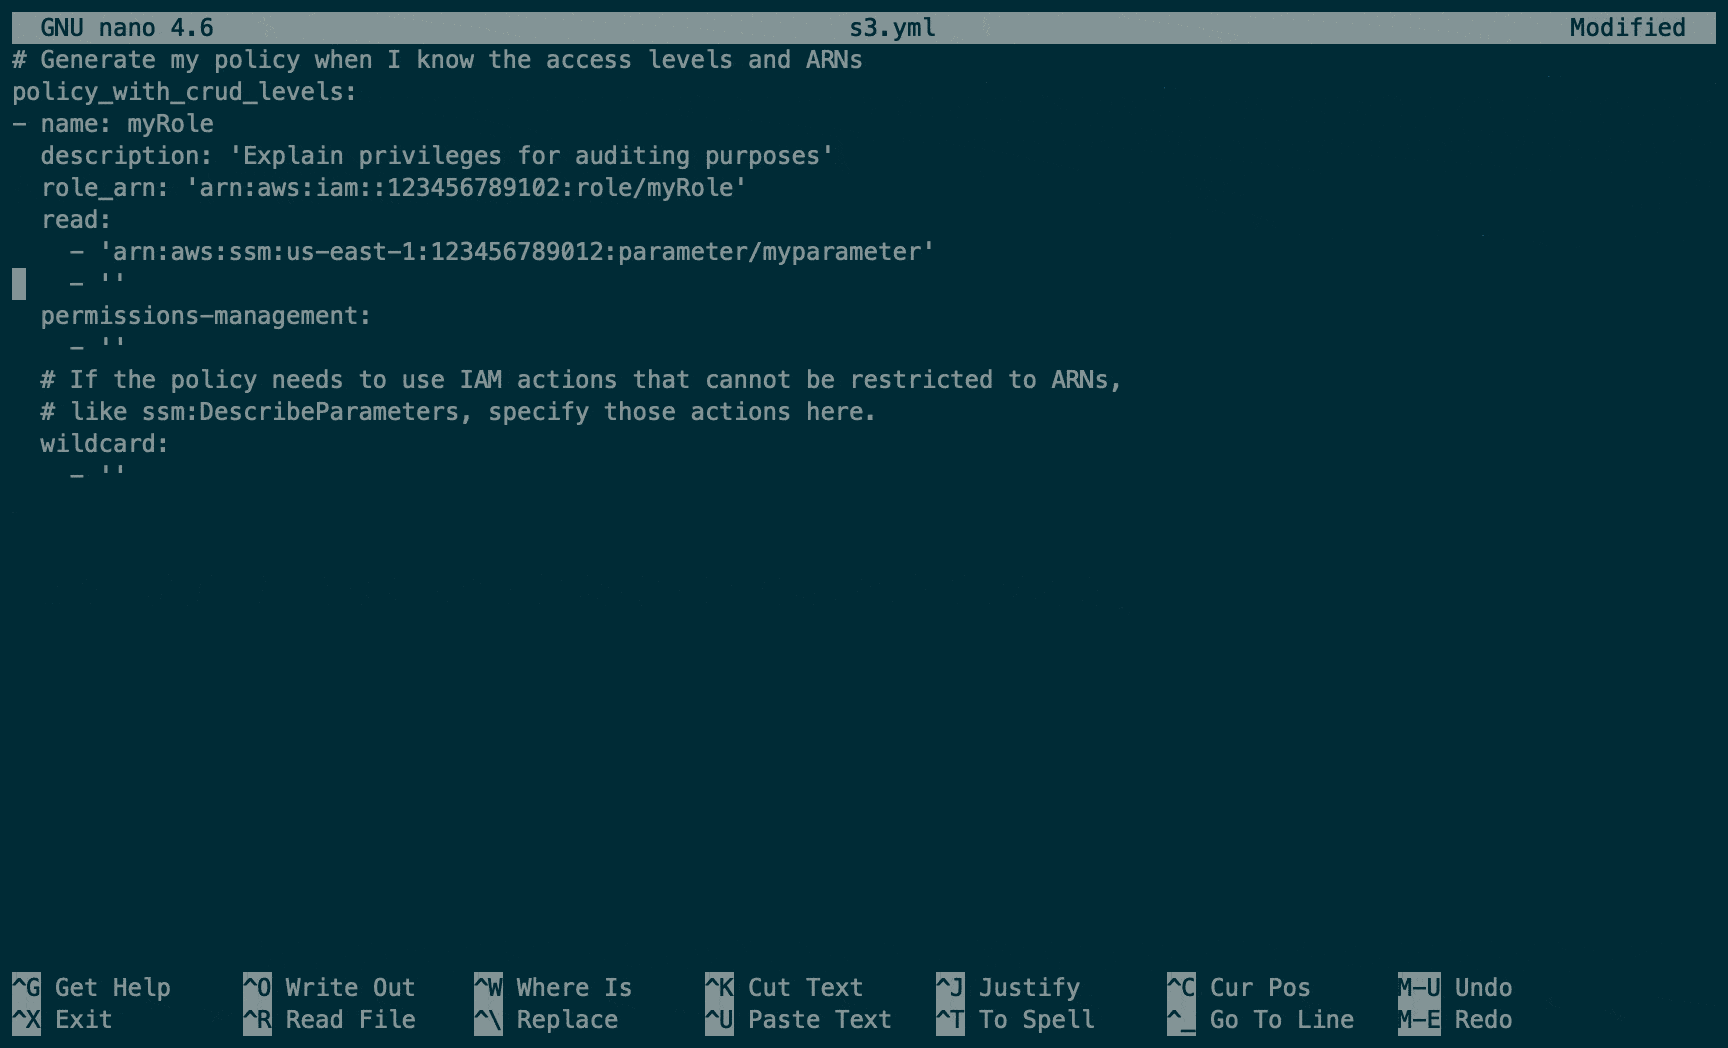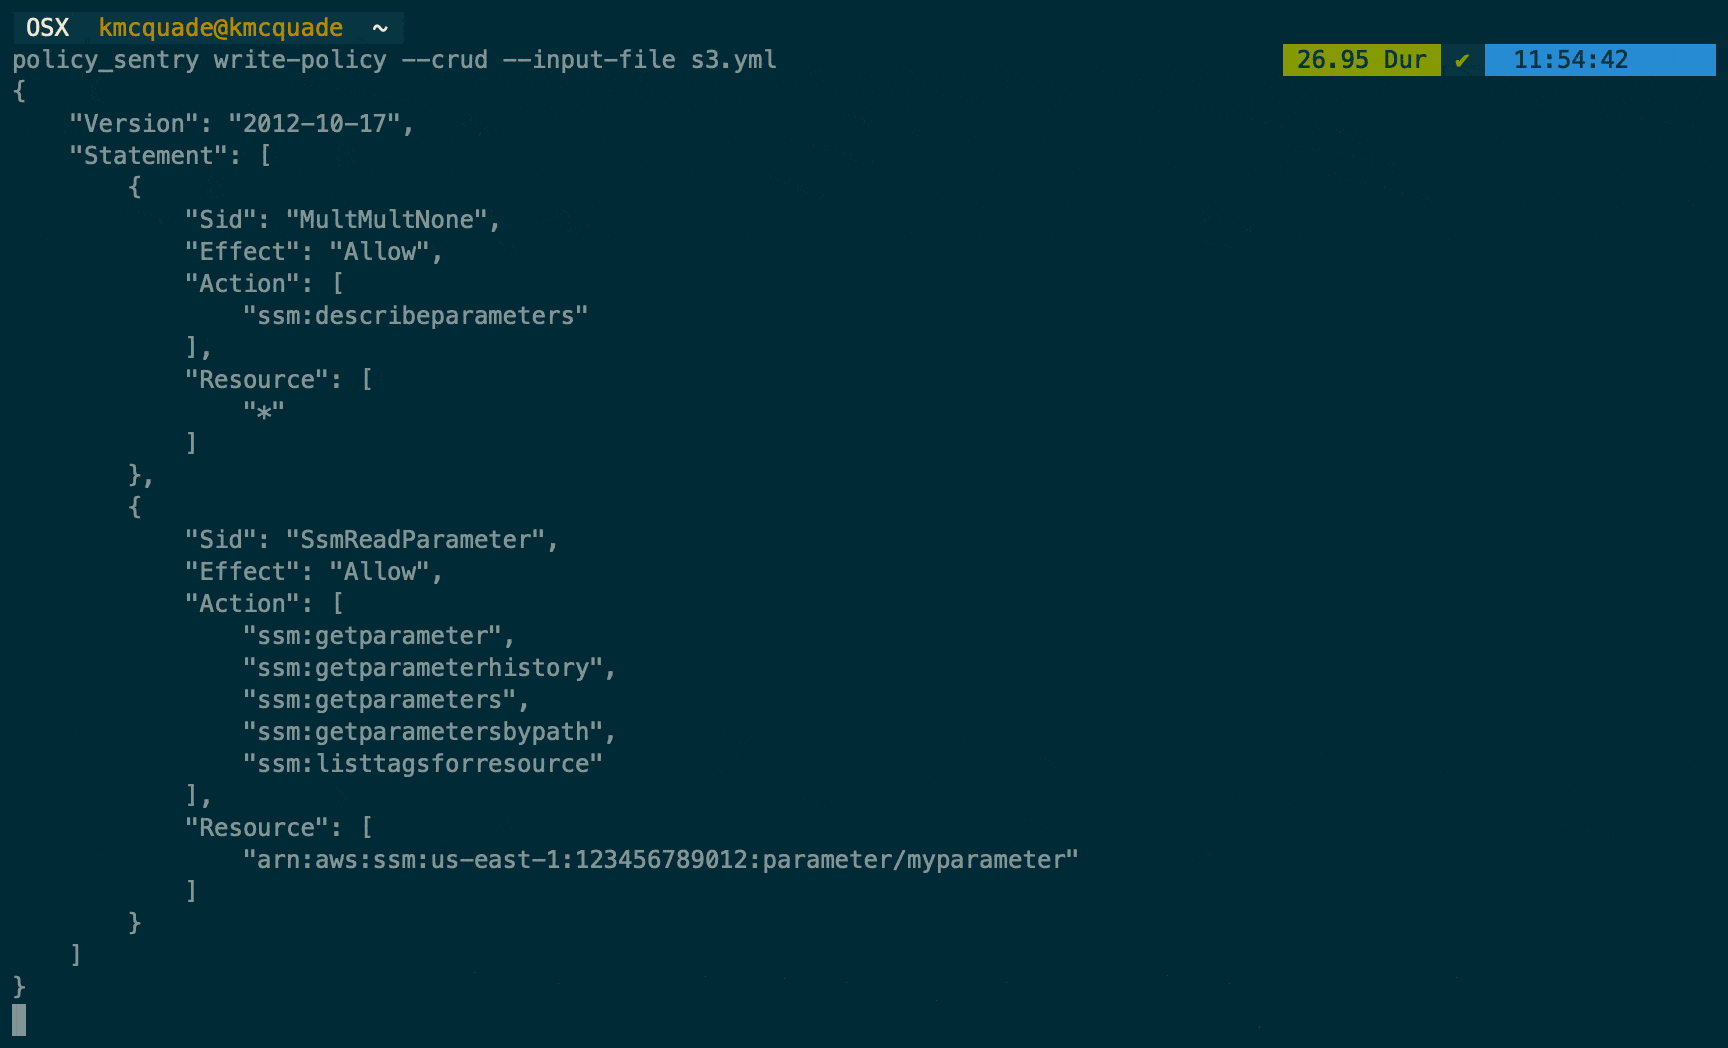 salesforce/policy_sentry
Generates least-privilege AWS IAM policies based on resource ARNs and access levels, automating secure policy creation for cloud infrastructure.
 santhreal/keyhog
Open-source secret scanner in Rust
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
 eduardolat/authkeysync
🔐 Lightweight CLI utility designed to synchronize SSH public keys from remote URLs into local authorized_keys files
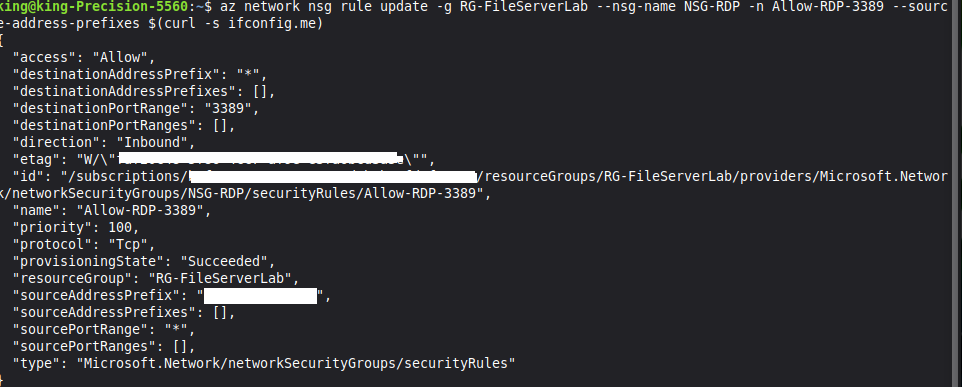 kingsrule50/nessus-vulnerability-scanning-lab
Enterprise vulnerability management on Azure — Terraform-deployed Nessus scanner, credentialed scanning, CVE-2013-3900 remediation with verified…
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
 anchore/anchore-engine
A service that analyzes docker images and scans for vulnerabilities