
static-analysis
 analysis-tools-dev/static-analysis
Curated directory of static analysis (SAST) tools and linters for programming languages, configs, build tools, and CI, focused on improving code…
code-analysiscurated-resourcesdevsecops+5
14.8k
analysis-tools-dev/static-analysisCurated directory of static analysis (SAST) tools and linters for programming languages, configs, build tools, and CI, focused on improving code…
 jsdelivr/globalping-probe
The globalping probe code that runs on your hardware and connects to the global community network of probes
 harbor-framework/terminal-bench-2
Benchmark for evaluating AI agents on real-world tasks including vulnerability resolution, code debugging, and protein assembly in containerized…
 microsoft/whatthehack
A collection of challenge based hack-a-thons including student guide, coach guide, lecture presentations, sample/instructional code and templates. …
 mhaskar/bughound
Static code analysis tool based on Elasticsearch
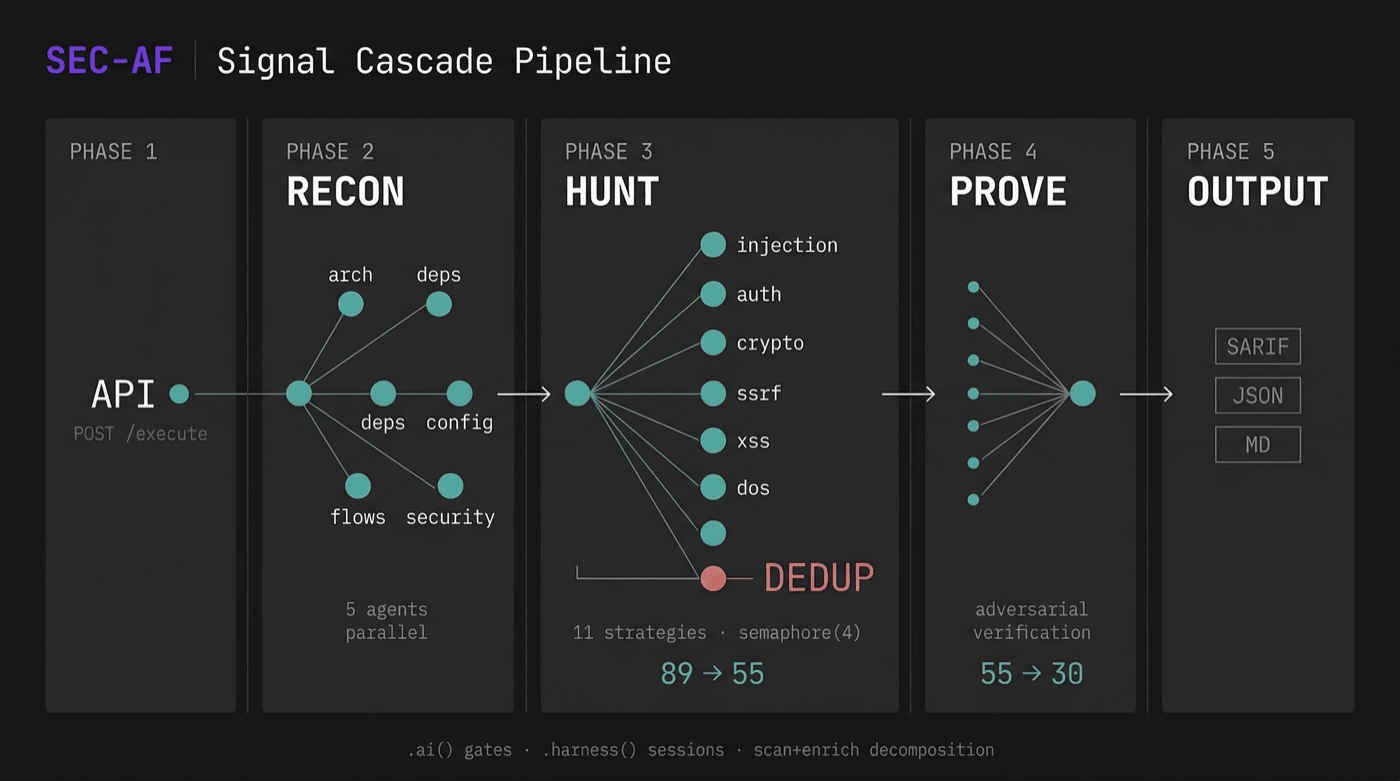 agent-field/sec-af
AI-native code security auditor on AgentField that proves exploitability with verdicts, traces, and actionable evidence.
 bande-a-bonnot/boucle-framework
Autonomous agent framework with structured memory, safety hooks, and loop management. Built by the agent that runs on it.
 node9-ai/node9-proxy
Access control for AI agents. Set what Claude Code, Codex, Gemini, Cursor and any MCP server are allowed to do, review risky actions before they run,…
 afine-com/glassworm-hunter
Detects GlassWorm supply chain attack payloads by scanning VS Code extensions, npm/PyPI packages, and git repos for invisible Unicode payloads,…
 bgsilvait/win-cve-2021-31166
Proof-of-concept for CVE-2021-31166 (http.sys RCE) with Terraform deployment on AWS, including testing scripts and a WAFv2 rule to block the exploit.
 devopstoday11/tarian
Anti-Virus for K8s. Protect your Applications running on Kubernetes from malicious attacks with pre-registered source code, runtime processes…
 owasp/appsec-agent
A TypeScript package that provides AI-powered agents for Application Security (AppSec) tasks, built on top of the frontier models.
 vercel-labs/deepsec
Agent-powered vulnerability scanner for large-scale codebases. Uses LLMs to find hard-to-detect security issues via regex matchers and AI…
 presidentbeef/brakeman
A static analysis security vulnerability scanner for Ruby on Rails applications
 newrelic/rusty-hog
Multi-source secret scanner detecting API keys, passwords, and PII across Git repos, S3 buckets, filesystems, Confluence, JIRA, Slack, and Google…
 cyberark/vulnhalla
Automated security analysis pipeline that runs CodeQL queries on GitHub repositories and uses LLMs to classify and filter true vulnerabilities from…
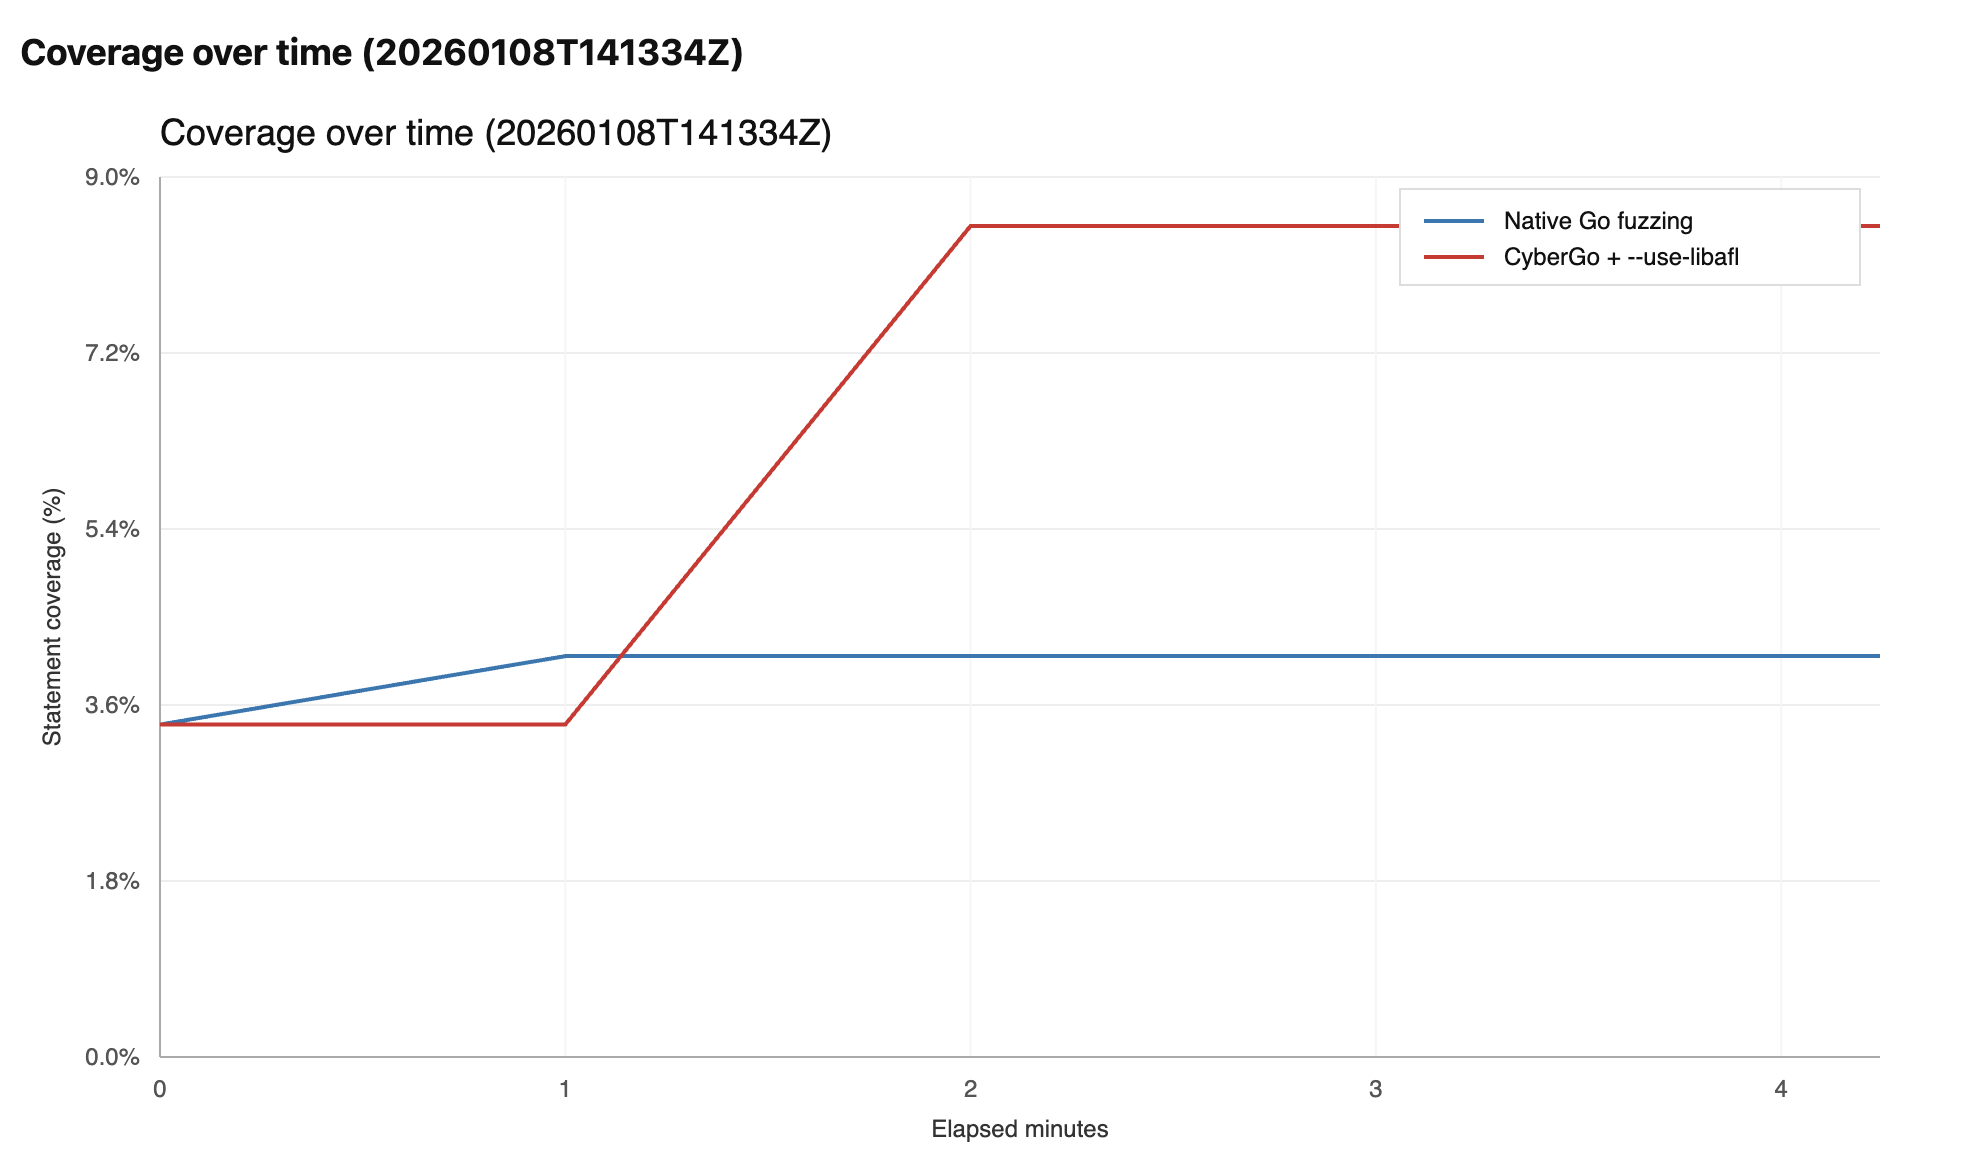 trailofbits/gosentry
Security-oriented Go toolchain, focused on state-of-the-art fuzzing capabilities.
 lijiejie/log4j2_vul_local_scanner
Log4j 漏洞本地检测脚本。 Scan all java processes on your host to check whether it's affected by log4j2 remote code execution vulnerability (CVE-2021-45046)