React2shell-CVE-2025-55182-checker

Passive CVE-2025-55182 detection tool for vulnerable React Server Components. Scans package.json, JavaScript bundles, HTTP headers, and API endpoints…

Passive CVE-2025-55182 detection tool for vulnerable React Server Components. Scans package.json, JavaScript bundles, HTTP headers, and API endpoints…


Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.

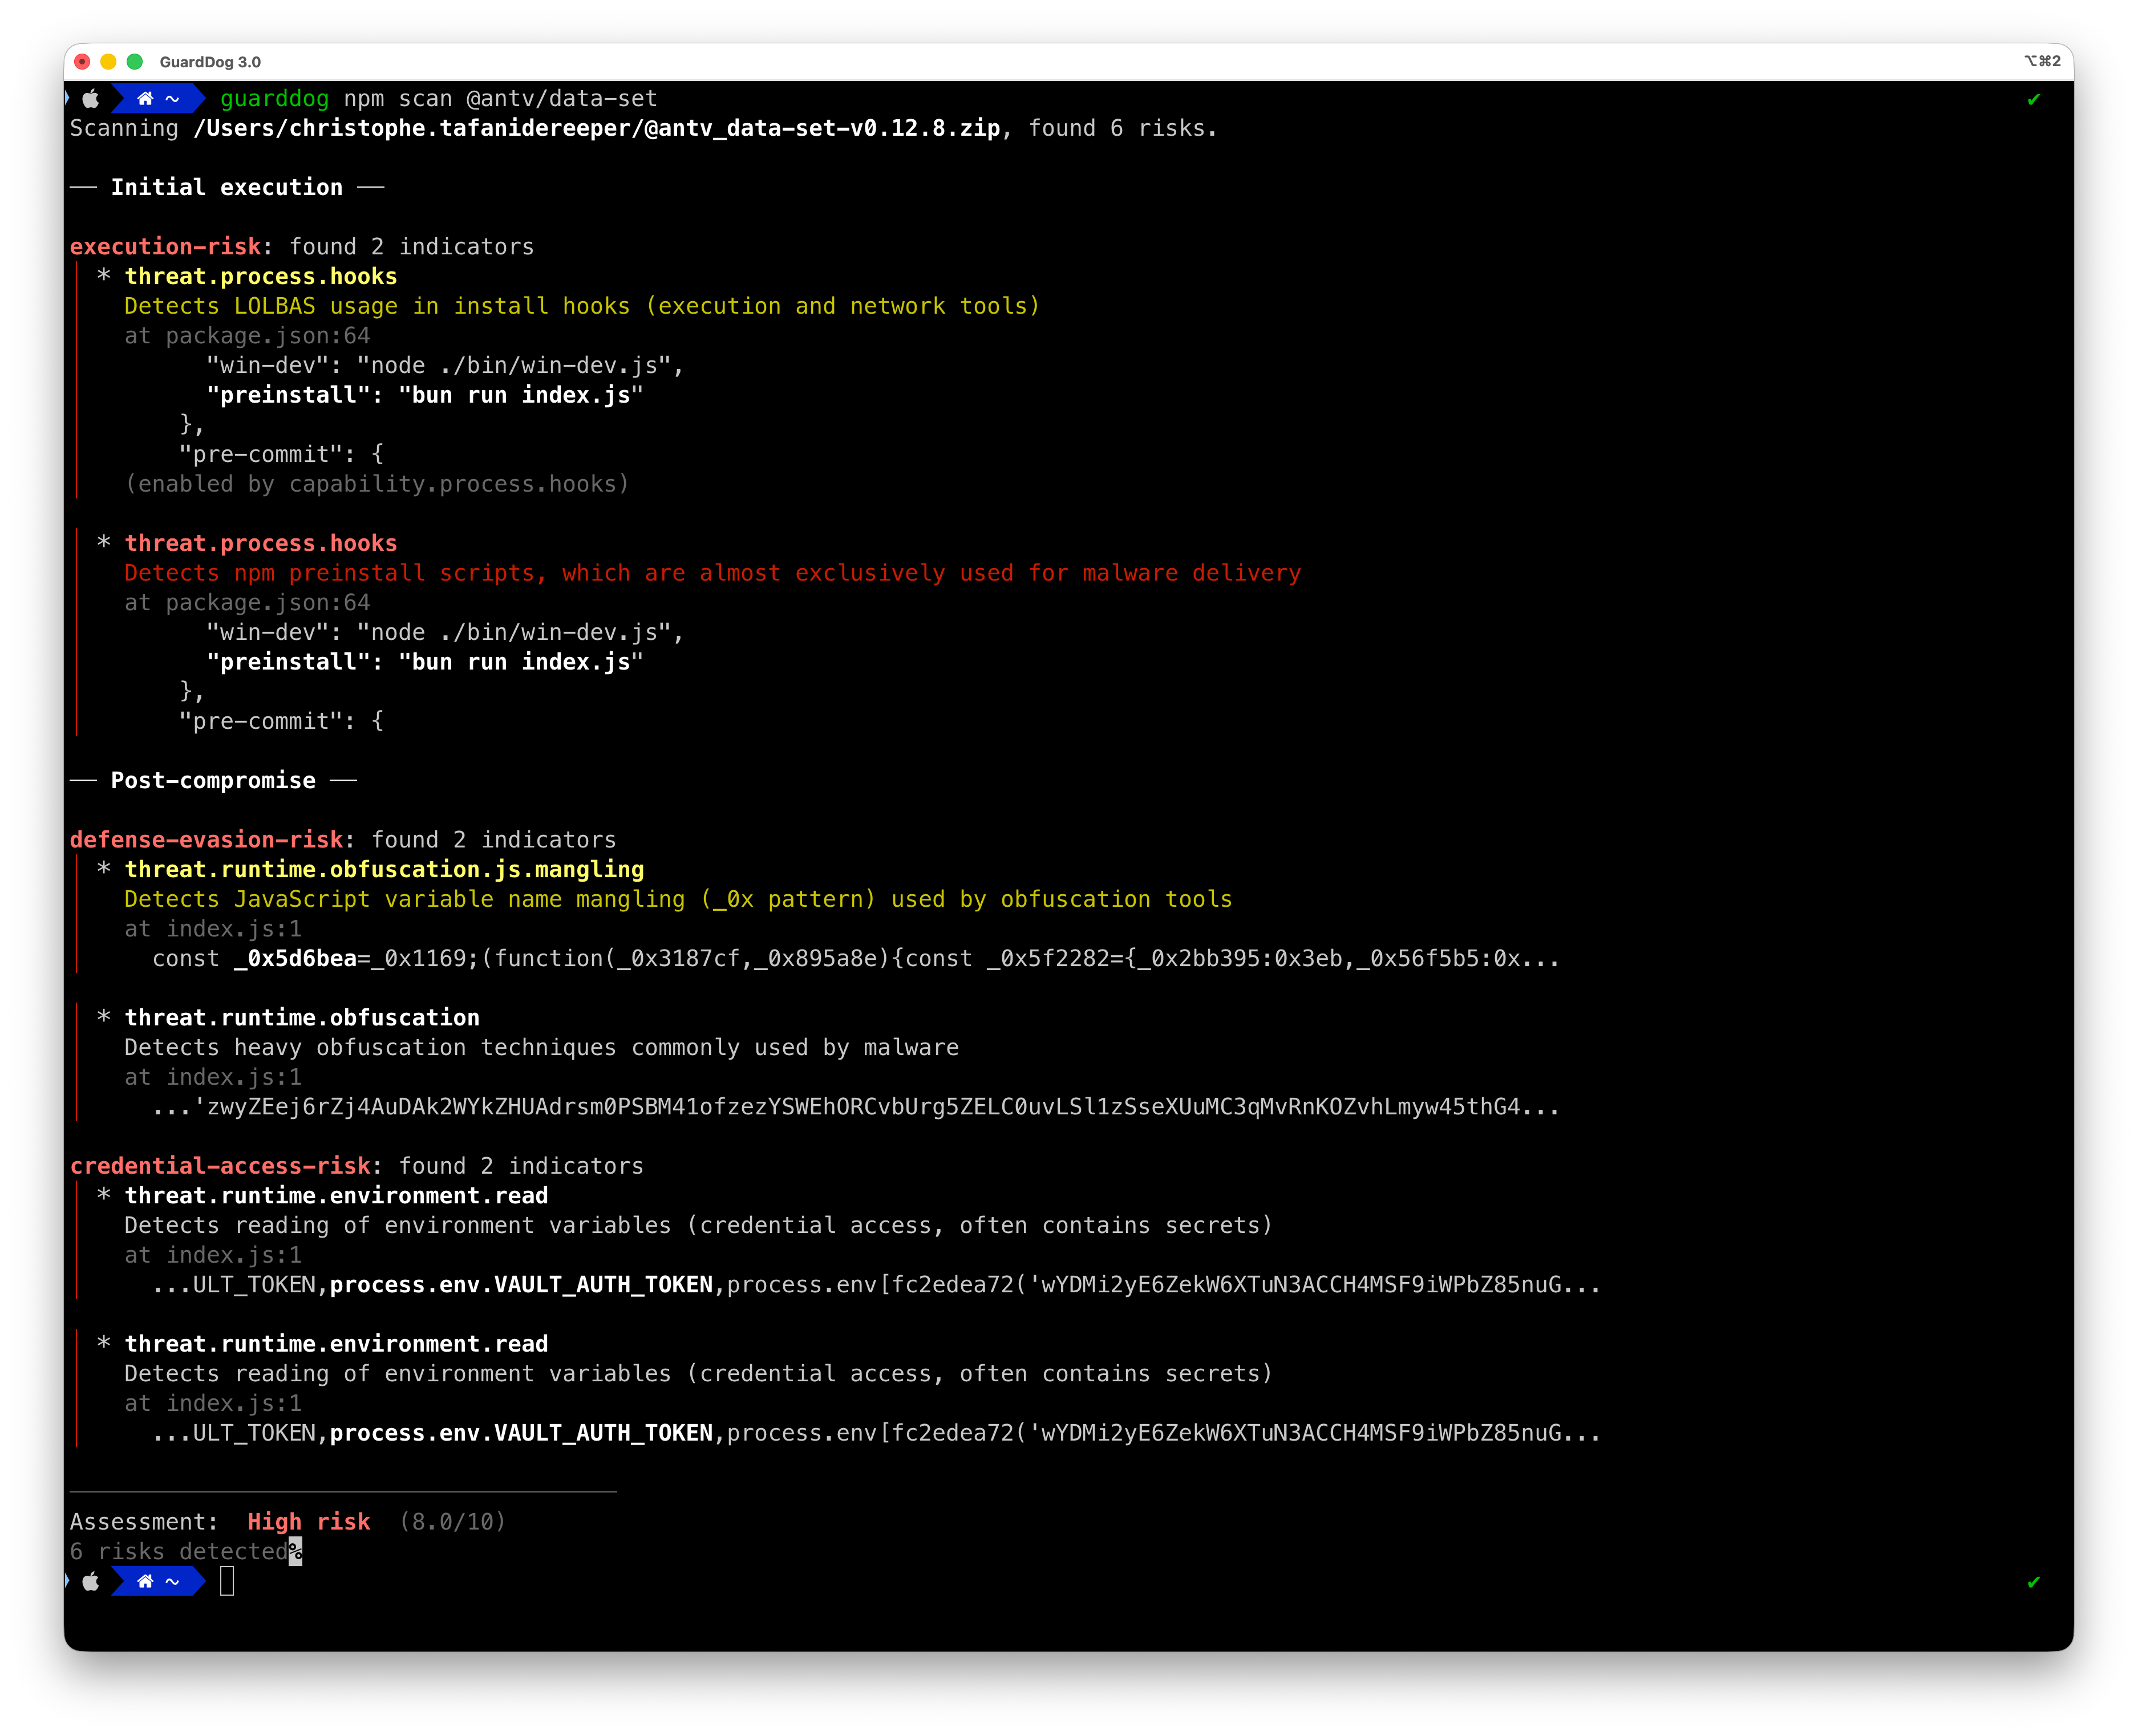
🐍 🔍 GuardDog is a CLI tool to Identify malicious PyPI and npm packages

Identify hardcoded secrets in static structured text

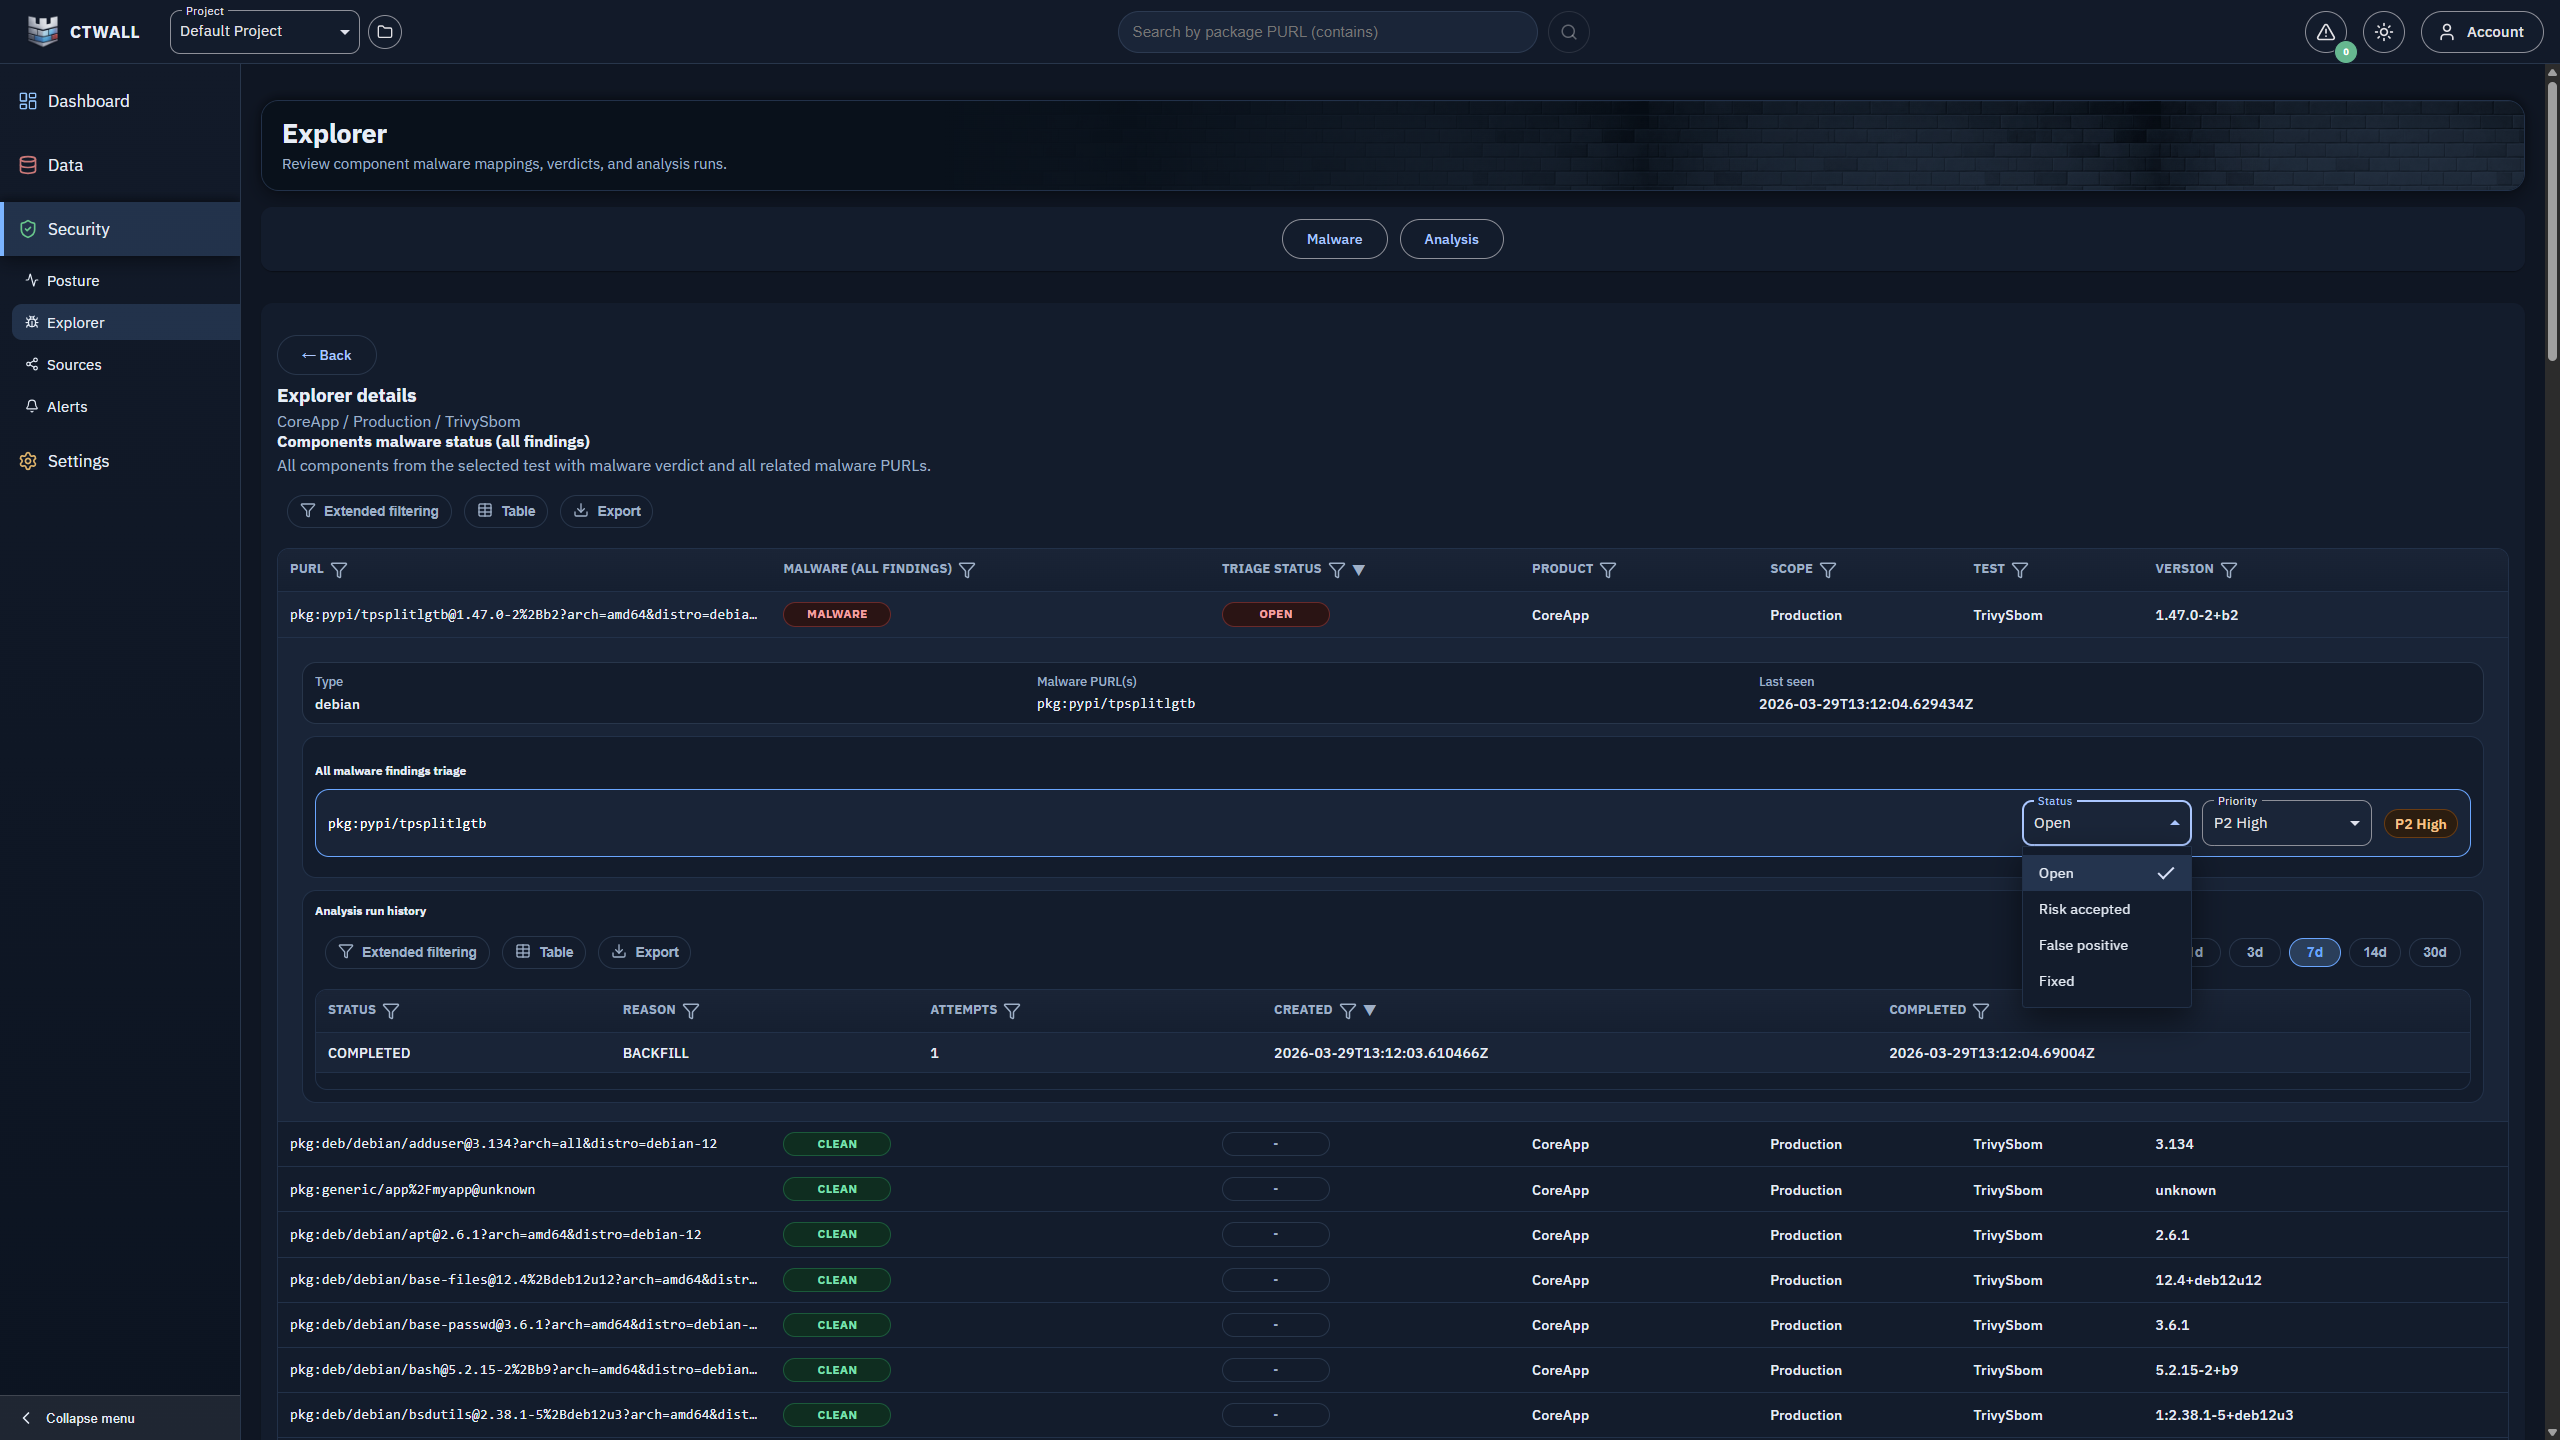
CTWall (ChainThreatWall) platform helps Security, DevOps, and Product teams make risk decisions faster by using SBOM/BOM data to identify malware in…

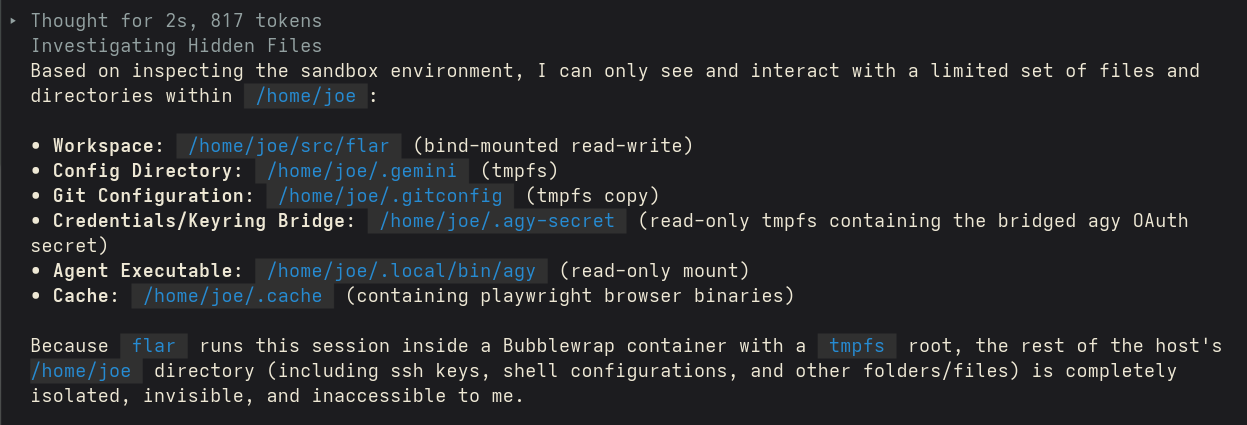
Lightweight CLI tool that runs AI coding agents inside isolated Bubblewrap sandboxes with strict filesystem, network, and credential isolation to…

Go-based automation tool that scans GitHub repositories for vulnerable Next.js versions (CVE-2025-66478) and automatically creates pull requests with…

Script to audit GitHub Action Workflow files for potential vulnerabilities.

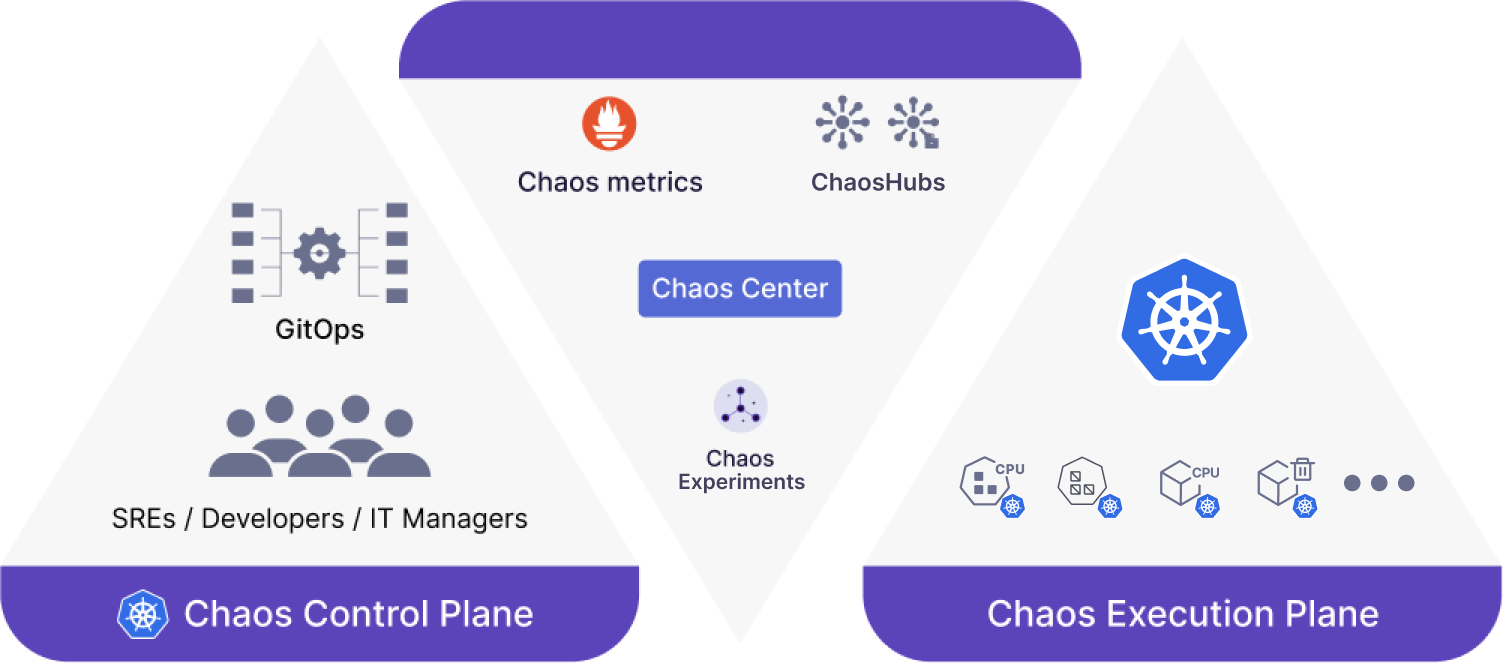
Cloud-native chaos engineering platform for Kubernetes with fault injection, workflow orchestration, and steady-state validation to surface system…

Intelligent Component Analysis platform that leverages SBOMs to identify and reduce software supply chain risk through continuous vulnerability…

🛡️ Scan and assess vulnerabilities in Next.js/Waku with the CVE-2025-55182-Scanner, combining static and dynamic analysis for robust security.

Running OWASP cve-lite-cli against the pi monorepo: scan journey and key finding (vitest CVE-2026-47429).

Integration of Clair and Docker Registry

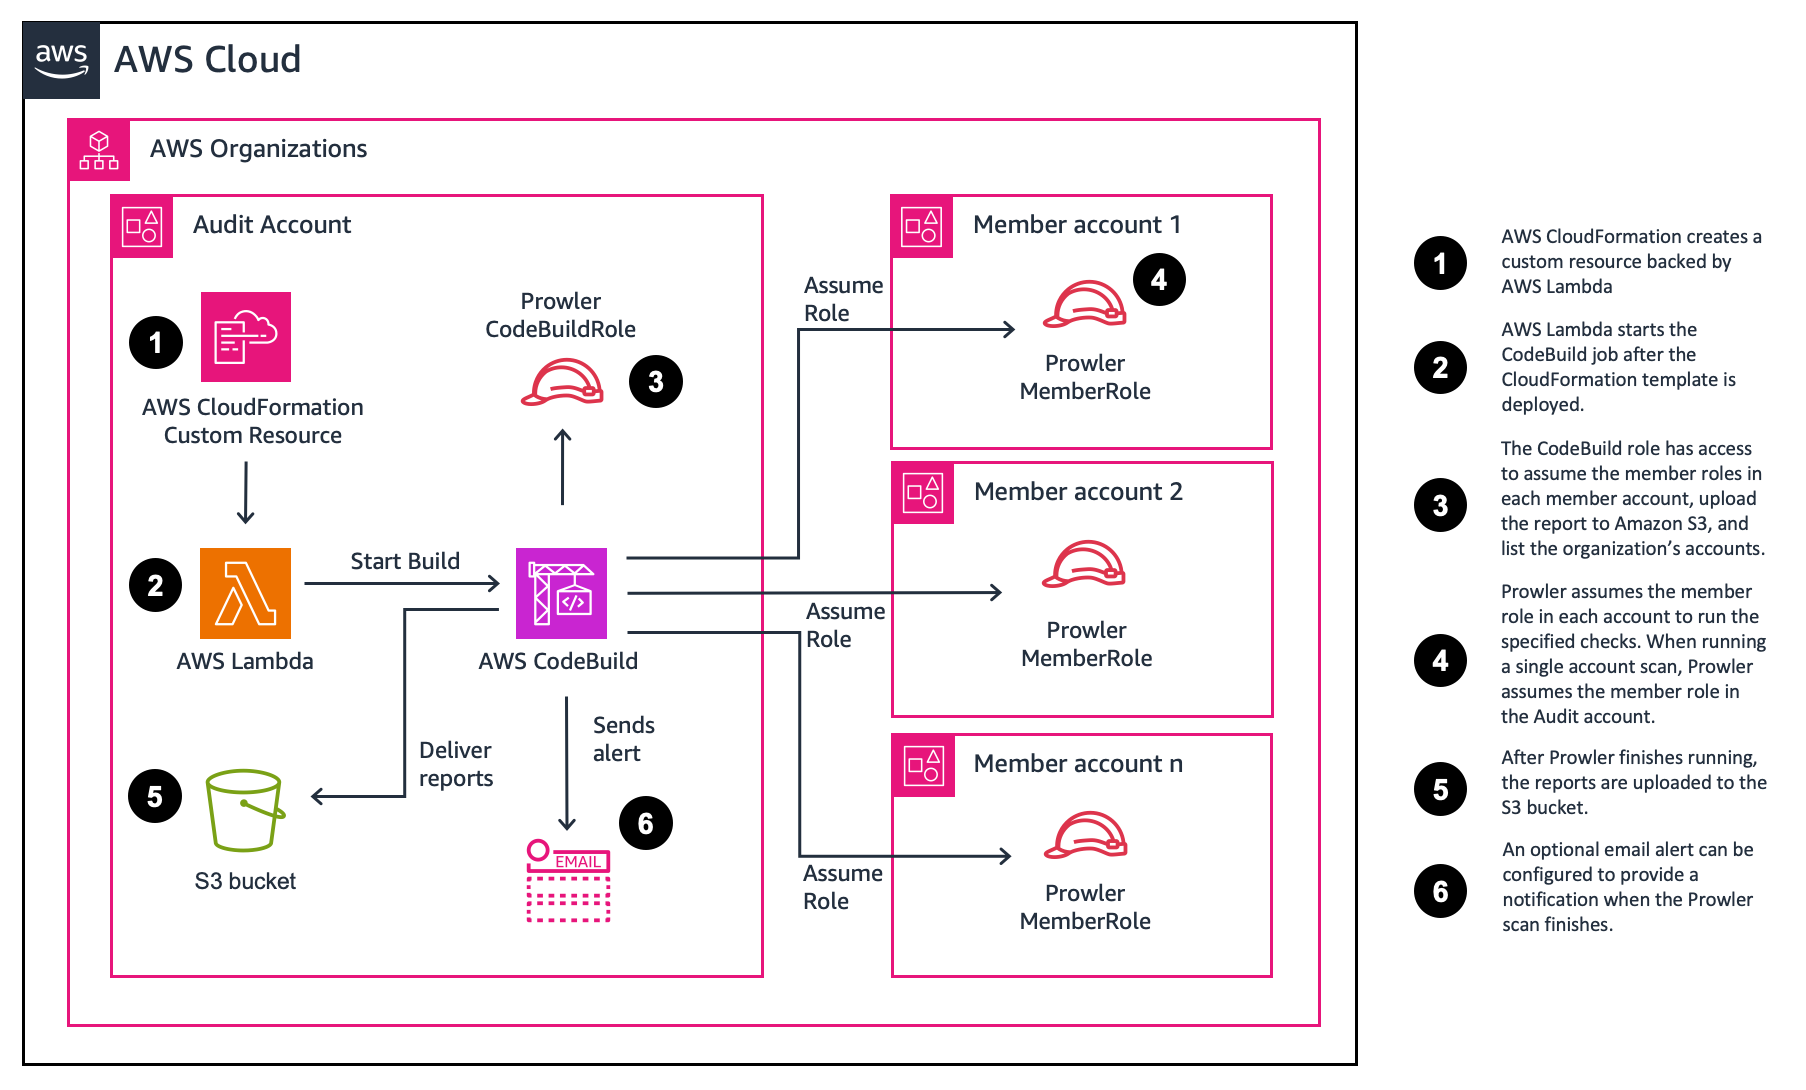
An AWS tool to help you create a point in time assessment of your AWS account using Prowler.

A passive detection tool for identifying potential exposure to CVE-2026-24061 in GNU inetutils telnet installations

A source code static analysis platform for AppSec enthusiasts.

Pluggable linting tool to prevent committing credential.