
flar
 swelljoe/flar
Lightweight CLI tool that runs AI coding agents inside isolated Bubblewrap sandboxes with strict filesystem, network, and credential isolation to…
ai-securitycontainer-securitydevsecops+5
552 months ago
swelljoe/flarLightweight CLI tool that runs AI coding agents inside isolated Bubblewrap sandboxes with strict filesystem, network, and credential isolation to…
 knqyf263/go-mal-pkgs
A security tool to detect malicious Go packages by verifying checksums in go.sum against the original source code
 jibaru/cve-2025-66478-github-patcher
Go-based automation tool that scans GitHub repositories for vulnerable Next.js versions (CVE-2025-66478) and automatically creates pull requests with…
 google/capslock
CLI tool for analyzing Go package capabilities by tracing transitive calls to privileged standard library operations, enabling supply chain risk…
 tanmayshahane/kyubisweep
A lightweight, cross-platform CLI tool that scans your filesystem to detect exposed secrets, API keys, and tokens. Built with Go for maximum…
 hillu/local-log4j-vuln-scanner
[Moved to Codeberg] Simple local scanner for vulnerable log4j instances
 ustayready/outpost
AWS Testing and Reporting Management Tool
 optiopay/klar
Integration of Clair and Docker Registry
 rapticore/orenpmguard
Defense Against the Shai-Hulud Supply Chain Attack
 bearer/bearer
Code security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.
 boratanrikulu/gobee
Write your BPF programs in Go, not C. gobee transpiles a Go subset to BPF C and generates typed cilium/ebpf bindings.
 dependency-check/dependencycheck
OWASP dependency-check is a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies.
 openbreach/canop
Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
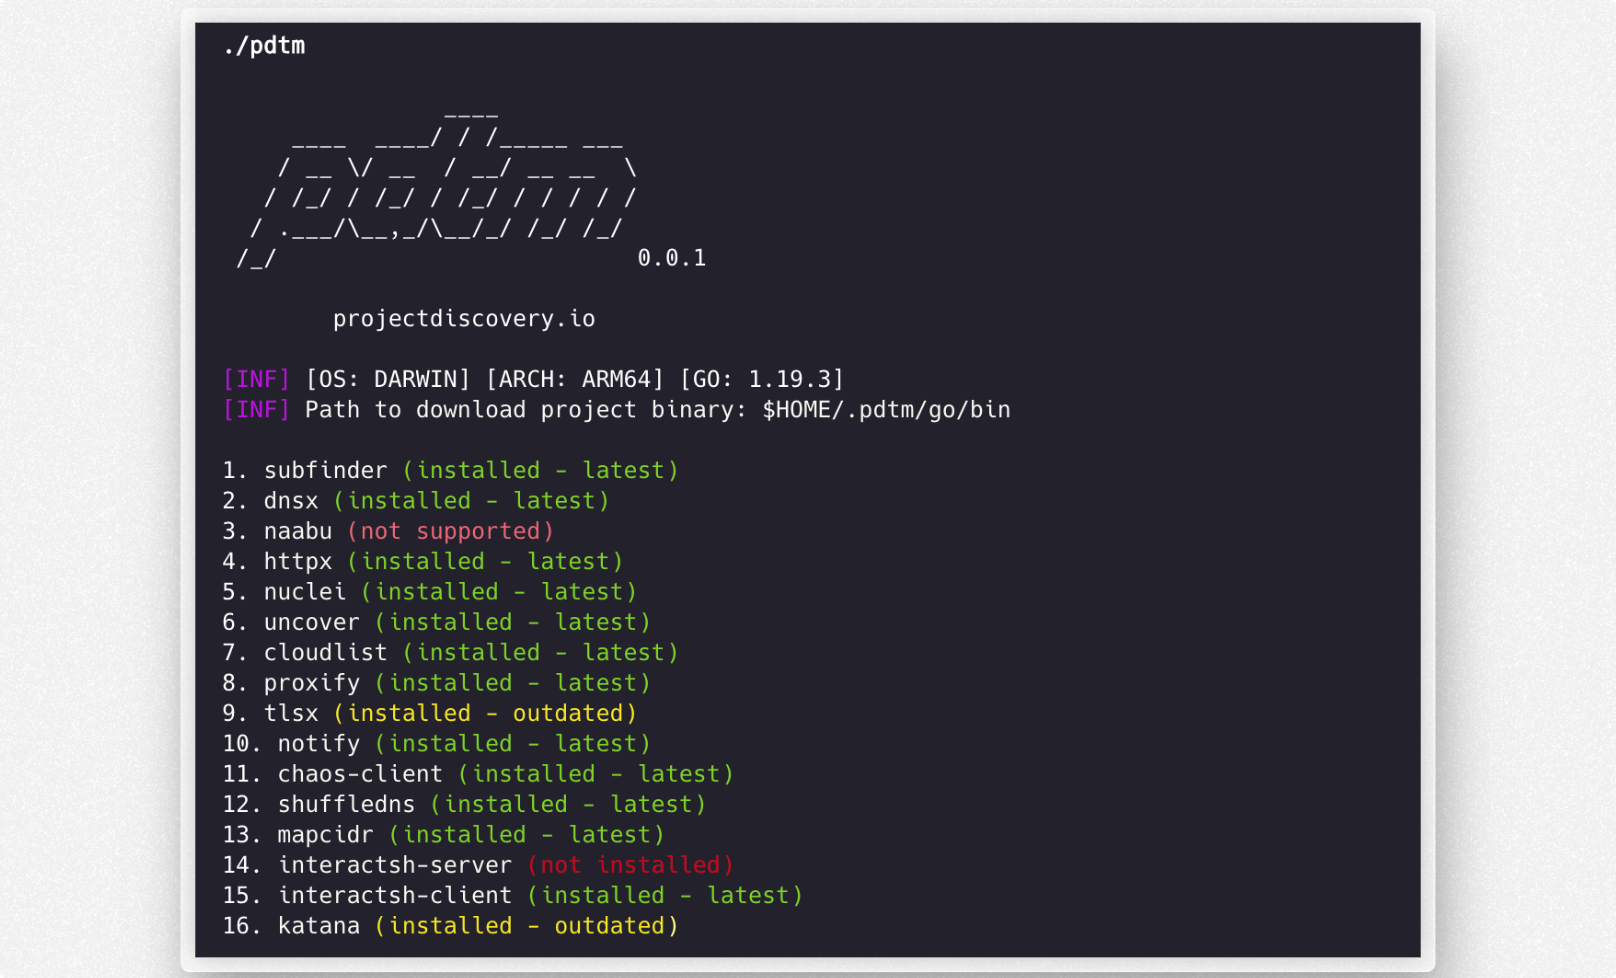 projectdiscovery/pdtm
ProjectDiscovery's Open Source Tool Manager
 gitleaks/gitleaks
Fast, open-source static analysis tool for detecting hardcoded secrets like passwords, API keys, and tokens in git repositories, files, and stdin…
 gravitational/teleport
The easiest, and most secure way to access and protect all of your infrastructure.
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
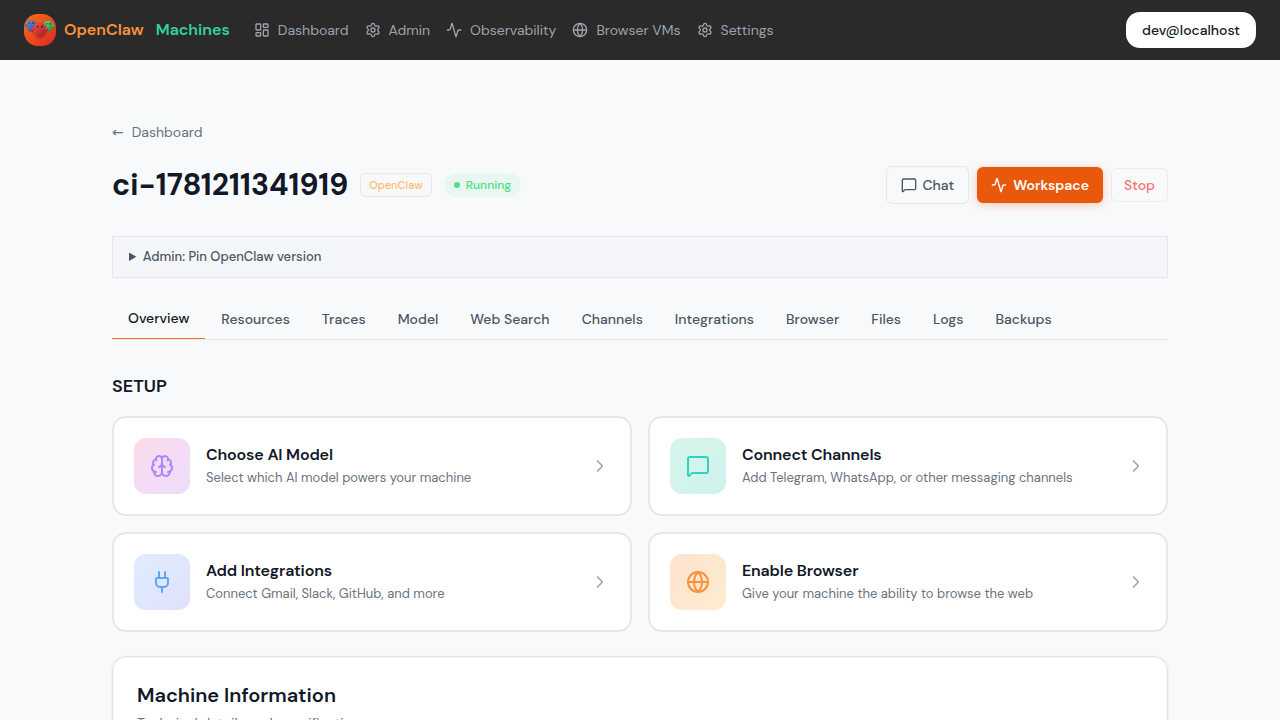 mathaix/openclawmachines
Manage OpenClaw in your team (Enterprise) by providing it compute infrastructure, tool integration, Authentication and security primitives