
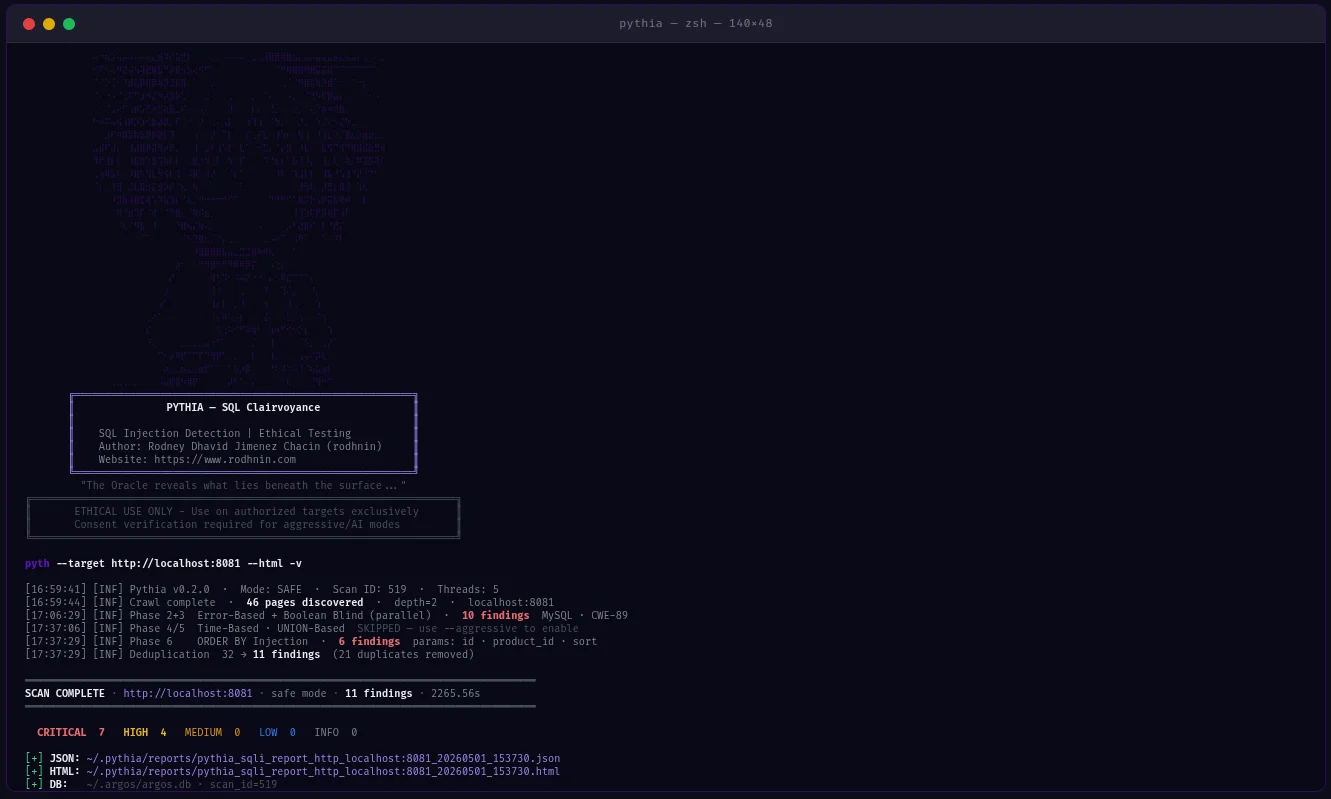
pythia-sql-clairvoyance
 rodhnin/pythia-sql-clairvoyance
Advanced SQL Injection Scanner with AI-powered analysis, ethical compliance framework, and professional reporting.
ai-securitycrawlerdevsecops+5
2
rodhnin/pythia-sql-clairvoyanceAdvanced SQL Injection Scanner with AI-powered analysis, ethical compliance framework, and professional reporting.
 gitguardian/ggshield
Detect and validate 500+ types of hardcoded secrets with advanced checks. Use it as a pre-commit hook, GitHub Action, or CLI for proactive secret…
 playtikaoss/leaktopus
Automated secret and leak detection scanner for GitHub and paste sites, with heuristic filtering, IOL enrichment via Shhgit/TruffleHog, and ELK-based…
 tejasprasad2008-afk/tracetree
Runtime behavioral analysis tool that sandboxes suspicious packages in Docker, traces syscalls with strace, maps process cascades into directed…
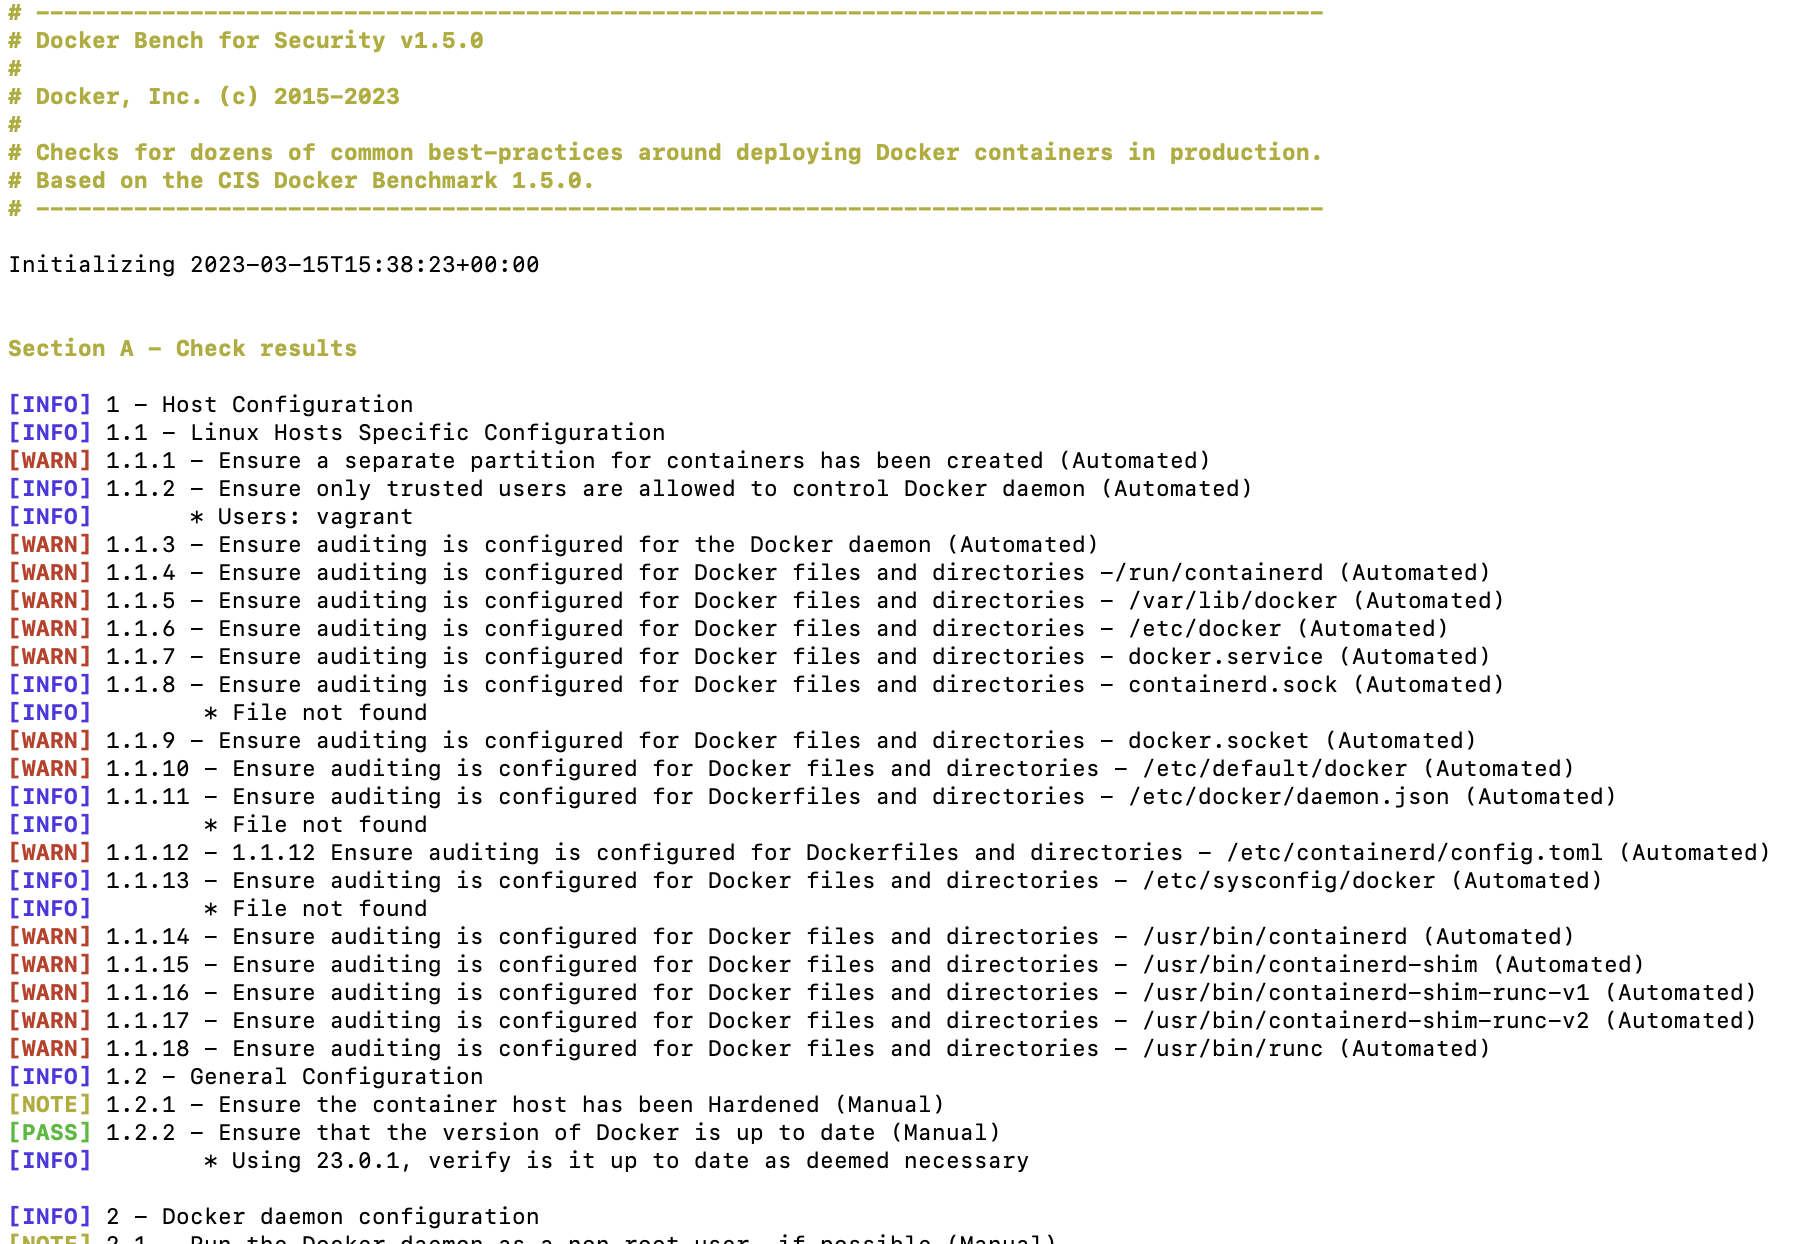 docker/docker-bench-security
The Docker Bench for Security is a script that checks for dozens of common best-practices around deploying Docker containers in production.
 snyk/snyk-scan
Automated Snyk vulnerability scanning for dependencies and Docker images in Bitbucket Pipelines, with severity thresholds and monitoring options.
 ght657/work1-secure-api
HDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis
 dtact/divd-2021-00038--log4j-scanner
Recursive vulnerability scanner for Log4j CVEs in archives and Docker images. Detects JndiLookup.class and vulnerable versions via SHA256 hashes,…
 alphacrack/readme2demo
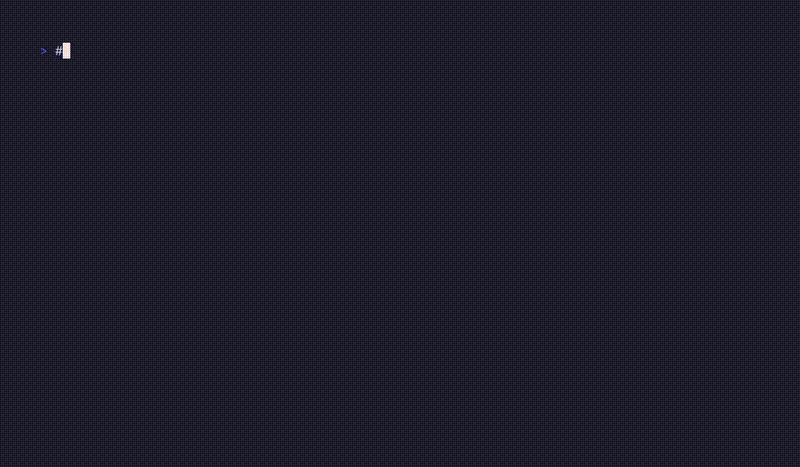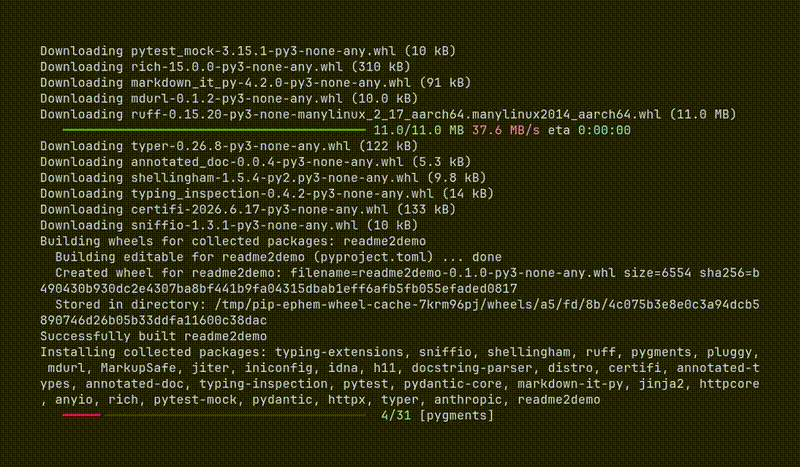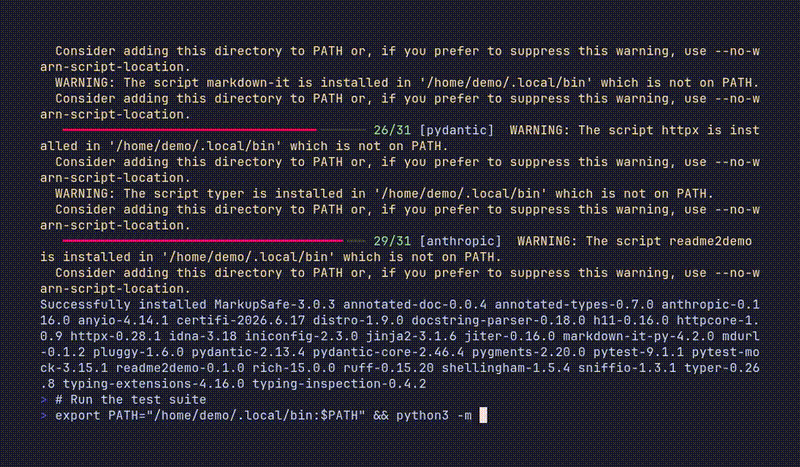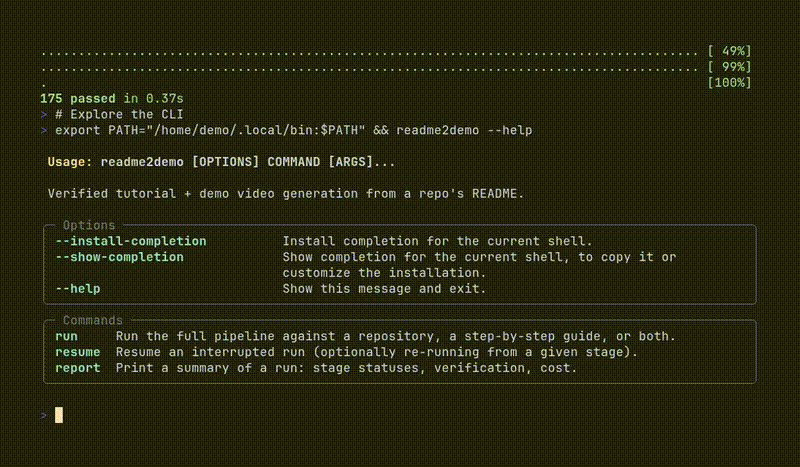
Verified tutorials and demo videos from your README. An AI agent runs it in a hardened Docker sandbox and replays it in a fresh container before…
 aquasecurity/trivy-action
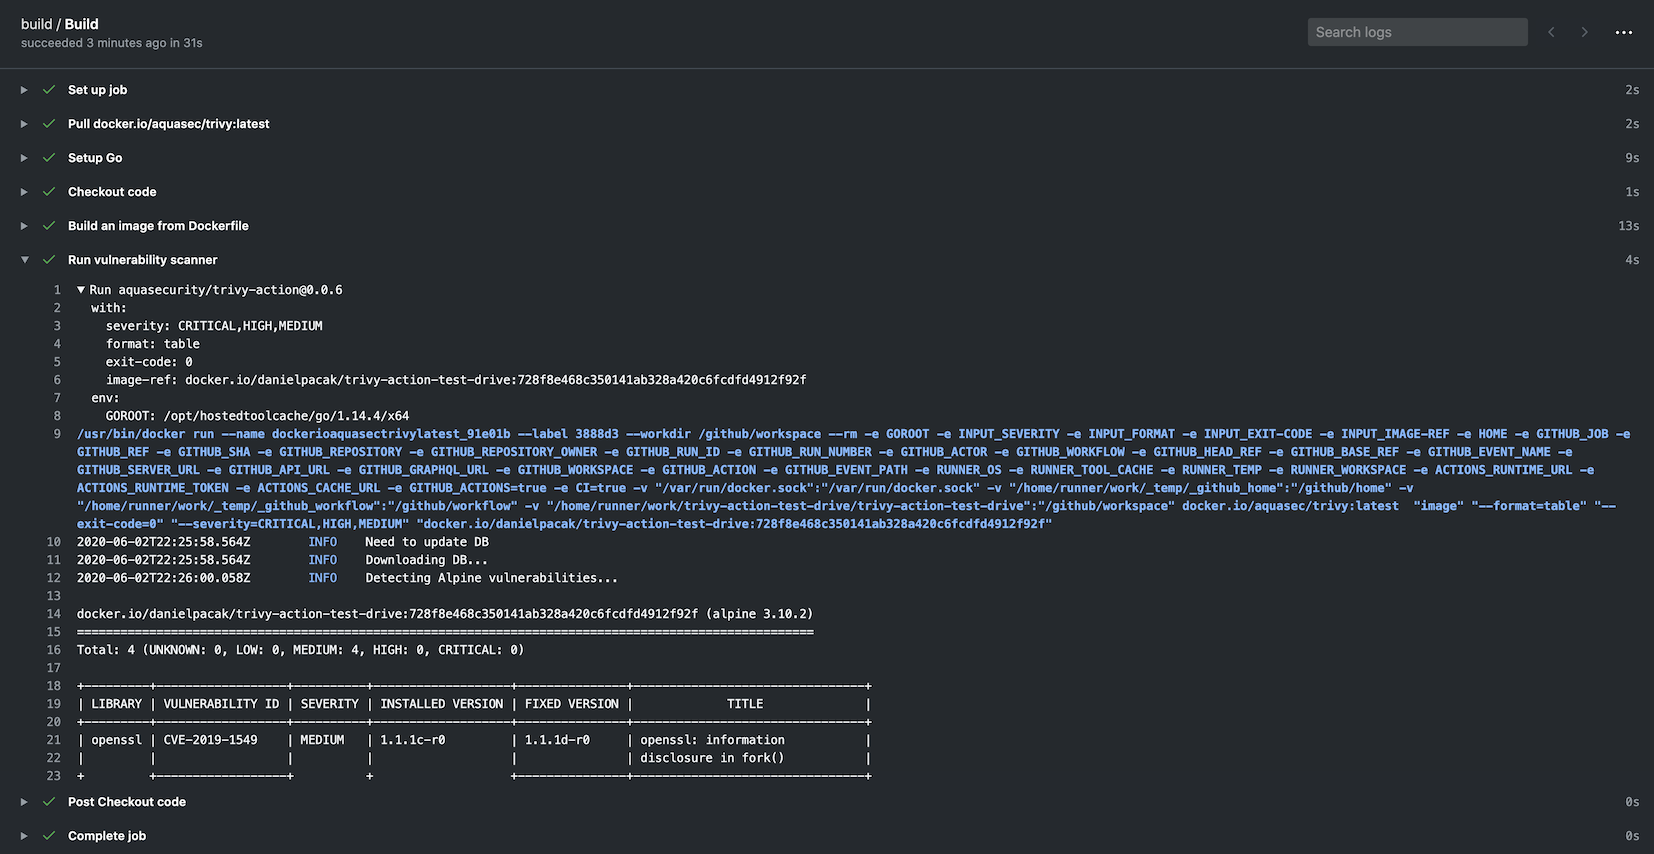
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities
 optiopay/klar
Integration of Clair and Docker Registry
 owasp/docksec
AI-powered Docker security scanner that explains vulnerabilities in plain English. An OWASP Lab Project.
 mightysai1997/cve-2024-3094
Shell scripts to detect CVE-2024-3094 backdoor in liblzma5 across Kubernetes pods and Docker containers, with SBOM generation via Trivy for…
 thewaterbug/alpr-dashboard-patches
Runtime patches for algertc/alpr-dashboard: async logger fix and CVE-2025-29927 nginx mitigation
 oriolrius/kafka-keycloak-oauth
Apache Kafka 4.1.0 (KRaft) with Keycloak OAuth2 authentication using Strimzi - bypasses CVE-2025-27817 URL allowlist restriction
 gensecaihq/react2shell-scanner
Detects CVE-2025-55182 RCE in React Server Components by scanning npm/pnpm/yarn lockfiles, Docker images, SBOMs, and live URLs. Includes auto-fix,…
 piecar21/cve-2026-0303
Proof-of-concept and Docker lab for CVE-2026-0303, demonstrating arbitrary code execution in Checkov via an auto-loaded .checkov.yml pointing to an…