
Archived
purpleteam-app-scanner
 purpleteam-labs/purpleteam-app-scanner
Application scanning component of purpleteam
api-security-testingcloud-securitydevsecops+4
purpleteam-labs/purpleteam-app-scannerApplication scanning component of purpleteam
 0x4d31/burpa
Burp-Automator: A Burp Suite Automation Tool with Slack Integration. It can be used with Jenkins and Selenium to automate Dynamic Application…
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
 infobyte/faraday_burp
Burp Extension for collaboration in Faraday
 vighnesh91/-logicsentry-ai
Offline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…
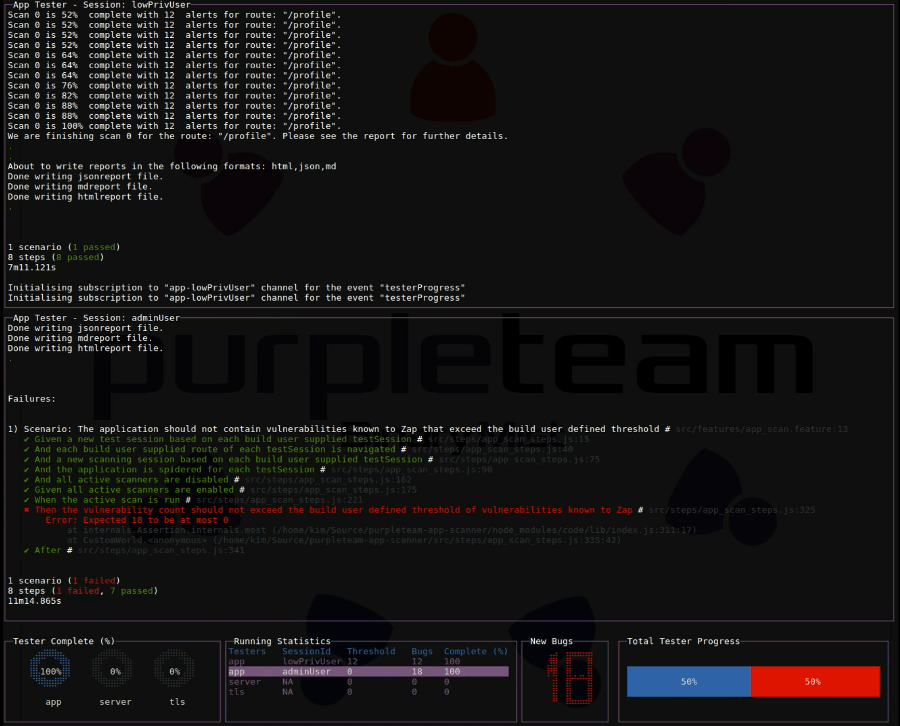 purpleteam-labs/purpleteam
CLI component of purpleteam
 purpleteam-labs/purpleteam-server-scanner
Server scanning component of purpleteam
 hahwul/dalfox
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 dipjyotimetia/hybridtestframework
End to End testing of Web, API, Cloud, Events and Security
 s4dhulabs/vimana-framework
Vimana is a modular security framework for auditing Python APIs and Web applications. The plugin-based architecture enables security professionals to…
 wi3memake/react2shell-scanner
Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…
 bogdanticu88/ratrace
A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.
 hahwul/smugglex
Rust-powered HTTP Request Smuggling Scanner.
 ericmtzmtz/pwnproxy
An open, local-first security testing platform for pentesters, AI agents, CI/CD pipelines, and teams.
 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
 usebruno/bruno
Opensource IDE For Exploring and Testing API's (lightweight alternative to Postman/Insomnia)
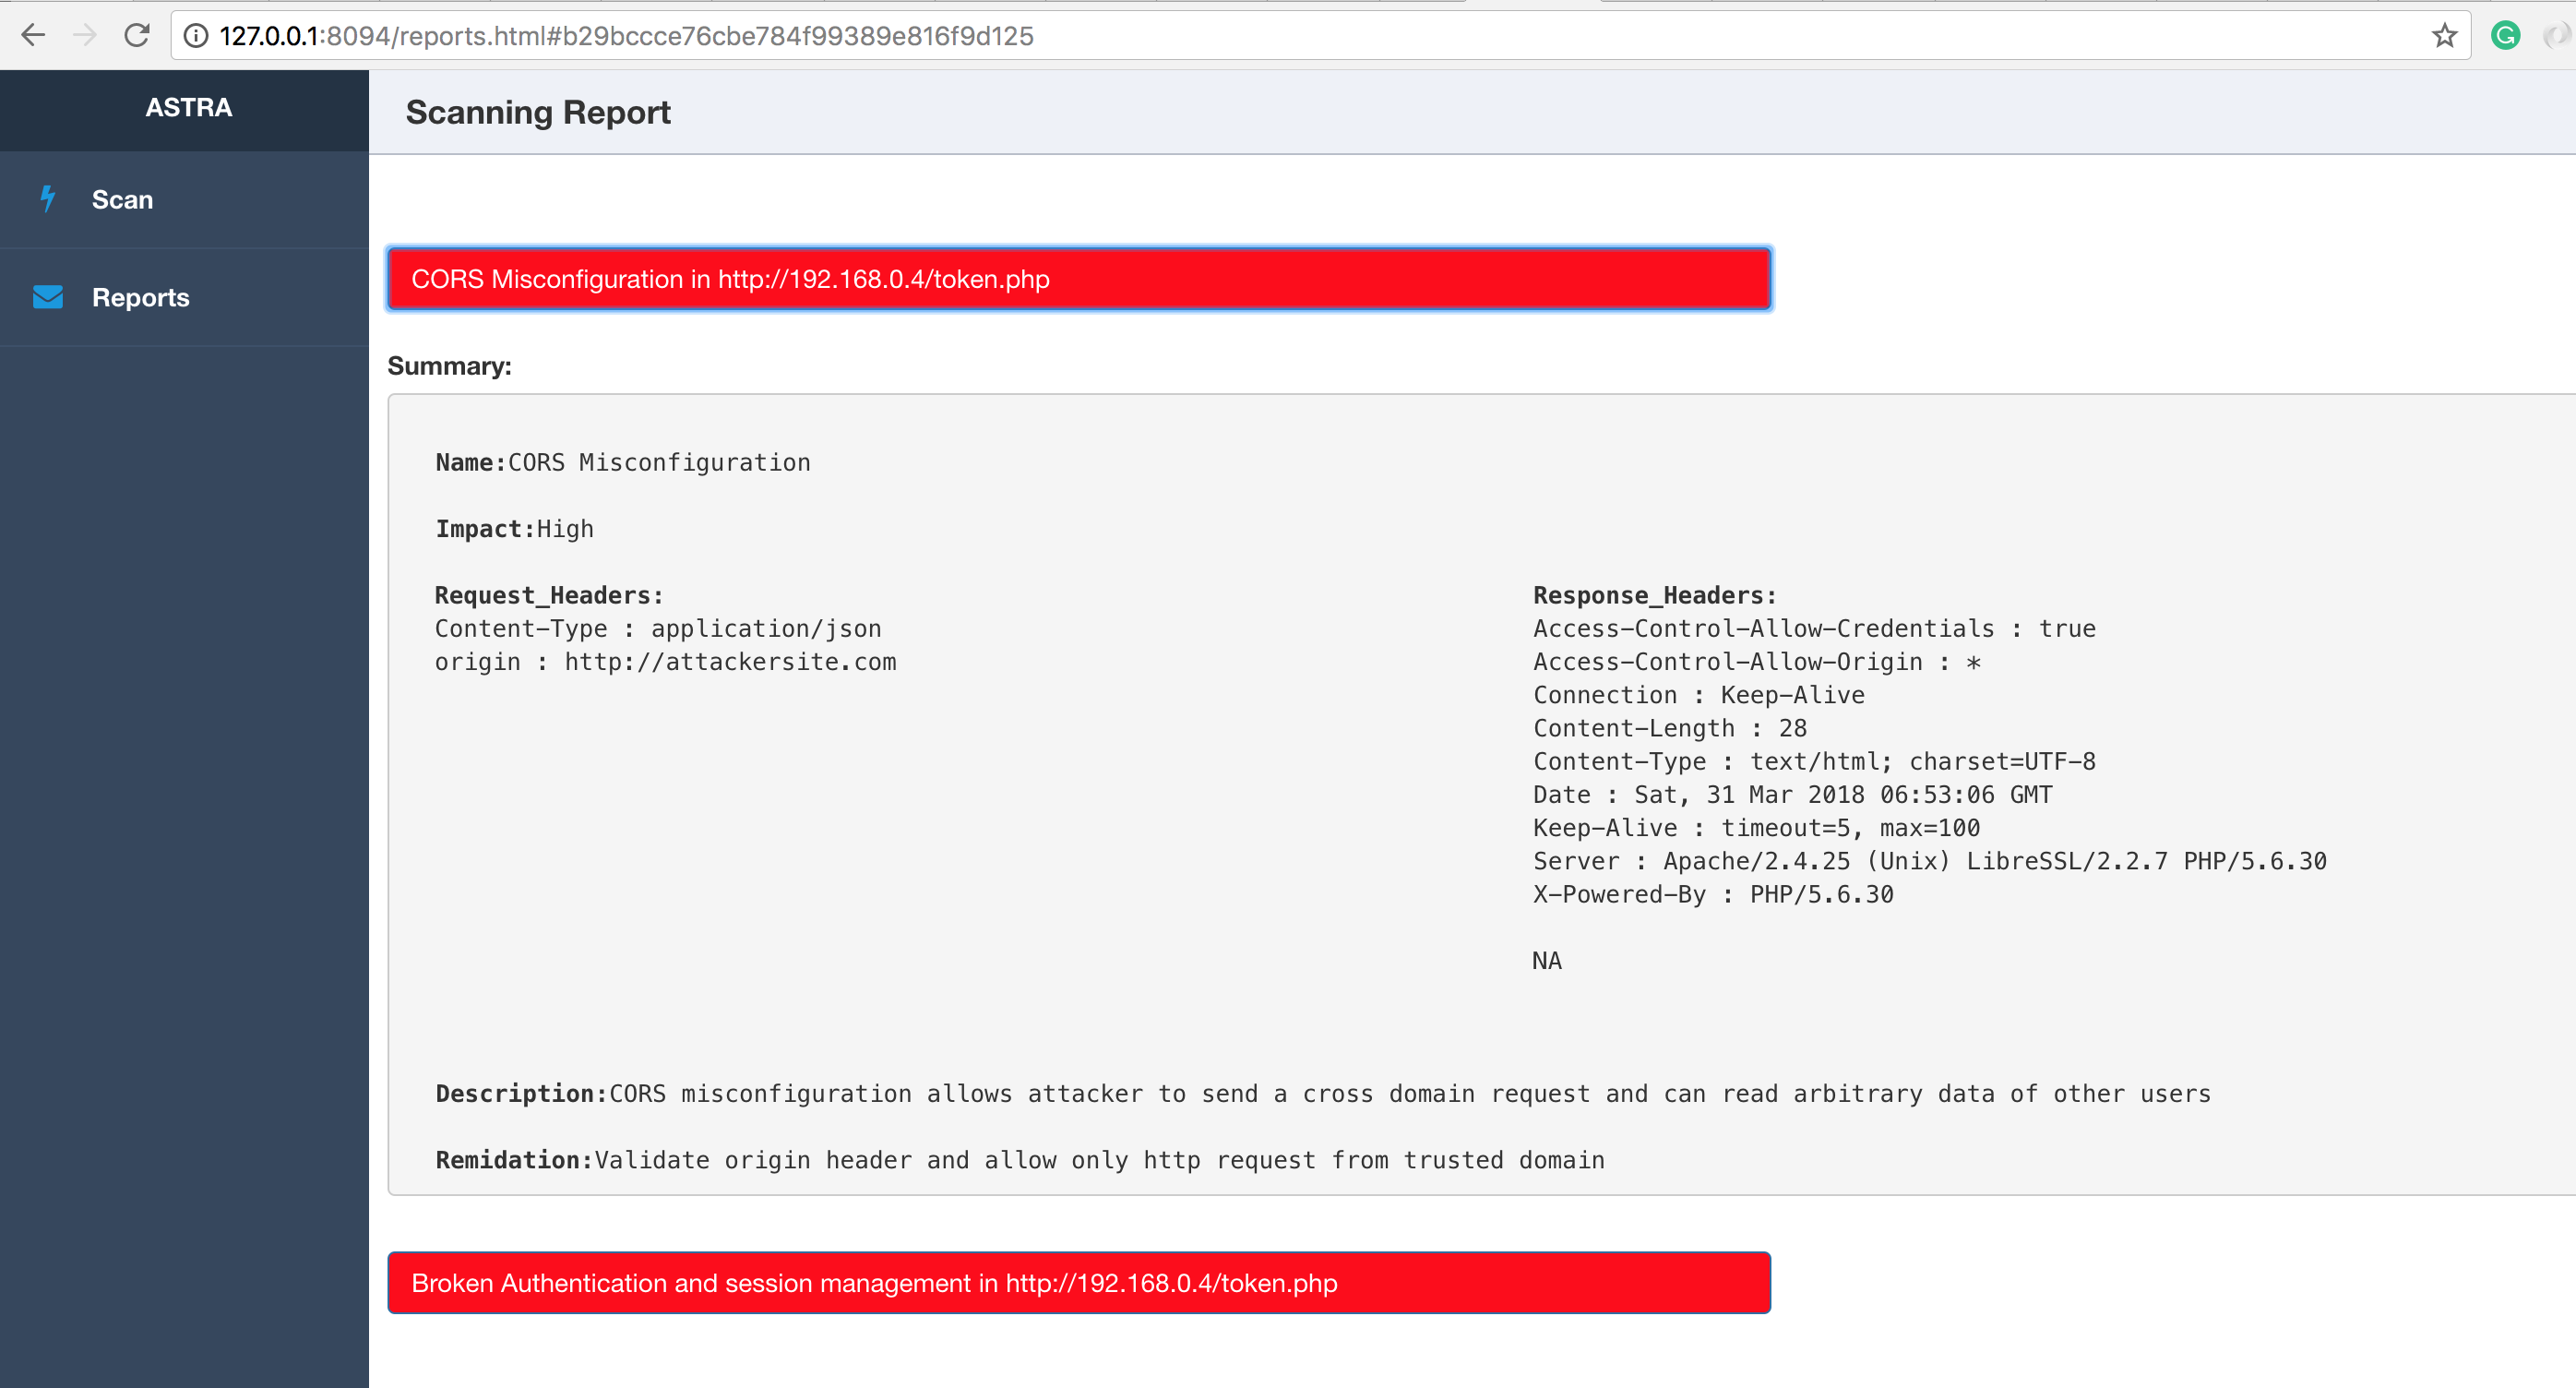 flipkart-incubator/astra
Automated Security Testing For REST API's