
Archived
local-log4j-vuln-scanner
 hillu/local-log4j-vuln-scanner
[Moved to Codeberg] Simple local scanner for vulnerable log4j instances
code-analysisdevsecopsstatic-analysis+3
hillu/local-log4j-vuln-scanner[Moved to Codeberg] Simple local scanner for vulnerable log4j instances
 disruptops/cred_scanner
A simple file-based scanner to look for potential AWS access and secret keys in files
 jenkinsci/nuclei-plugin
Nuclei is a fast tool for configurable targeted vulnerability scanning based on templates offering massive extensibility and ease of use.
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
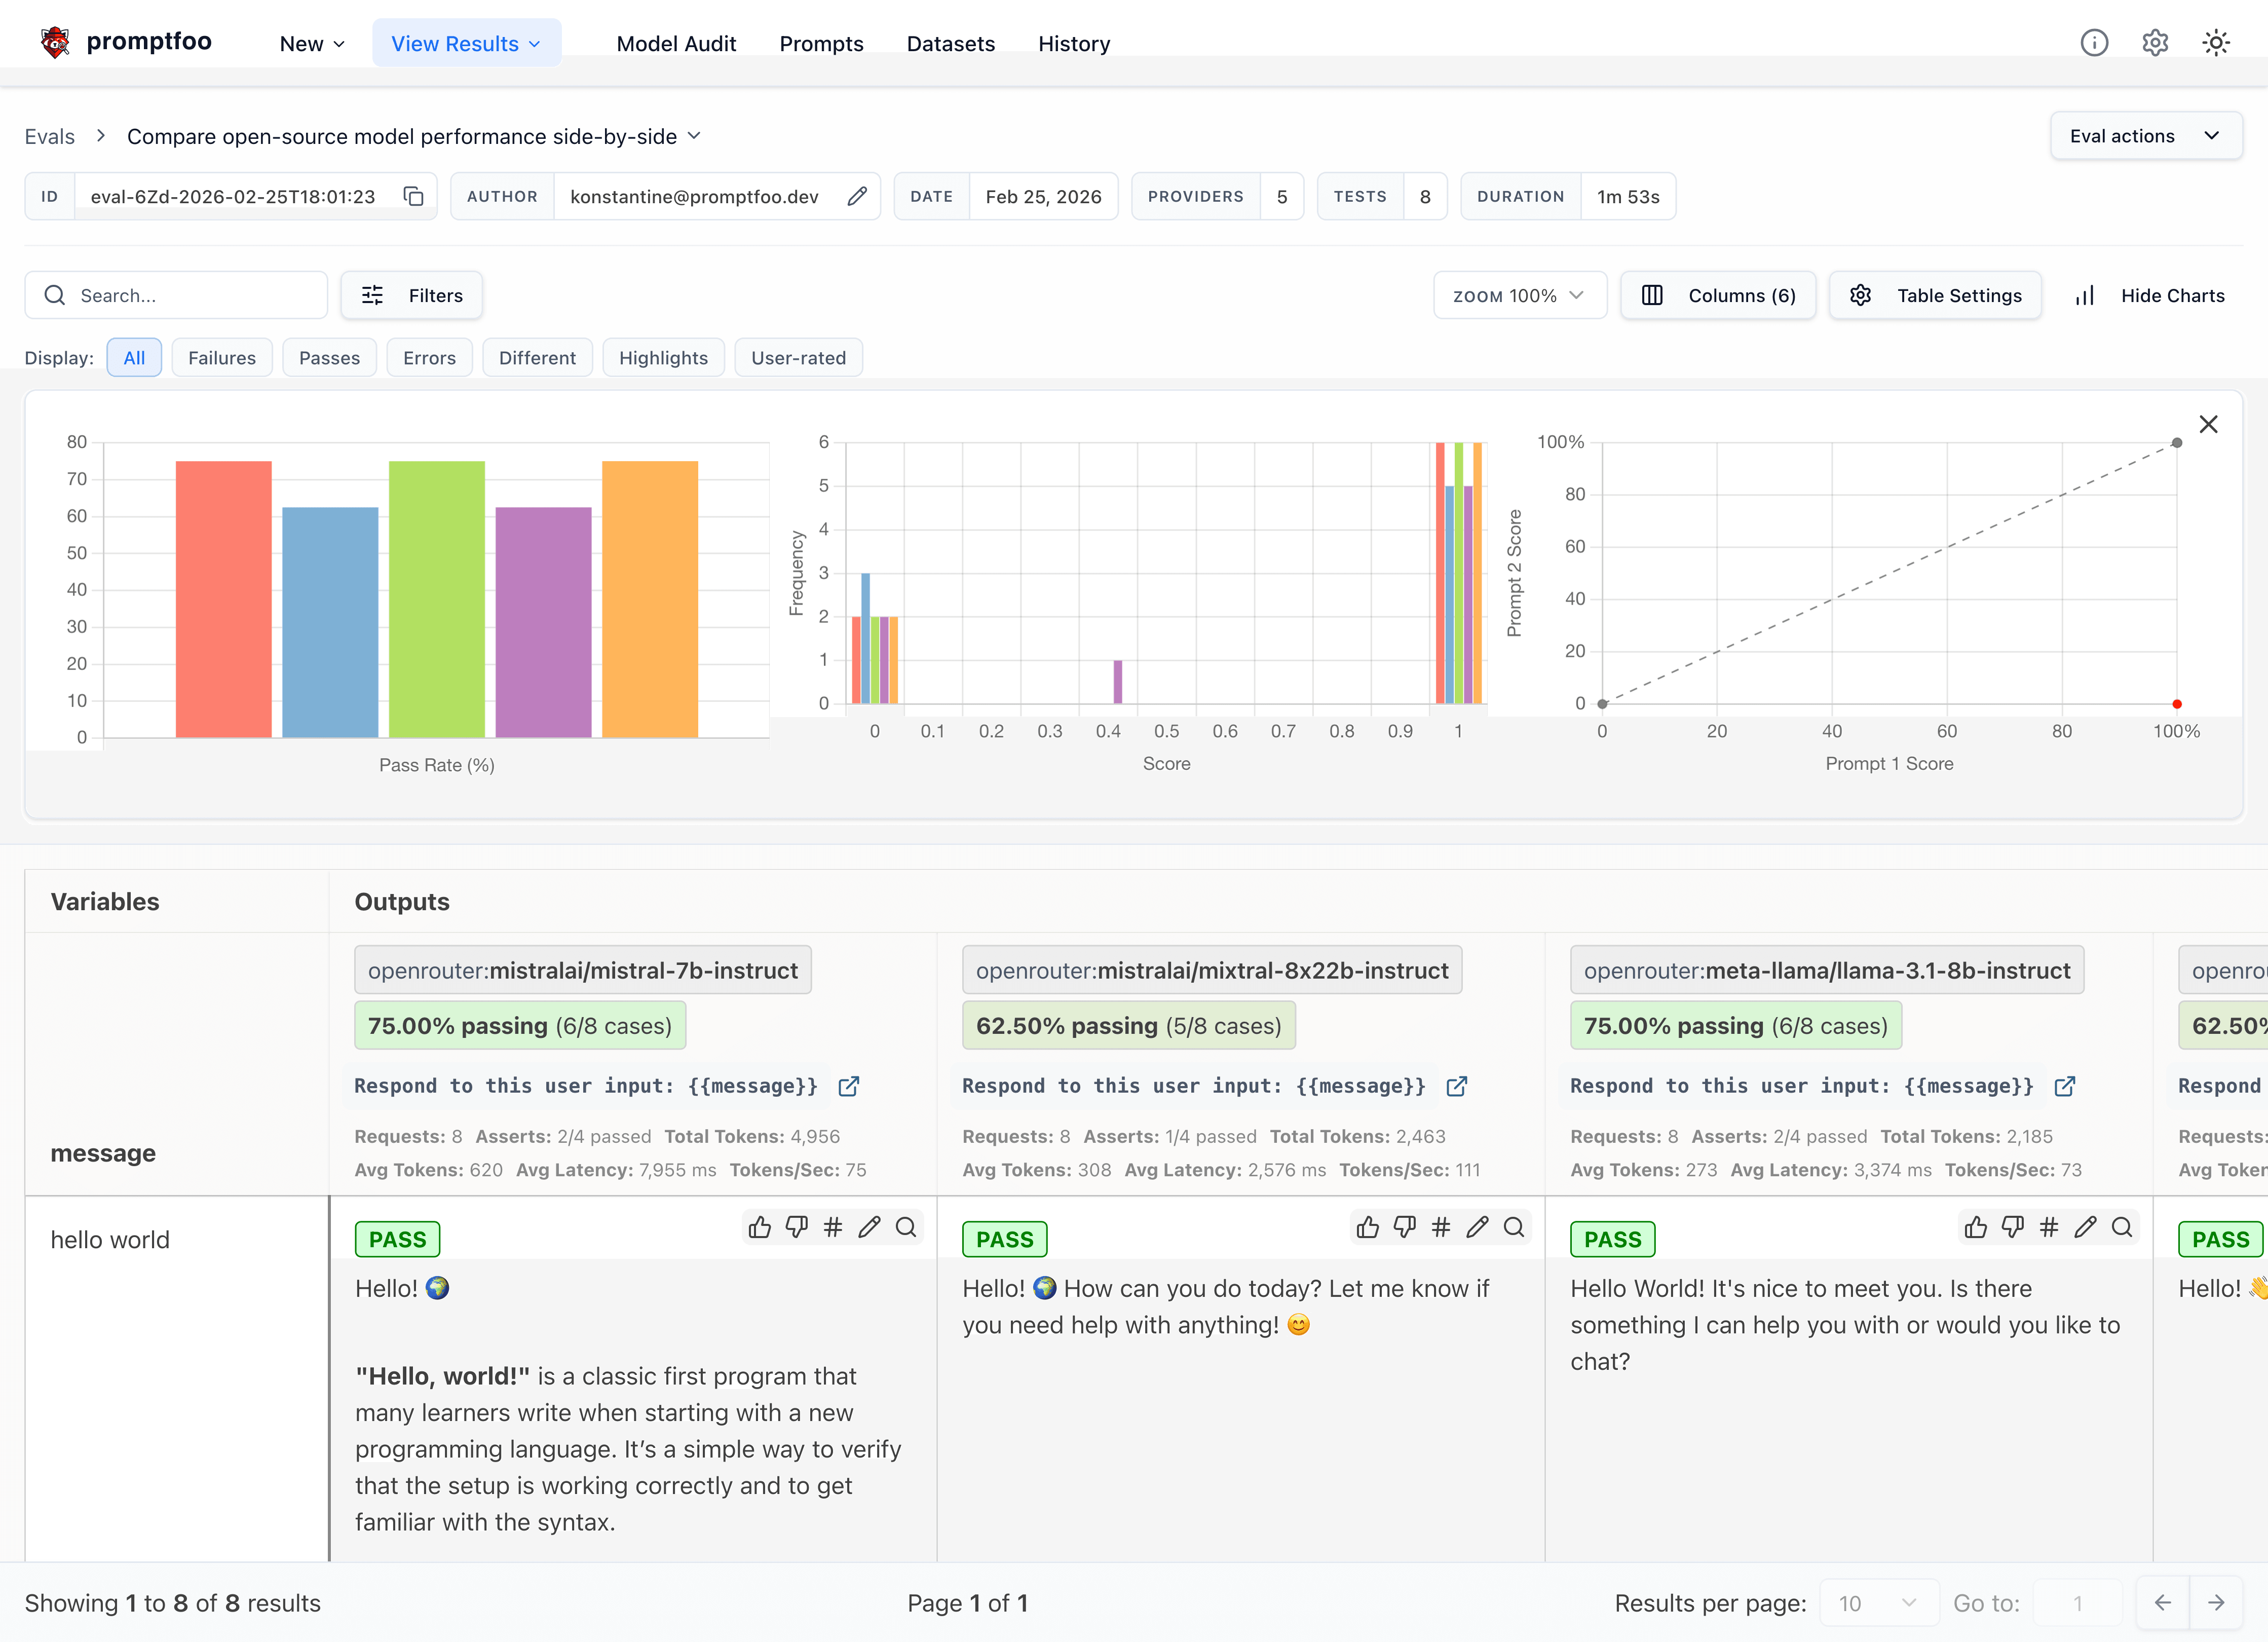 promptfoo/promptfoo
Test your prompts, agents, and RAGs. Red teaming/pentesting/vulnerability scanning for AI. Compare performance of GPT, Claude, Gemini, DeepSeek, and…
 getsops/sops
Simple and flexible tool for managing secrets
 p0ssuidao/terraguard
🛡️ 🔒 This project's goal is to be simple to create and destroy your own VPN service using WireGuard.
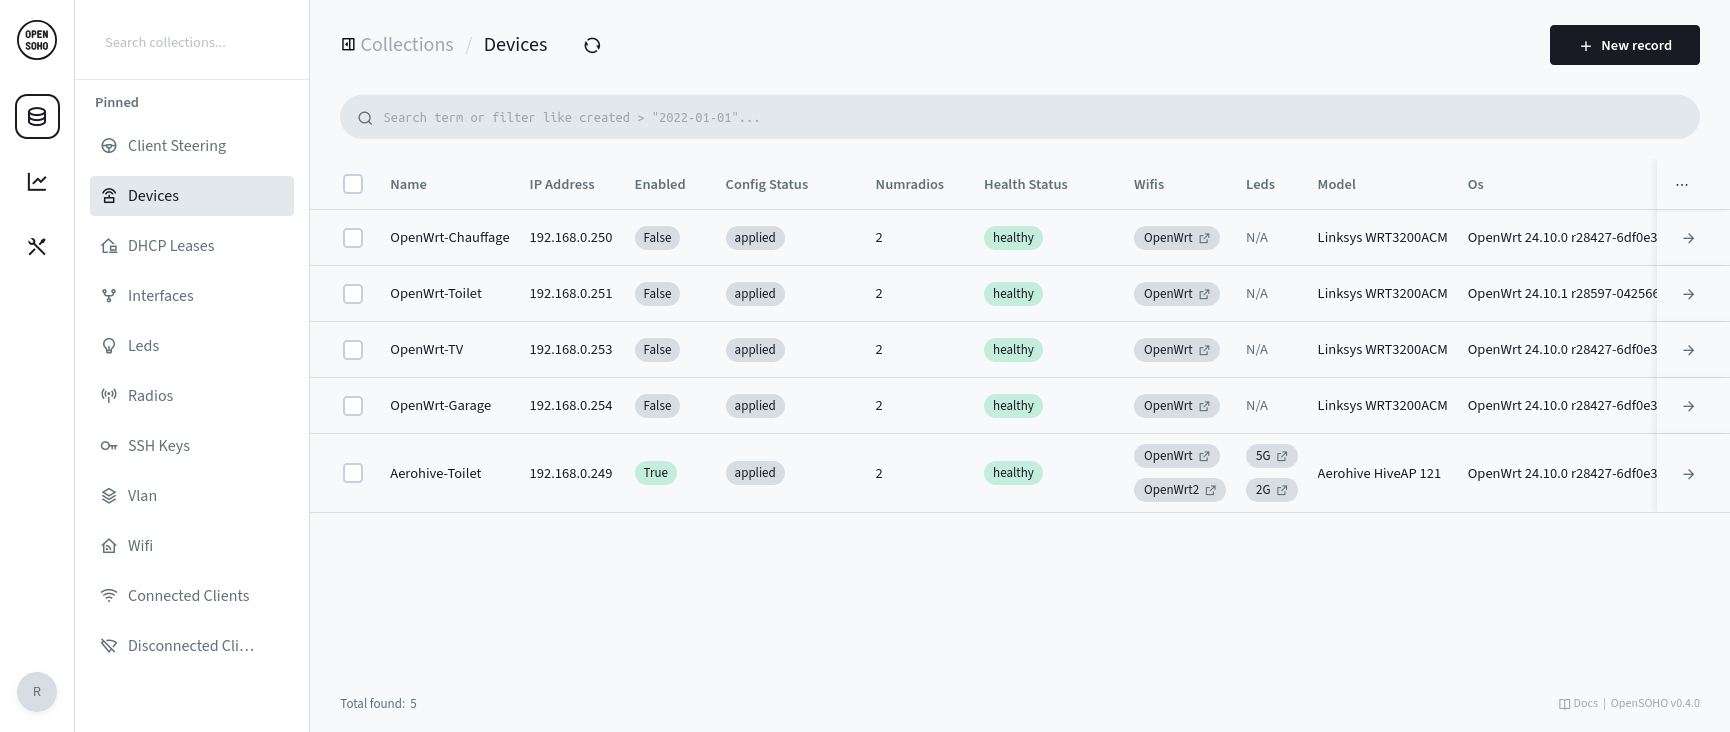 rubenbe/opensoho
Lightweight OpenWRT device management platform for small networks. Centralized configuration, monitoring, and WiFi management for 2–20 devices with…
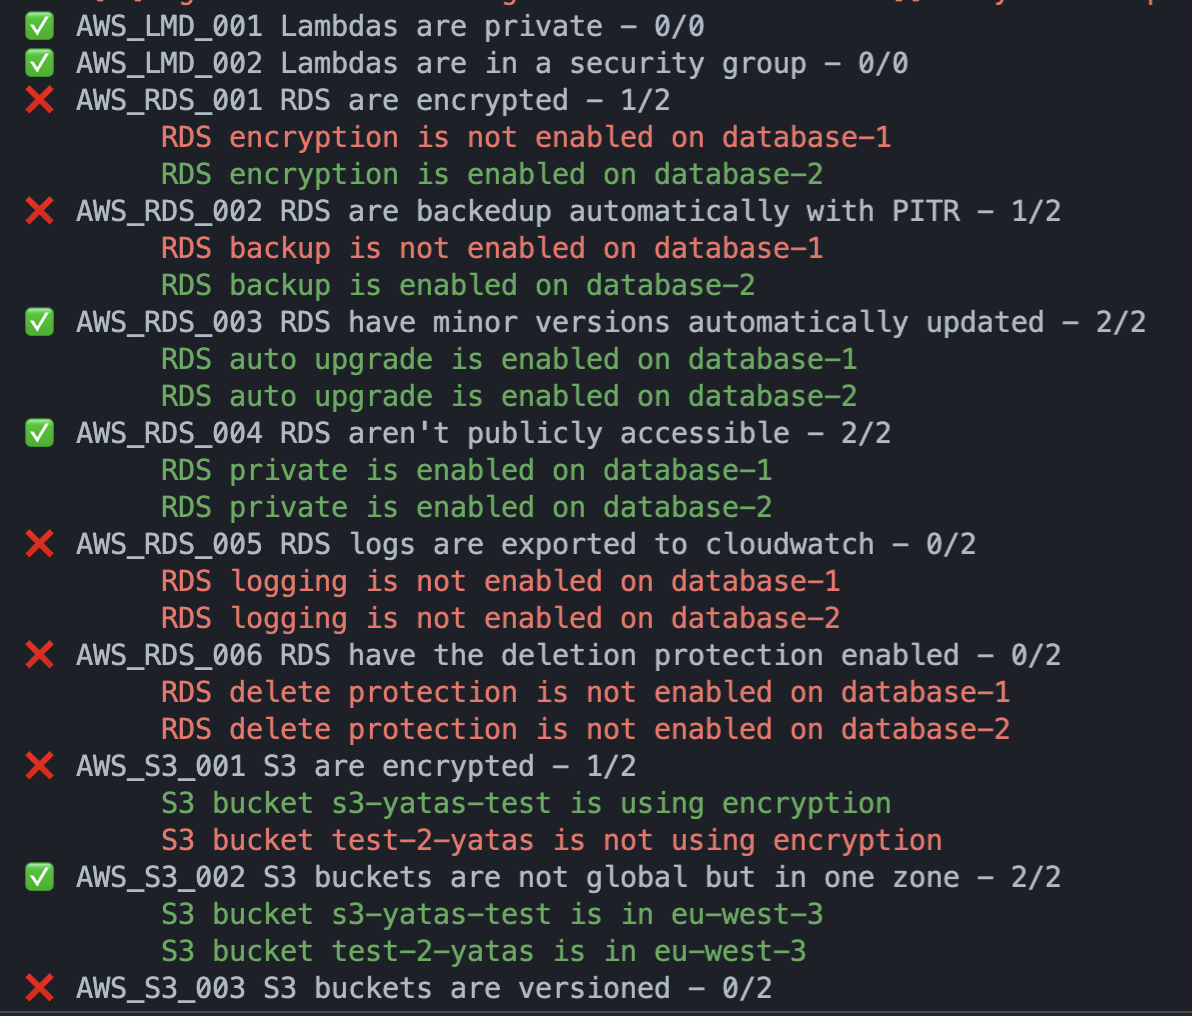 padok-team/yatas
:owl::mag_right: A simple tool to audit your AWS/GCP infrastructure for misconfiguration or potential security issues with plugins integration
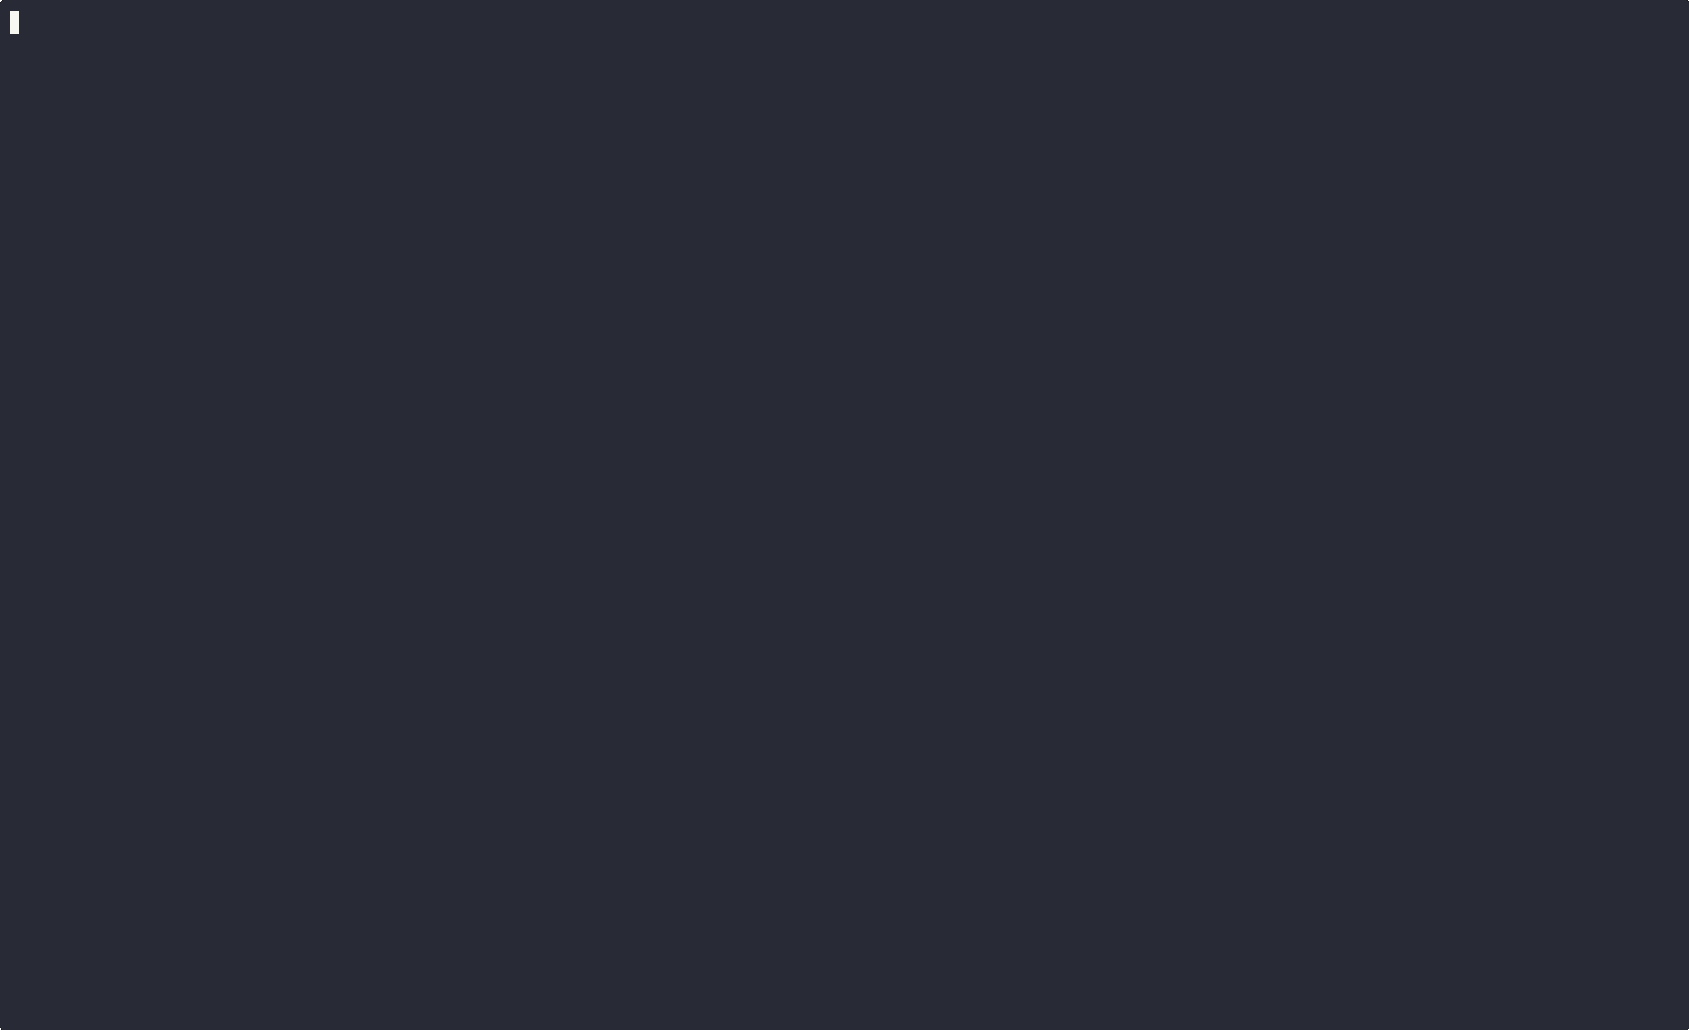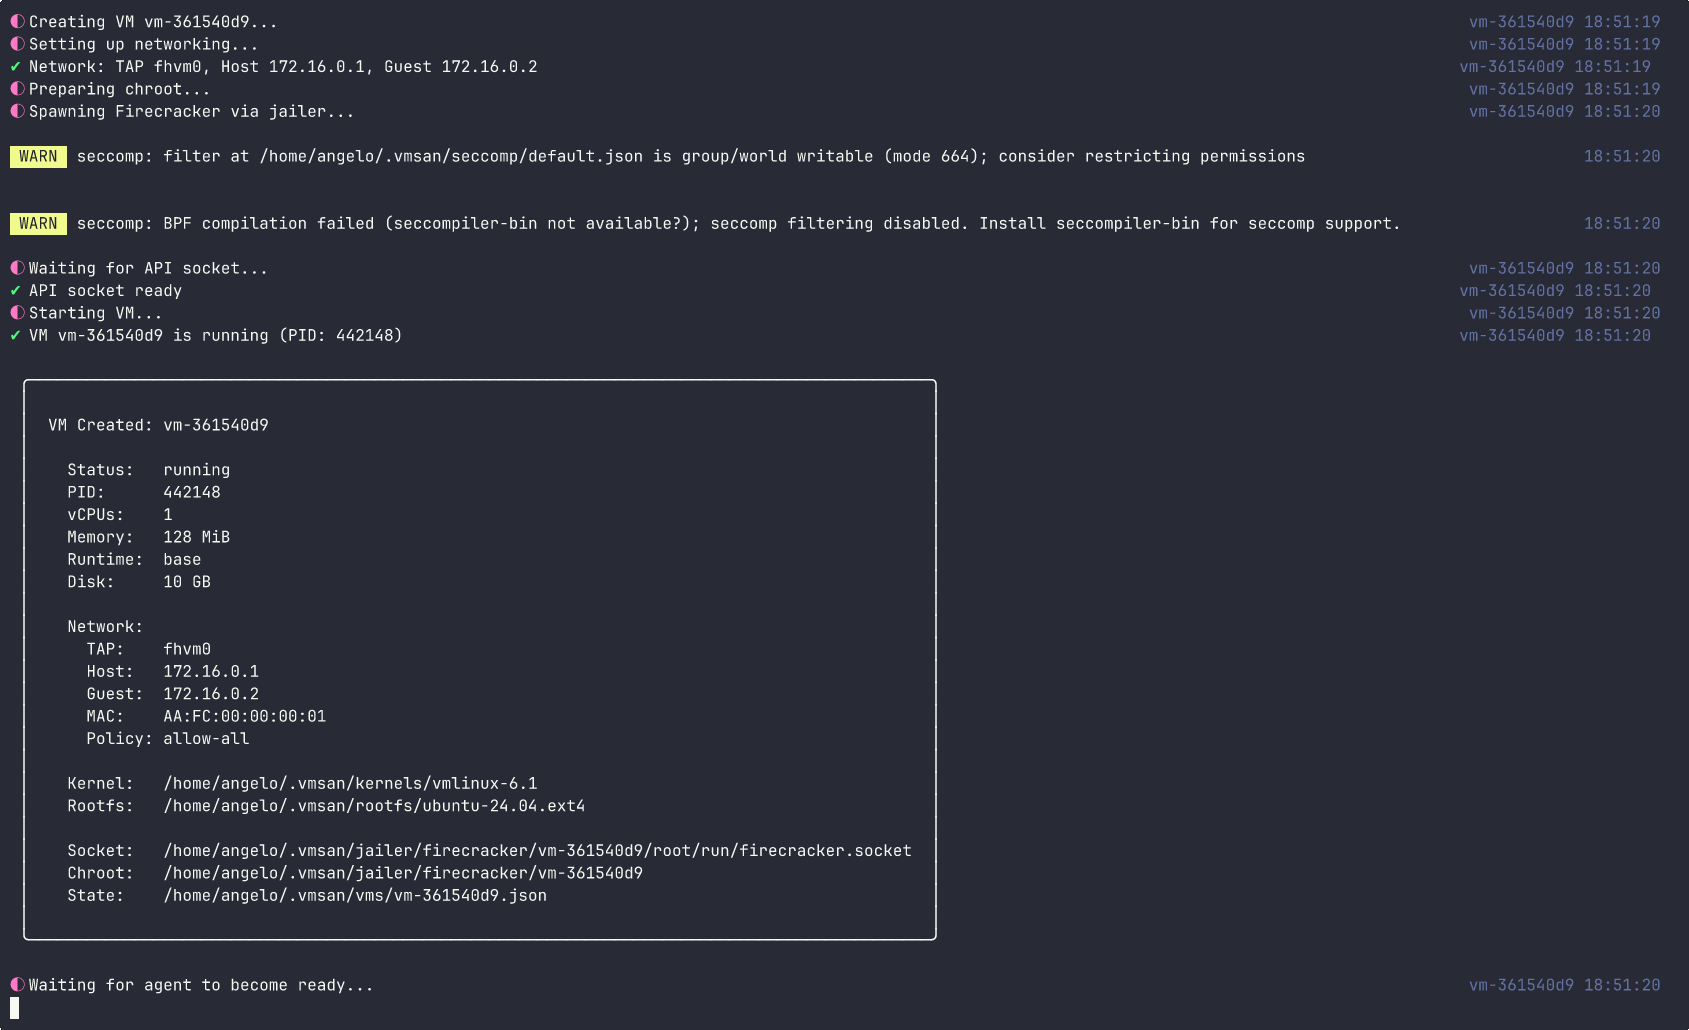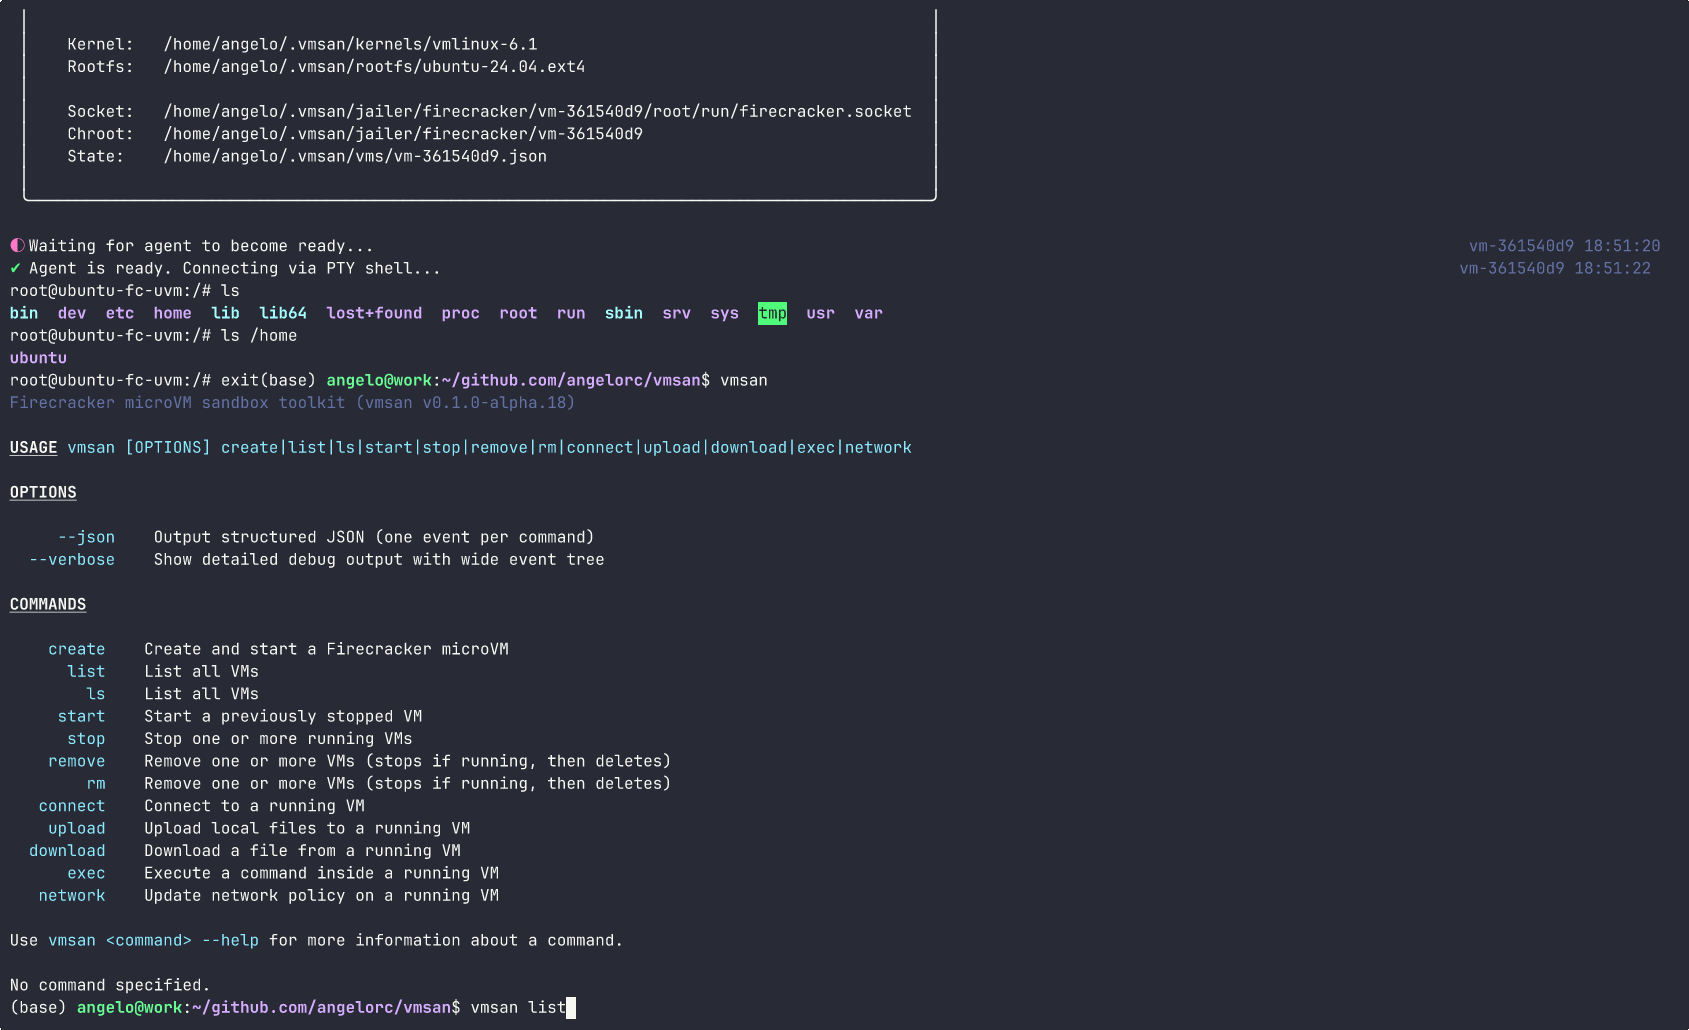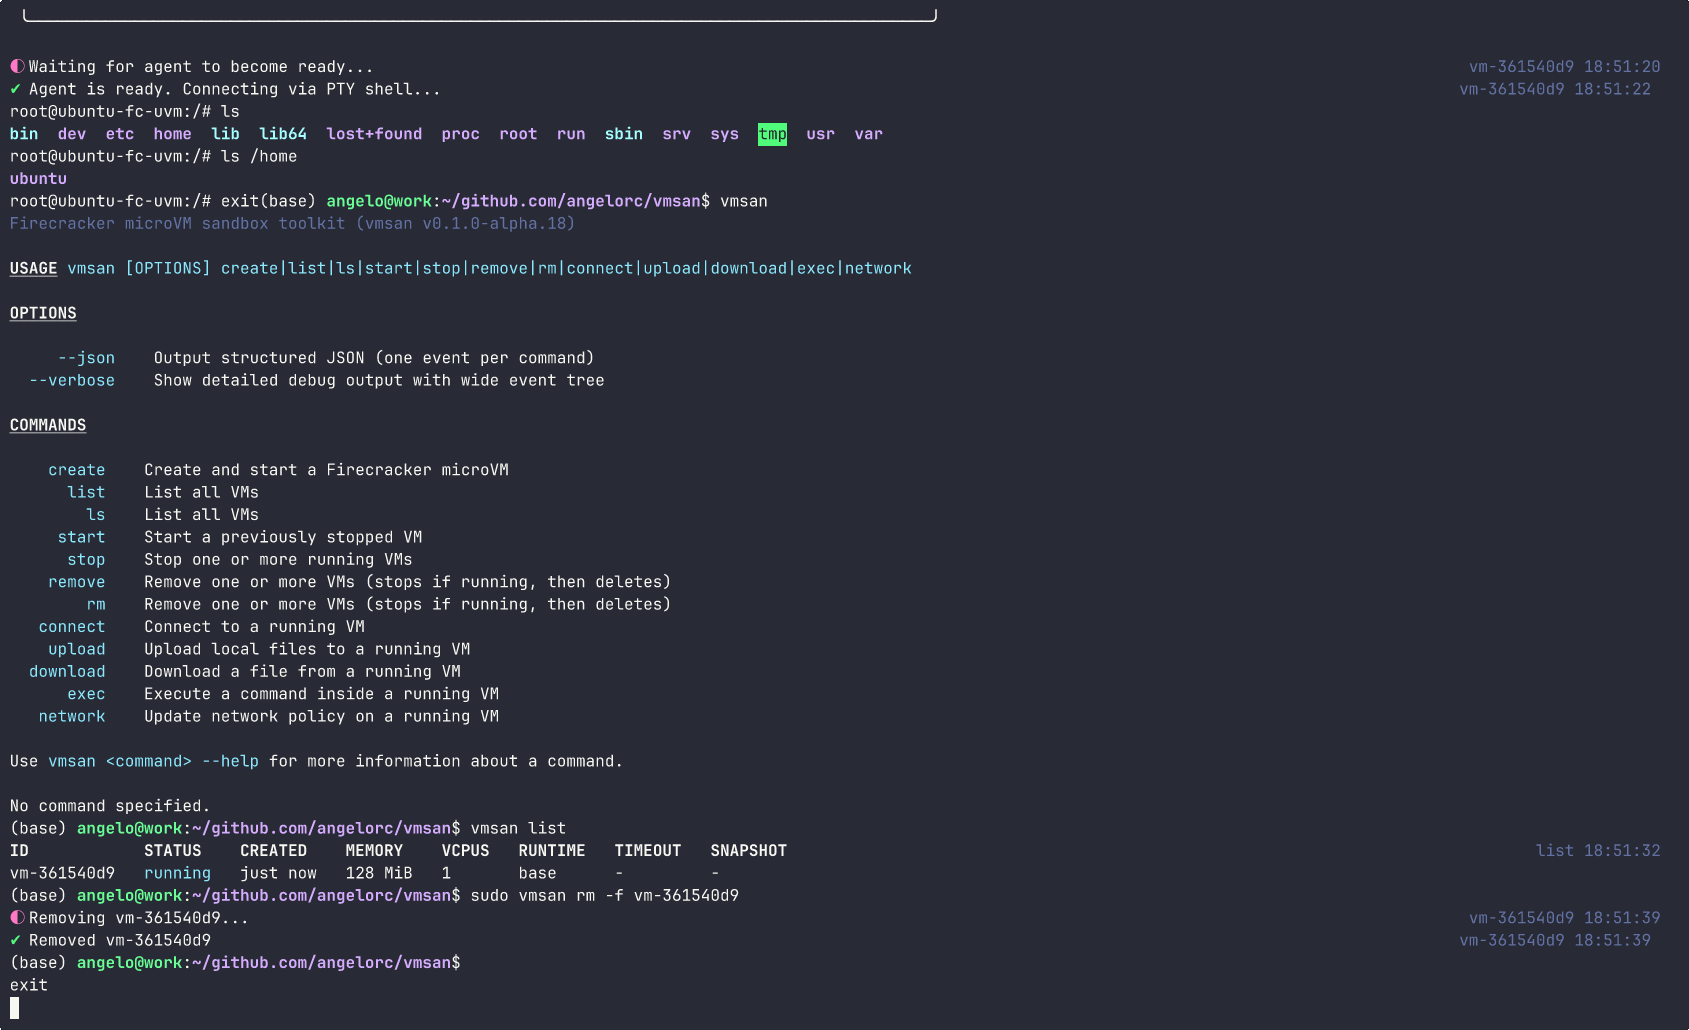 angelorc/vmsan
Firecracker made simple. Spin up secure microVMs in milliseconds, from install to interactive shell in one command.
 infiniroot/ansible-mitigate-copyfail-dirtyfrag
Simple Ansible Playbook to mitigate against CopyFail (CVE-2026-31431) and DirtyFrag (CVE-2026-43284) vulnerabilities.
 pmontesd/log4j-cve-2021-44228
Very simple Ansible playbook that scan filesystem for JAR files vulnerable to Log4Shell
 meersjo/ansible-mysql-cve-2016-6662
Simple ansible playbook to patch mysql servers against CVE-2016-6662
 meterianhq/log4j-vuln-coverage-check
A simple project to check coverage of Log4J vuln CVE-2021-44228 (and related)
 spiarh/webhook-cve-2022-0811
Simple webhook to block exploitation of CVE-2022-0811
 weaveworks/weave-gitops
Weave GitOps is transitioning to a community driven project! It provides insights into your application deployments, and makes continuous delivery…
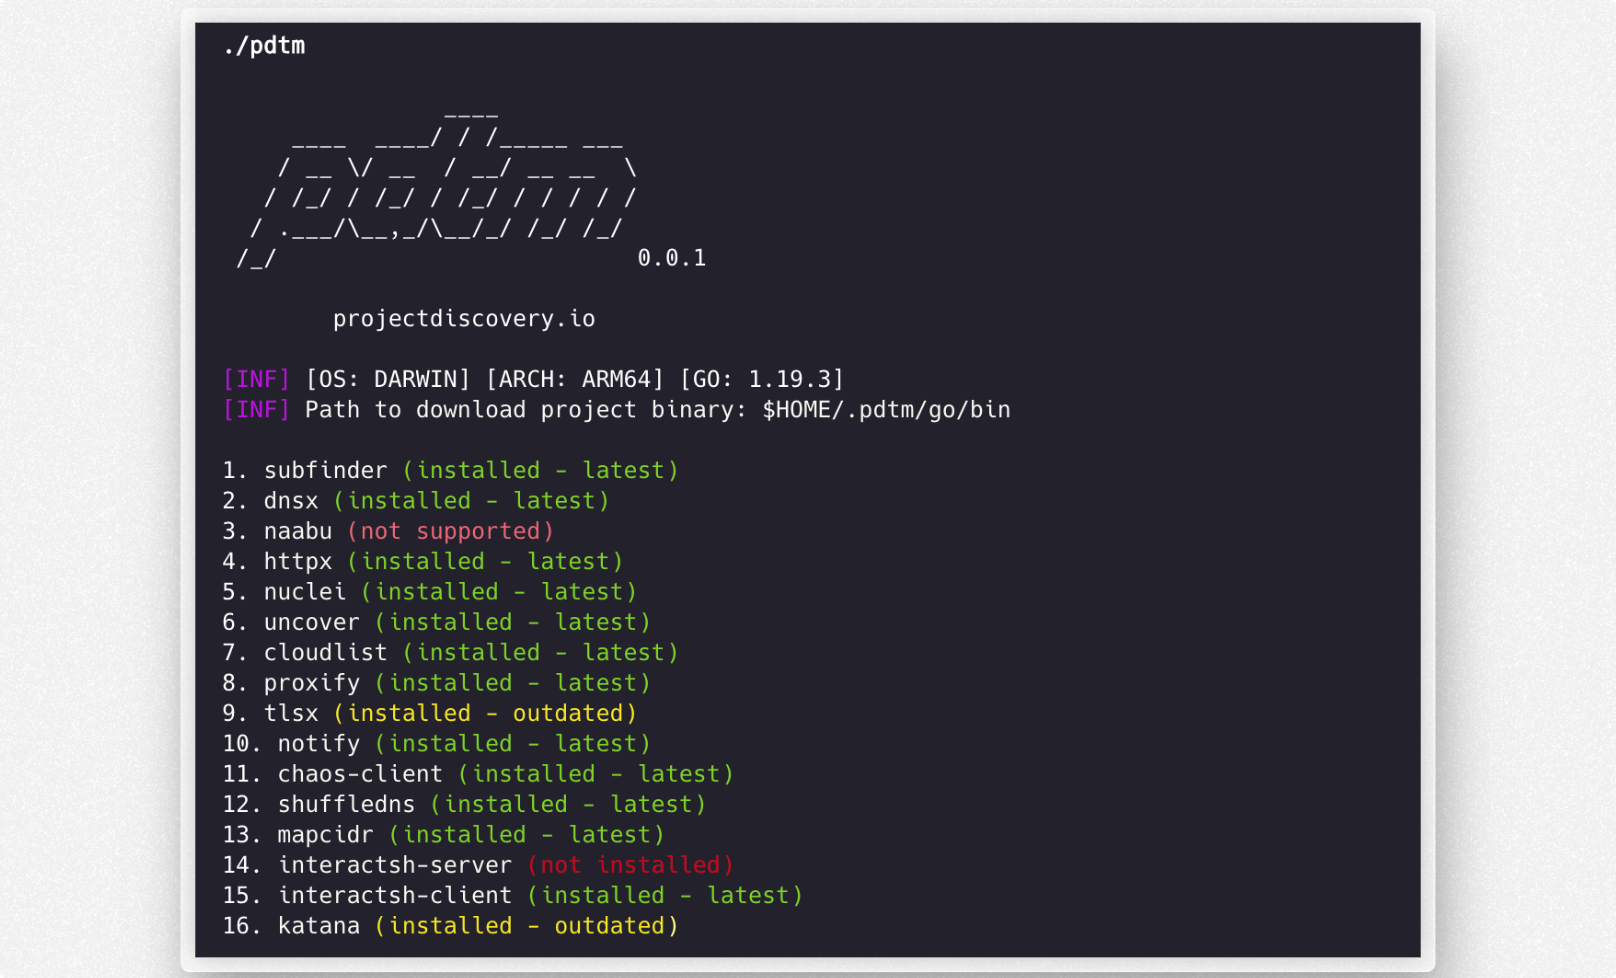 projectdiscovery/pdtm
ProjectDiscovery's Open Source Tool Manager
 optiopay/klar
Integration of Clair and Docker Registry