
cloudfoundry_uaa
 shanika04/cloudfoundry_uaa
CVE-2016-4468
api-securityauthentication-authorizationcloud-infrastructure-security+3
shanika04/cloudfoundry_uaaCVE-2016-4468
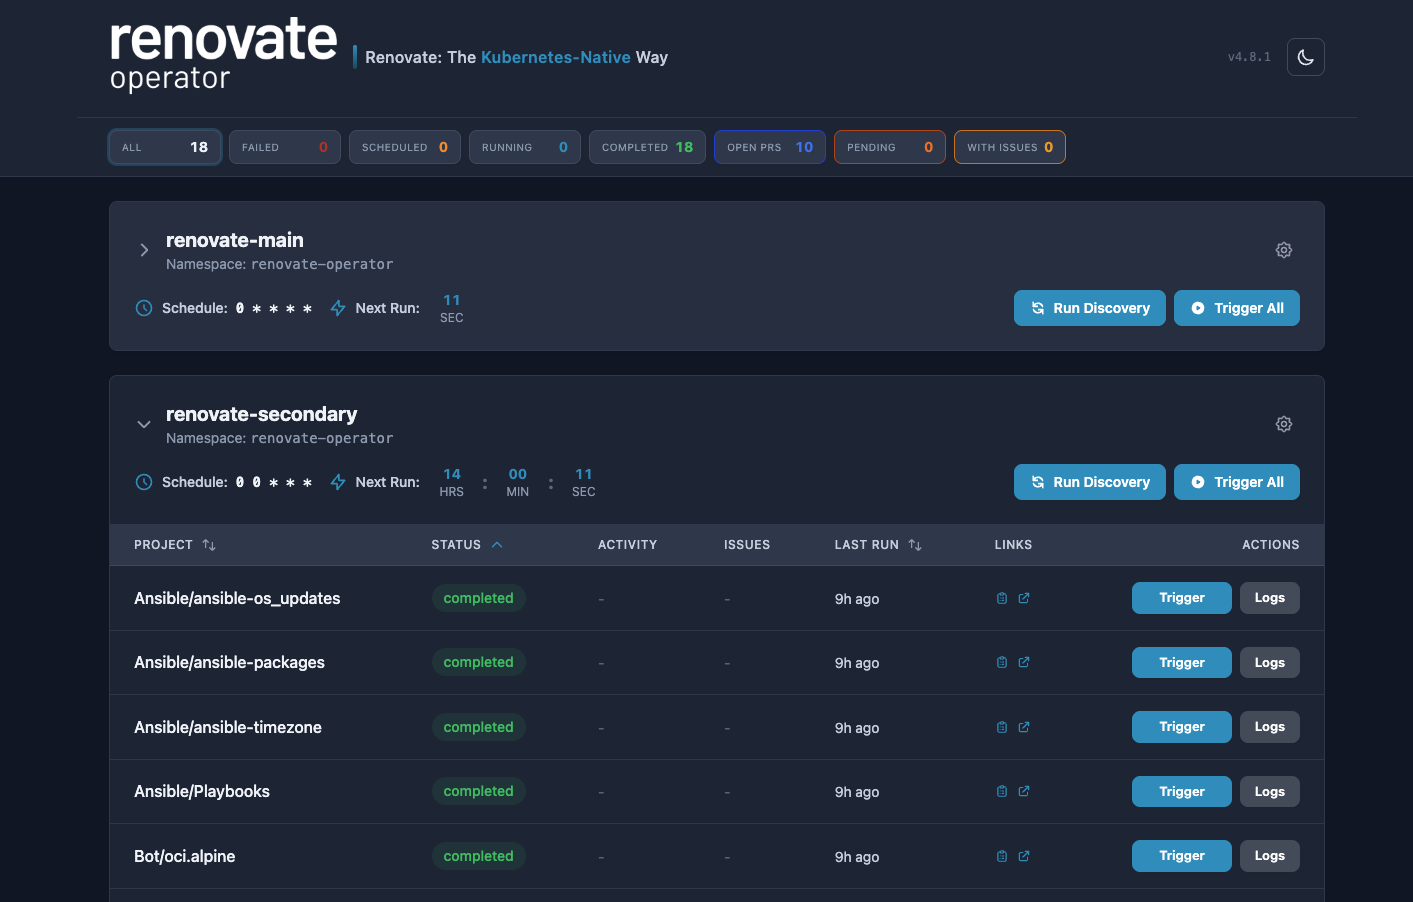 mogenius/renovate-operator
Operator to streamline renovate executions in Kubernetes
 ricccrd/dd
JIT-based userspace Linux kernel that runs containers natively on Apple Silicon macOS without a VM. Drop-in Docker Engine API replacement with…
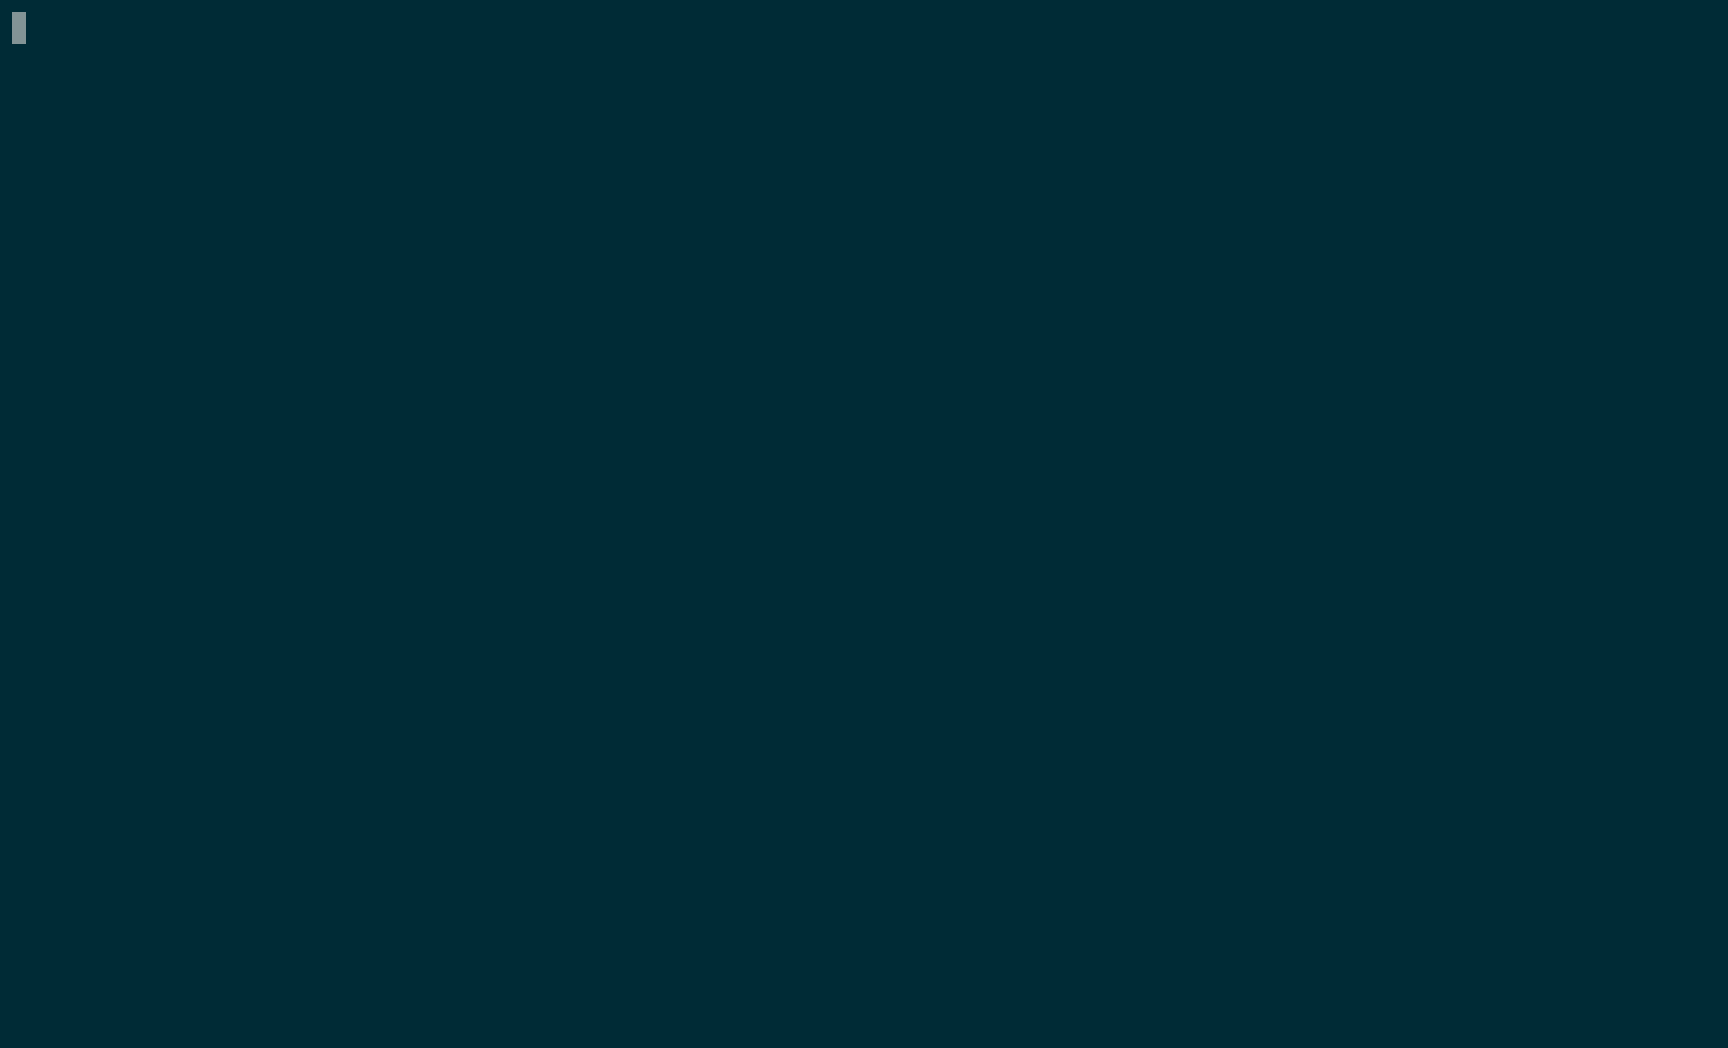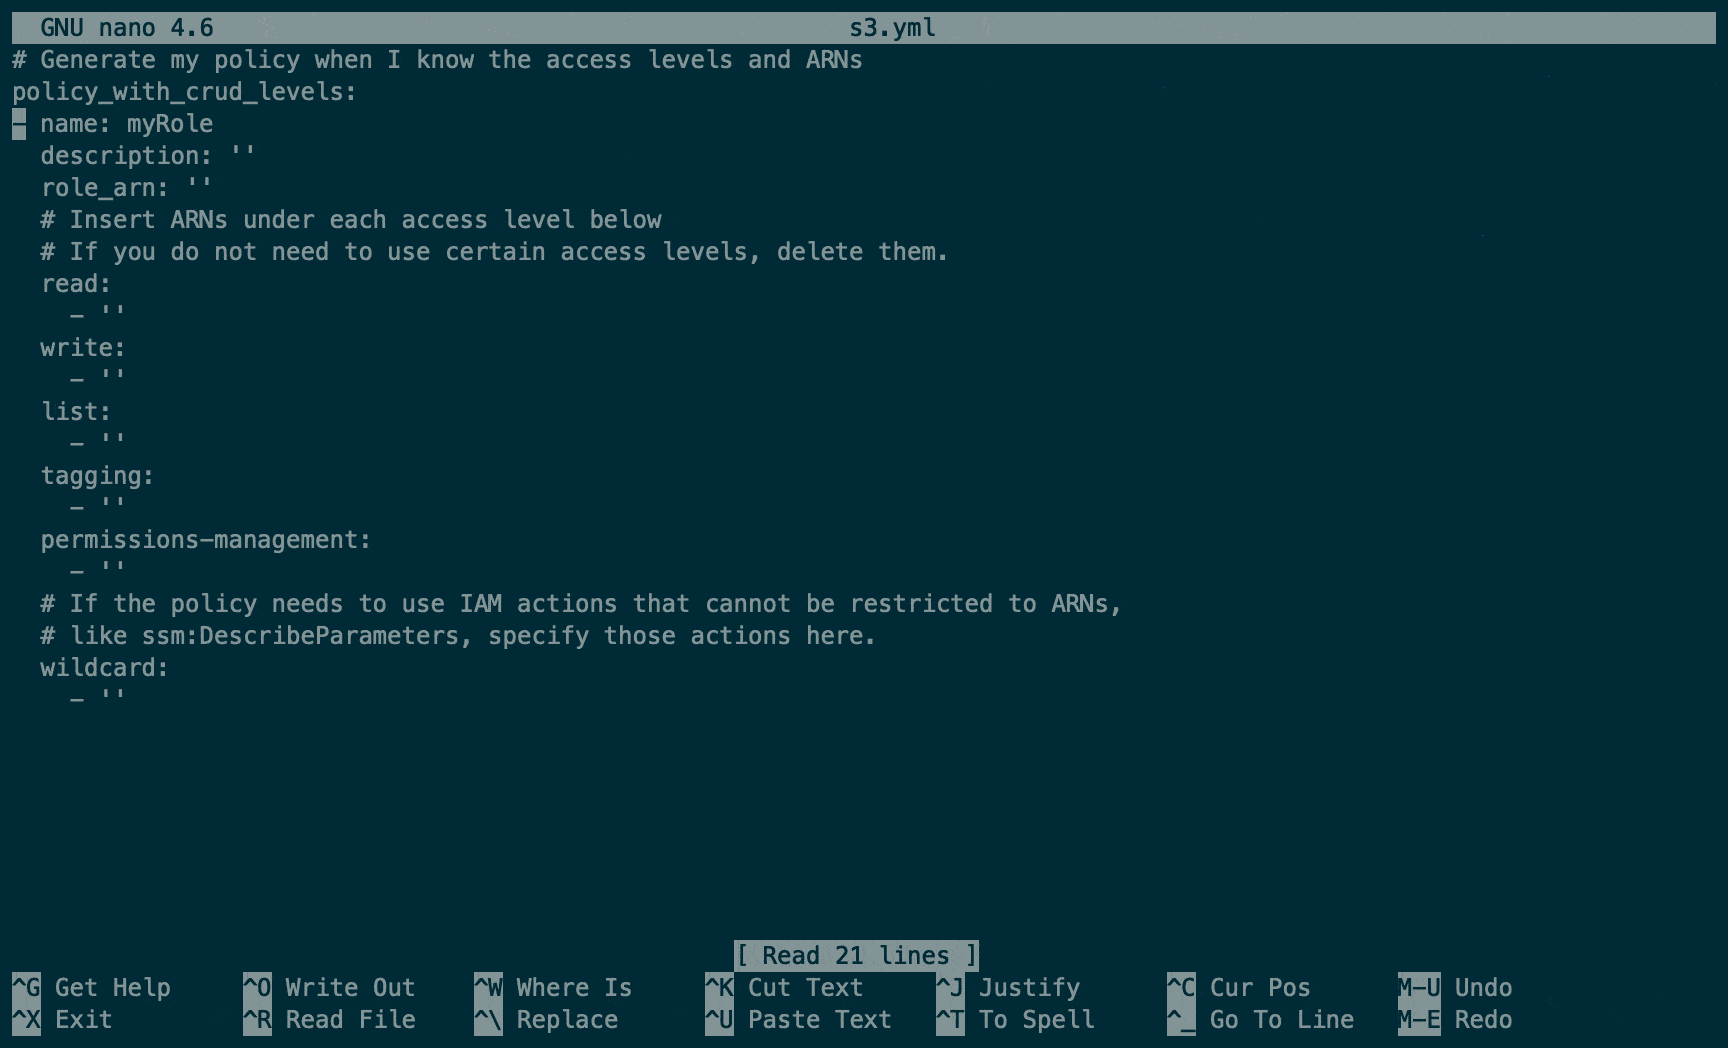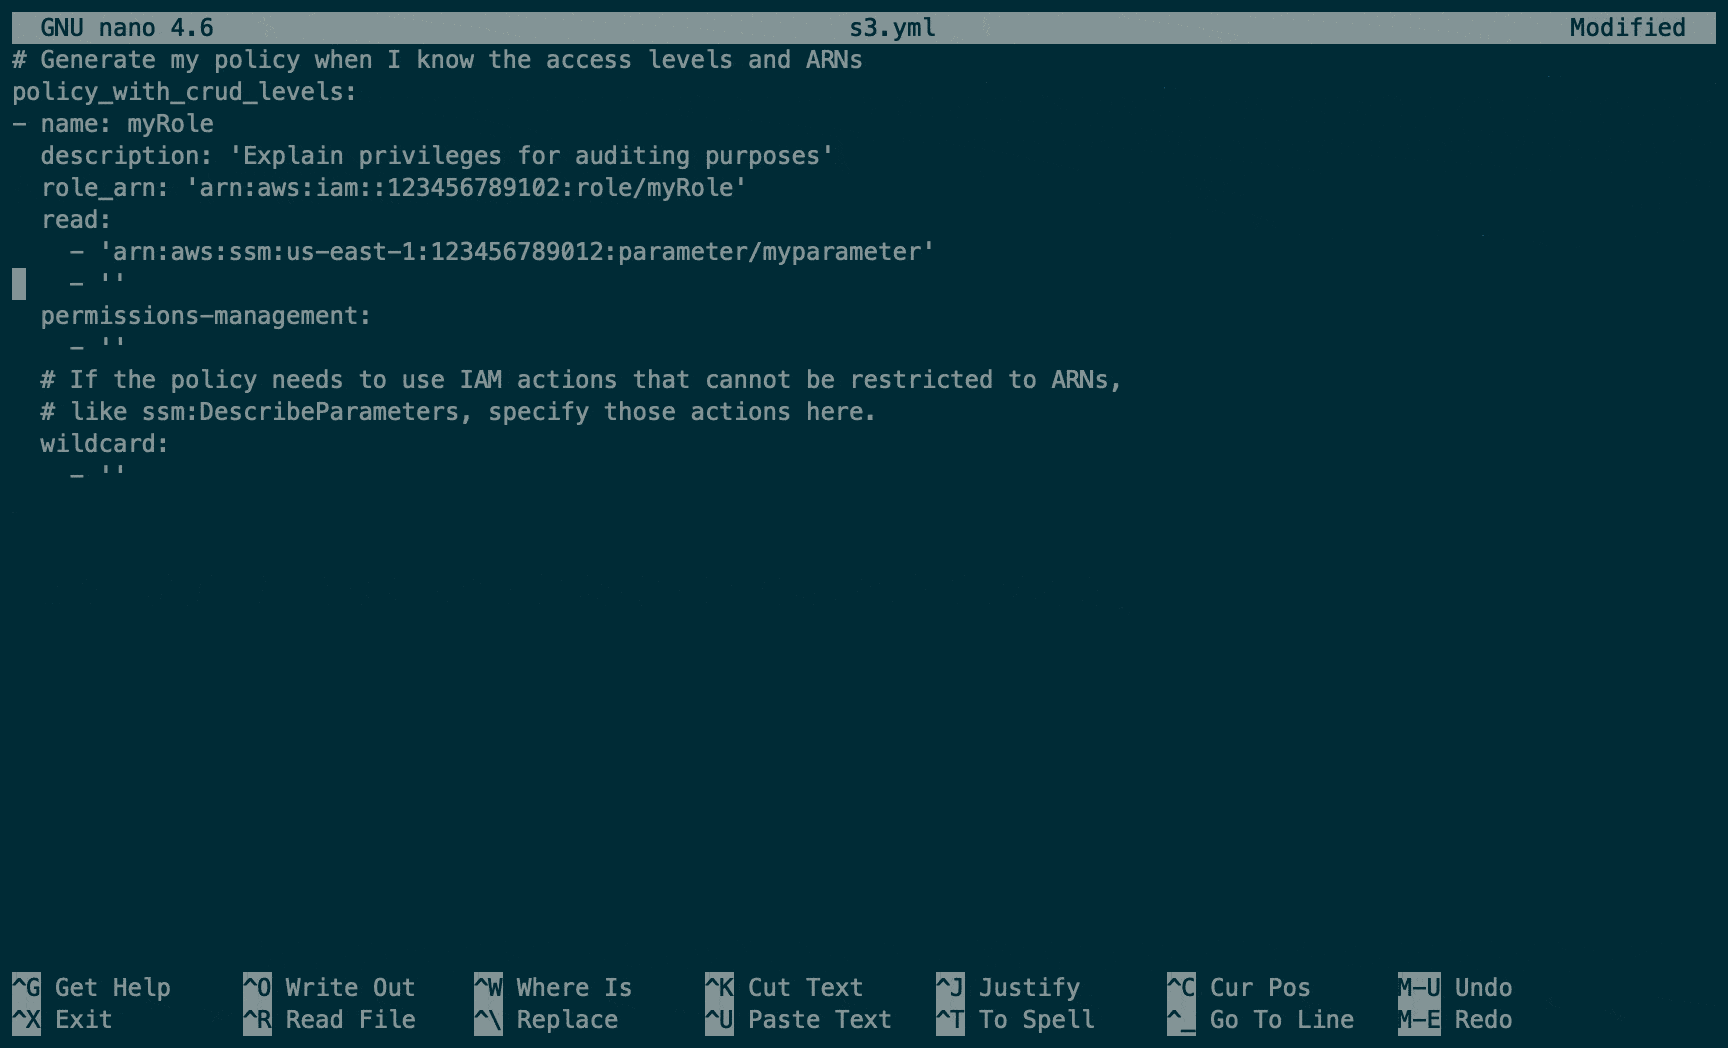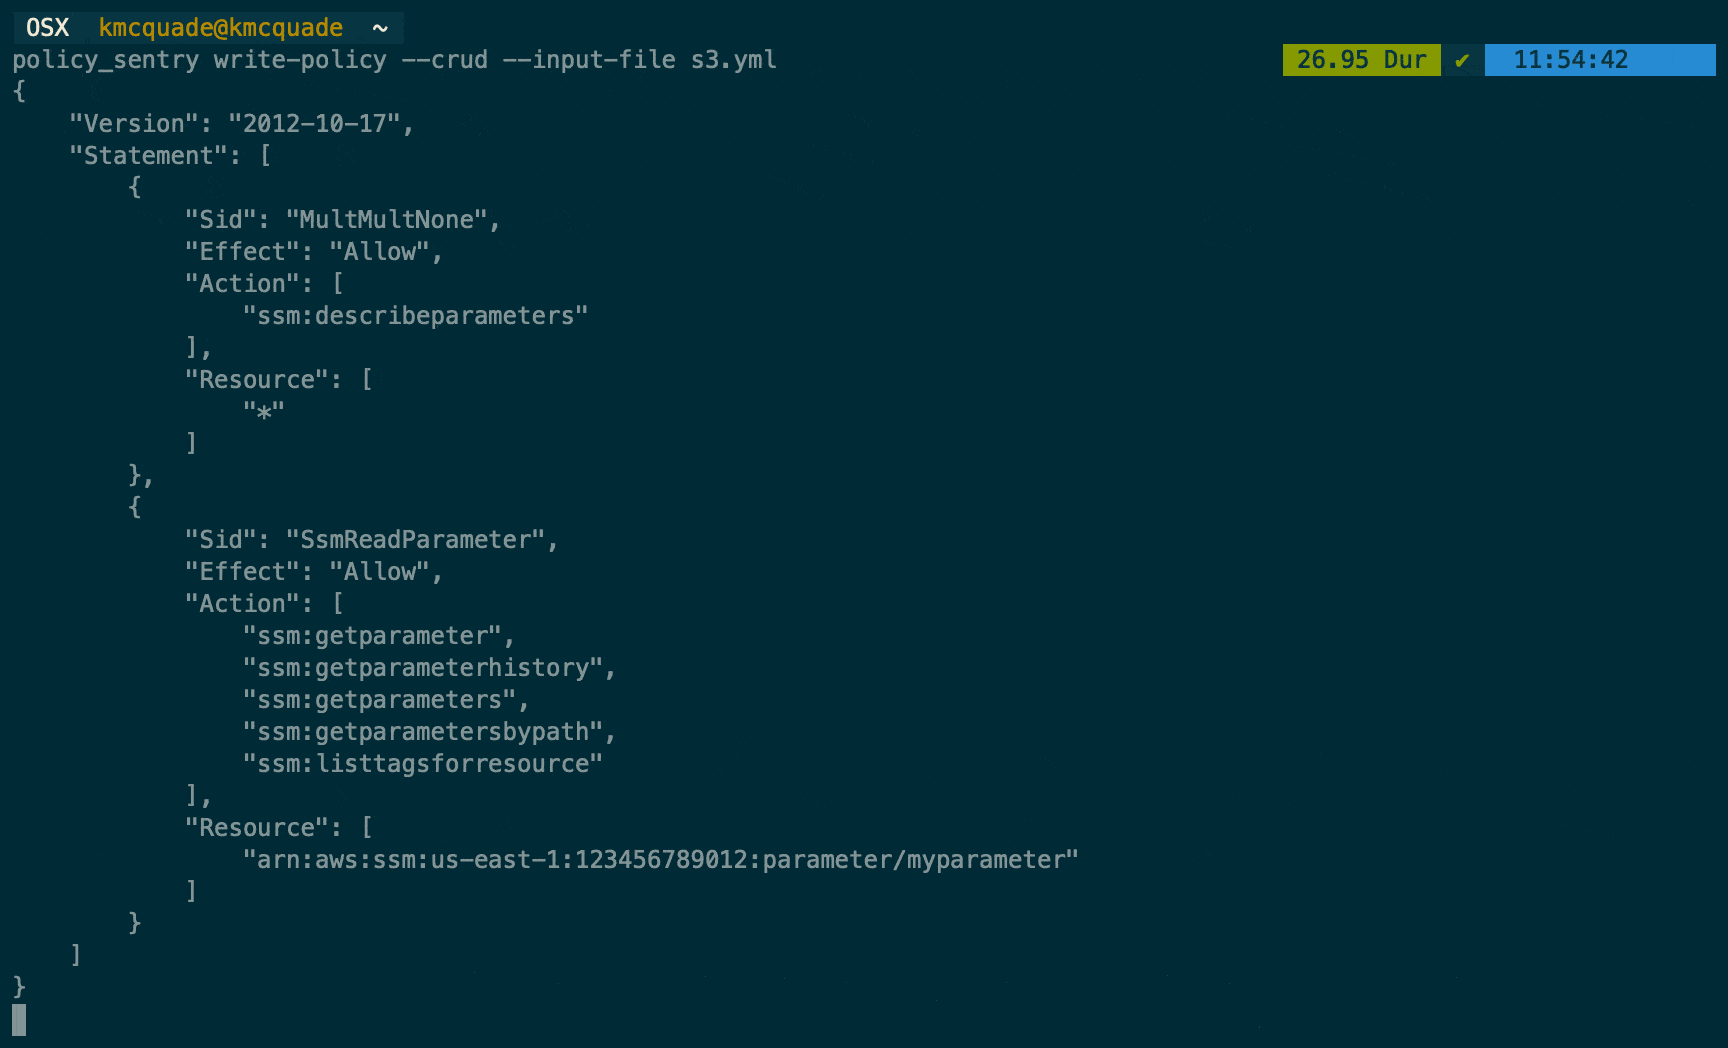 salesforce/policy_sentry
Generates least-privilege AWS IAM policies based on resource ARNs and access levels, automating secure policy creation for cloud infrastructure.
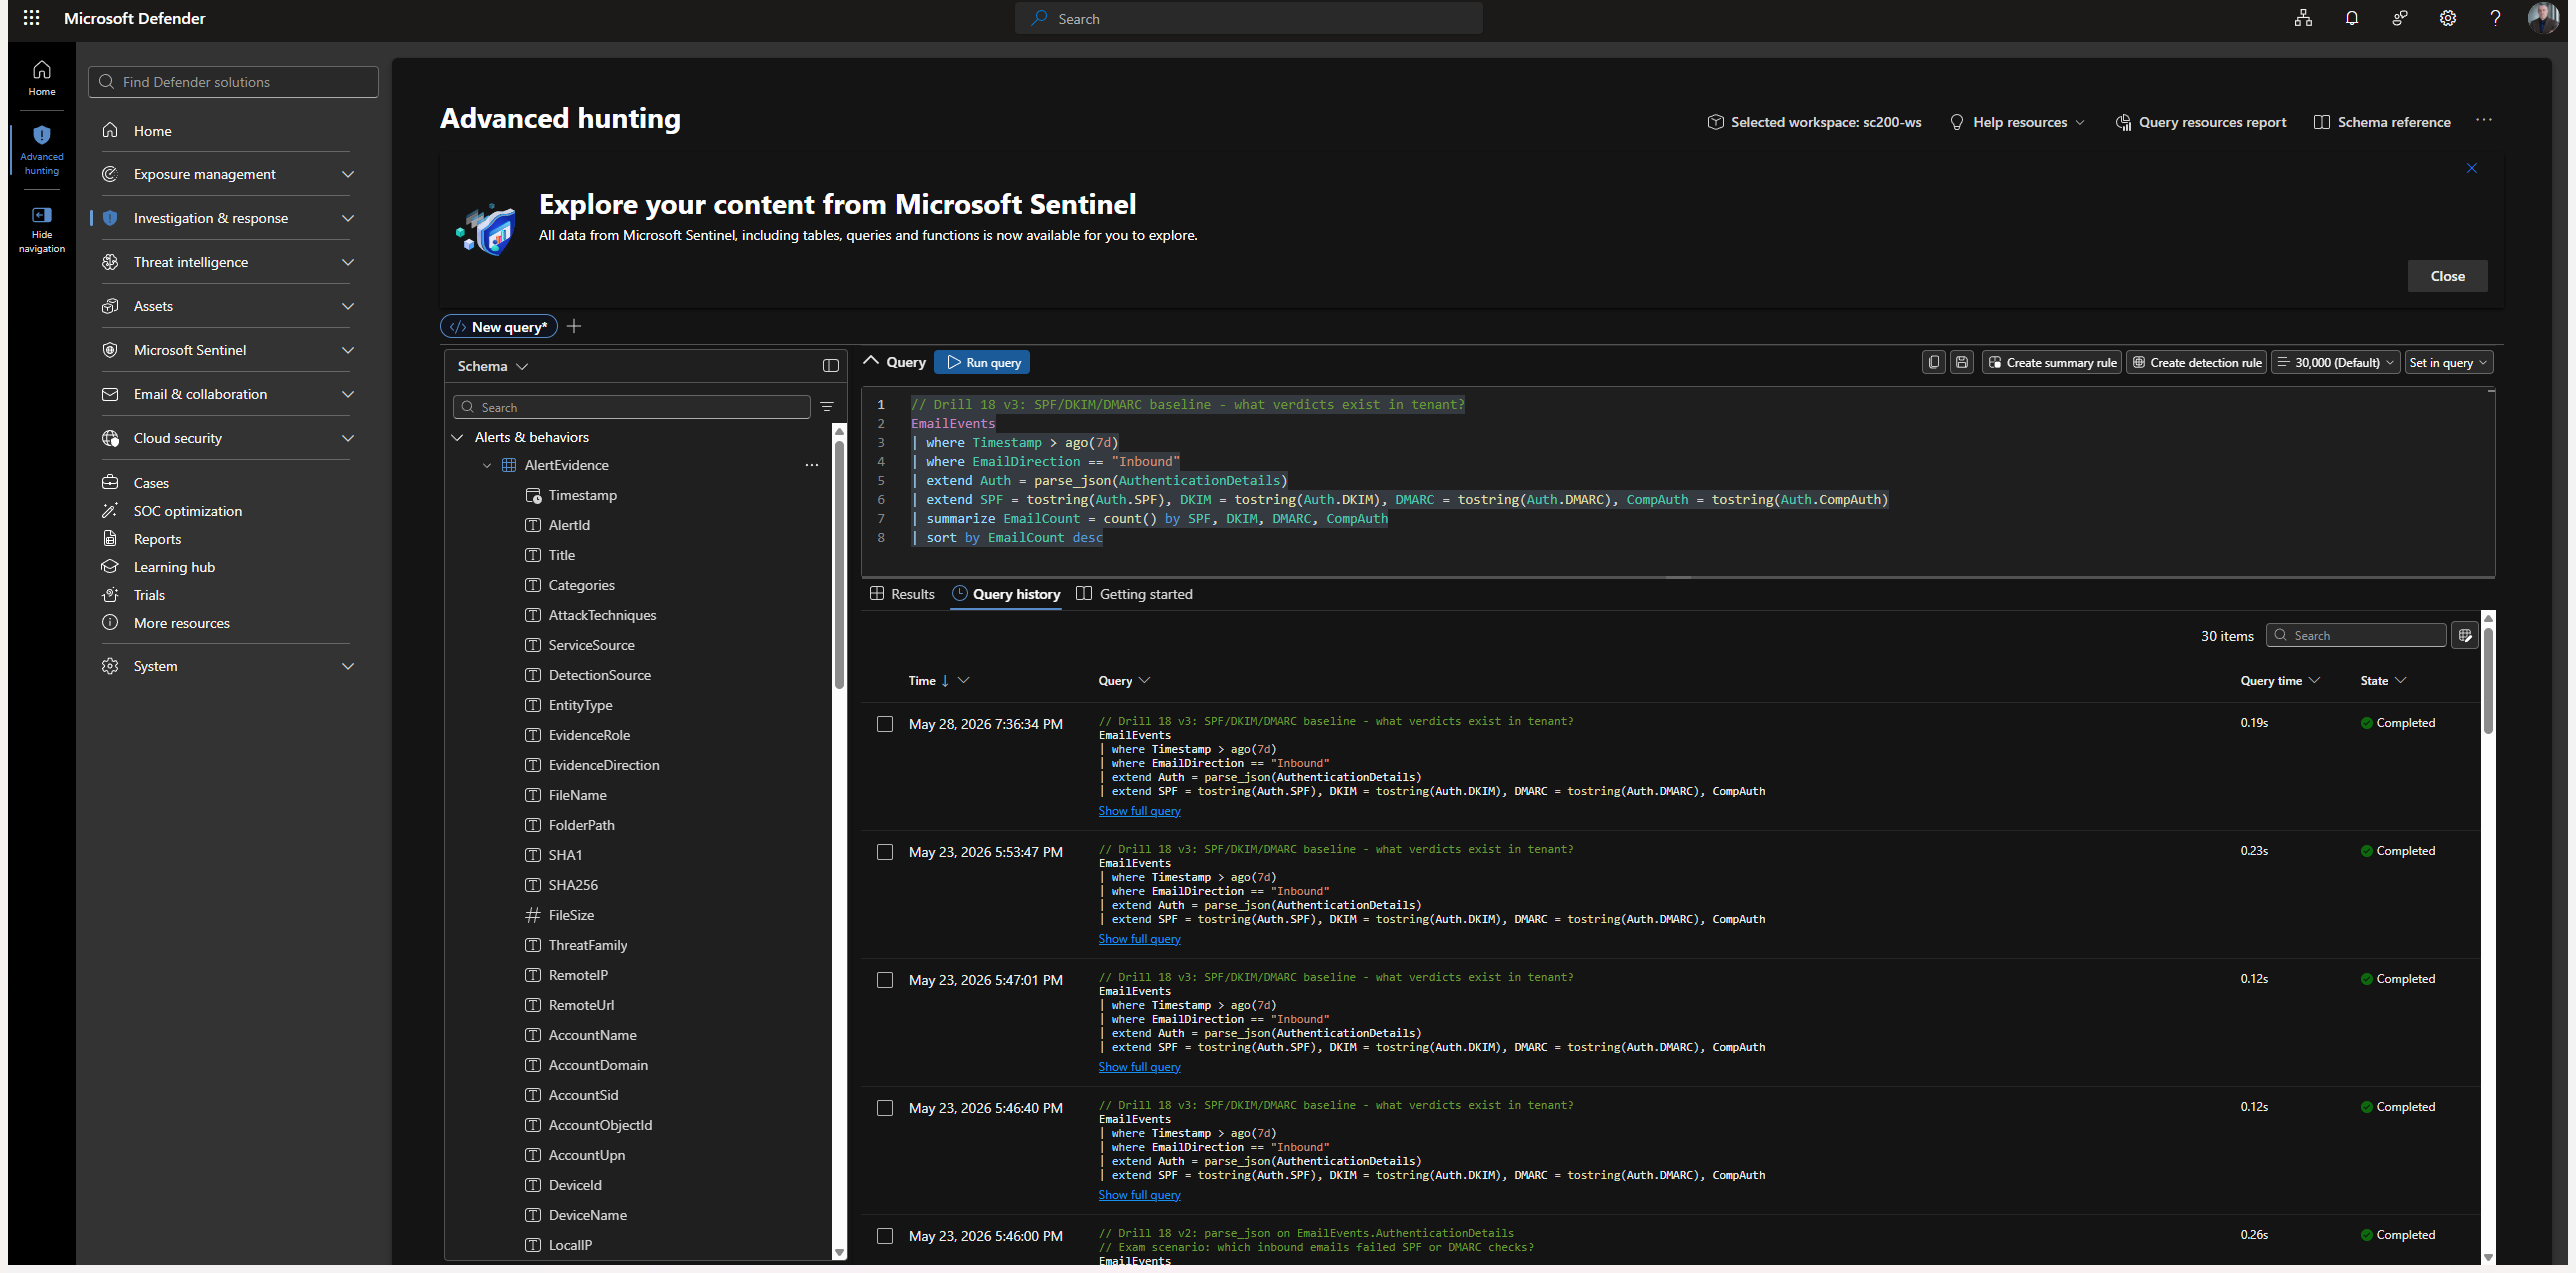 ibondarenko1/azure-sentinel-detection-engineering
9 MITRE ATT&CK-mapped KQL detections on a live Microsoft Sentinel + Defender XDR environment (control-plane, endpoint, identity), with a PR-gated…
 chaosblade-io/chaosblade
An easy to use and powerful chaos engineering experiment toolkit.(阿里巴巴开源的一款简单易用、功能强大的混沌实验注入工具)
 vishnunandan555/cordon
Run any command inside a restricted filesystem view on Linux
 vercel-labs/deepsec
Agent-powered vulnerability scanner for large-scale codebases. Uses LLMs to find hard-to-detect security issues via regex matchers and AI…
 fencesandbox/fence
Lightweight, container-free sandbox for running commands with network and filesystem restrictions
 pgporada/ansible-role-cve
Mitigates CVE-2016-5195 aka DirtyCOW
 offensive360/sast-scan-action
GitHub Action: Offensive360 SAST scan with SARIF output for code scanning. 60+ languages. Free for open source.
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 nearai/ironclaw
Secure, private AI agent operating system with local encrypted storage, OAuth/SSO authentication, policy-based access control, and extensible…
 nvidia/nemoclaw
Run agents like Hermes, LangChain Deep Agents, and OpenClaw more securely inside NVIDIA OpenShell with managed inference
 jsdelivr/globalping-probe
The globalping probe code that runs on your hardware and connects to the global community network of probes
 codesource/copyfail-check
Shell script to detect CVE-2026-31431 (Copy Fail) exposure and mitigations on Linux systems: kernel check, module state, boot params, AF_ALG…
 mikesplain/cve-2014-3566-poodle-cookbook
Chef cookbook that detects and fails runs on servers vulnerable to CVE-2014-3566 (POODLE) by scanning specified SSL ports, serving as both a security…
 eximiait/cve-2026-31431
Ansible playbooks to check and mitigate CVE-2026-31431 on Linux hosts, with scripts for local, remote, and containerized environments, including…