CVE-2026-31431-Copy-Fail---Vulnerability-Detection-Script

Detection script for CVE-2026-31431 (Copy Fail) that checks kernel version, patch presence, kernel configs, AF_ALG socket availability, setuid…

Detection script for CVE-2026-31431 (Copy Fail) that checks kernel version, patch presence, kernel configs, AF_ALG socket availability, setuid…

Rule-based linter for OpenSSH client config files that detects duplicate hosts, missing identity files, weak algorithms, wildcard ordering issues,…

MCP is being adopted rapidly. Security guidance is lagging behind. This checklist gives security engineers, platform teams, and technical leaders a…

A fast port scanner written in go with a focus on reliability and simplicity.

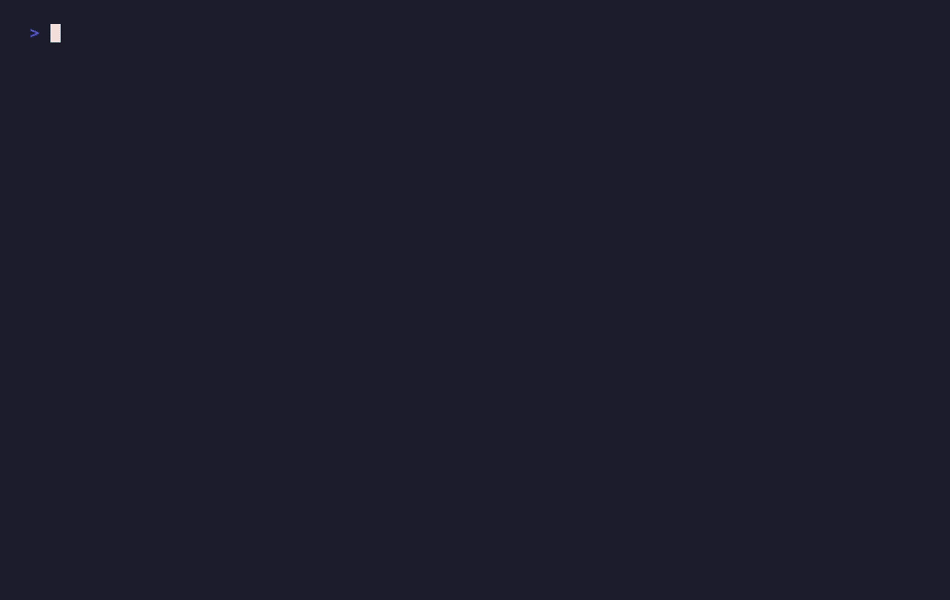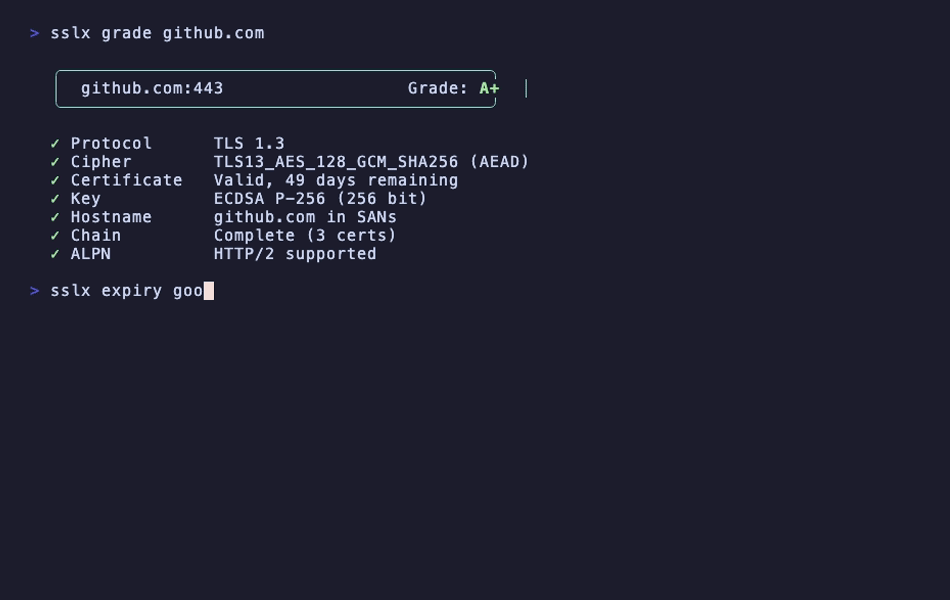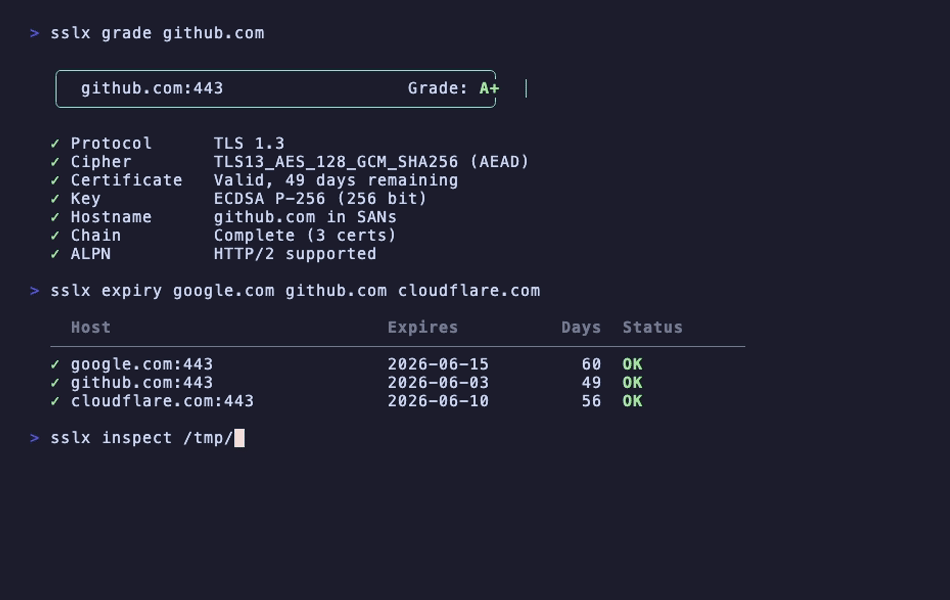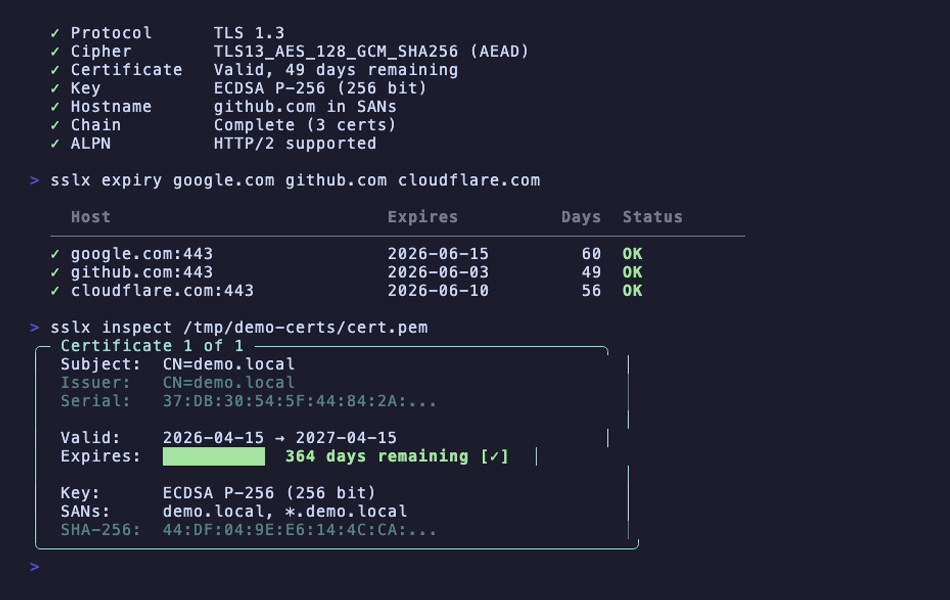
A fast, modern alternative to OpenSSL's CLI - inspect, grade, and manage certificates from the terminal

CLI tool that explains CVEs in plain English and scans repos for impact. Powered by Claude.

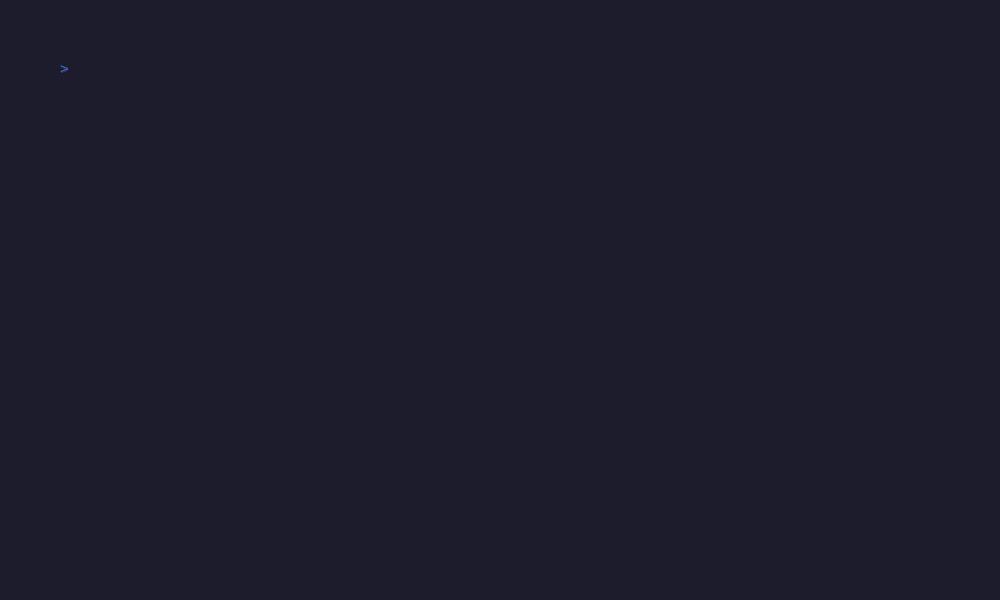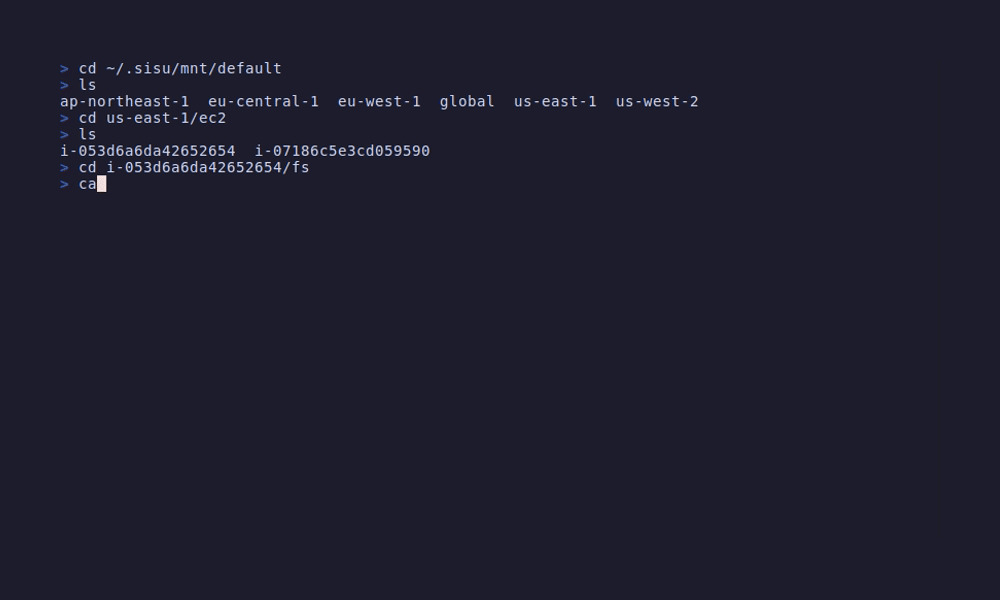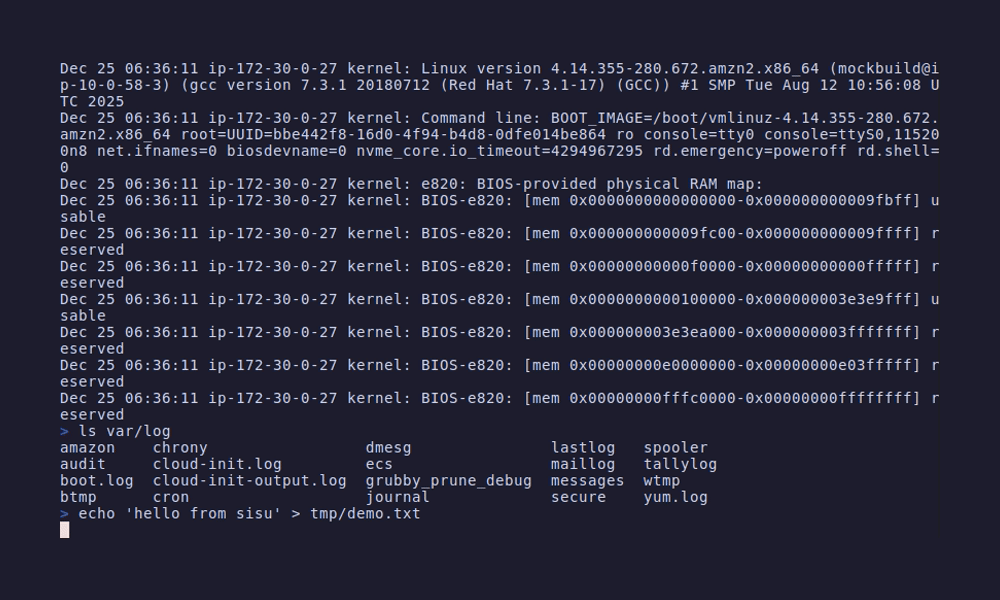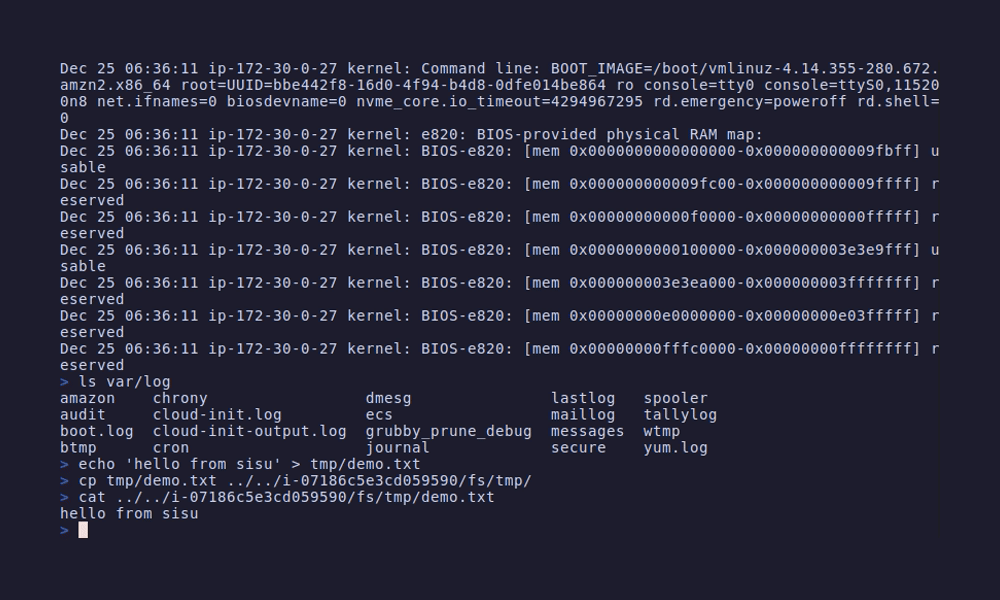
Mounts AWS resources as a local filesystem for infrastructure exploration, security auditing, and configuration analysis using standard Unix tools…

Vulnerability Assessment Scanner with Report Generation

HTTP Web Server probing

Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…

Forked from https://gitlab.alpinelinux.org/kaniini/secfixes-tracker

Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.

Safe detection tooling for CVE-2026-31431 "Copy Fail" and CVE-2026-43284 "Dirty Frag" — a local privilege escalation in the Linux kernel's algif_aead…

Corelight-Ansible-Roles are a collection of Ansible Roles and playbooks that install, configure, run and manage a variety of Corelight, Suricata and…

AIO Cloud Managment Server

Multi-Ecosystem Malicious Package Detection and Supply Chain Security Scanner

provides a Firewall Manager API designed to centralize and streamline the management of firewall configurations

A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.