
Archived
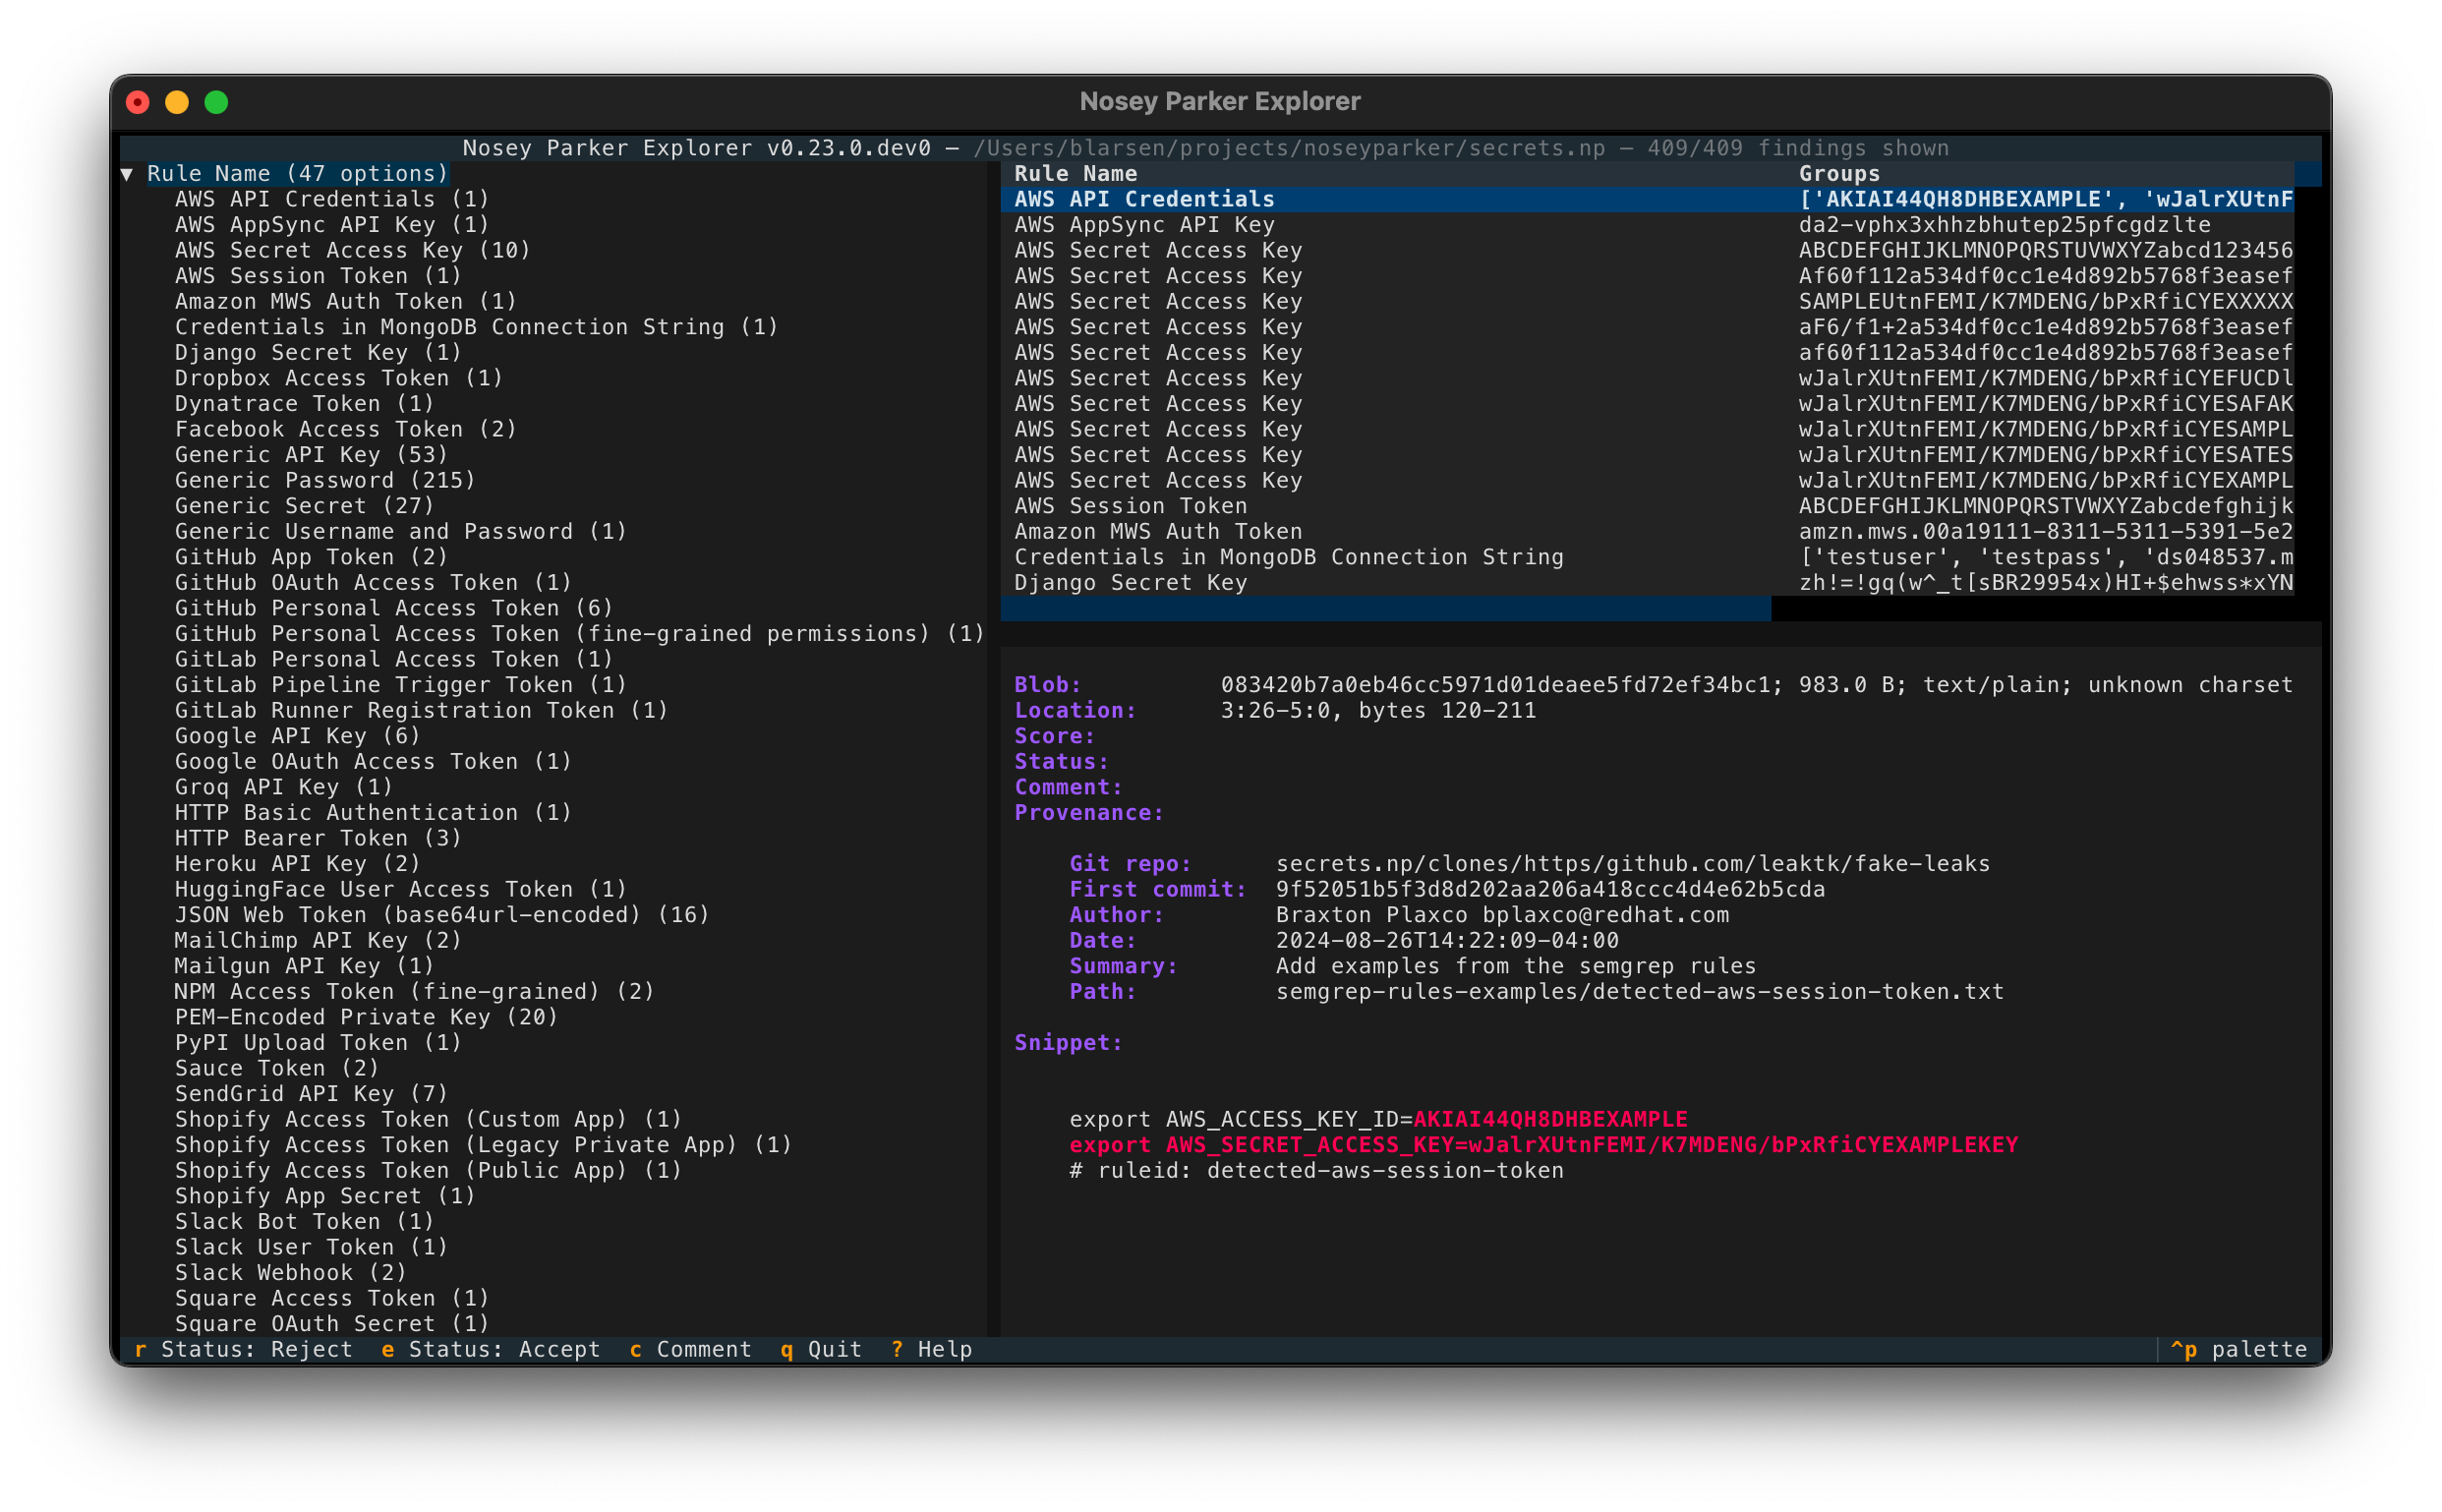
noseyparker
 praetorian-inc/noseyparker
Nosey Parker is a command-line tool that finds secrets and sensitive information in textual data and Git history.
code-analysisdevsecopsinformation-gathering+3
praetorian-inc/noseyparkerNosey Parker is a command-line tool that finds secrets and sensitive information in textual data and Git history.
 octarinesec/kube-scan
kube-scan: Octarine k8s cluster risk assessment tool
 hawkeyesec/scanner-cli
A project security/vulnerability/risk scanning tool
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 joshlarsen/aws-recon
Multi-threaded AWS inventory collection tool with a focus on security-relevant resources and metadata.
 praetorian-inc/gato
GitHub Actions Pipeline Enumeration and Attack Tool
 praetorian-inc/gokart
A static analysis tool for securing Go code
 reposaur/reposaur
Open source compliance tool for development platforms.
 nomograph/kit
Verified tool registry manager. Manages developer toolchains from git-based registries.

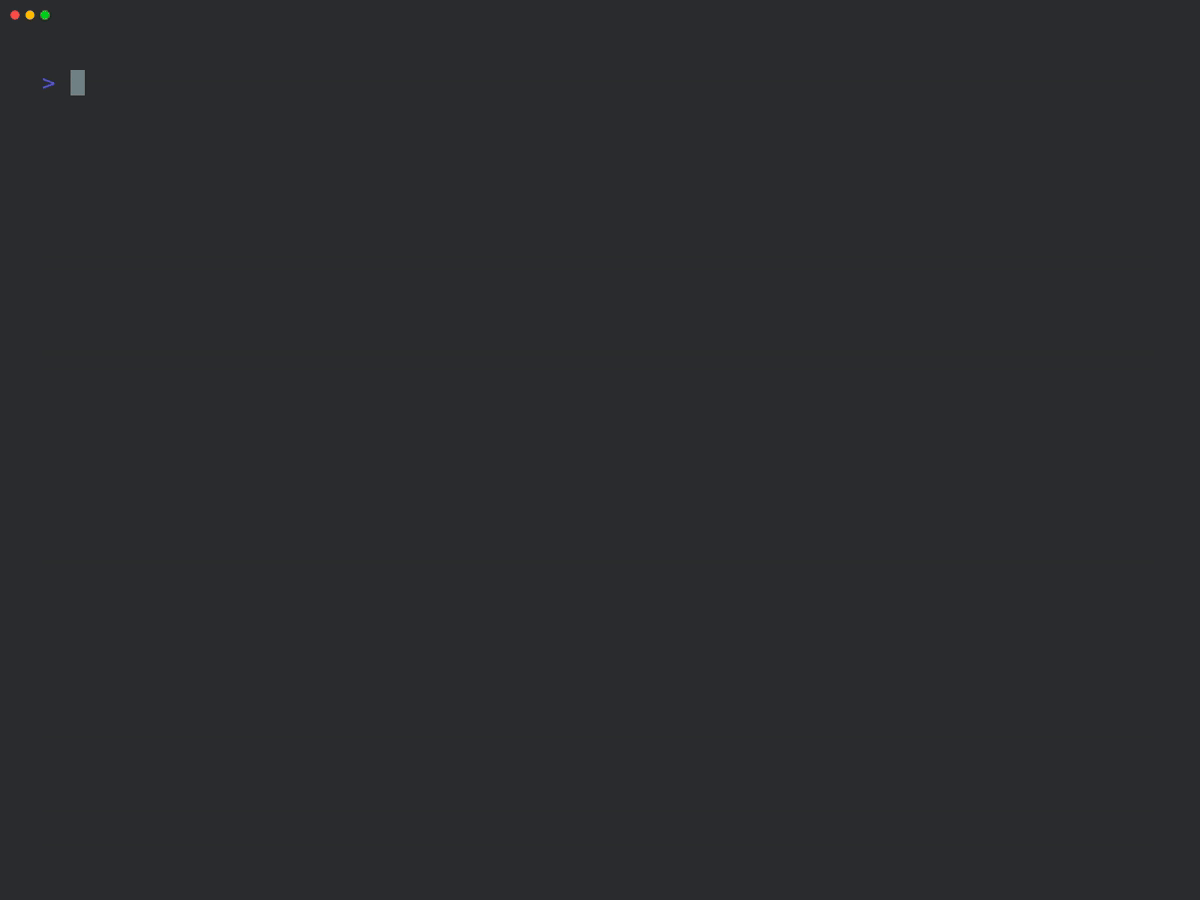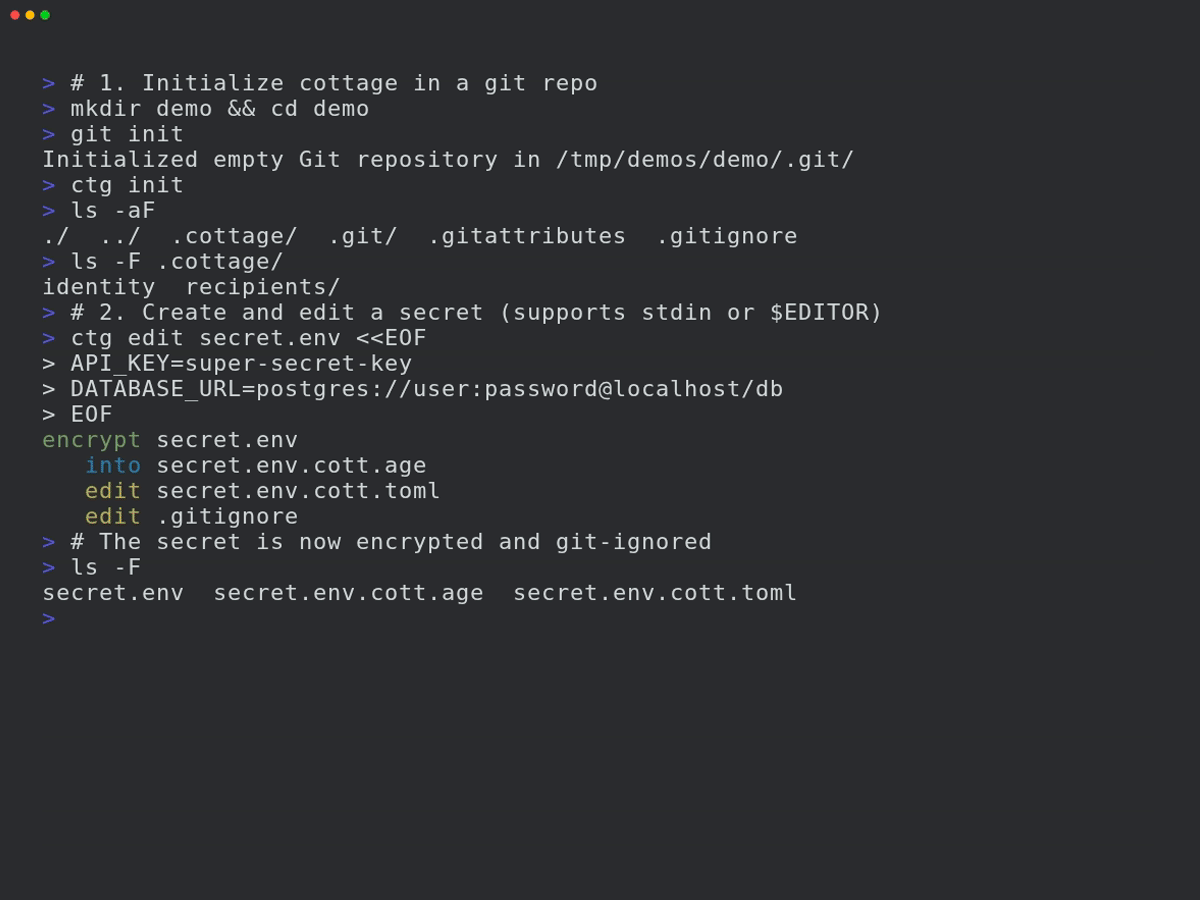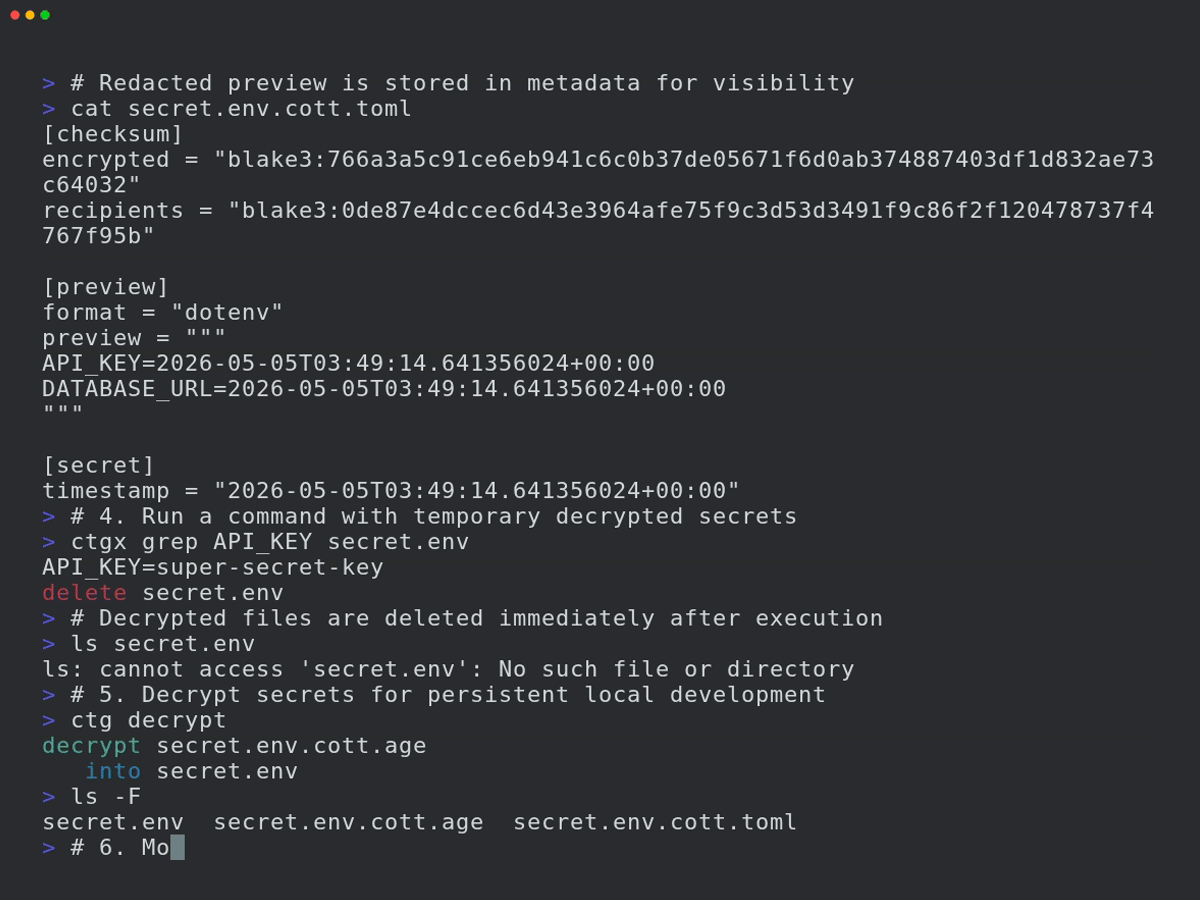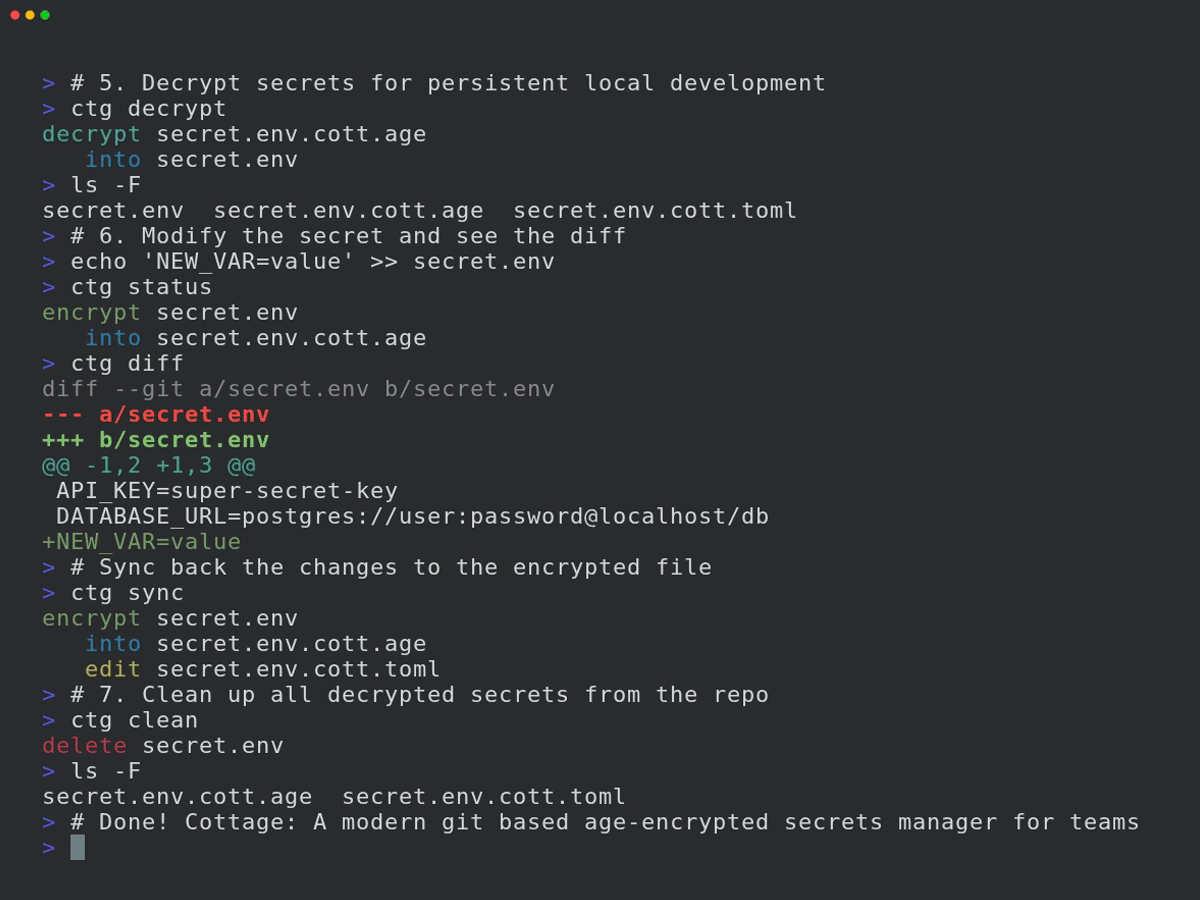 sayanarijit/cottage
A modern git based age-encrypted secrets manager for teams.
 scopeblind/scopeblind-gateway
Ed25519 signed receipts + Cedar policies for AI agents. Finance mandate gate (Legate), proof packs, 3 IETF Internet-Drafts. npx protect-mcp
 digitalocean/nginxconfig.io
⚙️ NGINX config generator on steroids 💉
 facebook/infer
A static analyzer for Java, C, C++, and Objective-C
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
 dependency-check/dependencycheck
OWASP dependency-check is a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies.
 hahwul/dalfox
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
