

GitLeaks
 niclas-zone/ctr/gitleaks
Containerized secret scanning tool that detects exposed credentials, API keys, and tokens in Git repositories using regex and entropy-based…
code-analysiscontainer-securitydevsecops+1
niclas-zone/ctr/gitleaksContainerized secret scanning tool that detects exposed credentials, API keys, and tokens in Git repositories using regex and entropy-based…
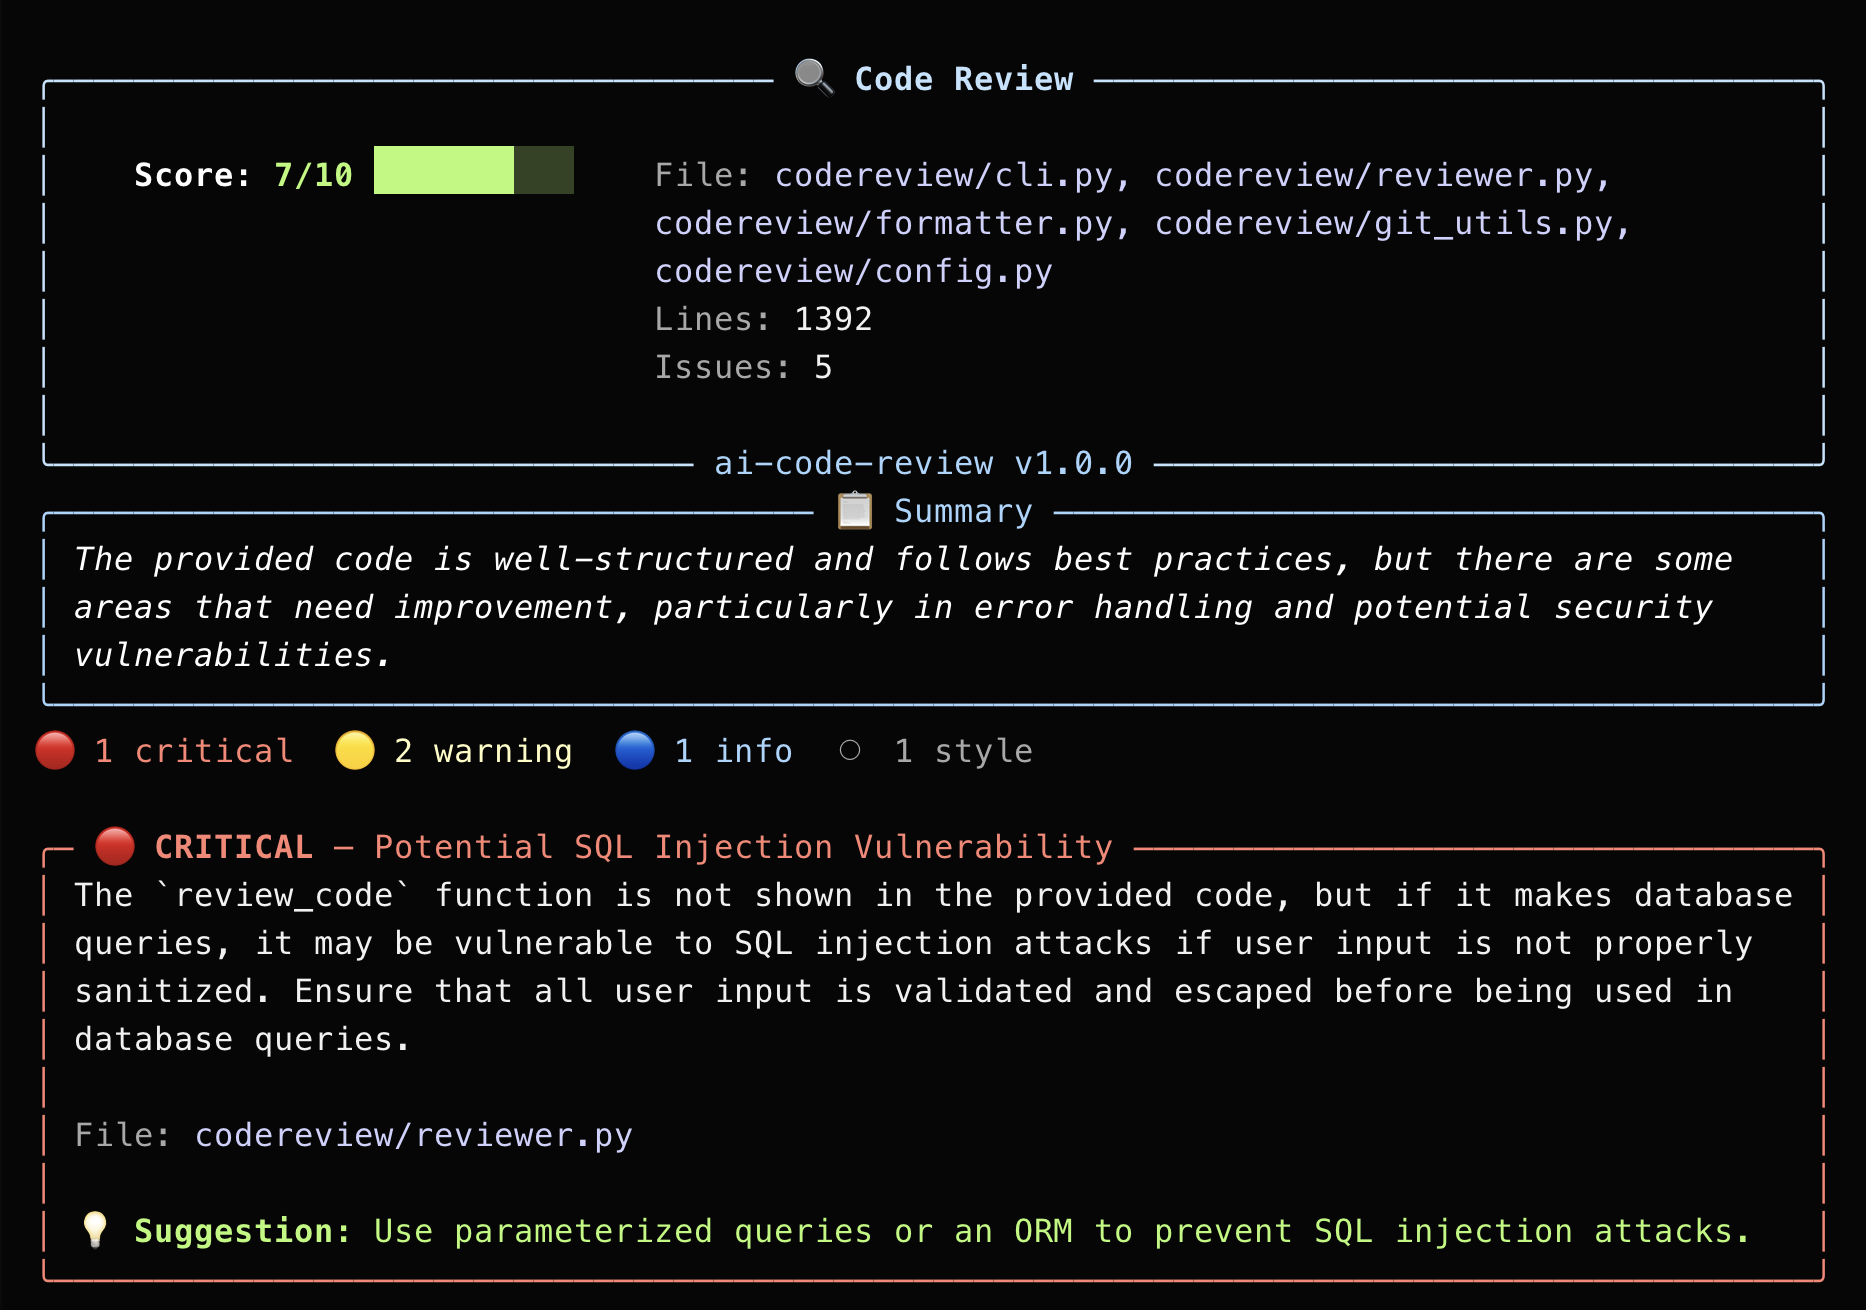
 jaydendancer12/ai-code-review
AI-powered CLI tool that reviews code for security vulnerabilities, bugs, and anti-patterns using LLMs. Supports local and cloud providers, git…
 mikesplain/cve-2014-3566-poodle-cookbook
Chef cookbook that detects and fails runs on servers vulnerable to CVE-2014-3566 (POODLE) by scanning specified SSL ports, serving as both a security…
 neelkotnis/azure-security-auditor
CLI tool to audit Azure security posture, RBAC, NSGs, storage, identity, and encryption
 niclas-zone/ci/gitleaks
CI component for Gitleaks SAST tool that scans git repositories for hardcoded secrets, API keys, and tokens with custom and remote configuration…
 mayank729/cve-2025-55182-scanner
🔍 Scan for CVE-2025-55182 risks in React Server Components with this non-intrusive tool that helps detect critical vulnerabilities in your…
 hackervlogofficial/cve-2026-23918
This is a proactive tool for security auditing. For your GitHub repository, you’ll want a description that highlights its safety (non-intrusive) and…
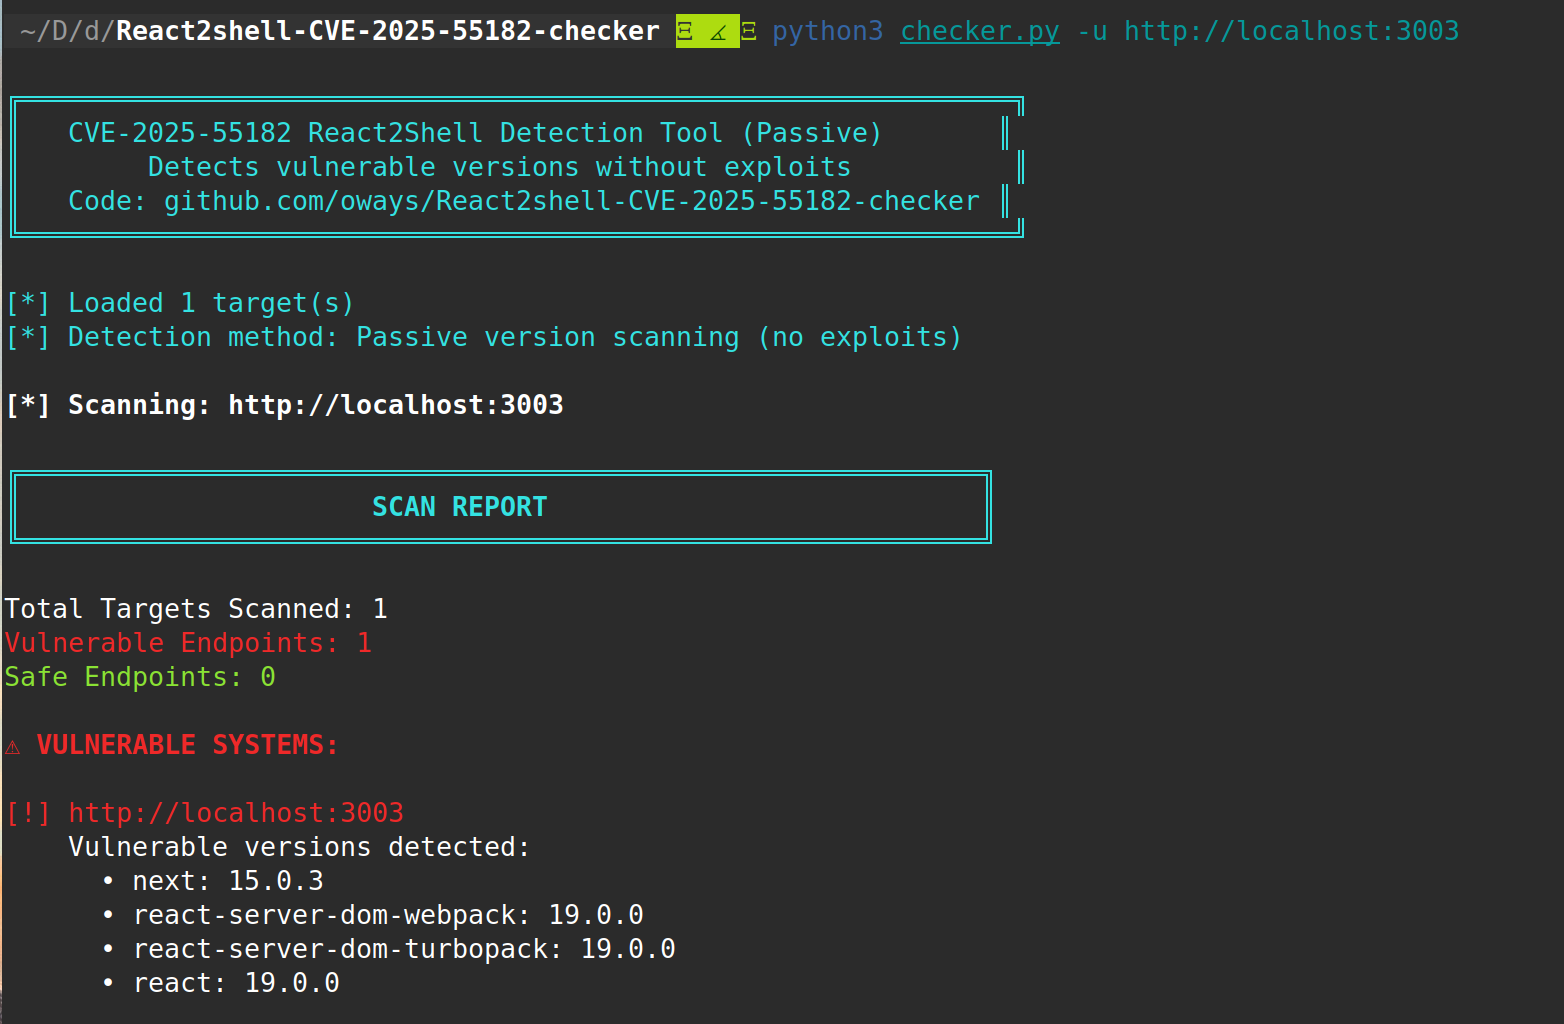 oways/react2shell-cve-2025-55182-checker
Passive CVE-2025-55182 detection tool for vulnerable React Server Components. Scans package.json, JavaScript bundles, HTTP headers, and API endpoints…
 thesisgroup3/secassessment_gapdetect
Rule-based CLI tool that grades organizational defenses against MITRE ATT&CK and D3FEND frameworks, detects security gaps, and proposes mitigations.…
 rashedhasan090/aegisjava
I have created AegisJava, a tool to fix (detect and mitigate) CVE-2025-30749.
 jibaru/cve-2025-66478-github-patcher
Go-based automation tool that scans GitHub repositories for vulnerable Next.js versions (CVE-2025-66478) and automatically creates pull requests with…
 nrnw/cve-2026-24061-gnu-inetutils-telnet-detector
A passive detection tool for identifying potential exposure to CVE-2026-24061 in GNU inetutils telnet installations
 titus-soc/-cve-2024-3094-vulnerability-checker-fixer-public
A lightweight utility designed to detect and remediate systems affected by CVE-2024-3094, a critical vulnerability impacting [insert affected…
 3pplus/loguccino
Scan and patch tool for CVE-2021-44228 and related log4j concerns.
 shoucheng3/jeremylong__dependencycheck_cve-2018-12036_3-1-2
Software composition analysis tool that detects publicly disclosed vulnerabilities in project dependencies using CPE matching, generating detailed…
 pierdipi/unicode-control-characters-action
A GitHub Action to find Unicode control characters using the Red Hat diagnostic tool https://access.redhat.com/security/vulnerabilities/RHSB-2021-007…
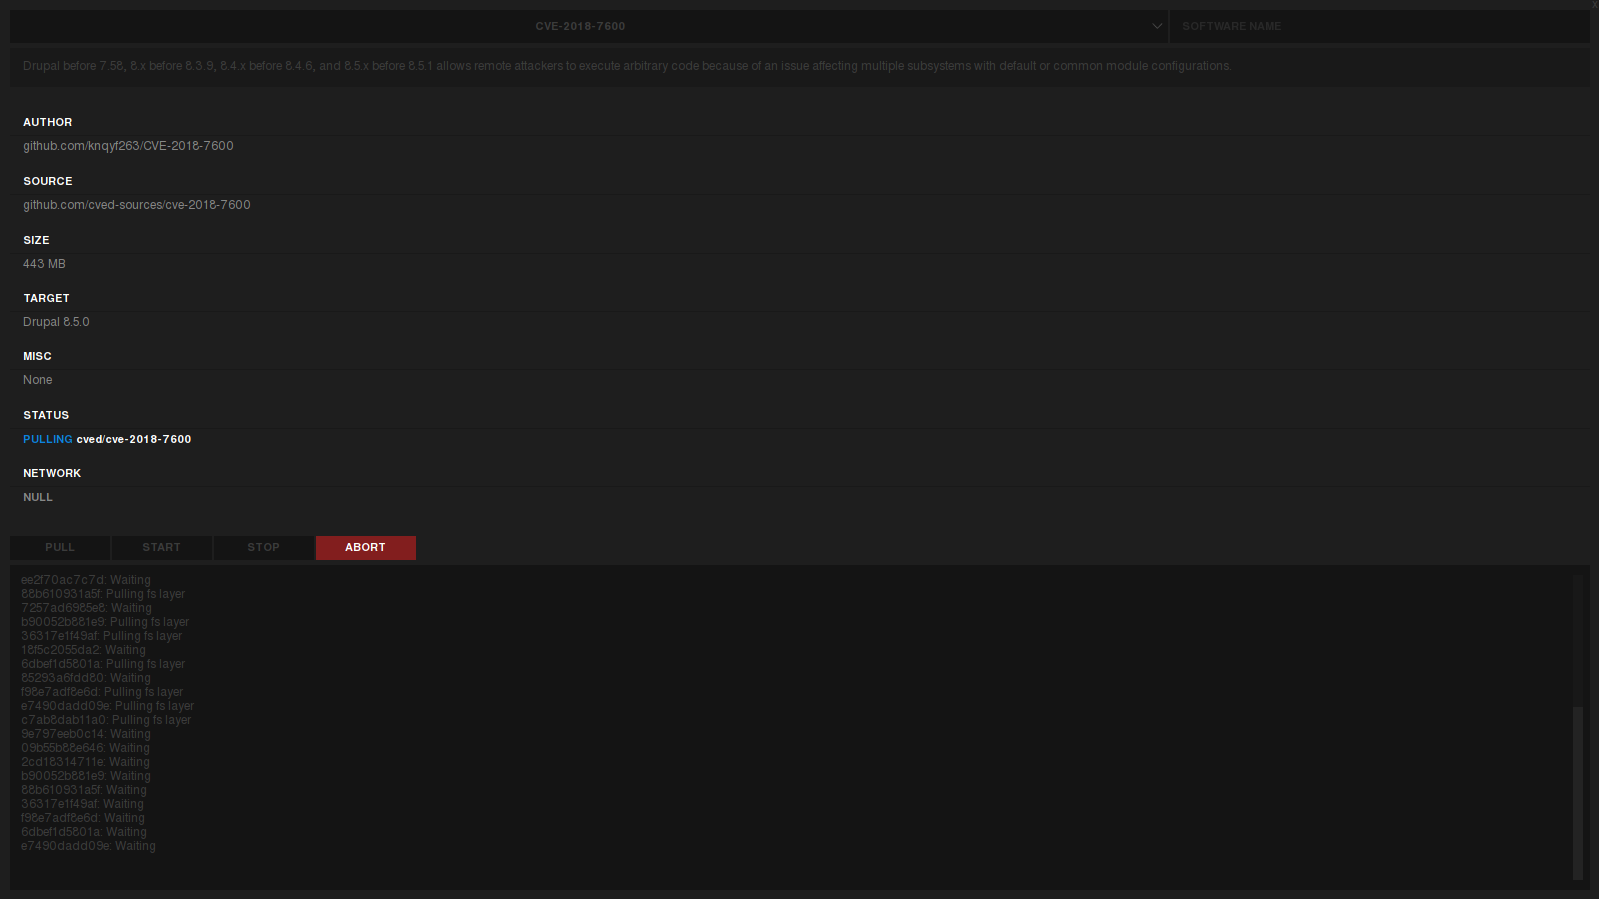 git-rep-src/cved
A tool to manage vulnerable docker containers
 openclarity/kubeclarity
KubeClarity is a tool for detection and management of Software Bill Of Materials (SBOM) and vulnerabilities of container images and filesystems