
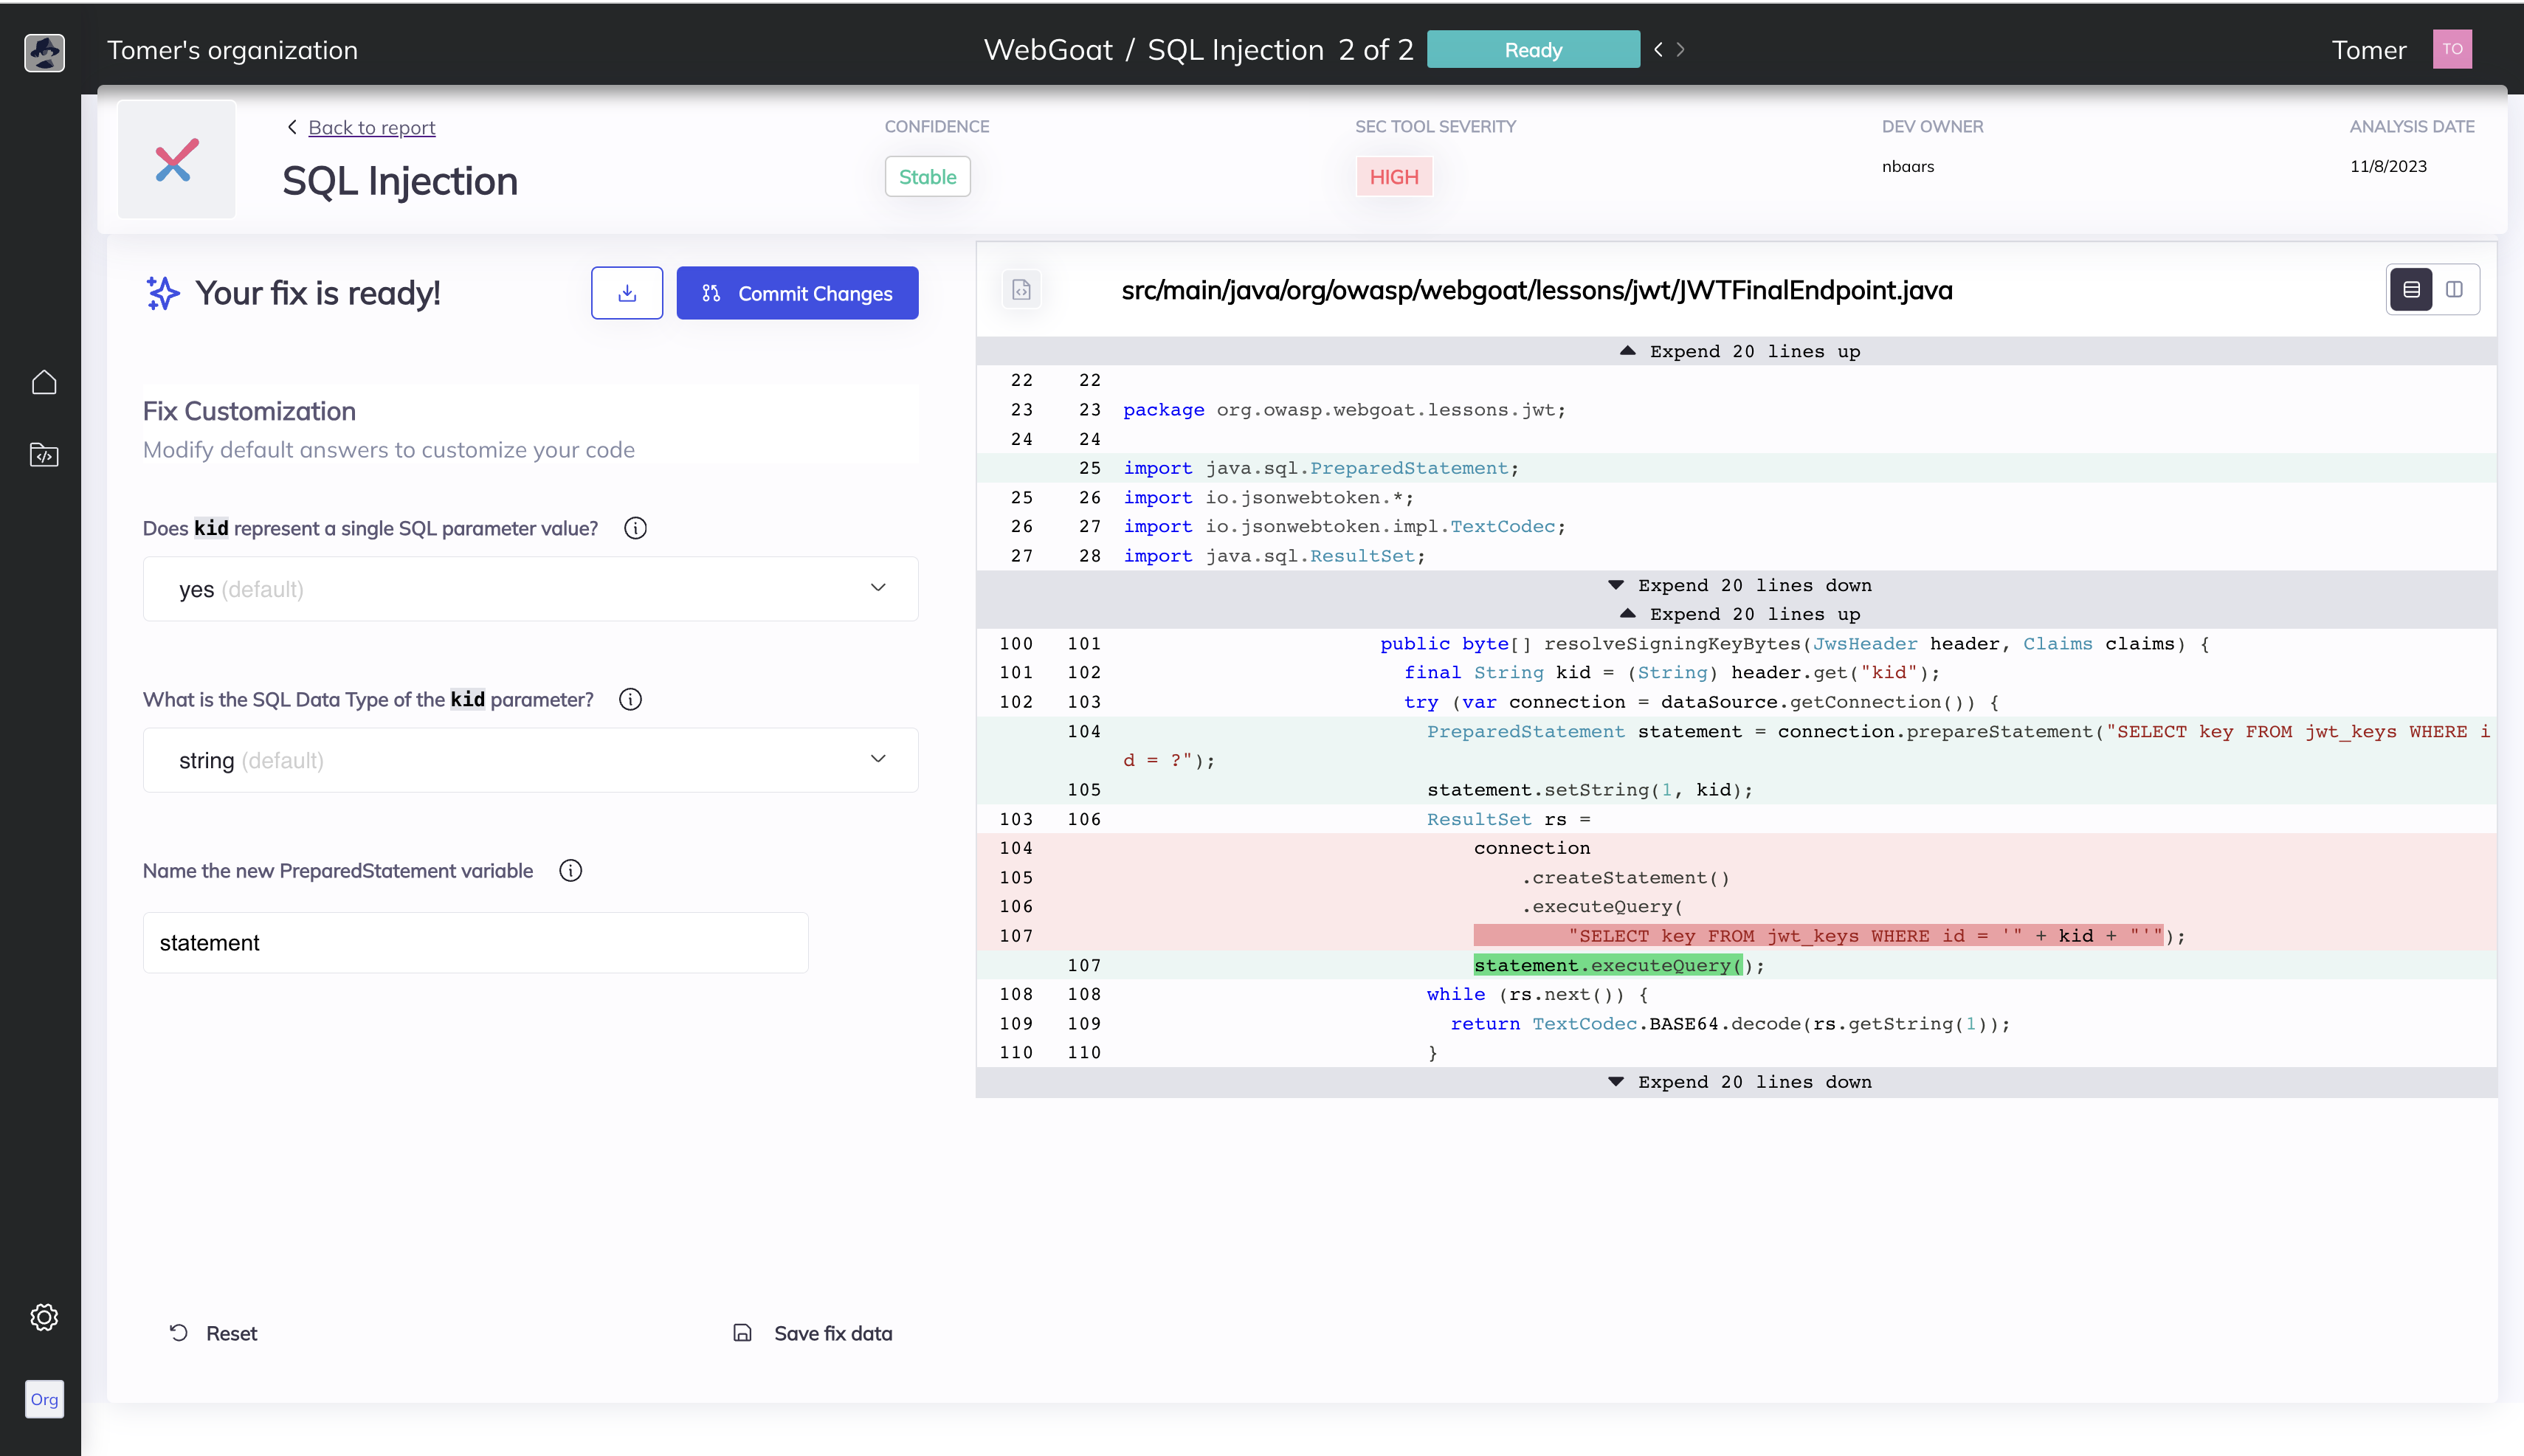
bugsy
 mobb-dev/bugsy
Automatic security vulnerability remediation for your code.
ai-securitycode-analysisdevsecops+2
mobb-dev/bugsyAutomatic security vulnerability remediation for your code.
 wavestone-cdt/defcon-cicd-pipelines-workshop
Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…
 warhorse/warhorse
Infrastructure Automation
 letsencrypt/test-certs-site
A simple server to host the valid, revoked, and expired certificates required by Section 2.2 of the CA/Browser Forum Baseline Requirements.
 dheeraj-jayaswal/cicd-goat-vapt-writeup
Full VAPT writeup of OWASP CICD-Goat — 9 CTFd flags captured, 4 critical + 5 high findings (incl. CVE-2024-23897) mapped to the OWASP Top 10 CI/CD…
 stackrox/stackrox
The StackRox Kubernetes Security Platform performs a risk analysis of the container environment, delivers visibility and runtime alerts, and provides…
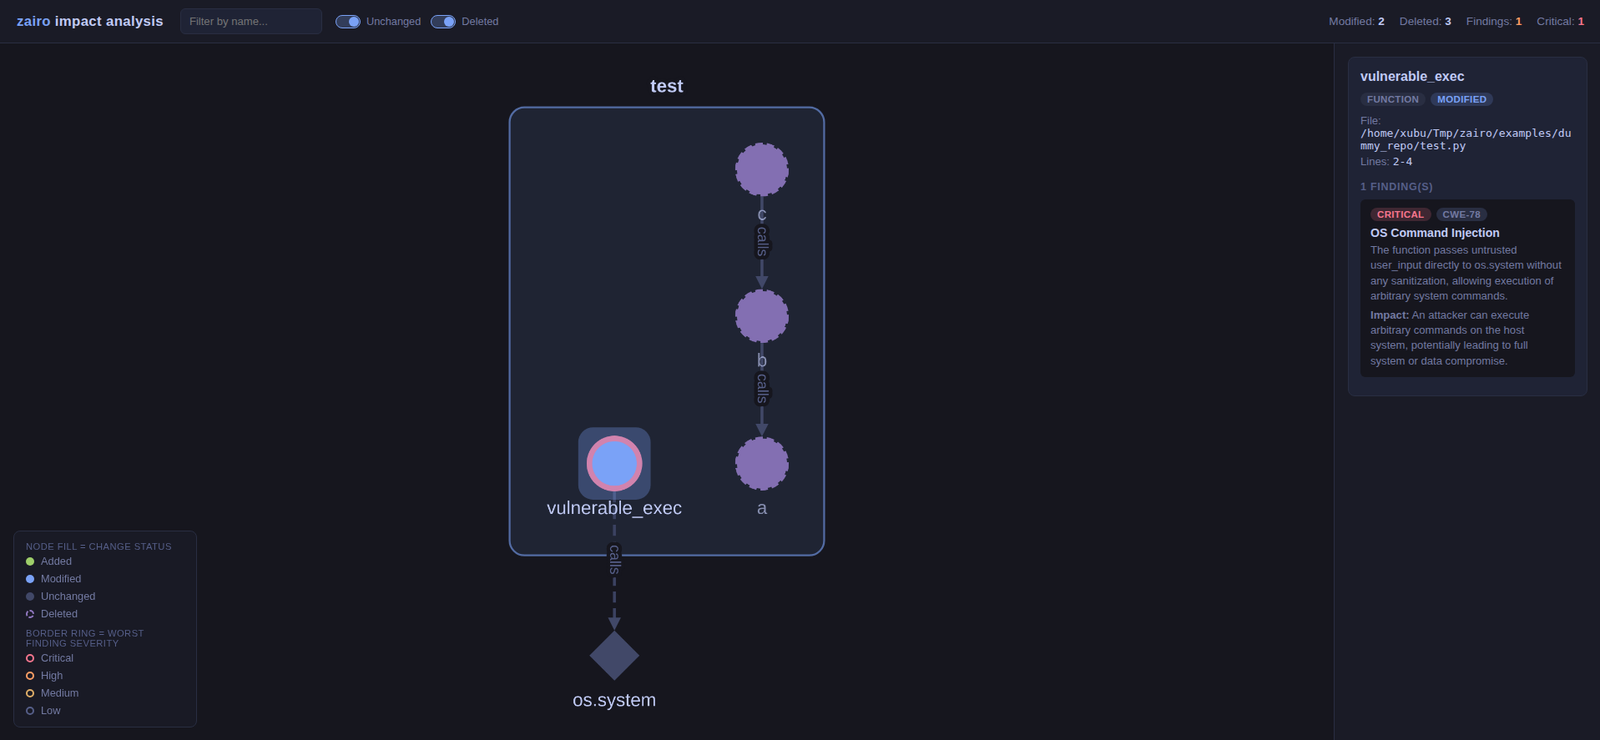 iamavu/zairo
Scans code diffs with context to build an impact graph and uses LLMs to find vulnerabilities, supporting multi-repo scans and CI gating with SARIF…
 bogdanticu88/ratrace
A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.
 moisestapia/http-react2shell
Detection of the React Server Actions Exploit vector – CVE-2025-55182 / CVE-2025-66478
 nestybox/sysbox
An open-source, next-generation "runc" that empowers rootless containers to run workloads such as Systemd, Docker, Kubernetes, just like VMs.
 microsoft/whatthehack
A collection of challenge based hack-a-thons including student guide, coach guide, lecture presentations, sample/instructional code and templates. …
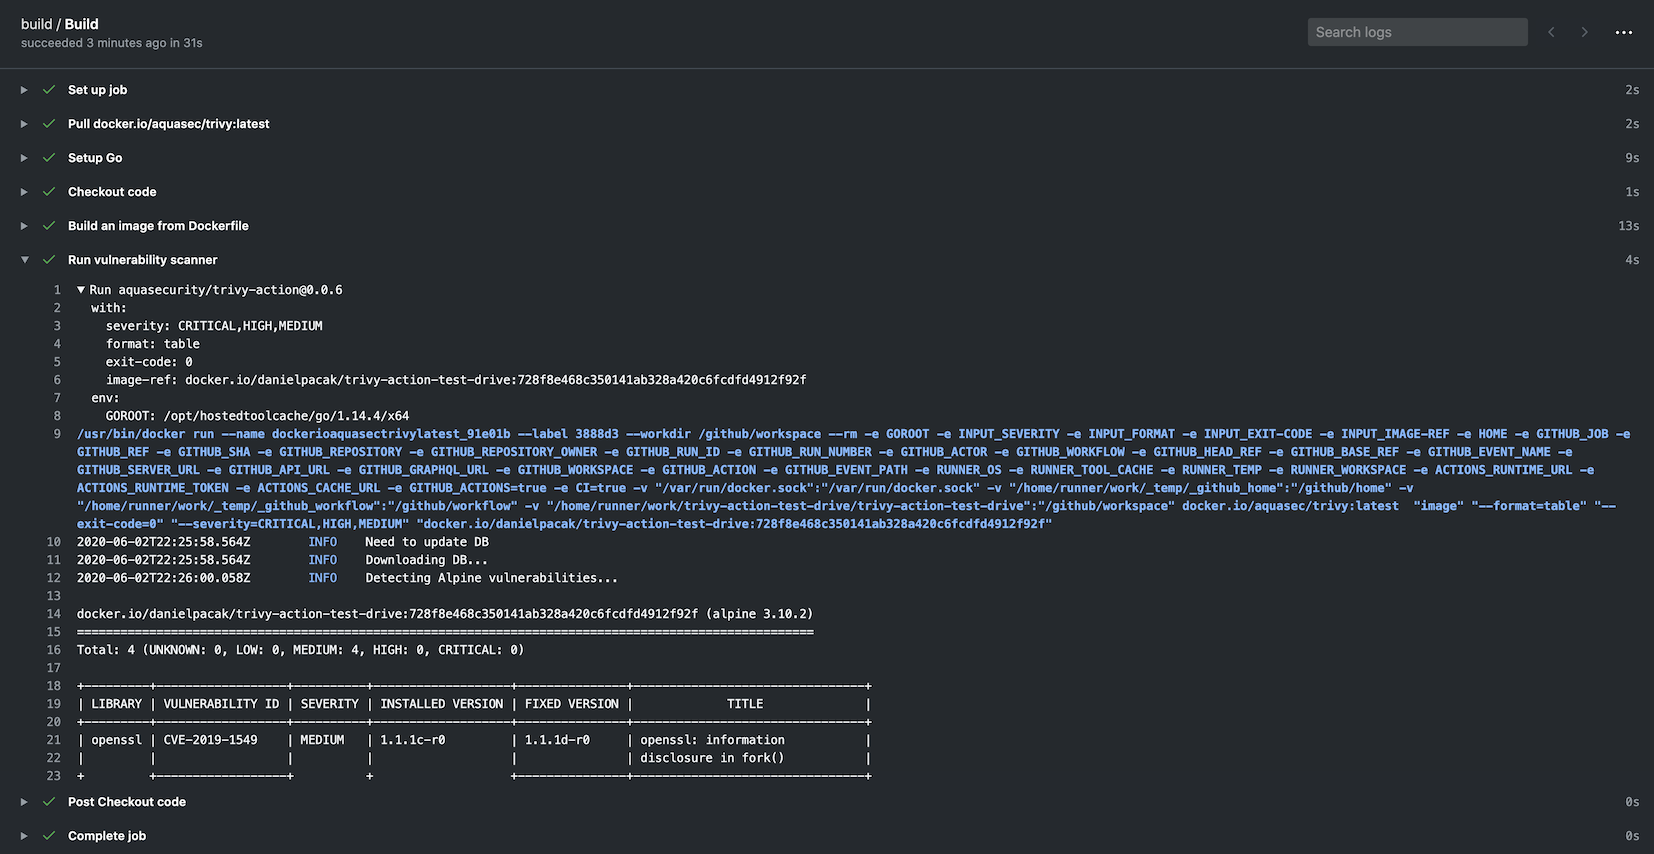 aquasecurity/trivy-action
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities
 dowjones/hammer
Dow Jones Hammer : Protect the cloud with the power of the cloud(AWS)
 backbay-labs/clawdstrike
Policy engine and EDR for AI agent fleets and developer workstations. Monitors tool calls, file access, network flows, and process execution with…
 heroku/heroku-cve-2013-0269
Inspect all of your Heroku apps for vulnerable versions of the JSON gem
 fabriziosalmi/tanstack-compromise-checker
Shell script to detect TanStack npm supply chain attack indicators (CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx)
 plutosecurity/mcpwnfluence
Information about CVE-2026-27825 & CVE-2026-27826 discovered by Pluto Security and a bash script for identifying vulnerable mcp-atlassian instances…
 mebibite/log4jhound
Created after the disclosure of CVE-2021-44228. Bash script that detects Log4j occurrences in your projects and systems, allowing you to get insight…