
osv-scanner
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
code-analysiscontainer-securitydevsecops+4
11.0k
google/osv-scannerVulnerability scanner written in Go which uses the data provided by https://osv.dev
 mayank729/cve-2025-55182-scanner
🔍 Scan for CVE-2025-55182 risks in React Server Components with this non-intrusive tool that helps detect critical vulnerabilities in your…
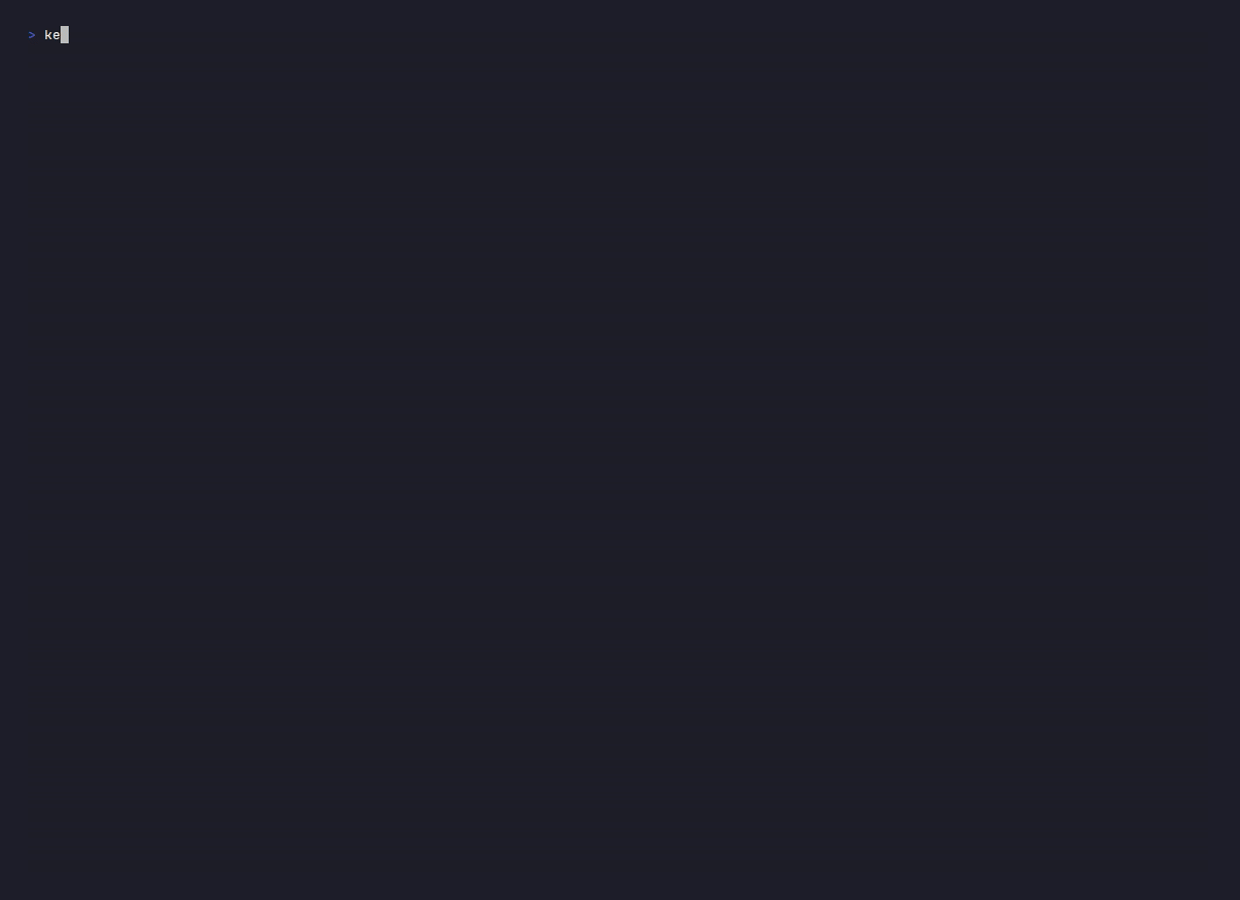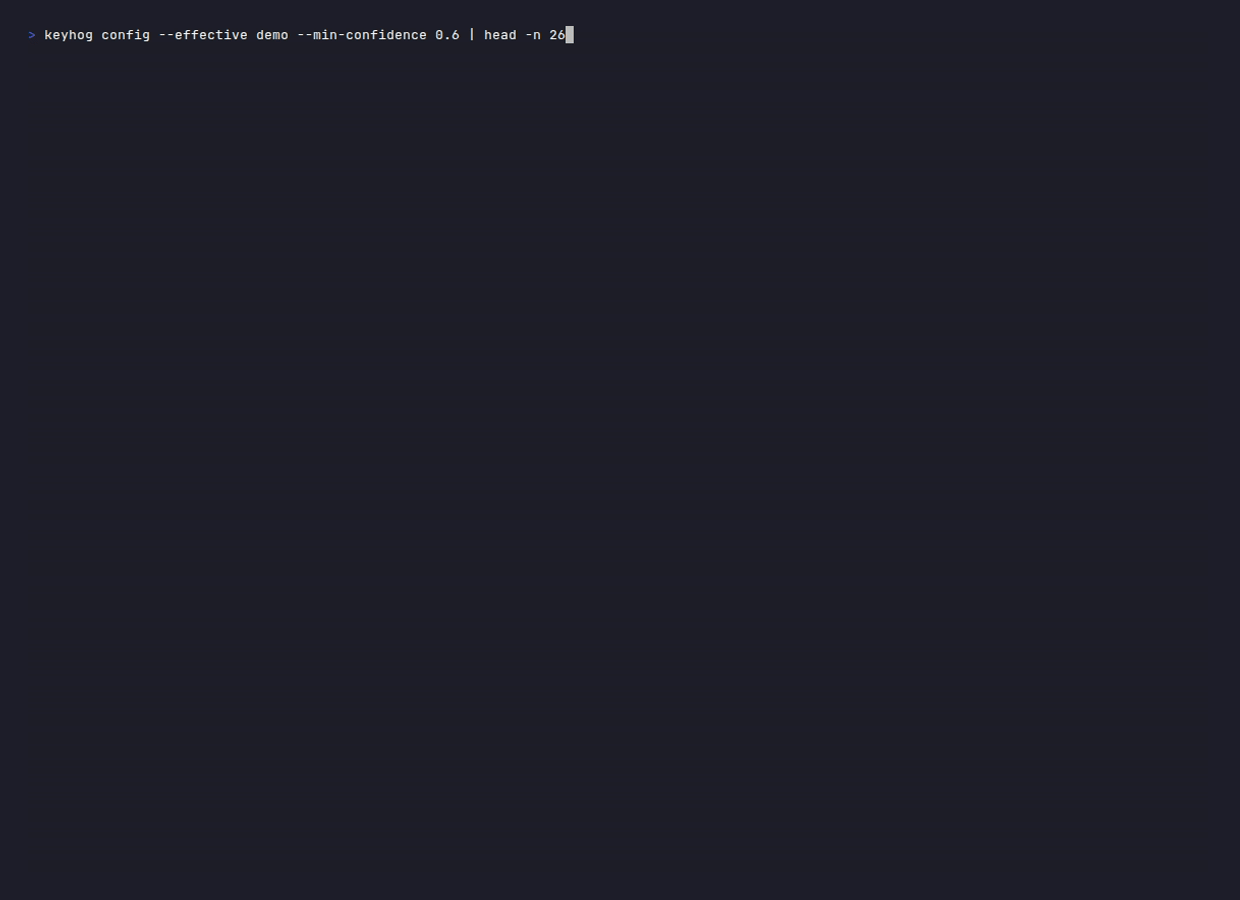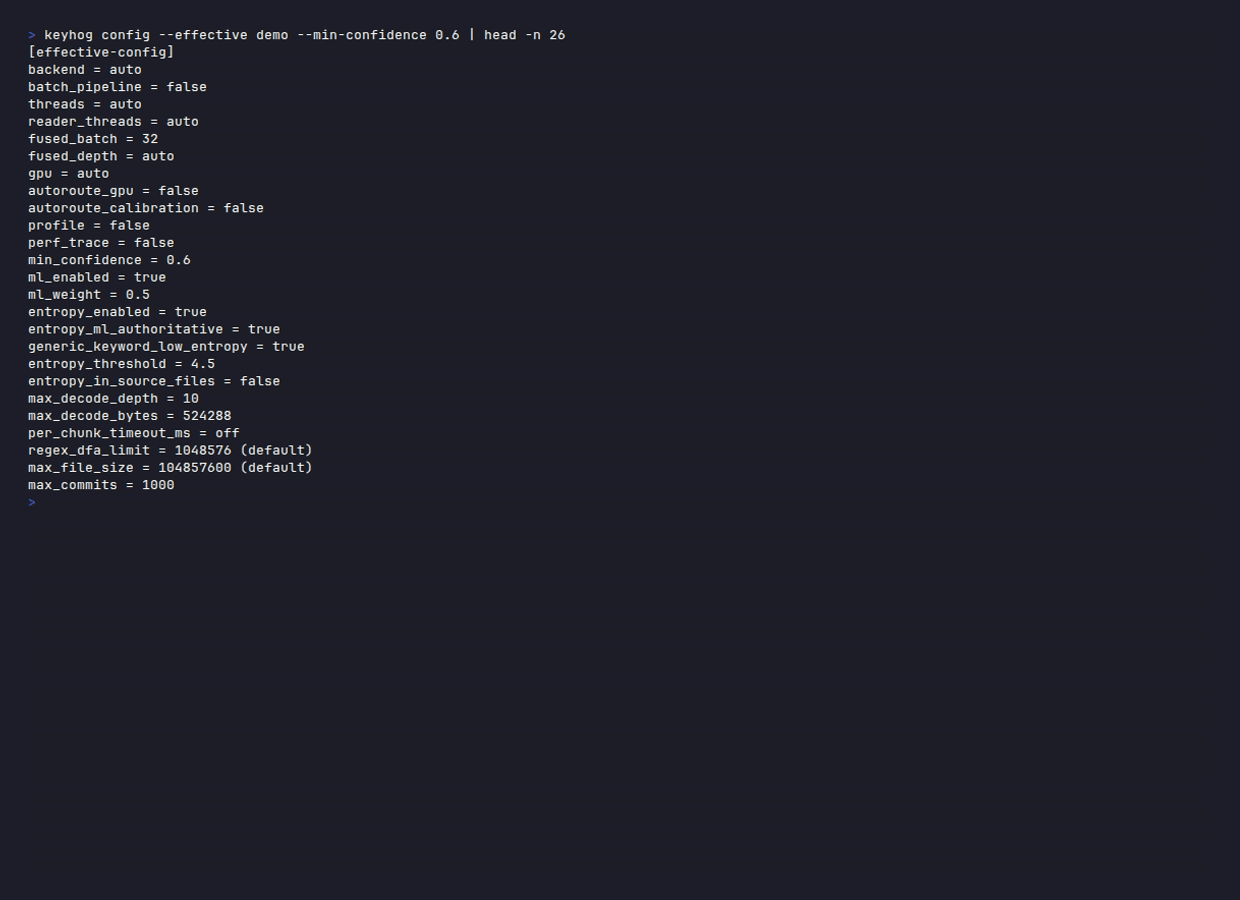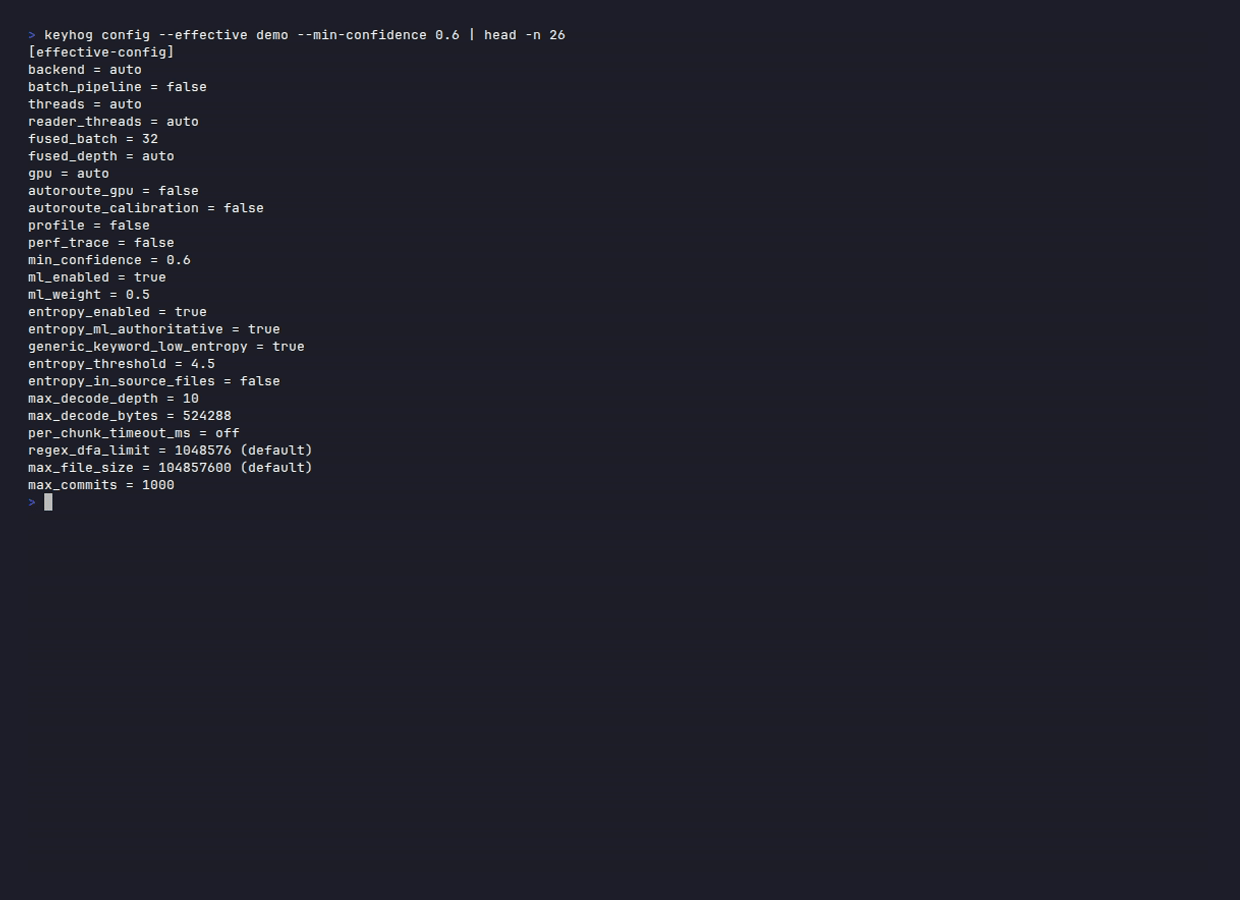 santhreal/keyhog
Open-source secret scanner in Rust
 offseq/threat-finder
Runtime vulnerability scanner: finds CVEs in the services actually running on a host and ranks them by network exposure.
 contrastsecurity/contrast
SAST CLI for scanning Java, JavaScript, and .NET applications plus AWS Lambda functions, detecting code vulnerabilities and over-permissive IAM…
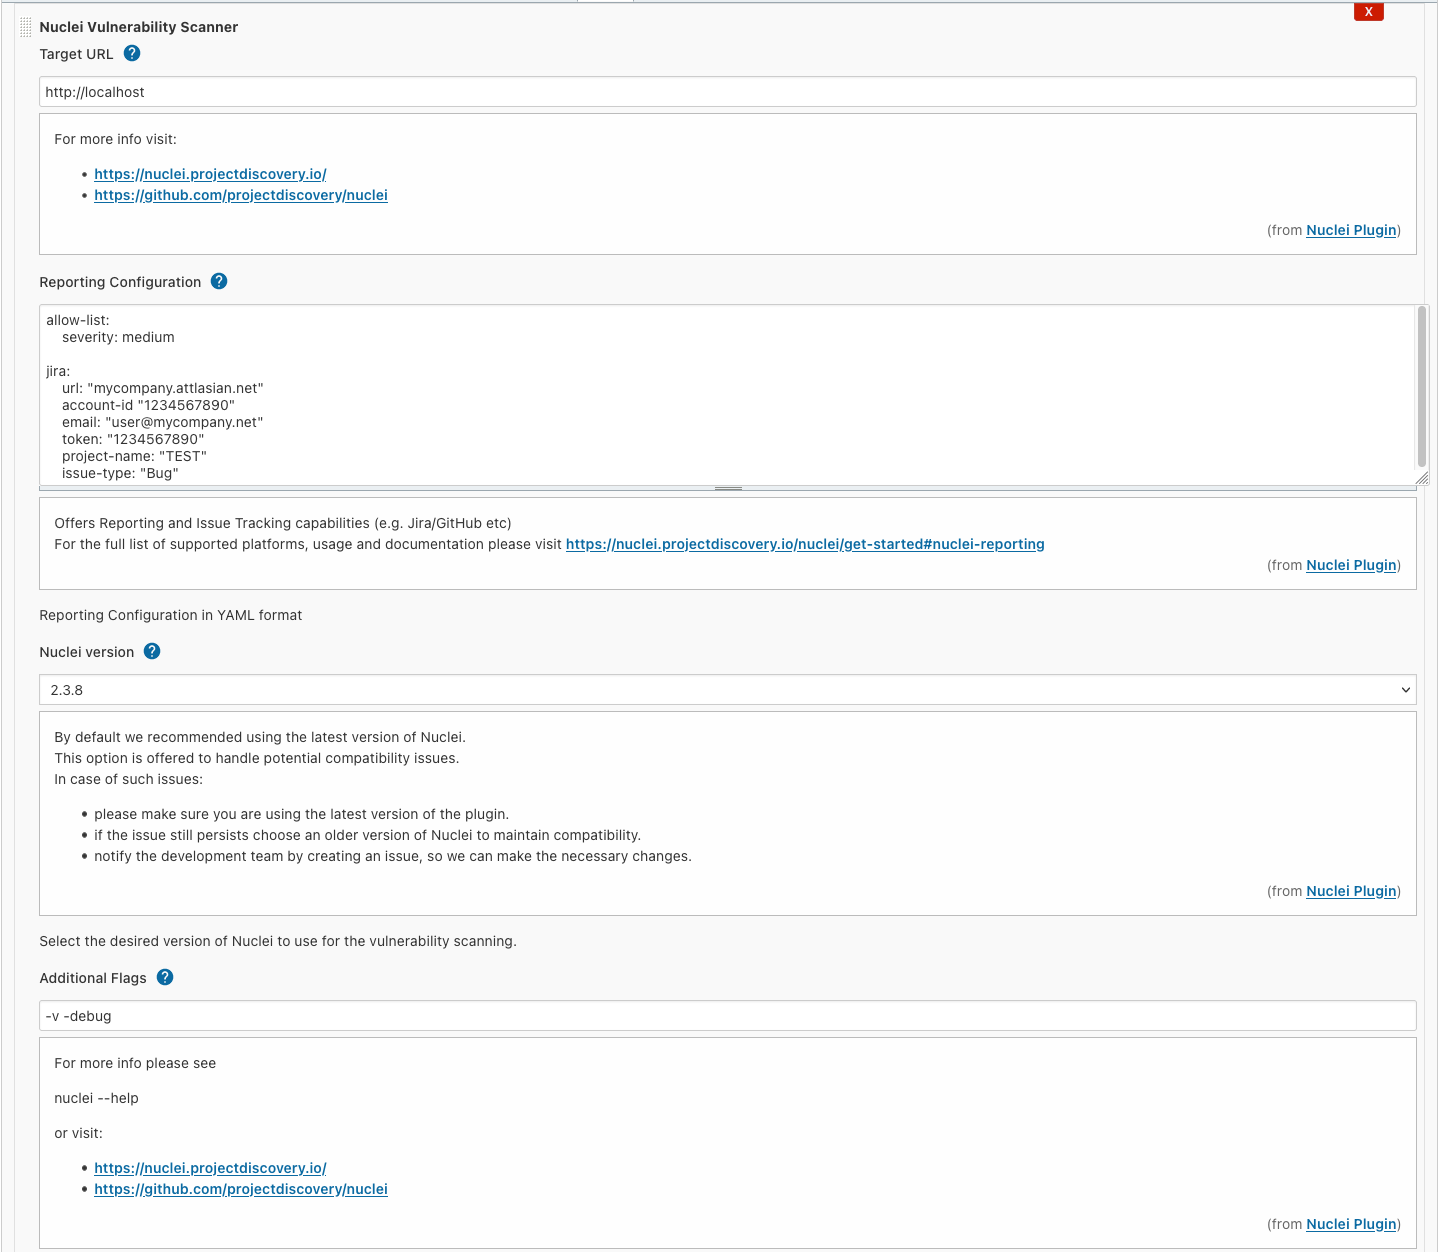 jenkinsci/nuclei-plugin
Nuclei is a fast tool for configurable targeted vulnerability scanning based on templates offering massive extensibility and ease of use.
 cspf-founder/api-scanner-docker
Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …
 jricramc/aigate
AI Prompt Secret Scanner: local proxy and Claude Code hook that blocks secrets before they reach AI APIs
 coinbase/salus
We would like to request that all contributors please clone a *fresh copy* of this repository since the September 21st maintenance.
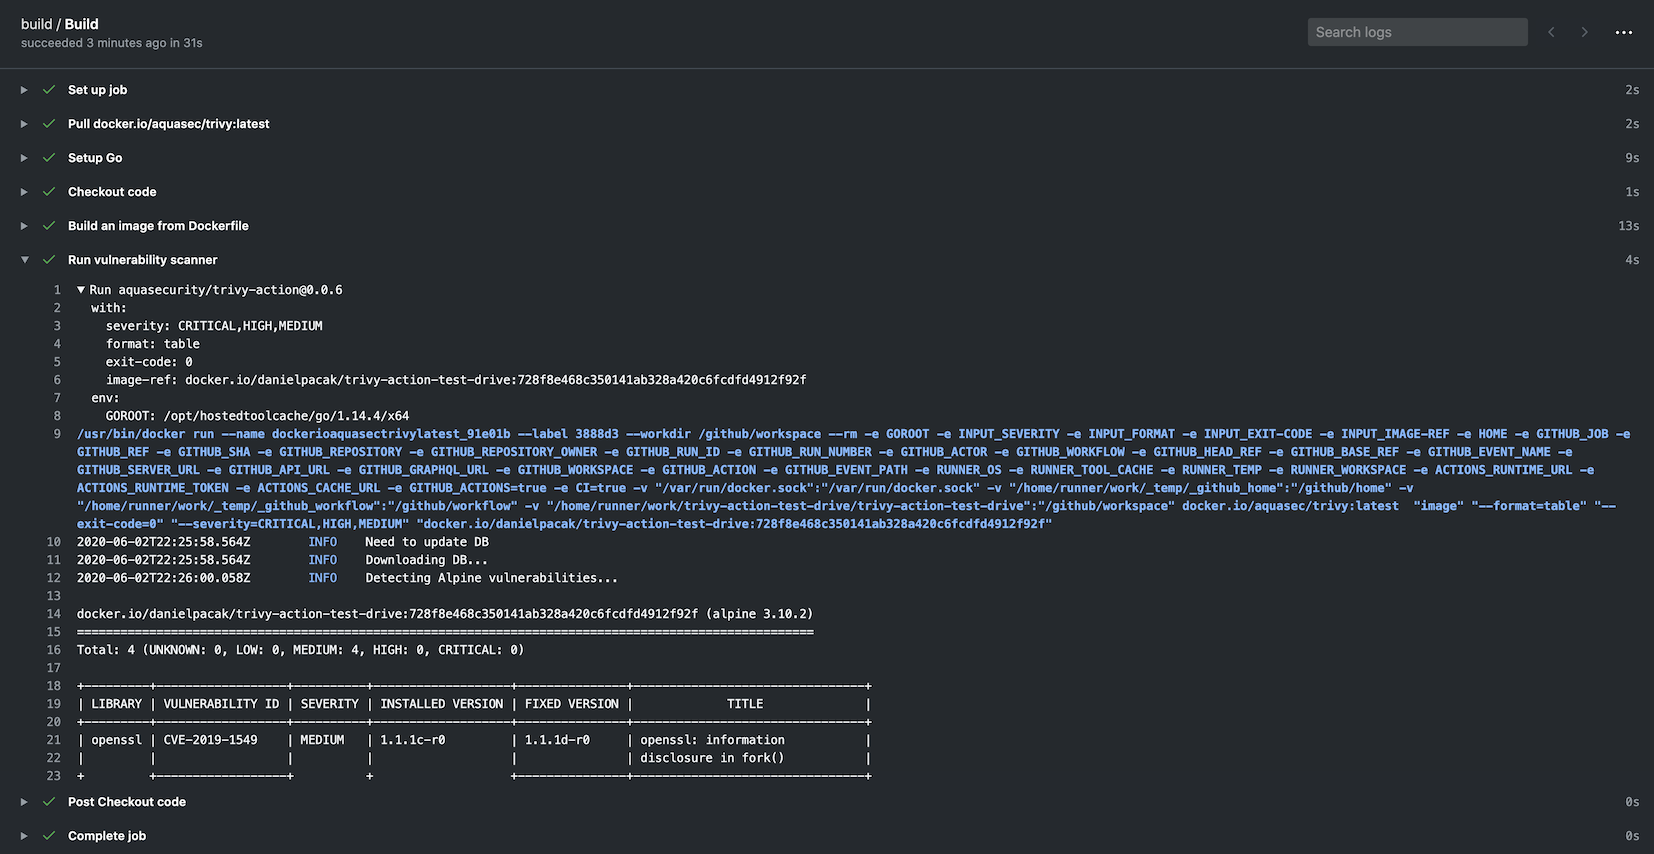 aquasecurity/trivy-action
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities
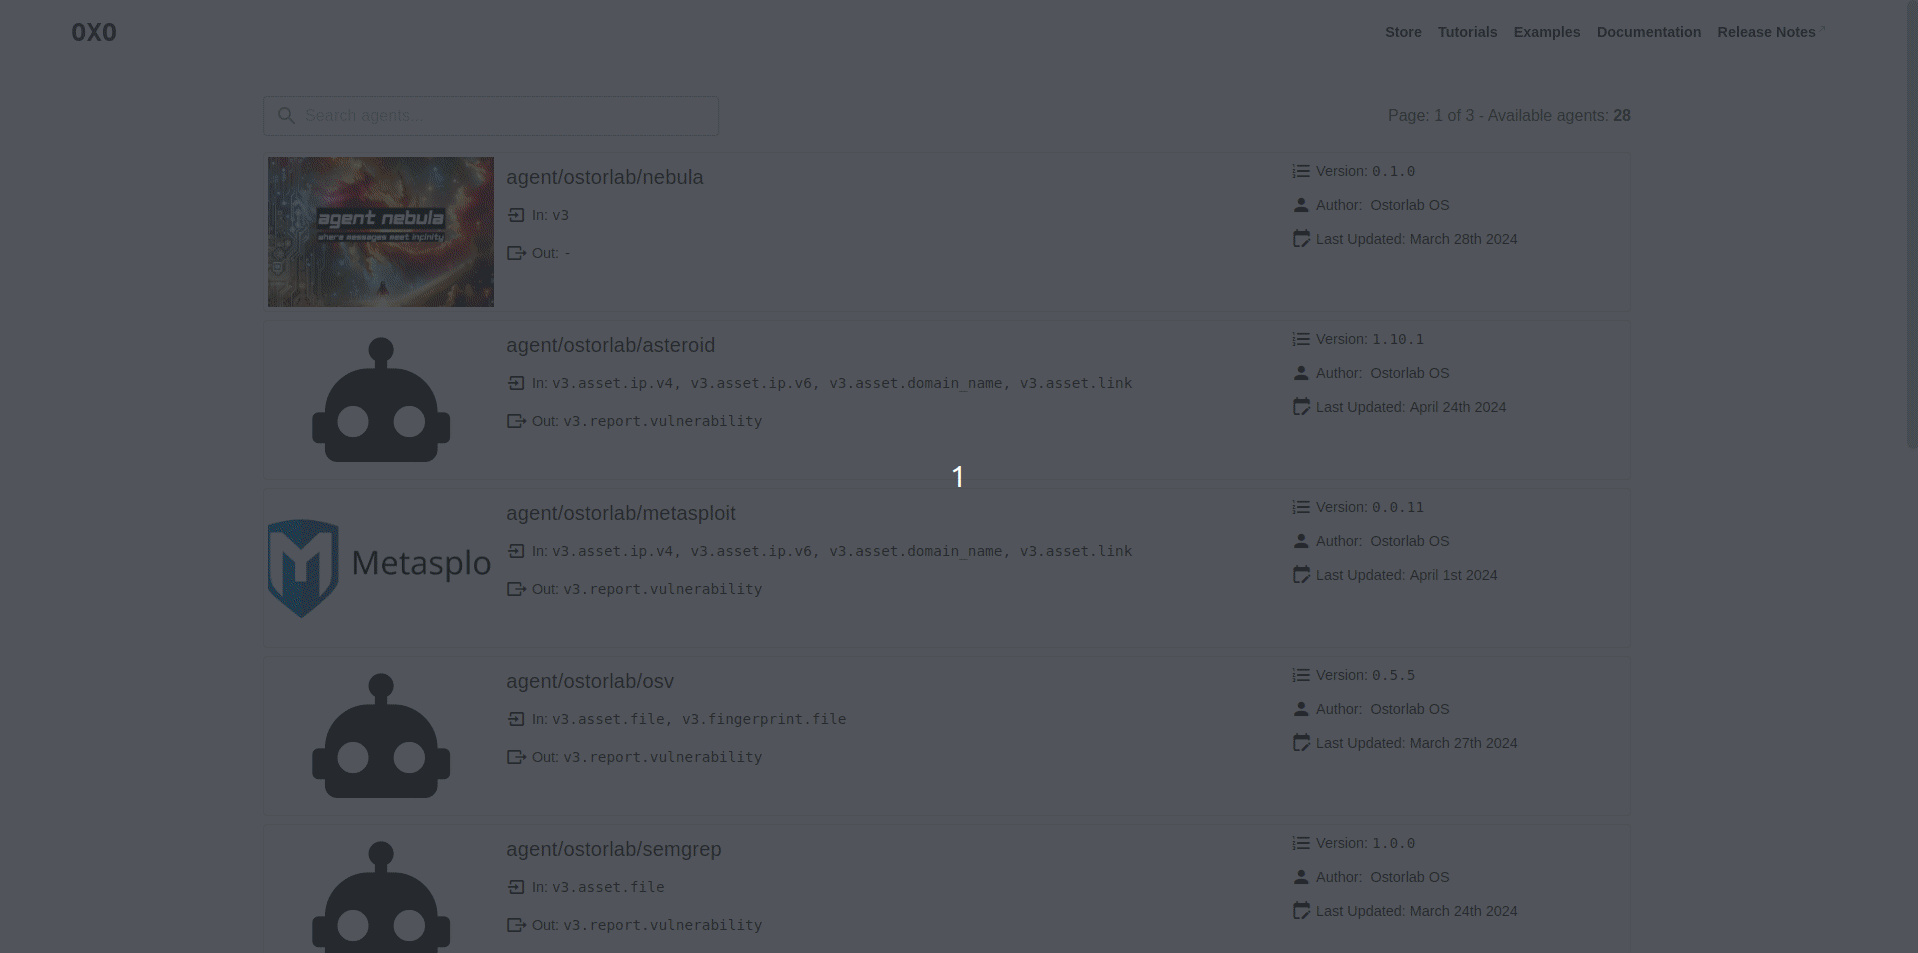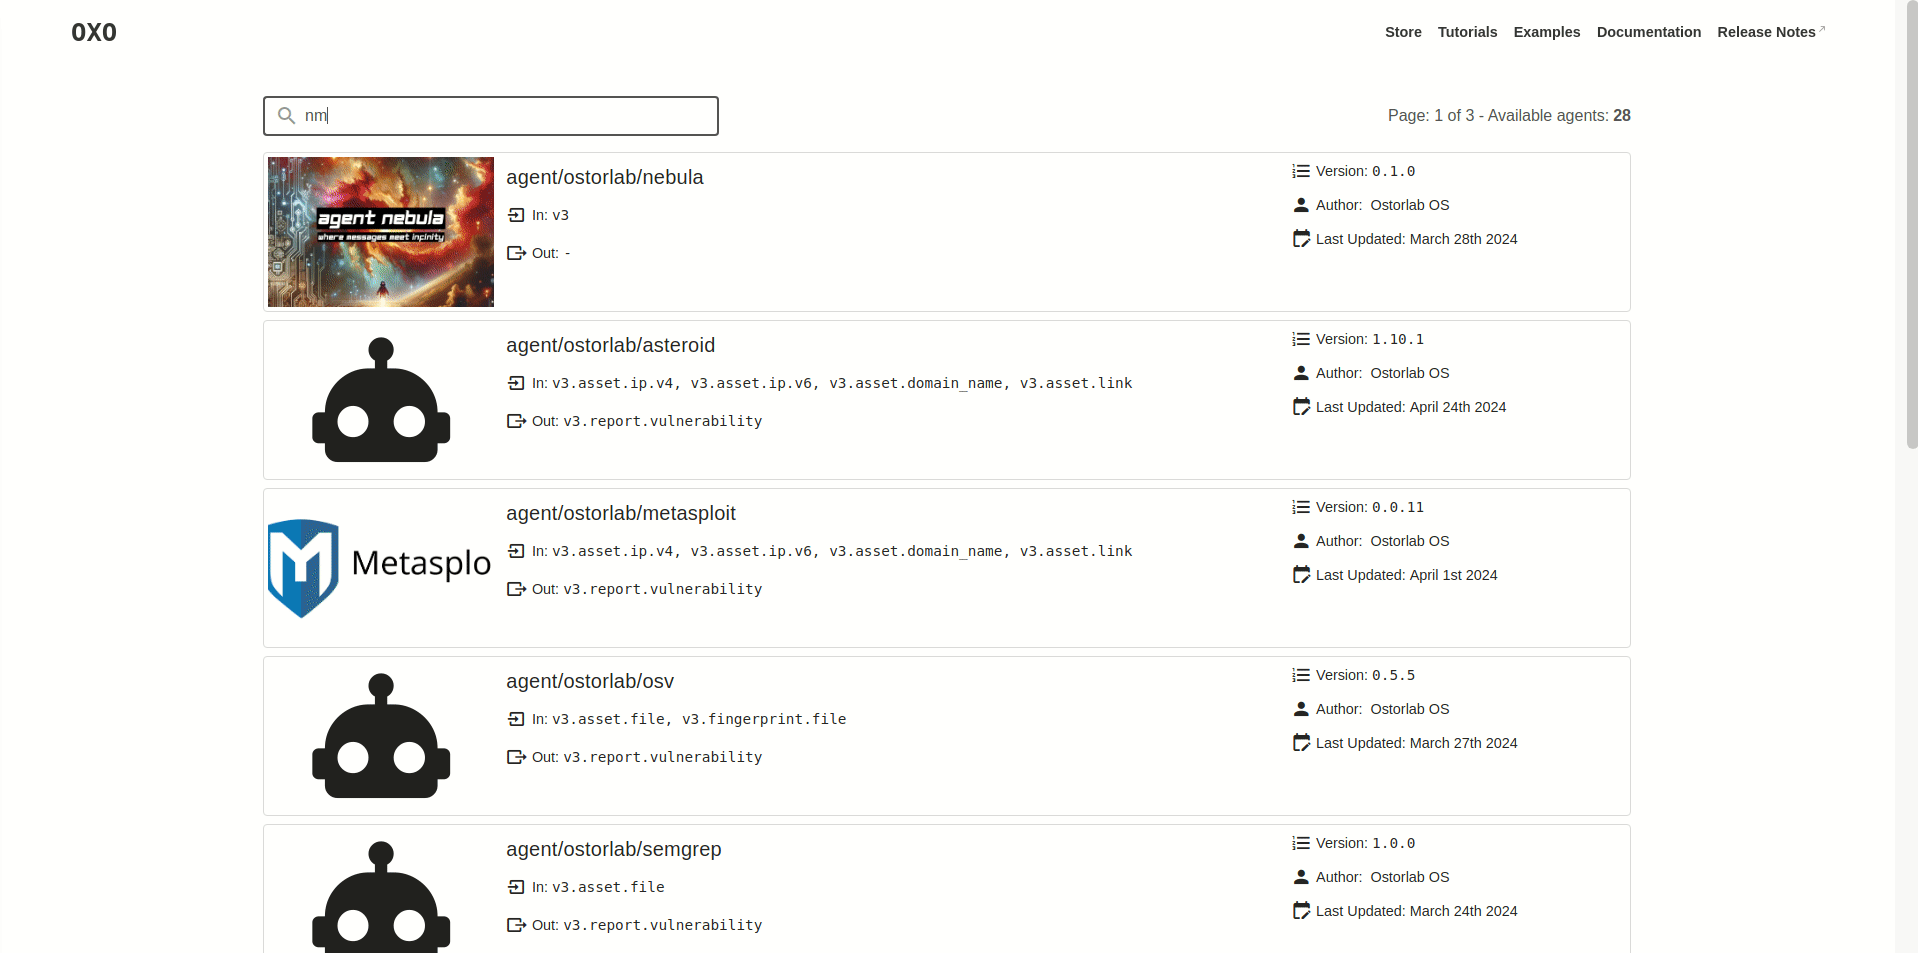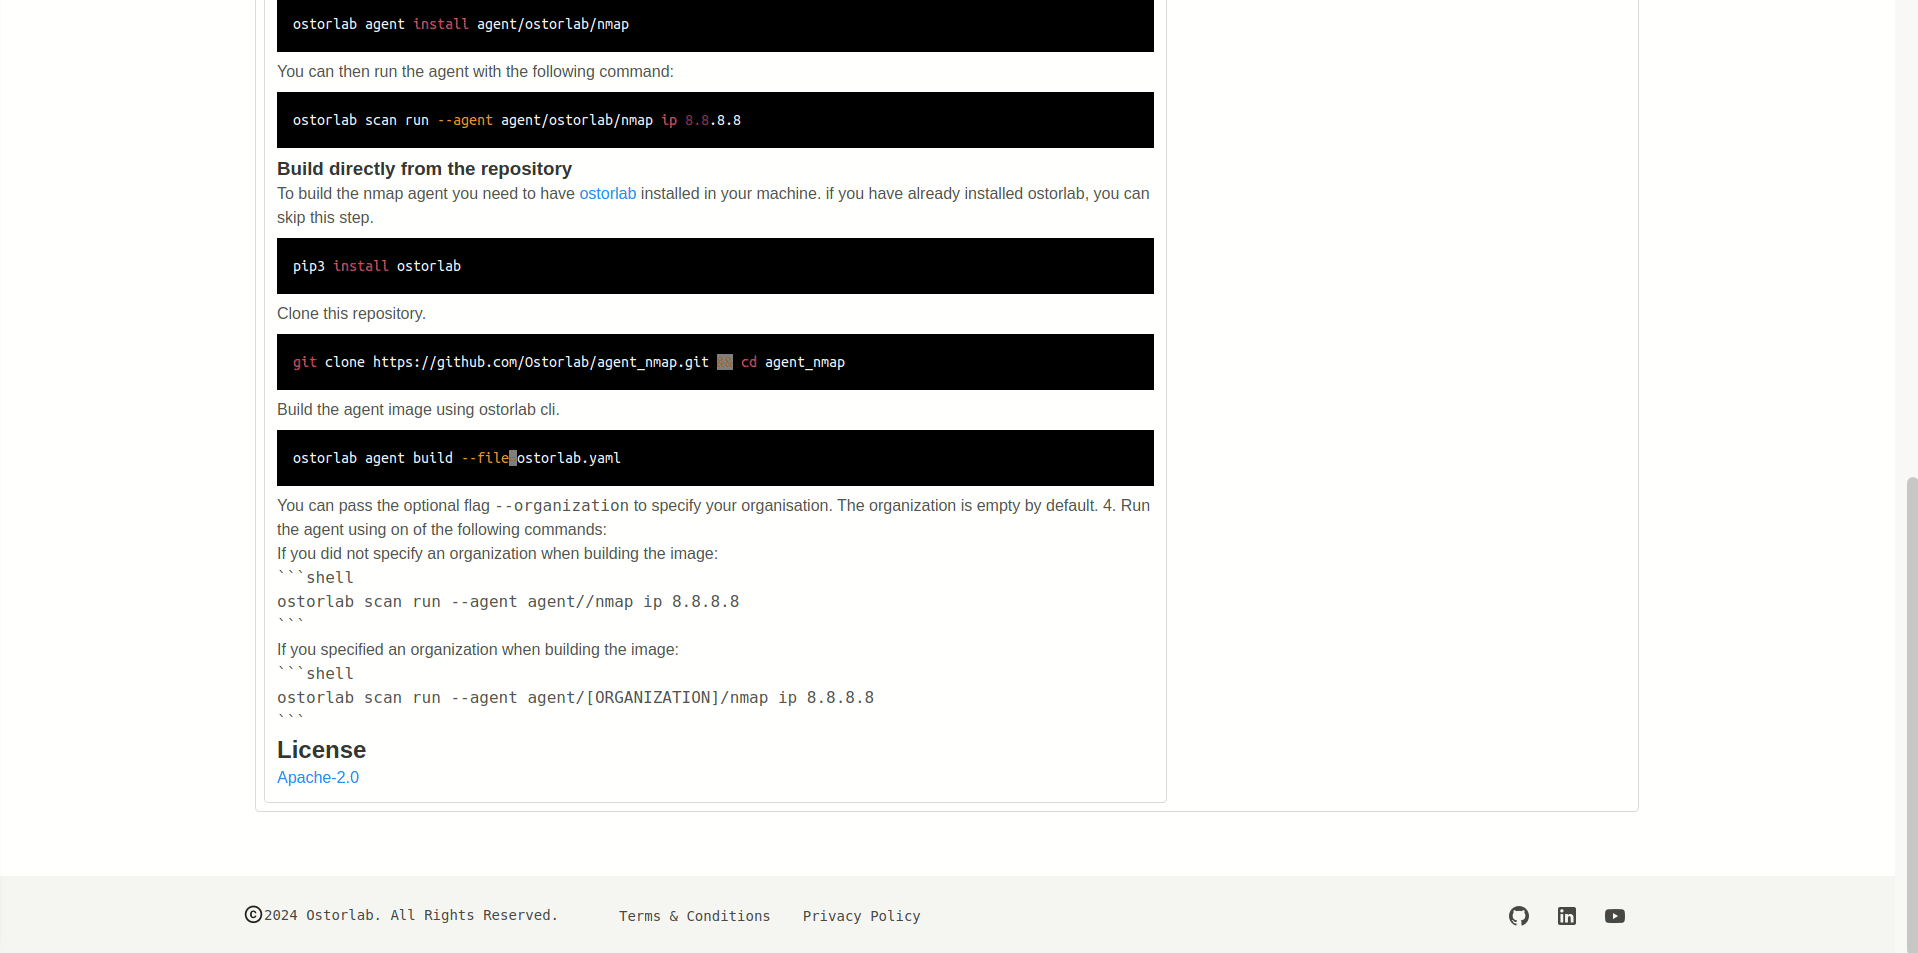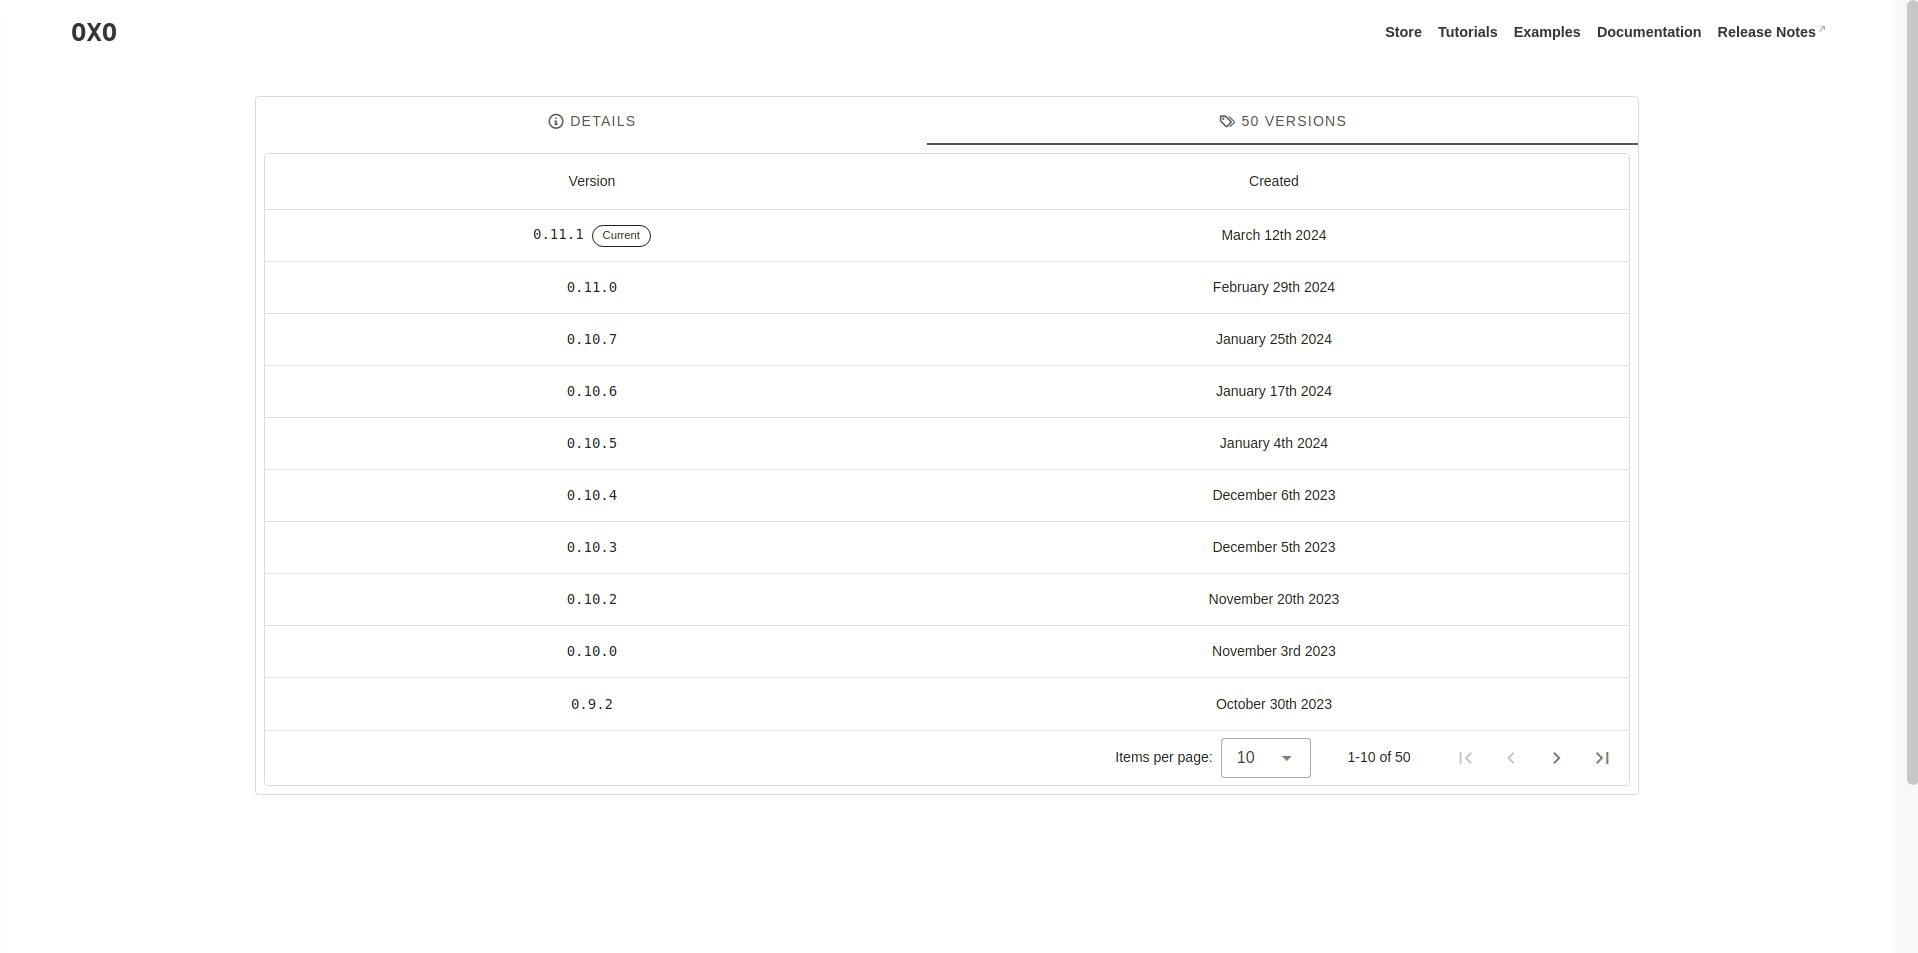 ostorlab/oxo
Modular security scanning orchestrator that combines specialized agents for vulnerability detection, reconnaissance, and fingerprinting across…
 hahwul/smugglex
Rust-powered HTTP Request Smuggling Scanner.
 xlab-si/iac-scan-runner
Service that scans your Infrastructure as Code for common vulnerabilities
 chen-keinan/mesh-kridik
Automated security checker for Kubernetes clusters with Istio service mesh, enforcing best practices via OPA policies and generating remediation…
 wi3memake/react2shell-scanner
Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…
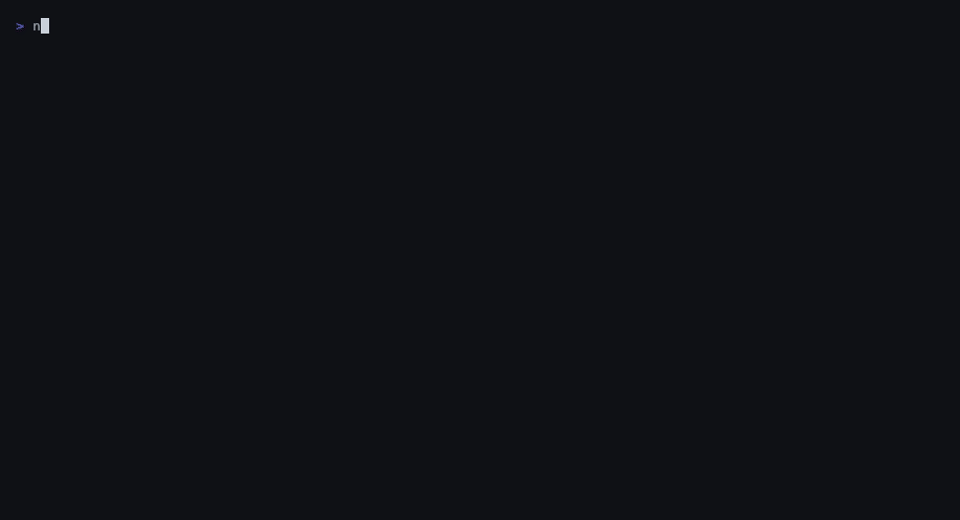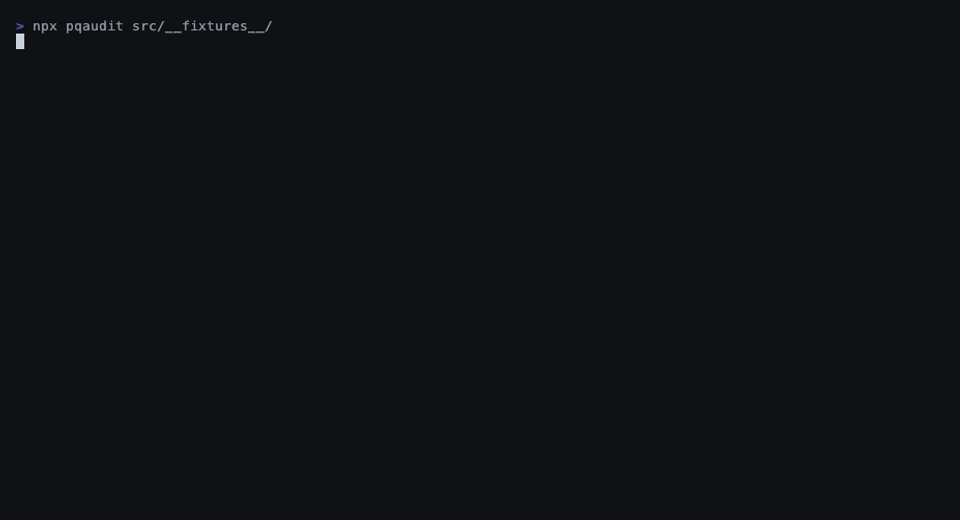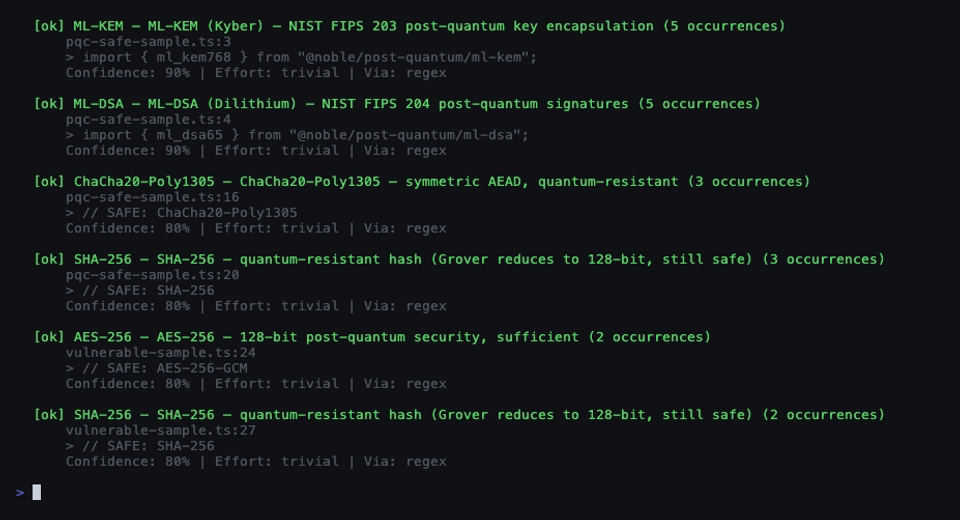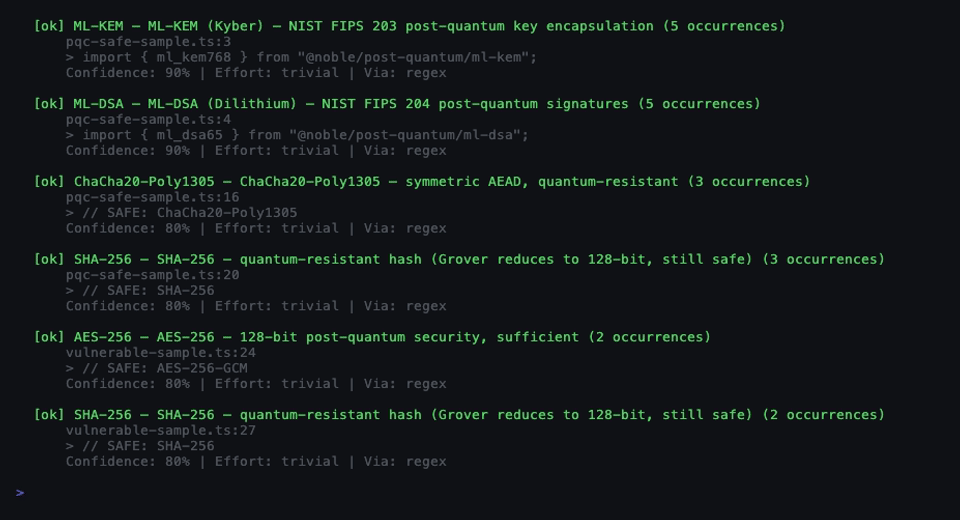 pqcworld/pqaudit
Scan codebases for quantum-vulnerable cryptography. Detect RSA, ECDSA, Ed25519, ECDH before Q-Day. CycloneDX CBOM + SARIF output.
 nxgn-kd01/react2shell-scanner
Detect CVE-2025-55182 (React2Shell) RCE vulnerability in React Server Components. Fast, accurate scanner with zero false positives.
 openclarity/kubeclarity
KubeClarity is a tool for detection and management of Software Bill Of Materials (SBOM) and vulnerabilities of container images and filesystems