
depsguard
 arnica/depsguard
Harden your package manager configs against supply chain attacks.
cloud-securityconfiguration-auditingdevsecops+3
arnica/depsguardHarden your package manager configs against supply chain attacks.
 otsmane-ahmed/ci-supplychain-guard
Static analysis tool that detects malicious dependencies in CI/CD pipelines using pattern matching and AST analysis, with a traffic-light risk…
 xiaoqimikko/netty-http2-check
Offline Java tool that scans jars and versions to determine exposure to seven netty-codec-http2 CVEs, recommending the single patched version that…
 az9713/cve-lite-on-pi
Running OWASP cve-lite-cli against the pi monorepo: scan journey and key finding (vitest CVE-2026-47429).

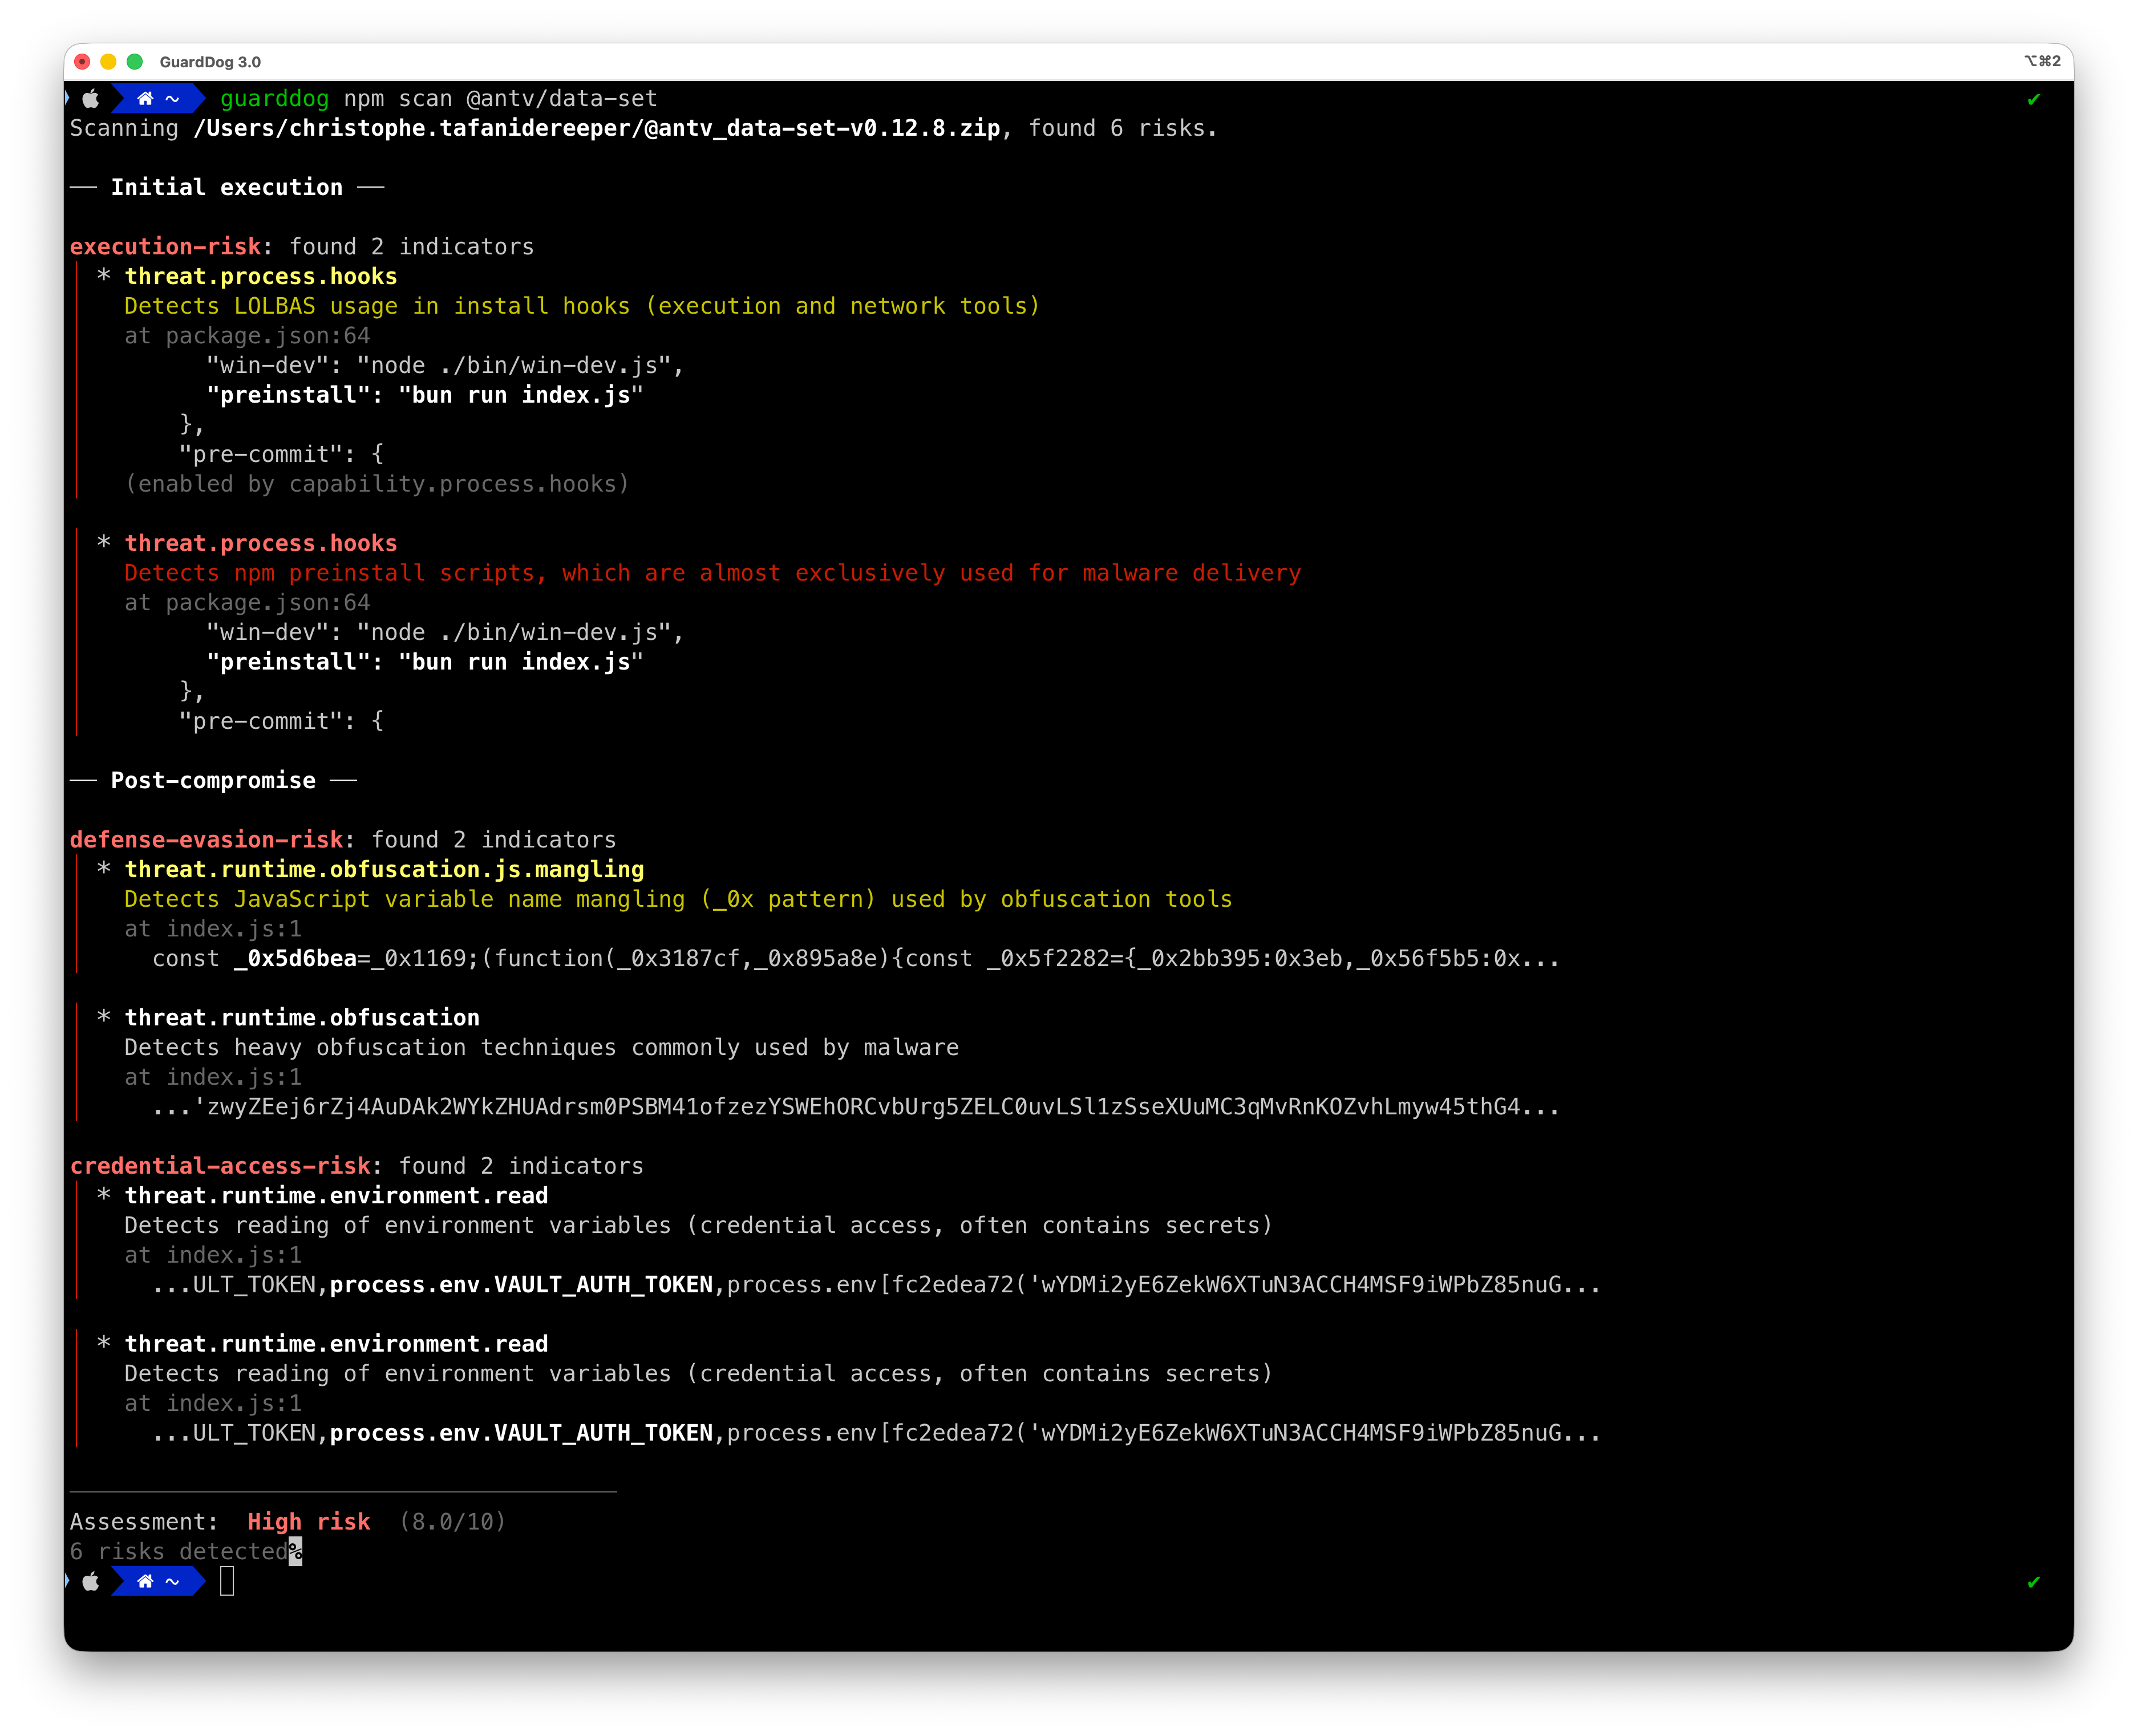 datadog/guarddog
🐍 🔍 GuardDog is a CLI tool to Identify malicious PyPI and npm packages
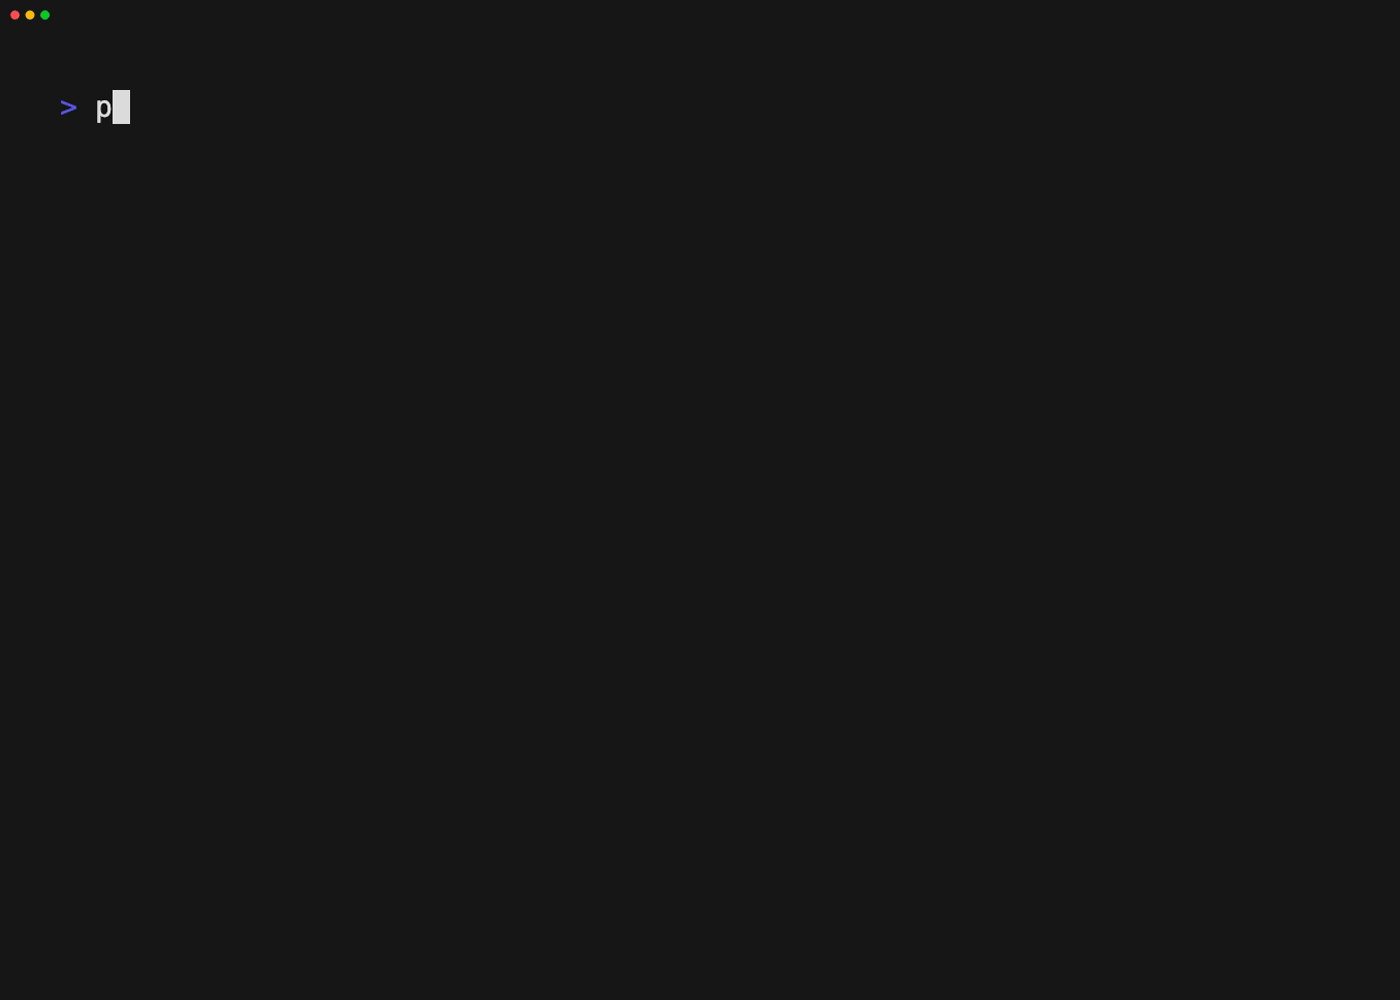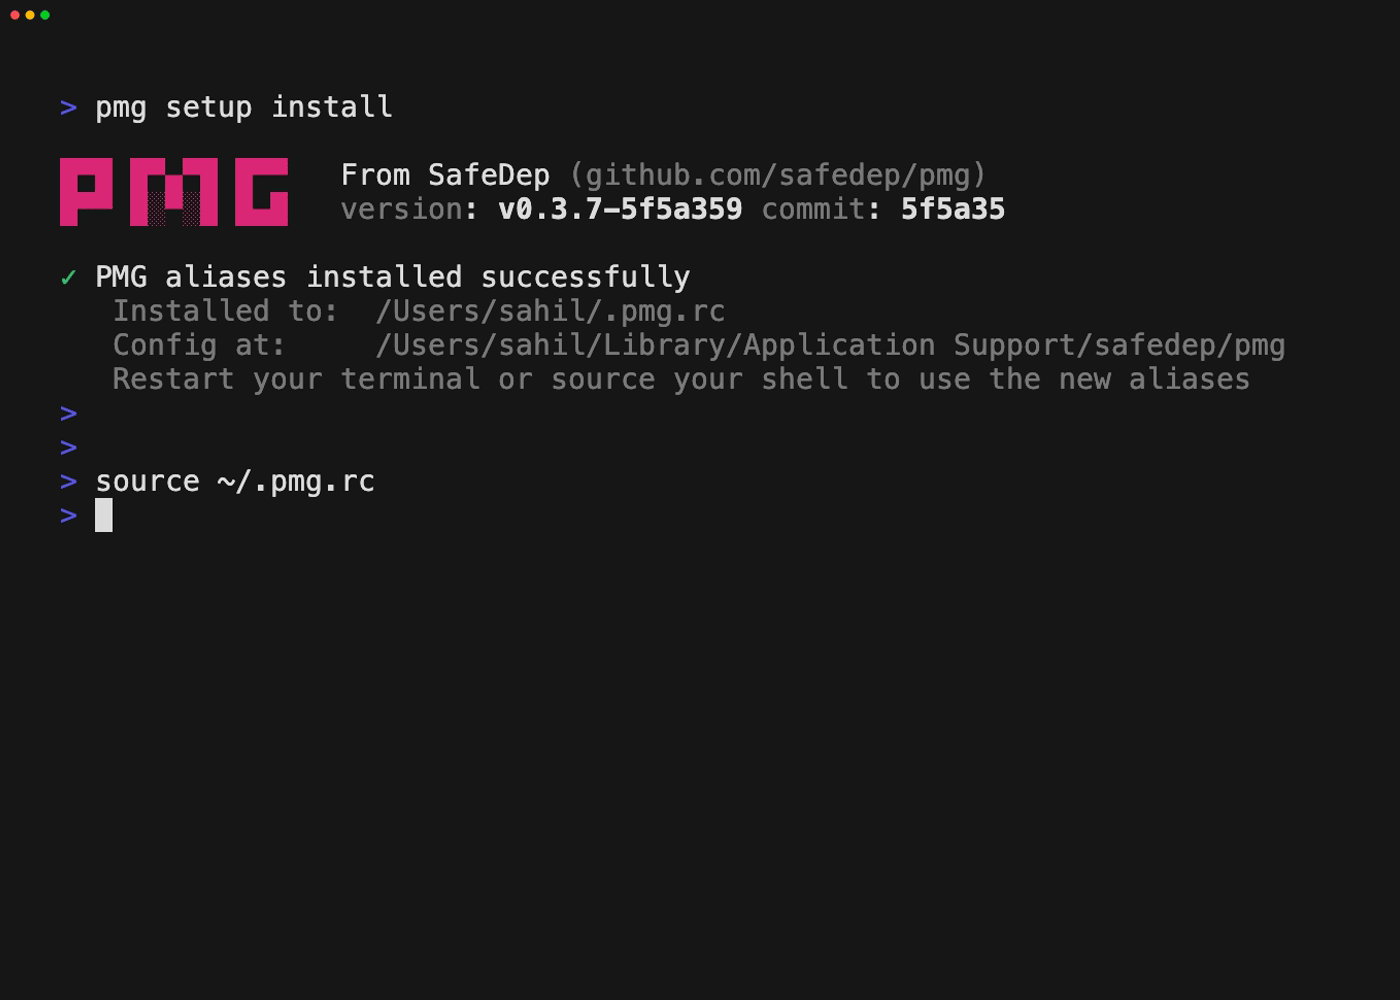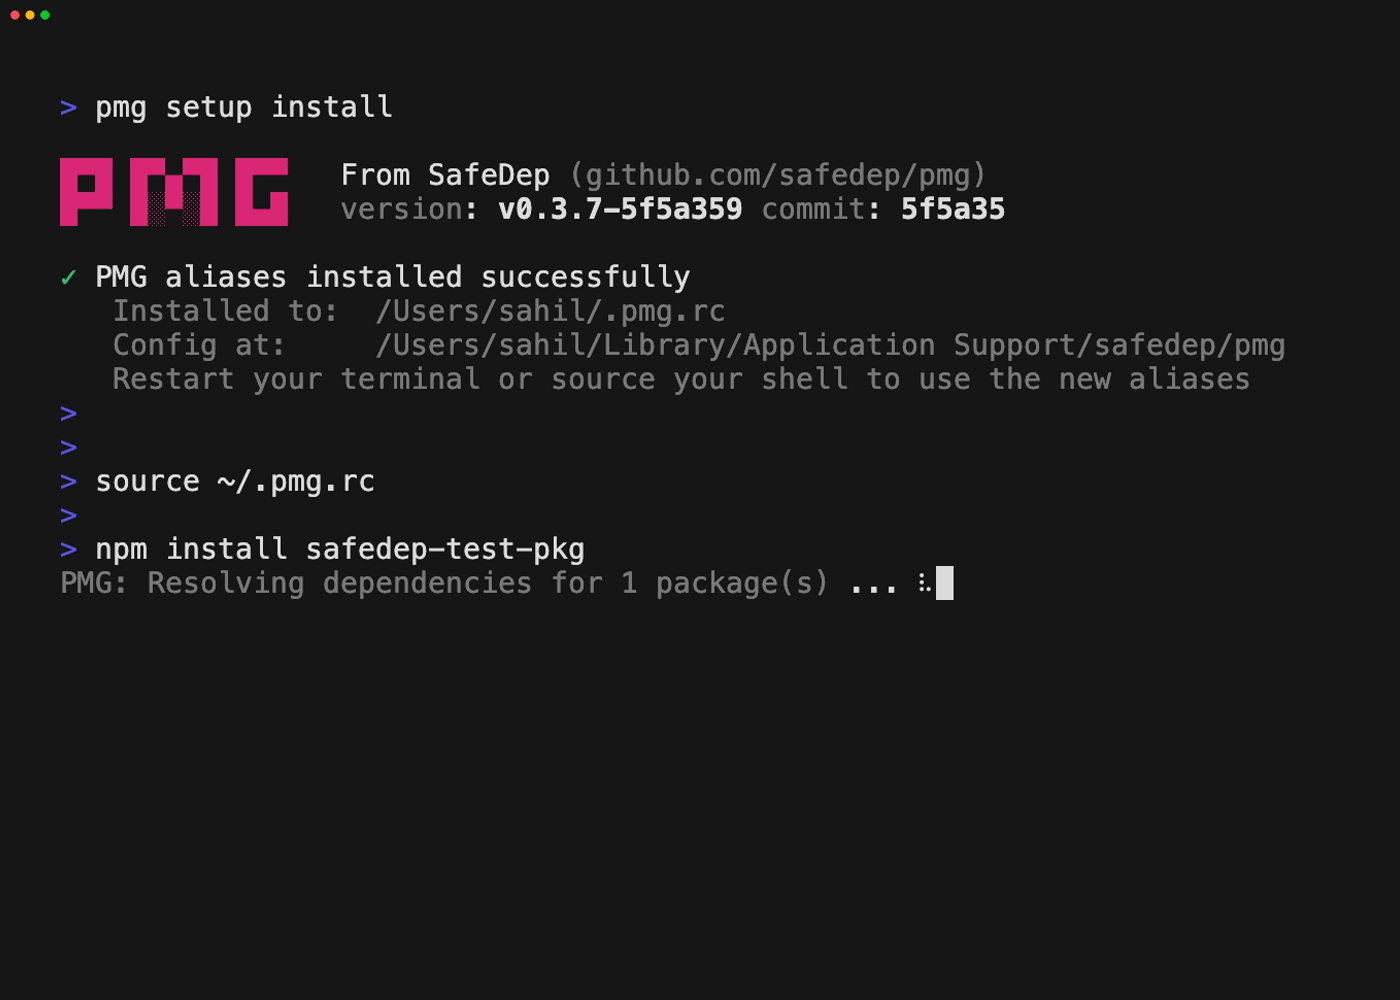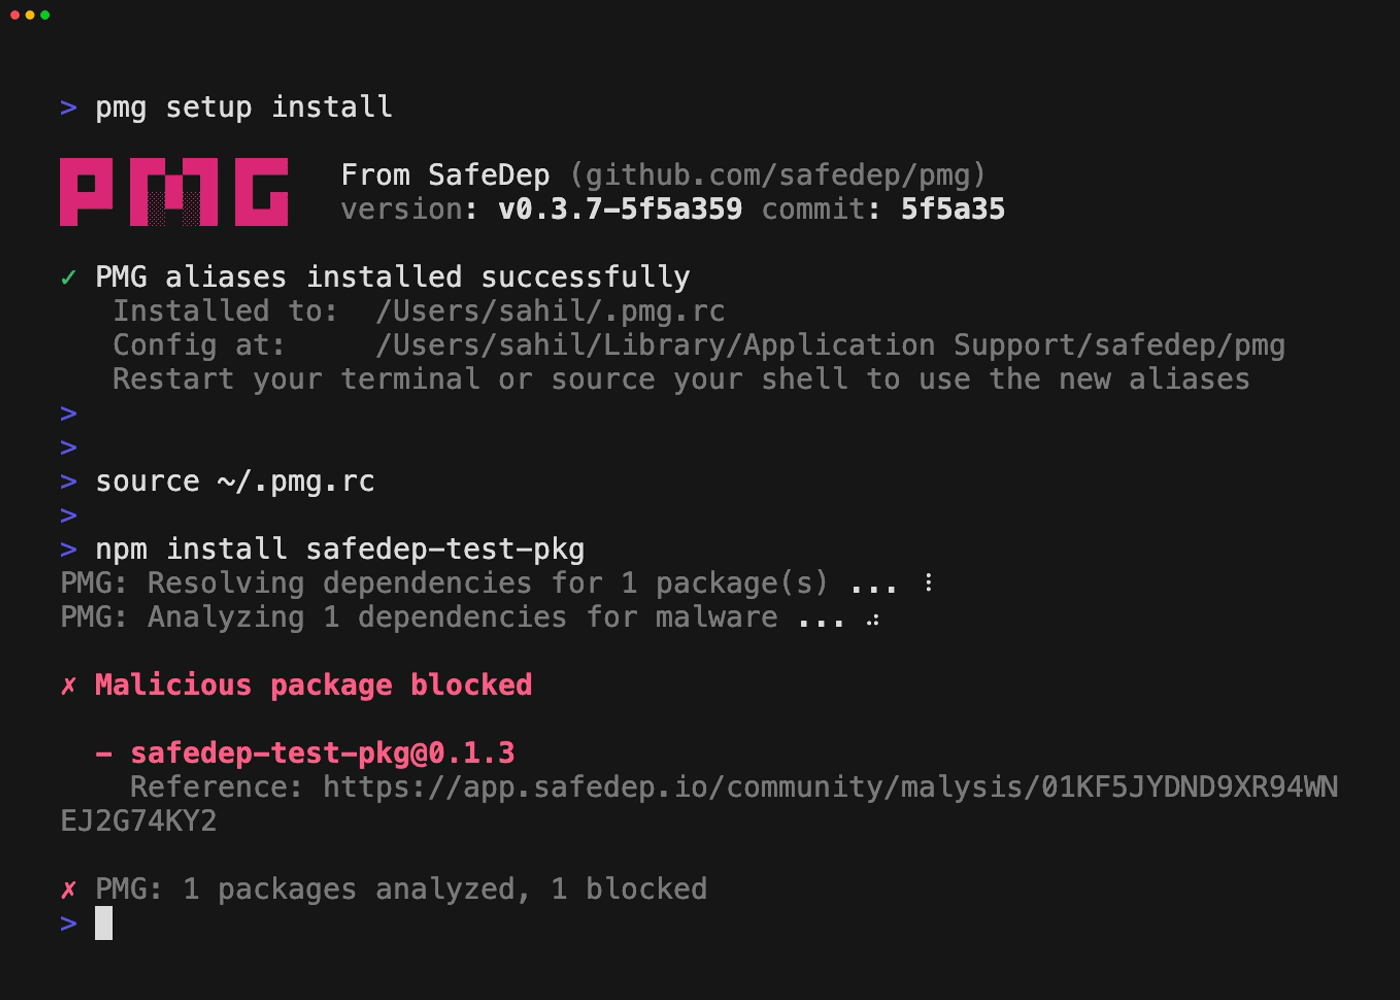 safedep/pmg
PMG protects developers, AI agents from malicious open source packages using proxy, sandbox and SafeDep's threat intelligence feed.
 mondoohq/cnspec
An open source, cloud-native security to protect everything from build to runtime
 secdevops-cuse/cyberrange
The Open-Source AWS Cyber Range
 manuelschipper/nah
a guard that blocks catastrophic agent actions
 synacktiv/nord-stream
Nord Stream is a tool that allows you to extract secrets stored inside CI/CD environments by deploying malicious pipelines. It currently supports…
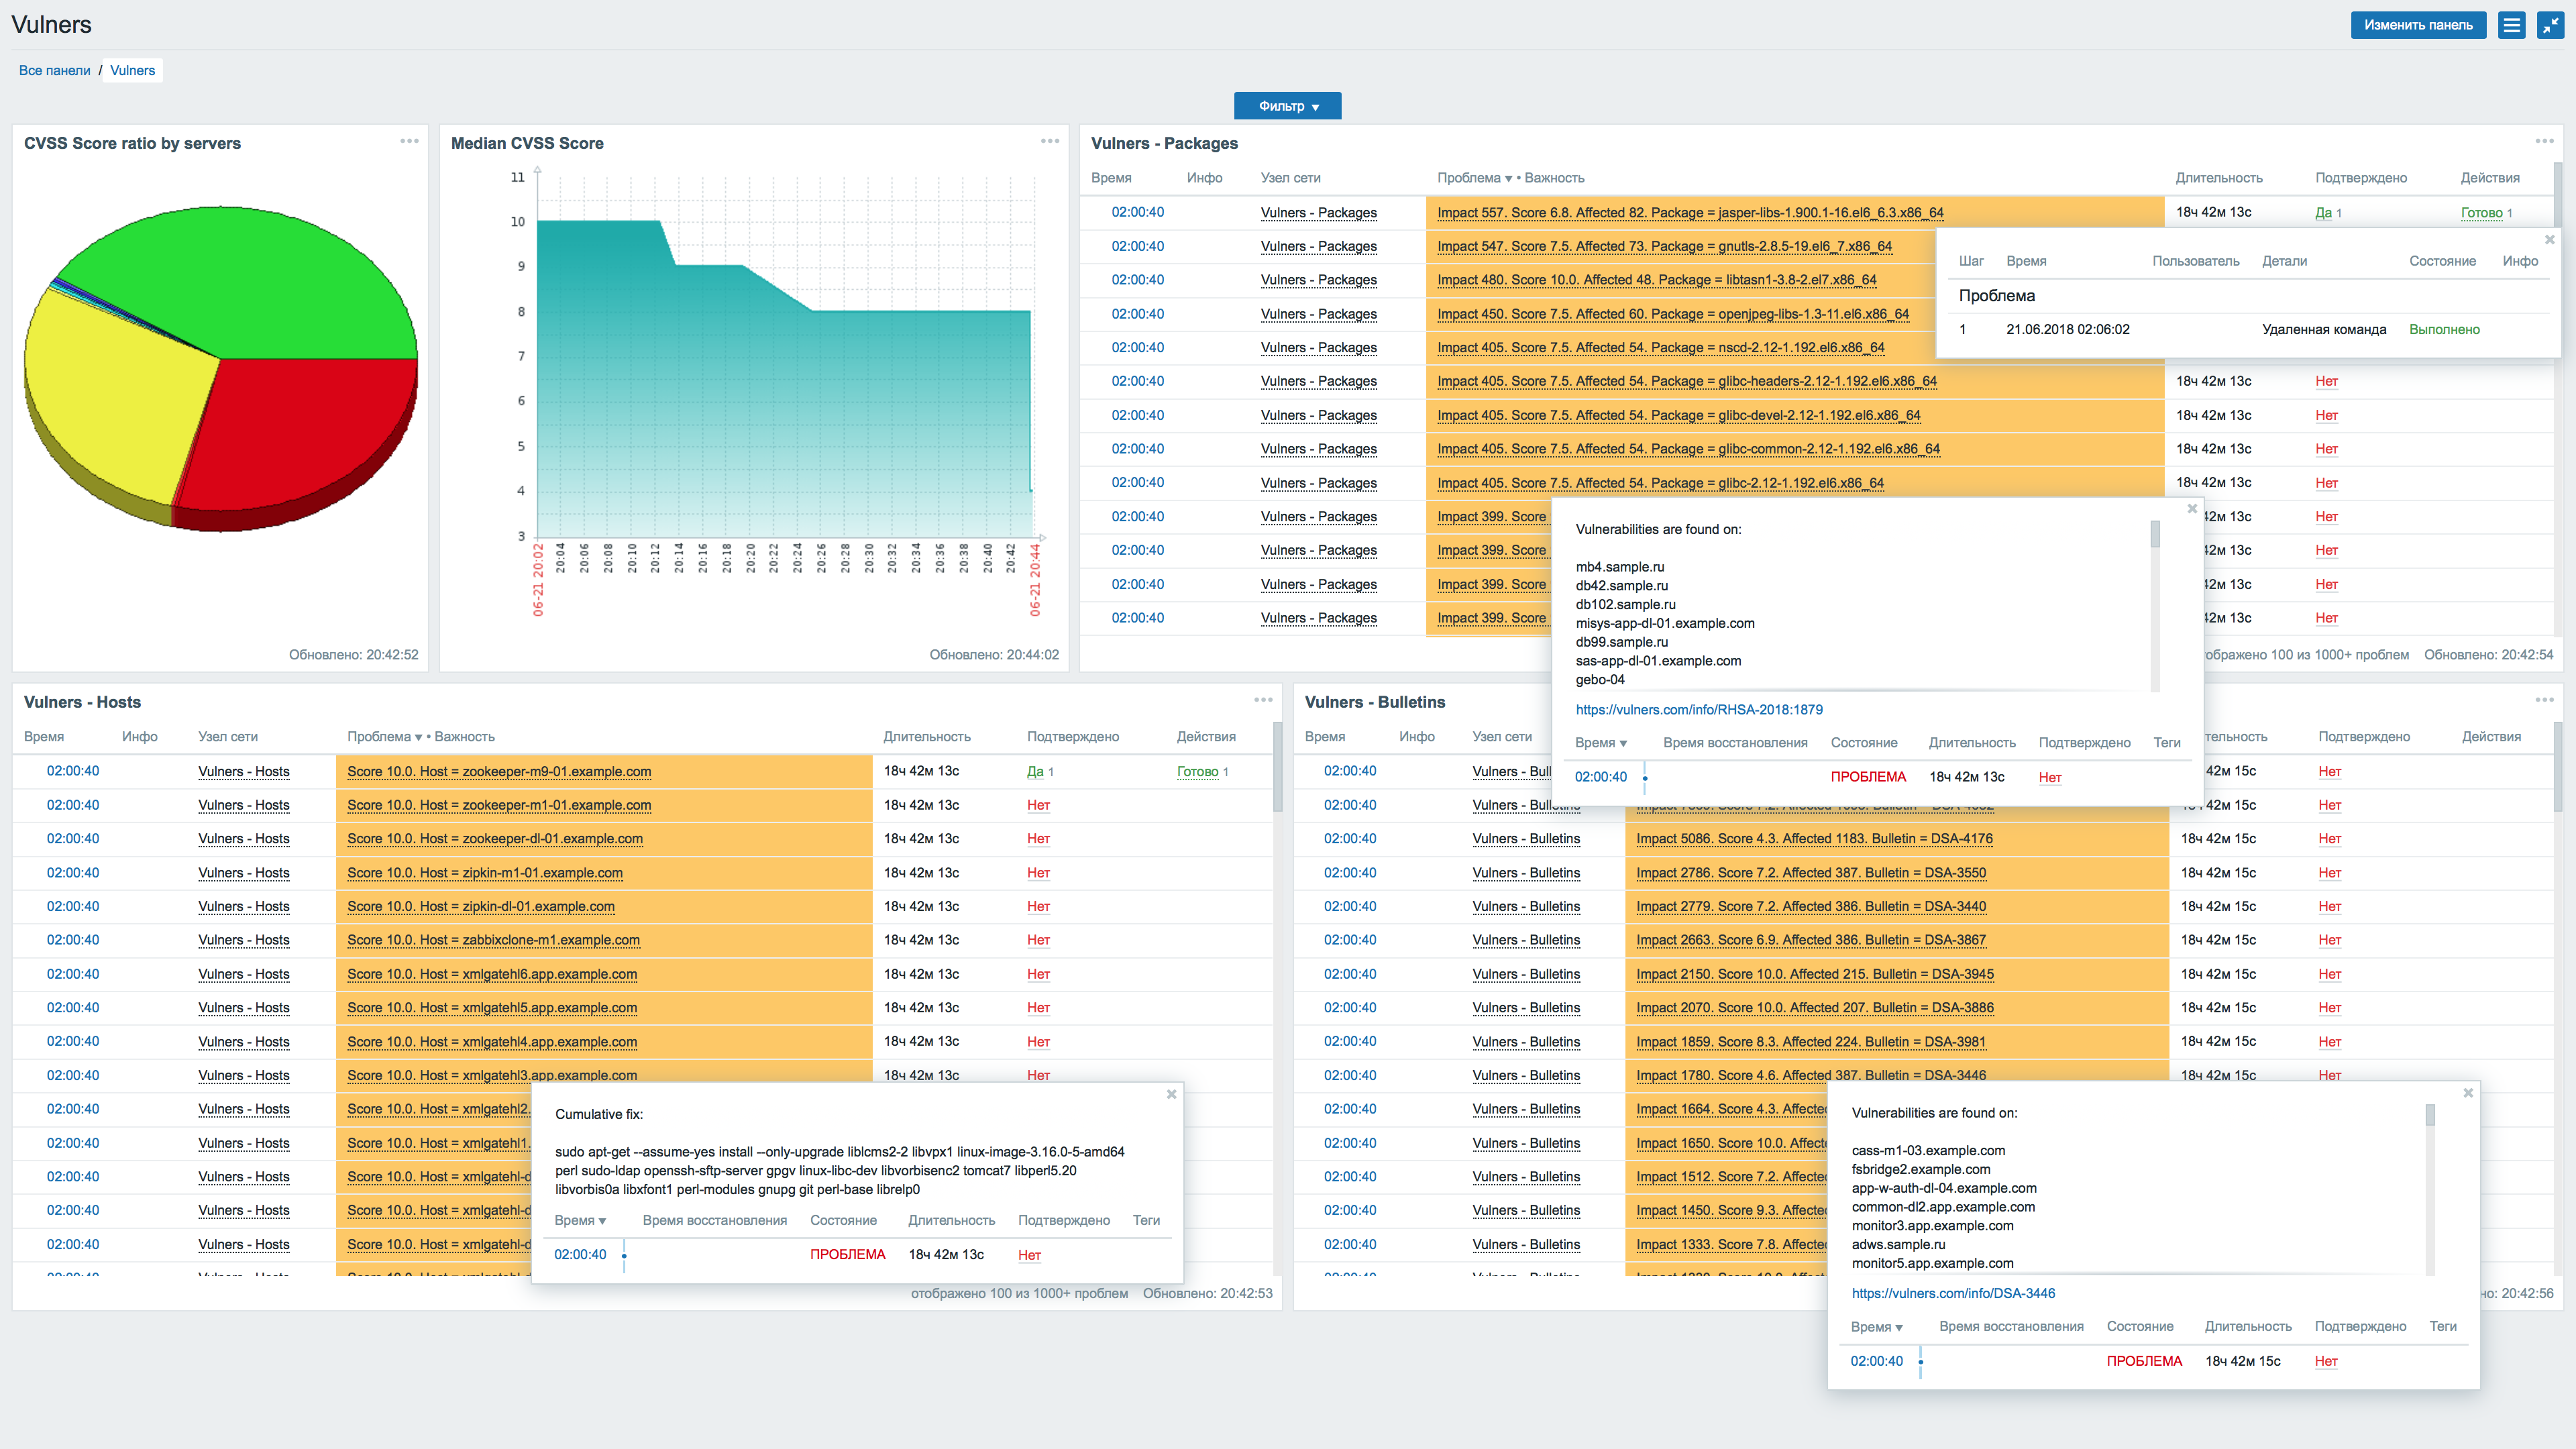 vulnerscom/zabbix-threat-control
Zabbix vulnerability assessment plugin
 kvesta/vesta
A static analysis of vulnerabilities, Docker and Kubernetes cluster configuration detect toolkit based on the real penetration of cloud computing
 mathaix/openclawmachines
Manage OpenClaw in your team (Enterprise) by providing it compute infrastructure, tool integration, Authentication and security primitives
 fabriziosalmi/tanstack-compromise-checker
Shell script to detect TanStack npm supply chain attack indicators (CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx)
 nu0l/nginx-rift
CVE-2026-42945 NGINX 堆溢出漏洞扫描与验证工具
 barrersoftware/opencode-secure
Security-hardened fork of OpenCode - Fixes CVE-2026-22812 (CVSS 8.8 RCE) that upstream refuses to patch