
patch-CVE-2026-19843
 gduma-phdata/patch-cve-2026-19843
Patch: Privilege escalation via web UI (Cisco IOS XE)
configuration-auditingdevsecopsnetwork-security+1
gduma-phdata/patch-cve-2026-19843Patch: Privilege escalation via web UI (Cisco IOS XE)
 hackervlogofficial/cve-2026-23918
This is a proactive tool for security auditing. For your GitHub repository, you’ll want a description that highlights its safety (non-intrusive) and…
 sibersan/web-server-audit_cve-2026-42945
Trigger-aware web server CVE audit for nginx and Apache. Goes beyond version matching by checking whether the vulnerable code path is actually…
 thesisgroup3/secassessment_gapdetect
Rule-based CLI tool that grades organizational defenses against MITRE ATT&CK and D3FEND frameworks, detects security gaps, and proposes mitigations.…
 brunoh6/web-threat-mitigation
Hands-on lab on detecting and mitigating web app threats using OWASP ZAP, Burp Suite, and ModSecurity WAF (with OWASP CRS). Case study: Spring4Shell…
 cybervixy/vulnerability-management
NGINX Security Hardening & Vulnerability Remediation Analysis of critical CVEs (CVE-2021-23017, HTTP/2 DoS flaws) in outdated NGINX versions, with…
 shoucheng3/wildfly__wildfly_cve-2018-1047_11-0-0-final
Java EE 7 application server with modular design, unified configuration, and management. Supports standalone and domain modes with built-in testing…
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 digitalocean/nginxconfig.io
⚙️ NGINX config generator on steroids 💉
 getsops/sops
Simple and flexible tool for managing secrets
 future-architect/vuls
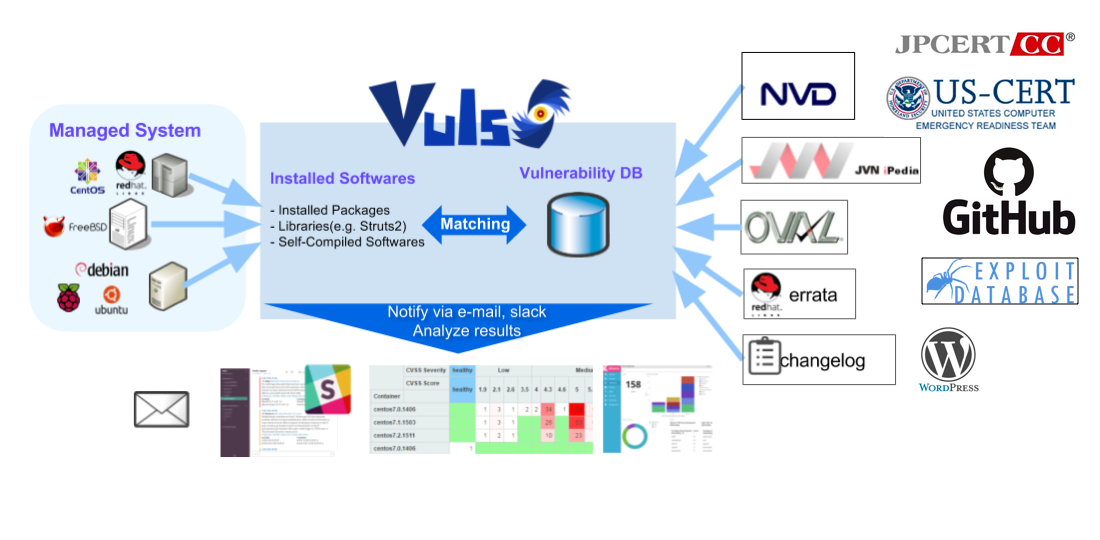
Agent-less vulnerability scanner for Linux, FreeBSD, Container, WordPress, Programming language libraries, Network devices
 netalertx/netalertx
Centralized network visibility and continuous asset discovery. Monitor devices, detect change, and stay aware across distributed networks.
 aquasecurity/starboard
Superseded by https://github.com/aquasecurity/trivy-operator
 tugcantopaloglu/openclaw-dashboard
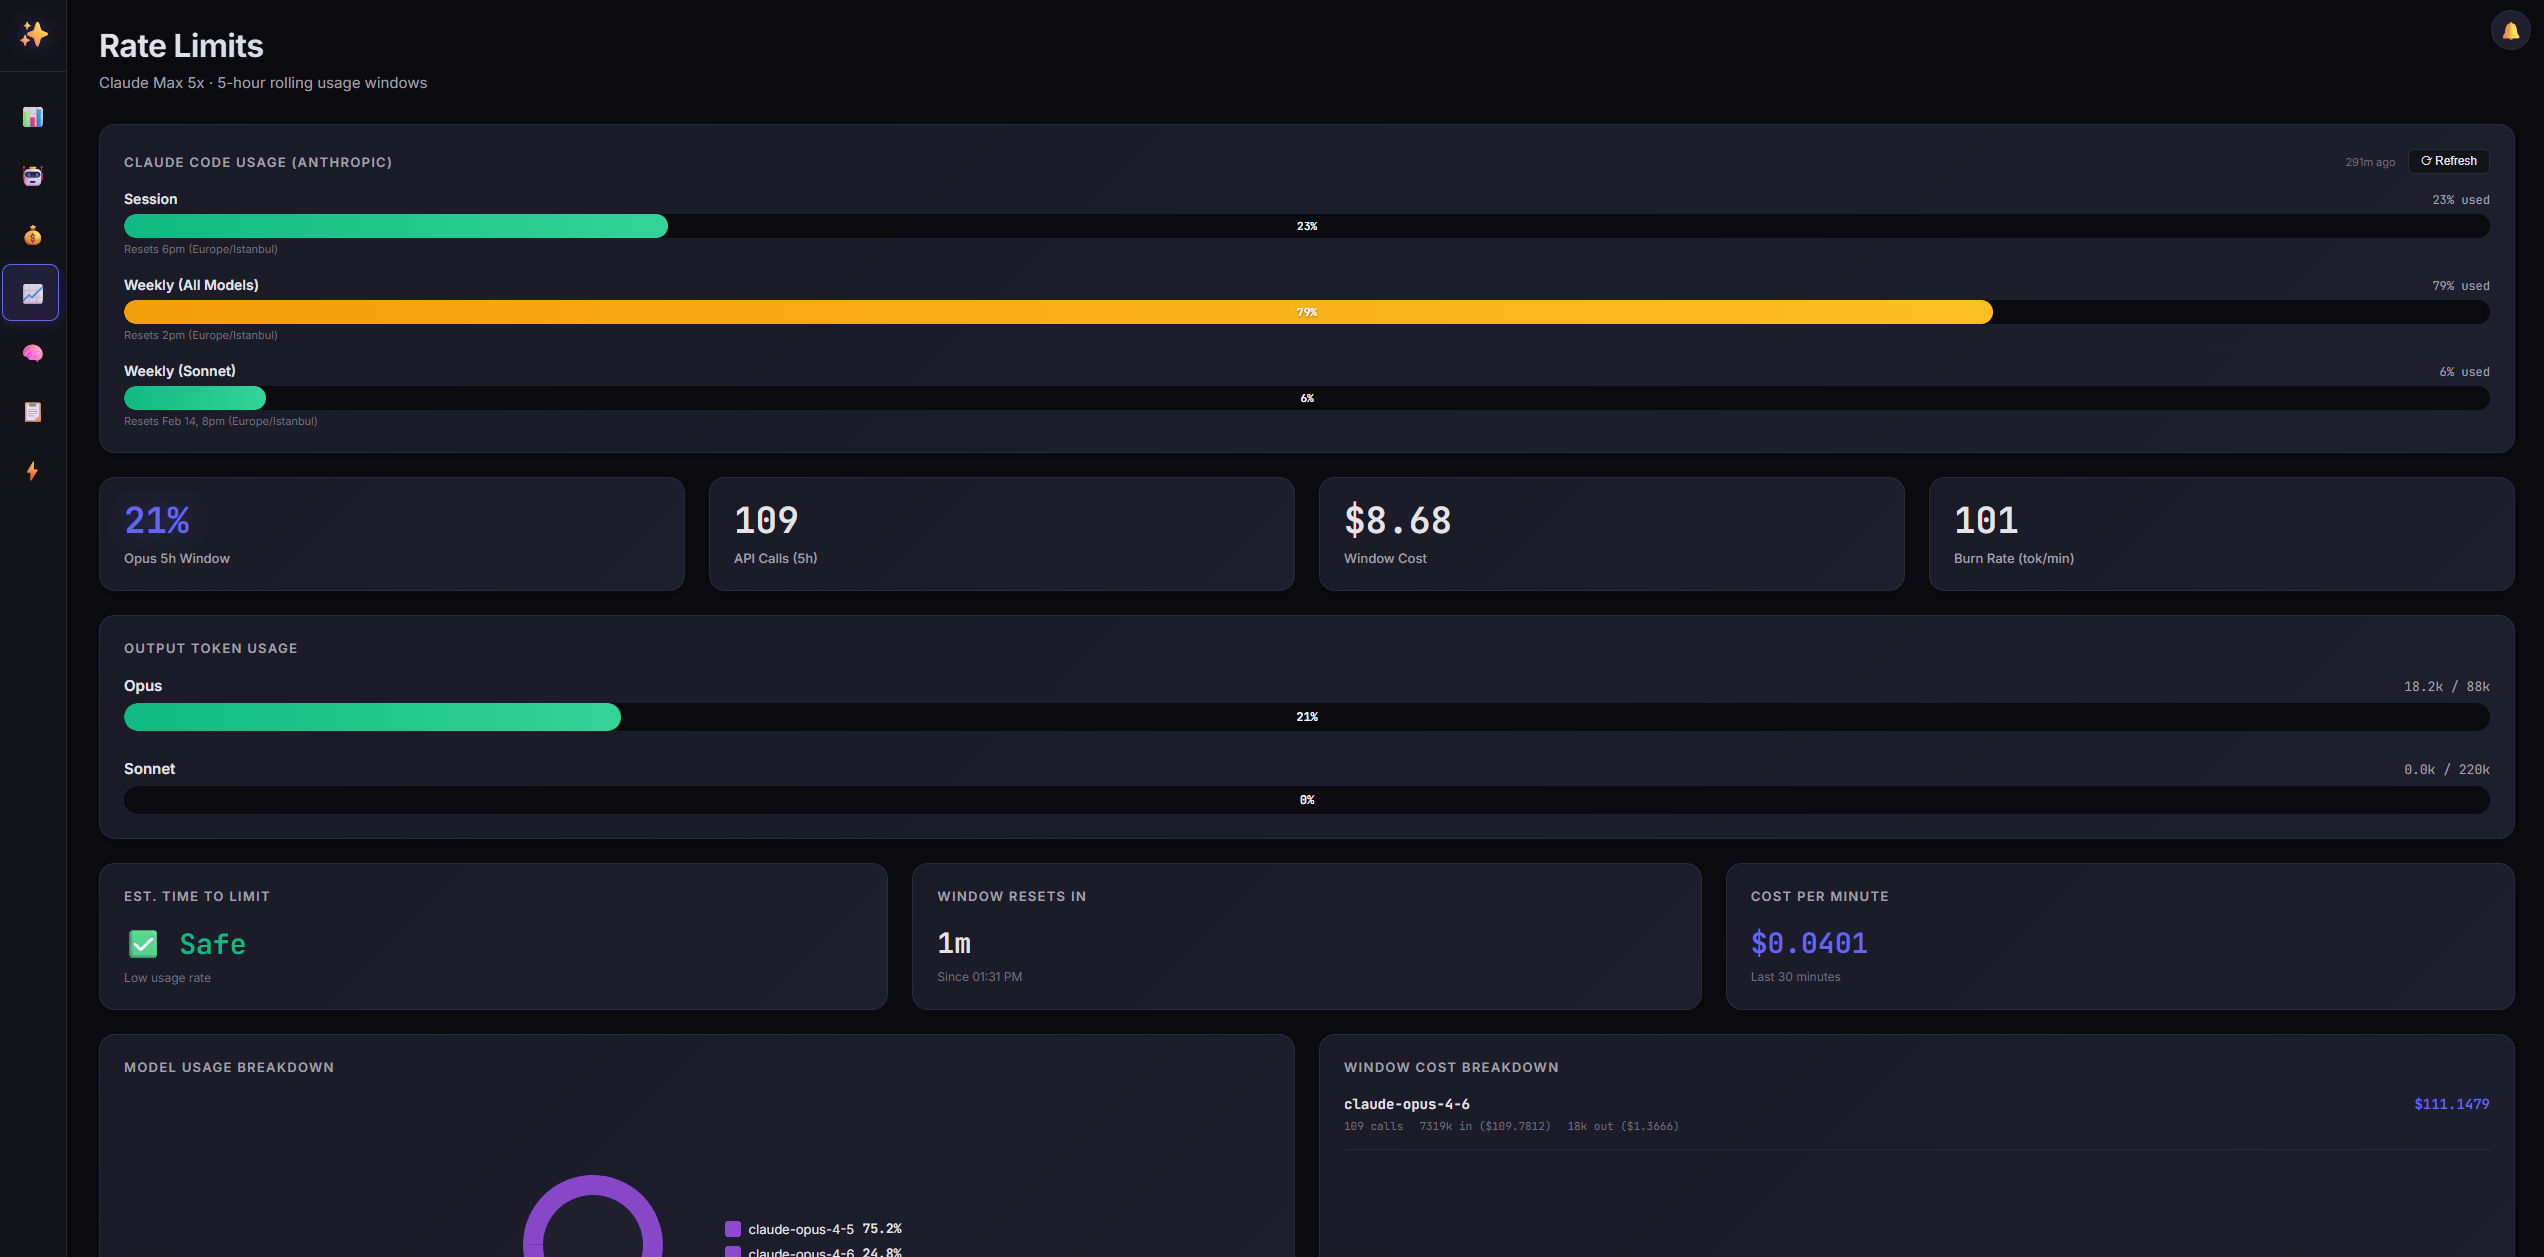
🔐 Secure, real-time monitoring dashboard for OpenClaw AI agents. Auth, TOTP MFA, cost tracking, live feed, memory browser and more.
 ttlab-research/awesome-wazuh
🛡️Awesome lists about all kinds of interesting topics of Wazuh XDR/SIEM
 tindersec/gh-workflow-auditor
Script to audit GitHub Action Workflow files for potential vulnerabilities.
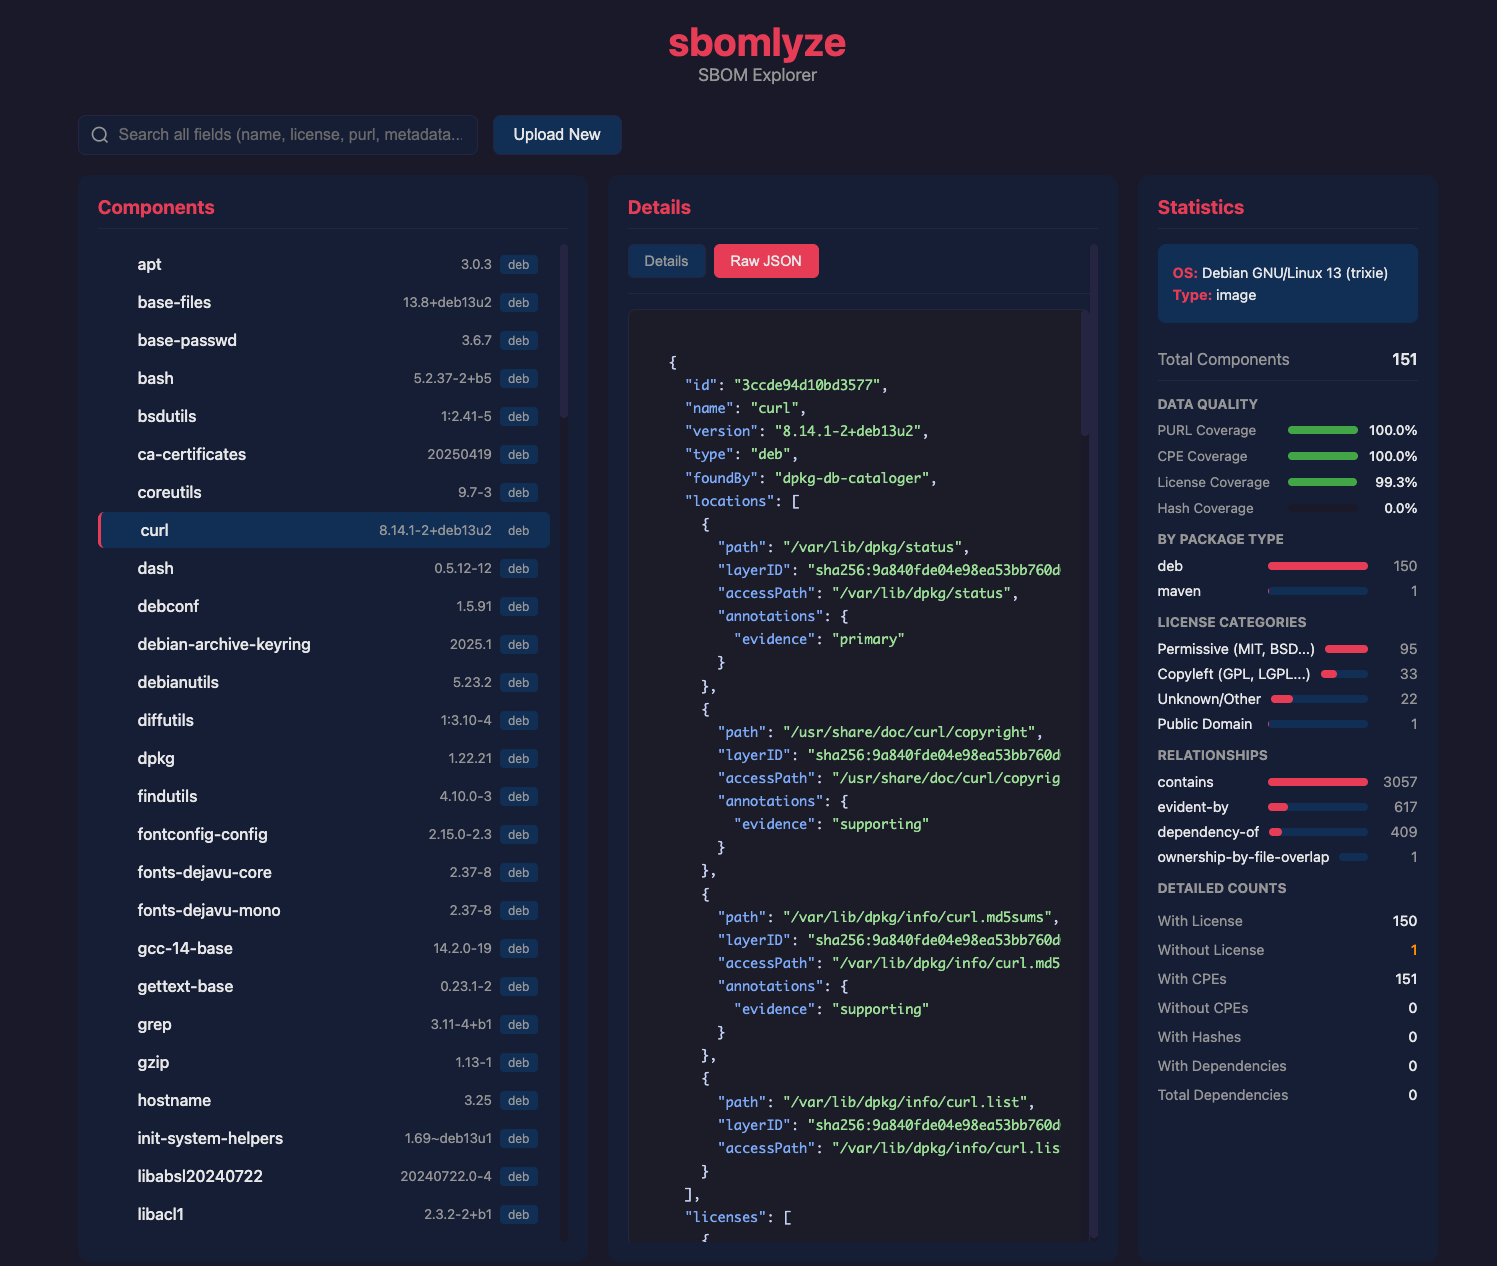 rezmoss/sbomlyze
Git diff for SBOMs—compare CycloneDX, SPDX, and Syft documents, detect tampering, and gate CI.
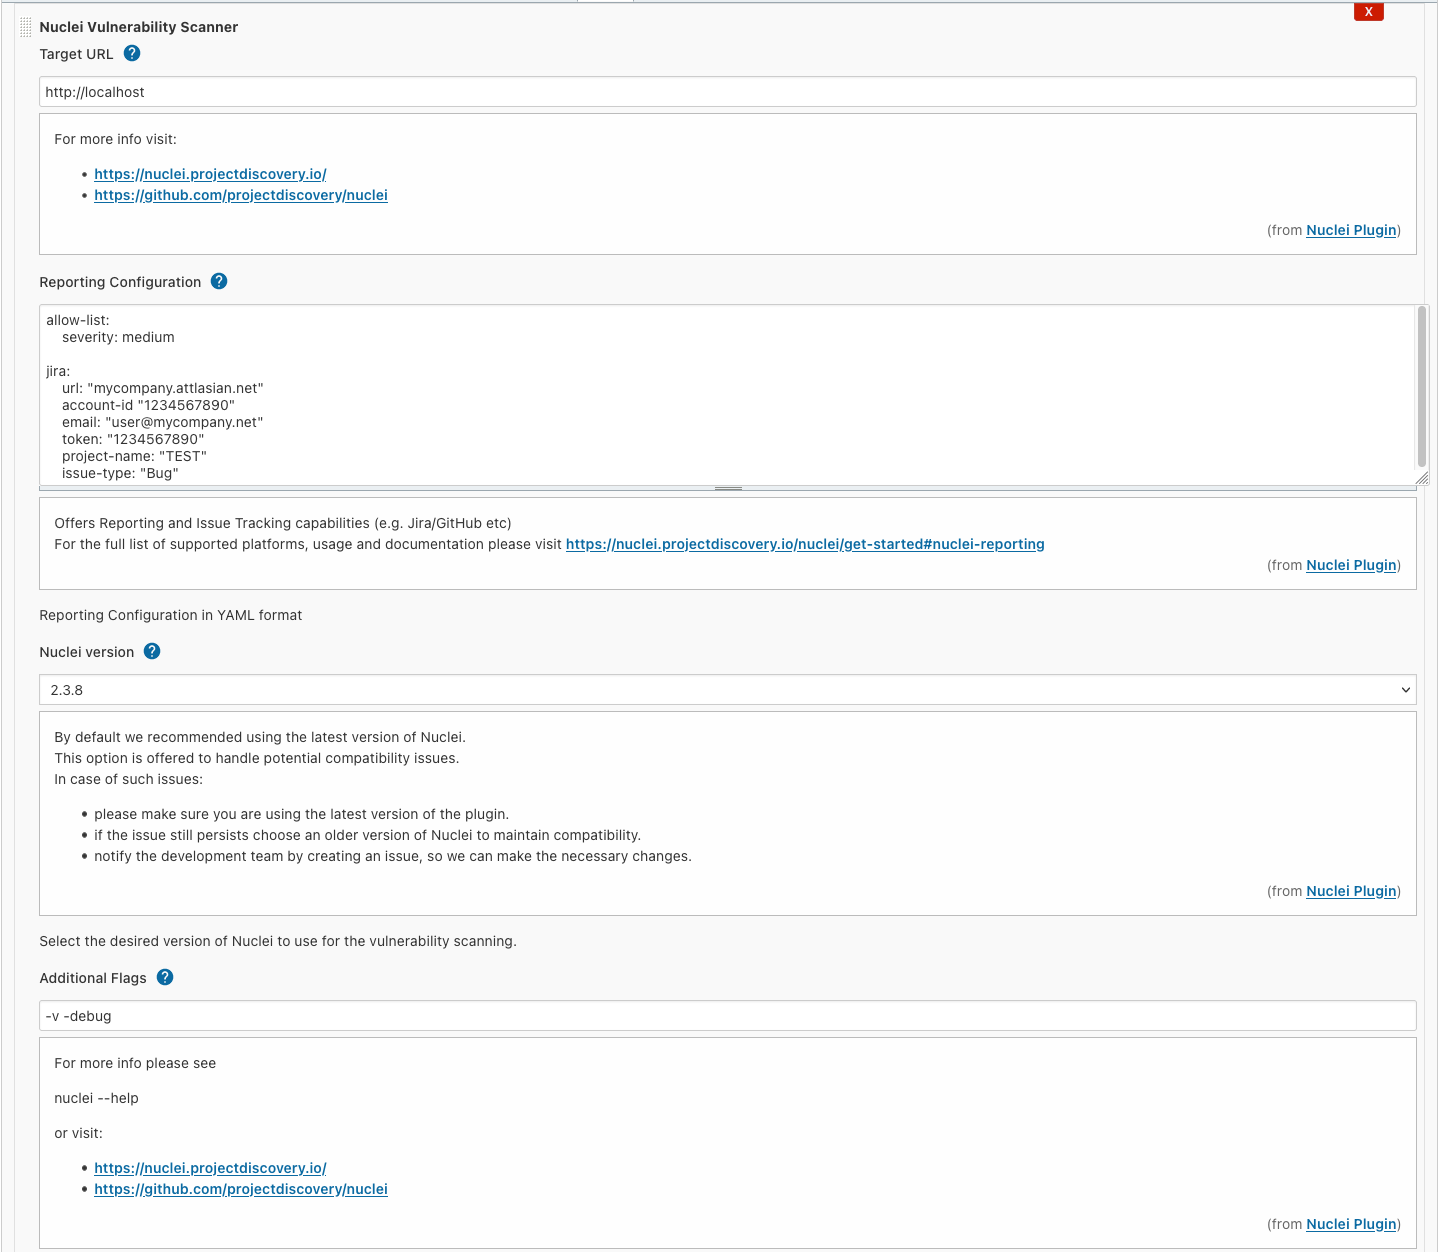 jenkinsci/nuclei-plugin
Nuclei is a fast tool for configurable targeted vulnerability scanning based on templates offering massive extensibility and ease of use.