
nord-stream
 synacktiv/nord-stream
Nord Stream is a tool that allows you to extract secrets stored inside CI/CD environments by deploying malicious pipelines. It currently supports…
data-exfiltrationdevsecopsexploitation+5
378
synacktiv/nord-streamNord Stream is a tool that allows you to extract secrets stored inside CI/CD environments by deploying malicious pipelines. It currently supports…
 0sec-labs/foxguard
A fast universal code security scanner, written in Rust. Batteries included: supports 14 languages, TUI for triage, secrets, post-quantum audits,…
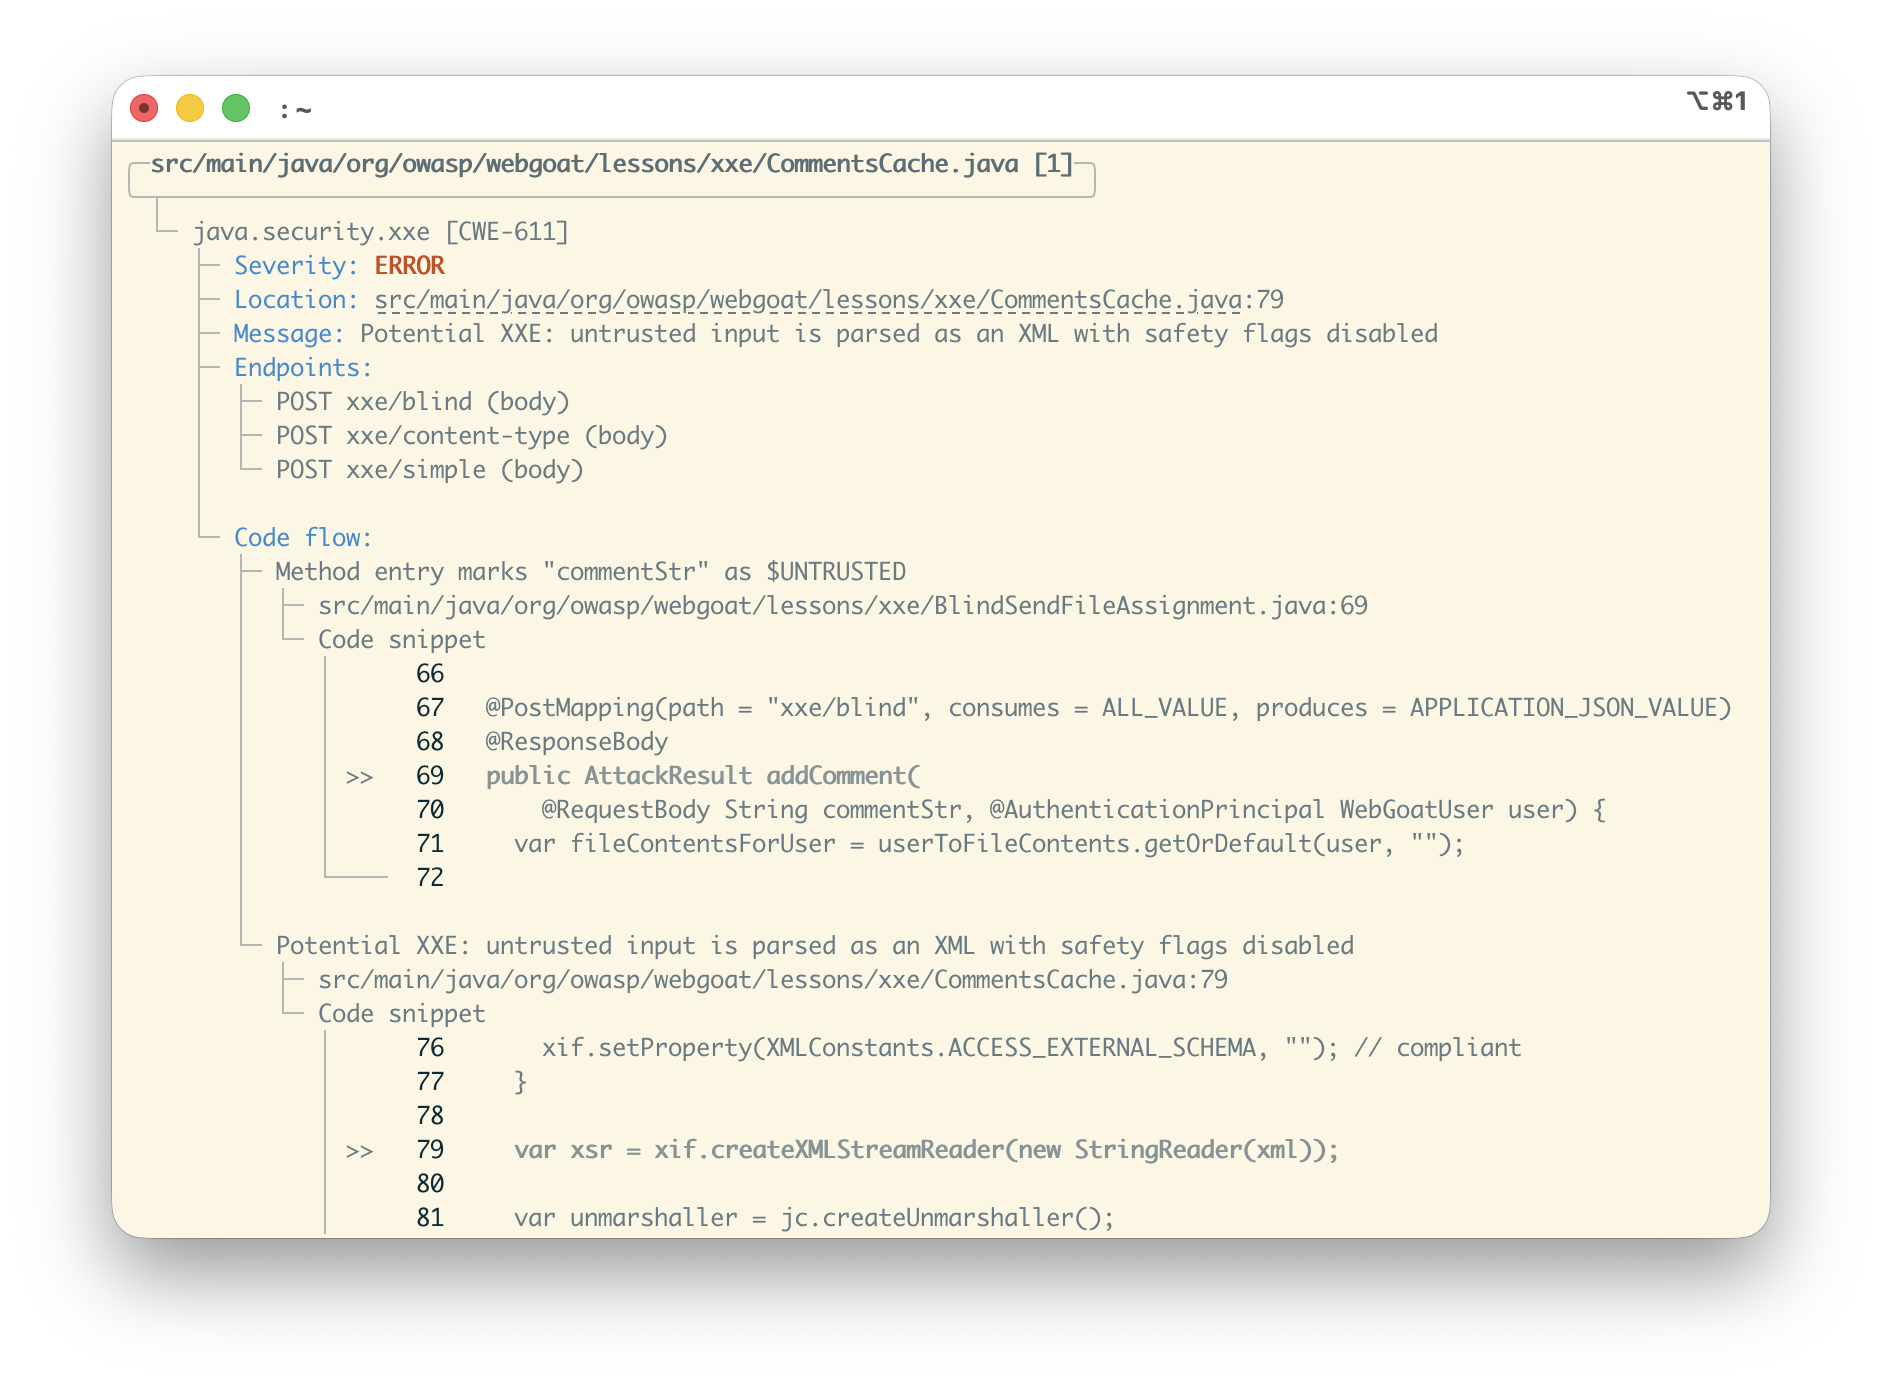 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
 kvesta/vesta
A static analysis of vulnerabilities, Docker and Kubernetes cluster configuration detect toolkit based on the real penetration of cloud computing
 horizon3ai/h3-cli
CLI tool for the Horizon3.ai API
 pigyon/mcpwner
Model Context Protocol server for autonomous vulnerability discovery
 momenbasel/malware-check
Static and dynamic analysis tool for detecting malicious code, suspicious binaries, and privacy violations
 offseq/threat-finder
Runtime vulnerability scanner: finds CVEs in the services actually running on a host and ranks them by network exposure.
 owasp/vulnreach
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 tanmayshahane/kyubisweep
A lightweight, cross-platform CLI tool that scans your filesystem to detect exposed secrets, API keys, and tokens. Built with Go for maximum…
 plutosecurity/mcpwnfluence
Information about CVE-2026-27825 & CVE-2026-27826 discovered by Pluto Security and a bash script for identifying vulnerable mcp-atlassian instances…
 nu0l/nginx-rift
CVE-2026-42945 NGINX 堆溢出漏洞扫描与验证工具
 vulnz/sast
Free offline SAST engine for CI/CD: AST and cross-file taint analysis, secret detection with live validation, SCA/CVE, IaC misconfiguration, and…
 kaminaduck/ansible-cve-2024-3094
Ansible playbooks designed to check and remediate CVE-2024-3094 (XZ Backdoor)
 aestechno/cve-2026-31431-ansible
Ansible playbook to detect and apply kernel cmdline mitigation for CVE-2026-31431 (Copy Fail) across Debian/Ubuntu/RHEL fleets, with read-only…
 studiomeyer-io/mcp-stdio-shellguard
Defense-in-depth bundle for MCP stdio servers: drop-in guardExec/guardSpawn wrappers, AST audit CLI, reference MCP server. Closes the Ox-Security…
 brunoh6/web-threat-mitigation
Hands-on lab on detecting and mitigating web app threats using OWASP ZAP, Burp Suite, and ModSecurity WAF (with OWASP CRS). Case study: Spring4Shell…