

Xpsd
 owasp/xpsd
Reachability triage for vulnerability scans. Feeds scanner findings to an LLM agent that reads your source and decides which CVEs are actually…
ai-securitycode-analysisdevsecops+6
410 days ago
owasp/xpsdReachability triage for vulnerability scans. Feeds scanner findings to an LLM agent that reads your source and decides which CVEs are actually…
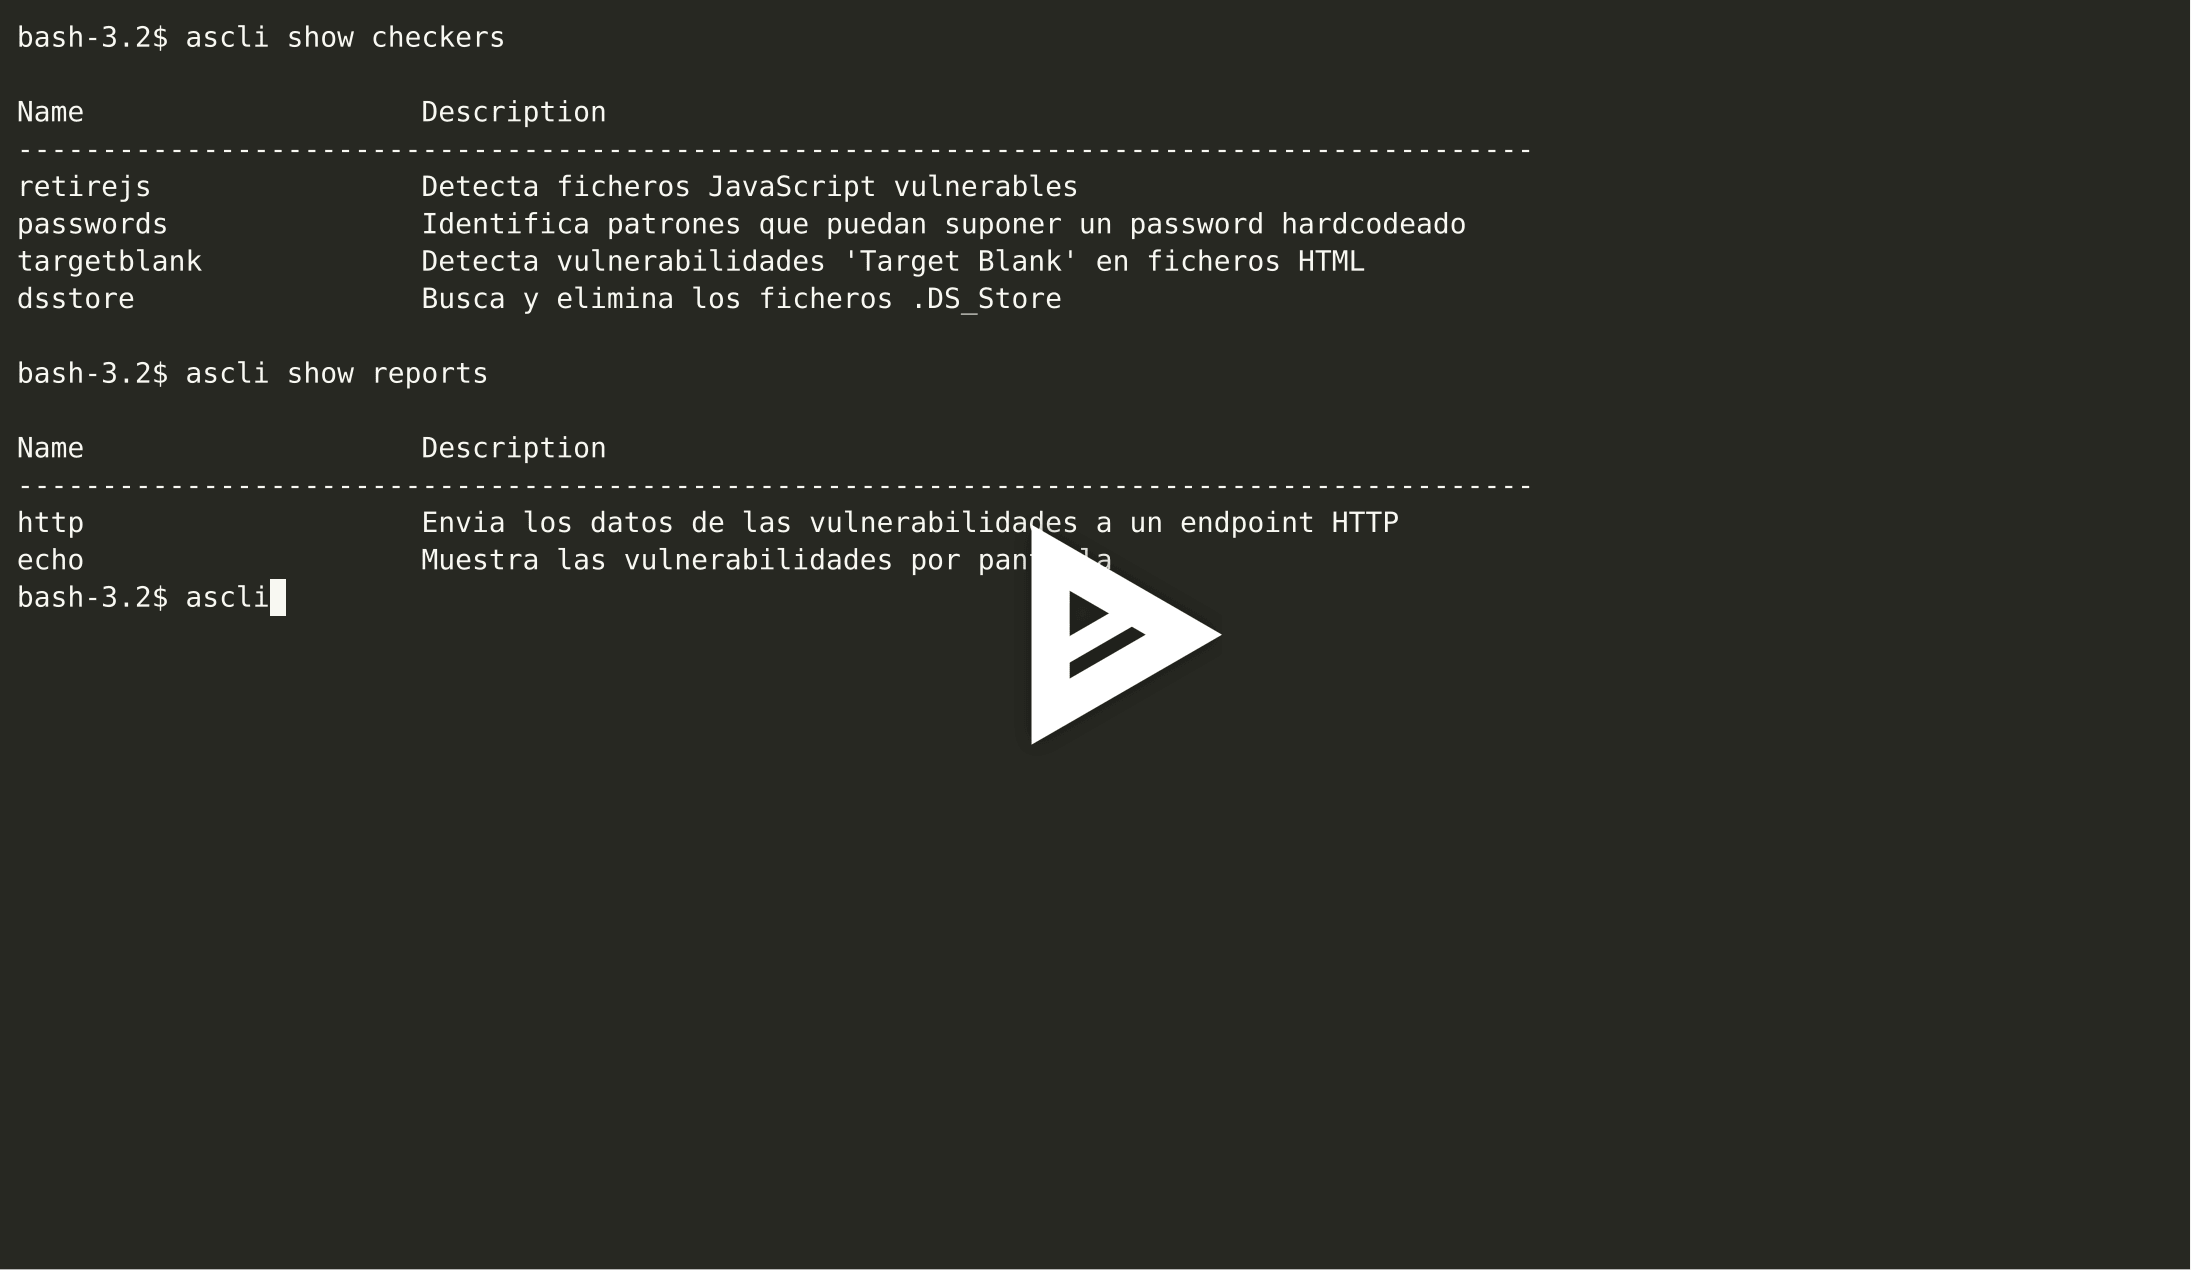 elevenpaths/atomshields-cli
CLI for AtomShields static analysis scanner. Install, uninstall, and run checkers and reports to detect vulnerabilities in source code projects.
 kriskimmerle/wheelaudit
Python Wheel File Security Scanner — scan .whl files for security issues before installation. Detects path traversal (CVE-2026-24049), RECORD…
 newrelic/rusty-hog
Multi-source secret scanner detecting API keys, passwords, and PII across Git repos, S3 buckets, filesystems, Confluence, JIRA, Slack, and Google…
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
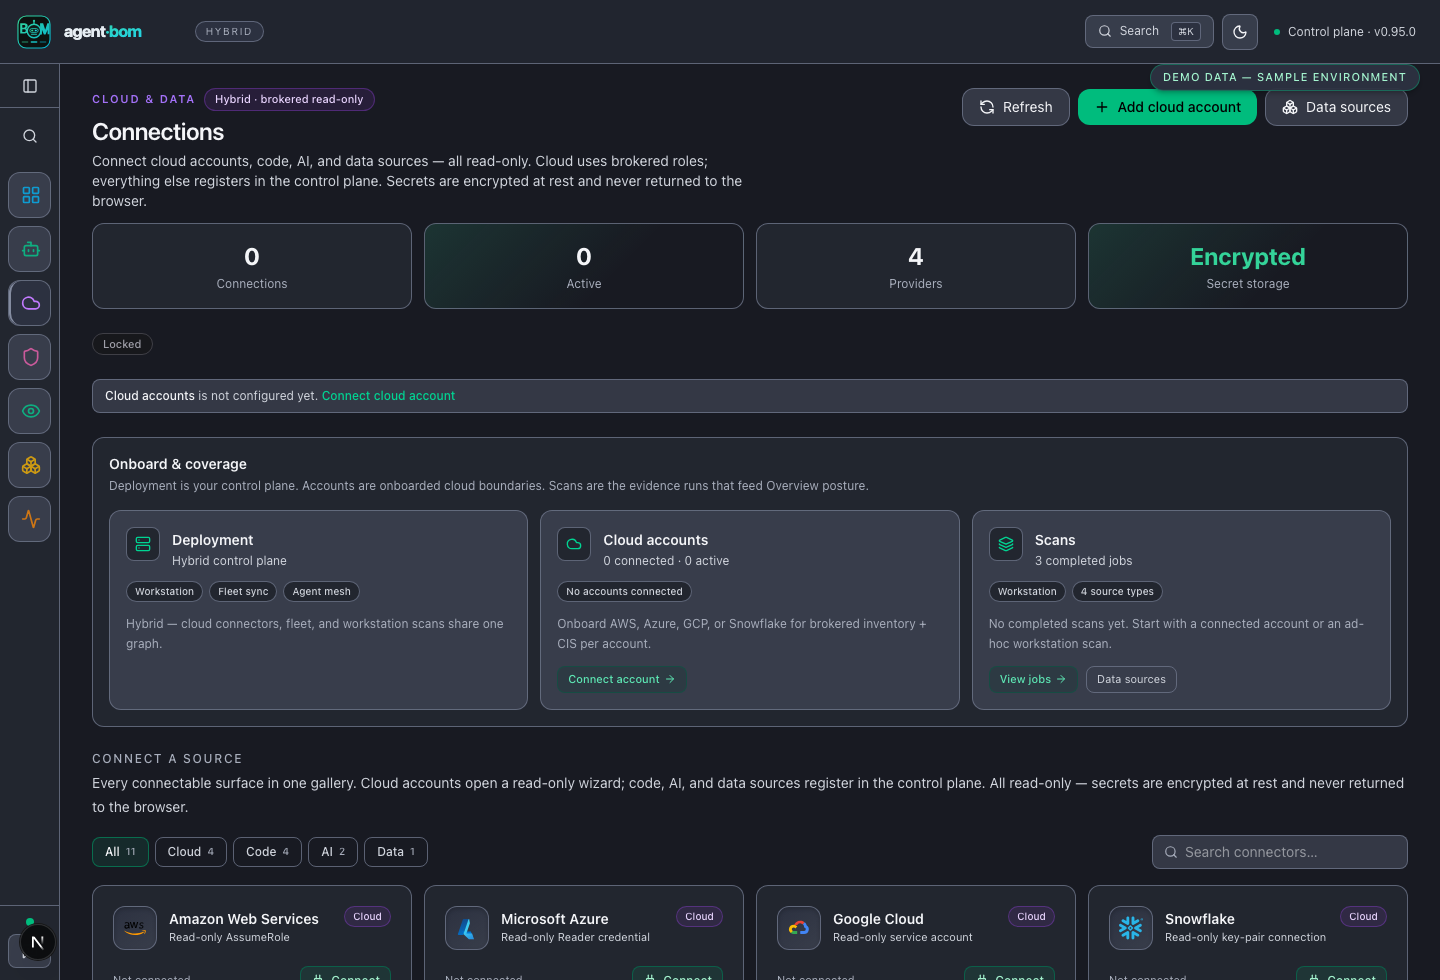 msaad00/agent-bom
AI supply-chain BOM: every agent, MCP server and AI package, and what each one can reach. Open-source scanner and self-hosted control plane for code,…
 abhishek2512mishra/claude-code-security-audit
Security scanner auditing Claude Code environments for CVE-2026-21852 pre-trust execution, hook hijacking, and eBPF lockdown.
 danielxavierjob/-cve-2025-55182
Browser-based scanner that audits GitHub repositories for known vulnerabilities in React and Next.js dependencies, checking all branches and…
 owasp/agent-security-regression-harness
Executable security regression testing for agentic applications and MCP-integrated systems.
 mindpatch/vulfy
🐺 Vulfy – Fast Rust based package version scanner
 rapticore/ore-mal-pkg-inspector
Multi-Ecosystem Malicious Package Detection and Supply Chain Security Scanner
 captain4554/cve-2025-55182-scanner
🛡️ Scan and assess vulnerabilities in Next.js/Waku with the CVE-2025-55182-Scanner, combining static and dynamic analysis for robust security.
 corgea/sighthound
Tree-sitter based static vulnerability scanner with pattern matching and taint-flow analysis for multi-language source code. Outputs findings as…
 pii-shield/pii-shield
Zero-code K8s sidecar for log sanitization. Detects secrets via Entropy Analysis, preserves JSON integrity, and redacts PII deterministically. 🛡️
 niclas-zone/ci/trivy
GitLab CI component for Trivy scanning
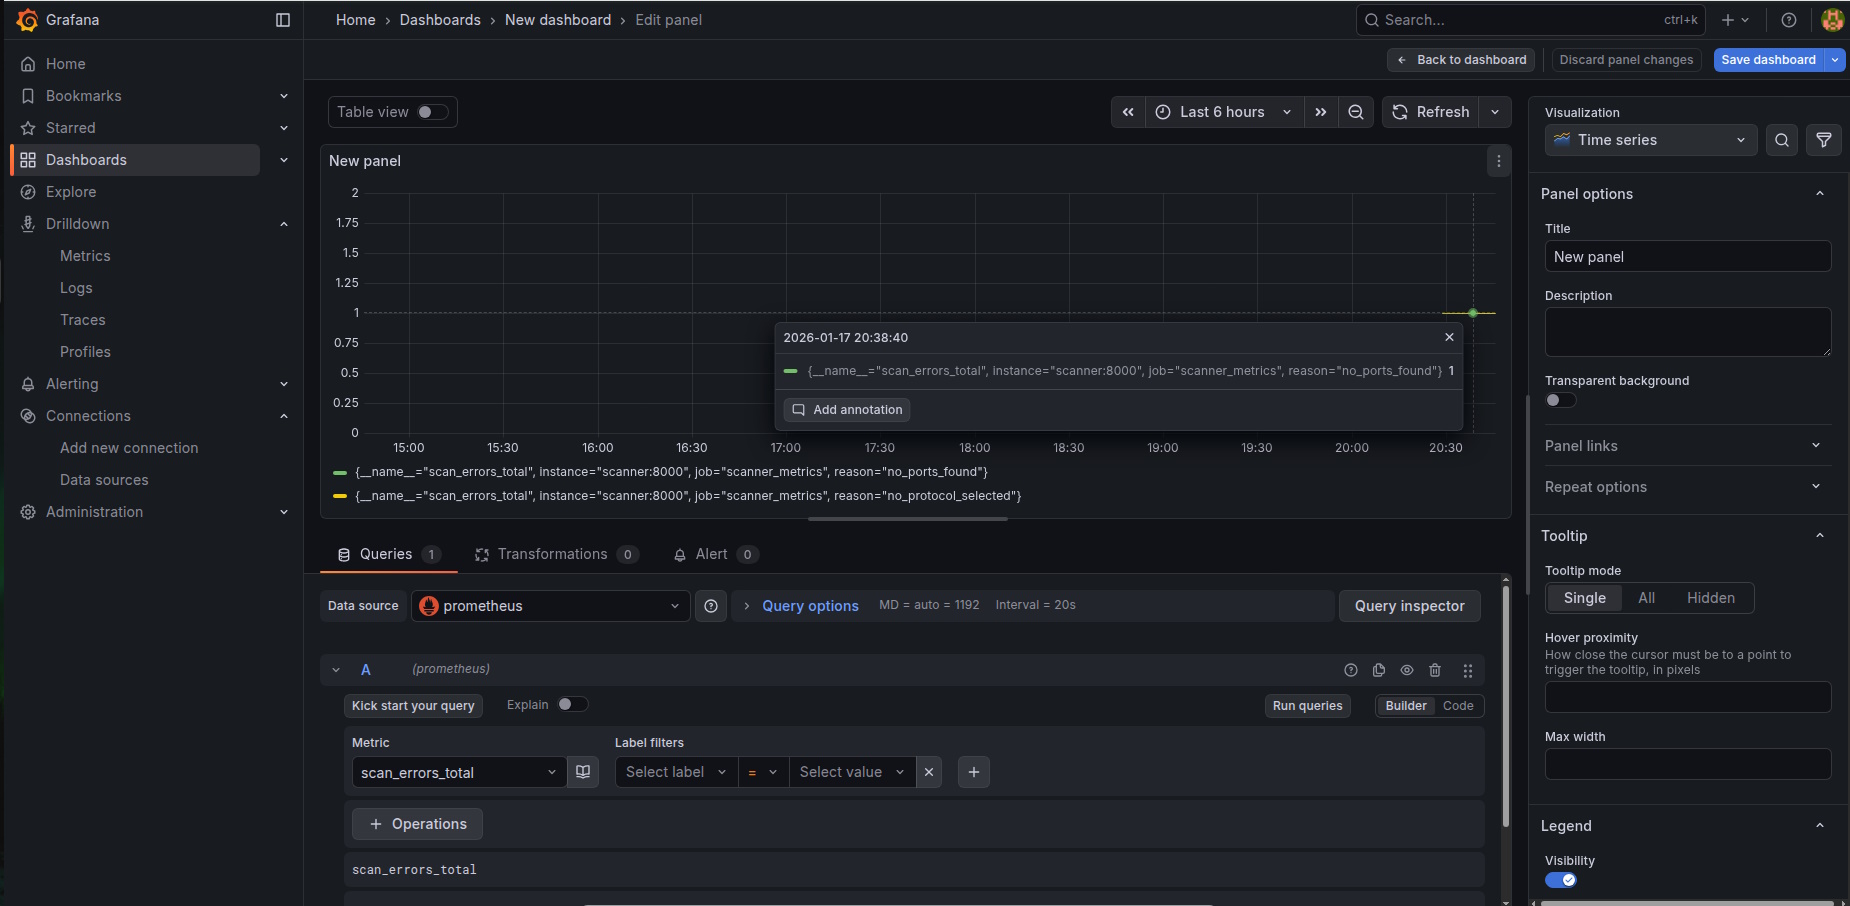 znakar/sharktooth
Port Scanner with Docker & Prometheus + Grafana integration. A tool for network auditing with multithreading support and real-time monitoring.
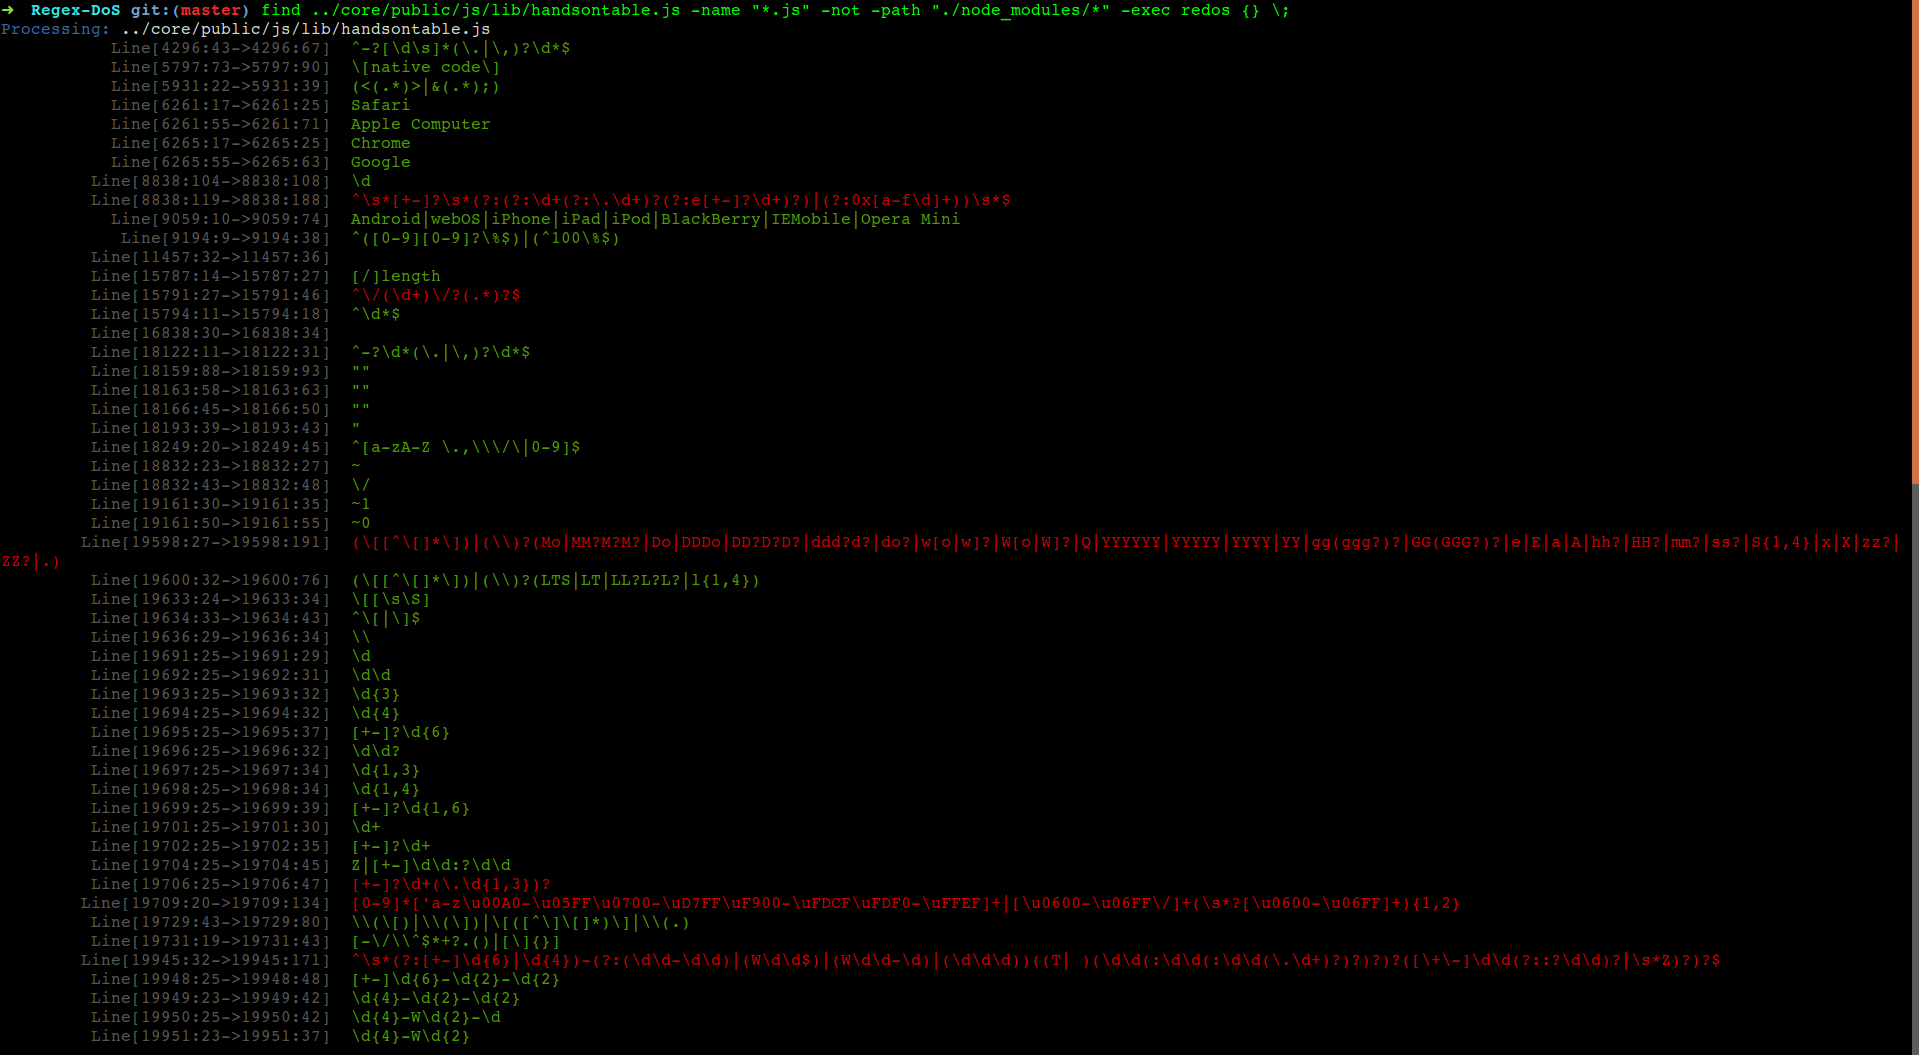 jagracey/regex-dos
:cop: :punch: RegEx Denial of Service (ReDos) Scanner
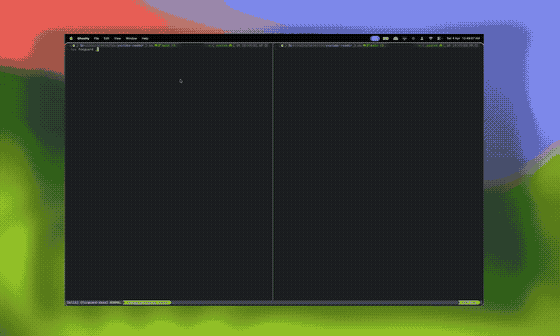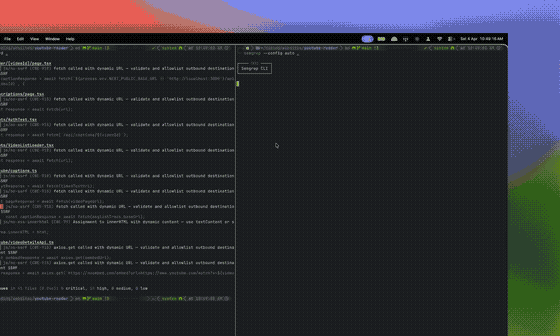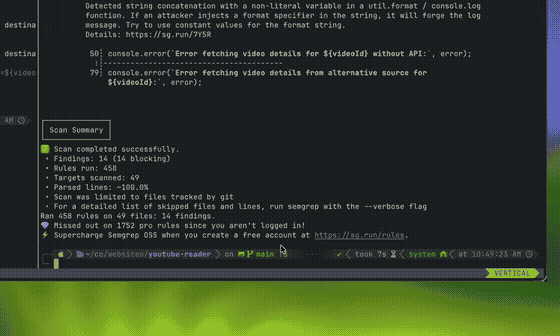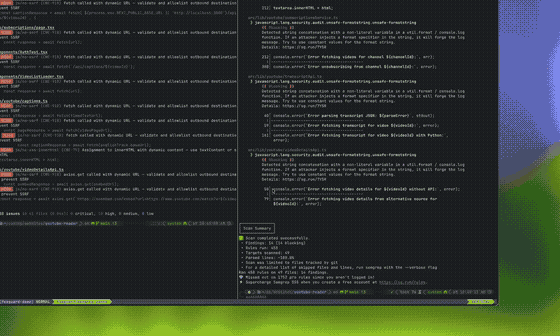 0sec-labs/foxguard
A fast universal code security scanner, written in Rust. Batteries included: supports 14 languages, TUI for triage, secrets, post-quantum audits,…