
bomber
 devops-kung-fu/bomber
Scans Software Bill of Materials (SBOMs) for security vulnerabilities
devsecopssupply-chain-securityvulnerability-scanners
devops-kung-fu/bomberScans Software Bill of Materials (SBOMs) for security vulnerabilities
 devsecopsdocs/nuclearpond
Nuclear Pond is a utility leveraging Nuclei to perform internet wide scans for the cost of a cup of coffee.
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
 infobyte/faraday_plugins
Security tools report parsers for Faradaysec.com
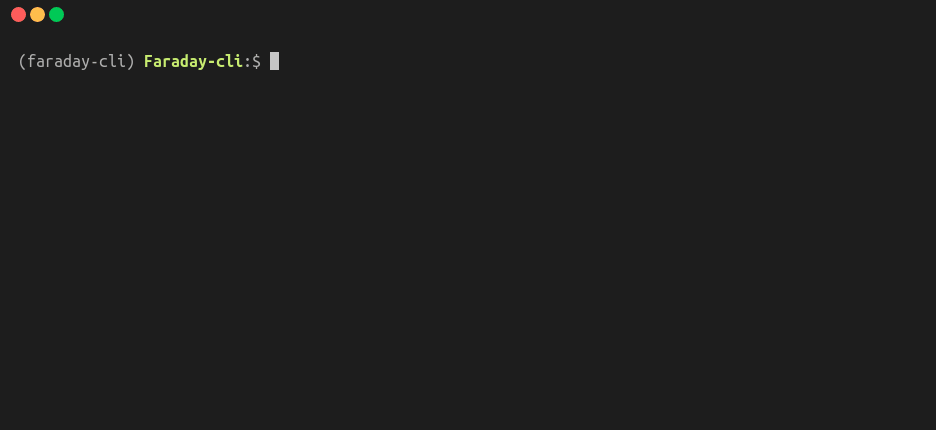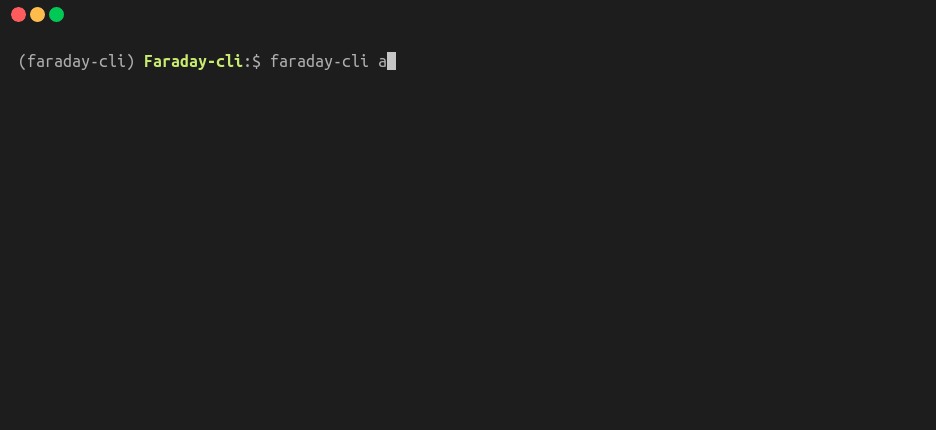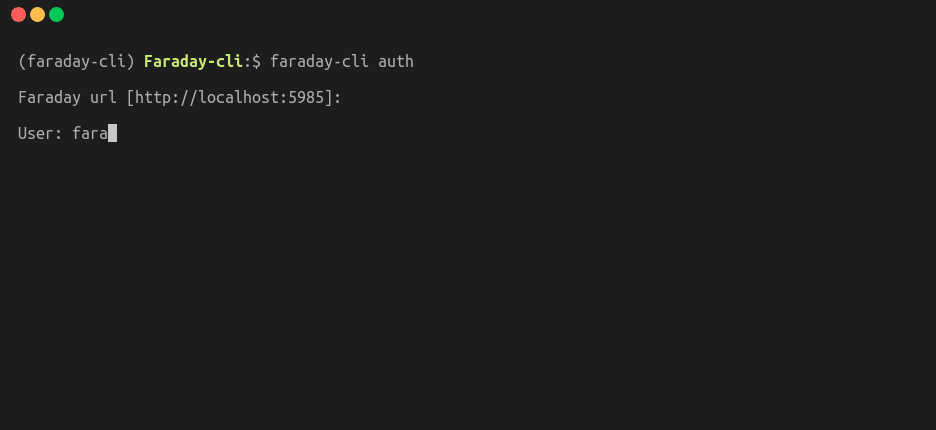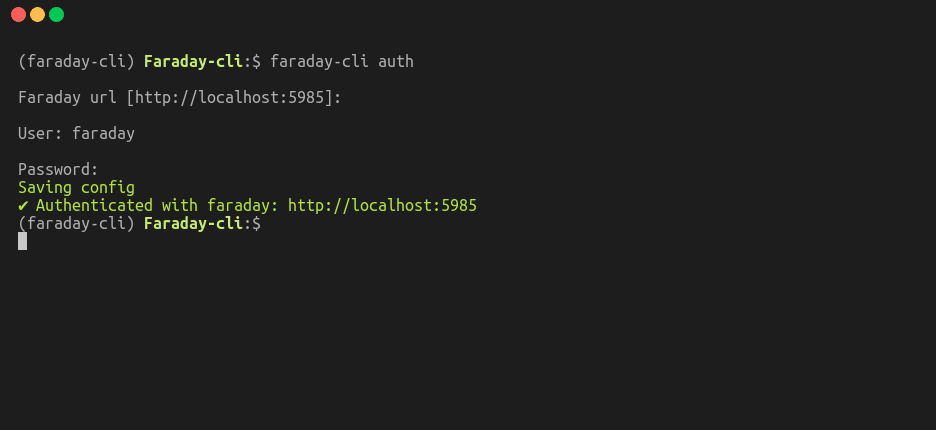 infobyte/faraday-cli
Faraday's Command Line Interface
 apiiro/combobulator
Modular framework to detect and prevent dependency confusion attacks by analyzing package manifests across multiple sources and package management…
 robert-auger/safer-dependencies
Automated dependency security layer for AI coding assistants that audits packages for CVEs, typosquats, abandonment, version-age issues, and hash…
 bugbounty-site/gitsecure
Detect exposed API keys on GitHub commits.
 components/dependency-scanning
Generates CycloneDX SBOMs and dependency scanning reports to identify project dependencies, licenses, and vulnerabilities within GitLab CI/CD…
 kingofbugbounty/nuclearpond-ofjaaah
Nuclear Pond is a utility leveraging Nuclei to perform internet wide scans for the cost of a cup of coffee.
 aaravmaloo/revera
The credit score for npm packages. Analyze package reputation, maintenance, security, publisher trust, and ecosystem health before you install any…
 knqyf263/go-mal-pkgs
A security tool to detect malicious Go packages by verifying checksums in go.sum against the original source code
 irgoncalves/f5-waf-quick-patch-cve-2021-44228
This tool creates a custom signature set on F5 WAF and apply to policies in blocking mode
 appomni-labs/heisenberg-ssc-gha
GitHub Action for Heisenberg SSC
 george0papasotiriou/cve-2026-22018-jenkins-pipeline-shared-library-code-execution-via-grab-
PoC for CVE-2026-22018, a critical Jenkins Pipeline Shared Library RCE via Groovy @Grab, demonstrating supply-chain code injection and mitigation…
 guardia-ai/gitlab-component
EU AI Act compliance scanner for GitLab CI/CD pipelines — detects AI/ML libraries and posts risk classification as MR comments.
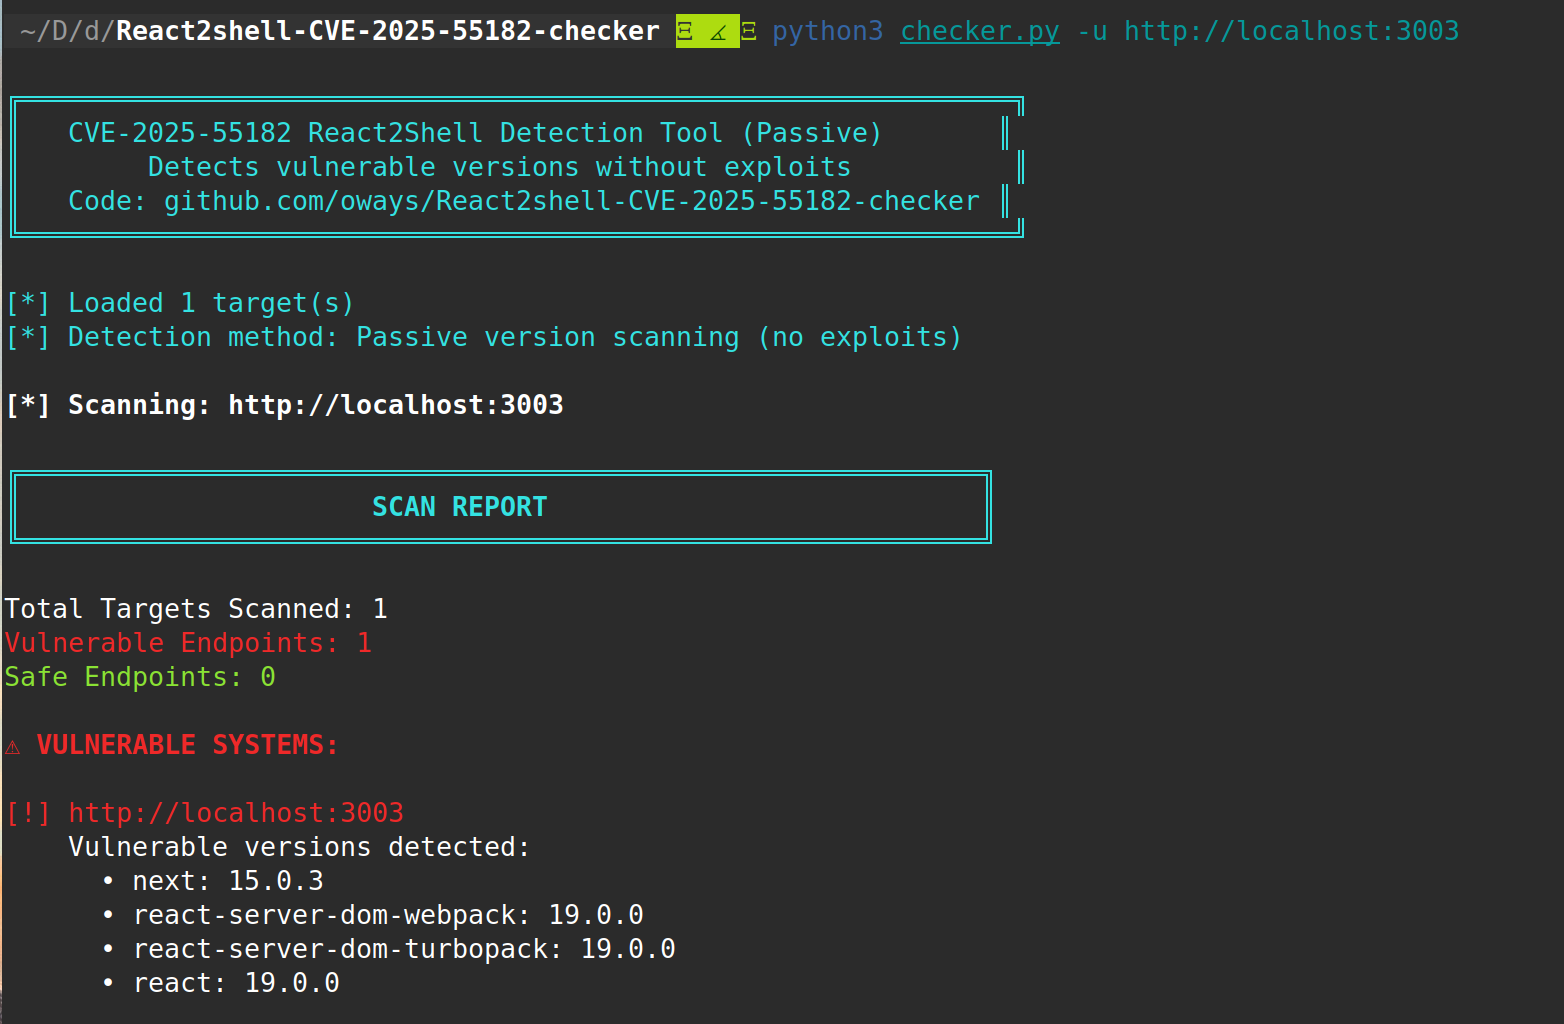 oways/react2shell-cve-2025-55182-checker
Passive CVE-2025-55182 detection tool for vulnerable React Server Components. Scans package.json, JavaScript bundles, HTTP headers, and API endpoints…