

intercept
 xfhg/intercept
INTERCEPT / Policy as Code Auditing
configuration-auditingdevsecopsstatic-analysis
xfhg/interceptINTERCEPT / Policy as Code Auditing
 armourbird/csf
ArmourBird CSF - Container Security Framework
 gojek/cureiam
Clean accounts over permissions in GCP infra at scale
 gensecaihq/react2shell-scanner
Detects CVE-2025-55182 RCE in React Server Components by scanning npm/pnpm/yarn lockfiles, Docker images, SBOMs, and live URLs. Includes auto-fix,…
 dnszlsk/muad-dib
Real-time npm/PyPI supply-chain threat detection. Behavioral chain analysis, AST scanning, IOC feeds, and compound scoring engine.
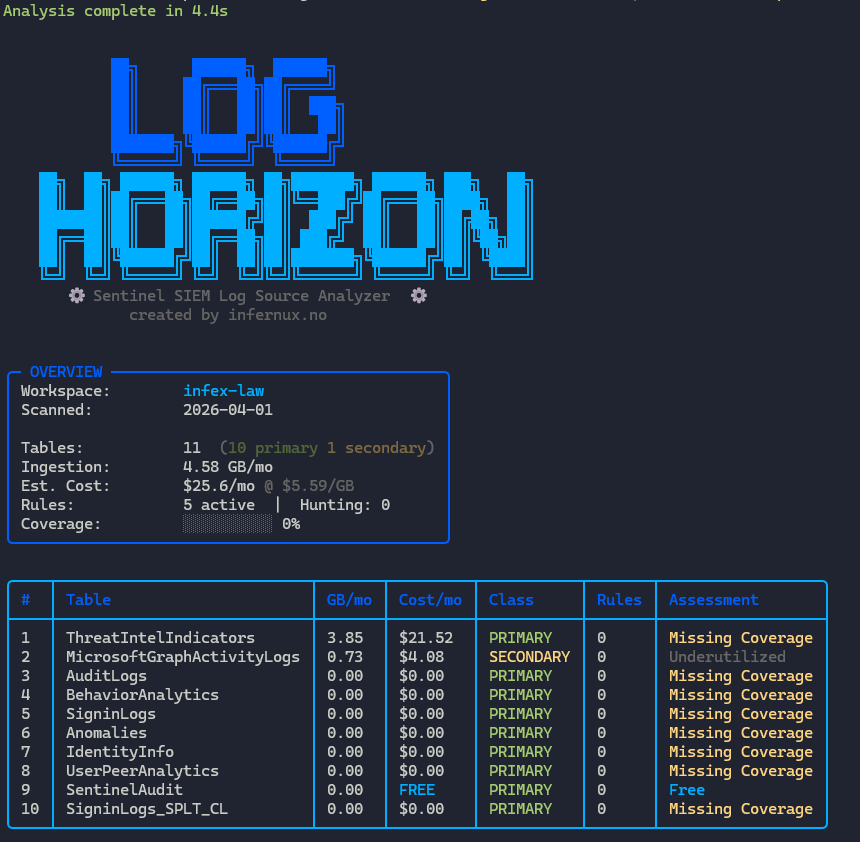 lnfernux/log-horizon
Microsoft Sentinel SIEM Log Source Analyzer
 bugbounty-site/gitsecure
Detect exposed API keys on GitHub commits.
 otsmane-ahmed/ci-supplychain-guard
Static analysis tool that detects malicious dependencies in CI/CD pipelines using pattern matching and AST analysis, with a traffic-light risk…
 ntanwir10/guardscan
100% Free & Open Source • Privacy-First Security Scanning and AI Code Review CLI
 ustayready/outpost
AWS Testing and Reporting Management Tool

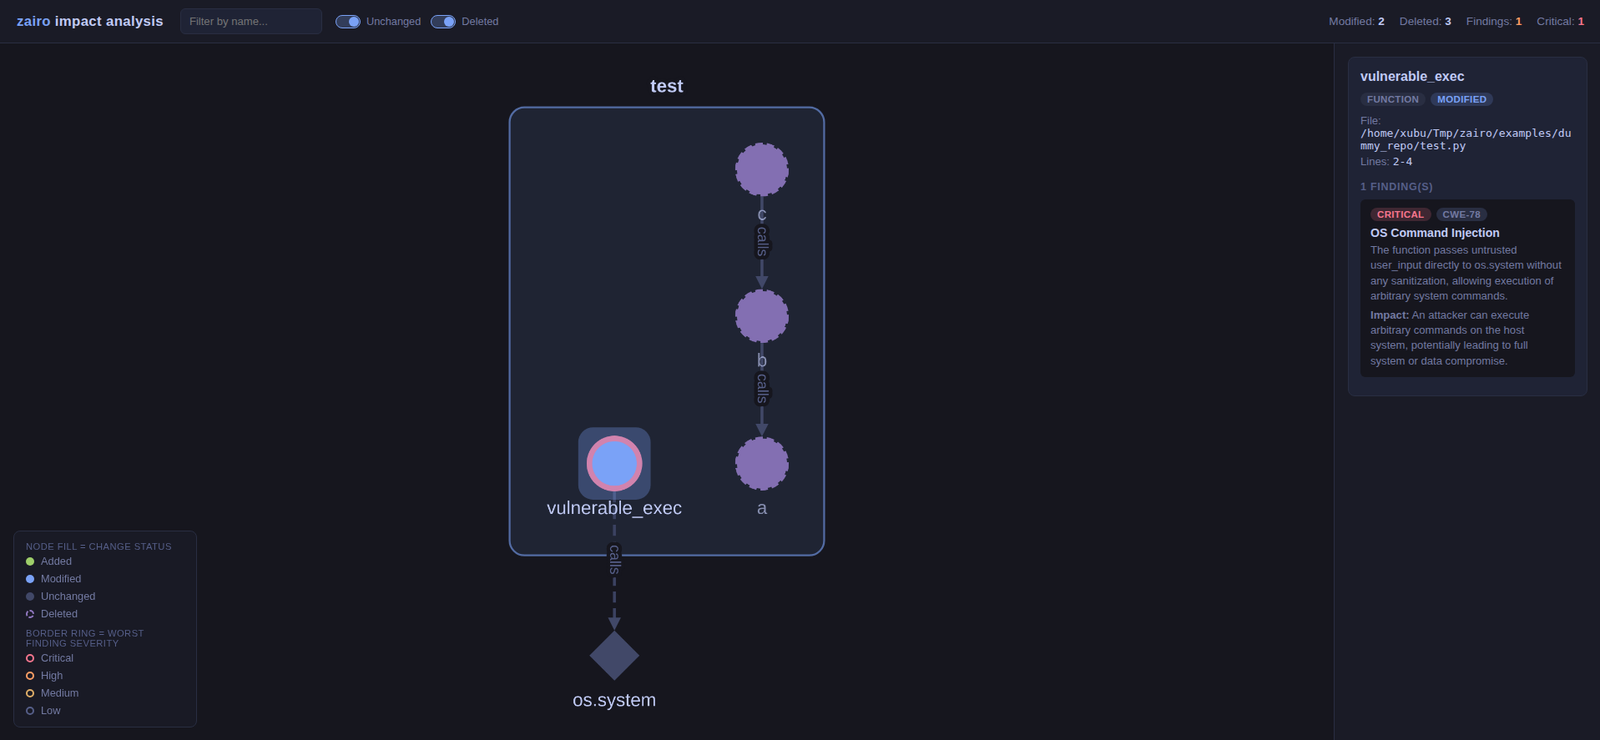 iamavu/zairo
Scans code diffs with context to build an impact graph and uses LLMs to find vulnerabilities, supporting multi-repo scans and CI gating with SARIF…
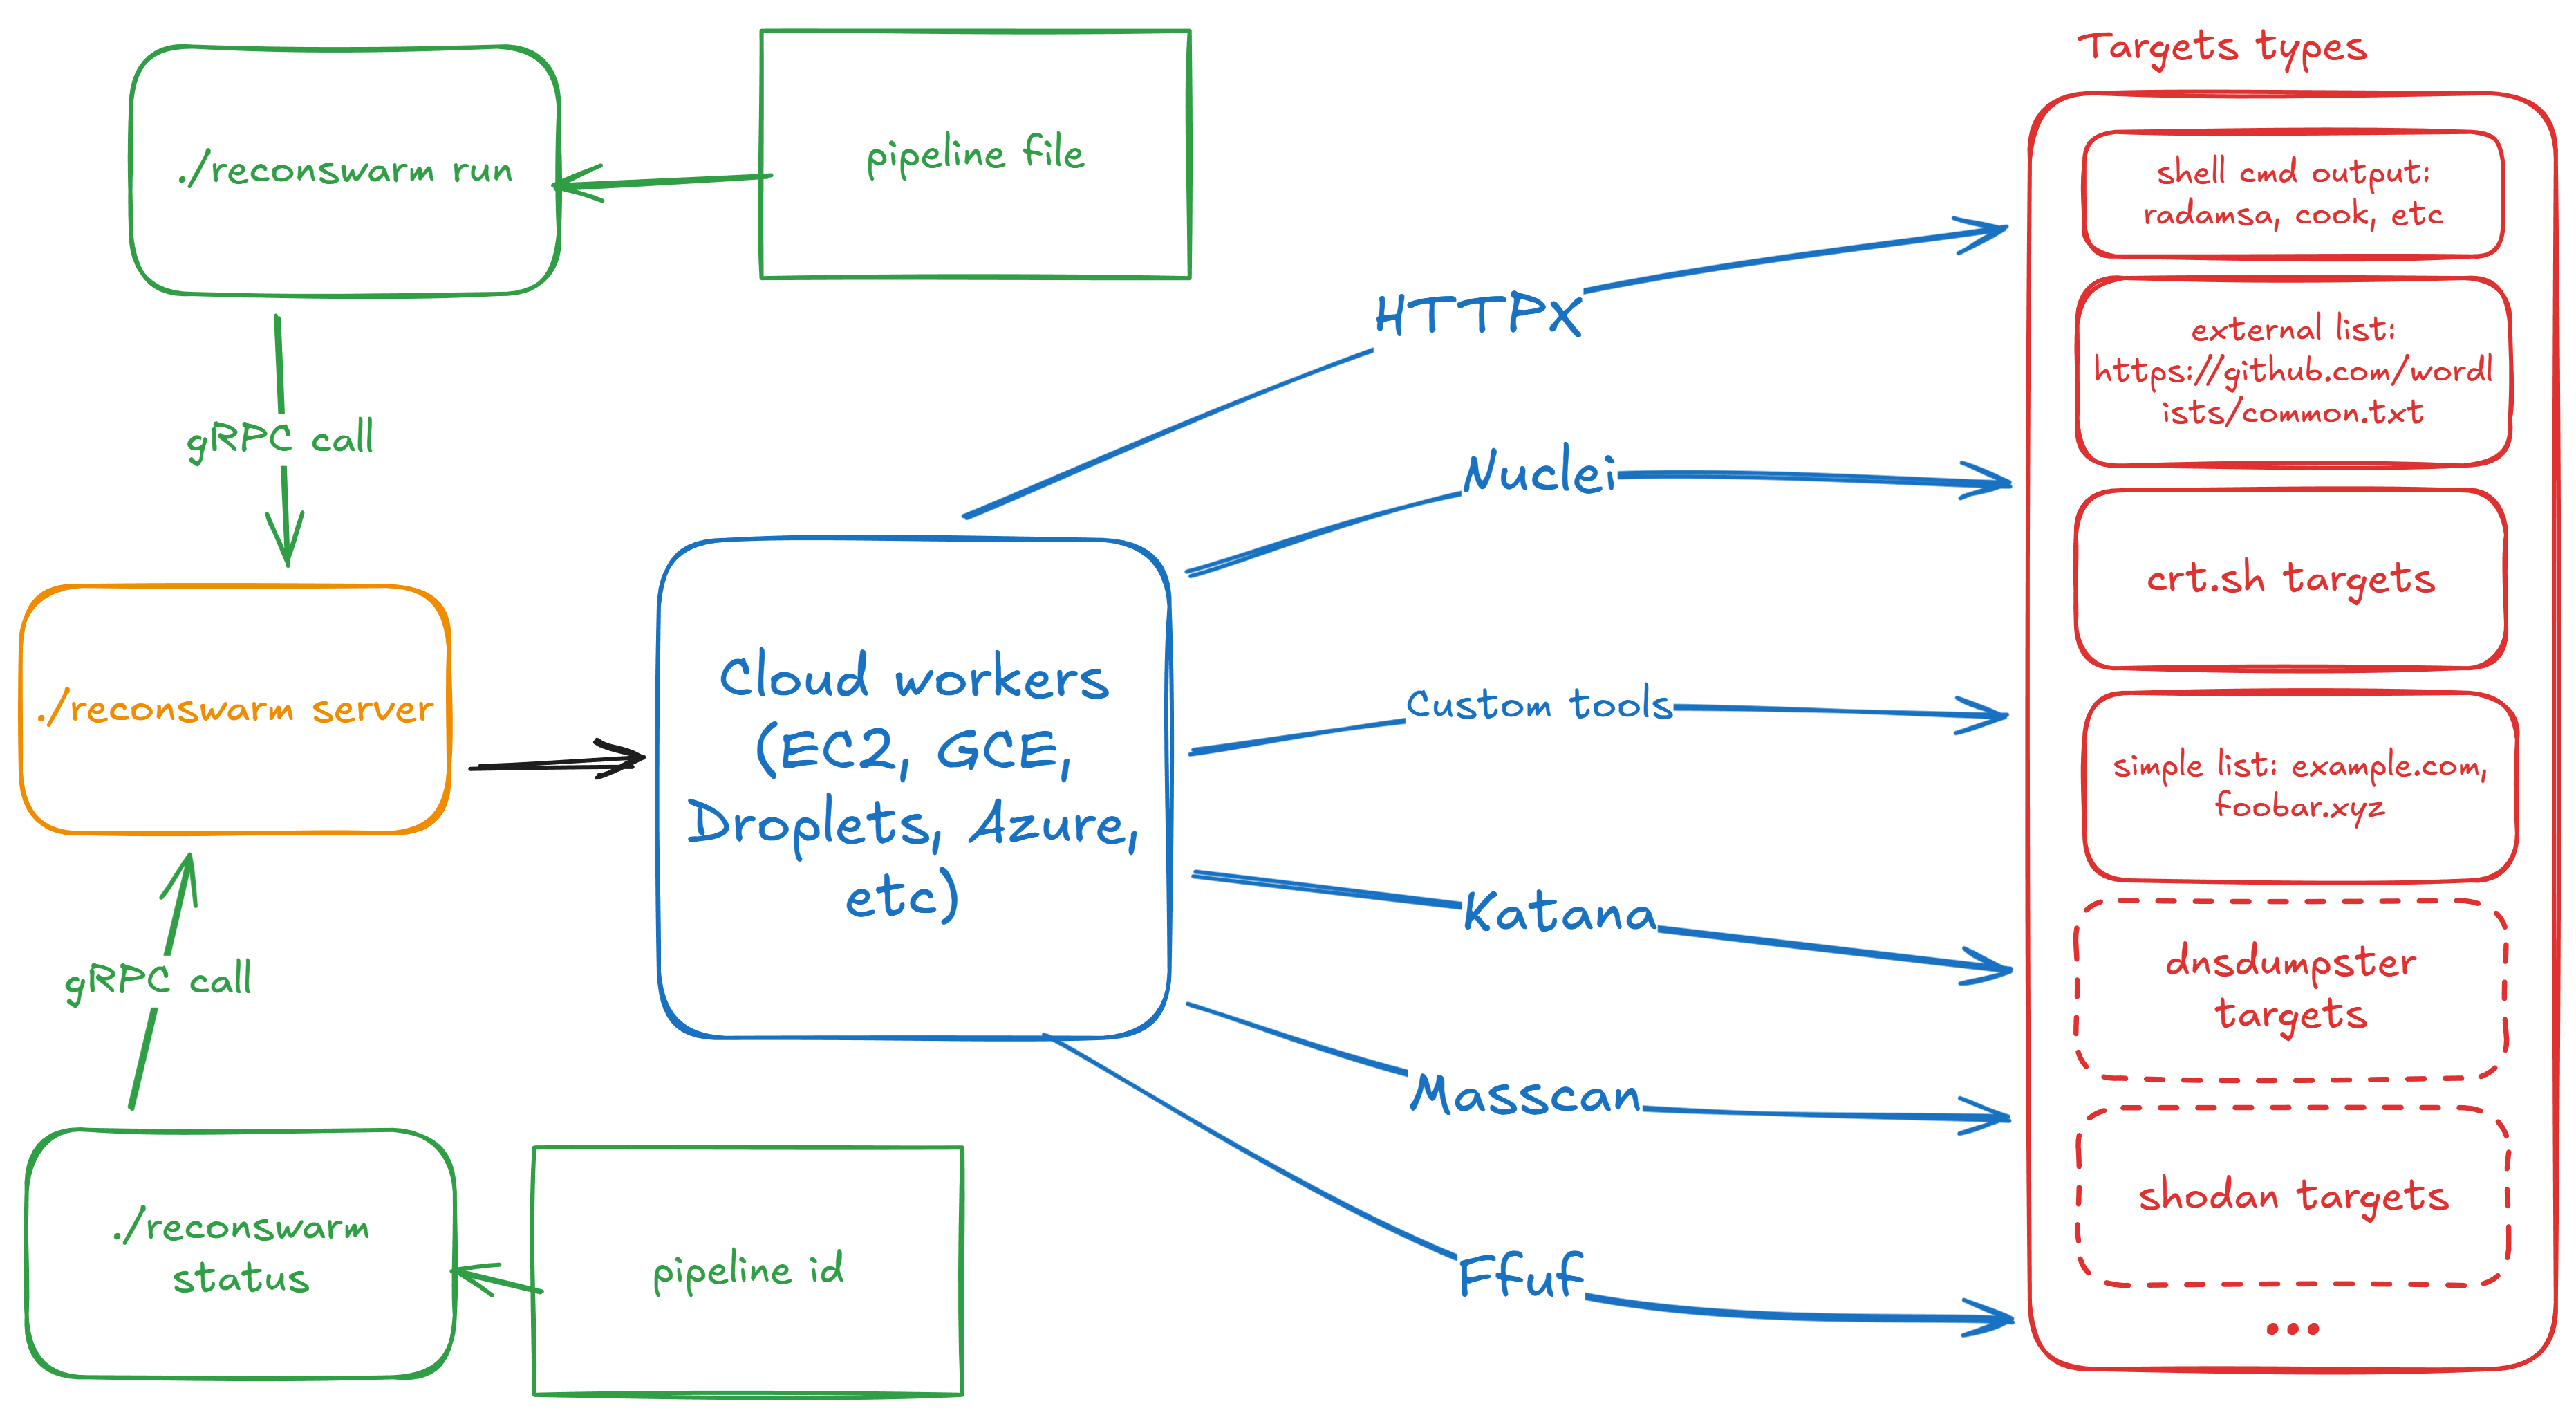 renatus-cartesius/reconswarm
Extend your recon with cloud power
 the-infra-company/kcatcher
Catch what's lurking in your Kafka clusters.
 xiaoqimikko/netty-http2-check
Offline Java tool that scans jars and versions to determine exposure to seven netty-codec-http2 CVEs, recommending the single patched version that…
 xiaoqimikko/netty-http-check
Offline Java tool that scans application jars to determine exposure to 14 Netty codec-http CVEs, identifying the exact patched version…
 derekpreston81/cve_adc_ioc_2026
Citrix NetScaler CVE Preconditions Checker as per CTX696604 | Supported CVE : CVE-2026-8451, CVE-2026-8452, CVE-2026-8655, CVE-2026-10816,…
 reverseclabs/azuredevops-enum
Read-only Azure DevOps enumeration tool that queries the REST API to surface projects, repositories, service connections, builds, pipeline secrets,…