
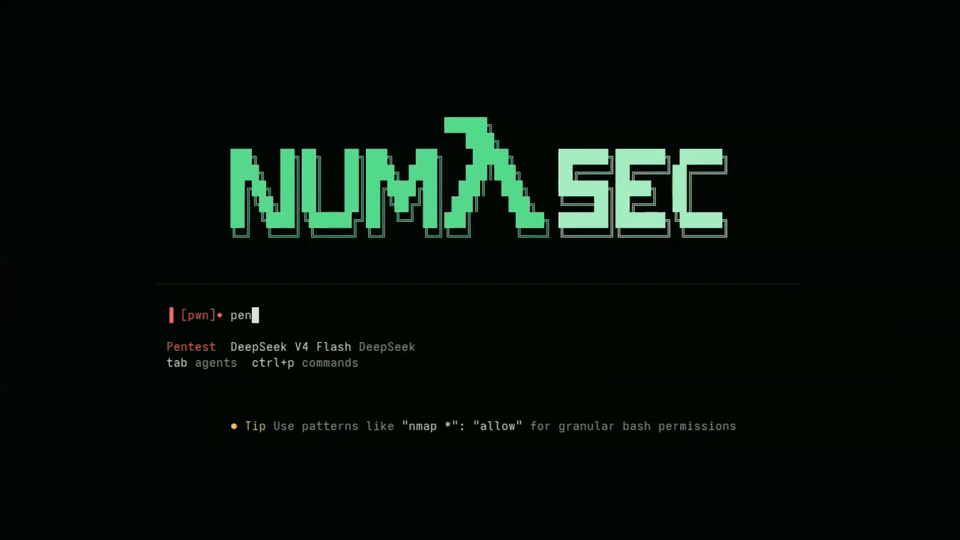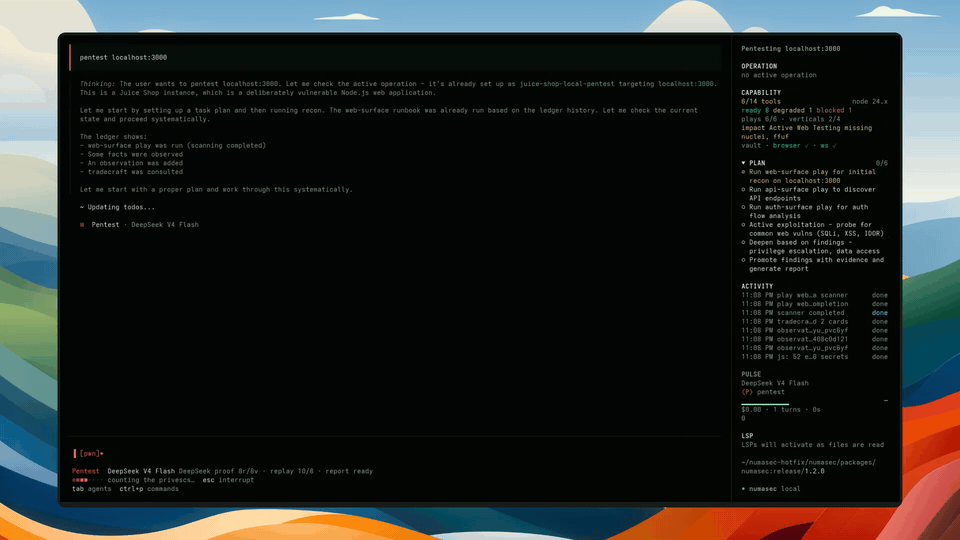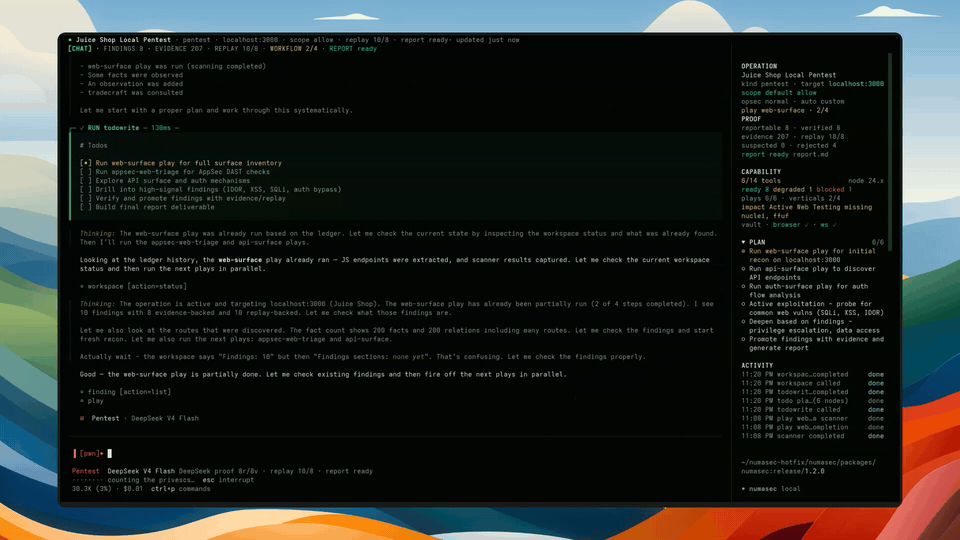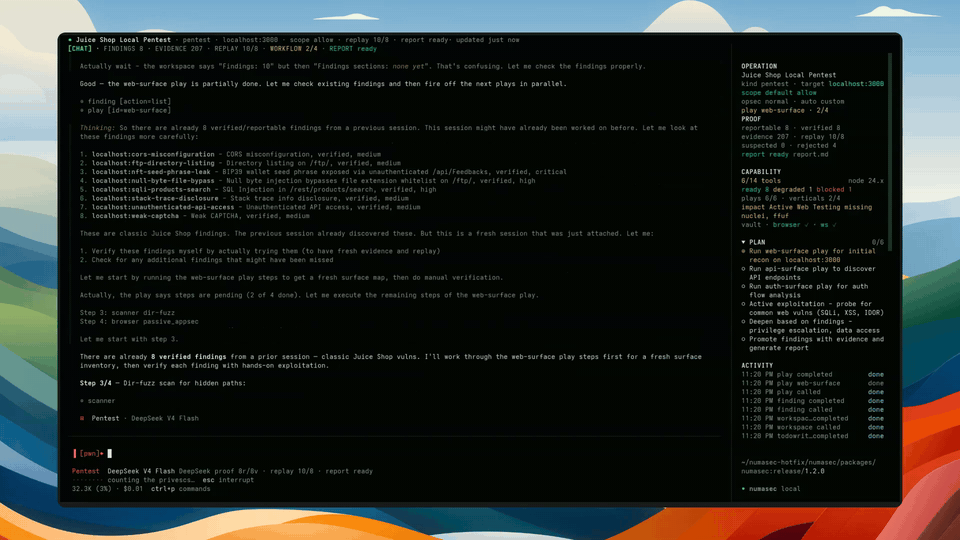
numasec
 francescostabile/numasec
AI security agent that runs in your terminal, orchestrating local tools, runbooks, and agents for authorized AppSec, pentest, OSINT, and CTF…
ai-securityctfdevsecops+7
781
francescostabile/numasecAI security agent that runs in your terminal, orchestrating local tools, runbooks, and agents for authorized AppSec, pentest, OSINT, and CTF…
 noveogroup/android-check
Static code analysis plugin for Android project. (Checkstyle, PMD)
 sshwarts/skillscript
Skillscript — a small declarative language for authoring agent workflows. Runtime, compiler, and CLI.
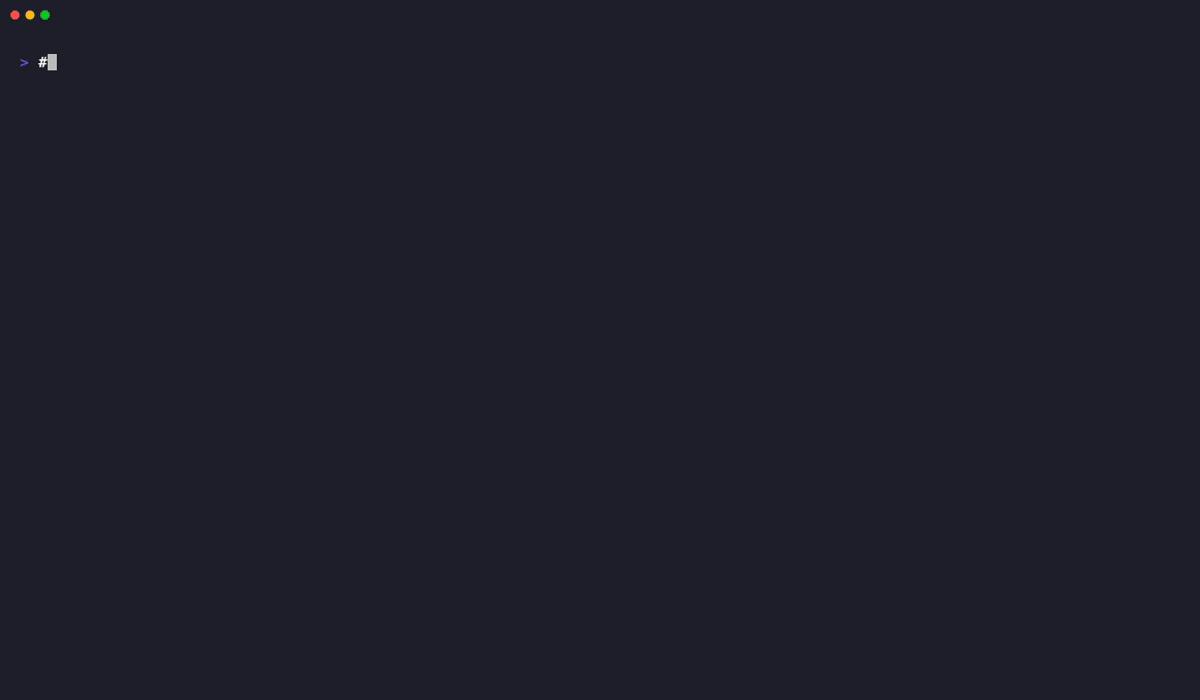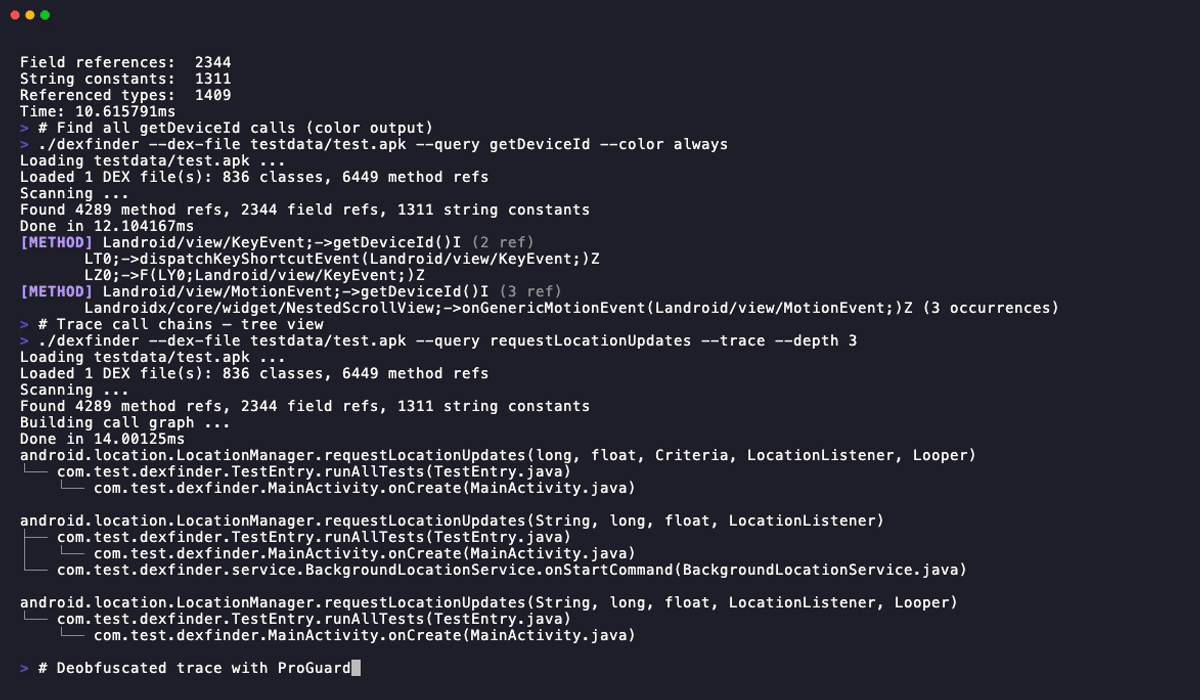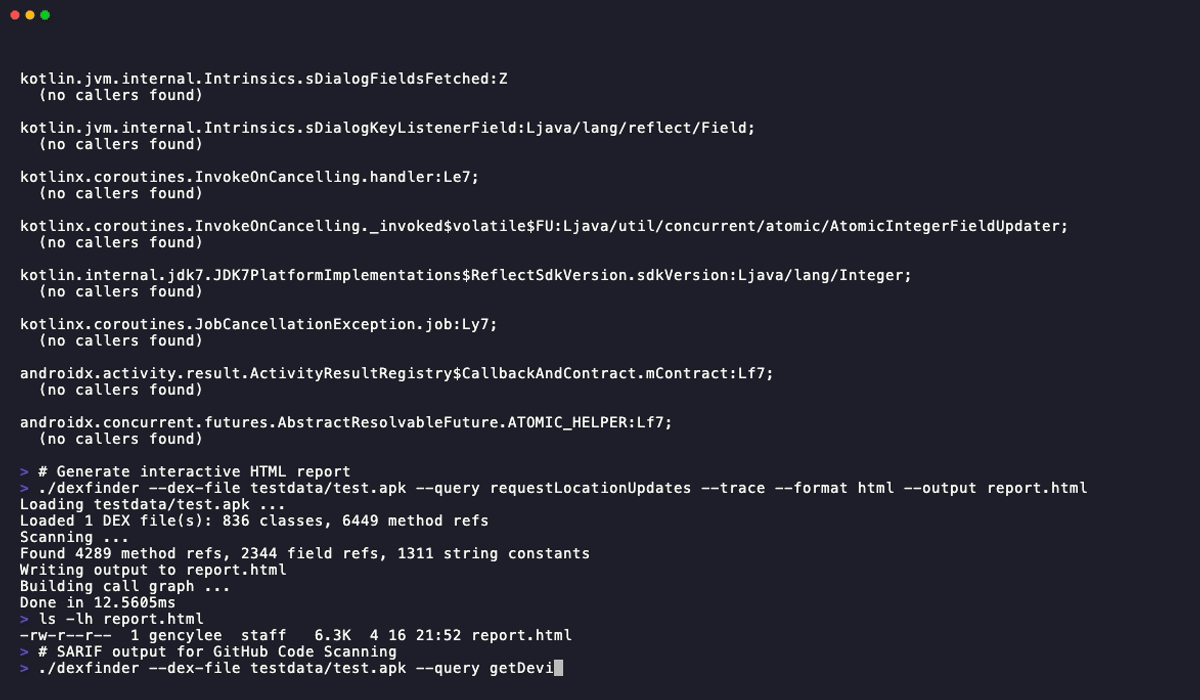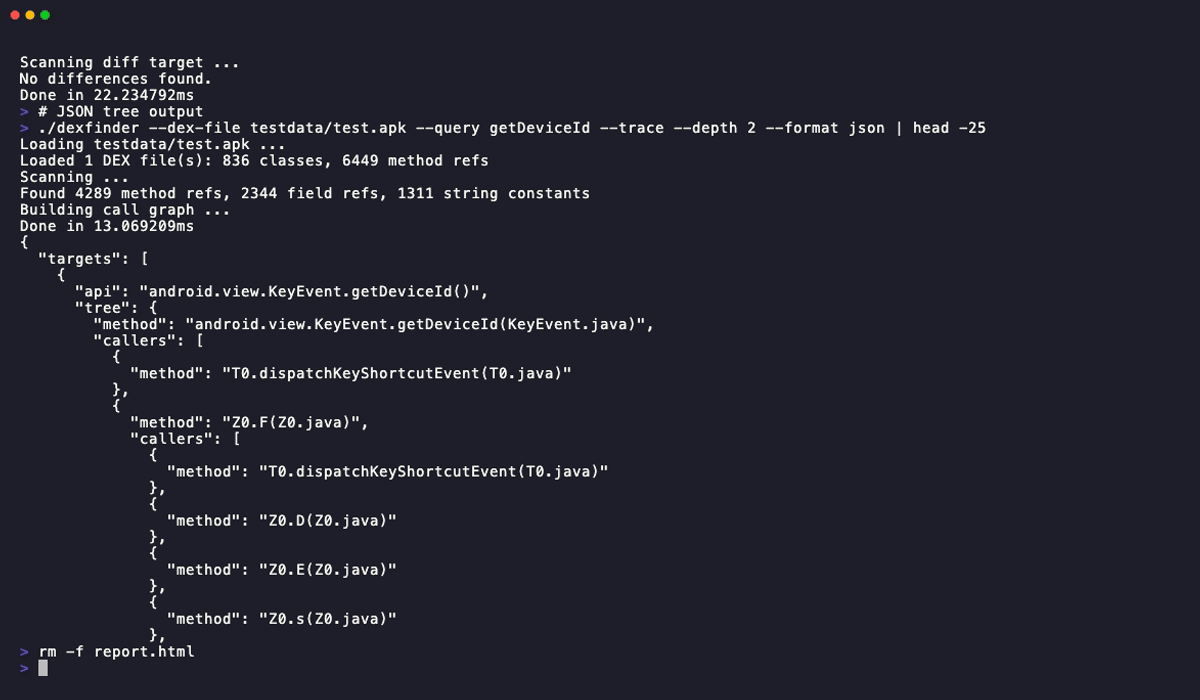 junelegency/dexfinder
Cross-platform APK/DEX method finder with call chain tracing, ProGuard deobfuscation, and hidden API detection
 danielbohannon/devsec-defense
Accompanying PowerShell Modules for DevSec Defense Presentation
 brennhill/sloppy-joe
Shields against supply-chain, slopsquatting, and typosquatting attacks from dependencies and code.
 afine-com/glassworm-hunter
Detects GlassWorm supply chain attack payloads by scanning VS Code extensions, npm/PyPI packages, and git repos for invisible Unicode payloads,…
 taptap/cve-2025-59489
Automated scanner that detects Unity runtime injection vulnerability CVE-2025-59489 in Android APKs by extracting Unity version and checking against…
 moshe-ship/bidi-guard
Scan code for invisible bidirectional Unicode characters (Trojan Source attack prevention, CVE-2021-42574)
 abdozkaya/rsc-security-auditor
🛡️ Audit your Next.js & React Server Components stack for critical vulnerabilities (CVE-2025-66478, CVE-2025-55184). Detects risks & generates fix…
 george0papasotiriou/cve-2026-11120-command-injection-via-git-url-in-ci-cd-pipeline
Demonstrates command injection via unsanitized Git URLs in CI/CD pipelines, including a vulnerable build script and exploit example for a critical…
 bfurkanyildiz/android-rce-analizi
Android CVE-2024-0044, 43093, 23706 zafiyet analizi ve PoC lab ortamı
 super-vulnerable-org/compromised-action
Test repo: simulates CVE-2025-30066 style compromised GitHub Action (for security research/testing chainradar)
 dannyendortest/node-vulnerable
Synthetic demo target for EXPOSURE — CVE-2018-21268 (traceroute) + CVE-2018-3757 (pdf-image)
 aaronm-sysdig/log4j-vuln-demo
Intentionally vulnerable Log4j 2.14.1 demo for Sysdig CNAPP scanning (CVE-2021-44228)
 owasp/teach-appsec
OWASP teaching modules covering application security fundamentals including risk management, secure software development, and operations security for…
 bhimsekhar/vulnerable-java-app
Spring Boot app with log4j 2.14.1 (CVE-2021-44228) — VulnFix agent test target
 dannyendortest/ollama
Synthetic demo target for Endor Labs EXPOSURE, tracking CVE-2024-12886 with a deliberately vulnerable dependency and a one-click PR-based fix…