
log4shell
 hozyx/log4shell
Applications that are vulnerable to the log4j CVE-2021-44228/45046 issue may be detectable by scanning jar, war, ear, zip files to search for the…
code-analysisdevsecopsstatic-analysis+3
hozyx/log4shellApplications that are vulnerable to the log4j CVE-2021-44228/45046 issue may be detectable by scanning jar, war, ear, zip files to search for the…
 konstantin-kelemen/mysqld_safe-cve-2016-6662-patch
Ansible playbook that applies the Percona patch for CVE-2016-6662 to the mysqld_safe file on CentOS and FreeBSD systems.
 hpcprofessional/remediate_cesa_2019_2091
Remediation task for CVE-2018-15686, CVE-2018-16866, and CVE-2018-16888 affecting SystemD in EL7
 cybervixy/vulnerability-management
NGINX Security Hardening & Vulnerability Remediation Analysis of critical CVEs (CVE-2021-23017, HTTP/2 DoS flaws) in outdated NGINX versions, with…
 simplifi-ed/cve-2024-3094-patcher
Ansible playbook for patching CVE-2024-3094
 f88/ghostbusters15
Playbooks 'Fix for CVE-2015-0235(GHOST)' running on Ansible
 vkaushik-chef/regresshion
Chef Inspec profile for checking regreSSHion vulnerability CVE-2024-6387
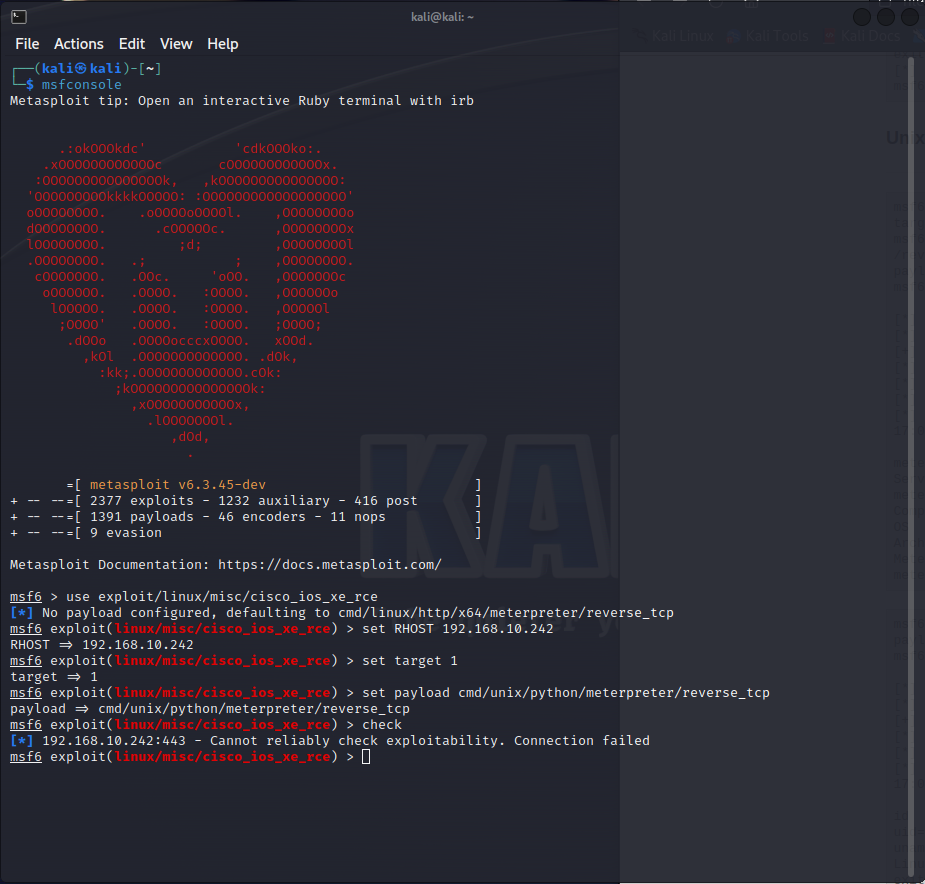 netbell/cve-2023-20198-fix
Check for and remediate conditions that make an IOS-XE device vulnerable to CVE-2023-20198
 malindarathnayake/intel-cve-2018-3639-mitigation_registryupdate
PowerShell script to apply Windows registry mitigation for CVE-2018-3639 (Speculative Store Bypass), enabling automated security hardening against…
 zenzue/cve-2024-6387-mitigation
Mitigation Guide for CVE-2024-6387 in OpenSSH
 sondermc/git-cveissues
vulnerabilities, CVE-2022-41903, and CVE-2022-23521, that affect versions 2.39 and older. Git for Windows was also patched to address an additional,…
 shoucheng3/ff4j__ff4j_cve-2022-44262_1-8-13
Feature toggle framework for Java enabling runtime feature activation, role-based access, AOP-driven toggling, monitoring, audit trails, and a web…
 githubfoam/nxlog-ubuntu-githubactions
CI pipeline for building nxlog-ce on Ubuntu with CVE-2020-35488 vulnerability detection, enabling automated log collection and security auditing in…
 clickswave/limeyard
Deliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 runewardd/runeward
Governed execution cells for AI agents.
 philippeabraxas-jpg/responsible-alliance-protocol
Safety cannot be a prompt instruction. TBP provides an external execution-layer boundary for autonomous agents, enforcing hard F/I/W invariants via…
 rauc/rauc-1.5-integration
integration examples for the CVE-2020-25860 fix