
ThreatMapper
 deepfence/threatmapper
Open Source Cloud Native Application Protection Platform (CNAPP)
cloud-securityconfiguration-auditingcontainer-security+4
5.3k
deepfence/threatmapperOpen Source Cloud Native Application Protection Platform (CNAPP)
 nozaq/terraform-aws-secure-baseline
Terraform module to set up your AWS account with the secure baseline configuration based on CIS Amazon Web Services Foundations and AWS Foundational…
 mebibite/log4jhound
Created after the disclosure of CVE-2021-44228. Bash script that detects Log4j occurrences in your projects and systems, allowing you to get insight…
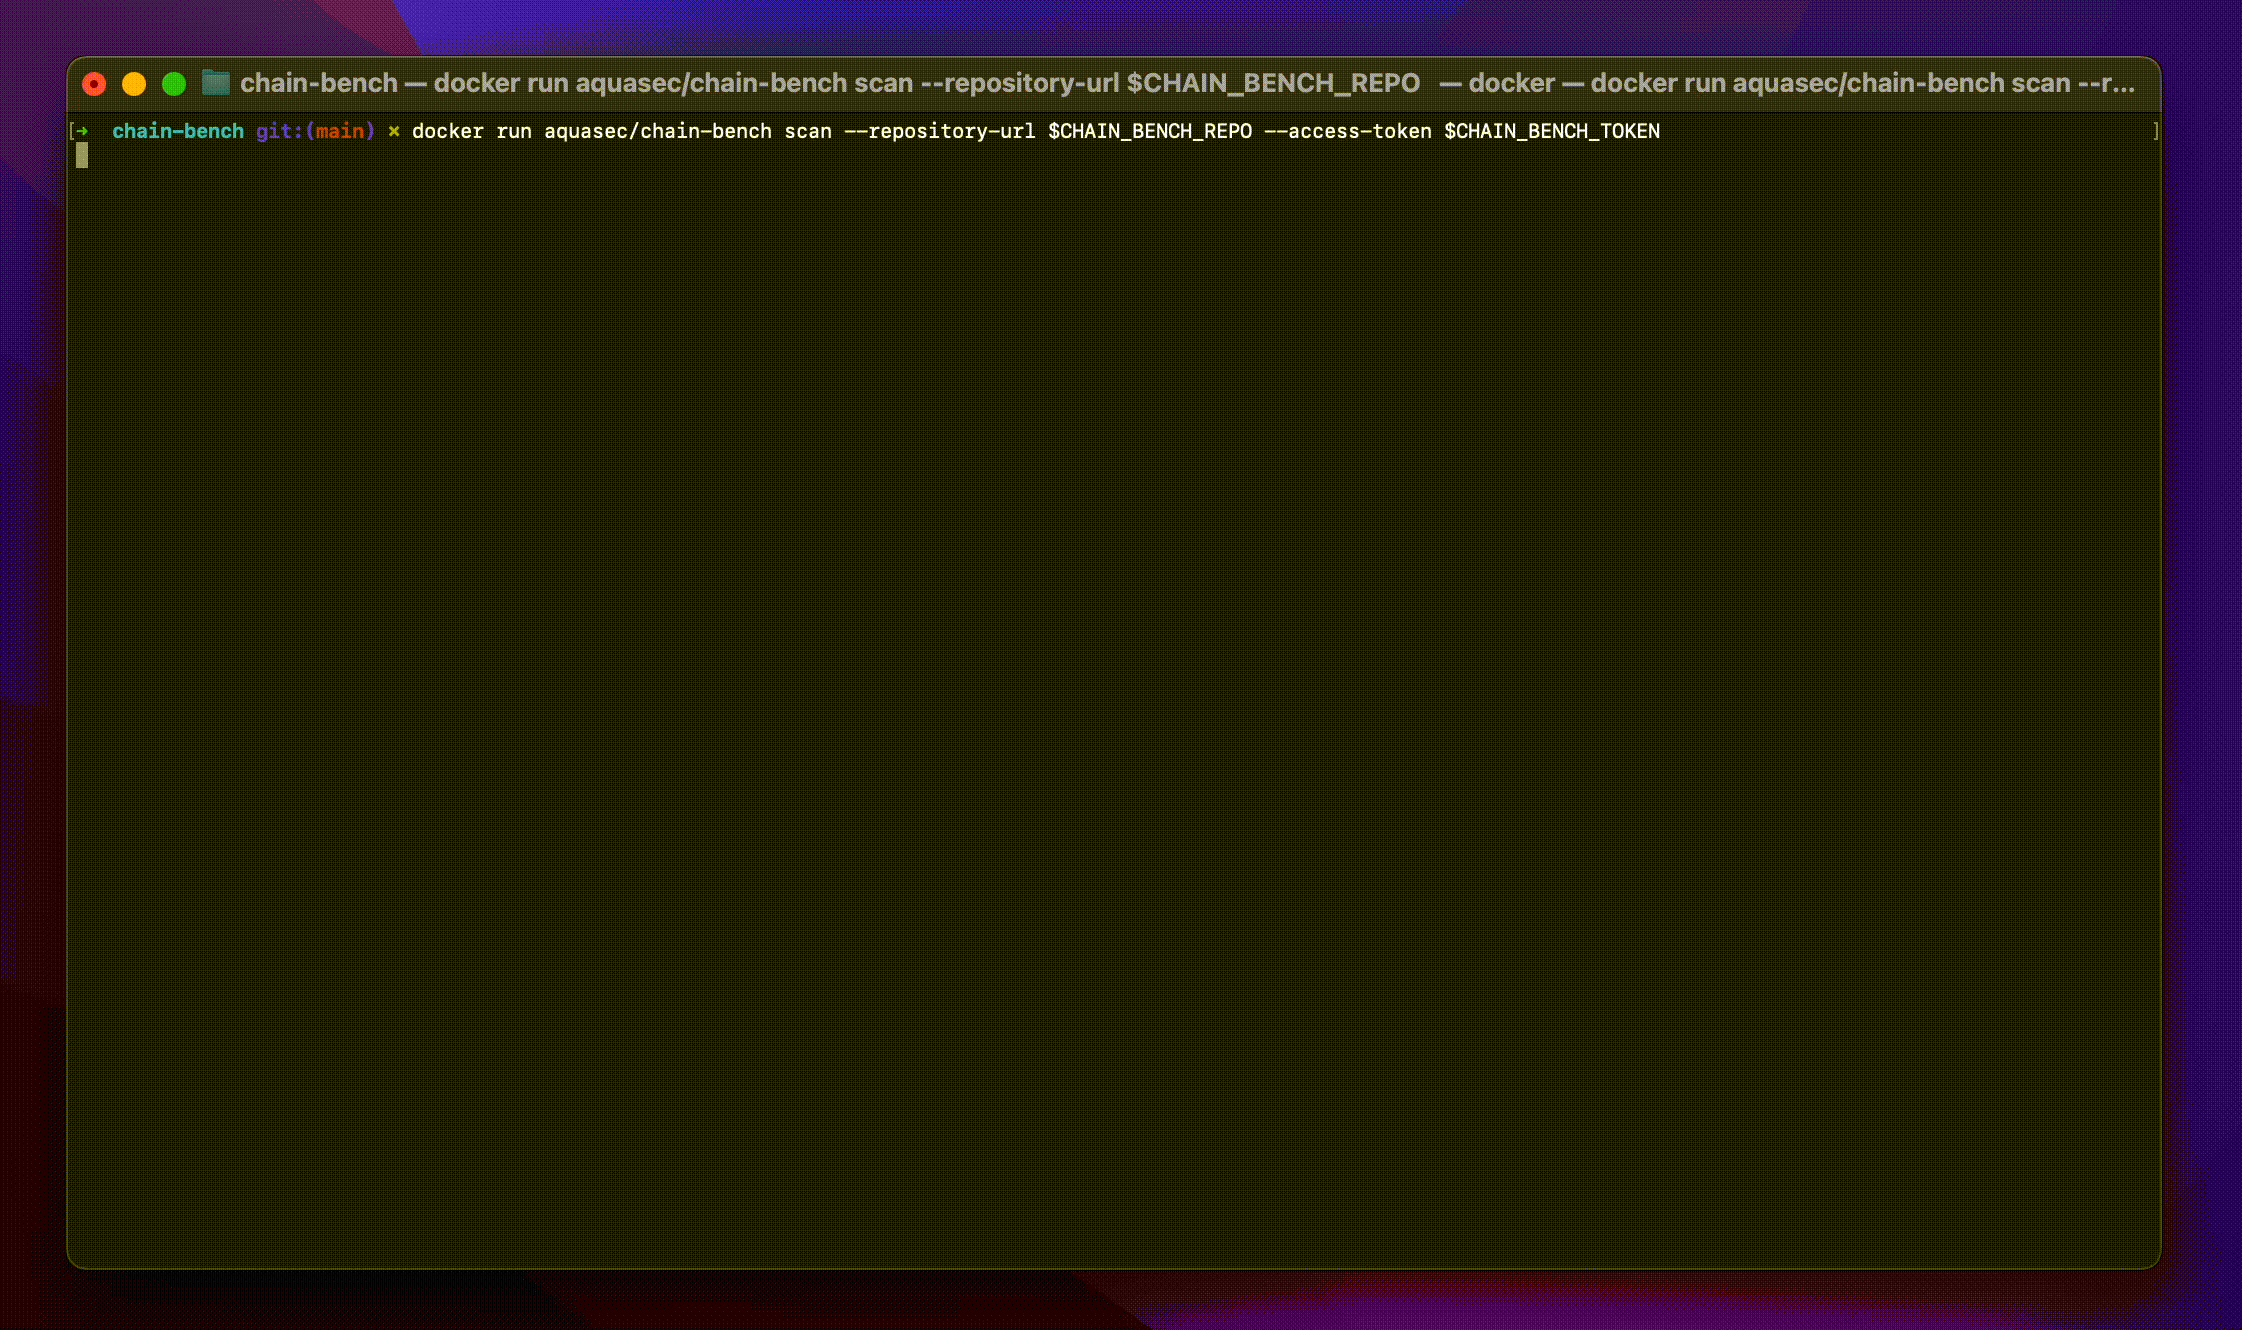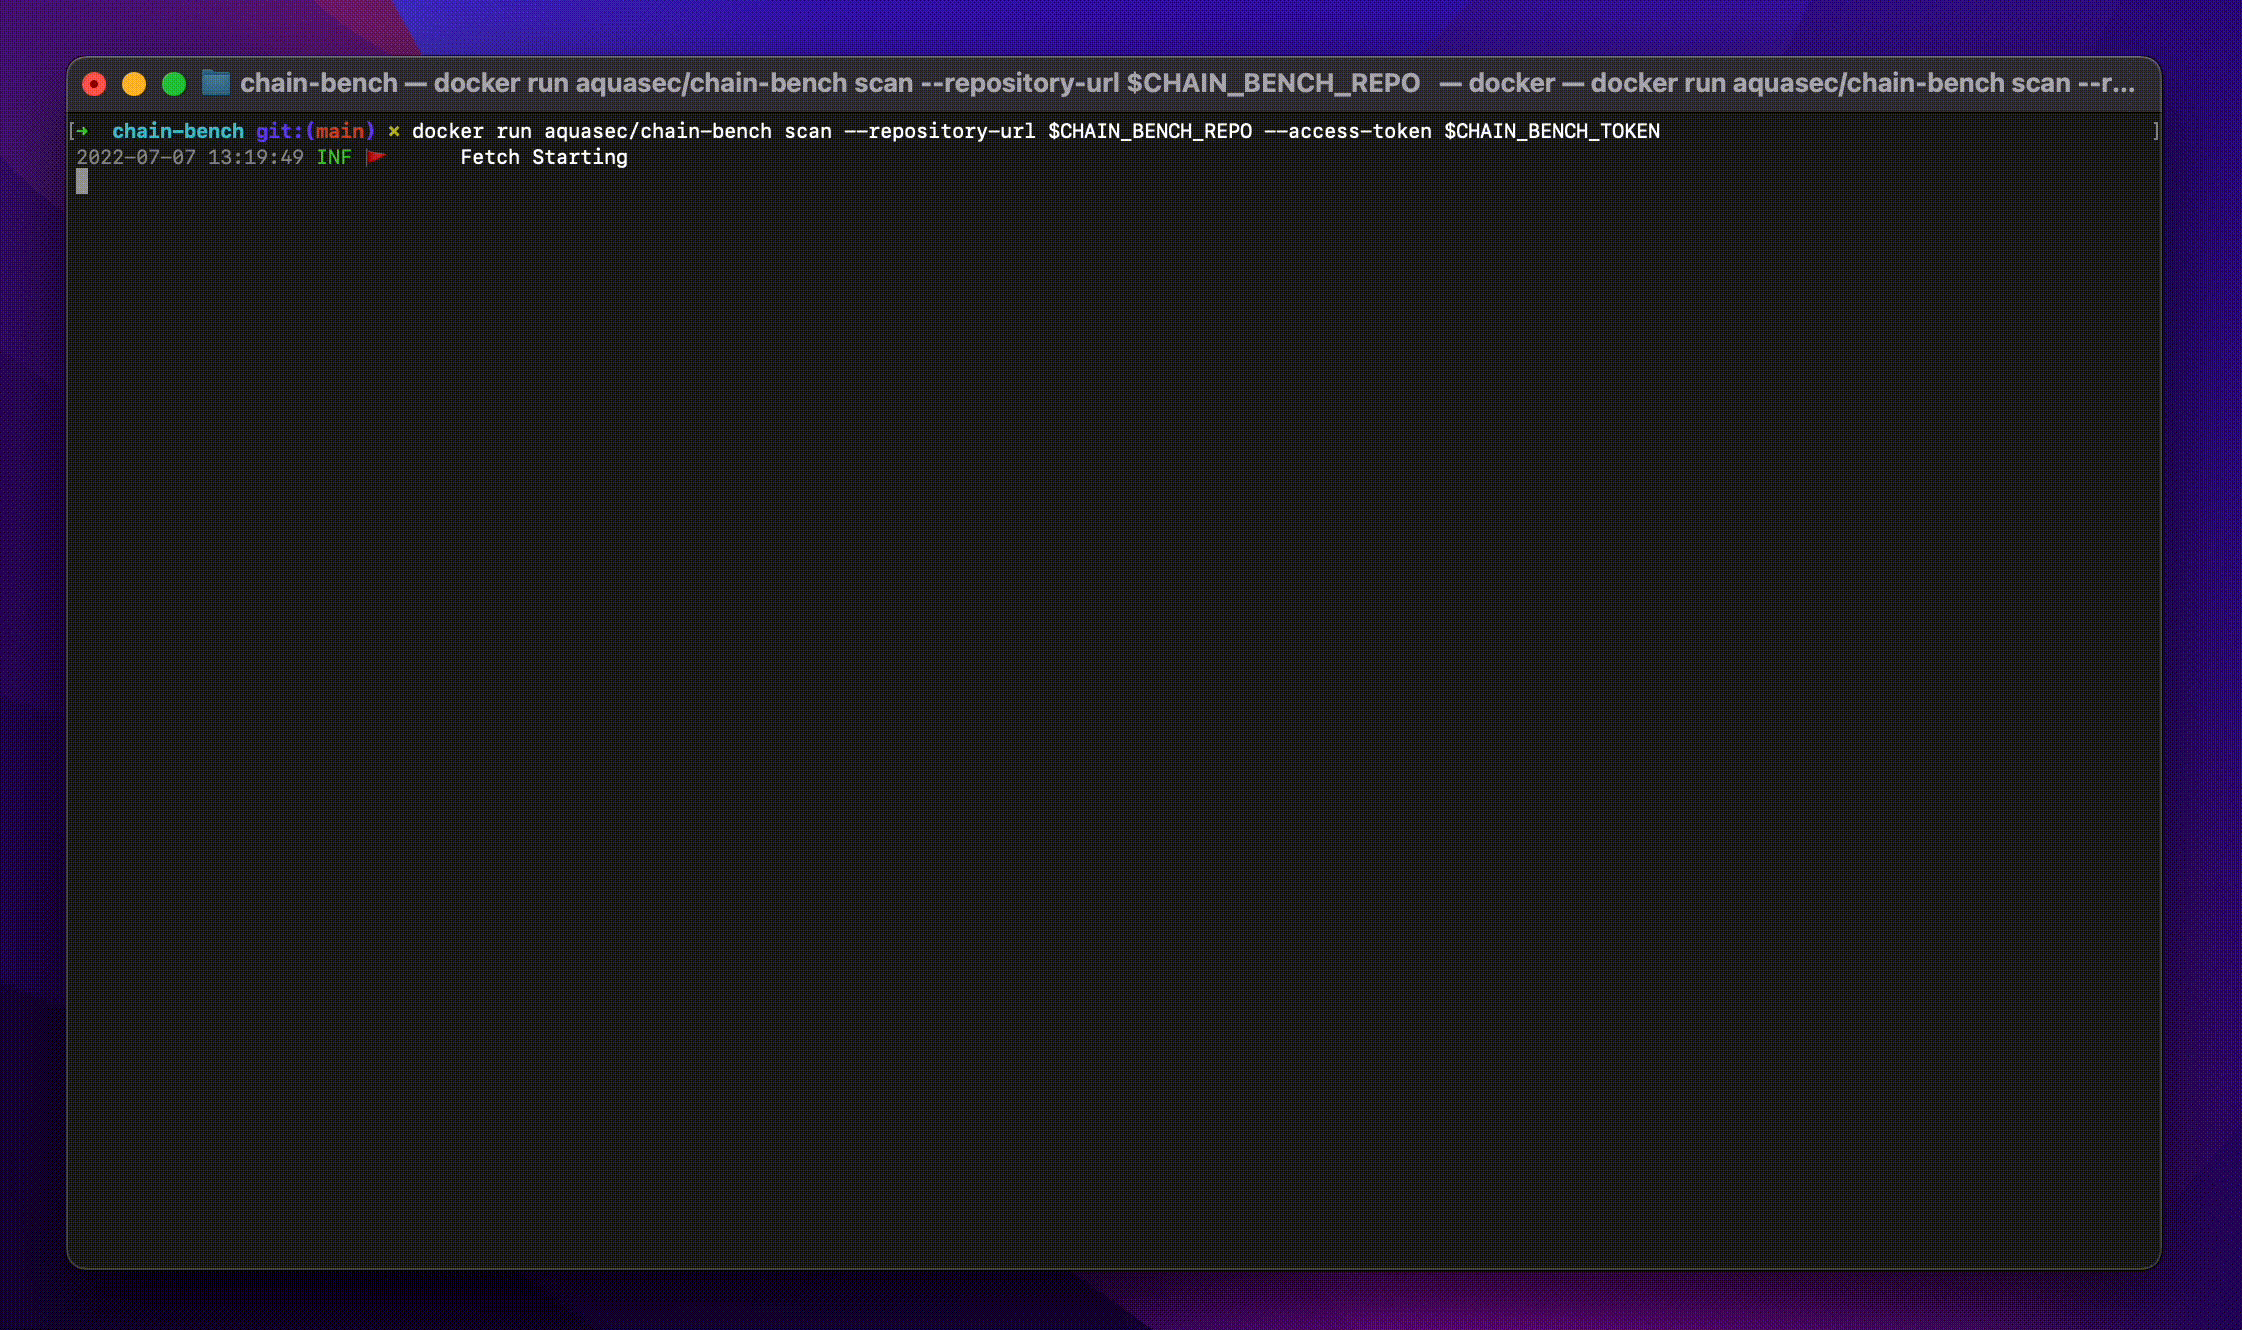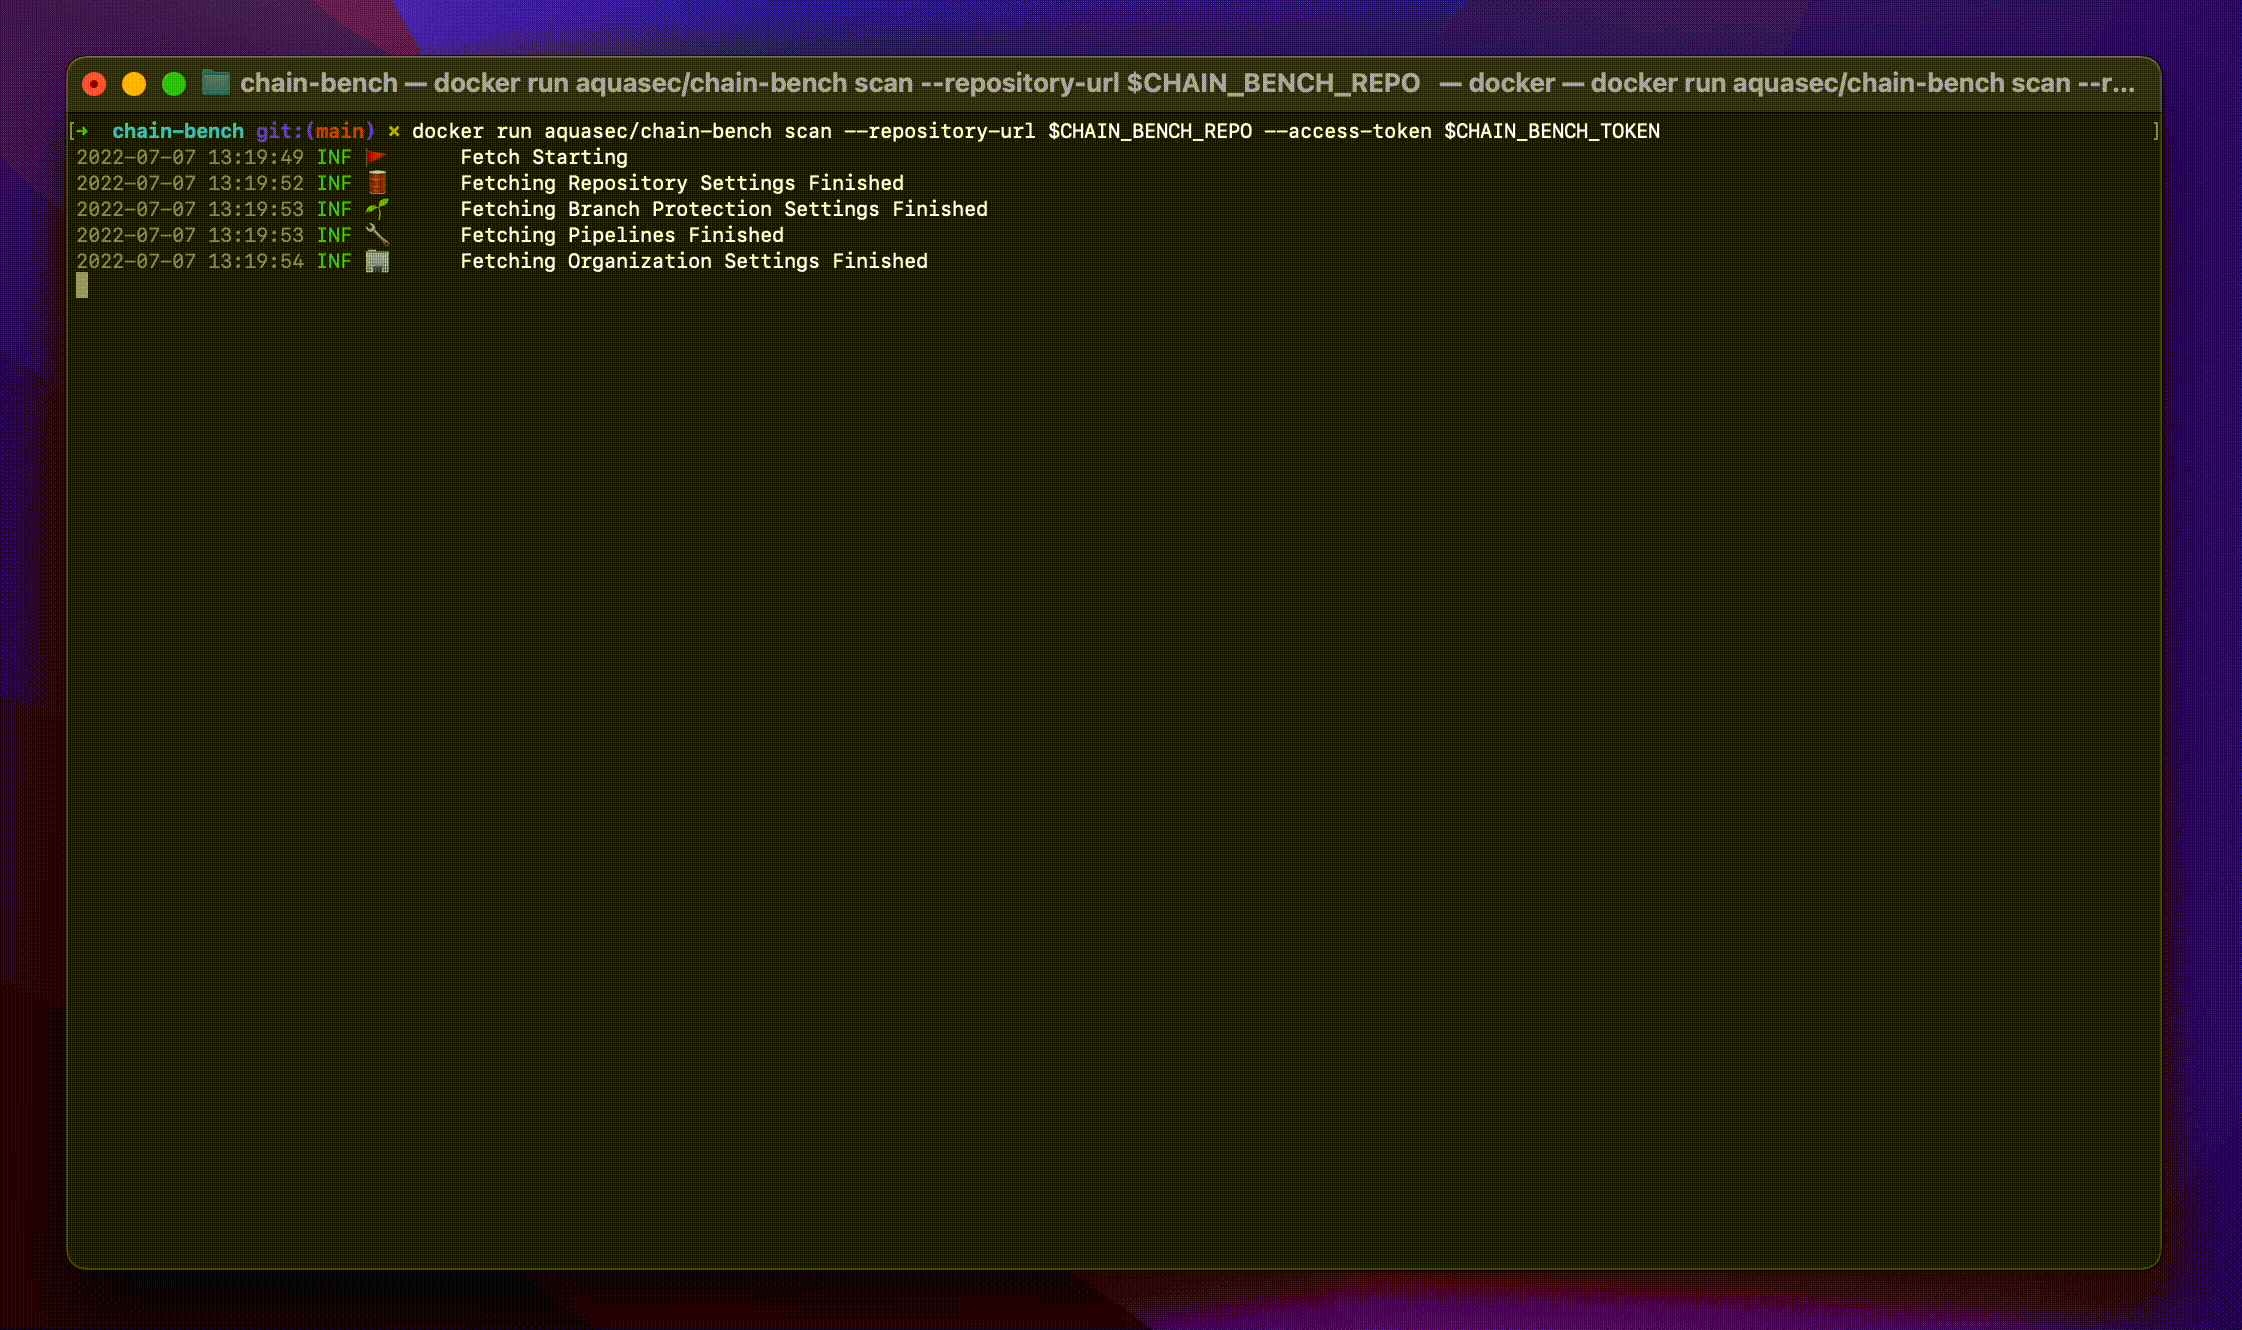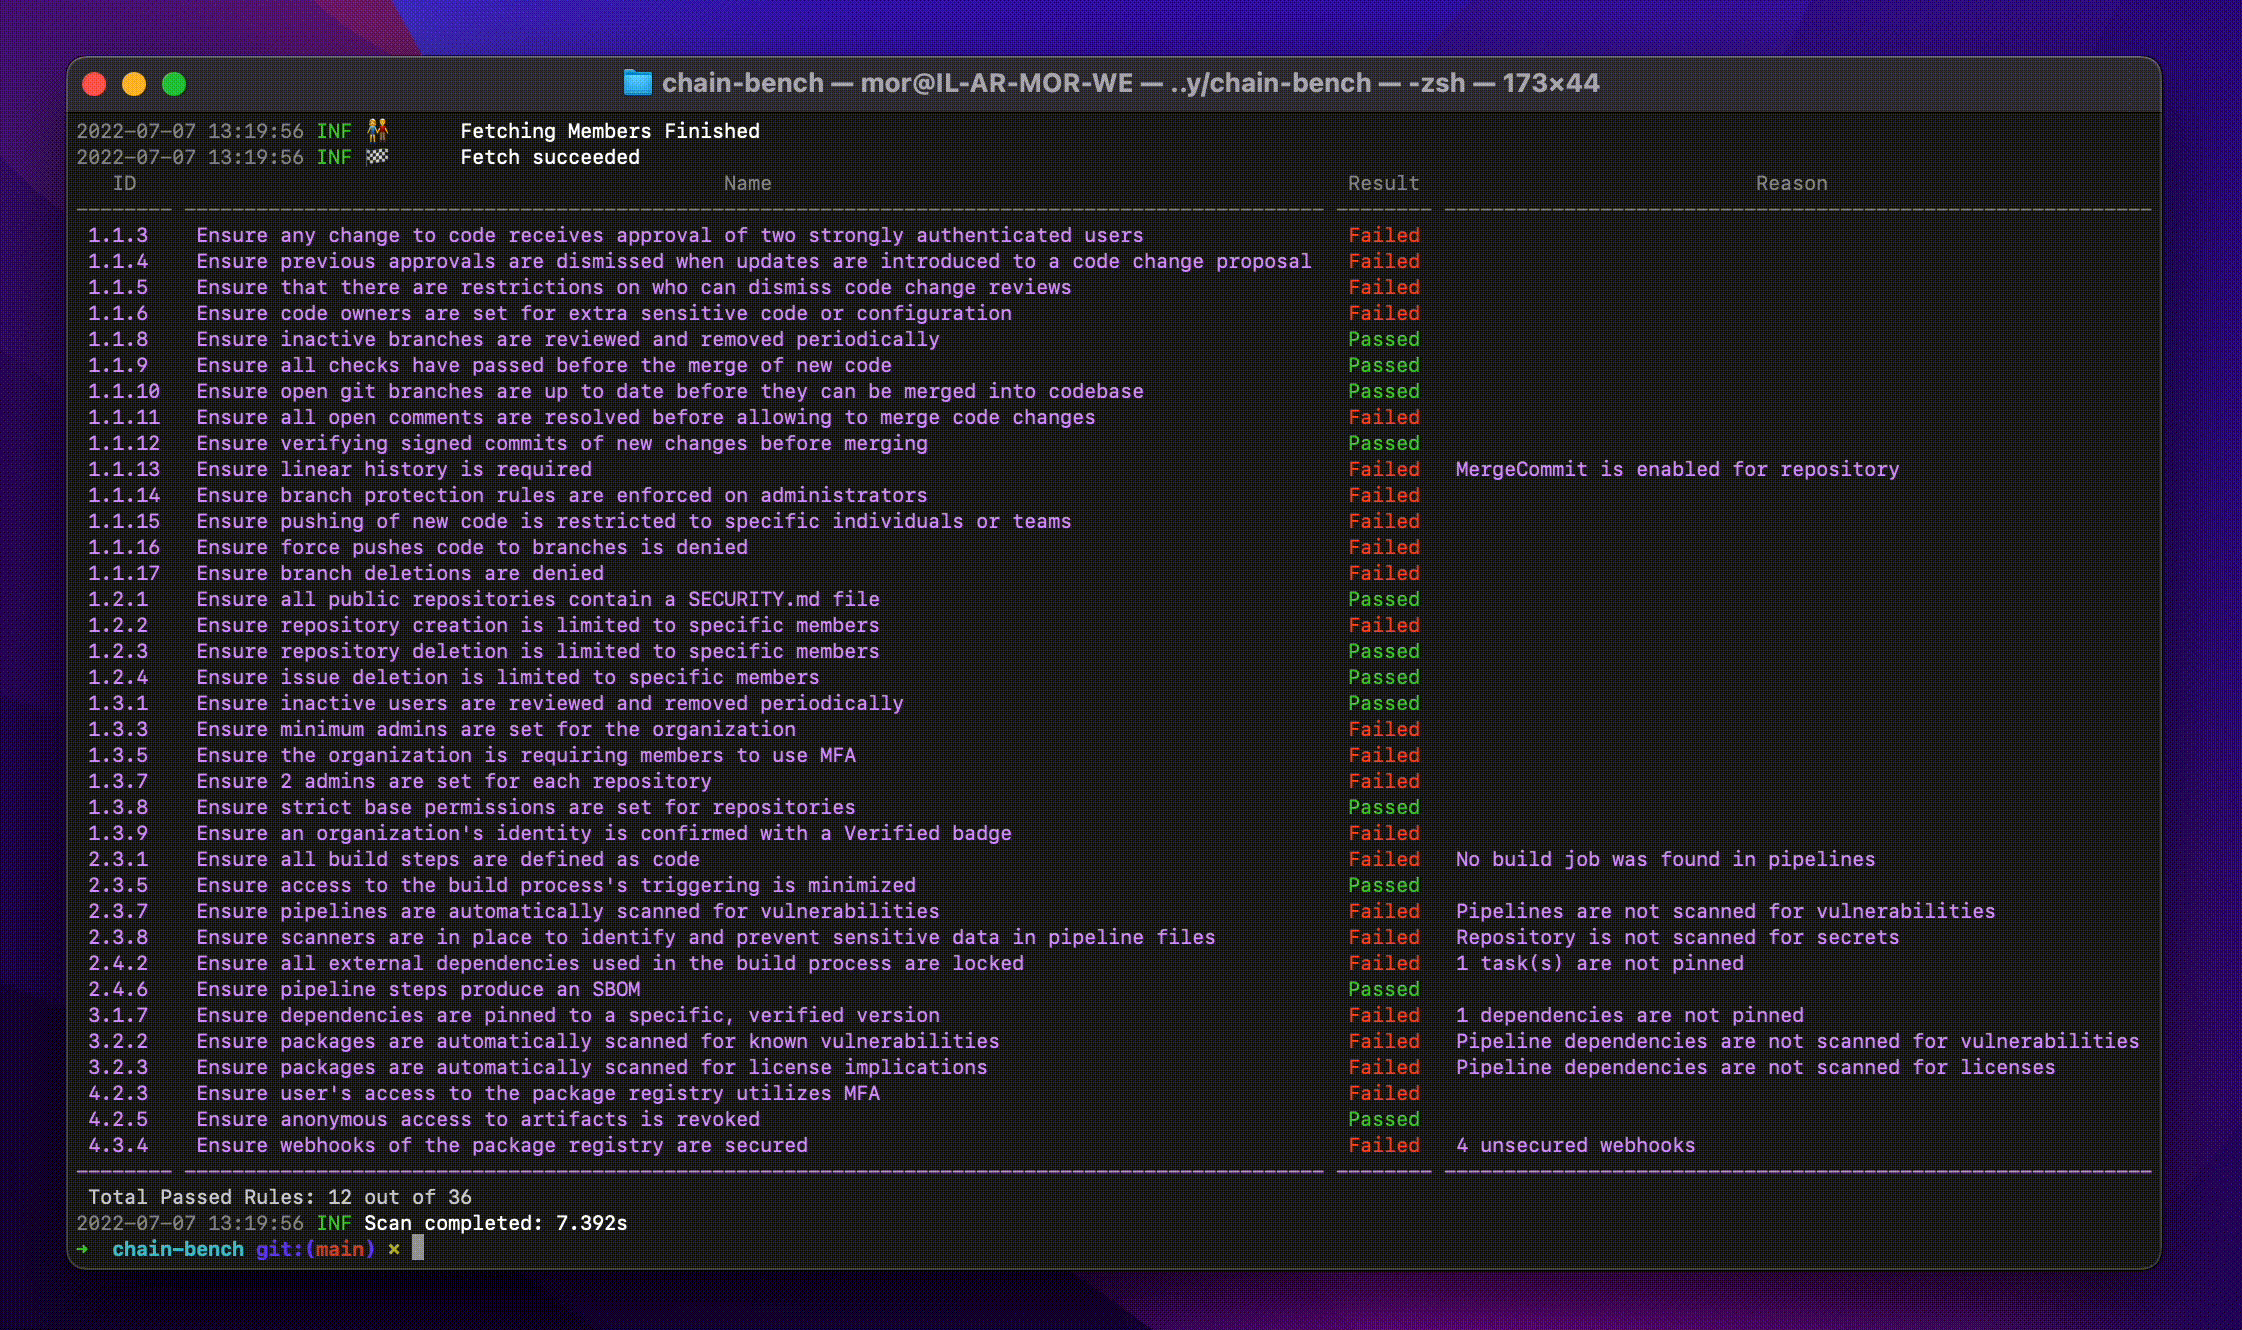 aquasecurity/chain-bench
Audits software supply chain security compliance against the CIS benchmark, scanning SCM settings, branch protections, dependencies, and CI/CD…
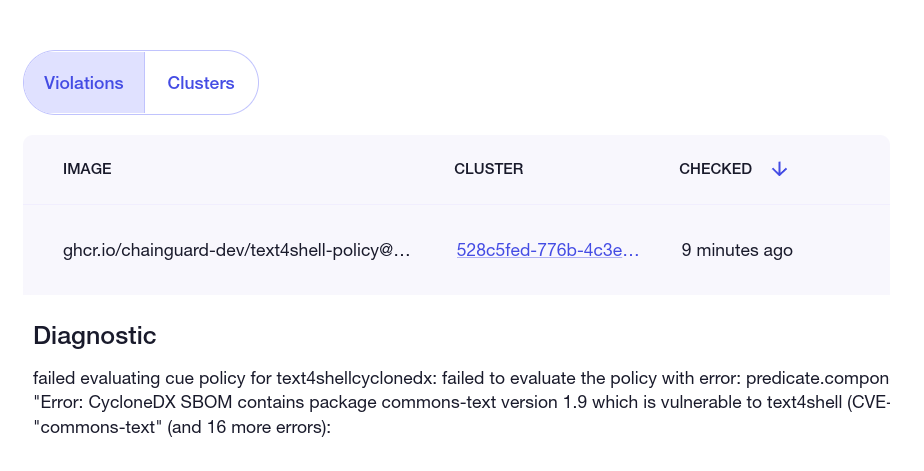 chainguard-dev/text4shell-policy
ClusterImagePolicy demo for cve-2022-42889 text4shell
 node9-ai/node9-proxy
Access control for AI agents. Set what Claude Code, Codex, Gemini, Cursor and any MCP server are allowed to do, review risky actions before they run,…
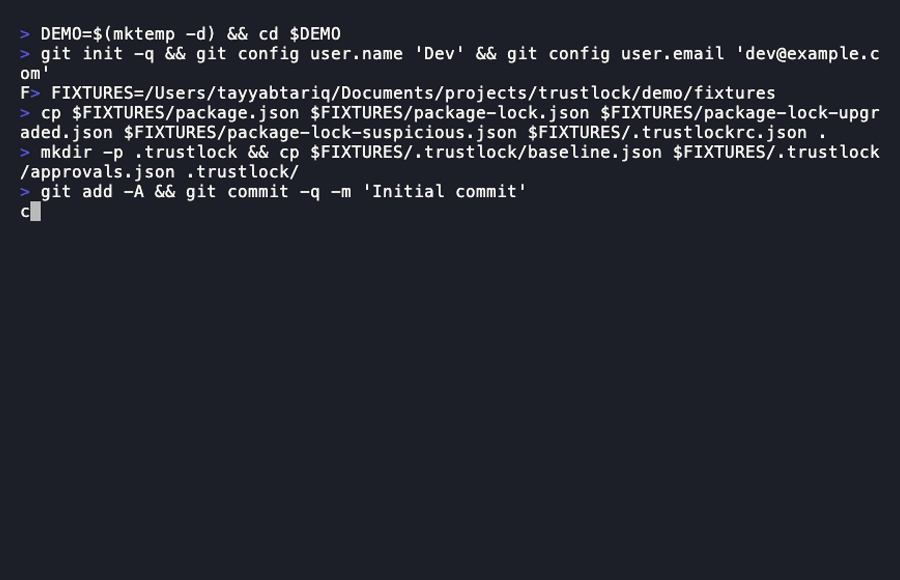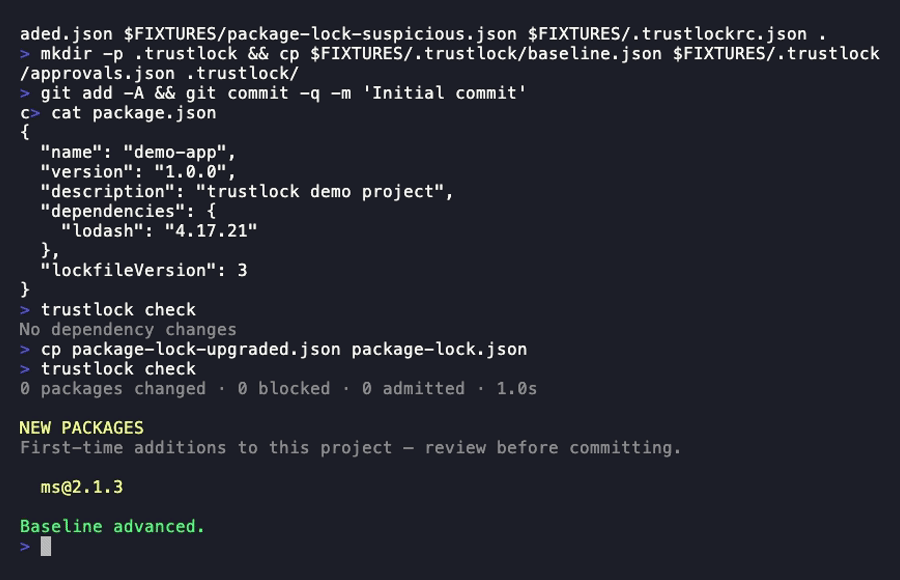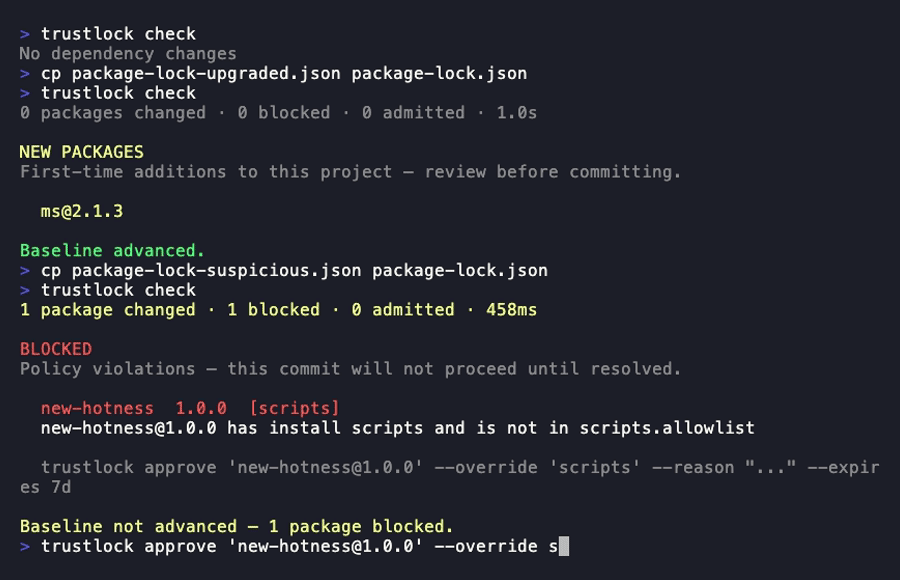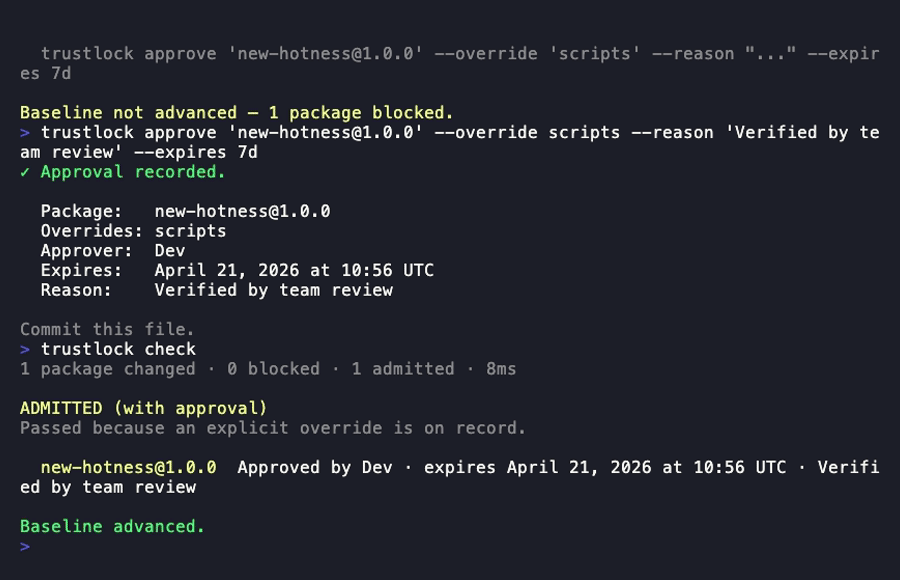 tayyabt/trustlock
A Git-native dependency admission controller. Evaluates trust signals on every dependency change and blocks commits or builds when packages fail your…
 digitalocean/nginxconfig.io
⚙️ NGINX config generator on steroids 💉
 mhaskar/bughound
Static code analysis tool based on Elasticsearch
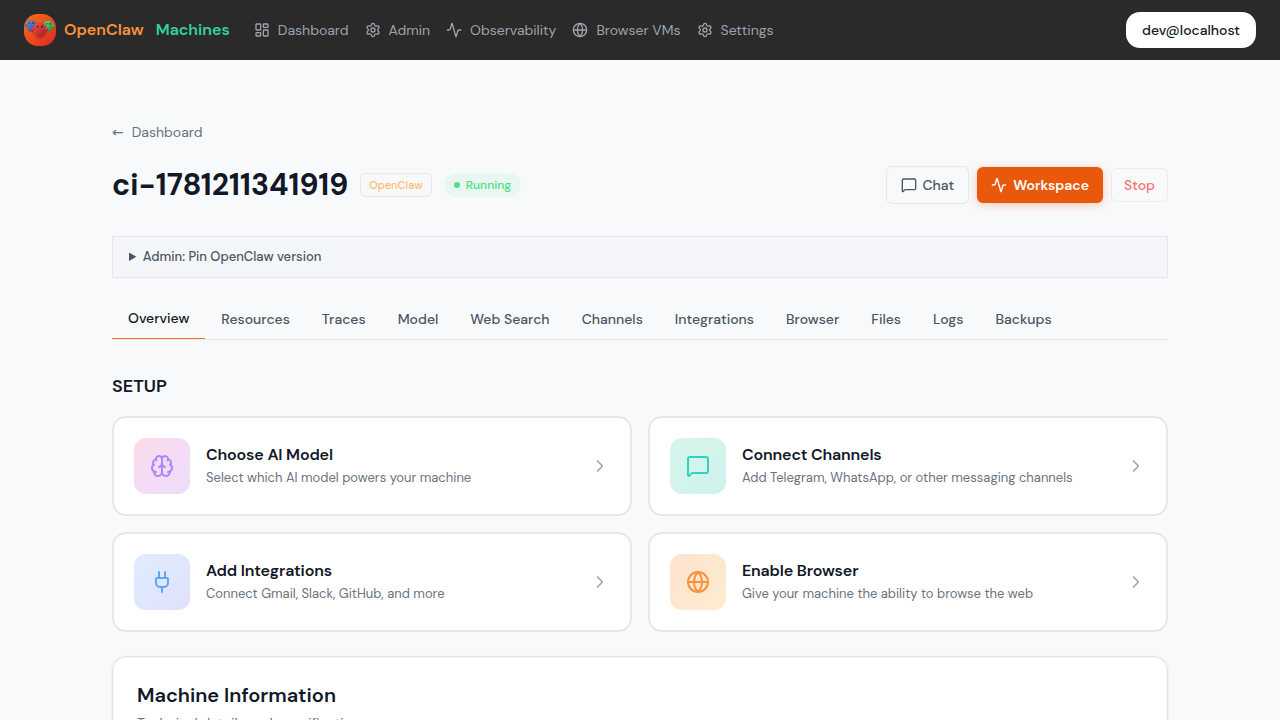 mathaix/openclawmachines
Manage OpenClaw in your team (Enterprise) by providing it compute infrastructure, tool integration, Authentication and security primitives
 offensive360/mcp-server
MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…
 mikesplain/cve-2014-3566-poodle-cookbook
Chef cookbook that detects and fails runs on servers vulnerable to CVE-2014-3566 (POODLE) by scanning specified SSL ports, serving as both a security…
 eskatos/creadur-rat-gradle
Apache RAT (Release Audit Tool) Gradle Plugin
 appomni-labs/heisenberg-ssc-gha
GitHub Action for Heisenberg SSC