
tirith
 sheeki03/tirith
Terminal security for developers and AI agents. Intercepts homograph URLs, pipe-to-shell, ANSI injection, obfuscated payloads, data exfiltration, and…
curated-resourcesdata-exfiltrationdevsecops+8
sheeki03/tirithTerminal security for developers and AI agents. Intercepts homograph URLs, pipe-to-shell, ANSI injection, obfuscated payloads, data exfiltration, and…
 anshumanbh/git-all-secrets
A tool to capture all the git secrets by leveraging multiple open source git searching tools
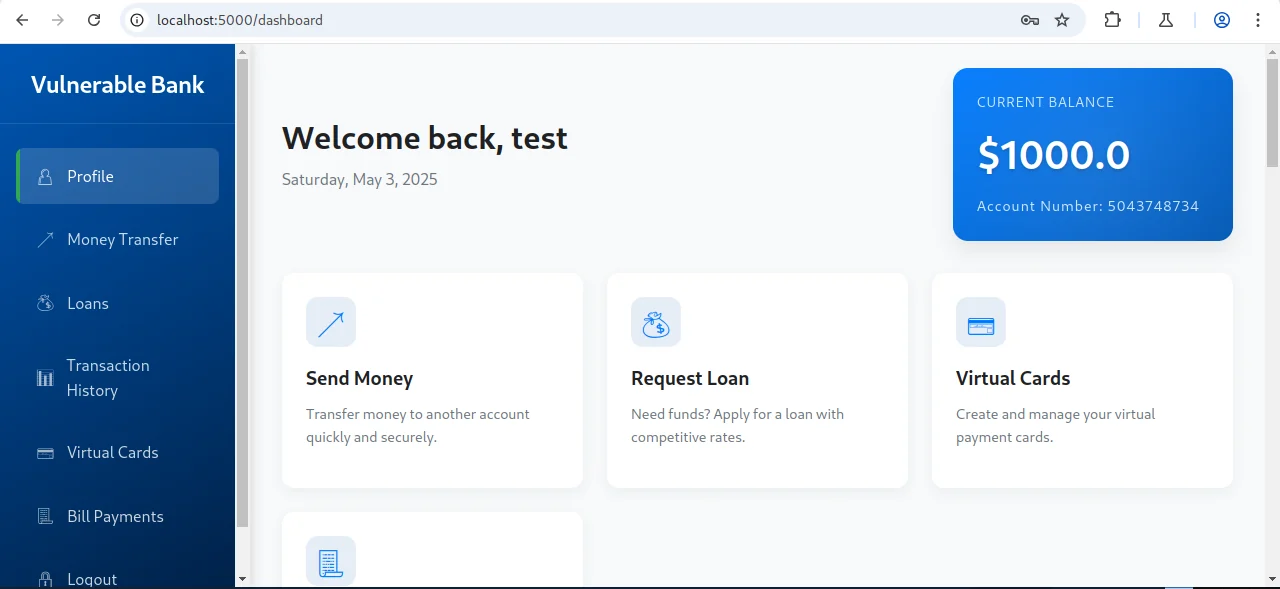 commando-x/vuln-bank
Intentionally vulnerable banking platform for practicing web application, API, and AI/LLM security testing, secure code review, and DevSecOps…
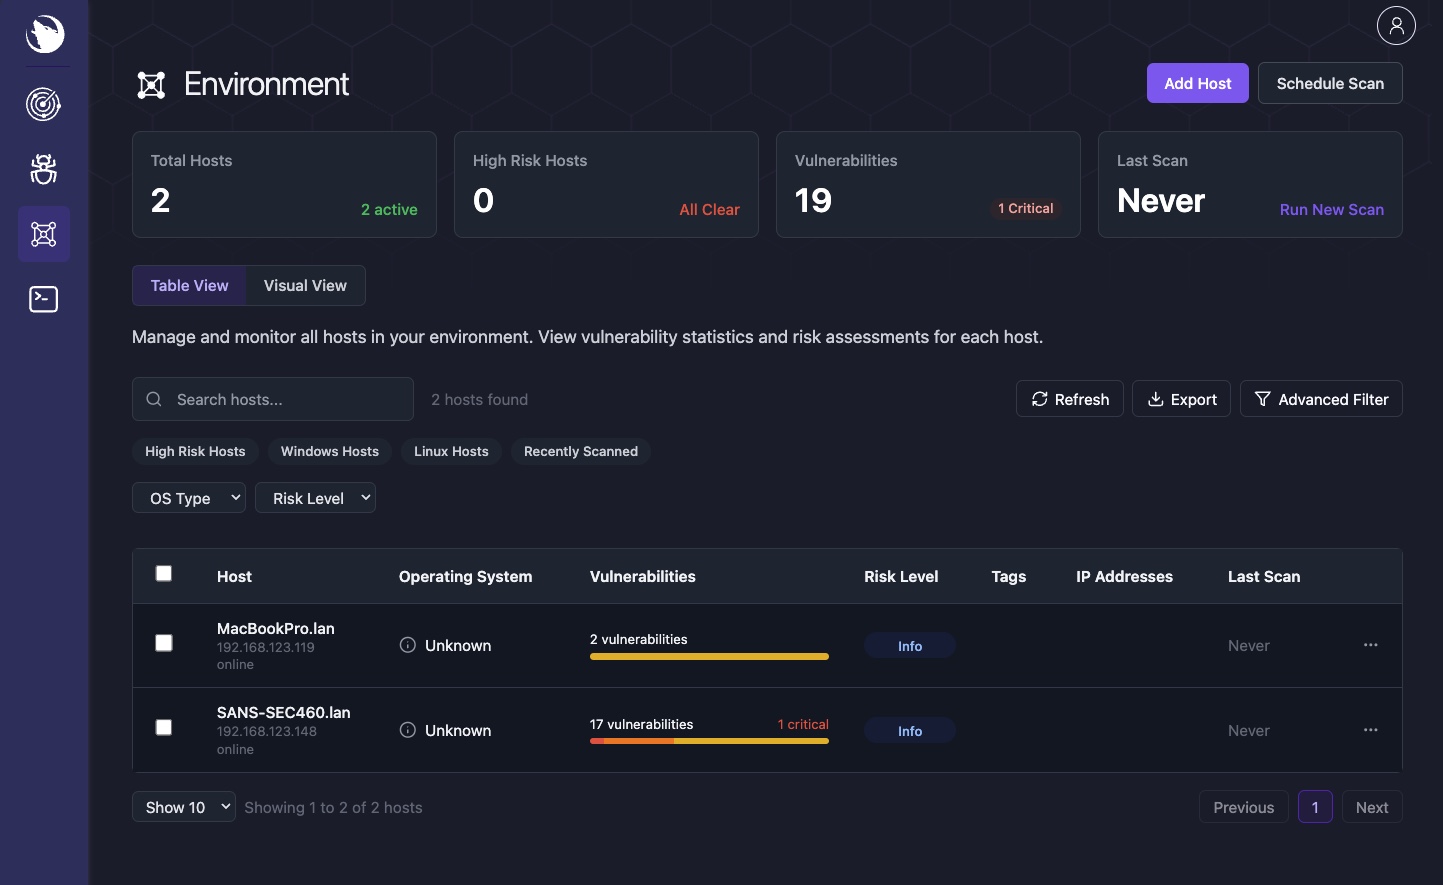 siriusscan/sirius
Open-source vulnerability scanner with automated network discovery, CVE-based detection, CVSS scoring, risk dashboards, remote agents via gRPC, and a…
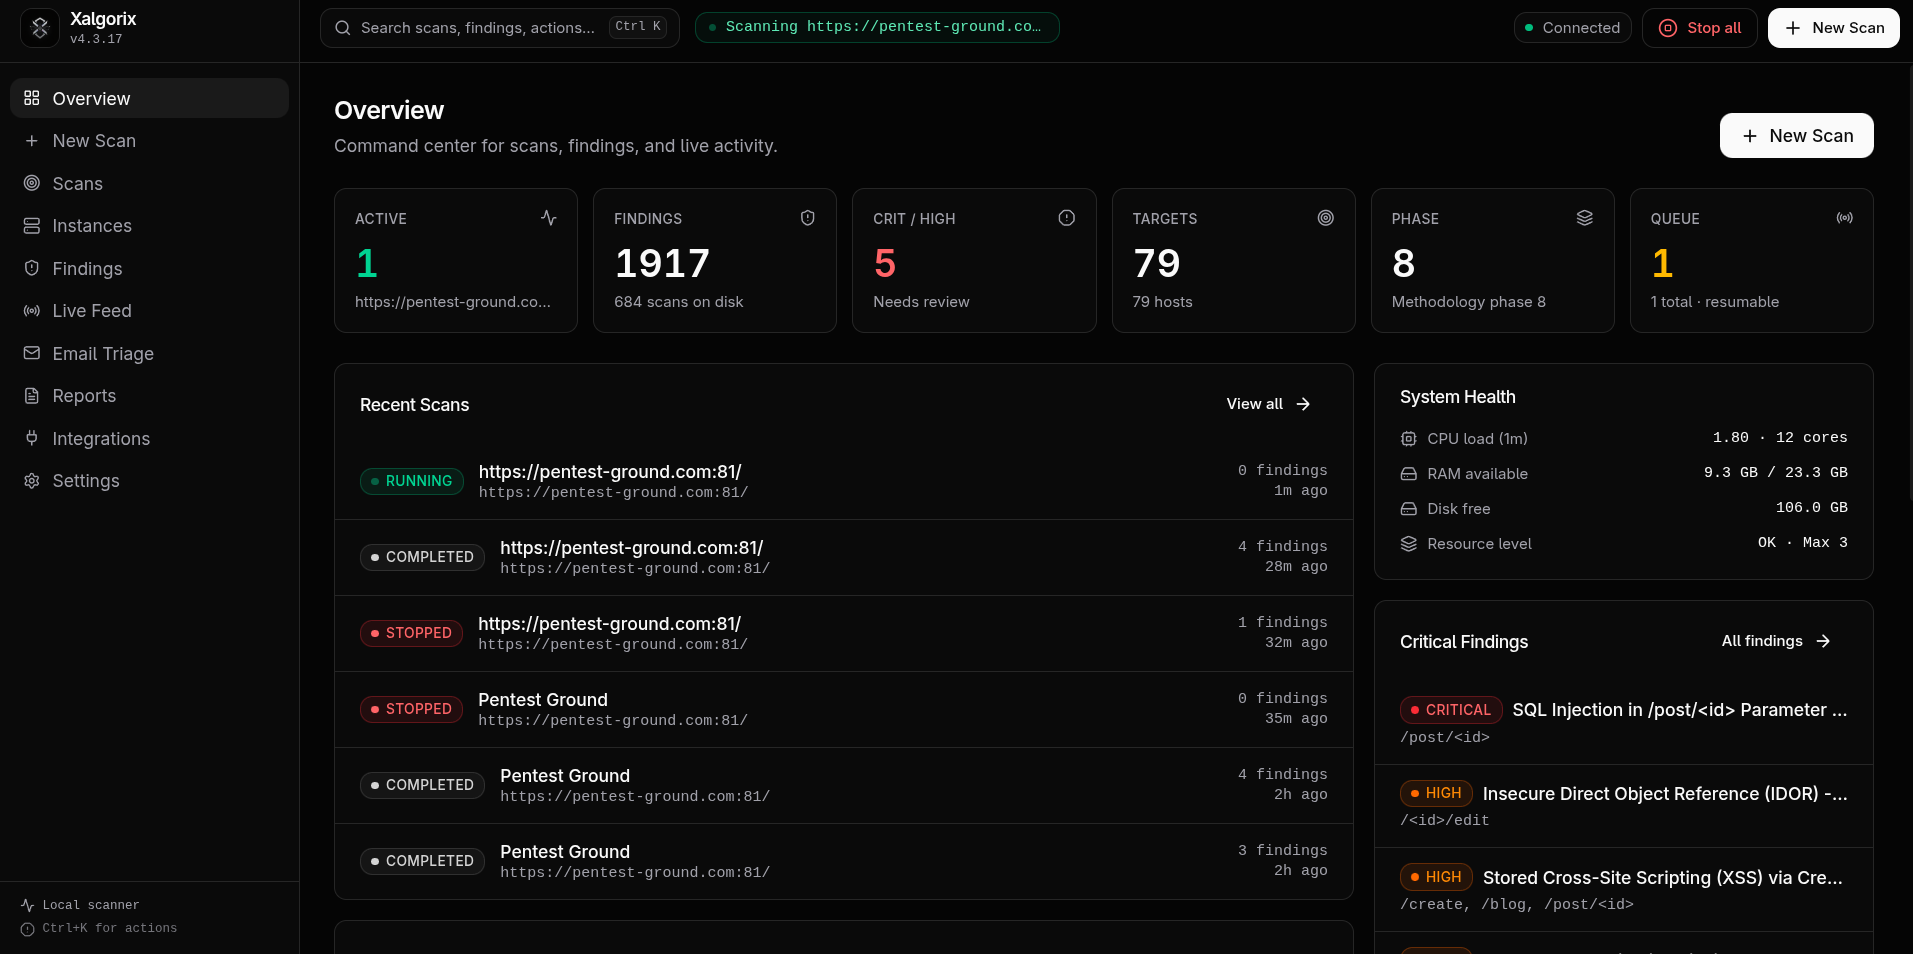 xalgord/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 mukul975/cve-mcp-server
Production-grade MCP server giving Claude 27 security intelligence tools across 21 APIs — CVE lookup, EPSS scoring, CISA KEV, MITRE ATT&CK, Shodan,…
 hacktricks-wiki/hacktricks-cloud
Community-driven knowledge base for pentesting cloud environments and CI/CD pipelines: attack techniques, enumeration, privilege escalation, and…
 punk-security/dnsreaper
Fast subdomain takeover scanner with 50+ signatures, supporting cloud provider integrations (AWS, Azure, Cloudflare) and CI/CD pipeline mode for…
 ascit31/dark-moon
Autonomous AI pentesting engine, continuous offensive security across web, cloud, AD & Kubernetes. Agentic reasoning + real exploit execution deliver…
 reconmap/reconmap
Reconmap is a collaboration-first security operations platform for infosec teams and MSSPs, enabling end‑to‑end engagement management, from…
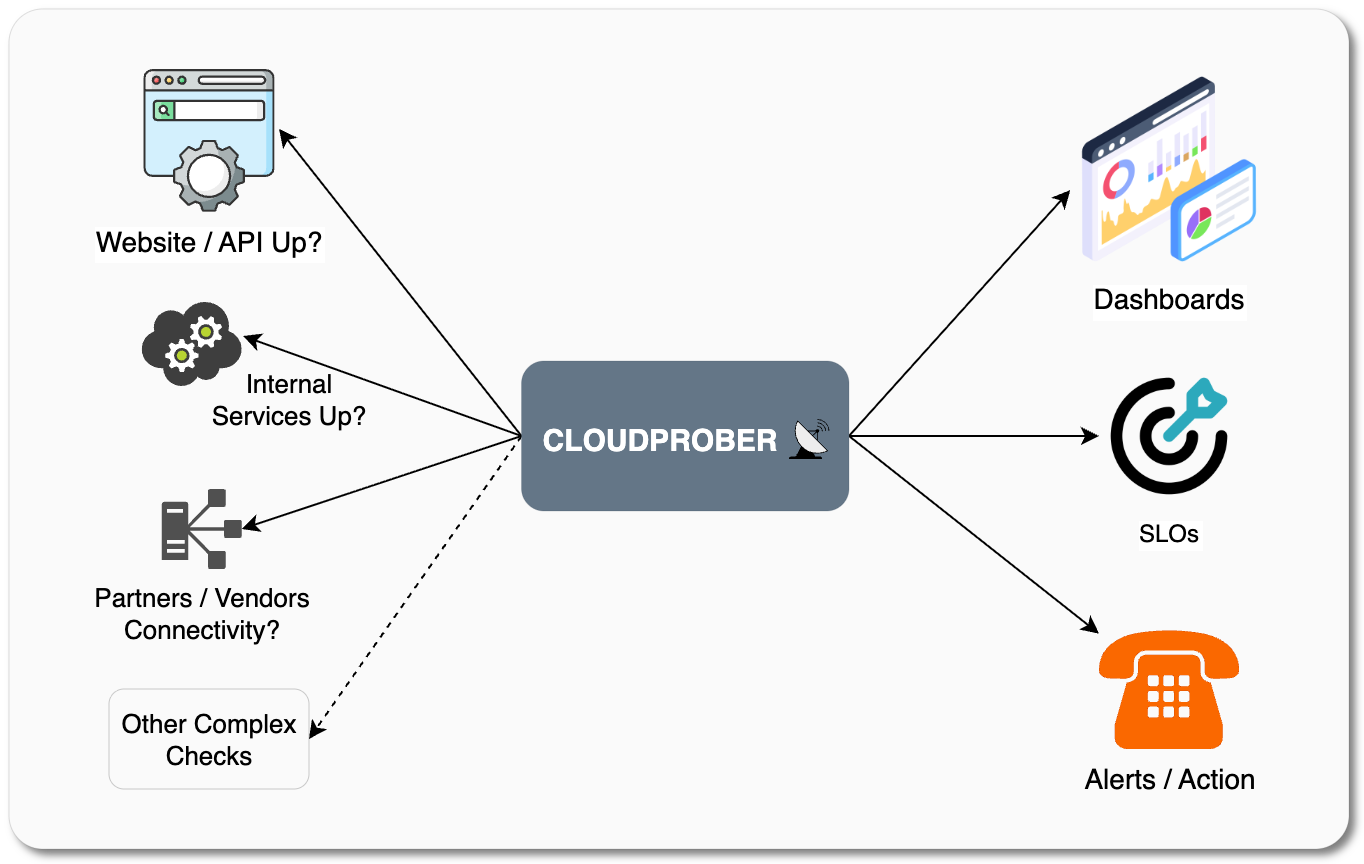 cloudprober/cloudprober
An active monitoring software to detect failures before your customers do.
 raskrebs/sonar
CLI tool for inspecting and managing services listening on localhost ports
 ostorlab/oxo
Modular security scanning orchestrator that combines specialized agents for vulnerability detection, reconnaissance, and fingerprinting across…
 pensarai/apex
AI-powered offensive security testing using autonomous agents, directly in your terminal.
 david-a-wheeler/flawfinder
a static analysis tool for finding vulnerabilities in C/C++ source code
 synacktiv/nord-stream
Nord Stream is a tool that allows you to extract secrets stored inside CI/CD environments by deploying malicious pipelines. It currently supports…
 michelin/chopchop
YAML-driven CLI scanner that detects exposed services, files, and folders on web endpoints. Designed for developers to integrate security checks into…
 cycodelabs/raven
Scans GitHub Actions CI/CD workflows for security vulnerabilities, indexes findings into a Neo4j graph database, and provides a query library for…