

gh-workflow-auditor
 tindersec/gh-workflow-auditor
Script to audit GitHub Action Workflow files for potential vulnerabilities.
configuration-auditingdevsecopsstatic-analysis+2
152
tindersec/gh-workflow-auditorScript to audit GitHub Action Workflow files for potential vulnerabilities.
 pypa/pip-audit
Audits Python environments, requirements files and dependency trees for known security vulnerabilities, and can automatically fix them
 boringtools/git-alerts
Tool to detect and monitor GitHub org users' public repositories for secrets and sensitive files
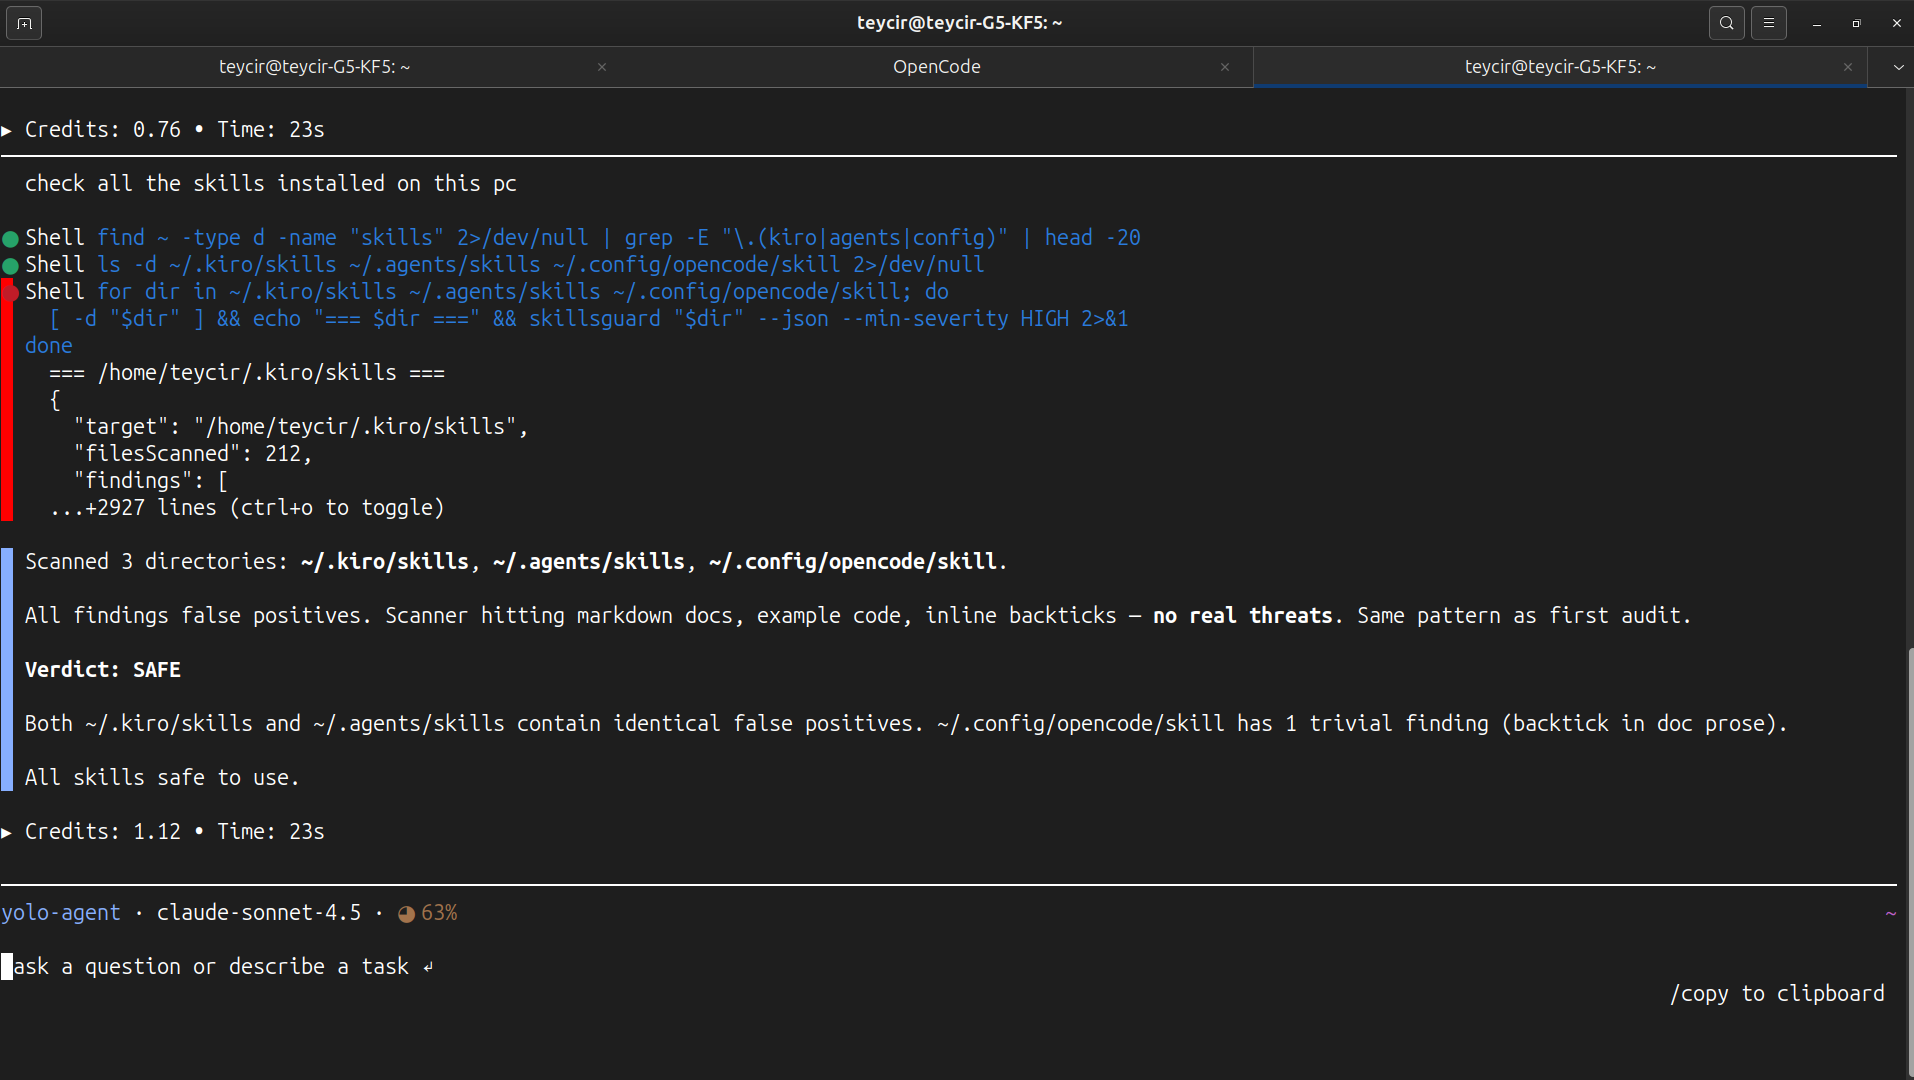 teycir/skillsguard
Static security scanner for AI agent skill packages. Detects malicious SKILL.md files and bundled scripts before they run.
 dbzoo/log4j_scanner
Filesystem scanner for Log4Shell (CVE-2021-44228) and related CVEs. Detects vulnerable JAR files via hash matching and class presence. Runs…
 atlassian/bitbucket-iac-scan
Scans Infrastructure as Code files for security misconfigurations and vulnerabilities using KICS, with Bitbucket Code Insights reporting.
 hozyx/log4shell
Applications that are vulnerable to the log4j CVE-2021-44228/45046 issue may be detectable by scanning jar, war, ear, zip files to search for the…
 trufflesecurity/trufflehog
Find, verify, and analyze leaked credentials
 xddxdd/nixos-config
Lan Tian's NixOS Configuration
 ustayready/outpost
AWS Testing and Reporting Management Tool
 hristiy4n/bom-view
Static web application for viewing SBOMs and performing on-demand vulnerability scanning with osv.dev. Easily deployable to GitHub/GitLab Pages.
 derekpreston81/cve_adc_ioc_2026
Citrix NetScaler CVE Preconditions Checker as per CTX696604 | Supported CVE : CVE-2026-8451, CVE-2026-8452, CVE-2026-8655, CVE-2026-10816,…