

infer
 facebook/infer
A static analyzer for Java, C, C++, and Objective-C
code-analysisdevsecopsstatic-analysis+1
facebook/inferA static analyzer for Java, C, C++, and Objective-C
 skyscanner/whispers
Identify hardcoded secrets in static structured text
 dependency-check/dependencycheck
OWASP dependency-check is a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies.
 shiftleftsecurity/sast-scan
Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
 cyclonedx/cyclonedx-cli
CLI for generating, analyzing, merging, diffing, validating, signing, and converting CycloneDX SBOMs across JSON, XML, Protobuf, CSV, and SPDX…
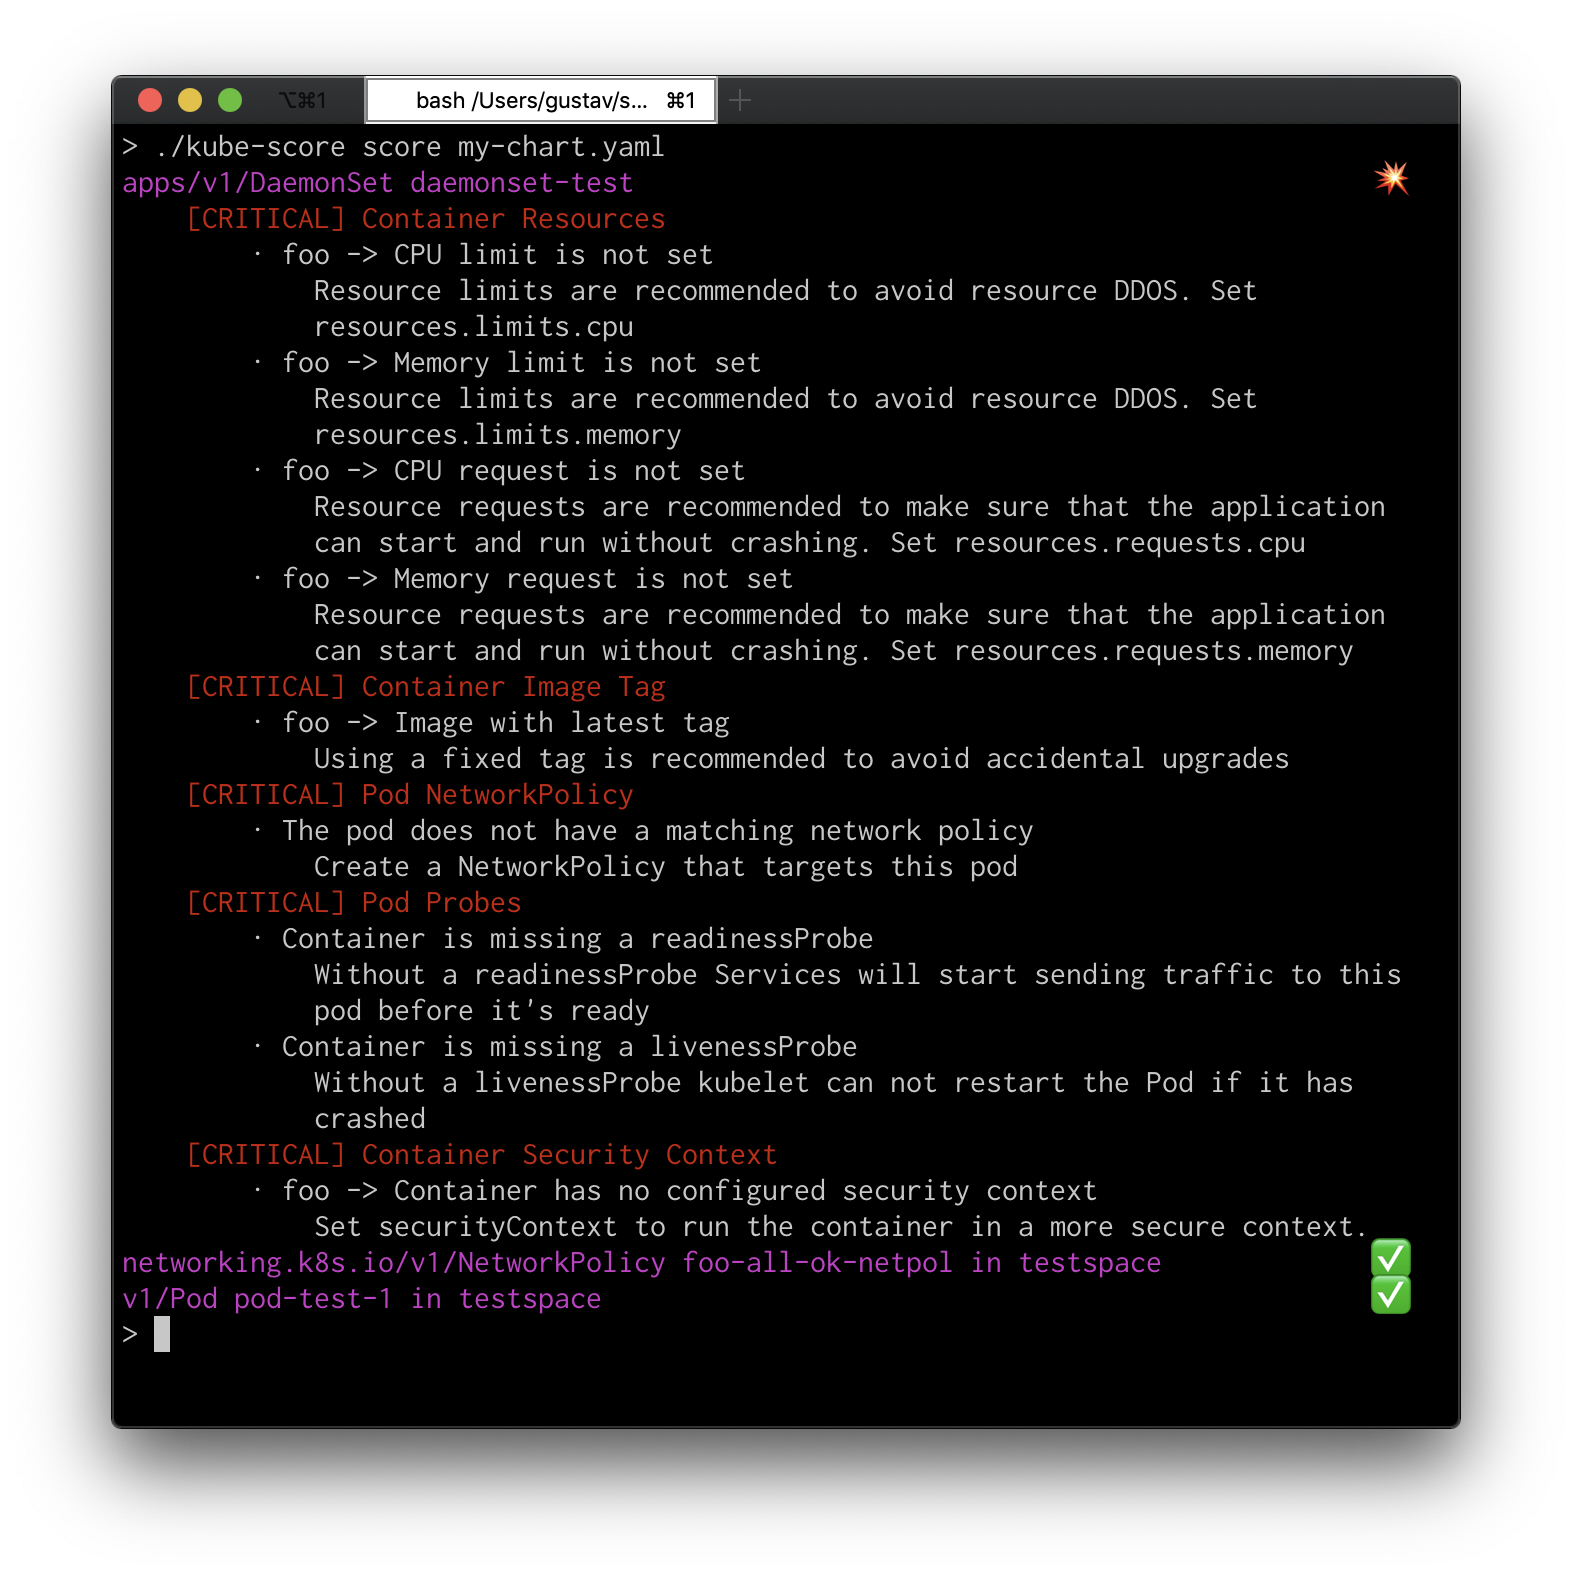 zegl/kube-score
Kubernetes object analysis with recommendations for improved reliability and security. kube-score actively prevents downtime and bugs in your…
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 cartography-cncf/cartography
Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and…
 thesisgroup3/secassessment_gapdetect
Rule-based CLI tool that grades organizational defenses against MITRE ATT&CK and D3FEND frameworks, detects security gaps, and proposes mitigations.…
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
 cycodelabs/raven
Scans GitHub Actions CI/CD workflows for security vulnerabilities, indexes findings into a Neo4j graph database, and provides a query library for…
 hahwul/dalfox
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
 owasp-dep-scan/dep-scan
Next-generation dependency vulnerability scanner with reachability analysis, SBOM generation, license audit, and container image scanning for CI/CD…
 google/capslock
CLI tool for analyzing Go package capabilities by tracing transitive calls to privileged standard library operations, enabling supply chain risk…
 tillson/git-hound
Fast GitHub recon tool. Scans for leaked secrets across all of GitHub, not just known repos and orgs. Support for GitHub dorks.
 rakosn1cek/oversight
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…
 opengrep/opengrep
🔎 Static code analysis engine to find security issues in code.
 shubhamshubhankar/autosource
Automated static code analysis framework integrated with SonarQube for early vulnerability detection in source code by scanning Git repositories…