
api-scanner-docker
Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …

Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …

Skills for threat modeling, scanning, triage, patching, plus an autonomous scanning harness you can /customize

Scans GitHub Actions CI/CD workflows for security vulnerabilities, indexes findings into a Neo4j graph database, and provides a query library for…

Safe detection tooling for CVE-2026-31431 "Copy Fail" and CVE-2026-43284 "Dirty Frag" — a local privilege escalation in the Linux kernel's algif_aead…

A high-performance automation tool designed to bridge the gap between technical web reconnaissance and executive reporting. Developed by **Adi…

Zero-downtime Linux kernel zero-day defense case study. For the automated CLI and dual-witness notary framework, see mc493/kshield.

Fixes CVE-2021-44228 in log4j by patching JndiLookup class

Detection script for CIFSwitch - CVE-2026-46243

Here is patch script to CVE-2026-31431 CopyFail

I have created AegisJava, a tool to fix (detect and mitigate) CVE-2025-30749.

Detection of the React Server Actions Exploit vector – CVE-2025-55182 / CVE-2025-66478

Docker base image with backported Host header validation fix for CVE-2025-12543 in Undertow 1.4.x, enabling secure deployment of WildFly 11…

Detects and fixes CVE-2025-55182 (React2Shell) in React Server Components and Next.js apps. Scans package versions, suggests safe upgrades, and…

A passive detection tool for identifying potential exposure to CVE-2026-24061 in GNU inetutils telnet installations

Ansible playbook for patching CVE-2024-3094

An Ansible Playbook to mitigate the risk of RCE (CVE-2024-6387) until platforms update OpenSSH to a non-vulnerable version.

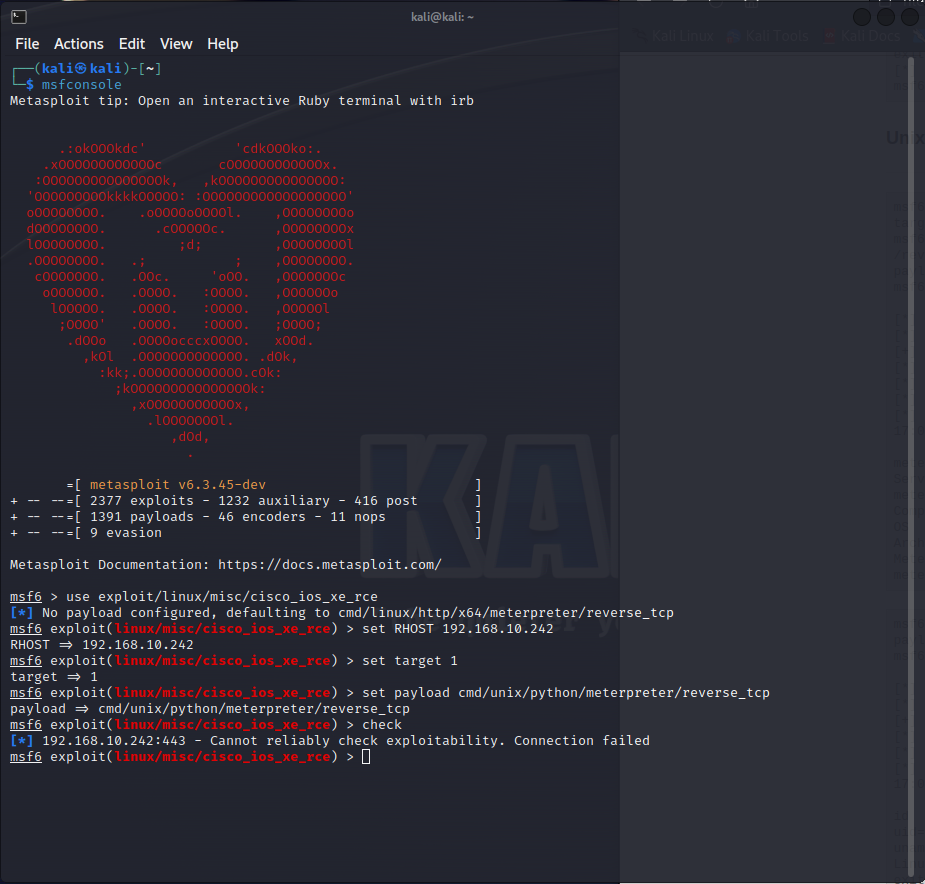
Check for and remediate conditions that make an IOS-XE device vulnerable to CVE-2023-20198

log4j mitigation work