
conftest
 open-policy-agent/conftest
Write tests against structured configuration data using the Open Policy Agent Rego query language
cloud-infrastructure-securityconfiguration-auditingdevsecops+2
3.3k
open-policy-agent/conftestWrite tests against structured configuration data using the Open Policy Agent Rego query language
 google/safetext
Go library for safe YAML and shell generation, using syntax-aware templates to detect and block injection attacks via annotations for trusted data.
 zeroecco/holos
Declarative KVM/QEMU VM orchestration tool using YAML compose files. Manages multi-VM stacks with cloud-init, SSH, PCI passthrough, and image…
 oseguera12/cowrie-honeypot-digitalocean
Medium-interaction SSH/Telnet honeypot built with Cowrie, Loki, Promtail, and Grafana - provisioned on DigitalOcean via Terraform with a GitLab CI…
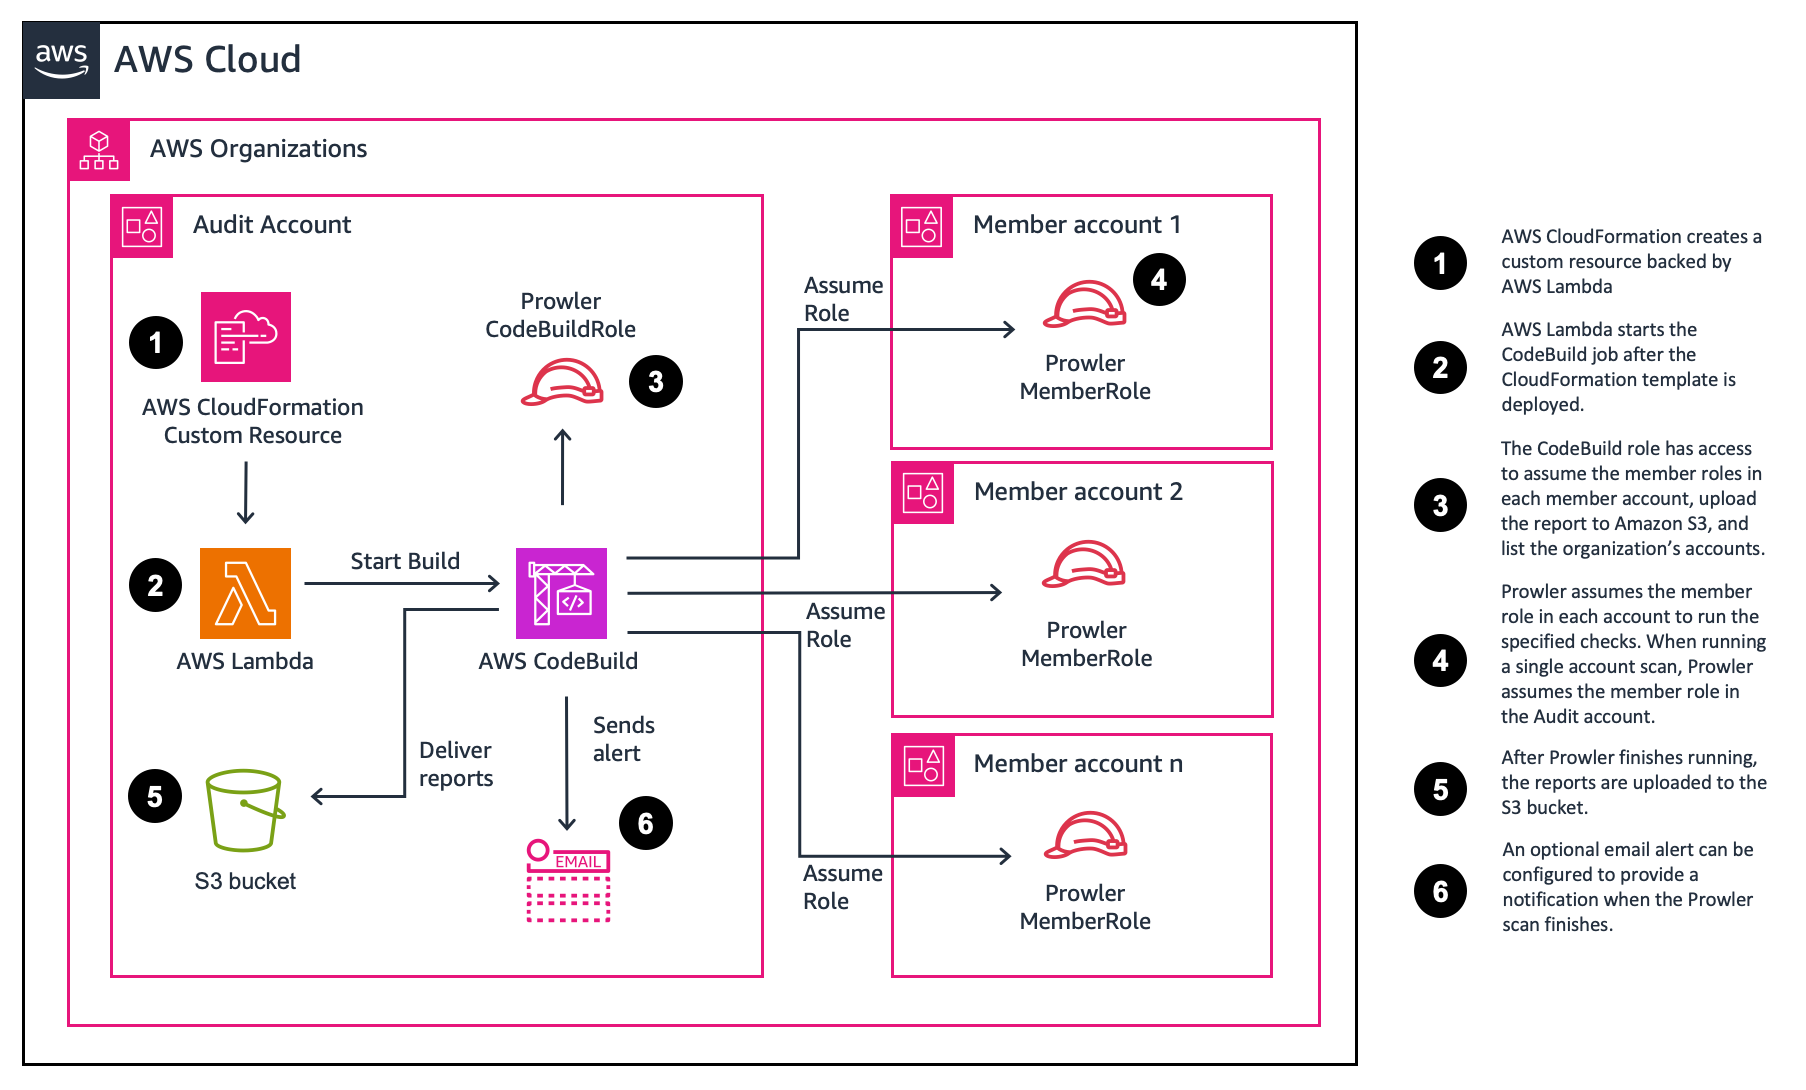 awslabs/aws-security-assessment-solution
An AWS tool to help you create a point in time assessment of your AWS account using Prowler.
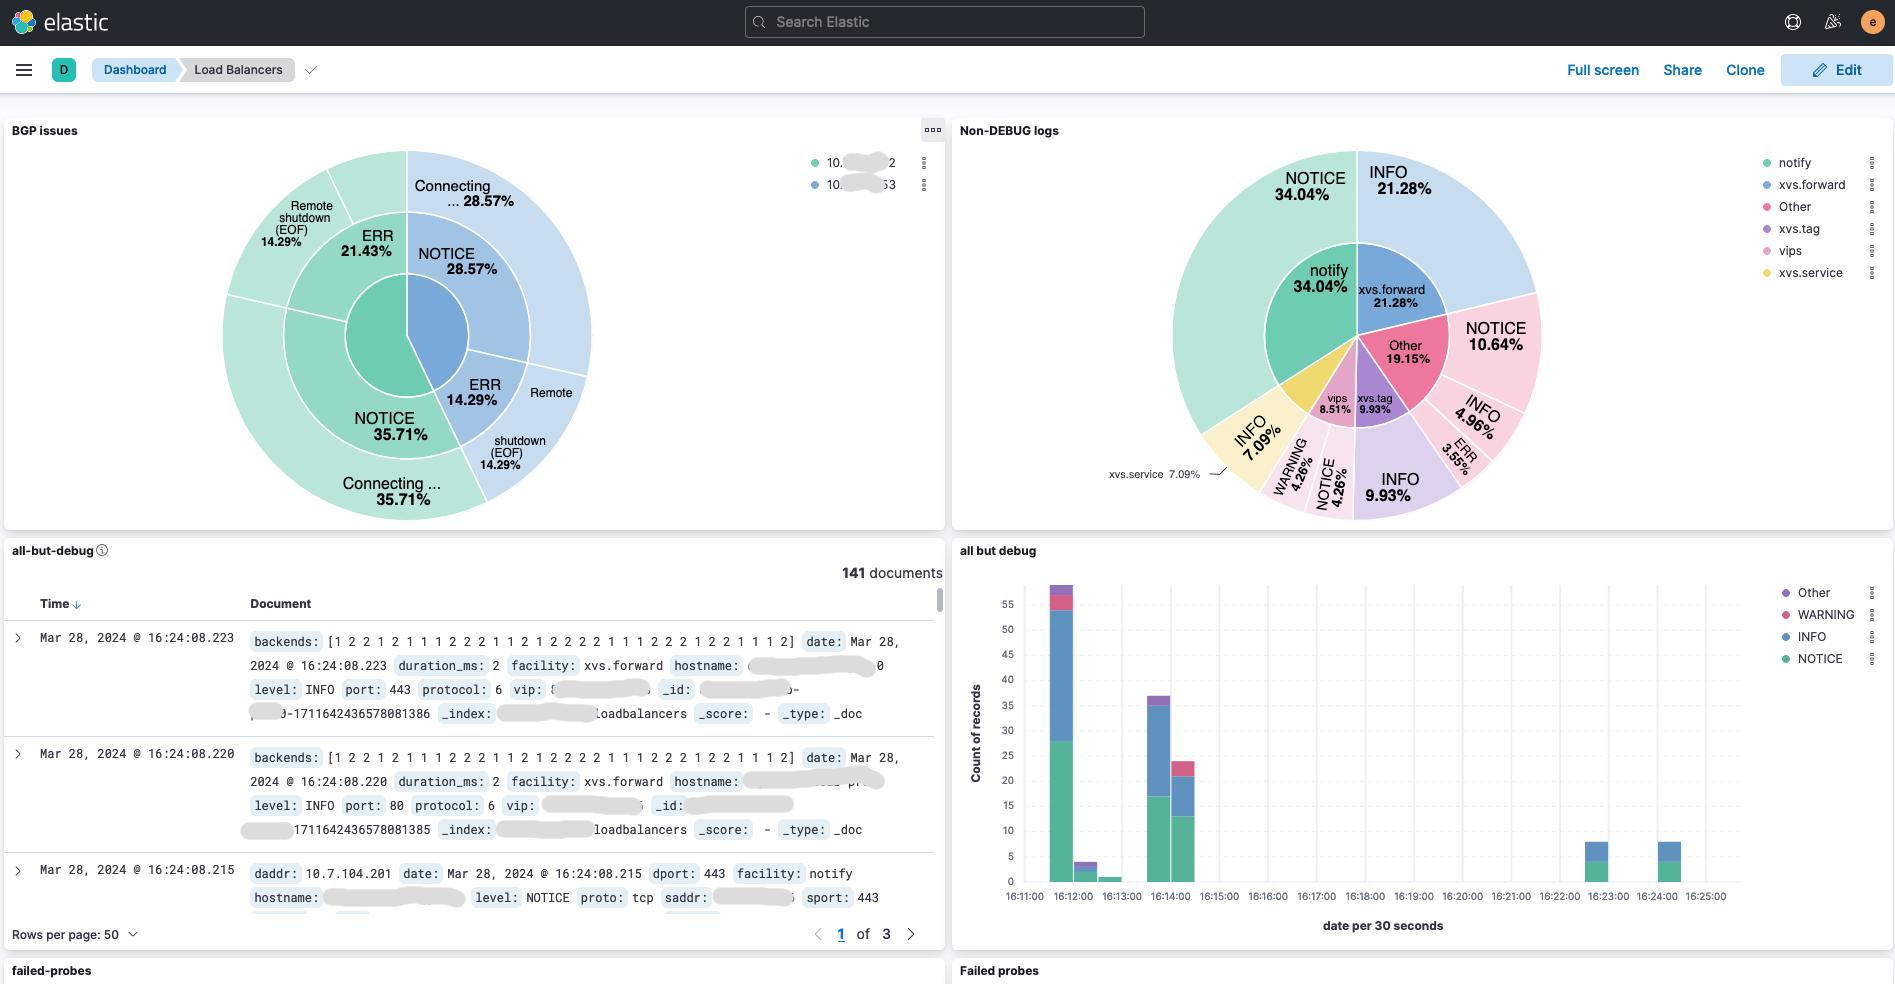 davidcoles/vc5
A horizontally scalable Direct Server Return layer 4 load balancer for Linux using XDP/eBPF
 newrelic/rusty-hog
Multi-source secret scanner detecting API keys, passwords, and PII across Git repos, S3 buckets, filesystems, Confluence, JIRA, Slack, and Google…
 zzugab/juice-shop-with-kubeadm-and-tf
Automated deployment of OWASP Juice Shop on Kubernetes using kubeadm and Terraform, with integrated Trivy vulnerability scanning for DevSecOps…
 infiniroot/ansible-mitigate-copyfail-dirtyfrag
Simple Ansible Playbook to mitigate against CopyFail (CVE-2026-31431) and DirtyFrag (CVE-2026-43284) vulnerabilities.
 aestechno/cve-2026-31431-ansible
Ansible playbook to detect and apply kernel cmdline mitigation for CVE-2026-31431 (Copy Fail) across Debian/Ubuntu/RHEL fleets, with read-only…
 jbiniek/copy.fail-mitigation-mlm
Salt state to deploy a mitigation of the copy.fail vulnerability (CVE-2026-31431)
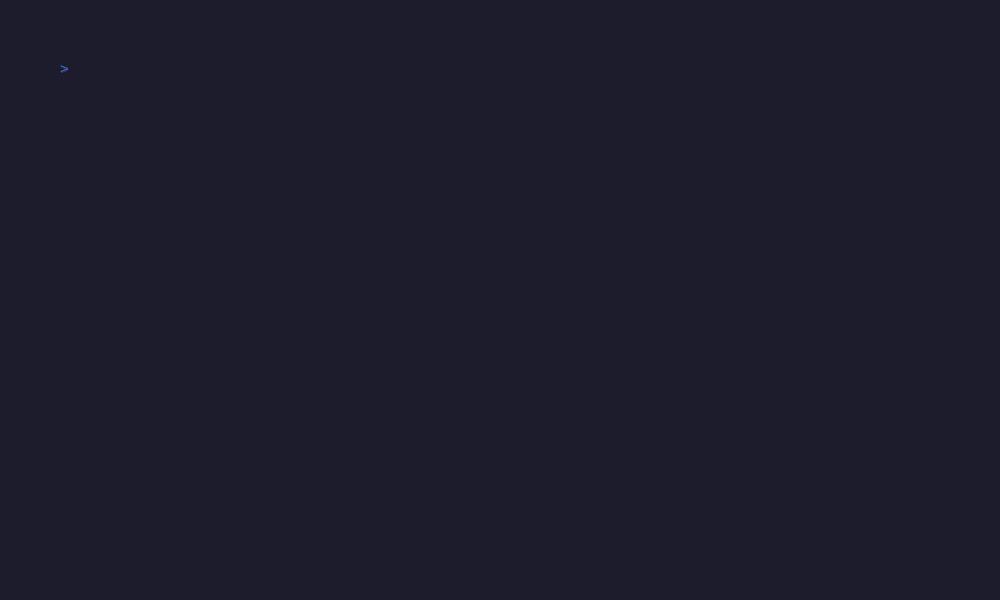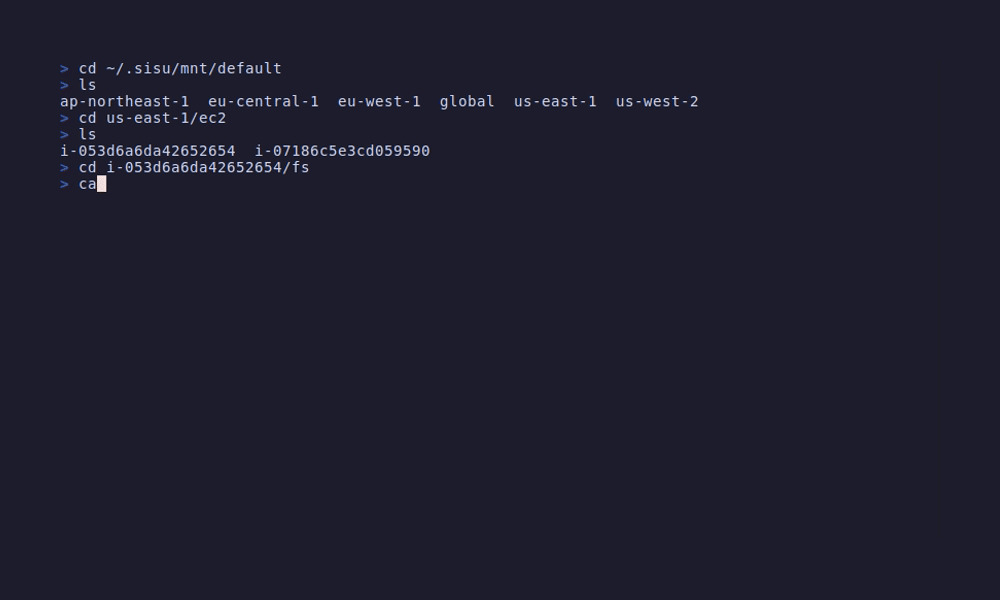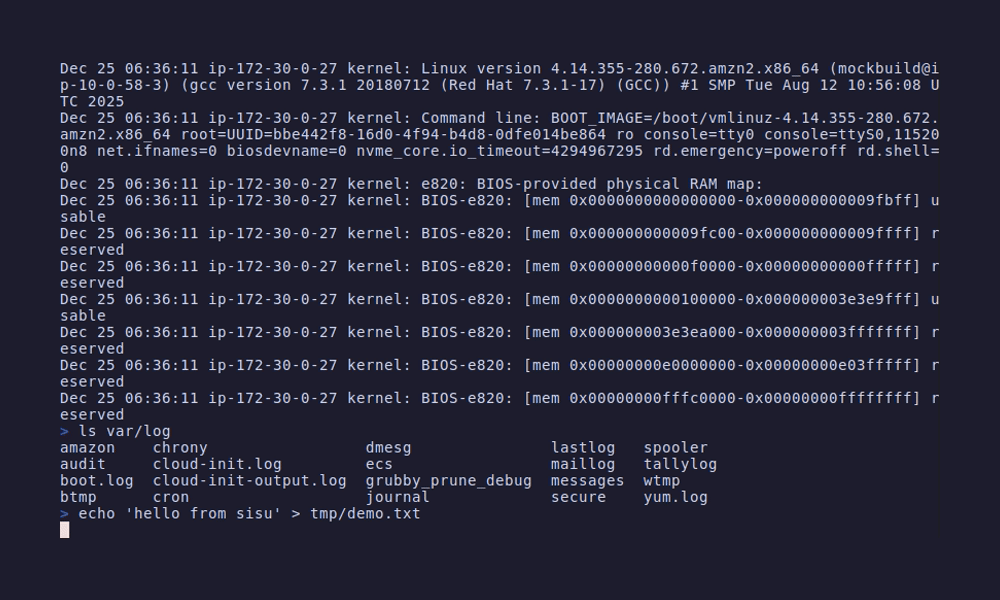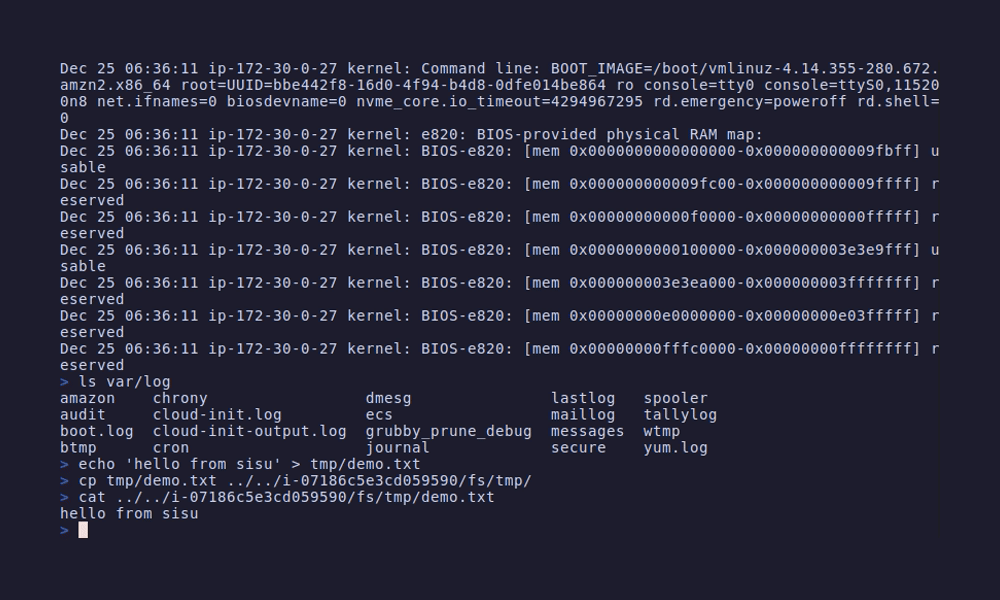 semonte/sisu
Mounts AWS resources as a local filesystem for infrastructure exploration, security auditing, and configuration analysis using standard Unix tools…
 atlassian/bitbucket-iac-scan
Scans Infrastructure as Code files for security misconfigurations and vulnerabilities using KICS, with Bitbucket Code Insights reporting.
 p0ssuidao/terraguard
🛡️ 🔒 This project's goal is to be simple to create and destroy your own VPN service using WireGuard.