
kubescape
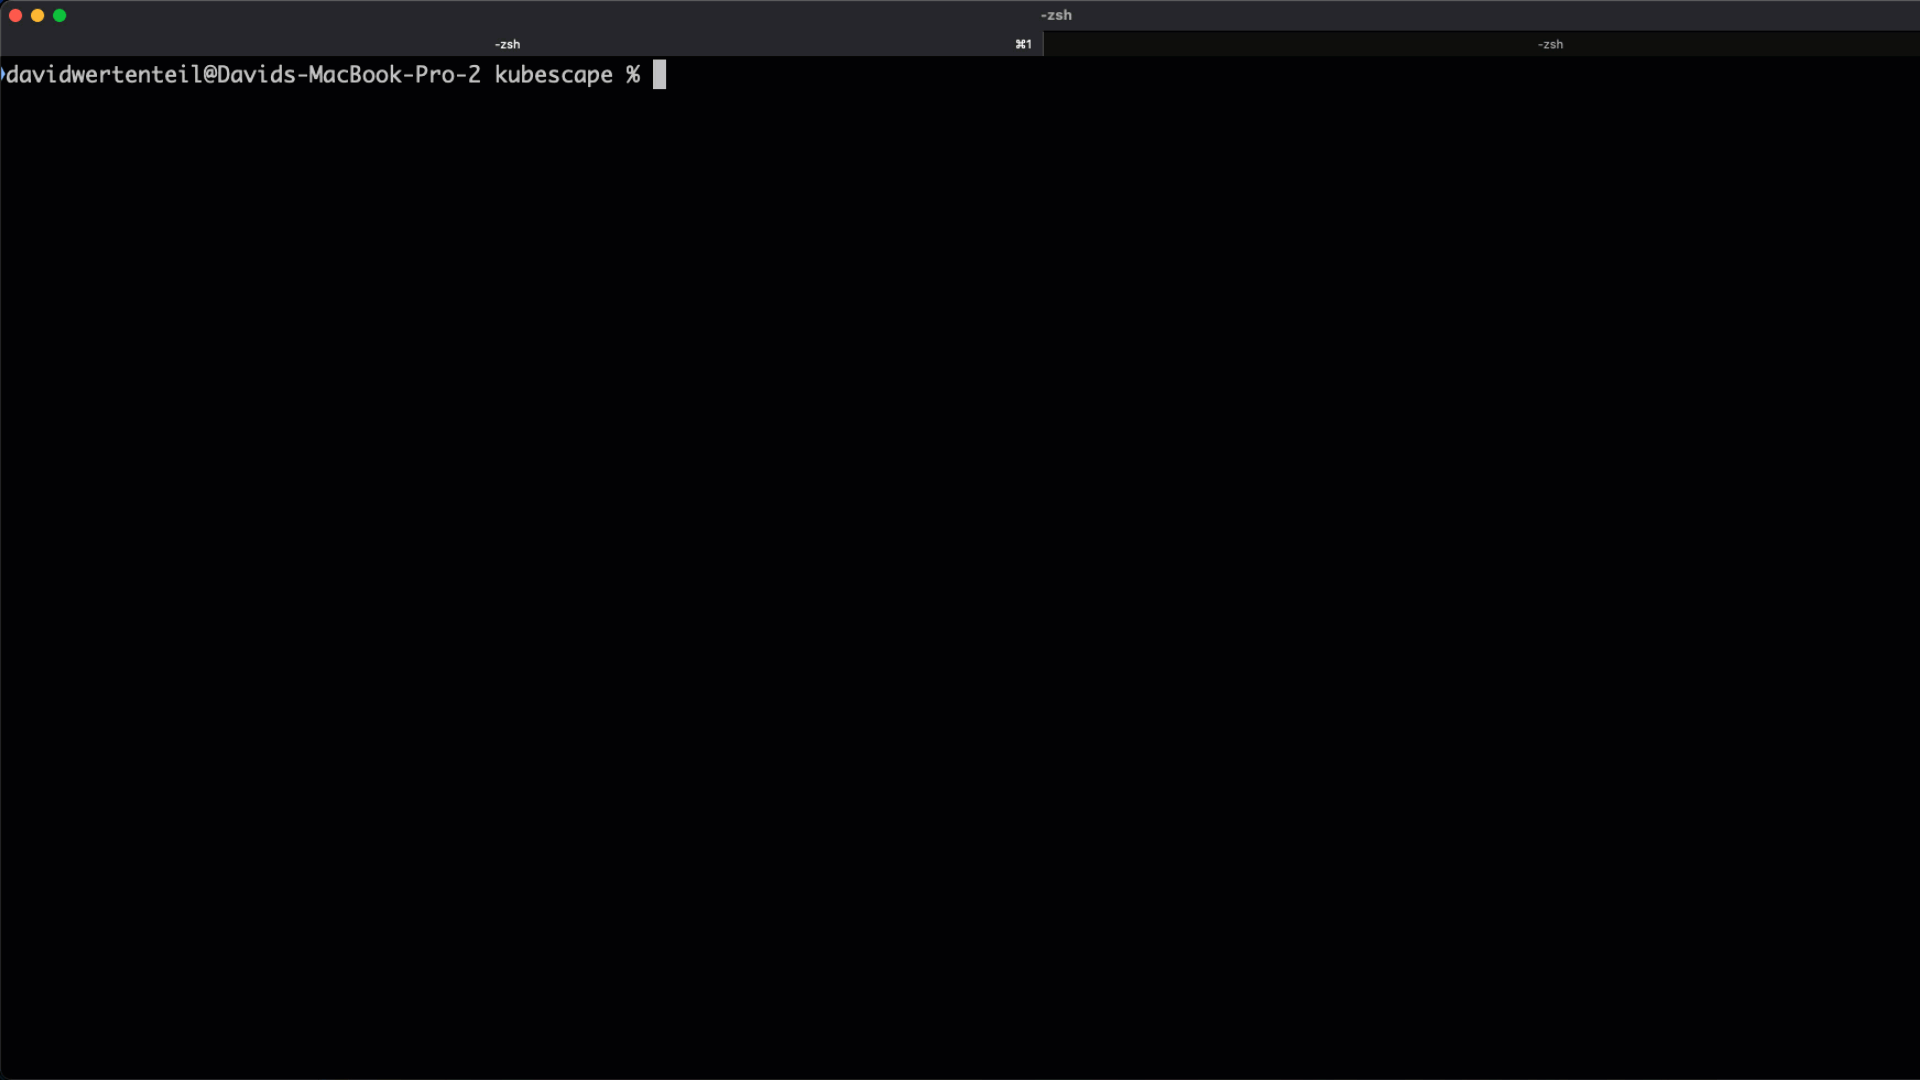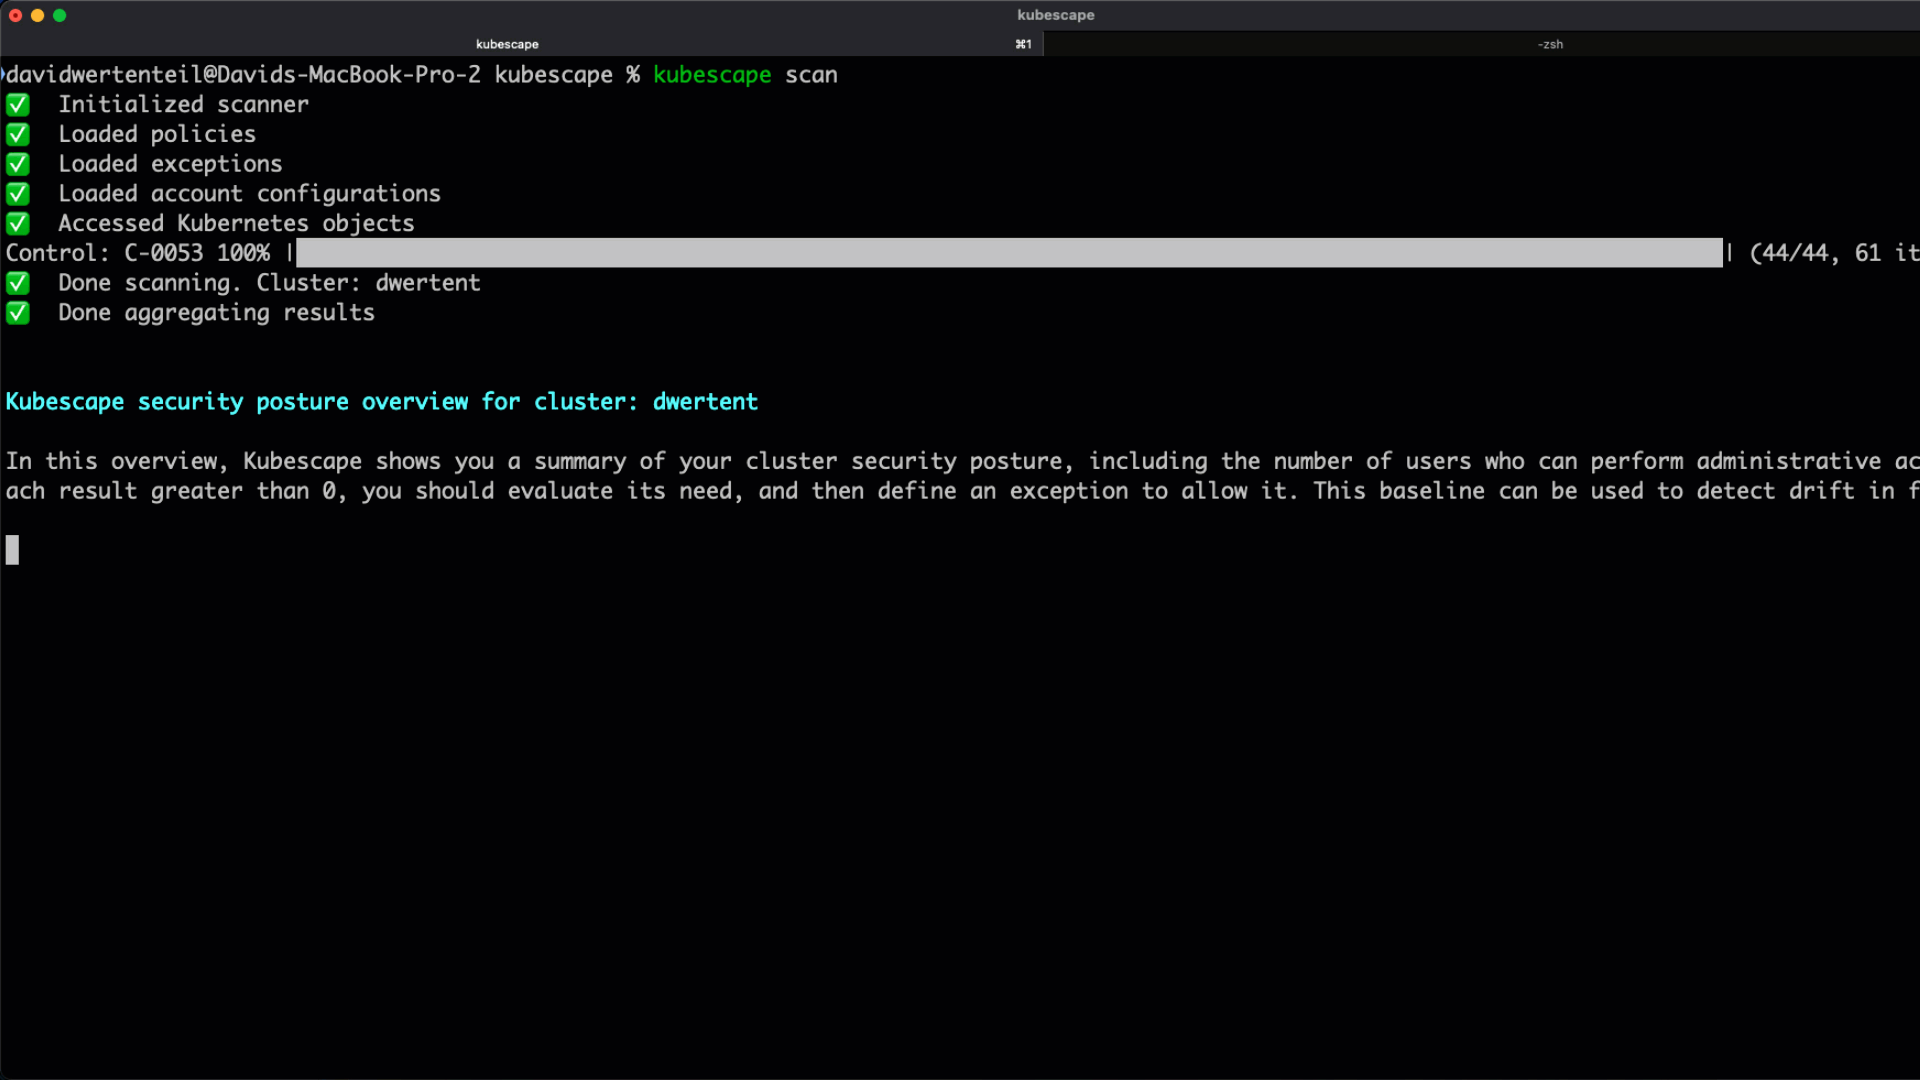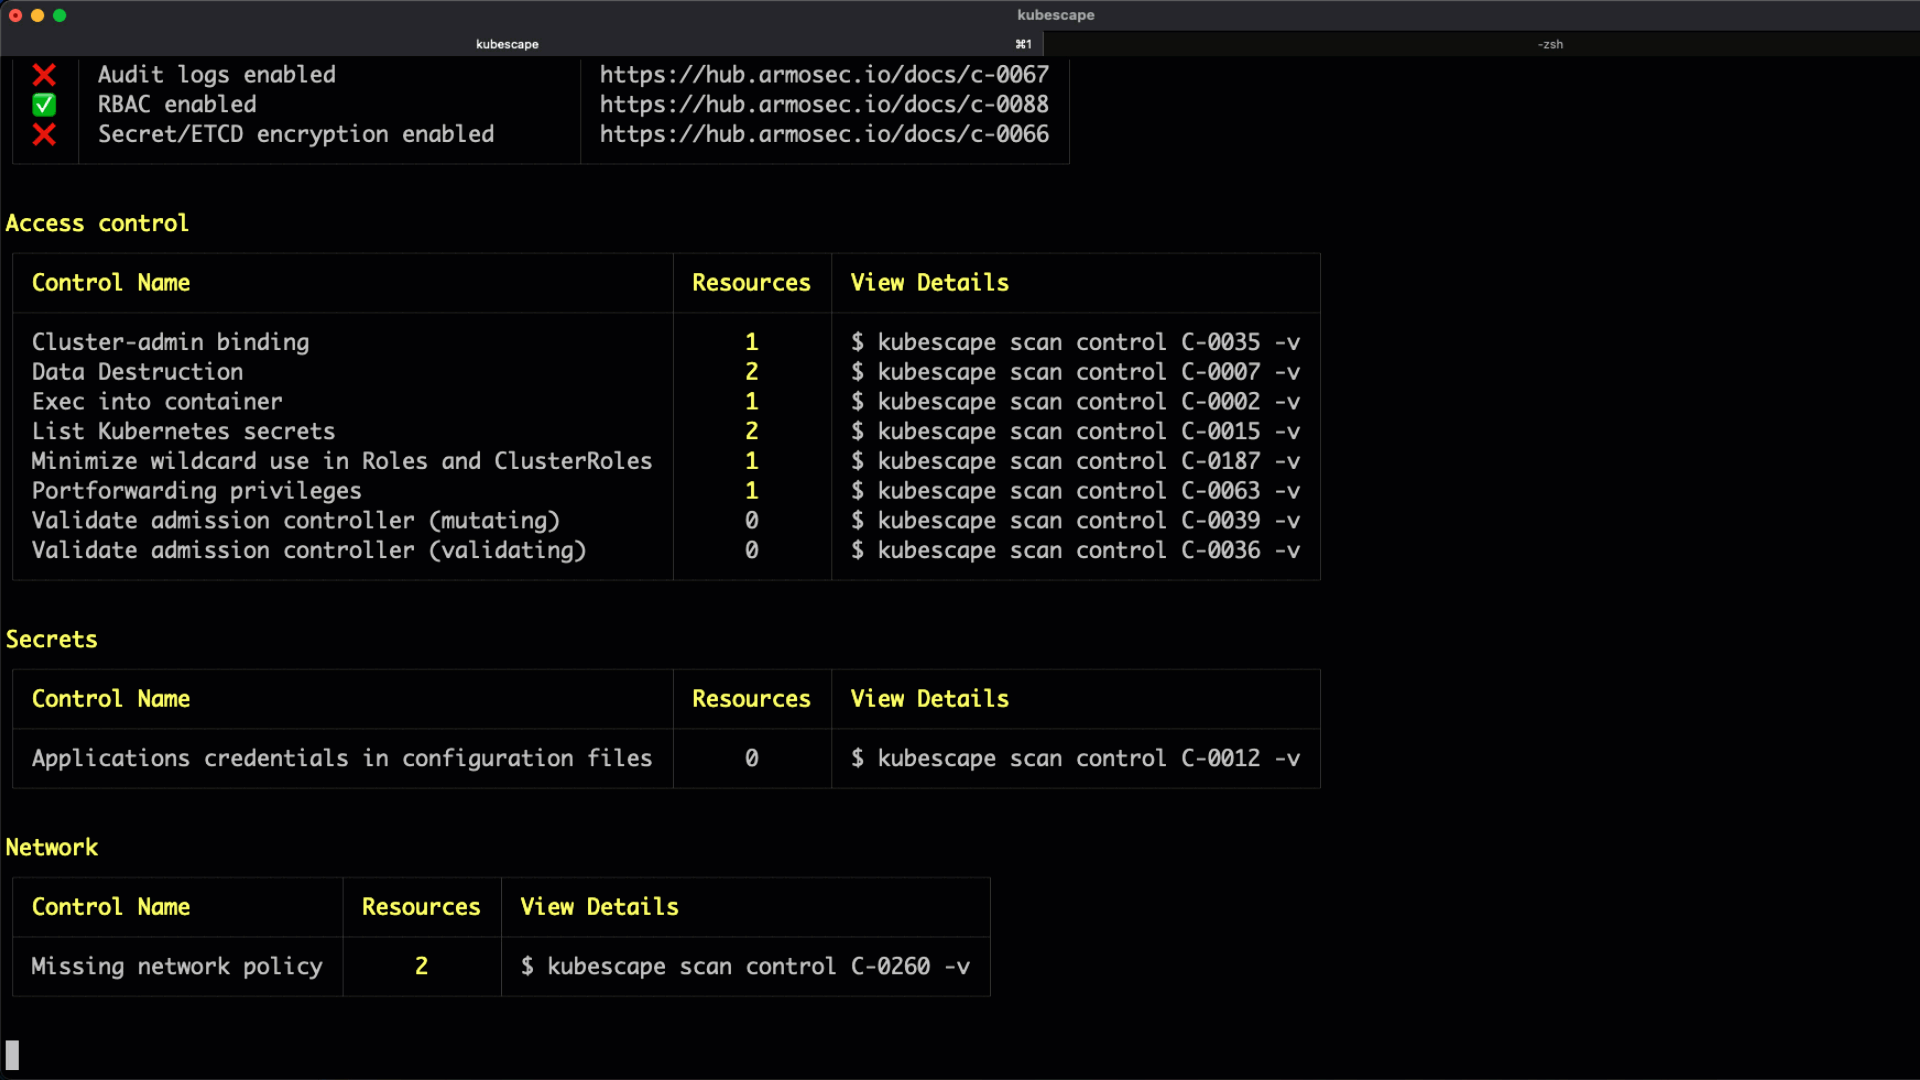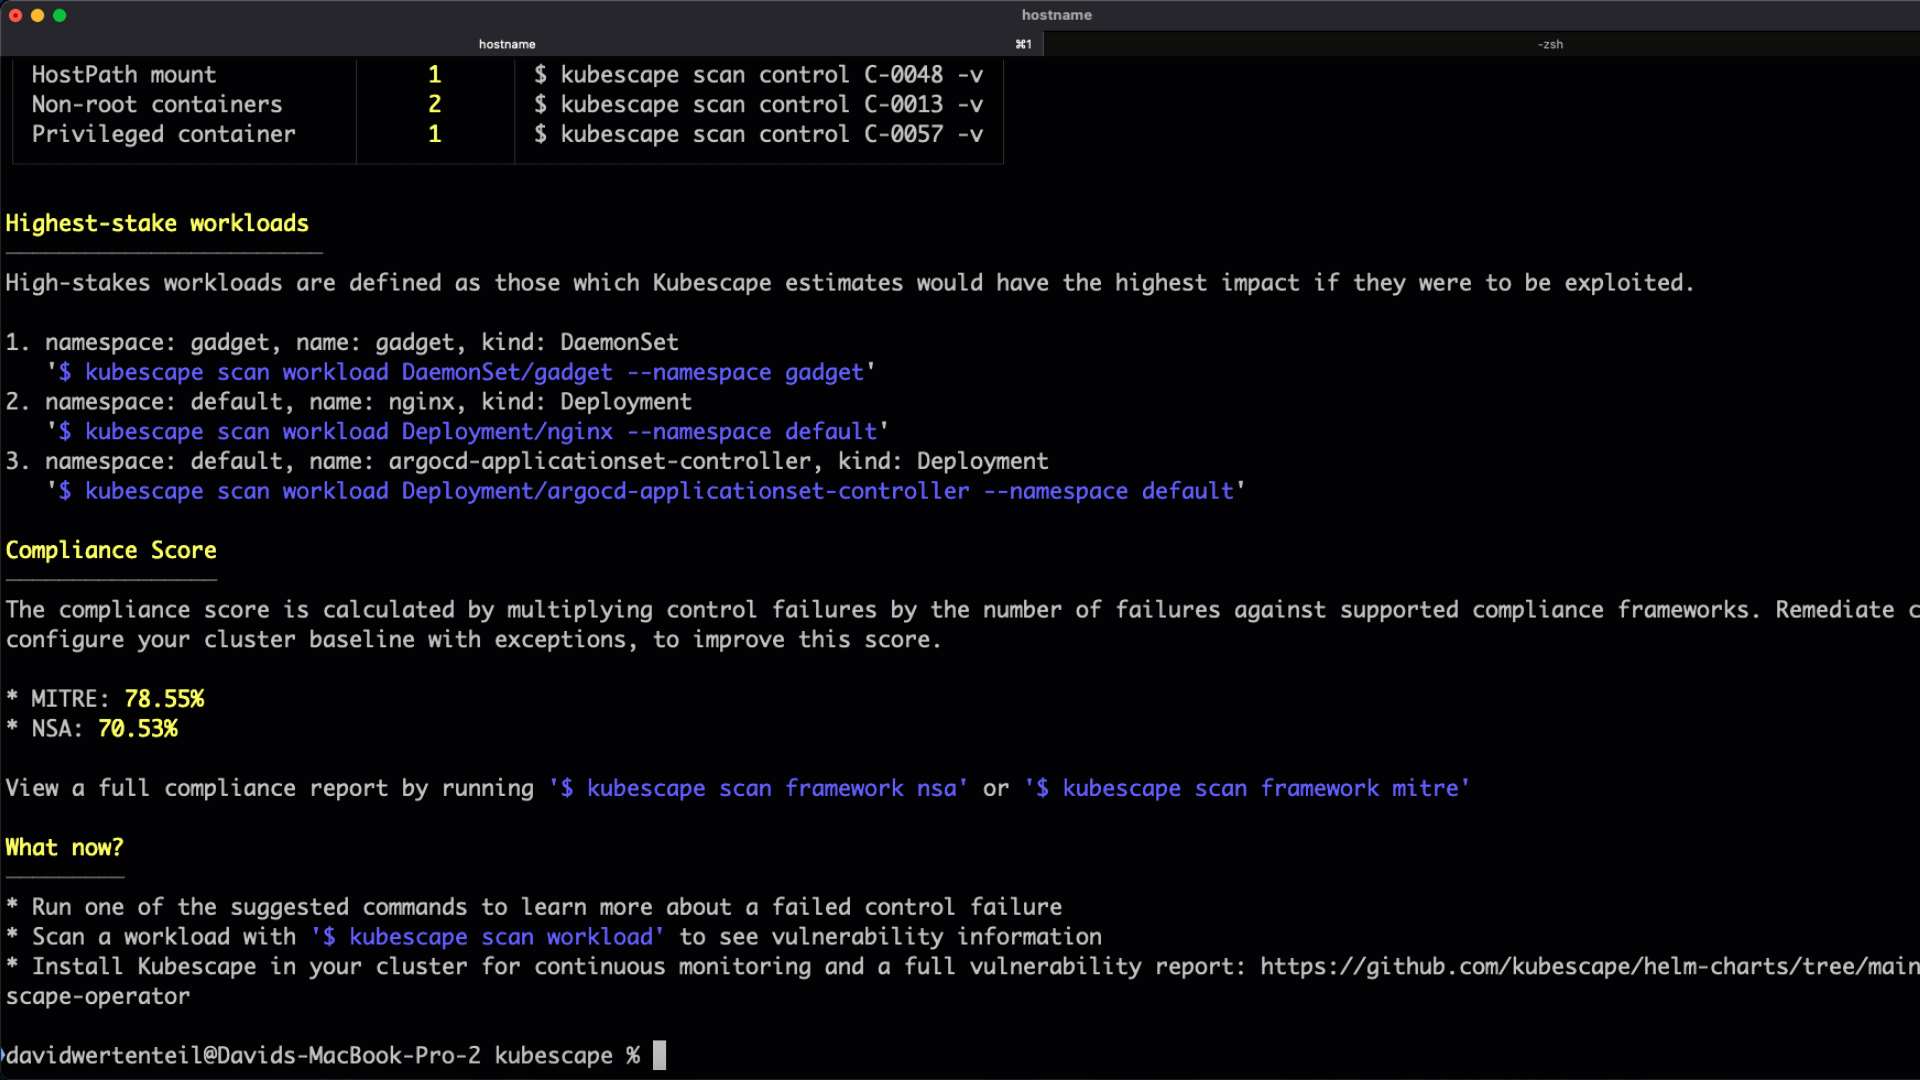
Open-source Kubernetes security platform scanning clusters, manifests, and images for misconfigurations, vulnerabilities, and compliance against NSA,…

Open-source Kubernetes security platform scanning clusters, manifests, and images for misconfigurations, vulnerabilities, and compliance against NSA,…

Minimal CVE Hardened container image collection

CLI tool and library for generating a Software Bill of Materials from container images and filesystems

A repo to automatically generate and keep updated a series of Docker images through GitHub Actions.

Generates SCAP, Ansible, Bash, and CEL security content for compliance evaluation and automated hardening across Linux hosts, containers, and…

Compiles source code into auditable, signed APK packages using declarative pipelines for Wolfi/Alpine, with multi-architecture QEMU emulation and…

A vulnerability scanner for container images and filesystems

Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…

Client-side Linux virtual machine running in the browser via WebAssembly, with Tailscale networking, Dockerfile-based custom images, and CTF…

Rootless container runtime and sandbox that launches kernel-enforced OCI images in milliseconds with no daemon, featuring resource profiles, seccomp…

JIT-based userspace Linux kernel that runs containers natively on Apple Silicon macOS without a VM. Drop-in Docker Engine API replacement with…

OWASP project defining an AI Bill of Materials (AIBOM) standard to document AI/ML components, dependencies, and supply chain risks for AI security…

GitLab CI component for Trivy scanning

Automated Snyk vulnerability scanning for dependencies and Docker images in Bitbucket Pipelines, with severity thresholds and monitoring options.

Monitors cryptographic integrity of container images, releases, and Git tags for supply chain security, verifying Sigstore cosign signatures with…

:unlock: :unlock: Find secrets and passwords in container images and file systems :unlock: :unlock:

CLI tool that explains CVEs in plain English and scans repos for impact. Powered by Claude.

Public OCI-Image (docker image) Security Checker